
#FactCheck-Amarnath Yatra Video Falsely Shared as Chinese Incursion in Arunachal Pradesh
Executive Summary
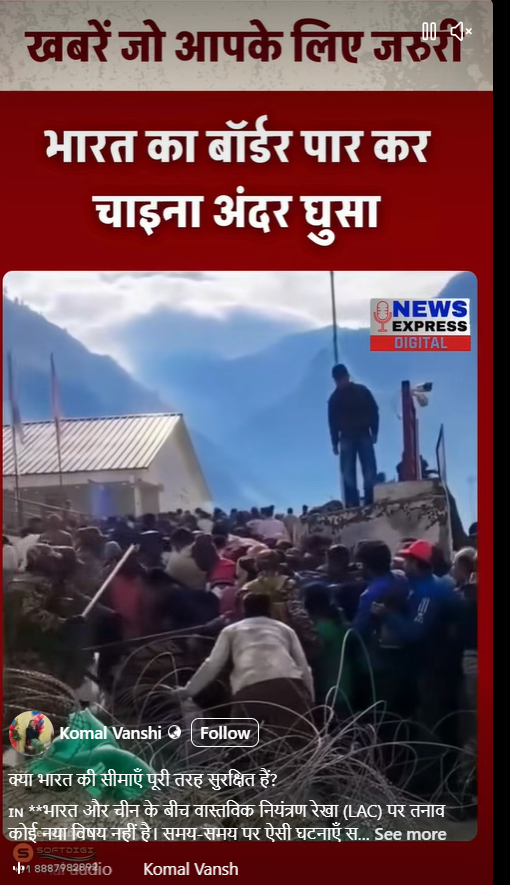
Several social media posts are claiming that Chinese troops have entered nearly 60 kilometres inside Arunachal Pradesh. Amid these claims, a video showing security personnel managing a large crowd is being widely circulated as footage from Arunachal Pradesh. Users are sharing the clip claiming it captures the situation following the alleged Chinese intrusion. CyberPeace Research Wing found the claim to be false. The viral video is not from Arunachal Pradesh. It actually shows Baltal Base Camp during the Amarnath Yatra in Jammu and Kashmir. The Government of India has also categorically denied reports of any recent Chinese intrusion into Indian territory.
Claim
A Facebook user, "Komal Vanshi," shared the video on July 8, 2026, claiming that Chinese People's Liberation Army (PLA) soldiers had entered deep inside Arunachal Pradesh and referring to alleged incidents along the Line of Actual Control (LAC). The post was accompanied by the viral video, suggesting it was related to the alleged intrusion.
https://www.facebook.com/reel/1585091393251089
Fact Check
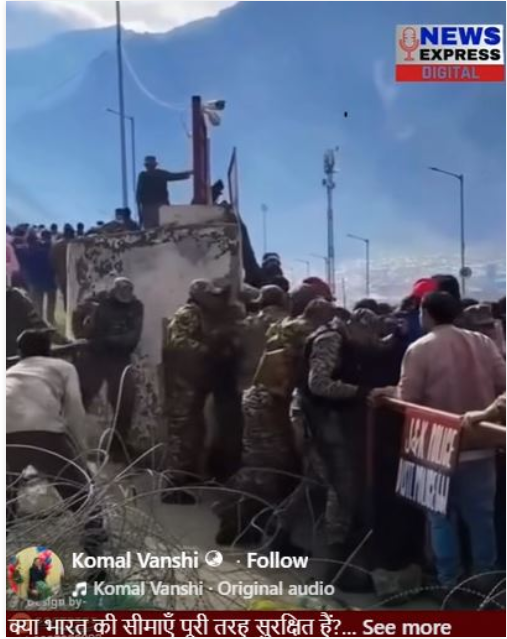
We first carefully examined the viral video. During the analysis, we noticed barricades bearing the words "Jammu & Kashmir Police." This clearly indicated that the footage could not have been recorded in Arunachal Pradesh.
In the next step, we extracted multiple keyframes from the video and conducted a reverse image search using Google Lens. Although the video was widely shared with the Arunachal Pradesh claim, our search led us to a YouTube Shorts video uploaded on July 7, 2026, identifying the location as Baltal, one of the main base camps for the annual Amarnath Yatra in Jammu and Kashmir.
https://www.youtube.com/watch?v=EEfP2RckyJM
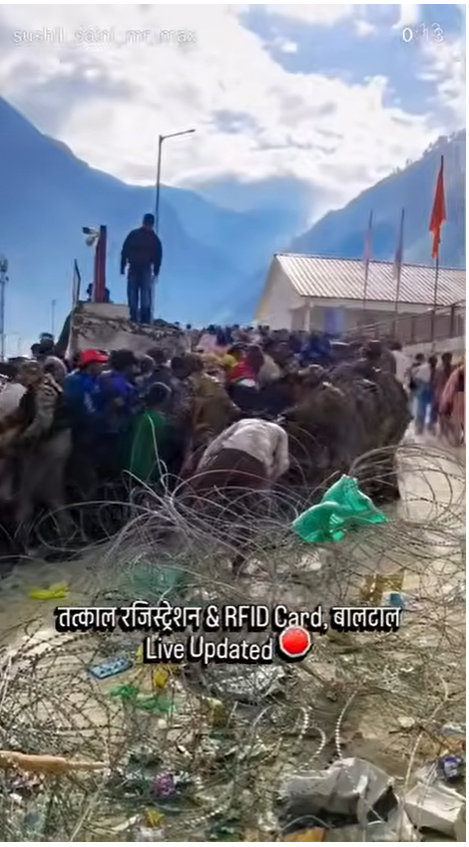
The visual details in the YouTube video matched the viral footage, confirming that it was filmed at Baltal Base Camp and had no connection with Arunachal Pradesh or any alleged Chinese military movement
Conclusion
CyberPeace Research Wing found that the viral claim is false. The video being circulated as evidence of a Chinese military incursion into Arunachal Pradesh actually shows crowd management arrangements at Baltal Base Camp during the Amarnath Yatra in Jammu and Kashmir. The footage has been falsely linked to an unrelated claim about Chinese troops entering Indian territory. There is no evidence that the video depicts any incident related to the India-China border.

Related Blogs
With AI touching new milestones everyday an increasing need for making it secure is also arising. As these AI companies increase their operations and position in the market as providers of powerful tools in the market. A recent concern due to Anthropic's recent privacy policy update which will be effective from July 8, 2026 shows how companies have begun expanding the amount of personal information they collect in the name of safety, compliance, and trust. While they are being demonstrated as measures to improve safety of users and prevent abuse, it raises important questions about privacy, biometric data, surveillance, data retention, and user autonomy, some of which we will be addressing in this article.
Identity Verification of consumers
One of the most notable update to Anthropic's privacy policy is the category of "Verification Data." According to the policy, users may be asked to verify their age or identity in certain circumstances. Depending on the verification method, Anthropic may collect:
- Images of government-issued identity documents;
- Information appearing on those documents, including identification numbers and date of birth for age verification;
- Photographs or videos of the user;
- Facial geometry templates, which may constitute biometric data under certain legal frameworks; and
- The outcome of the verification process.
At first, this may appear similar to the Know Your Customer (KYC) procedures employed by banks or financial institutions but Claude is not a banking service. It is a consumer AI platform. The issue is not that verification exists, but that the circumstances under which it may be required remain undefined.
THE PROBLEM WITH “CERTAIN CIRCUMSTANCES”
The policy refers to verification being required in "certain circumstances." The public notification from Anthropic mentions that these circumstances may include access to particular features, routine platform integrity checks, abuse prevention mechanisms, policy enforcement activities, or legal compliance obligations. The ambiguity of this phrase raises important concerns. From a user perspective, it is difficult to determine, When verification may be triggered ? Whether verification applies only to suspicious accounts ? Whether access to future features may depend upon verification ? Whether users in particular regions will face more frequent verification requirements ? Whether verification requests may increase as AI regulation expands ? This broad language and discretionary power that the company has along with flexibility in the hands of the company creates uncertainty for users who may have initially joined a platform expecting only an email address and payment information to be required.
Government IDs collection: A new risk category
Almost all AI services have operated without collecting government-issued identity documents. Once a company begins processing such information, the privacy implications change dramatically. Because government issued IDs contain: Full legal names, Dates of birth, Identification numbers, Addresses, Photographs and information regarding nationality. When companies collect these documents, they will have an important database of highly sensitive personal information. Even if the company itself does not retain the documents indefinitely, the existence of a verification process introduces additional privacy and security risks. As per Anthropic has stated that identity verification is conducted through third-party providers such as Persona. According to article on the official site titled ‘Identity verification on Claude’, Persona stores the identity documents and selfie data, while Anthropic retains access to verification records when necessary. From the user's perspective, several important realities remain: First, the data still exists somewhere. Second, another third party organization is now involved in processing highly sensitive personal information. Third, Anthropic retains the ability to access verification records under certain circumstances. Therefore, although Anthropic may not directly maintain copies of every uploaded identity document, the practical result remains that sensitive information enters a broader ecosystem of entities and systems. Identity documents today are among the most valuable forms of personal information from the perspective of fraudsters, cybercriminals, and malicious actors. Therefore, any system that handles such documents becomes an attractive target for attack.
More information on persona’s government ID verification- https://withpersona.com/blog/what-is-government-id-verification
The Biometric Dimension
Another significant aspect of the update is the reference to facial geometry templates. Unlike passwords, biometric identifiers cannot easily be changed if compromised. A person can replace a password or even obtain a new identification card, but they cannot simply obtain a new face. Facial geometry templates are sensitive because they enable automated identity matching. Although these templates, as claimed, are not equivalent to photographs, they are nevertheless derived from unique physical characteristics of a person. In many jurisdictions, including parts of the European Union and several U.S. states, biometric data receives enhanced legal protection because of its permanence and sensitivity, let us see how it unfolds in these jurisdictions.
The Unanswered Retention Question
It is unclear in the policy as to how long the data will be retained because retention limits serve as one of the most important safeguards in modern privacy law, they have given another vague answer that “They're bound to protect it with industry-standard security controls and delete it in line with the retention limits we've set and applicable law.” The longer sensitive information remains stored, the greater the likelihood of unauthorized access, misuse, accidental disclosure, or legal compulsion.
Court Orders and Government Access
Anthropic may be required to disclose information pursuant to valid legal processes such as subpoenas, court orders, warrants, or regulatory directives. The existence of identity verification records means that future requests could potentially be linked to verified identities rather than pseudonymous accounts. This does not mean governments receive unrestricted access to user data. However, it does mean that once identity verification information exists within a company's ecosystem, it may become subject to lawful disclosure requirements. The privacy implications are therefore materially different from those associated with anonymous or pseudonymous AI usage.
Shifting Responsibility onto Users
Another concern is that the privacy policy states that users are responsible for ensuring they possess the necessary rights, permissions, or authority when uploading files, connecting third-party services, or instructing Claude to retrieve information. Anthropic is effectively informing users that they bear responsibility for ensuring that uploaded or connected data is lawfully accessible. As AI assistants gain greater capabilities, this transfer of responsibility from platform to user is likely to become increasingly common. Beyond individual privacy, Anthropic's verification policy also raises larger questions about data sovereignty and the cross-border movement of sensitive personal information. In India, the Justice K.S. Puttaswamy (Retd.) v. Union of India judgment recognized privacy as a fundamental right under Article 21 of the Constitution, affirming that individuals have the right to informational self-determination and control over their personal data. Yet, under Anthropic's verification framework, an Indian user may be required to upload a government-issued identity document and biometric information, which are processed by Persona, a U.S.-based identity verification company acting on behalf of Anthropic. Although users voluntarily consent to this process, it nevertheless results in highly sensitive identity information crossing national borders and entering the control of foreign private entities governed primarily by foreign contractual arrangements and multiple legal regimes. While governments issue identity documents as sovereign instruments of citizenship, their verification and processing are increasingly outsourced to multinational technology companies. Questions arise not only about how securely such information is handled, but also about which country's laws ultimately govern access, retention, disclosure, and accountability when personal data leaves the jurisdiction in which it originated. Under the Digital Personal Data Protection Act, 2023, cross-border transfer of personal data is generally permitted unless the Central Government specifically restricts transfers to certain jurisdictions. Therefore, a foreign company processing identity documents is not, by itself, unlawful but this legality does not eliminate legitimate concerns. Users realistically have limited bargaining power and little practical understanding of how long their identity documents, biometric templates, or verification records will be retained, who within the corporate ecosystem may access them, or how they may be disclosed pursuant to foreign legal processes.
Conclusion
The policy is commendable in some respects because it openly identifies the categories of information that may be collected rather than obscuring them behind vague terminology. However, important concerns remain regarding the extent of verification triggers, the handling of biometric information, the absence of clearly disclosed retention periods, and the long-term implications of linking AI accounts to government-issued identities. As AI systems become more integrated into daily life, these questions will likely become central issues in debates about digital privacy, surveillance, autonomy, and the future governance of artificial intelligence.
Executive Summary:
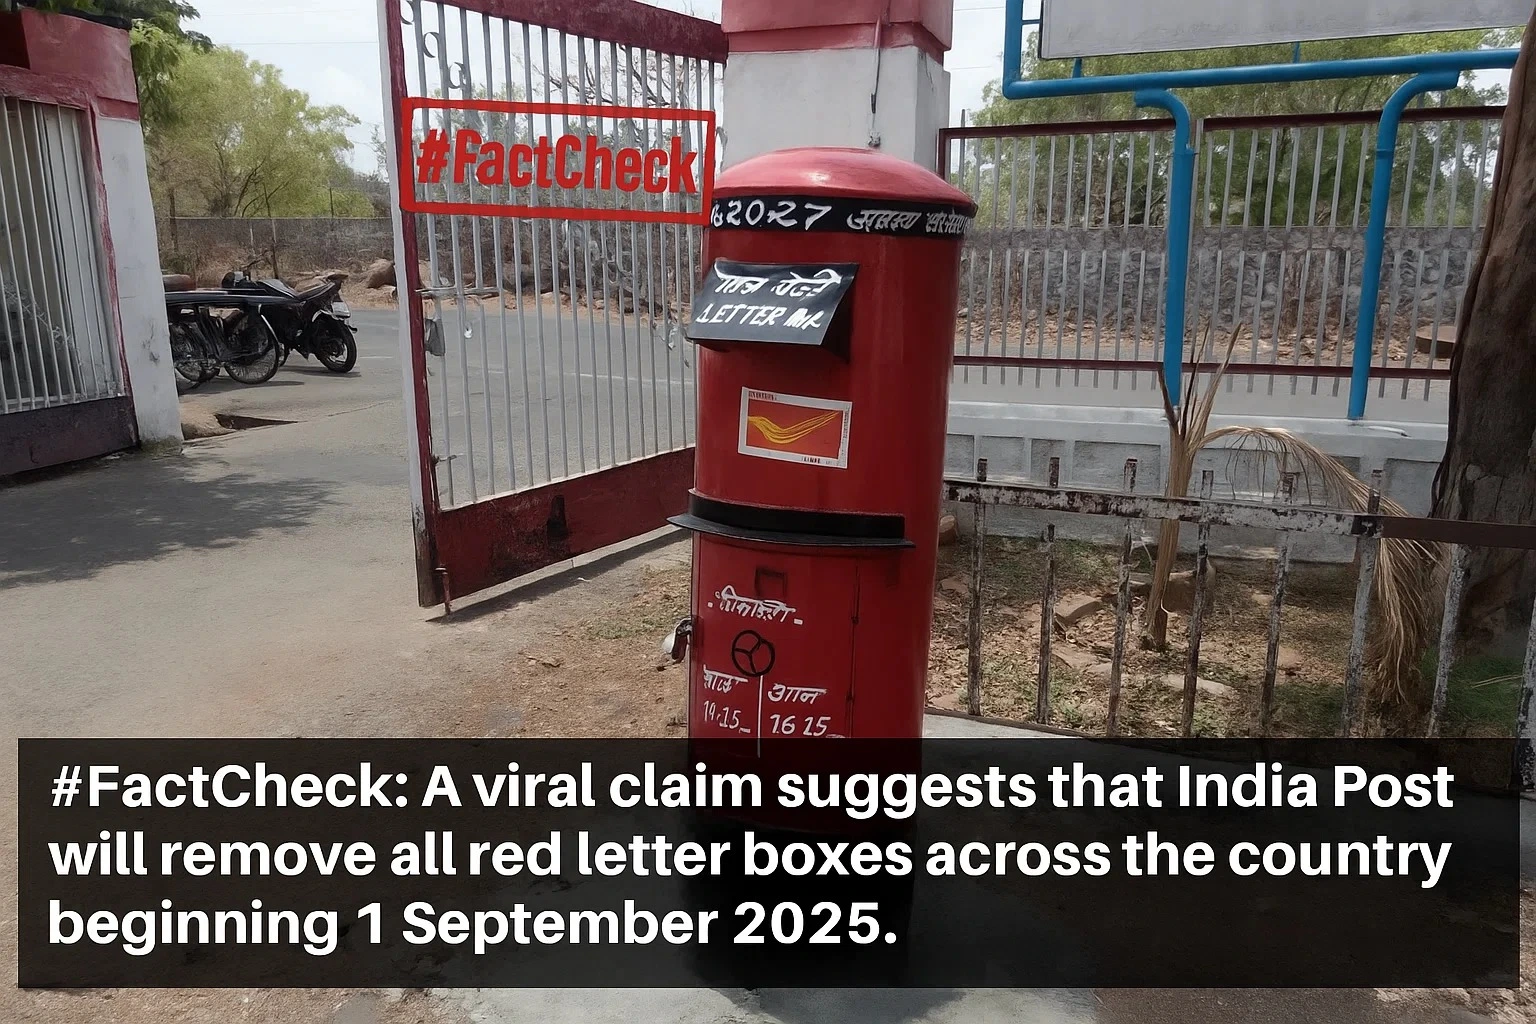
A viral social media claim suggested that India Post would discontinue all red post boxes across the country from 1 September 2025, attributing the move to the government’s Digital India initiative. However, fact-checking revealed this claim to be false. India Post’s official X (formerly Twitter) and Instagram handles clarified on 7 August 2025 that red letterboxes remain operational, calling them timeless symbols of connection and memories. No official notice or notification regarding their discontinuation exists on the Department of Posts’ website. This indicates the viral posts were misleading and aimed at creating confusion among the public.
Claim:
A claim is circulating on social media stating that India Post will discontinue all red post boxes across the country effective 1 September 2025. According to the viral posts,[archived link] the move is being linked to the government’s push towards Digital India, suggesting that traditional post boxes have lost their relevance in the digital era.
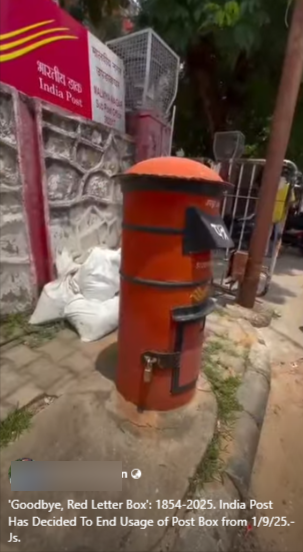
Fact Check:
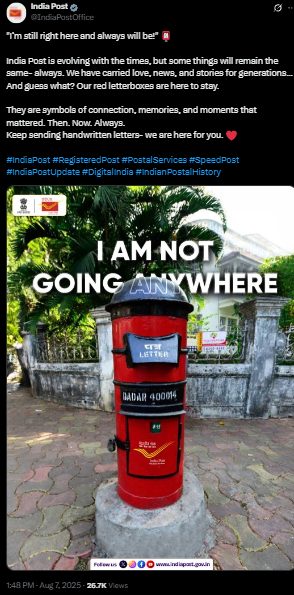
After conducting a reverse image analysis, we found that the official X handle of India Post, in a post dated 7 August 2025, clarified that the viral claim was incorrect and misleading. The post was shared with the caption:
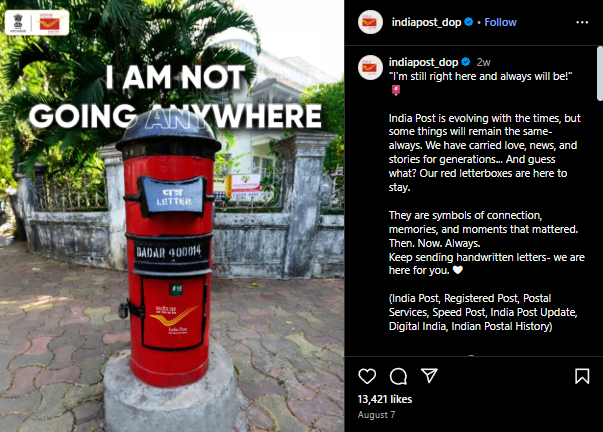
I’m still right here and always will be!"
India Post is evolving with the times, but some things will remain the same- always. We have carried love, news, and stories for generations... And guess what? Our red letterboxes are here to stay.
They are symbols of connection, memories, and moments that mattered. Then. Now. Always.
Keep sending handwritten letters- we are here for you.
This directly refutes the viral claim about the discontinuation of the red post box from 1 September 2025. A similar clarification was also posted on the official Instagram handle @indiapost_dop on the same date.
Furthermore, after thoroughly reviewing the official website of the Department of Posts, Government of India, we found absolutely no trace, notice, or even the slightest mention of any plan to discontinue the iconic red post boxes. This complete absence of official communication strongly reinforces the fact that the viral claim is nothing more than a baseless and misleading rumour.
Conclusion:
The claim about the discontinuation of red post boxes from 1 September 2025 is false and misleading. India Post has officially confirmed that the iconic red letterboxes will continue to function as before and remain an integral part of India’s postal services.
- Claim: A viral claim suggests that India Post will remove all red letter boxes across the country beginning 1 September 2025.
- Claimed On: Social Media
- Fact Check: False and Misleading

Introduction
Google Play has announced its new policy which will ensure trust and transparency on google play by providing a new framework for developer verification and app details. The new policy requires that new developer accounts on Google Play will have to provide a D-U-N-S number to verify the business. So when an organisation will create a new Play Console developer account the organisation will need to provide a D-U-N-S number. Which is a nine-digit unique identifier which will be used to verify their business. The new google play policy aims to enhance user trust. And the developer will provide detailed developer details on the app’s listing page. Users will get to know who is behind the app which they are installing.
Verifying Developer Identity with D-U-N-S Numbers
To boost security the google play new policy requires the developer account to provide the D-U-N-S number when creating a new Play Console developer account. The D-U-N-S number assigned by Dun & Bradstreet will be used to verify the business. Once the developer creates his new Play Console developer account by providing a D-U-N-S number, Google Play will verify the developer’s details, and he will be able to start publishing the apps. Through this step, Google Play aims to validate the business information in a more authentic way.
If your organisation does not have a D-U-N-S number, you may check on or request for it for free on this website (https://www.dnb.com/duns-number/lookup.html). The request process for D-U-N-S can take up to 30 days. Developers are also required to keep the information up to date.
Building User Trust with Enhanced App Details
In addition to verifying developer identities in a more efficient way, google play also requires that developer provides sufficient app details to the users. There will be an “App Support” section on the app’s store listing page, where the developer will display the app’s support email address and even can include their website and phone number for support.
The new section “About the developer” will also be introduced to provide users with verified identity information, including the developer’s name, address, and contact details. Which will make the users more informed about the valuable information of the app developers.
Key highlights of the Google Play Polic
- Google Play came up with the policy to keep the platform safe by verifying the developers’ identity and it will also help to reduce the spread of malware apps and help the users to make confident informed decisions about the apps they download. Google Play announced the policy by expanding its developer verification requirement to strengthen Google Play as a platform and build user trust. When you create a new Play Console Developer account and choose organisation as your account type you will now need to provide a D-U-N-S number.
- Users will get detailed information about the developers’ identities and contact information, building more transparency and encouraging responsible app development practices.
- This policy will enable the users to make informed choices about the apps they download.
- The new “App support” section will provide enhanced communication between users and developers by displaying support email addresses, website and support phone numbers, streamlining the support process and user satisfaction.
Timeline and Implementation
The new policy requirements for D-U-N-S numbers will start rolling out on 31 August 2023 for all new Play Console developer accounts. The “About the developer” section will be visible to users as soon as a new app is published. and In October 2023, existing developers will also be required to update and verify their existing accounts to comply with the new verification policy.
Conclusion
Google Play’s new policy will aim to enhance the more transparent app ecosystem. This new policy will provide the users with more information about the developers. Google Play aims to establish a platform where users can confidently discover and download apps. This new policy will enhance the user experience on google play in terms of a reliable and trustworthy platform.
