
#FactCheck- AI-Generated Video Falsely Linked to Iranian Attack on Amazon Data Center in Bahrain
Executive Summary
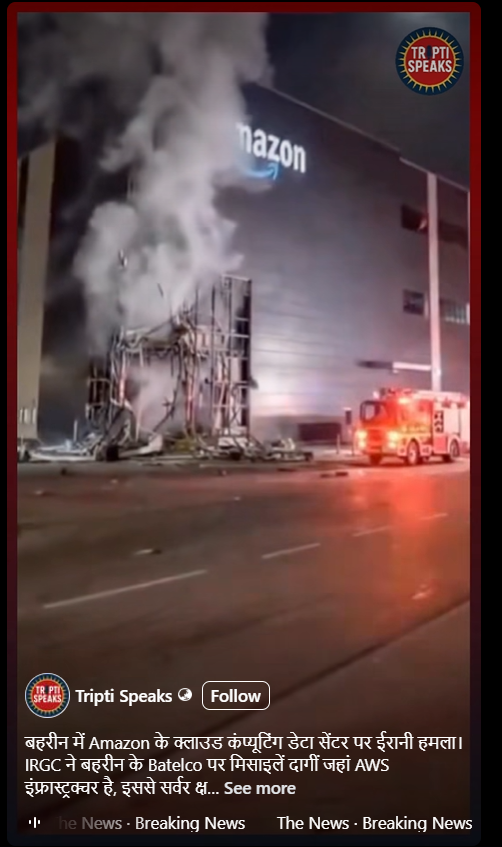
A video showing a damaged building allegedly belonging to Amazon is going viral on social media. The clip is being shared with the claim that it depicts the aftermath of an Iranian missile strike on an Amazon data center in Bahrain on April 1, 2026. However, research by CyberPeace has found the claim to be misleading. While reports confirm that Iran targeted a U.S.-linked cloud infrastructure in Bahrain, the viral video itself is not real footage and has been created using artificial intelligence.
Claim
A Facebook user, “Tripti Speaks,” shared the viral video on April 2, 2026, with the caption:“Iranian attack on Amazon’s cloud computing data center in Bahrain. IRGC fired missiles at Batelco in Bahrain where AWS infrastructure is located, damaging servers and disrupting services.”
- Archived link::https://perma.cc/XH7S-QTX6
Fact Check
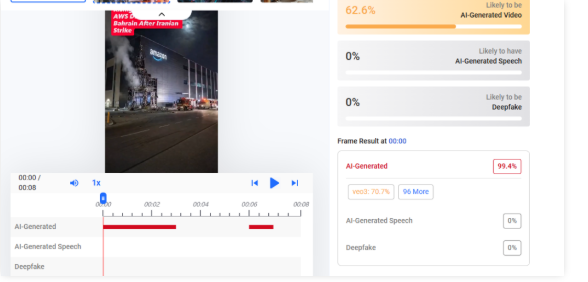
To verify the claim, we extracted multiple keyframes from the viral video and conducted a reverse image search using Google. However, we did not find any credible sources or reports featuring this specific footage. This raised suspicion about the authenticity of the video. We then analyzed it using the AI detection tool Hive Moderation, which indicated a 63% probability that the video is AI-generated.
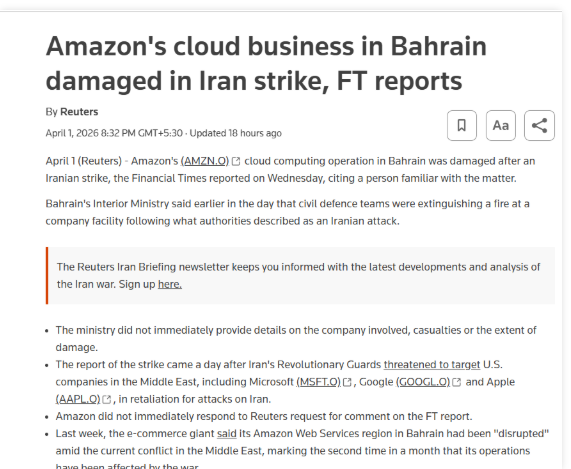
According to a report published by Reuters on April 1, 2026, Iran launched a missile attack targeting Amazon’s cloud computing operations in Bahrain. The Islamic Revolutionary Guard Corps (IRGC) had earlier warned that U.S.-linked companies in the Middle East—including Microsoft, Google, and Apple—could be targeted.
Conclusion
Our research found that while there are credible reports confirming an Iranian attack on cloud infrastructure linked to Amazon in Bahrain, the viral video circulating on social media does not depict the real incident. The footage shows no presence in verified news coverage and has been flagged by AI detection tools as likely artificial. Therefore, the video is AI-generated and misleadingly linked to the incident.

Related Blogs
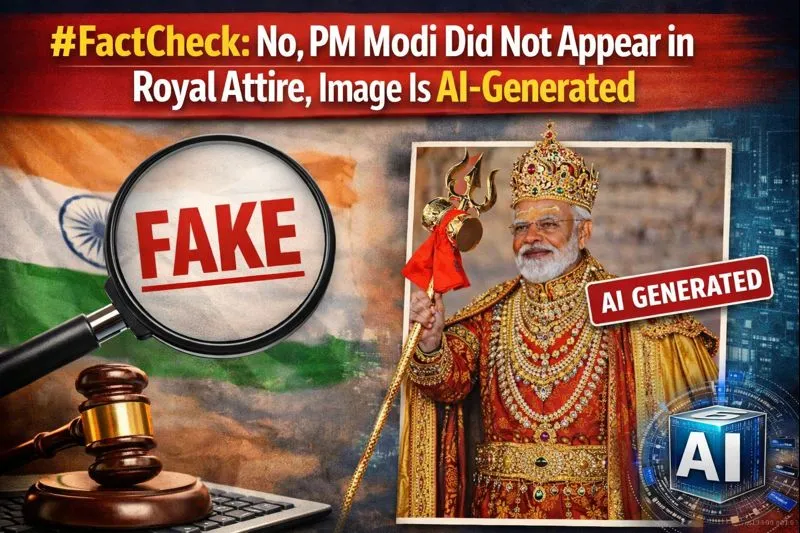
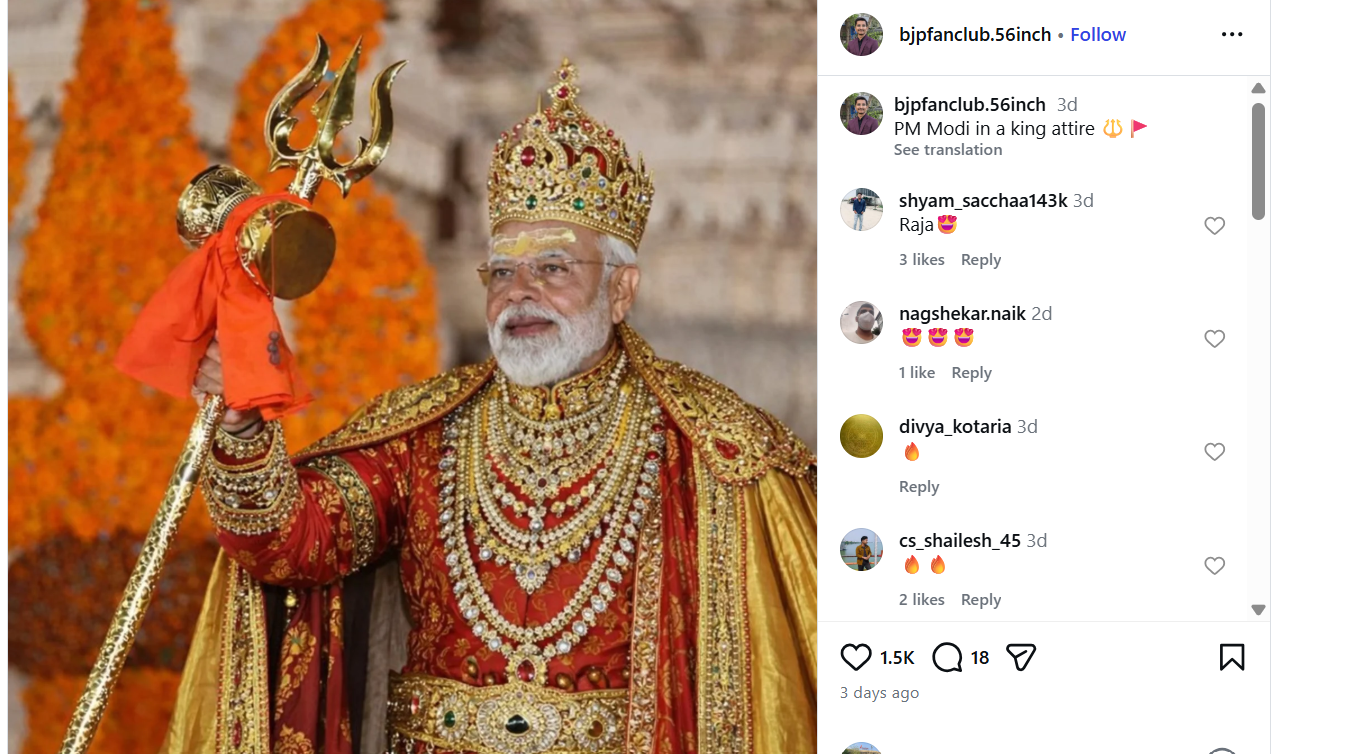
A photograph showing Prime Minister Narendra Modi holding a trident and dressed in royal attire is being widely shared on social media. Users circulating the image are claiming that it shows PM Modi in a regal outfit.
However, a verification by the Cyber Peace Foundation’s Research Desk has found that the claim is false. The investigation established that the viral image is not authentic and has been generated using Artificial Intelligence (AI).
Claim:
On January 11, 2026, several Instagram users shared the image with captions describing it as a photograph of Prime Minister Modi in royal attire.
Links and archived versions of the posts, along with screenshots, are provided below.
Fact Check:
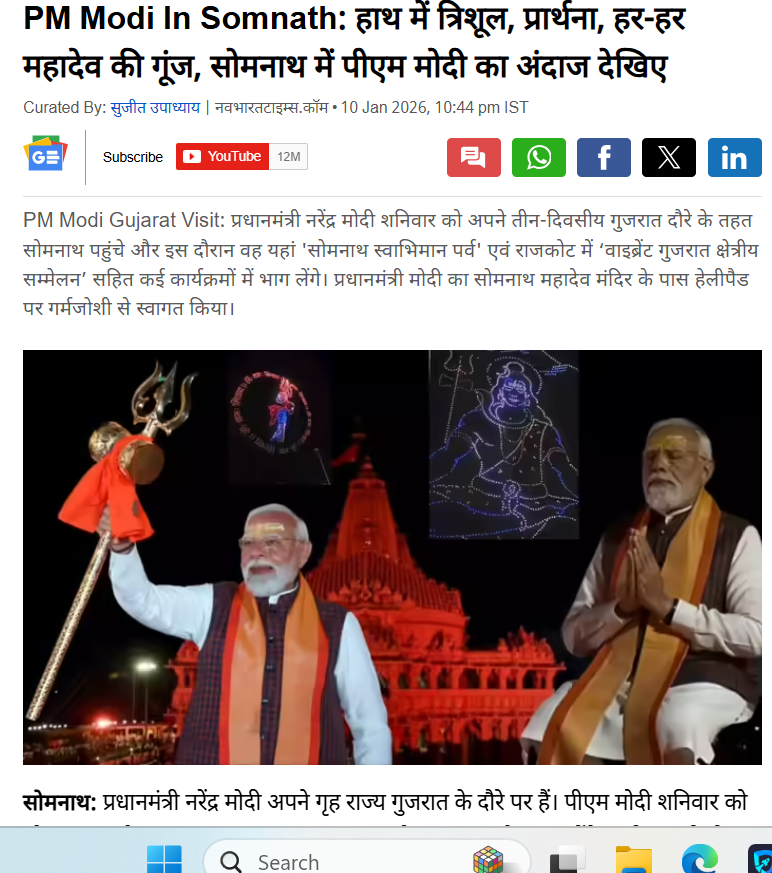
To verify the claim, relevant keywords such as “PM Modi holding trishul” were searched on Google. This led to a report published by Navbharat Times on January 10, 2025. The report features photographs of Prime Minister Modi holding a trident during his visit to the Somnath Temple. However, in the original images, he is seen wearing normal attire, not royal clothing as shown in the viral image. Link and screenshot
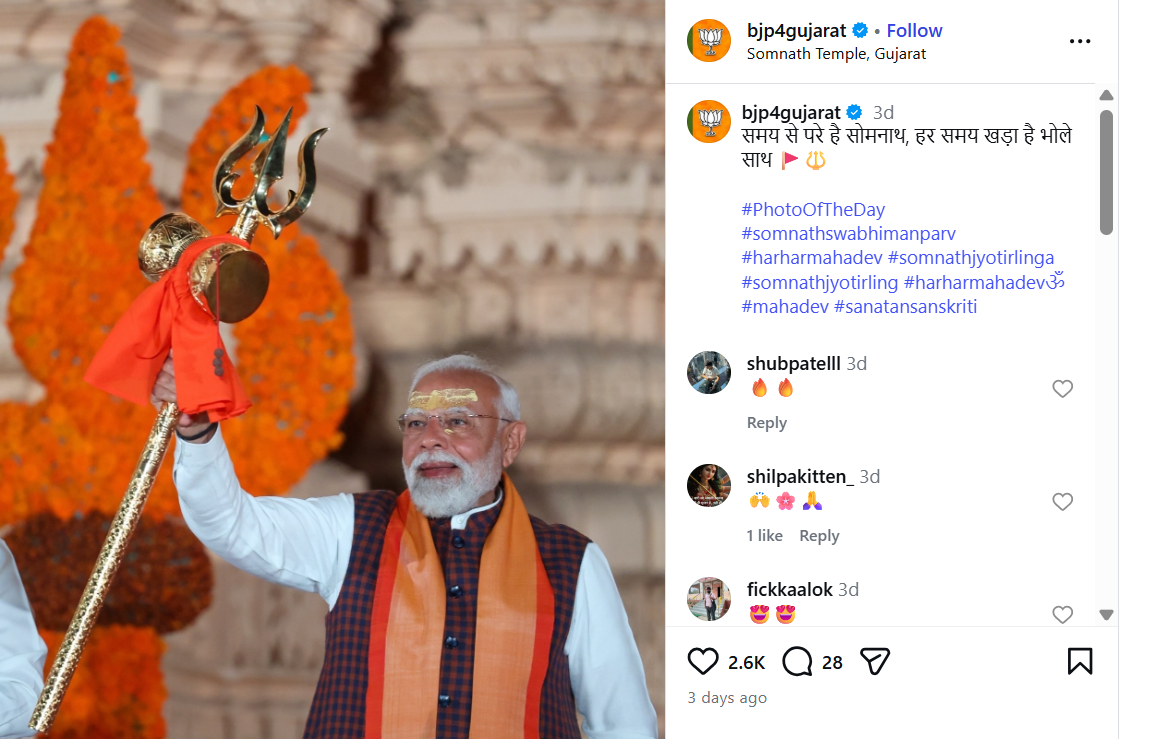
In the next step of the investigation, the original photograph was traced to the official Instagram account of BJP Gujarat, where it was posted on January 11, 2026. The post clearly identifies the image as being from Somnath Temple. Link and screenshot: https://www.instagram.com/p/DTVlb-9Da1V
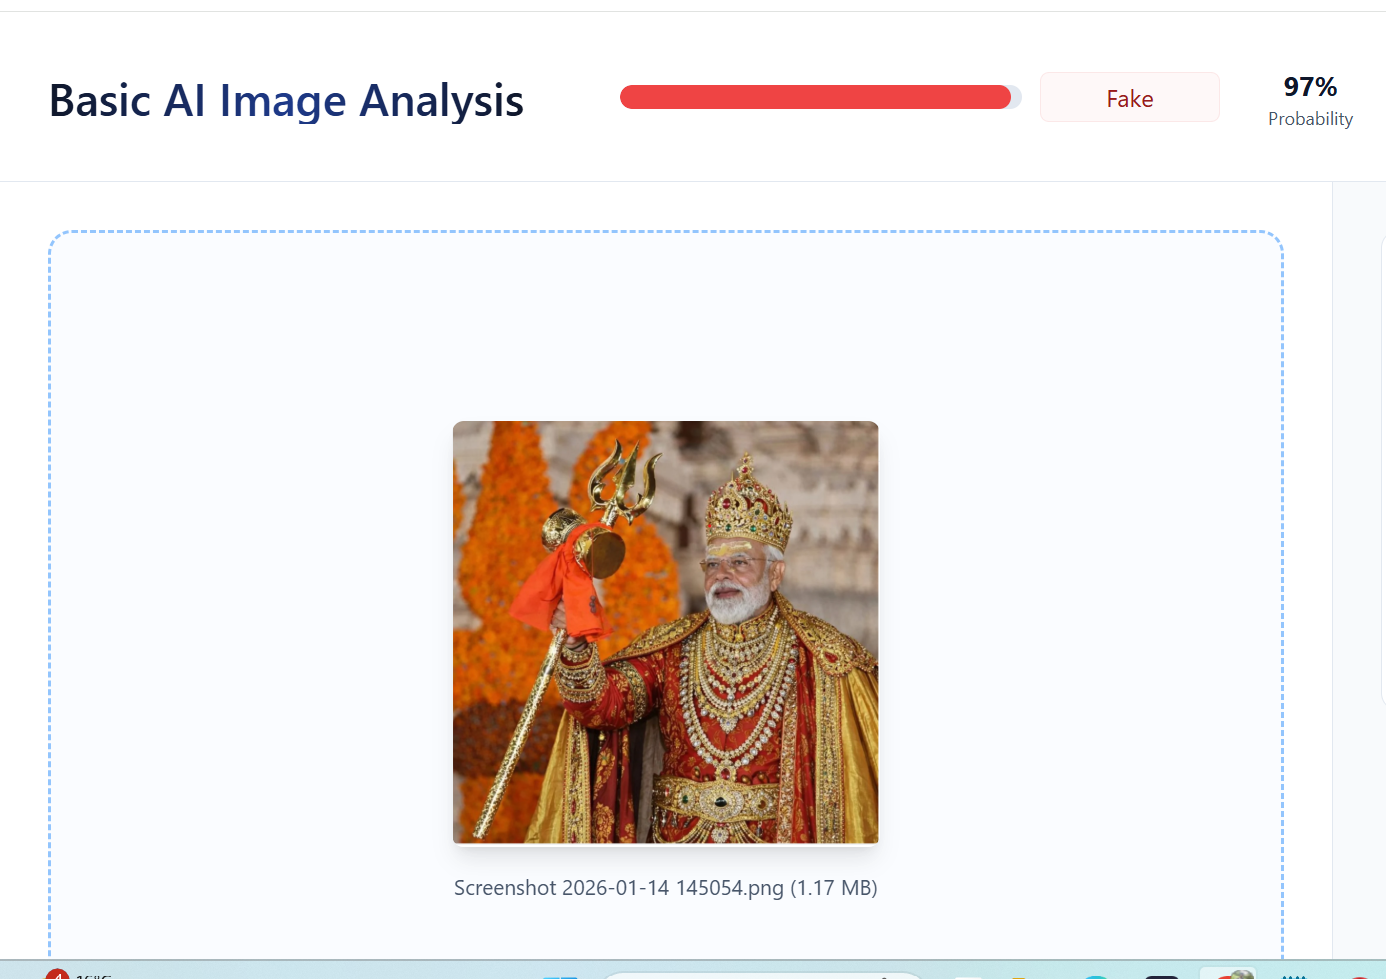
A close examination of the viral image raised suspicion about digital manipulation. The image was then analysed using the AI detection tool TruthScan. The tool’s assessment indicated a 97 percent likelihood that the image was AI-generated.
Further comparison between the viral image and the original photograph revealed that all visual elements match except the clothing, confirming that the attire was digitally altered using AI tools.
Conclusion
The claim that Prime Minister Narendra Modi appeared in royal attire is false. The Cyber Peace Foundation’s research confirms that the viral image was created using AI by altering the clothing in an original photograph taken during PM Modi’s visit to Somnath Temple. The manipulated image was shared online to mislead users.
Introduction
Picture this - you wake up one morning, check your phone, and discover that a fraudster has emptied your bank account overnight. Your first instinct is to call someone, anyone, who can stop the money from vanishing for good. For millions of Indians today, that number is 1930, the national cybercrime helpline. At a high-level review meeting in June 2026, Union Home Minister Amit Shah directed that the helpline undergo a comprehensive revamp, one that brings in artificial intelligence, multilingual support, and a stronger framework for resolving victim grievances. This is not a minor patch. It is a signal that India wants to treat cybercrime response as a serious governance priority rather than an administrative checkbox.
The Evolution of 1930: From a Pilot Number to National Infrastructure
The helpline’s origin lies in 155260 (Old helpline no.), launched in 2020 by the Indian Cyber Crime Coordination Centre (I4C) with the Reserve Bank of India and the banking sector, built specifically to intercept financial fraud before funds could be laundered across accounts. In 2021, it was renamed 1930 to make the number easier for citizens to recall under stress, a small but telling decision: a security architecture only works if people can remember it during a crisis. It was paired with the National Cybercrime Reporting Portal, launched in August 2019 to strengthen reporting and response mechanisms nationwide, which was later expanded to cover all categories of cybercrime after starting out limited to content-related offences. Over five years, state police forces extended 1930 into round-the-clock, multi-line operations and linked it to local cyber cells, turning a central scheme into genuinely federated infrastructure. The numbers now justify that investment: more than ₹7,000 crore has been saved nationally through the Citizen Financial Cyber Fraud Reporting and Management System, while Mumbai alone blocked or recovered nearly ₹202 crore for victims in 2025 through the helpline. What began as a pilot number has become a core node in India’s financial security architecture.
AI and Multilingual Support as a Citizen-Centric Governance Shift
What makes Shah’s directive significant is not the technology itself but the design philosophy it embeds. The instruction to integrate AI and multilingual support is explicitly aimed at removing language barriers and enabling faster, more efficient complaint registration across the country. For a country with no single dominant spoken language, this is not a feature addition; it is a recognition that uniform, English-or-Hindi-first service design has been quietly excluding the citizens most vulnerable to fraud. Multilingual access addresses a long-standing gap by allowing citizens from non-Hindi-speaking states to report cybercrime in their own languages, significantly broadening reach. This marks a shift away from treating digital governance as a one-size-fits-all portal and toward treating it as a service obligation that adapts to the citizen rather than the reverse, a principle with implications well beyond cybercrime reporting.
Routing, Tracking and Escalation: Engineering Accountability into Redressal
The proposed reforms move beyond the front-end call experience into the architecture of follow-through. AI integration is expected to improve call routing, enable faster identification of fraud patterns, and assist real-time coordination between central and state law enforcement agencies. This matters because cyber fraud is intrinsically cross-jurisdictional: a victim in one state is often defrauded through an account opened in another. Shah directed central agencies to work closely with state governments to ensure that every call received on the helpline is followed through to its logical conclusion — language that, in policy terms, is an attempt to convert a complaint-registration system into a complaint-resolution system. Intelligent routing and case tracking, if implemented well, replace ad hoc coordination between states with a traceable escalation mechanism, the missing link that has historically allowed cases to stall after the first call was logged.
Frozen Accounts and the Procedural Burden on Victims
No part of the revamp is more consequential for ordinary victims than the directive on bank account freezes. The problem is compounded when a cybercrime complaint is registered in one state while the frozen account sits in another, leaving legitimate account holders, sometimes innocent third parties, locked out of their own funds for weeks. Shah directed that grievances arising from the freezing of bank accounts linked to financial frauds be addressed promptly, an instruction that responds directly to a problem now before the courts Judicial scrutiny on this exact question is intensifying: the Karnataka High Court recently held that banks cannot freeze an account completely when investigating agencies have directed only a partial freeze limited to a specified amount. A national, technology-backed mechanism for resolving such freezes would convert a recurring source of citizen grievance into a procedural safeguard, addressing one of the most cited failures of the existing system.
Reading the Reforms Within India’s Broader Cyber Resilience Strategy
Positioned within India’s wider digital governance trajectory, the 1930 revamp fits a recognisable pattern: build foundational infrastructure first, then layer intelligence and personalisation onto it once adoption is proven. The same logic shaped Aadhaar, UPI and the Digital India programme more broadly. India has seen a sharp rise in digital financial fraud, investment scams, sextortion and phishing attacks in recent years, and the Ministry of Home Affairs’ response, expanding I4C, building specialised cybercrime units, and now investing in AI-led citizen interfaces, signals that cyber resilience is being treated less as a law-enforcement afterthought and more as a core pillar of financial-system integrity, alongside RBI and NPCI-led safeguards.
Will These Reforms Strengthen Trust?
The credibility of any reform lies in implementation, not announcement. Public commentary on the revamp captures this tension well: citizens have welcomed the intent while noting that earlier promises of coordination did not always translate into resolved cases, and that awareness gaps in rural India persist regardless of how sophisticated the backend becomes The 1930 revamp will be judged not by how quickly complaints are registered, an area where India already performs reasonably, but by how reliably they are closed. If AI-driven routing and a genuine national escalation mechanism reduce the gap between complaint and resolution, particularly on account freezes, the reform will have done more for citizen trust than any awareness campaign could. If implementation falters at the state-bank coordination layer, the technology will simply make an old problem move faster without making it smaller.
Conclusion
The story of 1930 is the story of Indian digital governance maturing in real time: from a hastily assembled fraud helpline to a piece of national financial security infrastructure now being re-engineered for scale, language diversity and accountability. Amit Shah’s directive should be read not as a single announcement but as an acknowledgment that citizen-facing systems must keep pace with the sophistication of the threats they are built to counter. Whether this becomes a genuine trust-building reform or another well-intentioned upgrade depends entirely on what happens after the press statement — in LEA’s call centres, bank back-offices and state coordination desks across the country.
References
- https://www.republicworld.com/india/amit-shah-orders-major-overhaul-of-national-cybercrime-helpline-1930-calls-for-ai-upgrade-2026-06-17-128739
- https://the420.in/amit-shah-national-cybercrime-helpline-revamp/
- https://inc42.com/buzz/home-minister-amit-shah-calls-for-ai-led-revamp-of-national-cybercrime-helpline/
- https://thenewsmill.com/2026/06/amit-shah-directs-ai-upgrade-for-national-cybercrime-helpline-1930/
- https://risingkashmir.com/national/amit-shah-reviews-national-cybercrime-helpline-1930-calls-for-ai-upgrade-12048424
- https://www.newkerala.com/news/a/amit-shah-reviews-national-cybercrime-helpline-1930-calls-929.htm
- https://simple.wikipedia.org/wiki/1930_(Indian_Cybercrime_Helpline)
- https://www.newsonair.gov.in/over-rs-7000-crore-saved-through-citizen-financial-cyber-fraud-reporting-and-management-system
- https://the420.in/mumbai-1930-cyber-helpline-saves-202-crore-2025

Introduction
Recently the Indian Government banned the import of Laptops and tablets in India under the computers of HSN 8471. According to the notification of the government, Directorate General of foreign trade, there will be restrictions on the import of Laptops, tablets, and other electronic items from 1st November 2023. The government advised the Domestic companies to apply for the license within three months. As the process is simple, and many local companies have already applied for the license. The government will require a valid license for the import of laptops and other electronic items.
The Government imposed restrictions on the Import of Laptops & other electronic products
The DGFT (The directorate General of foreign trade) imposed restrictions on the import of electronic items in India. And, there has been the final date has also been given that the companies only have 3 months to apply for a valid license, from November 1st 2023there will be a requirement for a valid license for the import, and there will be a proper ban on the import of laptops & tablets, and other electronic items. The ban is on the HSN-8471. These are the products that indicate that they are taxable. It is a classification code to identify the taxable items. India has sufficient capacity and capability to manufacture their own IT hardware devices and boost production.
The government has notified production linked incentive, PLI Scheme 2.0, for the IT devices, which will soon be disclosed, and the scheme is expected to lead to a total of 29 thousand crore rupees worth of IT hardware nearly. And this will create future job opportunities in the five to six years.
The pros & cons of the import
Banning import has two sides. The positive one is that, it will promote the domestic manufacturers, local companies will able to grow, and there will be job opportunities, but if we talk about the negative side of the import, then the prices will be high for the consumers. One aspect is making India’s digital infrastructure stable, and the other side is affecting consumers.
Reasons Behind the ban on the Import of electronic items
There are the following reasons behind the ban on the Import of laptops and tablets,
- The primary reason why the government banned the import of laptops and other electronic items is because of security concerns about the data. And to prevent data theft a step has been taken by the Government.
- The banning will help the domestic manufacturer to grow and will provide opportunities to the local companies in India.
- It will help in the creation of Job vacancies in the country.
- There will be a curb down of selling of Chinese products.
The government will promote the digital infrastructure of India by putting a ban on imports. Such as there are domestic companies like Reliance recently launched a laptop by the name of Jio Book, and there is a company that sells the cheapest tablet called Aakash, so the import ban will promote these types of electronic items of the local companies. This step will soon result in digital advancement in India.
Conclusion
The laptop, tablets, and other electronic products that have been banned in India will make a substantial move with the implications. The objective of the ban is to encourage domestic manufacturing and to secure the data, however, it will also affect the consumers which can not be ignored. The other future effects are yet to be seen. But the one scenario is clear, that the policy will significantly make a change in India’s Technology industry.
