
#FactCheck - Fake Video Uses AI Voice to Falsely Attribute Remarks on Prasidh Krishna to Virat Kohli
A video circulating widely on social media claims that Indian cricketer Virat Kohli made a sarcastic remark about fast bowler Prasidh Krishna ahead of the New Zealand series. In the clip, Kohli is allegedly heard saying that he expected to be the top scorer of the series, but lost all hope after seeing Prasidh Krishna’s name in the squad.
Users sharing the video claim that Kohli publicly commented on Prasidh Krishna in this manner.
Research by the CyberPeace Foundation has found the viral claim to be false. Our probe revealed that the viral clip has been digitally manipulated. The video is originally from a 2024 advertisement featuring Virat Kohli, in which his voice has been altered using deepfake (AI-generated) technology and falsely presented with a misleading narrative.
Claim
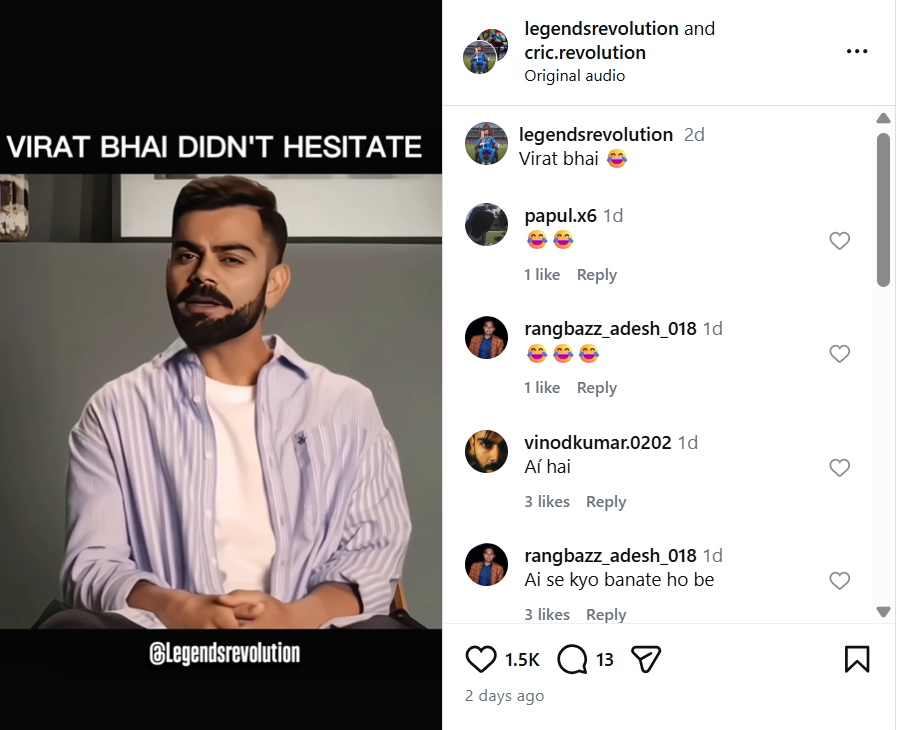
The video was shared on Instagram on January 6, 2025, with users claiming that Kohli made the remark after the New Zealand squad was announced. The post included the altered audio suggesting Kohli’s disappointment over Prasidh Krishna’s selection. Link, archive link
Fact Check:
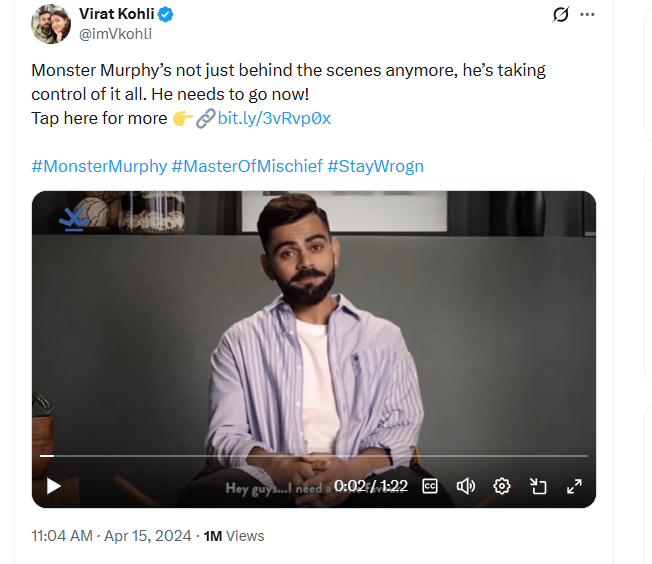
To verify the claim, we extracted key frames from the viral video and conducted a Google Reverse Image Search. This led us to the original video posted by Virat Kohli himself on X (formerly Twitter) on April 15, 2024. The original clip was part of a brand advertisement, and no such statement about the New Zealand series or Prasidh Krishna was made in it. Link and Screenshot
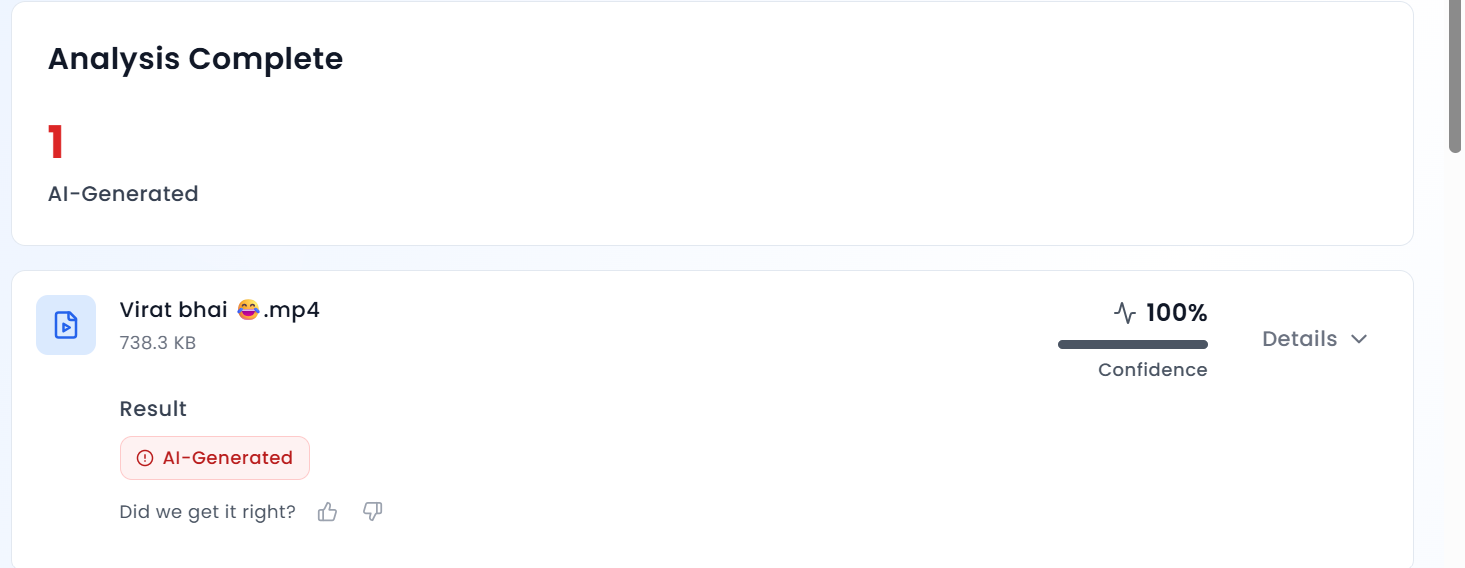
A close review of the viral clip raised suspicions due to the unnatural tone and inconsistencies in Kohli’s voice. To confirm this, we analysed the video using the AI detection tool Aurigin AI. The tool’s results showed that the audio in the viral clip is 100 percent AI-generated, confirming that Kohli’s voice was artificially manipulated.
Conclusion
The CyberPeace Foundation’s research confirms that the viral video claiming Virat Kohli mocked Prasidh Krishna is fake and misleading. The clip is taken from an old advertisement and has been doctored using deepfake technology to alter Kohli’s voice. The video is being circulated on social media with a false claim, and Virat Kohli has made no such statement regarding the New Zealand series or Prasidh Krishna.

Related Blogs

Recent Incidents:
Recent reports are revealing a significant security threat linked to a new infostealer based malware campaign known to solely target gaming accounts. This attack has affected users of Activision and other gaming websites. The sophisticated software has captured millions of login credentials, notably from the cheats and players. The officials at Activision Blizzard, an American video game holding company, are still investigating the matter and collaborating with cheated developers to minimize the impact and inform the accounts’ residents of appropriate safety measures.
Overview:
Infostealer, also known as information stealer, is a type of malware designed in the form of a Trojan virus for stealing private data from the infected system. It can have a variety of incarnations and collect user data of various types such as browser history, passwords, credit card numbers, and login details and credentials to social media, gaming platforms, bank accounts, and other websites. Bad actors use the log obtained as a result of the collection of personal records to access the victim’s financial accounts, appropriate the victim’s online identity, and perform fraudulent actions on behalf of the victim.
Modus Operandi:
- Infostealer is a malicious program created to illegally obtain people's login details, like usernames and passwords. Its goal is to enable cyberattacks, sell on dark web markets, or pursue malicious aims.
- This malware targets both personal devices and corporate systems. It spreads through methods like phishing emails, harmful websites, and infected public sites.
- Once inside a device, Infostealer secretly gathers sensitive data like passwords, account details, and personal information. It's designed to infiltrate systems being undetected. The stolen credentials are compiled into datalogs. These logs are then sold illegally on dark web marketplaces for profit.
Analysis:


Basic properties:
- MD5: 06f53d457c530635b34aef0f04c59c7d
- SHA-1: 7e30c3aee2e4398ddd860d962e787e1261be38fb
- SHA-256: aeecc65ac8f0f6e10e95a898b60b43bf6ba9e2c0f92161956b1725d68482721d
- Vhash: 145076655d155515755az4e?z4
- Authentihash: 65b5ecd5bca01a9a4bf60ea4b88727e9e0c16b502221d5565ae8113f9ad2f878
- Imphash: f4a69846ab44cc1bedeea23e3b680256
- Rich PE header hash: ba3da6e3c461234831bf6d4a6d8c8bff
- SSDEEP: 6144:YcdXHqXTdlR/YXA6eV3E9MsnhMuO7ZStApGJiZcX8aVEKn3js7/FQAMyzSzdyBk8:YIKXd/UgGXS5U+SzdjTnE3V
- TLSH:T1E1B4CF8E679653EAC472823DCC232595E364FB009267875AC25702D3EFBB3D56C29F90
- File type: Win32 DLL executable windows win32 pepe dll
- Magic: PE32+ executable (DLL) (GUI) x86-64, for MS Windows
- File size: 483.50 KB (495104 bytes)
Additional Hash Files:
- 160389696ed7f37f164f1947eda00830
- 229a758e232aeb49196c862655797e12
- 23e4ac5e7db3d5a898ea32d27e8b7661
- 3440cced6ec7ab38c6892a17fd368cf8
- 36d7da7306241979b17ca14a6c060b92
- 38d2264ff74123f3113f8617fabc49f6
- 3c5c693ba9b161fa1c1c67390ff22c96
- 3e0fe537124e6154233aec156652a675
- 4571090142554923f9a248cb9716a1ae
- 4e63f63074eb85e722b7795ec78aeaa3
- 63dd2d927adce034879b114d209b23de
- 642aa70b188eb7e76273130246419f1d
- 6ab9c636fb721e00b00098b476c49d19
- 71b4de8b5a1c5a973d8c23a20469d4ec
- 736ce04f4c8f92bda327c69bb55ed2fc
- 7acfddc5dfd745cc310e6919513a4158
- 7d96d4b8548693077f79bc18b0f9ef21
- 8737c4dc92bd72805b8eaf9f0ddcc696
- 9b9ff0d65523923a70acc5b24de1921f
- 9f7c1fffd565cb475bbe963aafab77ff
Indicators of Compromise:
- Unusual Outbound Network Traffic: An increase in odd or questionable outbound network traffic may be a sign that infostealer malware has accessed more data.
- Anomalies in Privileged User Account Activity: Unusual behavior or illegal access are two examples of irregular actions that might indicate a breach in privileged user accounts.
- Suspicious Registry or System File Changes: Infostealer malware may be trying to alter system settings if there are any unexpected changes to system files, registry settings, or configurations.
- Unusual DNS queries: When communicating with command and control servers or rerouting traffic, infostealer malware may produce strange DNS queries.
- Unexpected System Patching: Unexpected or unauthorized system patching by unidentified parties may indicate that infostealer malware has compromised the system and is trying to hide its footprint or become persistent.
- Phishing emails and social engineering attempts: It is a popular strategy employed by cybercriminals to get confidential data or implant malicious software. To avoid compromise, it is crucial to be wary of dubious communications and attempts of social engineering.
Recommendations:
- Be Vigilant: In today's digital world, many cybercrimes threaten online safety, Phishing tricks, fake web pages, and bad links pose real dangers. Carefully check email sources. Examine websites closely. Use top security programs. Follow safe browsing rules. Update software often. Share safety tips. These steps reduce risks. They help keep your online presence secure.
- Regular use of Anti-Virus Software to detect the threats: Antivirus tools are vital for finding and stopping cyber threats. These programs use signature detection and behavior analysis to identify known malicious code and suspicious activities. Updating virus definitions and software-patches regularly, improves their ability to detect new threats. This helps maintain system security and data integrity.
- Provide security related training to the employees and common employees: One should learn Cybersecurity and the best practices in order to keep the office safe. Common workers will get lessons on spotting risks and responding well, creating an environment of caution.
- Keep changing passwords: Passwords should be changed frequently for better security. Rotating passwords often makes it harder for cyber criminals to compromise and make it happen or confidential data to be stolen. This practice keeps intruders out and shields sensitive intel.
Conclusion:
To conclude, to reduce the impact and including the safety measures, further investigations and collaboration are already in the pipeline regarding the recent malicious software that takes advantage of gamers and has stated that about millions of credentials users have been compromised. To protect sensitive data, continued usage of antivirus software, use of trusted materials and password changes are the key elements. The ways to decrease risks and safely protect sensitive information are to develop improved Cybersecurity methods such as multi-factor authentication and the conduct of security audits frequently. Be safe and be vigilant.
Reference:
- https://techcrunch.com/2024/03/28/activision-says-its-investigating-password-stealing-malware-targeting-game-players/
- https://www.bleepingcomputer.com/news/security/activision-enable-2fa-to-secure-accounts-recently-stolen-by-malware/
- https://cyber.vumetric.com/security-news/2024/03/29/activision-enable-2fa-to-secure-accounts-recently-stolen-by-malware/
- https://www.virustotal.com/
- https://otx.alienvault.com/

Introduction
In today’s cybersecurity landscape, ransomware has emerged as one of the most significant and rapidly growing cyber threats. What began as attacks carried out by individual hackers has evolved into a highly organised criminal enterprise, with groups operating through structured business models and global networks. The emergence of The Gentlemen ransomware group reflects this transformation, demonstrating how modern threat actors can quickly expand their operations and target organisations across multiple sectors. Their rise highlights the increasing sophistication of ransomware campaigns and the growing challenges faced by organisations in defending against them. The attribution of the group's administrator to an identified individual in Izhevsk, Russia, provides a valuable lens through which to examine three interconnected developments: the maturation of ransomware-as-a-service (RaaS) business models, the inherent operational security (OPSEC) weaknesses that emerge over the course of cybercriminal careers, and the geopolitical environments that enable such actors to operate with relative impunity. Together, these dynamics illustrate the industrialisation of modern cybercrime.
The Industrialisation of Ransomware-as-a-Service
The remarkable rapid rise of The Gentlemen is impossible without discussing the maturation of ransomware-as-a-service (RaaS). RaaS systems utilize network intrusion experts as affiliates who conduct networks intrusions and secure access in exchange for a cut of the total ransoms paid, while a core group builds and maintains the ransomware framework itself. Although Reveton, one of the earliest Raas providers, can be credited with bringing early iterations of RaaS to fruition in 2012, the potential scale was truly evident in the mid-2020s. By 2025 it was estimated that there were over 100 active ransomware gangs operating; this proliferation is the direct result of the franchise-like system, which has lowered the barriers to entry for cybercrime.
The marketplace surrounding RaaS is intensely competitive, and this is clearly exemplified in the business structure of The Gentlemen: while many of the top ransomware groups provide an 80/20 profit share (with the majority of the profit going to the affiliates), The Gentlemen has an exceptionally profitable 90/10 split (affiliates keep 90% of the profit share) for affiliates, likely to draw experienced operators away from their rivals given recent decreases in victim willingness to pay and corresponding increases in the incentives RaaS platforms are required to offer.
The operational efficiency of the group is representative of a successful enterprise. They attack vulnerable internet-facing VPNs and firewalls and generally complete the network encryption within a matter of hours, leaving defenders with very little time to respond, as confirmed by Check Point Software, a renowned cybersecurity vendor.
Additionally, PRODAFT reports that the administrator of The Gentlemen, known by the alias Zeta88 (previously known as Hastalamuerte), directly provides affiliates with SSL VPN credentials, often obtained through brutal force attacks or their own private leaked databases, indicating an unusually high level of vertical integration for RaaS groups.
AI as a Force Multiplier in Ransomware Development
A particularly significant aspect of the Hastalamuerte case is PRODAFT's finding that the administrator employs artificial intelligence to develop and maintain ransomware, support associated tooling, and assist post-exploitation operations. This reflects a broader trend observed across the 2025–2026 threat landscape, where AI has increasingly lowered the capability threshold for participation in organised cybercrime. Researchers have documented its role in automating stages of intrusion, accelerating malware development cycles, and simplifying the maintenance of malicious infrastructure. These capabilities have been leveraged by both nation-state actors and criminal enterprises.
The trajectory of Hastalamuerte is especially illustrative. Cybersecurity Forum posts during 2019-2020 depict a hacker who is fairly novice at fundamental penetration testing procedures. A subsequent emergence as the operator of a top-tier ransomware-as-a-service operation indicates that AI-assisted development may be responsible for dramatically reducing the skill level and time necessary to create a successful criminal enterprise in cyberspace. The evolution of these tools should make the route from novice forum user to accomplished ransomware operator more attainable for a wider array of perpetrators in the future.
The OPSEC Paradox: How Cybercriminals Leave a Trail
The attribution of Hastalamuerte's identity by researchers from Intel 471, Flashpoint, and Constella Intelligence demonstrates the effectiveness of modern open-source and commercial intelligence methodologies. A forum registration traceable to an IP address from Izhevsk, Russia linked a Protonmail address, which linked to an Apple account, a GitHub profile, a Telegram handle, a Russian phone number, and finally to a 36 year old marketing professional named Alexander Andreevich Yapaev who was also living in Izhevsk. Investigators did not use an advanced capability in their attribution, but rather a simple OPSEC mistake of consistently reusing credentials. Every username and email address and every phone number creates a linkage between disparate data points, eventually building into a real-world persona.
It has also come out in the forum discussion that while training for a penetration testing course in 2020, Hastalamuerte displayed the kind of inexperience that a novice would display in traceable, recorded fashion to intelligence databases. It's an example of a broader rule about attribution; attacker mistakes provide the most value. With Russians the lack of apparent consequences may contribute to a lack of need to maintain tight OPSEC from the start.
The Russian Safe Haven: Conditional Impunity and Its Limits
Yapaev's base in Izhevsk is emblematic of the geostrategic situation that has allowed Russian cybercriminality to prosper. Security researchers routinely label Russia's policy as one of "controlled impunity," where the cybercriminality directed at foreign entities is ignored or implicitly condoned, while that directed at Russian interests will prompt a law enforcement response. This constitutes what has been called a "managed market" rather than an "unconditional sanctuary," where many of the named defendants could and likely will continue their illegal enterprise with little fear of reprisal, provided that they do not threaten the interests of the Russian state and do not attempt to move their operations outside of Russian control.
Yet this protection is neither absolute nor permanent. In May 2024, the transnational Operation Endgame campaign highlighted the growing global appetite for damaging the cybercrime ecosystem rooted in Russia. Russian authorities did indeed pursue and seize some assets and operators, but arrests seem largely confined to the lower-rung facilitators of these attacks (hosting providers and payment services), and it seems higher-end ransomware operators continue to evade scrutiny. Selective enforcement thus further bolsters the perception that protection is accorded according to strategic value, not legal standards. For operators such as Hastalamuerte, who possess no publicly documented intelligence connections, growing attribution capabilities, and sustained international pressure may gradually erode the security traditionally associated with operating from within Russia.
Attribution as a Deterrence Instrument
The public identification of Alexander Andreevich Yapaev as Hastalamuerte/Zeta88 shows the continued struggle with the utility of attribution in situations where immediate prosecution is not feasible. Its utility is far more extensive than simply an ability to make an arrest. Functionally, public naming forces a perpetrator into an open evidentiary space and can lead to alterations in their operational habits and effectiveness. Strategically, attribution provides future leverage for sanctions, indictments, financial restrictions, or extradition if the target can leave their safe haven country. The logic behind US rewards programs (paying up to $10 million for the capture and conviction of ransomware operators) relies on this principle. The analytical insight provided by the case cannot be understated either. Hastalamuerte's trajectory from a relative amateur forum participant on Nulled and Raidforums in 2019 to leading a significant ransomware operation by 2026 offers an invaluable look into the career progression of a cyber criminal. It confirms one of the lessons learned through deterrence and attribution: pseudonymity is not everlasting, and many years of OPSEC failures can be pieced together to establish a real-world identity.
Conclusion
The Gentlemen incident is emblematic of the three broad themes that currently characterise cyber warfare: ransomware-as-a-service through innovative competition, common OPSEC failures that enable attribution, and a new, conditional regime of protection for Russian cybercriminals. The obvious defense lesson: increasing attack surfaces require stronger identity, behavioural monitoring, and intelligence capacities. The policy lesson: effective attribution is still an essential tool for comprehension, deterrence, and disruption in an increasingly industrialised environment of criminals supporting each other's operations in ransomware-as-a-service.
References
- https://krebsonsecurity.com/2026/06/who-runs-the-ransomware-group-the-gentlemen/
- https://www.recordedfuture.com/
- https://www.vectra.ai/topics/ransomware-as-a-service
- https://www.trmlabs.com/es/resources/blog/new-disruption-opportunities-in-the-evolving-ransomware-ecosystem

Introduction
A 33-year-old MBA graduate and 36-year-old software engineer set up the cybercrime hub in one bedroom. They formed the nameless private enterprise two years ago and hired the two youngsters as employees. The police revealed that the fraudsters moved Rs 854 crore rapidly through 84 bank accounts in the last two years. They were using eight mobile phones active during the day and night for their malicious operations. This bad actors group came in the eyes of the police when a 26-year-old woman filed a complaint, she was lured and cheated for Rs 8.5 lakh on the pretext of making small investments for high returns. It led to cyber crime police on their doorstep. The police discovered that they were operating a massive cyber fraud network from that single room, targeting a large number of people for committing cyber fraud through offering investment schemes and luring innocent people.
How cybercrime fraudsters lured the victims?
The Bangalore police have busted a cyber fraud scam worth 854 Crore rupees. And police have arrested 6 accused. These bad actors illegally deceived numerous victims on the pretext of investment schemes. The gang used to lure them through WhatsApp and Telegram. Initially, the people were asked to invest small amounts, promising daily profits ranging from 1 thousand to 5 thousand rupees. As the trust grew, thousands of victims indulged in investments ranging from 1 lack to 10 lack rupees. This Money luring modus operandi was used by the fraudsters to attract them and get the victims to invest more and more. The amount invested by the victims was deposited into various bank accounts by the fraudsters. When the victims tried to withdraw their amount after depositing they were unable to do so. Soon after the amount was received, the accused gang would launder the money and divert it to other accounts.
Be cautious of online investment fraud
It concerns all of us who used to invest online. The Bangalore police have busted cyber crime or cyber investment fraud of 854 crore rupees. The 6 members of the gang that the police have arrested used to approach victims through WhatsApp and telegram to convince them to invest small amounts, from 1 thousand to 10 thousand at the bare minimum and promising them returns or profit amount per day and later lock this amount and diverting it into different bank accounts, ensuring that those get invested never get access to it again. Now, this went on in the country receiving a large number of cases that have been registered from various states in the country.
Advisory and best practices
- It is important to mention that there could be several other cybercrime investment frauds like this that you may not even be aware of. Hence, this incident of massive online investment fraud operated from the IT capital of the country definitely acts as an eye-opener for all of us. We urge people to be cautious and raise the alarm about any such cyber crime or investment fraud that they see in the cyber world today.
- In the age of the internet, where there is a large number of mobile users in the country, and users look for a source of income on the internet and use it to invest their money, it is important to be aware of such fraud and be cautious and take proper precautions before investing in any such online scheme. It is always advisable to invest only in legitimate sources and after conducting due diligence.
- Be cautious and do your research: Whenever you are investing in any scheme or in digital currency, make sure to verify the authenticity or legitimacy of the person or company who is offering such service. Check the reviews, official website, and feedback from authentic sources. Find out whether the agents or brokers who contact you are licensed to operate in your state and are compliant with regulators or other investors.
- Verify the credentials: Check the genuineness by checking the licenses, registration and certification of the person or company offering such services, whether he is authorised or not.
- Be Skeptical of offers which seem to be too good: If it sounds too good, be cautious and inquire about its authenticity, such as unsolicited offers. Be especially careful if you receive an unsolicited pitch to invest in a particular company or see it praised online but if you could not find current financial information about it from independent sources. It could be a fraudulent scheme. It is advisable to compare promised yields with current returns on well-known stock indexes.
- Seek Expert Advice: If you are a beginner in online investment, you may seek advice from reliable resources such as financial advisors who can provide more clarity on aspects of investment and guidance to help you make informed decisions.
- Avoid Unreliable Platforms: Be cautious and stick to authorised established agencies. Be cautious when dealing with a person or company lacking sufficient user reviews and credible security measures.
- Protect yourself online: Protect yourself online. Fraudsters target users on online and social marketing sites and commit various online frauds; hence, it's important to be cautious and protect yourself online. So be cautious and make your own sound decision after all analysis while investing in any such services.
- Report Suspicious Accounts: If you encounter any social media accounts, social media groups or profiles which seem suspicious and engaged in fraudulent services, you must report such profiles to the respective platform immediately.
- Report cyber crimes to law enforcement agencies: A powerful resource available to victims of cybercrime is the National Cyber Crime Reporting Portal, equipped with a 24x7 helpline number, 1930. This portal serves as a centralised platform for reporting cybercrimes, including financial fraud.
Conclusion:
This recent cyber investment fraud worth Rs 854 Crore, orchestrated by a group of fraudsters operating from a single room, serves as a stark reminder of the risks posed by bad actors. This incident underscores the importance of being vigilant when it comes to online investments and financial transactions. As we navigate the vast and interconnected landscape of the internet, it is imperative that we exercise due diligence and employ best practices to protect ourselves. We need to be cautious and protected from falling victim to these fraudulent schemes, actively reporting suspicious accounts and cybercrimes to relevant authorities through resources like the National Cyber Crime Reporting Portal will contribute to helping stop these types of cyber crimes. Knowledge and awareness are some of the biggest factors we have in fighting back against such cyber frauds in this digital age and making a safer digital environment for everyone.
References
- https://www.news18.com/india/bengaluru-cyber-crime-rs-854-crore-84-banks-accounts-fraud-network-one-bedroom-house-yelahanka-karnataka-8618426.html
- https://indianexpress.com/article/cities/bangalore/cyber-crime-bengaluru-links-over-5000-cases-india-8982753/lite/
