
#FactCheck - Viral Video Falsely Linked to Netanyahu’s Brother’s Death, Old Funeral Clip Misused
Executive Summary:
A video is going viral on social media claiming to show family members mourning the death of Iddo Netanyahu, brother of Israeli Prime Minister Benjamin Netanyahu. However, an research by the CyberPeace found that the claim being shared with the video is false. The video has been available on the internet since 2024. According to available information, it shows the funeral of an Israeli soldier who was killed in an attack in the Jabalia area of northern Gaza.Moreover, no credible news reports were found confirming the death of Iddo Netanyahu.
Claim:
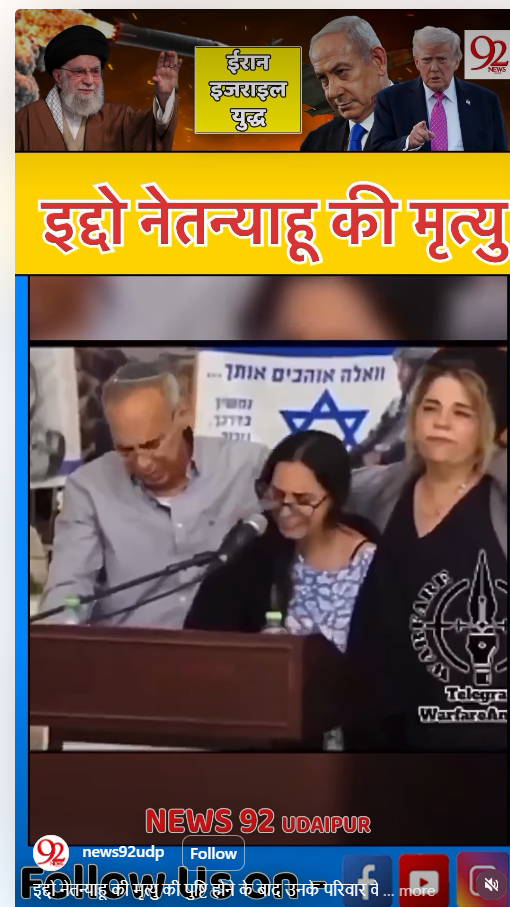
An Instagram user shared the viral video with an English caption stating, “Family members are crying after the death of Iddo Netanyahu was confirmed.”
Fact Check:
During the investigation, we found the original video on an X (formerly Twitter) account named Warfare Analysis. The video was posted on October 12, 2024, confirming that it predates the recent Iran-Israel conflict. Notably, the “Warfare Analysis” logo is also visible in the viral video. According to the caption, the footage shows the funeral of Israeli soldier Netanel Hershkovit, who was killed on October 11, 2024, in an attack by Al-Qassam in Jabalia, northern Gaza.
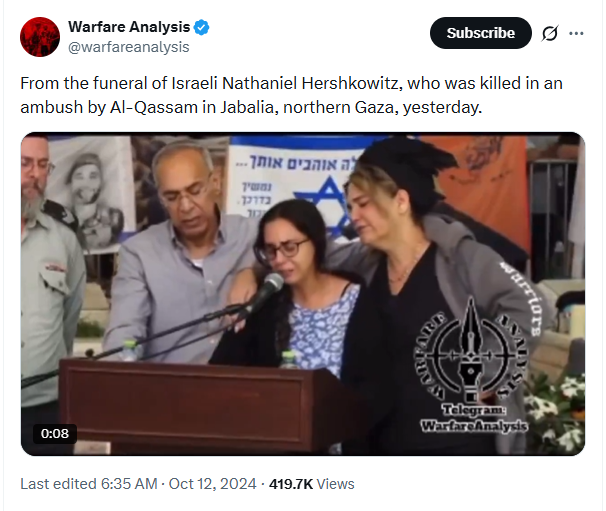
A report published by VIN News on October 12, 2024, also covered the funeral of Netanel Hershkovit and included statements from his family members.
Conclusion:
Our research found that the claim shared with the video is false. The video has been online since 2024 and shows the funeral of an Israeli soldier killed in northern Gaza. Additionally, no credible reports confirm the death of Iddo Netanyahu.

Related Blogs

Introduction
As India moves full steam ahead towards a trillion-dollar digital economy, how user data is gathered, processed and safeguarded is under the spotlight. One of the most pervasive but least known technologies used to gather user data is the cookie. Cookies are inserted into every website and application to improve functionality, measure usage and customize content. But they also present enormous privacy threats, particularly when used without explicit user approval.
In 2023, India passed the Digital Personal Data Protection Act (DPDP) to give strong legal protection to data privacy. Though the act does not refer to cookies by name, its language leaves no doubt as to the inclusion of any technology that gathers or processes personal information and thus cookies regulation is at the centre of digital compliance in India. This blog covers what cookies are, how international legislation, such as the GDPR, has addressed them and how India's DPDP will regulate their use.
What Are Cookies and Why Do They Matter?
Cookies are simply small pieces of data that a website stores in the browser. They were originally designed to help websites remember useful information about users, such as your login session or what is in your shopping cart. Netscape initially built them in 1994 to make web surfing more efficient.
Cookies exist in various types. Session cookies are volatile and are deleted when the browser is shut down, whereas persistent cookies are stored on the device to monitor users over a period of time. First-party cookies are made by the site one is visiting, while third-party cookies are from other domains, usually utilised for advertisements or analytics. Special cookies, such as secure cookies, zombie cookies and tracking cookies, differ in intent and danger. They gather information such as IP addresses, device IDs and browsing history information associated with a person, thus making it personal data per the majority of data protection regulations.
A Brief Overview of the GDPR and Cookie Policy
The GDPR regulates how personal data can be processed in general. However, if a cookie collects personal data (like IP addresses or identifiers that can track a person), then GDPR applies as well, because it sets the rules on how that personal data may be processed, what lawful bases are required, and what rights the user has.
The ePrivacy Directive (also called the “Cookie Law”) specifically regulates how cookies and similar technologies can be used. Article 5(3) of the ePrivacy Directive says that storing or accessing information (such as cookies) on a user’s device requires prior, informed consent, unless the cookie is strictly necessary for providing the service requested by the user.
In the seminal Planet49 decision, the Court of Justice of the European Union held that pre-ticked boxes do not represent valid consent. Another prominent enforcement saw Amazon fined €35 million by France's CNIL for using tracking cookies without user consent.
Cookies and India’s Digital Personal Data Protection Act (DPDP), 2023
India's Digital Personal Data Protection Act, 2023 does not refer to cookies specifically but its provisions necessarily come into play when cookies harvest personal data like user activity, IP addresses, or device data. According to DPDP, personal data is to be processed for legitimate purposes with the individual's consent. The consent has to be free, informed, clear and unambiguous. The individuals have to be informed of what data is collected, how it will be processed.. The Act also forbids behavioural monitoring and targeted advertising in the case of children.
The Ministry of Electronics and IT released the Business Requirements Document for Consent Management Systems (BRDCMS) in June 2025. Although it is not binding by law, it provides operational advice on cookie consent. It recommends that websites use cookie banners with "Accept," "Reject," and "Customize" choices. Users must be able to withdraw or change their consent at any moment. Multi-language handling and automatic expiry of cookie preferences are also suggested to suit accessibility and privacy requirements.
The DPDP Act and the BRDCMS together create a robust user-rights model, even in the absence of a special cookie law.
What Should Indian Websites Do?
For the purposes of staying compliant, Indian websites and online platforms need to act promptly to harmonise their use of cookies with DPDP principles. This begins with a transparent and simple cookie banner providing users with an opportunity to accept or decline non-essential cookies. Consent needs to be meaningful; coercive tactics such as cookie walls must not be employed. Websites need to classify cookies (e.g., necessary, analytics and ads) and describe each category's function in plain terms under the privacy policy. Users must be given the option to modify cookie settings anytime using a Consent Management Platform (CMP). Monitoring children or their behavioural information must be strictly off-limits.
These are not only about being compliant with the law, they're about adhering to ethical data stewardship and user trust building.
What Should Users Do?
Cookies need to be understood and controlled by users to maintain online personal privacy. Begin by reading cookie notices thoroughly and declining unnecessary cookies, particularly those associated with tracking or advertising. The majority of browsers today support blocking third-party cookies altogether or deleting them periodically.
It is also recommended to check and modify privacy settings on websites and mobile applications. It is possible to minimise surveillance with the use of browser add-ons such as ad blockers or privacy extensions. Users are also recommended not to blindly accept "accept all" in cookie notices and instead choose "customise" or "reject" where not necessary for their use.
Finally, keeping abreast of data rights under Indian law, such as the right to withdraw consent or to have data deleted, will enable people to reclaim control over their online presence.
Conclusion
Cookies are a fundamental component of the modern web, but they raise significant concerns about individual privacy. India's DPDP Act, 2023, though not explicitly referring to cookies, contains an effective legal framework that regulates any data collection activity involving personal data, including those facilitated by cookies.
As India continues to make progress towards comprehensive rulemaking and regulation, companies need to implement privacy-first practices today. And so must the users, in an active role in their own digital lives. Collectively, compliance, transparency and awareness can build a more secure and ethical internet ecosystem where privacy is prioritised by design.
References
- https://prsindia.org/billtrack/digital-personal-data-protection-bill-2023
- https://gdpr-info.eu/
- https://d38ibwa0xdgwxx.cloudfront.net/create-edition/7c2e2271-6ddd-4161-a46c-c53b8609c09d.pdf
- https://oag.ca.gov/privacy/ccpa
- https://www.barandbench.com/columns/cookie-management-under-the-digital-personal-data-protection-act-2023#:~:text=The%20Business%20Requirements%20Document%20for,the%20DPDP%20Act%20and%20Rules.
- https://samistilegal.in/cookies-meaning-legal-regulations-and-implications/#
- https://secureprivacy.ai/blog/india-digital-personal-data-protection-act-dpdpa-cookie-consent-requirements
- https://law.asia/cookie-use-india/
- https://www.cookielawinfo.com/major-gdpr-fines-2020-2021/#:~:text=4.,French%20websites%20could%20refuse%20cookies.
Introduction
In today’s digital era, warfare is being redefined. Defence Minister Rajnath Singh recently stated that “we are in the age of Grey Zone and hybrid warfare where cyber-attacks, disinformation campaigns and economic warfare have become tools to achieve politico-military aims without a single shot being fired.” The crippling cyberattacks on Estonia in 2007, Russia’s interference in the 2016 US elections, and the ransomware strike on the Colonial Pipeline in the United States in 2021 all demonstrate how states are now using cyberspace to achieve strategic goals while carefully circumventing the threshold of open war.
Legal Complexities: Attribution, Response, and Accountability
Grey zone warfare challenges the traditional notions of security and international conventions on peace due to inherent challenges such as :
- Attribution
The first challenge in cyber warfare is determining who is responsible. Threat actors hide behind rented botnets, fake IP addresses, and servers scattered across the globe. Investigators can follow digital trails, but those trails often point to machines, not people. That makes attribution more of an educated guess than a certainty. A wrong guess could lead to misattribution of blame, which could beget a diplomatic crisis, or worse, a military one. - Proportional Response
Even if attribution is clear, designing a response can be a challenge. International law does give room for countermeasures if they are both ‘necessary’ and ‘proportionate’. But defining these qualifiers can be a long-drawn, contested process. Effectively, governments employ softer measures such as protests or sanctions, tighten their cyber defences or, in extreme cases, strike back digitally. - Accountability
States can be held responsible for waging cyber attacks under the UN’s Draft Articles on State Responsibility. But these are non-binding and enforcement depends on collective pressure, which can be slow and inconsistent. In cyberspace, accountability often ends up being more symbolic than real, leaving plenty of room for repeat offences.
International and Indian Legal Frameworks
Cyber law is a step behind cyber warfare since existing international frameworks are often inadequate. For example, the Tallinn Manual 2.0, the closest thing we have to a rulebook for cyber conflict, is just a set of guidelines. It says that if a cyber operation can be tied to a state, even through hired hackers or proxies, then that state can be held responsible. But attribution is a major challenge. Similarly, the United Nations has tried to build order through its Group of Governmental Experts (GGE) that promotes norms like “don’t attack. However, these norms are not binding, effectively leaving practice to diplomacy and trust.
India is susceptible to routine attacks from hostile actors, but does not yet have a dedicated cyber warfare law. While Section 66F of the IT ACT, 2000, talks about cyber terrorism, and Section 75 lets Indian courts examine crimes committed abroad if they impact India, grey-zone tactics like fake news campaigns, election meddling, and influence operations fall into a legal vacuum.
Way Forward
- Strengthen International Cooperation
Frameworks like the Tallinn Manual 2.0 can form the basis for future treaties. Bilateral and multilateral agreements between countries are essential to ensure accountability and cooperation in tackling grey zone activities. - Develop Grey Zone Legislation
India currently relies on the IT Act, 2000, but this law needs expansion to specifically cover grey zone tactics such as election interference, propaganda, and large-scale disinformation campaigns. - Establish Active Monitoring Systems
India must create robust early detection systems to identify grey zone operations in cyberspace. Agencies can coordinate with social media platforms like Instagram, Facebook, X (Twitter), and YouTube, which are often exploited for propaganda and disinformation, to improve monitoring frameworks. - Dedicated Theatre Commands for Cyber Operations
Along with the existing Defence Cyber Agency, India should consider specialised theatre commands for grey zone and cyber warfare. This would optimise resources, enhance coordination, and ensure unified command in dealing with hybrid threats.
Conclusion
Grey zone warfare in cyberspace is no longer an optional tactic used by threat actors but a routine activity. India lacks the early detection systems, robust infrastructure, and strong cyber laws to counter grey-zone warfare. To counter this, India needs sharper attribution tools for early detection and must actively push for stronger international rules in this global landscape. More importantly, instead of merely blaming without clear plans, India should focus on preparing for solid retaliation strategies. By doing so, India can also learn to use cyberspace strategically to achieve politico-military aims without firing a single shot.
References
- Tallinn Manual 2.0 on the International Law Applicable to Cyber Operations (Michael N. Schmitt)
- UN Document on International Law in Cyberspace (UN Digital Library)
- NATO Cyber Defence Policy
- Texas Law Review: State Responsibility and Attribution of Cyber Intrusions
- Deccan Herald: Defence Minister on Grey Zone Warfare
- VisionIAS: Grey Zone Warfare
- Sachin Tiwari, The Reality of Cyber Operations in the Grey Zone
Perth, Western Australia — For most of the past year, the name TeamPCP has circulated quietly within cybersecurity circles as shorthand for a particular kind of dread: not the dread of a phishing email or a suspicious link, but the dread of software you already trusted turning against you. This week, that quiet circulation became public record. The Australian Federal Police, working alongside the FBI and the Western Australia Police Force, arrested and charged two Western Australian men, aged 21 and 23, with a combined 14 offences over their alleged role in the group.
The arrests themselves are notable. The story behind them is more so.
A Campaign Built on Borrowed Trust
TeamPCP's alleged method was not to break down the front door. It was to compromise the door itself, the trusted mechanisms by which developers pull code into their own projects every day. The group has been linked to widespread supply-chain attacks that targeted open-source software and developer platforms to steal credentials, authentication secrets, and source code, with high-profile incidents affecting projects including Trivy, LiteLLM, Telnyx, SAP, and TanStack, alongside breaches at organisations such as the European Commission, Mistral AI, OpenAI, and GitHub. Reporting has also linked the campaign to ecosystems including GitHub Actions, Docker Hub, npm, PyPI and OpenVSX, the invisible plumbing through which most modern software is assembled.
The scale, as alleged by investigators, is difficult to overstate. Authorities say the malicious code potentially compromised over a thousand organisations worldwide, enabling the theft of roughly half a million credentials and the exfiltration of at least 300GB of data, figures that should be understood as allegations under active investigation rather than an independently verified victim count. The AFP itself has said the compromise of a small number of trusted software components had a significant global impact, with remediation costs estimated in the hundreds of millions of dollars.
Why This Attack Was So Hard to See Coming
The mechanics matter. Rather than tricking a user into clicking something malicious, the alleged operation worked by compromising the credentials developers use to publish legitimate software updates, then pushing tampered versions out through the same trusted distribution pipelines millions of applications rely on automatically. There is no obviously suspicious file, no rogue website, only a routine update, arriving exactly where it was expected.
Investigators also describe a cascading structure to the intrusions: credentials harvested from one compromised project reportedly opened the door to the next, turning isolated breaches into a chain reaction across the open-source ecosystem. TeamPCP has been described as running one of the most consequential campaigns of software supply-chain attacks investigators have tracked, and the group's reach extended notably into the AI stack — LiteLLM, one of the projects reportedly compromised, is an open-source gateway widely used to connect applications to large language model providers, meaning the attack's blast radius extended into the very infrastructure powering today's AI boom.
The Investigation and the Charges
The two men were charged following a joint investigation by the AFP and WAPF, working in parallel with the FBI, into what authorities describe as a sophisticated cybercrime syndicate accused of creating malicious open-source software to defraud thousands of global businesses. The charges span identity theft, unauthorised data modification, and money laundering, with maximum penalties ranging from three to twenty years' imprisonment. Search warrants were executed in Perth on 26 August 2026, and investigators seized electronic devices for forensic analysis after raids at properties in Cottesloe, Hamilton Hill, and Mandurah. FBI Cyber Division Assistant Director Brett Leatherman noted the significance of the international cooperation involved in the case, while investigators have not ruled out further arrests.
The Real Story: A Governance Problem, Not Just a Crime Story
It would be easy to file this under "hackers caught" and move on. But the more consequential story is structural. Modern organisations do not merely secure their own infrastructure, they inherit risk from every library, package, CI/CD pipeline, repository, vendor and developer tool they depend on, often without ever auditing that dependency chain directly. Guidance from the U.S. Cybersecurity and Infrastructure Security Agency (CISA) on securing open-source software has increasingly emphasised managing these dependencies through software bills of materials (SBOMs), precisely because so few organisations can otherwise answer a basic question: what, exactly, is running inside our systems?
TeamPCP's alleged campaign is a case study in why that question can no longer be optional. If an organisation's security posture is only as strong as the thousands of components it silently trusts, then supply-chain security is not a developer problem to be quietly patched — it is a governance issue, deserving board-level attention, vendor accountability frameworks, and mandatory disclosure practices.
CyberPeace's Take
At CyberPeace, we've been watching campaigns like TeamPCP's less as isolated incidents and more as a pattern that keeps repeating with higher stakes each time. What stands out to our team isn't the sophistication of the code, open-source poisoning is, frankly, not a new technique, it's the sophistication of patience. Compromising a maintainer's publishing credentials and simply waiting for the next scheduled release to carry the payload downstream is a strategy built for an ecosystem that still largely operates on implicit trust rather than continuous verification. That gap between how fast software moves and how slowly trust is actually checked is precisely where operations like this thrive.
We'd also push back gently on treating this as a "developer hygiene" story. Most engineering teams pulling in a package from npm or PyPI are not, and should not be expected to be, forensically auditing every dependency update by hand, that isn't scalable, and it was never a realistic line of defence. The actual fix has to sit further upstream: provenance verification baked into CI/CD pipelines, signed commits and releases treated as non-negotiable rather than optional, and SBOMs that are actually queried during incident response rather than generated once and filed away.
Our broader concern, honestly, is about incentive alignment. Open-source maintainers are frequently unpaid or under-resourced volunteers holding publishing keys to software depended on by billion-dollar enterprises. Until organisations that consume open-source software at scale start meaningfully funding its security, not just its development, this pattern isn't going away. It will simply find its next entry point.
References
- Australian Federal Police. Two WA men charged following AFP-FBI-WAPF disruption of alleged global cybercrime syndicate. afp.gov.au
- Bleeping Computer. Australia arrests alleged TeamPCP hackers behind supply-chain attacks. bleepingcomputer.com
- CyberScoop. Two alleged TeamPCP members arrested and charged after months of software supply-chain chaos. cyberscoop.com
- Cyber Daily. Busted! Alleged Aussie hackers linked to TeamPCP arrested in joint AFP-FBI-WAPF operation. cyberdaily.au
- Help Net Security. Two alleged TeamPCP hackers arrested over global supply chain attacks. helpnetsecurity.com
- Krebs on Security. Two Alleged 'TeamPCP' Hackers Arrested in Australia. krebsonsecurity.com
- TechCrunch. Australian police arrest two over TeamPCP hacks targeting Mercor, OpenAI, and others. techcrunch.com
- The Hacker News. Alleged TeamPCP Hackers Charged in Australia Over Major Supply Chain Attacks. thehackernews.com
