
#FactCheck - Viral image claiming to show injury marks of the MP Kangana Ranaut slapped is fake & misleading
Executive Summary:
The viral image in the social media which depicts fake injuries on the face of the MP(Member of Parliament, Lok Sabha) Kangana Ranaut alleged to have been beaten by a CISF officer at the Chandigarh airport. The reverse search of the viral image taken back to 2006, was part of an anti-mosquito commercial and does not feature the MP, Kangana Ranaut. The findings contradict the claim that the photos are evidence of injuries resulting from the incident involving the MP, Kangana Ranaut. It is always important to verify the truthfulness of visual content before sharing it, to prevent misinformation.

Claims:
The images circulating on social media platforms claiming the injuries on the MP, Kangana Ranaut’s face were because of an assault incident by a female CISF officer at Chandigarh airport. This claim hinted that the photos are evidence of the physical quarrel and resulting injuries suffered by the MP, Kangana Ranaut.


Fact Check:
When we received the posts, we reverse-searched the image and found another photo that looked similar to the viral one. We could verify through the earring in the viral image with the new image.

The reverse image search revealed that the photo was originally uploaded in 2006 and is unrelated to the MP, Kangana Ranaut. It depicts a model in an advertisement for an anti-mosquito spray campaign.
We can validate this from the earrings in the photo after the comparison between the two photos.

Hence, we can confirm that the viral image of the injury mark of the MP, Kangana Ranaut has been debunked as fake and misleading, instead it has been cropped out from the original photo to misrepresent the context.
Conclusion:
Therefore, the viral photos on social media which claimed to be the results of injuries on the MP, Kangana Ranaut’s face after being assaulted allegedly by a CISF officer at the airport in Chandigarh were fake. Detailed analysis of the pictures provided the fact that the pictures have no connection with Ranaut; the picture was a 2006 anti-mosquito spray advertisement; therefore, the allegations that show these images as that of Ranaut’s injury are fake and misleading.
- Claim: photos circulating on social media claiming to show injuries on the MP, Kangana Ranaut's face following an assault incident by a female CISF officer at Chandigarh airport.
- Claimed on: X (Formerly known as Twitter), thread, Facebook
- Fact Check: Fake & Misleading

Related Blogs
Executive Summary
A video is being widely shared on social media, claiming it shows a terrifying scene from a recent earthquake in Venezuela. The 9-second clip shows a multi-storey building collapsing like a house of cards, while people nearby are seen running in panic as chaos unfolds. The video is being widely circulated by users as evidence of massive destruction caused by the alleged earthquake in Venezuela. CyberPeace Research Wing research found the claim to be misleading. The viral video has no connection to any recent earthquake in Venezuela. In fact, the footage is from a completely different event that took place nearly three years ago in Turkey. It is being falsely shared with a wrong context on social media.
Claim:
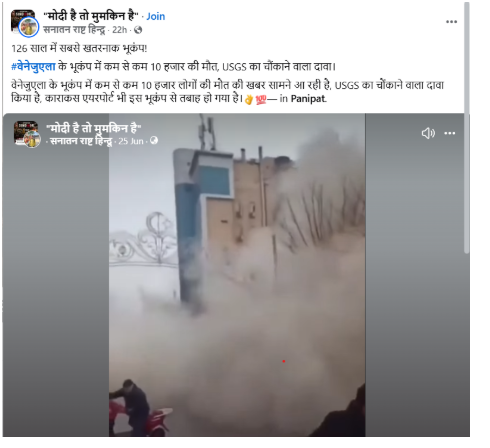
A Facebook user shared the viral video with the caption: “The most dangerous earthquake in 126 years! At least 10,000 deaths in Venezuela earthquake, shocking claim by USGS. Reports say massive destruction has occurred, Caracas airport has also been destroyed. Statement by Yogi Adityanath after Bharat Tiwari’s encounter.” The post link, archived link, and screenshots are provided below.
https://www.facebook.com/groups/2438255879794217/posts/4830038697282578/
FactCheck
To verify the claim, we performed a reverse image search of the video keyframes using Google Lens. During the search, we found the same video on WION’s Facebook page, where it was published on February 6, 2023. The original post link and screenshots are provided below. https://www.facebook.com/watch/?v=917786002738401
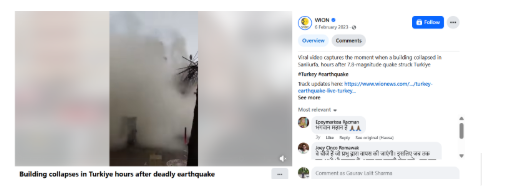
The original caption of the video clearly states that it shows a building collapse in Sanliurfa, Turkey, occurring hours after the 7.8-magnitude earthquake that struck the country. Based on clues from the Facebook post, we further searched using relevant keywords and found a report published by The Guardian on February 6, 2023, which also included the viral footage. https://www.theguardian.com/world/video/2023/feb/06/building-collapses-earthquake-aftershock-turkey-video
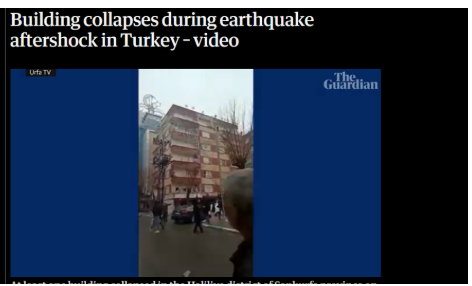
The report confirms that the video is from the aftermath of the devastating 2023 Turkey earthquake in Sanliurfa, not Venezuela.
Conclusion:
Our research confirms that the viral video has no connection to any recent earthquake in Venezuela. The footage is actually from the 2023 Turkey earthquake and is being falsely shared with a misleading context on social media.
Introduction
With the modernization of automobiles, so have the methods employed by criminals who seek to commit thefts. The old method of smashing a car window or bypassing an engine lock is no longer prevalent. Modern car thieves employ cloning techniques for keys and digital signals, and sophisticated methods to commit crimes without any traces left behind. In an era where intelligence is crucial, the forensic examination of car keys has become an indispensable tool for investigations, providing clues buried within ordinary car keys.
The Need for Car Key Forensics Today
Daily, thousands of cars worth millions are being hacked or stolen around the globe. The shocking thing is that most of these hacks do not have any sign of breakage or forced entry. It is because the thieves use vulnerabilities in the wireless key systems to unlock the vehicles without leaving any trace behind. Therefore, car-key forensics has now become more important than ever before.
Forensic Value of Smart Key
The smart key is not just comprised of locking and unlocking features for vehicles. Actually, it operates as a miniature computer within the key itself. Information such as pairing records, frequency of use, or the last instance that the key was used to unlock something could be contained in smart keys, thus offering evidence of any criminal activity conducted using these items.
Patterns of Vehicle Theft
Through the examination of the chip in a key, one will be able to establish whether the key was legally programmed or had been tampered with by some other means. Such forensics become more important when trying to detect and monitor any car theft rings, which employ cloning machines or software.
Confirming Ownership and Authenticity
In cases involving insurance claims or fraud, smart key data can help confirm whether the person making a claim actually owned or used the car during the incident. It’s digital proof that goes beyond what paperwork or statements can show.
Strengthening Legal Cases
When brought to court, data doesn’t lie. A properly handled forensic examination of a car key can provide hard evidence — the kind that holds up under questioning and supports or disproves claims with complete accuracy. In many cases, this small device becomes the most reliable witness in the investigation.
A Real-Life Example
Consider the following scenario: An expensive SUV is stolen from a parking lot secured with security surveillance. No one is captured on camera and there is no sign of forced entry. After days of investigation, the police end up arresting a suspect with a smart key.
During forensic analysis of the smart key, it is revealed that:
- The transponder has an ID number which can be matched against the immobilizer installed in the vehicle.
- The rolling code counter has been incremented in such a way that the date corresponds with the report of theft of the vehicle.
- The extracted information helps match the pair timestamp of the key with the particular make and model of the vehicle.
All this from a single piece of evidence – the smart key.
Inside a Smart Key: Where the Data Lives
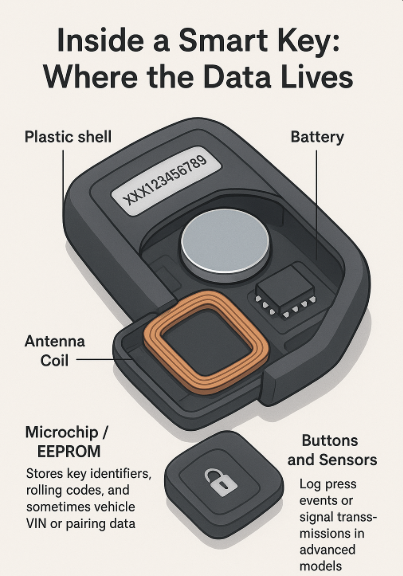
An average smart key is not only a remote but also a multi-level set of data carriers:
- Plastic Shell– could include serial numbers and information on the manufacture.
- Battery – helps calculate the time of using the key or detect any modifications.
- Antenna Coil – sends encrypted information to the immobilizer of a car. Draw the picture of this element.
- Microchip / EEPROM – holds key identification code, rolling code, VIN number, and/or other information of the vehicle.
- Buttons / sensors – could record any pressing or transmission actions in some cases.
All the little devices above, once properly studied via forensics software, provide valuable information.
How the Investigator Uncovers the Truth
In relation to investigating the true story about a vehicle, it is no different than handling other forms of digital evidence, as forensic analysts treat the car key in the same way. It is nothing more than an encrypted device in your hands, and using special techniques, they are able to reveal the information contained within the device.
Some of the methods used by modern forensic laboratories include:
1. Intercepting Radio Signals
Any intelligent key transmits radio signals to communicate with a car. Specialists employ advanced antennas and radio frequency (RF) analysers to catch and analyse them. This way, it is possible to understand the interaction between the key and the car – how often was it used, what kind of authentication procedure takes place, and if the signal matches the car’s one or has been forged somehow.
2. Checking Out the Key’s Brain (Analysis of EEPROM)
There is always a special chip on the key that is responsible for its activity. The chip contains an important memory module (EEPROM – Electrically Erasable Programmable Read-Only Memory), which holds various data, including key IDs and rolling codes. It can be carefully retrieved via advanced tools. Thus, it is possible to determine whether somebody tried to tamper with the key.
3. The Correlation between the Key and Car’s Information
The information stored inside the key will not be used separately since investigators will correlate the key's data with that of the vehicle itself (ECU and immobilizer). If the two kinds of information coincide, the investigation may conclude that the key belongs to the vehicle. Otherwise, this may mean either cloning or tampering.
4. Identifying the Tampering and Cloning Evidence
As was mentioned above, thieves sometimes resort to using unlawful programming devices for duplicating smart car keys. In order to detect possible cloning, experts examine the key using various diagnostic devices to find out whether the keys were modified by changing the encryption code, frequencies, and hardware itself.
At the end of the process, some kind of miracle occurs because of the following: all actions committed with this particular key become documented, recorded inside the device itself. Even if someone tries to hide anything or remove any information concerning this particular incident, there will always remain some data.
Car Key Forensics in the Future
The evolution of cars to connect with other devices and adopt self-driving technologies requires new investigative methods to be used for vehicle-related crimes. Advanced car keys or smartphone apps that replace physical keys will likely incorporate biometric authentication, cloud integration, or blockchain records of key activity in the near future.
Such improvements will pose several threats and offer many benefits:
- Artificial intelligence tools can determine if the car key is cloned based on its behaviour pattern.
- Blockchain validation ensures all key-related activities are recorded and cannot be altered.
- Cyber-forensic protocols will become increasingly necessary for investigating criminal activity related to vehicles.
Car key forensics technology will not only allow solving crimes but may become instrumental in crime prevention.
Conclusion
A car key in this era is more than just an unlocking mechanism; it is a miniature data storage facility, which can yield information about the user, intentions, and access rights. The more cars become technologically advanced, the more the examination of smart keys becomes necessary as part of correlating physical evidence with digital investigation. It clearly indicates how small objects such as keys can play pivotal roles in cracking cases.

Introduction
In the hyperconnected world, cyber incidents can no longer be treated as sporadic disruptions; such incidents have become an everyday occurrence. The attack landscape today is very consequential and shows significant multiplication in its frequency, with ransomware attacks incapacitating a health system, phishing attacks hitting a financial institution, or state-sponsored attacks on critical infrastructures. Towards counteracting such threats, traditional ways alone are not enough, they gravely rely on manual research and human intellect. Attackers exercise speed, scale, and stealth, and defenders are always four steps behind. With such a widening gap, it is deemed necessary to facilitate incident response and crisis management with the intervention of automation and artificial intelligence (AI) for faster detection, context-driven decision-making, and collaborative response beyond human capabilities.
Incident Response and Crisis Management
Incident response is the structured way in which organisations deal with responding to detecting, segregating, and recovering from security incidents. Crisis management takes this even further, dealing not only with the technical fallout of a breach but also its business, reputation, and regulatory implications. Echelon used to depend on manual teams of people sorting through logs, cross-correlating alarms, and generating responses, a paradigm effective for small numbers but quickly inadequate in today's threat climate. Today's opponents attack at machine speed, employing automation to launch attacks. Under such circumstances, responding with slow, manual methods means delay and draconian consequences. The AI and automation introduction is a paradigm change that allows organisations to equate the pace and precision with which attackers initiate attacks in responding to incidents.
How Automation Reinvents Response
Cybercrime automation liberates cybercrime analysts from boring and repetitive tasks that consume time. An analyst manually detects potential threats from a list of hundreds each day, while automated systems sift through noise and focus only on genuine threats. Malware can automatically cause infected computers to be disconnected from the network to avoid spreading or may automatically have its suspicious account permissions removed without human intervention. The security orchestration systems move further by introducing playbooks, predefined steps describing how incidents of a certain type (e.g., phishing attempts or malware infections) should be handled. This ensures fast containment while ensuring consistency and minimising human error amid the urgency of dealing with thousands of alerts.
Automation takes care of threat detection, prioritisation, and containment, allowing human analysts to refocus on more complex decision-making. Instead of drowning in the sea of trivial alerts, security teams can now devote their efforts to more strategic areas: threat hunting and longer-term resilience. Automation is a strong tool of defence, cutting response times down from hours to minutes.
The Intelligence Layer: AI in Action
If automation provides speed, then AI is what allows the brain to be intelligent and flexible. Working with old and fixed-rule systems, AI-enabled solutions learn from experiences, adapt to changes in threats, and discover hidden patterns of which human analysts themselves would be unaware. For instance, machine learning algorithms identify normal behaviour on a corporate network and raise alerts on any anomalies that could indicate an insider attack or an advanced persistent threat. Similarly, AI systems sift through global threat intelligence to predict likely attack vectors so organisations can have their vulnerabilities fixed before they are exploited.
AI also boosts forensic analysis. Instead of searching forever for clues, analysts let AI-driven systems trace back to the origin of an event, identify vulnerabilities exploited by attackers, and flag systems that are still under attack. During a crisis, AI is a decision support that predicts outcomes of different scenarios and recommends the best response. In response to a ransomware attack, for example, based on context, AI might advise separating a single network segment or restoring from backup or alerting law enforcement.
Real-World Applications and Case Studies
Already, this mitigation has been provided in the form of real-world applications of automation and AI. Consider, for example, IBM Watson for Cybersecurity, which has been applied in analysing unstructured threat intelligence and providing analysts with actionable results in minutes, rather than days. Like this, systems driven by AI in DARPA's Cyber Grand Challenge demonstrated the ability to automatically identify an instant vulnerability, patch it, and reveal the potential of a self-healing system. AI-powered fraud detection systems stop suspicious transactions in the middle of their execution and work all night to prevent losses. What is common in all these examples is that automation and AI lessen human effort, increase accuracy, and in the event of a cyberattack, buy precious time.
Challenges and Limitations
While promising, the technology is still not fully mature. The quality of an AI system is highly dependent on the training data provided; poor training can generate false positives that drown teams or worse false negatives that allow attackers to proceed unabated. Attackers have also started targeting AI itself by poisoning datasets or designing malware that does not get detected. Aside from risks that are more technical, the operational and financial costs involved in implementing advanced AI-based systems present expensive threats to any company. Organisations will have to make expenditures not only on technology but also for the training of staff to best utilise these tools. There are some ethical and privacy issues to consider as well because systems may be processing sensitive personal data, so global data protection laws such as the GDPR or India's DPDP Act could come into conflict.
Creating a Human-AI Collaboration
The future is not going to be one of substitution by machines but of creating human-AI synergy. Automation can do the drudgery, AI can provide smarts, and human professionals can use judgment, imagination, and ethical decisions. One would want to build AI-fuelled Security Operations Centres where technology and human experts work in tandem. Continuous training must be provided to AI models to reduce false alarms and make them most resistant against adversarial attacks. Regular conduct of crisis drills that combine AI tools and human teams can ensure preparedness for real-time events. Likewise, it is worth integrating ethical AI guidelines into security frameworks to ensure a stronger defence while respecting privacy and regulatory compliance.
Conclusion
Cyber-attacks are an eventuality in this modern time, but the actual impact need not be so harsh. The organisations can maintain the programmatic method of integrating automation and AI into incident response and crisis management so that the response against the very threat can be shifted from reactive firefighting to proactive resilience. Automation gives speed and efficiency while AI gives intelligence and foresight, hence putting the defenders on par and possibly exceeding the speed and sophistication of the attackers. But an utmost system without human inquisitiveness, ethical reasoning, and strategic foresight would remain imperfect. The best defence is in that human-machine relationship symbiotic system wherein automation and AI take care of how fast and how many cyber threats come in, whereas human intellect ensures that every response is aligned with larger organizational goals. This synergy is where cybersecurity resiliency will reside in the future-the defenders won't just be reacting to emergencies but will rather be driving the way.
References
- https://www.sisainfosec.com/blogs/incident-response-automation/
- https://stratpilot.ai/role-of-ai-in-crisis-management-and-its-critical-importance/
- https://www.juvare.com/integrating-artificial-intelligence-into-crisis-management/
- https://www.motadata.com/blog/role-of-automation-in-incident-management/
