
#FactCheck - False Claim of Hindu Sadhvi Marrying Muslim Man Debunked
Executive Summary:
A viral image circulating on social media claims to show a Hindu Sadhvi marrying a Muslim man; however, this claim is false. A thorough investigation by the Cyberpeace Research team found that the image has been digitally manipulated. The original photo, which was posted by Balmukund Acharya, a BJP MLA from Jaipur, on his official Facebook account in December 2023, he was posing with a Muslim man in his election office. The man wearing the Muslim skullcap is featured in several other photos on Acharya's Instagram account, where he expressed gratitude for the support from the Muslim community. Thus, the claimed image of a marriage between a Hindu Sadhvi and a Muslim man is digitally altered.

Claims:
An image circulating on social media claims to show a Hindu Sadhvi marrying a Muslim man.


Fact Check:
Upon receiving the posts, we reverse searched the image to find any credible sources. We found a photo posted by Balmukund Acharya Hathoj Dham on his facebook page on 6 December 2023.

This photo is digitally altered and posted on social media to mislead. We also found several different photos with the skullcap man where he was featured.

We also checked for any AI fabrication in the viral image. We checked using a detection tool named, “content@scale” AI Image detection. This tool found the image to be 95% AI Manipulated.

We also checked with another detection tool for further validation named, “isitai” image detection tool. It found the image to be 38.50% of AI content, which concludes to the fact that the image is manipulated and doesn’t support the claim made. Hence, the viral image is fake and misleading.

Conclusion:
The lack of credible source and the detection of AI manipulation in the image explains that the viral image claiming to show a Hindu Sadhvi marrying a Muslim man is false. It has been digitally altered. The original image features BJP MLA Balmukund Acharya posing with a Muslim man, and there is no evidence of the claimed marriage.
- Claim: An image circulating on social media claims to show a Hindu Sadhvi marrying a Muslim man.
- Claimed on: X (Formerly known as Twitter)
- Fact Check: Fake & Misleading

Related Blogs

Introduction
With the ever-growing technology where cyber-crimes are increasing, a new cyber-attack is on the rise, but it’s not in your inbox or your computer- it's targeting your phone, especially your smartphone. Cybercriminals are expanding their reach in India, with a new text-messaging fraud targeting individuals. The Indian Computer Emergency Response Team (CERT-In) has warned against "smishing," or SMS phishing.
Understanding Smishing
Smishing is a combination of the terms "SMS" and "phishing." It entails sending false text messages that appear to be from reputable sources such as banks, government organizations, or well-known companies. These communications frequently generate a feeling of urgency in their readers, prompting them to click on harmful links, expose personal information, or conduct financial transactions.
When hackers "phish," they send out phony emails in the hopes of tricking the receiver into clicking on a dangerous link. Smishing is just the use of text messaging rather than email. In essence, these hackers are out to steal your personal information to commit fraud or other cybercrimes. This generally entails stealing money – usually your own, but occasionally also the money of your firm.
The cybercriminals typically use these tactics to lure victims and steal the information.
Malware- The cyber crooks send the smishing URL link that might tick you into downloading malicious software on your phone itself. This SMS malware may appear as legitimate software, deceiving you into putting in sensitive information and transmitting it to crooks.
Malicious website- The URL in the smishing message may direct you to a bogus website that seeks sensitive personal information. Cybercriminals employ custom-made rogue sites meant to seem like legitimate ones, making it simpler to steal your information.
Smishing text messages often appear to be from your bank, asking you to share personal sensitive information, ATM numbers, or account details. Mobile device cybercrime is increasing, as is mobile device usage. Aside from the fact that texting is the most prevalent usage of cell phones, a few additional aspects make this an especially pernicious security issue. Let's go over how smishing attacks operate.
Modus Operandi
The cyber crooks commit the fraud via SMS. As attackers assume an identity that might be of someone trusted, Smishing attackers can use social engineering techniques to sway a victim's decision-making. Three things are causing this deception:
- Trust- Cyber crooks target individuals, by posing to someone from a legitimate individual and organization, this naturally lowers a person’s defense against threats.
- Context- Using a circumstance that might be relevant to targets helps an attacker to create an effective disguise. The message feels personalized, which helps it overcome any assumption that it is spam.
- Emotion- The nature of the SMS is critical; it makes the victim think that is urgent and requires rapid action. Using these tactics, attackers craft communications that compel the receiver to act.
- Typically, attackers want the victim to click on a URL link within the text message, which takes them to a phishing tool that asks them for sensitive information. This phishing tool is frequently in the form of a website or app that also assumes a phony identity.
How does Smishing Spread?
As we have revealed earlier smishing attacks are delivered through both traditional texts. However, SMS phishing attacks primarily appear to be from known sources People are less careful while they are on their phones. Many people believe that their cell phones are more secure than their desktops. However, smartphone security has limits and cannot always guard against smishing directly.
Considering the fact phones are the target While Android smartphones dominate the market and are a perfect target for malware text messages, iOS devices are as vulnerable. Although Apple's iOS mobile technology has a high reputation for security, no mobile operating system can protect you from phishing-style assaults on its own. A false feeling of security, regardless of platform, might leave users especially exposed.
Kinds of smishing attacks
Some common types of smishing attacks that occurred are;
- COVID-19 Smishing: The Better Business Bureau observed an increase in reports of US government impersonators sending text messages requesting consumers to take an obligatory COVID-19 test via a connected website in April 2020. The concept of these smishing assaults may readily develop, as feeding on pandemic concerns is a successful technique of victimizing the public.
- Gift Smishing: Give away, shopping rewards, or any number of other free offers, this kind of smishing includes free services or products, from a reputable or other company. attackers plan in such a way that the offer is for a limited time or is an exclusive offer and the offers are so lucrative that one gets excited and falls into the trap.
CERT Guidelines
CERT-In shared some steps to avoid falling victim to smishing.
- Never click on any suspicious link in SMS/social media charts or posts.
- Use online resources to validate shortened URLs.
- Always check the link before clicking.
- Use updated antivirus and antimalware tools.
- If you receive any suspicious message pretending to be from a bank or institution, immediately contact the bank or institution.
- Use a separate email account for personal online transactions.
- Enforce multi-factor authentication (MFA) for emails and bank accounts.
- Keep your operating system and software updated with the latest patches.
Conclusion
Smishing uses fraudulent mobile text messages to trick people into downloading malware, sharing sensitive data, or paying cybercriminals money. With the latest technological developments, it has become really important to stay vigilant in the digital era not only protecting your computers but safeguarding the devices that fit in the palm of your hand, CERT warning plays a vital role in this. Awareness and best practices play a pivotal role in safeguarding yourself from evolving threats.
Reference
- https://www.ndtv.com/india-news/government-warns-of-smishing-attacks-heres-how-to-stay-safe-4709458
- https://zeenews.india.com/technology/govt-warns-citizens-about-smishing-scam-how-to-protect-against-this-online-threat-2654285.html
- https://www.the420.in/protect-against-smishing-scams-cert-in-advice-online-safety/
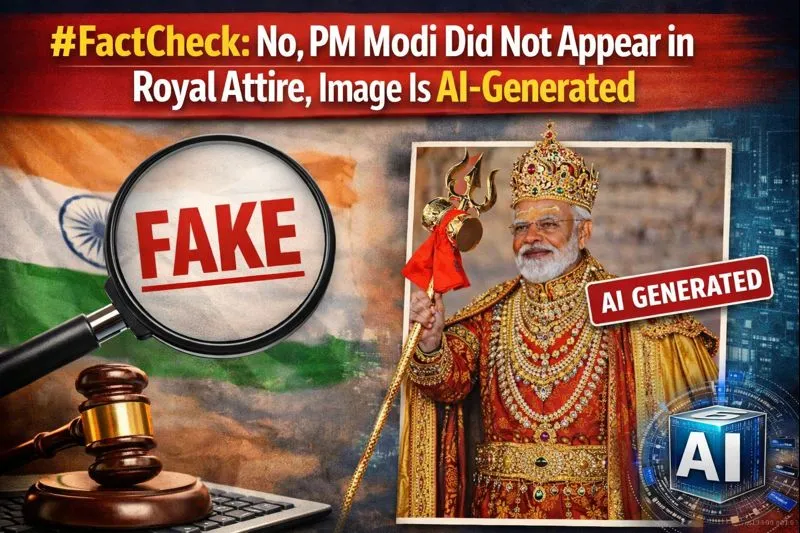
A photograph showing Prime Minister Narendra Modi holding a trident and dressed in royal attire is being widely shared on social media. Users circulating the image are claiming that it shows PM Modi in a regal outfit.
However, a verification by the Cyber Peace Foundation’s Research Desk has found that the claim is false. The investigation established that the viral image is not authentic and has been generated using Artificial Intelligence (AI).
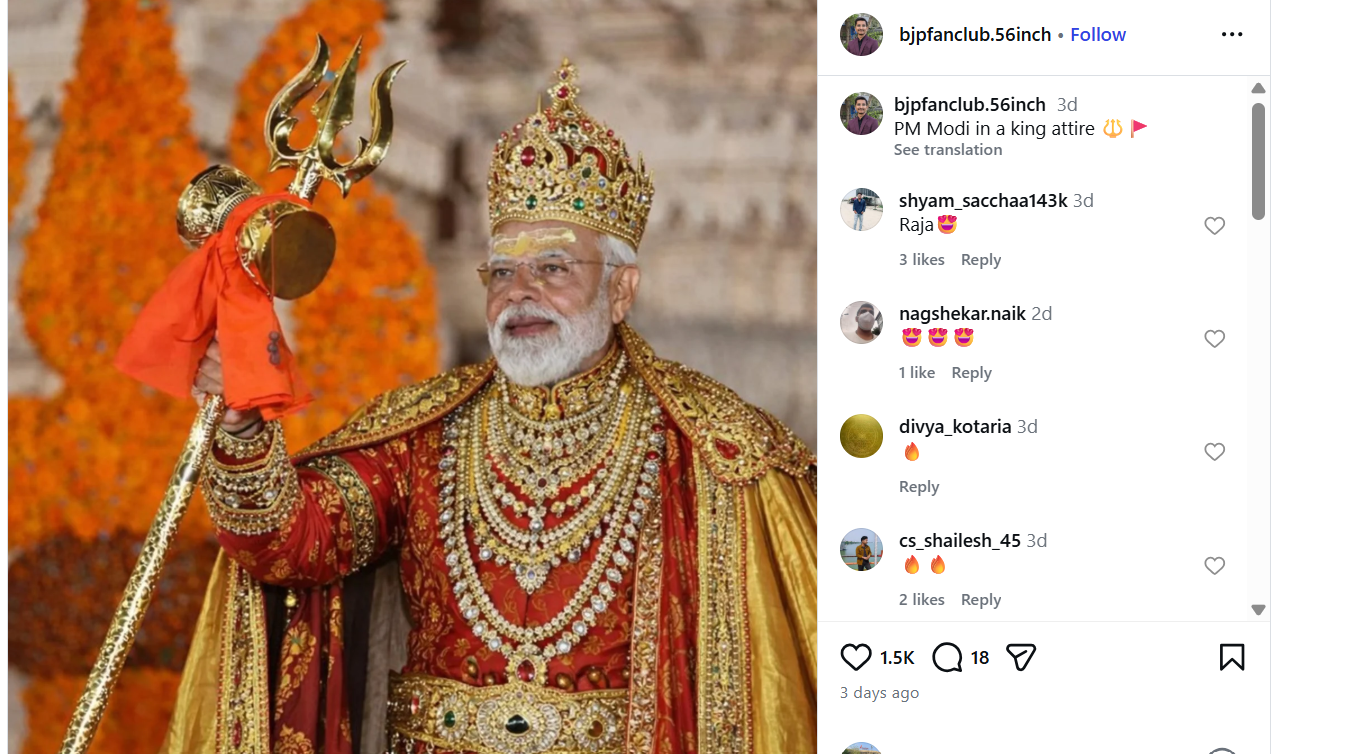
Claim:
On January 11, 2026, several Instagram users shared the image with captions describing it as a photograph of Prime Minister Modi in royal attire.
Links and archived versions of the posts, along with screenshots, are provided below.
Fact Check:
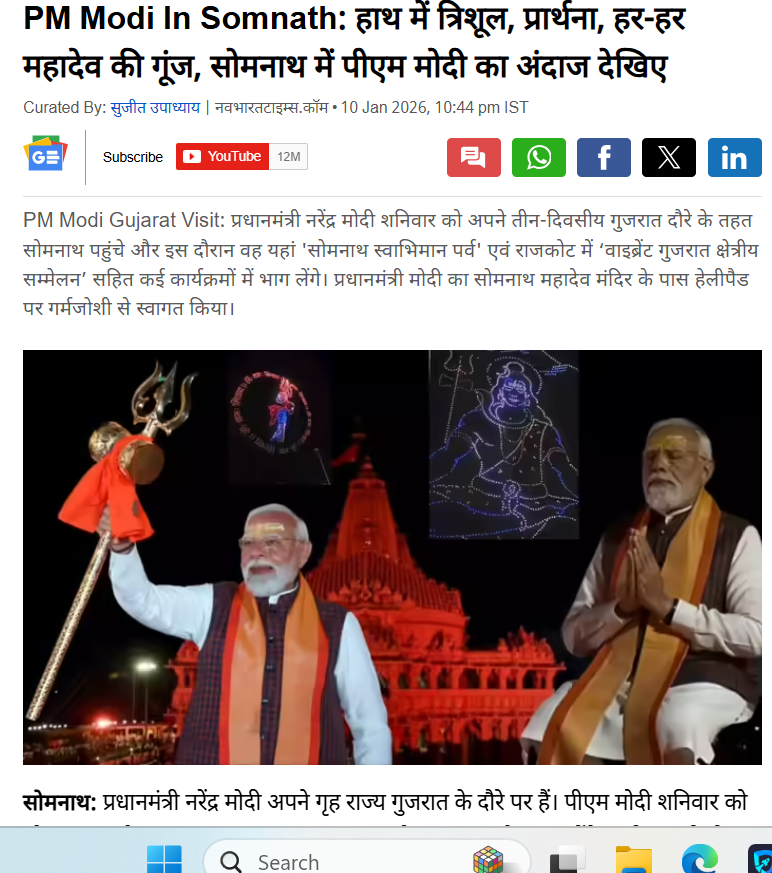
To verify the claim, relevant keywords such as “PM Modi holding trishul” were searched on Google. This led to a report published by Navbharat Times on January 10, 2025. The report features photographs of Prime Minister Modi holding a trident during his visit to the Somnath Temple. However, in the original images, he is seen wearing normal attire, not royal clothing as shown in the viral image. Link and screenshot
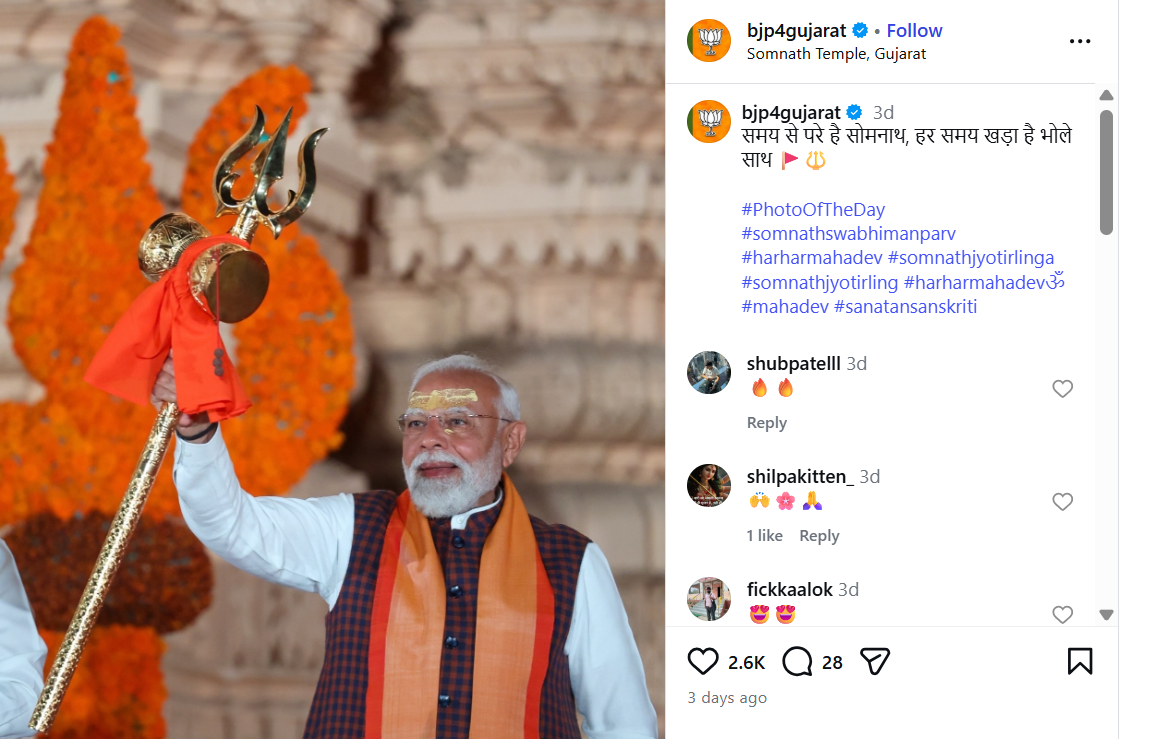
In the next step of the investigation, the original photograph was traced to the official Instagram account of BJP Gujarat, where it was posted on January 11, 2026. The post clearly identifies the image as being from Somnath Temple. Link and screenshot: https://www.instagram.com/p/DTVlb-9Da1V
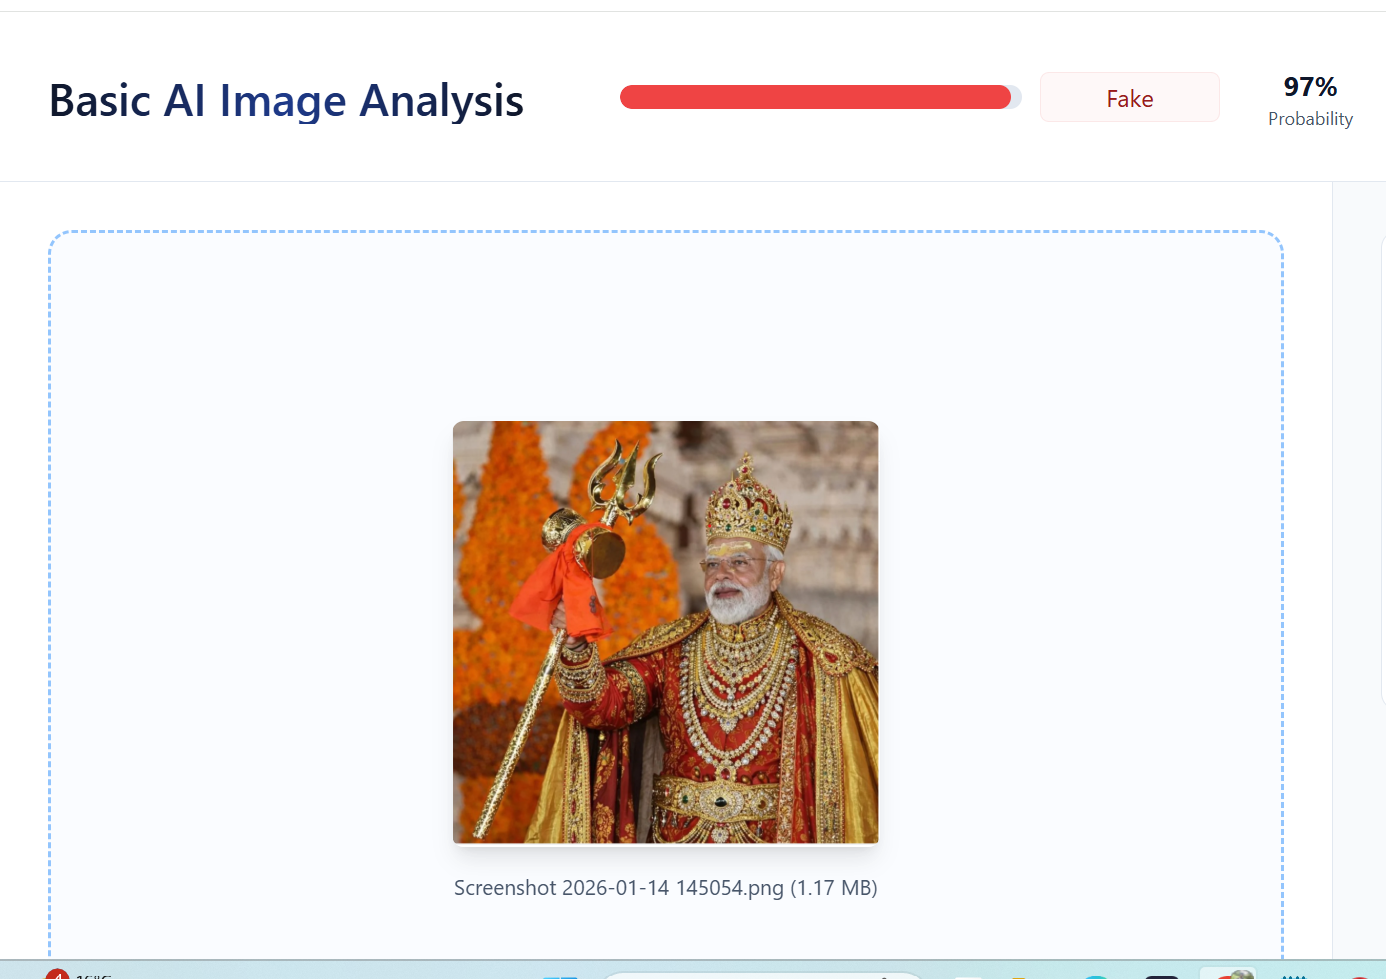
A close examination of the viral image raised suspicion about digital manipulation. The image was then analysed using the AI detection tool TruthScan. The tool’s assessment indicated a 97 percent likelihood that the image was AI-generated.
Further comparison between the viral image and the original photograph revealed that all visual elements match except the clothing, confirming that the attire was digitally altered using AI tools.
Conclusion
The claim that Prime Minister Narendra Modi appeared in royal attire is false. The Cyber Peace Foundation’s research confirms that the viral image was created using AI by altering the clothing in an original photograph taken during PM Modi’s visit to Somnath Temple. The manipulated image was shared online to mislead users.
Introduction
Cyberwarfare has evolved into one of the most decisive instruments of statecraft and conflict. The increasing digitisation of critical infrastructure like power grids, water systems, transportation systems, healthcare networks, and energy sources has made these systems new targets in the war of algorithms. Military logic is evolving to paralyse the nation’s critical infrastructure to keep its resources engaged in repairing them and thereby break the nation’s ability to deter and counter attacks, all without firing a single bullet.
From Ransomware to an Invisible Sabotage: The changing nature of warfare
The operational technology (OT) landscape has become the epicentre of cyber operations, all around the world. Once, which was insulated, related to industrial systems that controlled turbines, pipelines, or dams, they now stand connected to the Internet through supervisory control and data acquisition (SCADA) and the Internet of Things. These connections have also become gateways for attackers, besides enhancing the efficiency of the infrastructural lifelines of the nation.
Groups like Volt Typhoon, Sandworm, Laurionite, and Cyberavengers have transformed the art of digital infiltration into a strategic shift. Volt Typhoon, which is linked to China, has used “living-off-the-land” techniques to exploit the legitimate administrative tools to remain invisible while scanning the critical infrastructures in the US. Sandworm, which is aligned with Russia’s GRU (Glavnoye Razvedyvatelnoye Upravlenie) or Main Intelligence Directorate (in English), has demonstrated the power of cyber sabotage in real time, as its attacks on Ukraine’s power grids in 2015 and 2021 had left millions in darkness, coinciding with kinetic missile strikes. Meanwhile, the Iranian-affiliated Cyberavengers group, which has weaponised the AI-assisted malware, such as IOCONTROL, that are capable of hijacking water and energy control systems. Each of these systems used in these operations reflects a shift from direct espionage activities to a state of strategic paralysis.
In comparison to the traditional cybercrime activities that are aimed at stealing data and extortion of money, these campaigns repeatedly target the physical systems, which consist of the machinery that sustains civilian life and military preparedness.
The Military Logic behind Cyber Targeting: A Web of Vulnerabilities
A critical infrastructure is a complex ecosystem that covers power generation, transportation, communication, and manufacturing are all interconnected, which means a single compromised node can cascade into a national paralysis. For instance, a breach in the systems of the dam can flood an entire city, a grid shutdown can halt water supply to hospitals, and even affect air traffic. The 2015 Black Energy Malware attack in Ukraine has proved this possibility when three utilities were hacked, plunging thousands of homes into darkness. The Iranian hackers once again gained access to the Bowman Avenue Dam of New York and controlled its floodgates, which gave a chilling demonstration of the destructive reality of digital manipulation.
The systems remain vulnerable mainly for 3 reasons such as-
- Legacy Architectures: Many of these industrial systems were designed decades ago with no built-in cybersecurity mechanisms.
- Slow Patching and Segmentation Gaps: All updates and segmentation between IT and TO networks often lag, providing open entry points for attackers.
- Converging with IoT: The integration of smart sensors and cloud-based management tools has expanded the attack surface exponentially.
This interconnected fragility has turned our critical infrastructures into both a weapon and a target or a tool for coercion in modern hybrid warfare. Between 2023 and 2024, over 420 cyberattacks were witnessed in several critical global infrastructures, which averaged to 13 attacks per second, according to a news report. These were not just random acts of digital vandalism; they were deliberate and coordinated operational attempts by state-led actors from China, Russia, and Iran.
Developing a new Resilience as the new tool of Deterrence
Cyber deterrence no longer rests on the fear of retaliation, it relies on the need for resilience. Nations that can absorb attacks, maintain continuity, and recover rapidly would be the true superpowers of this digital age. Segmentation, real-time threat detection, and AI-assisted recovery models are vital pillars of this model of resilience. The logic of modern cyberwarfare is clear, which means that the more a nation digitizes, the more it will need to defend itself.
However, as the line between war and peace blurs, safeguarding critical infrastructure is no longer just an IT priority; rather, it is a national security doctrine. In this silent theatre of cyberwarfare, survival will depend not only on firepower, but on firewalls.
References
- https://rmcglobal.com/critical-infrastructure-under-siege-the-top-ot-threats-of-2025/
- https://ccdcoe.org/uploads/2018/10/Geers2009_The-Cyber-Threat-to-National-Critical-Infrastructures.pdf
- https://www.researchgate.net/publication/335752979_Cybersecurity_of_Critical_Infrastructure
- https://arxiv.org/html/2510.04118v1
- https://www.anapaya.net/blog/top-5-critical-infrastructure-cyberattacks
