
#FactCheck - Assam Video Falsely Shared as BJP Government Deporting Bangladeshis From West Bengal
Executive Summary
A video is being widely shared on social media amid claims that the BJP has formed a government in West Bengal. The video shows several people being taken away in a bus while their family members are seen crying and grieving nearby. Users sharing the clip claim that the scene is from West Bengal, where the BJP government has allegedly started sending back Bangladeshis who were living illegally in the state.
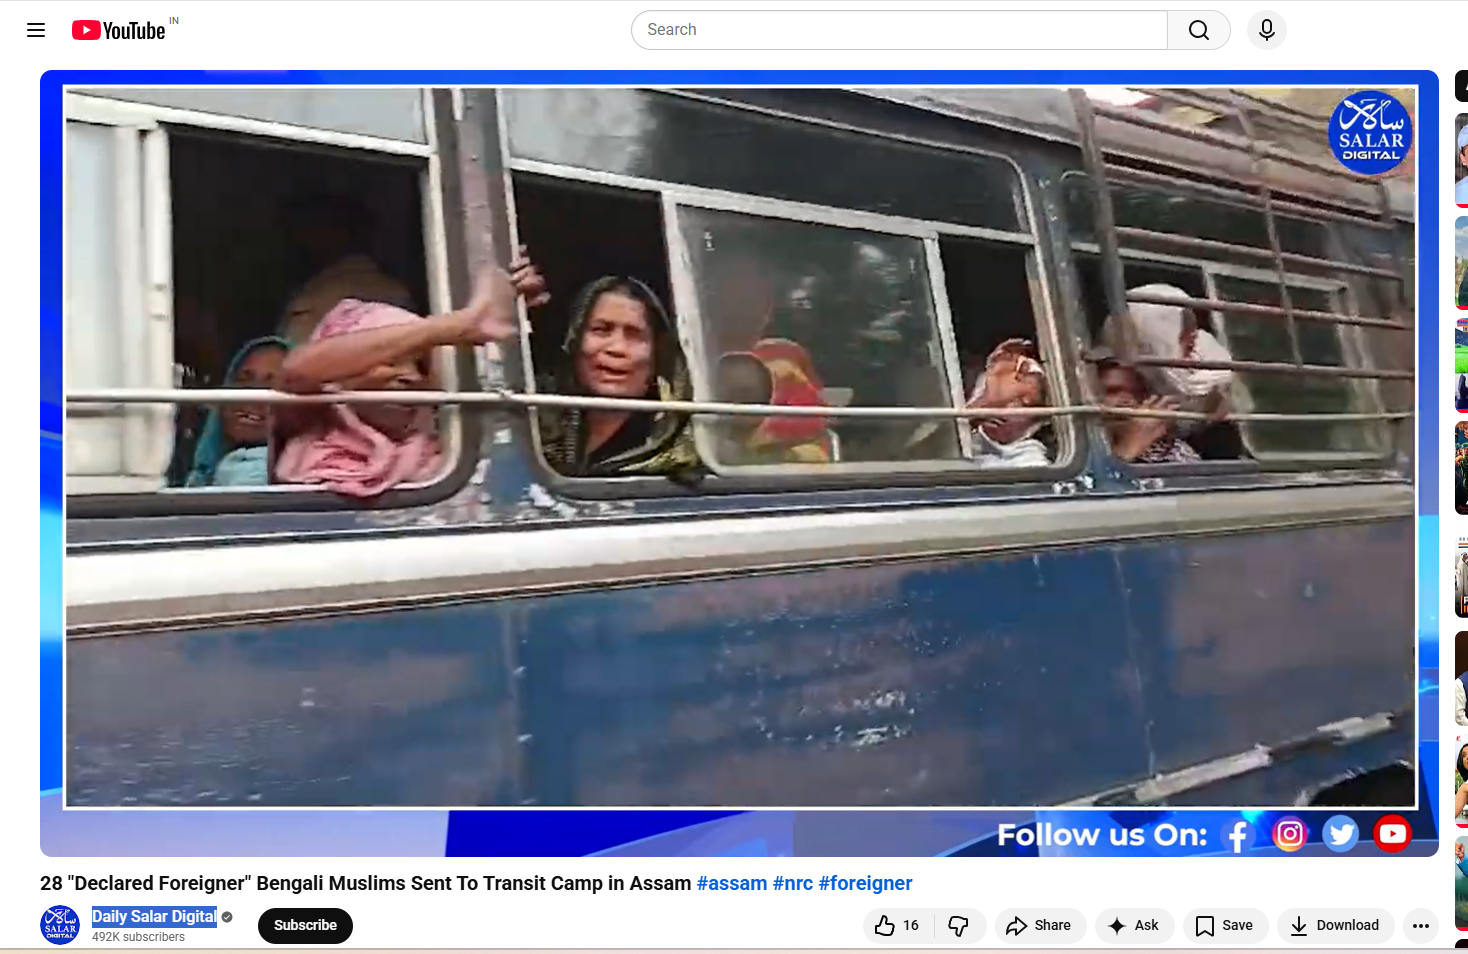
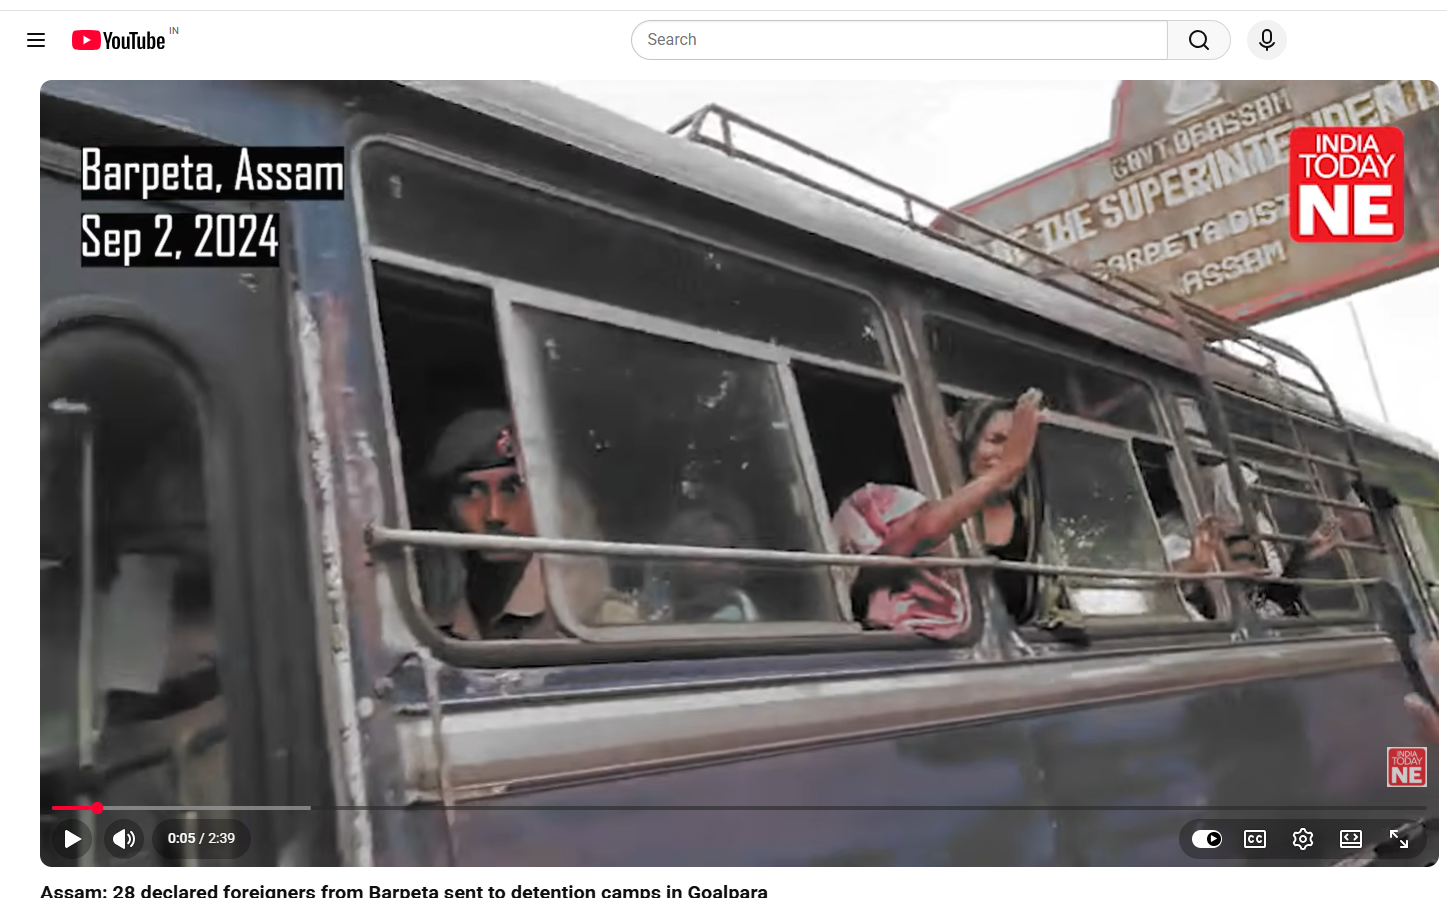
Research by CyberPeace Research Wing found the viral claim to be misleading. The research revealed that the viral video has no connection with West Bengal. The video is actually from Assam’s Barpeta district, where in 2024, a Foreigners Tribunal declared 28 people as non-citizens. Following the order, authorities shifted them to a transit camp. The viral clip is from that incident. An old and unrelated video is now being falsely shared as a recent incident from West Bengal.
Claim
On May 14, 2026, a Facebook user shared the viral video and wrote, “How sad… Opposition voters are now being packed off to the Bangladesh border from Bengal and Assam. How will they ever win now? Really terrible what is happening to these poor people.” The post link, archive link, and screenshot are provided below.
- https://www.facebook.com/rajendra.kasliwal1/posts/973081982000168/
- https://archive.ph/y7Y4D

Another user also shared the same viral video on social media with a similar claim. The post link, archive link, and screenshot are given below.
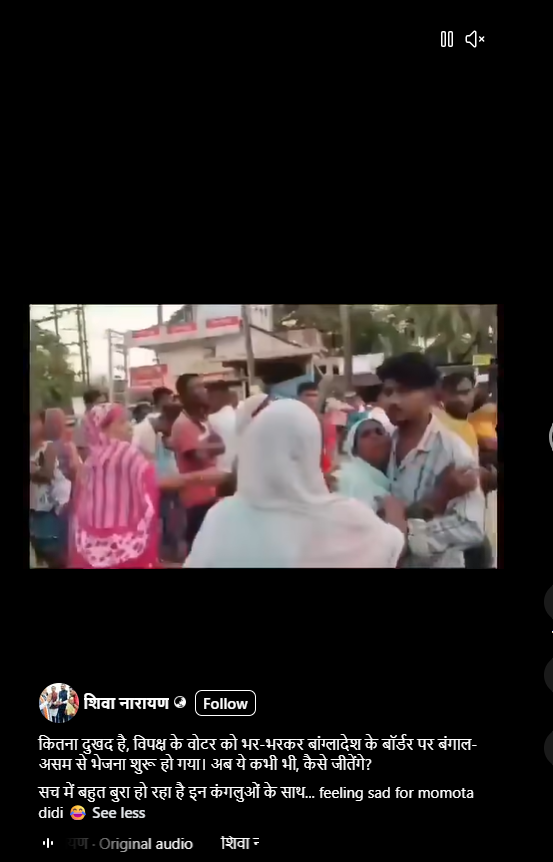
Fact Check
To verify the authenticity of the viral video, we extracted several key frames and performed a reverse image search. During the research, we found the same video uploaded on a YouTube channel named Daily Salar Digital on September 5, 2024. The link to the post and its screenshot are given below.
Further research led us to a report published by IndiaTodayNE on September 3, 2024, carrying a similar description of the incident. The post link and screenshot are provided below.
Conclusion
Our research found that the viral video has no connection with West Bengal. The clip is from Assam’s Barpeta district, where in 2024, 28 people were declared non-citizens by a Foreigners Tribunal and later shifted to a transit camp by authorities. The video being shared online is from that incident. An old and unrelated video is being falsely circulated as a recent development from West Bengal.

Related Blogs

Overview:
The National Payments Corporation of India (NPCI) officially revealed on the 31st of July 2024 that its client C-Edge Technologies had been subject to a ransomware attack. These circumstances have caused C-Edge to be separated from retail payment systems to eliminate more threats to the national payment systems. More than 200 cooperative and regional rural banks have been affected leading to disruptions in normal services including ATM withdrawals and UPI transactions.
About C-Edge Technologies:
C-Edge Technologies was founded in the year 2010 especially to meet the specific requirements of the Indian banking and other allied sectors accentuating more on the cooperative and the regional rural banks. The company offers a range of services such as Core Banking Solutions by functioning as the center of a bank where customers’ records are managed and accounting of transactions takes place, Payment Solutions through the implementation of payment gateways and mobile banking facilities, cybersecurity through threat detection and incident response to protect banking organizations, data analytics and AI through the analytics of big banking data to reduce risks and detect frauds.
Details of Ransomware attack:
Reports say, this ransomware attack has been attributed by the RansomEXX group which primarily targeted Brontoo Technology Solutions, a key collaborator with C-Edge, through a misconfigured Jenkins server, which allowed unauthorized access to the systems.
The RansomExx group also known as Defray777 or Ransom X utilized a sophisticated variant known as RansomEXX v2.0 to execute the attack. This group often targets large organizations and demands substantial ransoms. RansomEXX uses various malware tools such as IcedID, Vatet Loader, and PyXie RAT. It typically infiltrates systems through phishing emails, exploiting vulnerabilities in applications and services, including Remote Desktop Protocol (RDP). The ransomware encrypts files using the Advanced Encryption Standard (AES), with the encryption key further secured using RSA encryption. This dual-layer encryption complicates recovery efforts for victims. RansomEXX operates on a ransomware-as-a-service model, allowing affiliates to conduct attacks using its infrastructure. Earlier in 2021, it attacked StarHub and Gigabyte’s servers for ransome.
Impact due to the attack:
The immediate consequences of the ransomware attack include:
- Service Disruption: This has negative implications to consumers especially the citizens who use the banks to do their day to day banking activities such as withdrawals and online transactions. Among the complaints some of them relate to cases where the sender’s account has been debited without the corresponding credit to the receiver account.
- Isolation Measures: Likely, NPCI is already following the right measures as it had disconnected C-Edge from its networks to contain the proliferation of the ransomware. This decision was made as a precautionary measure so that all functional aspects in a larger financial system are safeguarded.
Operations resumed:
The National Payments Corporation of India (NPCI) said it has restored connectivity with C-Edge Technologies Ltd after the latter’s network connection was severed by NPCI over security concerns that were evaluated by an external forensic auditing firm. The audit affirmed that all affected systems were contained in order to avoid the occurrence of ransomware attack contagion. All the affected systems were localized in C-Edge’s data center and no repercussion was evidenced regarding the infrastructure of the cooperative banks or the regional rural banks that are involved in the business. Both NPCI and C-Edge Technologies have resumed normalcy so that the banking and financial services being offered by these banks remain safe and secure.
Major Implications for Banking Sector:
The attack on C-Edge Technologies raises several critical concerns for the Indian banking sector:
- Cybersecurity Vulnerabilities: It also shows the weak linkages which are present within the technology system that help smaller sized banks. Nevertheless, the service has been offered by C-Edge regarding their cybersecurity solution, this attack evidence that the securities required should improve in all types of banks and banking applications.
- Financial Inclusion Risks: Co operative and regional rural banks also have its importance in the financial inclusion especially in rural and semi urban areas. Gradually, interruptions to their services pose a risk to signal diminished improvement in financial literacy for the excluded groups contrary to the common year advancement.
- Regulatory Scrutiny: After this event, agencies such as the Reserve Bank of India (RBI) may enhance the examination of the banking sector’s cybersecurity mechanisms. Some of the directives may even require institutions to adhere to higher compliance measures regarding the defense against cyber threats.
Way Forward: Mitigation
- Strengthening Cybersecurity: It is important to enhance the cyber security to eliminate this kind of attacks in the future. This may include using better threat detection systems, penetration testing to find the vulnerabilities, system hardening, and network monitoring from time to time.
- Transition to Cloud-Based Solutions: The application of adaptations in cloud solutions can contribute to the enhancement in operative efficiency as well as optimization in the utilization of resources. The security features of cloud should be implemented for safety and protection against cyber threats for SMEs in the banking sector.
- Leveraging AI and Data Analytics: Development of the AI-based solutions for fraud and risk control means that bank organizations get the chance to address threats and to regain clients’ trust.
Conclusion:
This ransomware attack in C-Edge Technologies in the banking sector provides a warning for all the infrastructures. Initial cleanup methodologies and quarantining are effective. The continuous monitoring of cyber security features in the infrastructure and awareness between employees helps to avoid these kinds of attacks. Building up cyber security areas will also effectively safeguard the institution against other cyber risks in the future and fortify the confidence and reliability of the financial system, especially the regional rural banks.
Reference:
- https://www.businesstoday.in/technology/news/story/c-edge-technologies-a-deep-dive-into-the-indian-fintech-powerhouse-hit-by-major-cyberattack-439657-2024-08-01
- https://www.thehindu.com/sci-tech/technology/customers-at-several-small-sized-banks-affected-as-tech-provider-c-edge-suffers-ransomware-attack/article68470198.ece
- https://www.cnbctv18.com/technology/ransomware-attack-disrupts-over-200-co-operative-banks-regional-rural-banks-19452521.htm
- https://timesofindia.indiatimes.com/city/ahmedabad/ransomware-breach-at-c-edge-impacts-transactions-for-cooperative-banks/articleshow/112180914.cms
- https://www.emsisoft.com/en/blog/41027/ransomware-profile-ransomexx/

Executive Summary
The IT giant Apple has alerted customers to the impending threat of "mercenary spyware" assaults in 92 countries, including India. These highly skilled attacks, which are frequently linked to both private and state actors (such as the NSO Group’s Pegasus spyware), target specific individuals, including politicians, journalists, activists and diplomats. In sharp contrast to consumer-grade malware, these attacks are in a league unto themselves: highly-customized to fit the individual target and involving significant resources to create and use.
As the incidence of such attacks rises, it is important that all persons, businesses, and officials equip themselves with information about how such mercenary spyware programs work, what are the most-used methods, how these attacks can be prevented and what one must do if targeted. Individuals and organizations can begin protecting themselves against these attacks by enabling "Lockdown Mode" to provide an extra layer of security to their devices and by frequently changing passwords and by not visiting the suspicious URLs or attachments.
Introduction: Understanding Mercenary Spyware
Mercenary spyware is a special kind of spyware that is developed exclusively for law enforcement and government organizations. These kinds of spywares are not available in app stores, and are developed for attacking a particular individual and require a significant investment of resources and advanced technologies. Mercenary spyware hackers infiltrate systems by means of techniques such as phishing (by sending malicious links or attachments), pretexting (by manipulating the individuals to share personal information) or baiting (using tempting offers). They often intend to use Advanced Persistent Threats (APT) where the hackers remain undetected for a prolonged period of time to steal data by continuous stealthy infiltration of the target’s network. The other method to gain access is through zero-day vulnerabilities, which is the process of gaining access to mobile devices using vulnerabilities existing in software. A well-known example of mercenary spyware includes the infamous Pegasus by the NSO Group.
Actions: By Apple against Mercenary Spyware
Apple has introduced an advanced, optional protection feature in its newer product versions (including iOS 16, iPadOS 16, and macOS Ventura) to combat mercenary spyware attacks. These features have been provided to the users who are at risk of targeted cyber attacks.
Apple released a statement on the matter, sharing, “mercenary spyware attackers apply exceptional resources to target a very small number of specific individuals and their devices. Mercenary spyware attacks cost millions of dollars and often have a short shelf life, making them much harder to detect and prevent.”
When Apple's internal threat intelligence and investigations detect these highly-targeted attacks, they take immediate action to notify the affected users. The notification process involves:
- Displaying a "Threat Notification" at the top of the user's Apple ID page after they sign in.

- Sending an email and iMessage alert to the addresses and phone numbers associated with the user's Apple ID.
- Providing clear instructions on steps the user should take to protect their devices, including enabling "Lockdown Mode" for the strongest available security.
- Apple stresses that these threat notifications are "high-confidence alerts" - meaning they have strong evidence that the user has been deliberately targeted by mercenary spyware. As such, these alerts should be taken extremely seriously by recipients.
Modus Operandi of Mercenary Spyware
- Installing advanced surveillance equipment remotely and covertly.
- Using zero-click or one-click attacks to take advantage of device vulnerabilities.
- Gain access to a variety of data on the device, including location tracking, call logs, text messages, passwords, microphone, camera, and app information.
- Installation by utilizing many system vulnerabilities on devices running particular iOS and Android versions.
- Defense by patching vulnerabilities with security updates (e.g., CVE-2023-41991, CVE-2023-41992, CVE-2023-41993).
- Utilizing defensive DNS services, non-signature-based endpoint technologies, and frequent device reboots as mitigation techniques.
Prevention Measures: Safeguarding Your Devices
- Turn on security measures: Make use of the security features that the device maker has supplied, such as Apple's Lockdown Mode, which is intended to prevent viruses of all types from infecting Apple products, such as iPhones.
- Frequent software upgrades: Make sure the newest security and software updates are installed on your devices. This aids in patching holes that mercenary malware could exploit.
- Steer clear of misleading connections: Exercise caution while opening attachments or accessing links from unidentified sources. Installing mercenary spyware is possible via phishing links or attachments.
- Limit app permissions: Reassess and restrict app permissions to avoid unwanted access to private information.
- Use secure networks: To reduce the chance of data interception, connect to secure Wi-Fi networks and stay away from public or unprotected connections.
- Install security applications: To identify and stop any spyware attacks, think about installing reliable security programs from reliable sources.
- Be alert: If Apple or other device makers send you a threat notice, consider it carefully and take the advised security precautions.
- Two-factor authentication: To provide an extra degree of protection against unwanted access, enable two-factor authentication (2FA) on your Apple ID and other significant accounts.
- Consider additional security measures: For high-risk individuals, consider using additional security measures, such as encrypted communication apps and secure file storage services
Way Forward: Strengthening Digital Defenses, Strengthening Democracy
People, businesses and administrations must prioritize cyber security measures and keep up with emerging dangers as mercenary spyware attacks continue to develop and spread. To effectively address the growing threat of digital espionage, cooperation between government agencies, cybersecurity specialists, and technology businesses is essential.
In the Indian context, the update carries significant policy implications and must inspire a discussion on legal frameworks for government surveillance practices and cyber security protocols in the nation. As the public becomes more informed about such sophisticated cyber threats, we can expect a greater push for oversight mechanisms and regulatory protocols. The misuse of surveillance technology poses a significant threat to individuals and institutions alike. Policy reforms concerning surveillance tech must be tailored to address the specific concerns of the use of such methods by state actors vs. private players.
There is a pressing need for electoral reforms that help safeguard democratic processes in the current digital age. There has been a paradigm shift in how political activities are conducted in current times: the advent of the digital domain has seen parties and leaders pivot their campaigning efforts to favor the online audience as enthusiastically as they campaign offline. Given that this is an election year, quite possibly the most significant one in modern Indian history, digital outreach and online public engagement are expected to be at an all-time high. And so, it is imperative to protect the electoral process against cyber threats so that public trust in the legitimacy of India’s democratic is rewarded and the digital domain is an asset, and not a threat, to good governance.

Introduction
The Department of Telecommunications on 28th October 2024 notified an amendment to the Flight and Maritime Connectivity Rules, 2018 (FMCR 2018).
Rule 9 of the principle rules in FMCR 2018 stated:
“Restrictions–(1) The IFMC service provider shall provide the operation of mobile communication services in aircraft at minimum height of 3000 meters in Indian airspace to avoid interference with terrestrial mobile networks. (2) Internet services through Wi-Fi in aircraft shall be made available when electronic devices are permitted to be used only in airplane mode.”
In 2022, an amendment was made to the attached form in the Rules for obtaining authorisation to provide IFMC services.
Subsequently, the 2024 amendment substitutes sub-rule (2), namely :
“ (2) Notwithstanding the minimum height in Indian airspace referred to in sub-rule (1), internet services through Wi-Fi in aircraft shall be made available when electronic devices are permitted to be used in the aircraft.”
Highlights of the Amendment
These rules govern the use of Wi-Fi in airplanes and ships within or above India or Indian territorial waters through In Flight and Maritime Connectivity (IFMC) services provided by IFMC service providers responsible for establishing and maintaining them.
Airplanes are equipped with antennas, onboard servers, and routers to connect to signals received from ground towers via Direct Air-to-Ground Communications (DA2GC) or through satellites. The DA2GC system offers connectivity through various communication methods, supporting services like in-flight Internet access and mobile multimedia. Licensed In-Flight Mobile Connectivity (IFMC) providers must adhere to standards set by international organizations such as the International Telecommunications Union (ITU), the European Telecommunications Standards Institute (ETSI), and the Institute of Electrical and Electronics Engineers (IEEE), or by international forums like the 3rd Generation Partnership Project (3GPP) to offer In-Flight Connectivity. Providers using Indian or foreign satellite systems must obtain approval from the Department of Space.
The IFMC service provider must operate mobile communication services on aircrafts at a minimum altitude of 3,000 meters within Indian airspace to prevent interference with terrestrial mobile networks. However, Wi-Fi access can be enabled at any point during the flight when device use is permitted, not just after reaching 3,000 meters. This flexibility is intended to allow passengers to connect to Wi-Fi earlier in the flight. This amendment aims to ensure that passengers can access the internet while maintaining the safety standards critical to in-flight communication systems.
Implications
- Increased Data Security Needs: There will be a need for robust cybersecurity measures against potential threats and data breaches.
- Increased Costs: Airplanes will have to incur the initial costs for installing antennae. Since airfare pricing in India is market-driven and largely unregulated, these costing changes might find their way into ticket prices, making flight tickets more expensive.
- Interference Management: A framework regarding the conditions under which Wi-FI must be switched off to avoid interference with terrestrial communication systems can be determined by stakeholders and communicated to passengers.
- Enhanced Connectivity Infrastructure: Airlines may need to invest in better flight-connectivity infrastructure to handle increased network traffic as more passengers access Wi-fi at lower altitudes and for longer durations.
Conclusion
The Flight and Maritime Connectivity (Amendment) Rules, 2024, enhance passenger convenience and align India with global standards for in-flight connectivity while complying with international safety protocols. Access to the internet during flights and at sea provides valuable real-time information, enhances safety, and offers access to health support during aviation and maritime operations. However, new challenges including the need for robust cybersecurity measures, cost implications for airlines and passengers, and management of interference with terrestrial networks will have to be addressed through a collaborative approach between airlines, IFMC providers, and regulatory authorities.
Sources
- https://dot.gov.in/sites/default/files/2018_12_17%20AS%20IFMC_2.pdf?download=1
- https://dot.gov.in/sites/default/files/Amendment%20dated%2004112024%20in%20flight%20and%20maritime%20connectivity%20rules%202018%20to%20IFMC%20Service%20Provider.pdf
- https://www.t-mobile.com/dialed-in/wireless/how-does-airplane-wifi-work
- https://tec.gov.in/public/pdf/Studypaper/DA2GC_Paper%2008-10-2020%20v2.pdf
- https://www.indiatoday.in/india/story/wifi-use-flights-no-longer-linked-altitude-now-subject-permission-2628118-2024-11-05
- https://pib.gov.in/Pressreleaseshare.aspx?PRID=1843408#:~:text=With%20the%20repeal%20of%20Air,issue%20directions%20to%20such%20airline.
