
#FactCheck - AI Generated image of Virat Kohli falsely claims to be sand art of a child
Executive Summary:
The picture of a boy making sand art of Indian Cricketer Virat Kohli spreading in social media, claims to be false. The picture which was portrayed, revealed not to be a real sand art. The analyses using AI technology like 'Hive' and ‘Content at scale AI detection’ confirms that the images are entirely generated by artificial intelligence. The netizens are sharing these pictures in social media without knowing that it is computer generated by deep fake techniques.

Claims:
The collage of beautiful pictures displays a young boy creating sand art of Indian Cricketer Virat Kohli.


Fact Check:
When we checked on the posts, we found some anomalies in each photo. Those anomalies are common in AI-generated images.

The anomalies such as the abnormal shape of the child’s feet, blended logo with sand color in the second image, and the wrong spelling ‘spoot’ instead of ‘sport’n were seen in the picture. The cricket bat is straight which in the case of sand made portrait it’s odd. In the left hand of the child, there’s a tattoo imprinted while in other photos the child's left hand has no tattoo. Additionally, the face of the boy in the second image does not match the face in other images. These made us more suspicious of the images being a synthetic media.
We then checked on an AI-generated image detection tool named, ‘Hive’. Hive was found to be 99.99% AI-generated. We then checked from another detection tool named, “Content at scale”


Hence, we conclude that the viral collage of images is AI-generated but not sand art of any child. The Claim made is false and misleading.
Conclusion:
In conclusion, the claim that the pictures showing a sand art image of Indian cricket star Virat Kohli made by a child is false. Using an AI technology detection tool and analyzing the photos, it appears that they were probably created by an AI image-generated tool rather than by a real sand artist. Therefore, the images do not accurately represent the alleged claim and creator.
Claim: A young boy has created sand art of Indian Cricketer Virat Kohli
Claimed on: X, Facebook, Instagram
Fact Check: Fake & Misleading

Related Blogs
Executive Summary
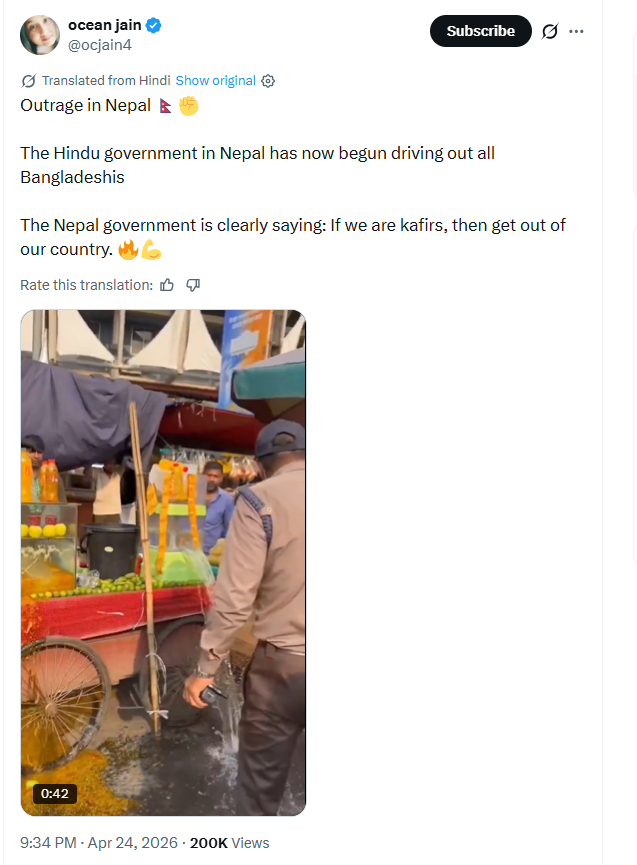
A video showing uniformed personnel removing street vendors and damaging roadside stalls is being circulated on social media with the false claim that the Nepal government has started expelling Bangladeshis from the country. The viral clip is around 49 seconds long and shows authorities clearing vendors from a public area. Nepali audio can also be heard in the background, which appears to have added to the misleading narrative.
However, an research by the CyberPeace Research Wing found that the claim is false. The video is not from Nepal, but from Bangladesh’s capital Dhaka, where authorities were carrying out an anti-encroachment operation near the National Stadium.
Claim:
The video was shared on X with a caption claiming that a Hindu-led government in Nepal had begun driving Bangladeshis out of the country.
Fact Check:
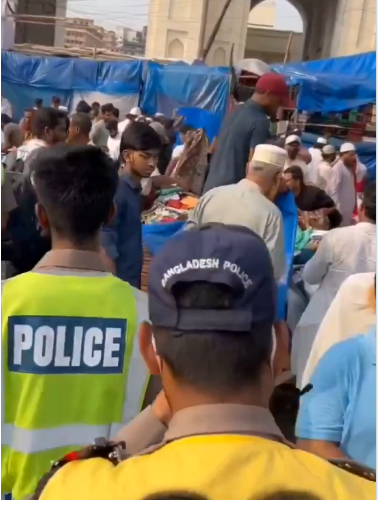
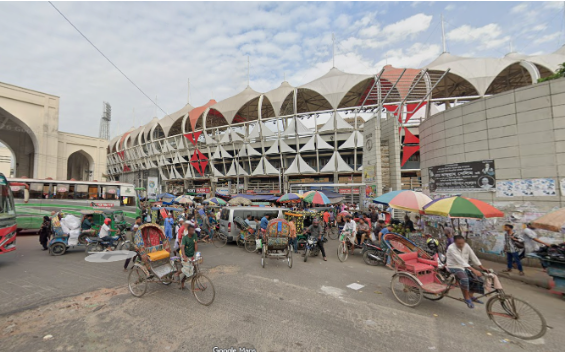
A close examination of the video revealed several signs contradicting the claim. Text written in Bengali can be seen at multiple places in the footage. The caps worn by uniformed personnel also appear to display “Bangladesh Police.” Investigators also noticed a stadium-like structure in the background. Comparing the visuals with street-view imagery available on Google Maps led to a match near the National Stadium area in Dhaka, Bangladesh.
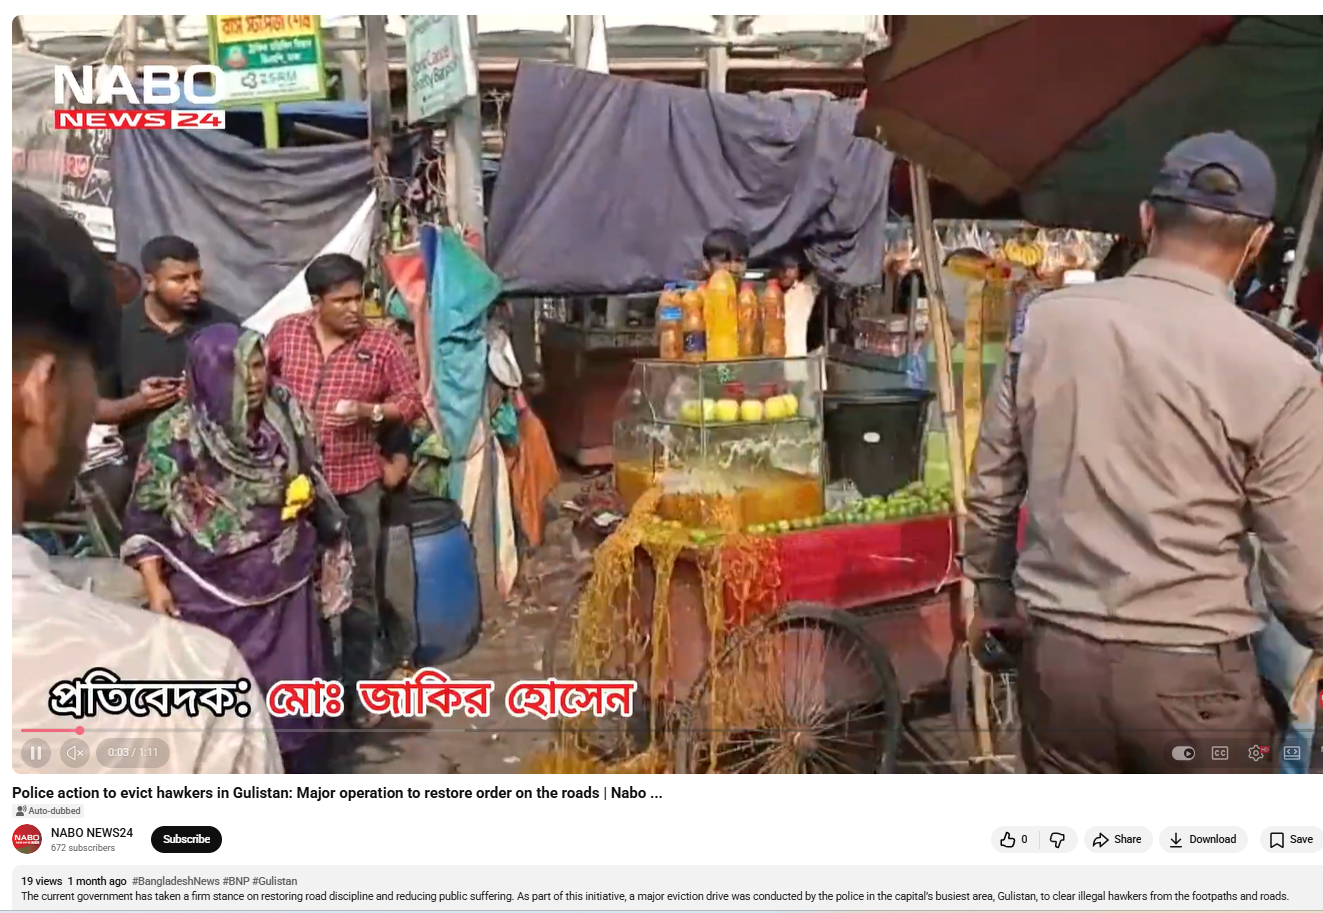
Further verification found a video uploaded on March 18, 2025, by a Bangladeshi news portal on YouTube containing scenes matching the viral clip. The caption described it as footage from an anti-encroachment drive in the Gulistan area of Dhaka.
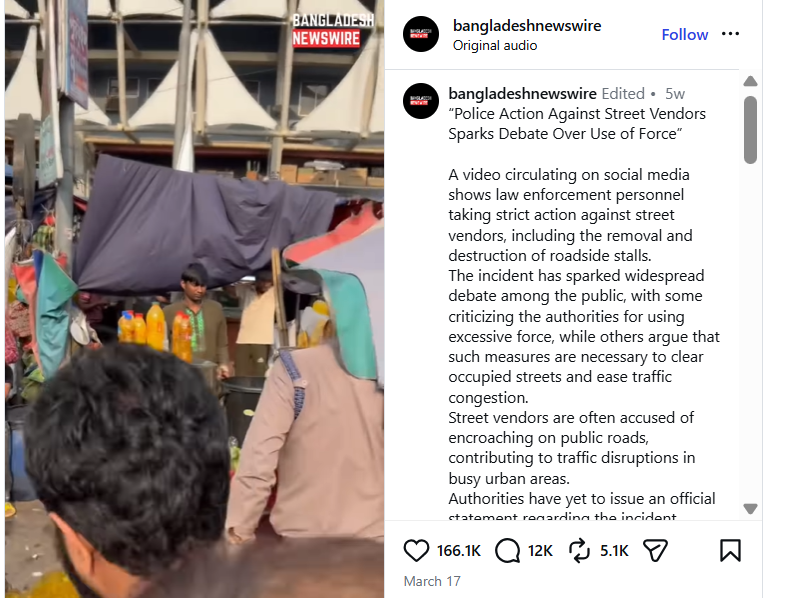
A similar version of the video was also found on a Bangladeshi Instagram account uploaded on March 17, where it was again described as police action against illegal encroachments. The video credit was attributed to a person named Zahir Rehan.
While the exact date of the original footage could not be independently confirmed, available evidence clearly links the video to Bangladesh and not Nepal.
Conclusion:
The viral claim that Nepal has begun expelling Bangladeshis is false. The video actually shows an anti-encroachment drive carried out by authorities in Dhaka, Bangladesh.
Introduction
India is operating on digital rails today. Even as UPI is set to hit over 130 billion transactions by 2025, it already makes up around 80% of retail payments flow by volume. That volume is really what it is all about: a single extra transaction is simply another attack surface, and fraud has correspondingly scaled up. FY 2024-25 alone saw an estimated 485 crore in losses to UPI-related fraud through 632,000 reported frauds. The response from the RBI has not been a single rulebook but a layered and dynamic regulatory infrastructure that currently spans banks, NBFCs, payment aggregators, card networks, and, by extension, the fintechs that connect into all of these components. Knowing why the infrastructure is shaped the way it is and what actual enforcement looks like is far more crucial than having a checklist in mind. This write-up moves beyond summarising the rules to outlining the thinking behind them, the latest trends shaping the segment and the reality of an implementation roadmap.
Why Has RBI Cybersecurity Compliance Become Non-Negotiable?
Three forces are converging on regulated entities at once:
1. The threat surface has outgrown legacy controls: Core banking systems were never designed for an ecosystem of APIs, third-party payment gateways, and unregulated fintech partners sitting on top of them. Every integration is a potential entry point, and attackers know it.
2. Financial stability is now a cyber question, not just a credit question: a prolonged outage at a large payment system operator doesn't just hurt one bank's balance sheet; it can freeze retail payments for hundreds of millions of people. RBI treats this as systemic risk, which is why its post-2020 directions lean so heavily on resilience (the ability to keep operating through an attack) rather than just prevention.
3. Enforcement has escalated: The RBI's May 2025 single order penalised five different banks, including levying a 97.80 lakh penalty on ICICI Bank with one part attributable to its late reporting of a cybersecurity incident and another to a lapse in account alert systems; this demonstrates this rise in intensity. Remember, under Sections 46 and 47A of the Banking Regulation Act 1949, the RBI has the power to levy penalties irrespective of the occurrence of an actual breach if an individual fails to comply with procedures like not properly assessing vendor access or reporting incidents late or failing to update crisis plans or timely reports. Now this is a significant development, an issue even in the absence of a full-scale 'hack'.
The Regulatory Architecture: What Actually Applies to Whom
Rather than one framework, regulated entities are governed by several overlapping directions depending on their category:
- Banks: The original RBI Cyber Security Framework requires board-approved cybersecurity policies, 24x7 Security Operations Centres, and defined incident reporting timelines.
- NBFCs: NBFCs were initially governed under the Master Direction on IT Framework for NBFC Sector, which escalates accordingly as per size of asset – the framework underwent substantial change in shape with the RBI notifying Cybersecurity, Technology Risk, Resilience and Assurance Framework directions, 2026 for NBFCs, which lays specific obligations based on tier level (NBFC-Base Layer, Middle Layer, Upper Layer & Top Layer entities) on issues like MIS reporting, fraud analytics & impact of incident reporting.
- PSOs: Non-bank Payment system Operators PSOs have been regulated under the Master Direction on Cyber Resilience and Digital Payment Security Controls, 2024 (July 2024). Card networks, payment aggregators, PPI issuers and other PSOs come under its umbrella, with staged compliance based on the volume/business size (large – NPCI, card networks and the largest PPI issuers will meet requirements on April 1, 2025; medium ones by April 1, 2026; and small ones by April 1, 2028).
- Other Bodies: IT Governance (on all regulated entities broadly) The Master Direction on Information Technology Governance, Risk, Controls and Assurance Practices, 2023, became effective on April 1, 2024, and has set basic benchmarks for information technology (IT) strategy committees, IT risk management processes & IT assurance functions.
Overall trends' information across all these is clear: escalating tier requirements as per size and board-led controls are mandatory; a conscious acceptance that there will inevitably be data breaches in the future; and increasing emphasis on response and recovery.
Governance: Where RBI Compliance Actually Starts
A recurring theme across every RBI direction is that cybersecurity cannot be delegated entirely to the IT department. The Board of Directors is expected to own information security risk, with oversight typically delegated to a board subcommittee that meets at least quarterly. A board-approved information security policy, reviewed annually, must define the following:
- Roles and responsibilities across the Board, senior management, and the CISO
- Processes to identify, assess, monitor, and manage cyber risk
- Employee and stakeholder training and awareness programs
RBI's own 2022 thematic review of IT governance across 20 banks found unmanaged third-party vendor access, with vendors retaining privileged access to core systems long after a project ended at more than half the institutions reviewed. That kind of gap is a governance failure as much as a technical one: it happens because nobody owns the review cycle, not because the firewall is misconfigured.
Key Technical and Operational Controls
Once governance is in place, RBI's expectations translate into concrete control domains:
Infrastructure and access hardening: Network segmentation, endpoint protection, server hardening baselines, and multi-factor authentication for privileged access. Access reviews should be continuous or, at minimum, periodic, enforcing least privilege and separation of duties, not a one-time onboarding checkbox.
Vulnerability and patch management: Regular vulnerability scanning, risk-prioritised remediation, and a documented process for feeding vulnerability data into risk decisions, not just a scanner report sitting in an inbox.
Data security and localisation: Encryption at rest, in transit, and during processing; sound key management; data classification and masking; and adherence to the RBI's data localisation requirements for payment data.
Vendor and third-party risk: This has become one of the sharpest areas of regulatory focus. The 2024 PSO Master Directions explicitly require oversight of "unregulated entities" in the payment chain like payment gateways, third-party service providers, and vendors with due diligence, contractual security clauses, and ongoing monitoring baked in. For a bank or fintech, this means your compliance posture is only as strong as your weakest vendor's; the RBI increasingly holds the regulated entity accountable for its partners' failures, not just its own.
Security operations and incident response: 24x7 SOC capability, threat intelligence integration, and tested incident response plans via tabletop exercises and simulated attacks. A Cyber Crisis Management Plan (CCMP) drafted once and never rehearsed is, in practice, treated by RBI examiners as functionally absent.
Incident Reporting
This is where two separate regulatory clocks run in parallel, and conflating them is a common compliance mistake:
- RBI requirements: Regulated entities will normally have around 2-6 hours of detection to report most security incidents to the RBI with follow-up notifications as and when the nature of the incident unfolds.
- CERT-In's 6-hour rule: The CERT-In Directions dated April 2022 stipulate that every body corporate, which includes any bank, NBFC or payment aggregator, is obligated to report specified categories of cyber incidents to CERT-In within 6 hours of noticing them and not after fully confirming details at an additional 6 hours after noticing them. CERT-In directions also mandated that ICT system clocks are to be synced to NIC/NPL time servers, and system logs are to be maintained for a rolling 180 days within India.
- The Digital Personal Data Protection Act overlay: In the case of a data breach involving personal data, there will additionally be a 72-hour notification obligation from the data fiduciary to the Data Protection Board under the Digital Personal Data Protection Act, 2023, which runs in parallel to, and not in substitution of, the CERT-In time.
The practical consequences: If an SOP for incident response only maps one regime, then it would fail in an actual incident. We need a single intake process whereby multiple notification tracks are automatically triggered at the precise time an incident is detected, given that the inability to report "because we were still figuring it out" does not constitute an acceptable justification for a late notification under either regime.
Why Penetration Testing Sits at the Center of Compliance
RBI's VAPT (Vulnerability Assessment and Penetration Testing) mandate isn't a box-ticking annual scan. It's meant to validate, under real attack conditions, whether the governance and technical controls described above actually hold up. Automated scanning finds known vulnerabilities; penetration testing, ideally combining automated coverage with manual, business-context-aware testing, finds the logic flaws, chained exploits, and privilege escalation paths that scanners miss and that attackers actually use.
For most regulated entities, a realistic testing cadence looks like:
- Semi-annual vulnerability assessments across critical systems
- Annual (at minimum) penetration testing of applications, networks, and infrastructure supporting payment and customer-data systems
- Testing triggered by events before go-live, after major changes, and post-deployment.
- Documented remediation cycles and rescans, with reports mapped directly to the relevant compliance clauses for audit purposes
The Cost of Getting It Wrong
RBI's enforcement history grounds the financial impact of enforcement actions. In addition to the May 2025 fines levied on ICICI, Axis, IDBI, Bank of Baroda and Bank of Maharashtra, the RBI's published Enforcement Guidelines differentiate three levels of severity; procedural breaches such as delayed policy review or late incident notifications usually warrant 10 lakh to 1 crore fines plus formal reprimands and remediation orders with deadlines. Recurring governance breaches go farther than fines, resulting in restrictions on business activities and more stringent supervisory reporting, with egregious breaches leading to inclusion under the RBI's Prompt Corrective Action regime. Penalty orders are also publicly available, and the resulting toll on customer trust, partner trust, and investor confidence often dwarfs the fines.
A Practical Implementation Roadmap
For an organisation building or maturing its RBI compliance programme, a sensible sequence looks like this:
- Establish board-level ownership first: Form or formalise the Board IT/Risk sub-committee, appoint or empower a CISO with real authority, and get the information security policy formally approved, and this is the foundation every RBI examiner checks first.
- Mapping: A mid-sized NBFC, a large payment aggregator, and a scheduled commercial bank face different, overlapping obligations. Get this scoping wrong and you'll either over-engineer or leave gaps.
- Secure third-party access: Audit every vendor with system access, revoke stale privileges, and build vendor security clauses into contracts going forward, not retroactively.
- Build one incident response SOP: Run one compiled playbook that satisfies RBI, Cert-In and DPDP.
- Schedule and actually rehearse tabletop exercises: not just write a CCMP and file it away.
- Institutionalise VAPT as a continuous, risk-triggered programme rather than an annual compliance event, and ensure reports are structured to map directly onto RBI's compliance clauses for audit readiness.
- Track the regulatory calendar actively: 2024–2026 has brought new NBFC directions, PSO phase-ins, and ITG-RC&AP obligations in quick succession, and the pace shows no sign of slowing.
Conclusion
RBI's shift from perimeter-focused prevention to a risk-based, resilience-first model reflects a broader reality: in a digital payments ecosystem processing billions of transactions a month, breaches are not a hypothetical to plan around; they're an operational certainty to plan for. The frameworks discussed here, cyber resilience directions, IT governance mandates, CERT-In's reporting clock and the new NBFC cybersecurity directions aren't separate hurdles to clear individually. They're converging into a single expectation: that regulated entities can detect an incident quickly, contain it, recover fast, and prove with documentation, tested plans, and independent penetration test evidence that they were ready for it in the first place.
For banks, NBFCs, and fintechs operating in India today, that readiness is no longer just a regulatory requirement. It's the baseline cost of operating in the financial system at all.
References
Sources
- Astra Security — RBI Cybersecurity Compliance Checklist for Banks & NBFCs in 2026: https://www.getastra.com/blog/compliance/rbi-cybersecurity-compliance-checklist/
- TaxGuru — RBI Issues NBFC Cybersecurity and Technology Risk Directions, 2026: https://taxguru.in/rbi/rbi-issues-nbfc-cybersecurity-technology-risk-directions-2026-governance-framework.html
- Mondaq — Cyber Resilience and Digital Payment Security Governance (Master Directions, 2024): https://www.mondaq.com/india/fin-tech/1527836/cyber-resilience-and-digital-payment-security-governance-a-step-towards-secured-payments-systems
- TaxGuru — Master Directions on Cyber Resilience & Digital Payment Security Controls for Non-bank PSOs: https://taxguru.in/rbi/master-directions-cyber-resilience-digital-payment-security-controls-non-bank-payment-system-operators.html
- CyberNX — Ultimate Guide on RBI Master Directions for Cyber Resilience: https://www.cybernx.com/rbi-master-directions-guide/
- SIRI Law LLP — A Comprehensive Guide to India's CERT-In 6-Hour Cyber Incident Reporting Mandate: https://sirilawllp.com/a-comprehensive-guide-to-indias-cert-in-6-hour-cyber-incident-reporting-mandate/
- CreativeCyber — CERT-In 6-Hour Incident Reporting SOP for Indian Banks & NBFCs: https://creativecyber.in/resources/cert-in-6-hour-incident-reporting/
- BW Businessworld — RBI Slaps Penalties on ICICI, Axis and Three Others Over Compliance Failures (May 2025): https://www.businessworld.in/article/rbi-slaps-penalties-on-icici-axis-three-others-over-compliance-failures-555643
- FluxForce — RBI Cyber Framework: Banks' Requirements & Penalties: https://www.fluxforce.ai/regulations/rbi-cyber-security-framework-banks
- MYITMANAGER — RBI Cybersecurity Guidelines 2026: What Banks and NBFCs Must Do: https://myitmanager.in/rbi-cybersecurity-guidelines-2026-banks-nbfcs/
Executive Summary
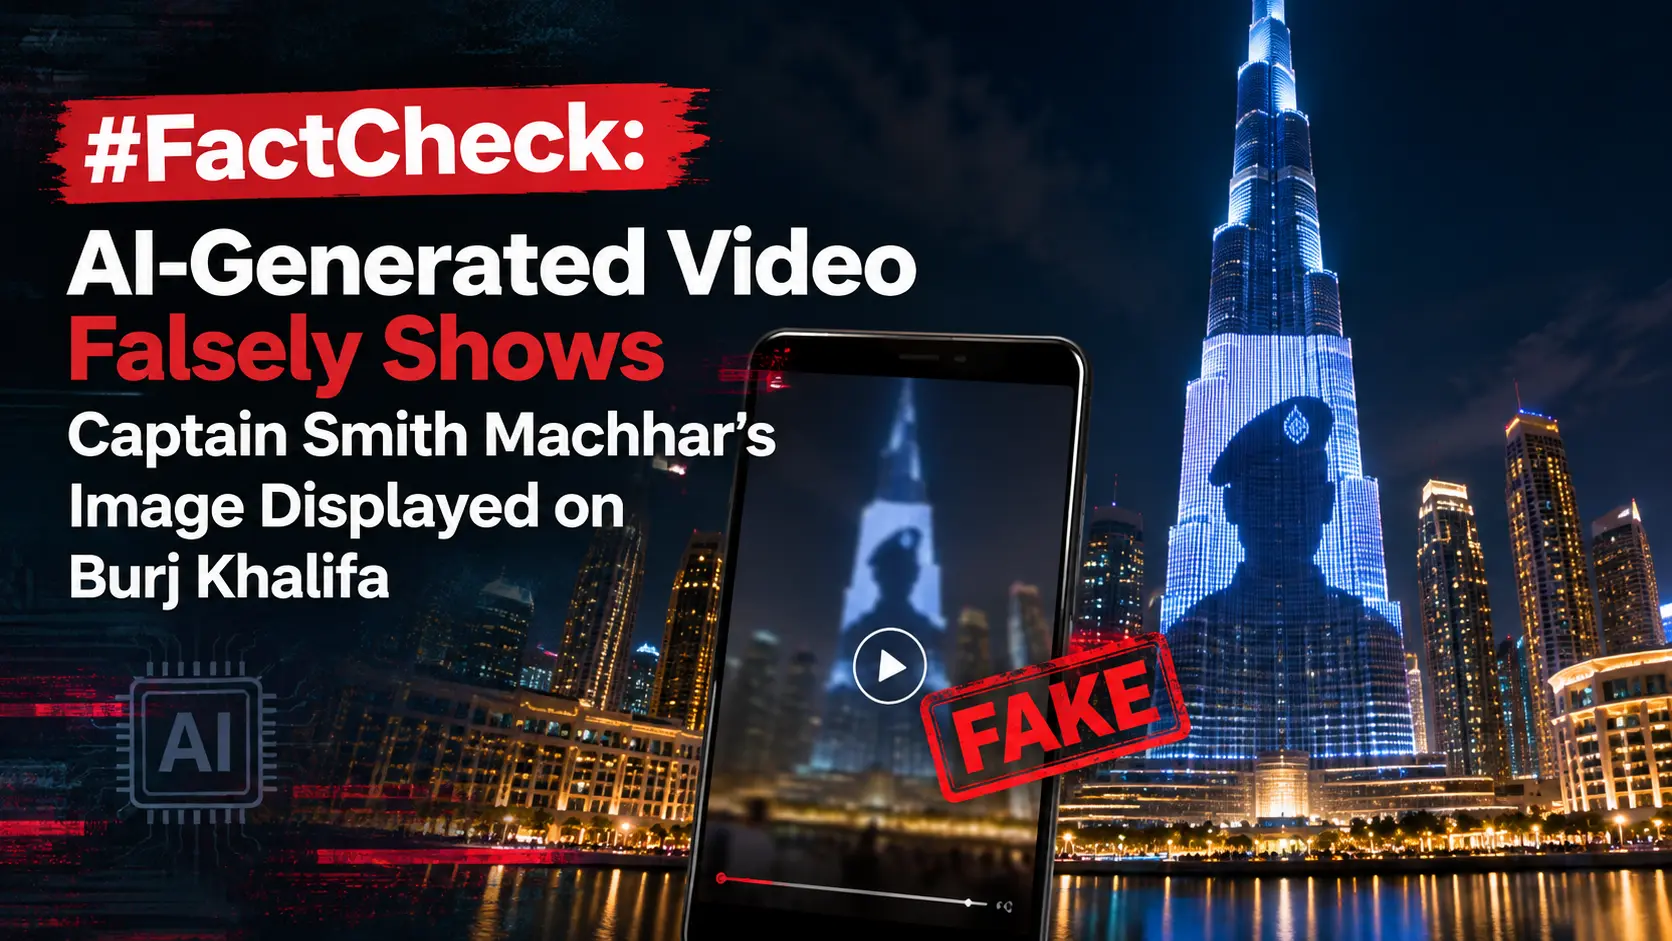
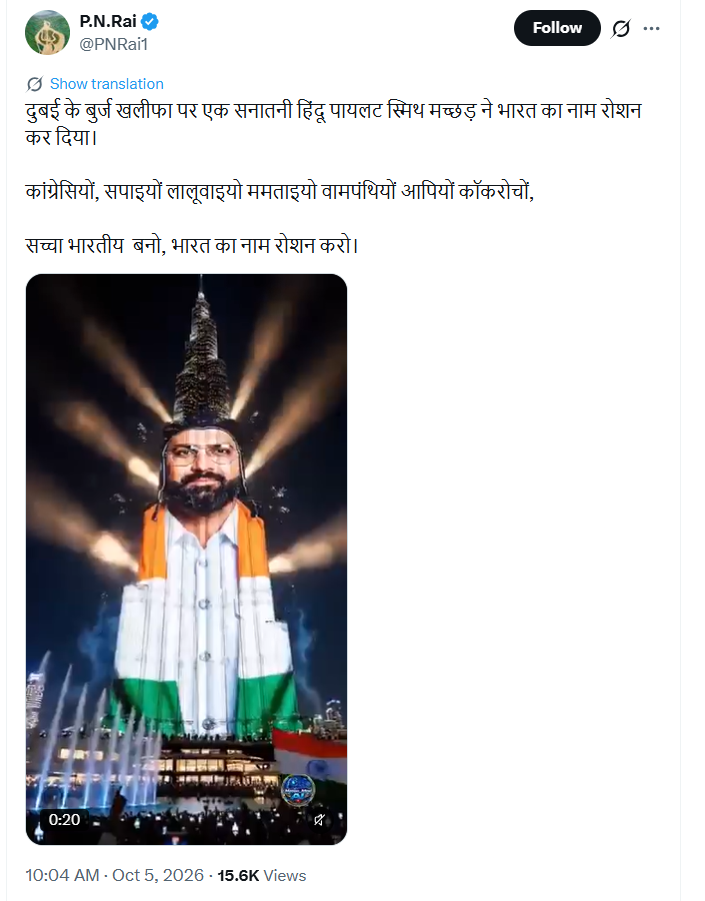
On September 30, 2026, reports emerged that Captain Smith Machhar, the Indian pilot of flydubai flight FZ1073 travelling from Dubai to Tel Aviv, was attacked by his co-pilot in the cockpit. Despite sustaining serious injuries, Captain Machhar reportedly managed to land the aircraft safely, saving the lives of all 174 passengers. Following the incident, a video is going viral on social media with the claim that a picture of Captain Smith Machhar was displayed on Dubai’s Burj Khalifa in his honour.
However, CyberPeace Research found the claim to be false. Our research found that the viral video is AI-generated and is being circulated on social media with a misleading claim.
Claim:
A user on the social media platform X (formerly Twitter) shared the viral video on October 5, 2026, with the caption: “A Sanatani Hindu pilot, Smith Machhar, has made India proud on Dubai’s Burj Khalifa. Congressis, Samajwadis, Lalu supporters, Mamata supporters, Leftists, AAP supporters and cockroaches, become true Indians and make India proud.” The post link, archive link and screenshot are provided below.
https://x.com/PNRai1/status/2106966191386611900
https://ghostarchive.org/archive/3RroW
Fact Check
To verify the viral claim, we conducted a Google search using relevant keywords. During the search, we did not find any credible media report confirming the claim.In the next stage of our research, we closely examined the video.
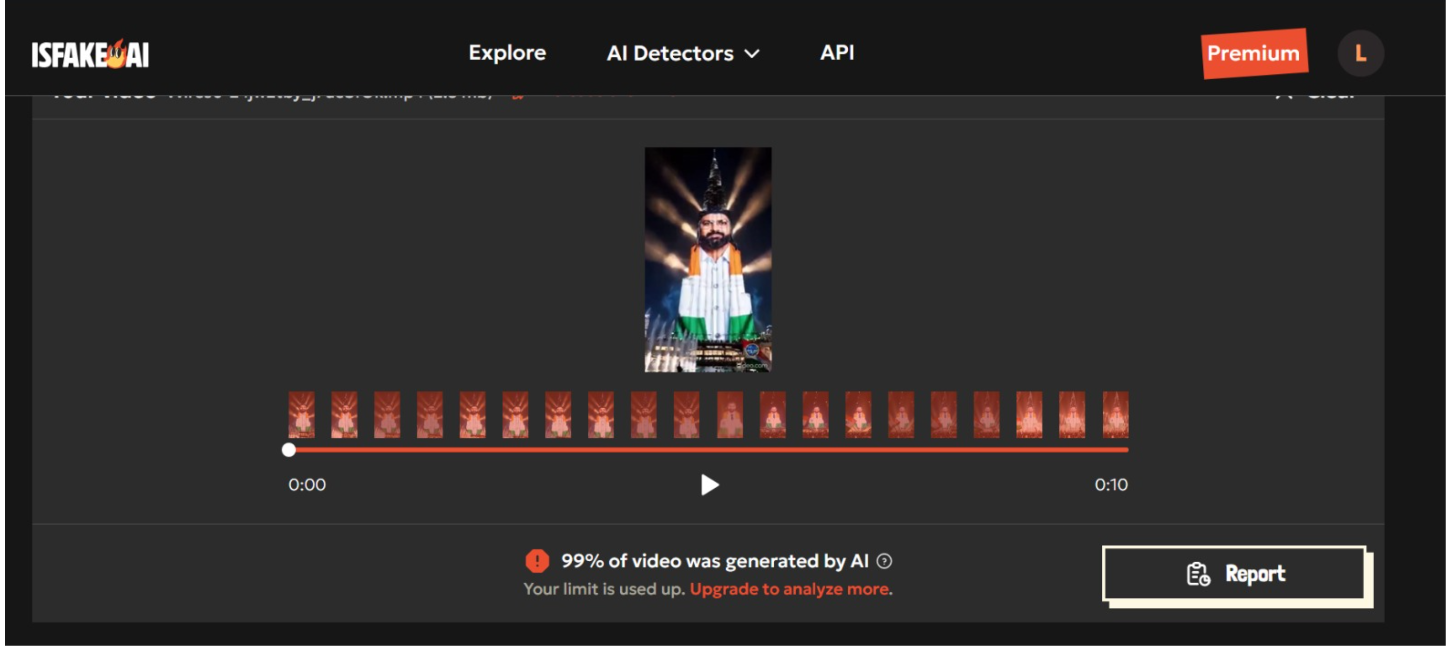
We noticed several inconsistencies that raised suspicions that it was AI-generated. In the video, the building’s texture appears to blend and shift strangely into a person’s clothing. Such changes do not appear natural or consistent with a genuine video. We then analysed the viral video using the AI detection tool ISFAKEAI. According to the results, the viral video is 99 per cent AI-generated.
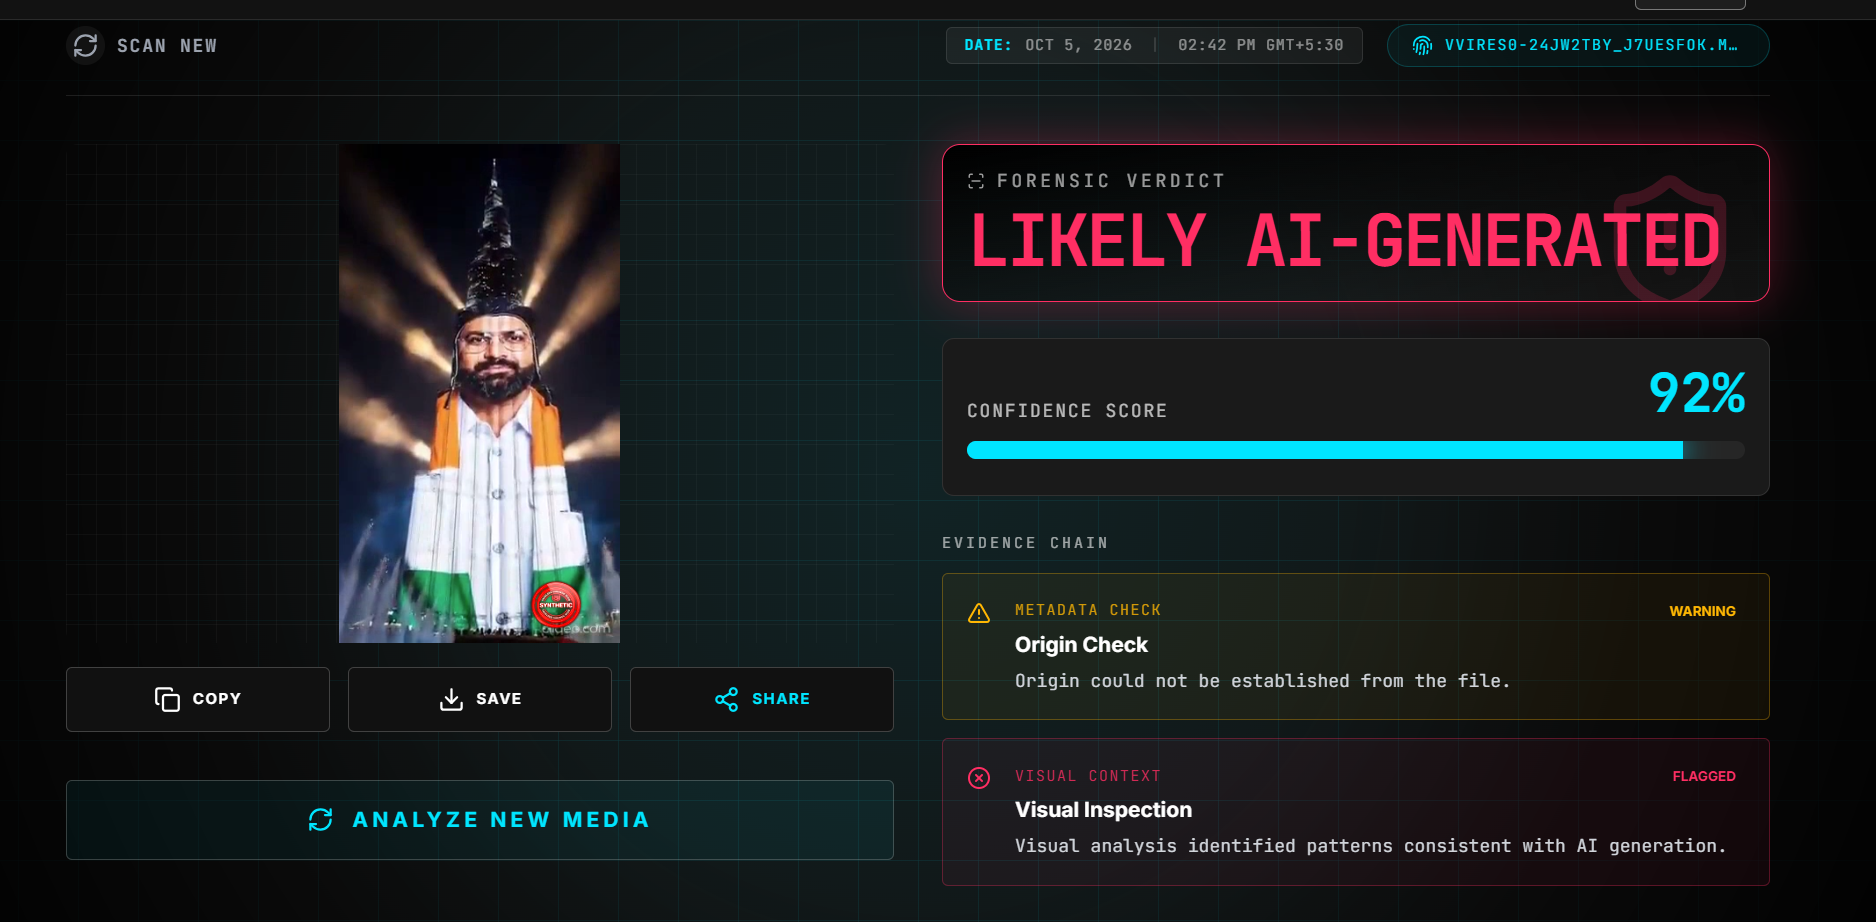
In the next stage of our research, we analysed the viral video using the AI detection tool FauxLens. According to the results, the viral video is 92 per cent AI-generated.
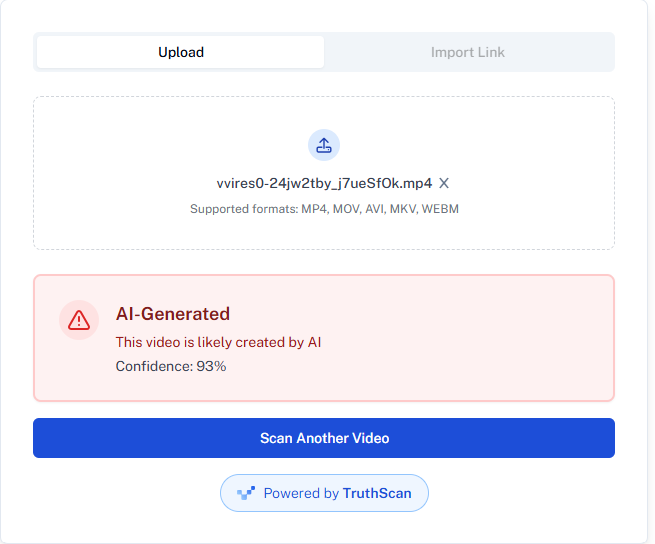
At the end of our research, we analysed the viral video using the AI detection tool Undetectable AI. According to the tool’s results, the viral video is 93 per cent AI-generated.
Conclusion
Our research found that the viral video is AI-generated and is being circulated on social media with a misleading claim. The video does not provide authentic evidence that a picture of Captain Smith Machhar was displayed on the Burj Khalifa. The visual inconsistencies observed in the video, along with the results of multiple AI detection tools, further indicate that the video has been digitally created or manipulated using AI.
