
#FactCheck - A misleading video falsely shows Former Prime Minister of India Pandit Jawaharlal Nehru admitting he had no role in India's independence
Executive Summary:
A misleading video has been widely shared online, falsely portraying Pandit Jawaharlal Nehru stating that he was not involved in the Indian independence struggle and he even opposed it. The video is a manipulated excerpt from Pandit Nehru’s final major interview in 1964 with American TV host Arnold Mich. The original footage available on India’s state broadcaster Prasar Bharati’s YouTube channel shows Pandit Nehru discussing about Muhammad Ali Jinnah, stating that Jinnah did not participate in the independence movement and opposed it. The viral video falsely edits Pandit Nehru’s comments to create a false narrative, which has been debunked upon reviewing the full, unedited interview.

Claims:
In the viral video, Pandit Jawaharlal Nehru states that he was not involved in the fight for Indian independence and even opposed it.


Fact check:
Upon receiving the posts, we thoroughly checked the video and then we divided the video into keyframes using the inVid tool. We reverse-searched one of the frames of the video. We found a video uploaded by Prasar Bharati Archives official YouTube channel on 14 May 2019.

The description of the video reads, “Full video recording of what was perhaps Pandit Jawaharlal Nehru's last significant interview to American TV Host Arnold Mich Jawaharlal Nehru's last TV Interview - May 1964e his death. Another book by Chandrika Prasad provides a date of 18th May 1964 when the interview was aired in New York, this is barely a few days before the death of Pandit Nehru on 27th May 1964.”
On reviewing the full video, we found that the viral clip of Pandit Nehru runs from 14:50 to 15:45. In this portion, Pandit Nehru is speaking about Muhammad Ali Jinnah, a key leader of the Muslim League.
At the timestamp 14:34, the American TV interviewer Arnold Mich says, “You and Mr. Gandhi and Mr. Jinnah, you were all involved at that point of Independence and then partition in the fight for Independence of India from the British domination.” Pandit Nehru replied, “Mr. Jinnah was not involved in the fight for independence at all. In fact, he opposed it. Muslim League was started in about 1911 I think. It was started really by the British encouraged by them so as to create factions, they did succeed to some extent. And ultimately there came the partition.”
Upon thoroughly analyzing we found that the viral video is an edited version of the real video to misrepresent the actual context of the video.
We also found the same interview uploaded on a Facebook page named Nehru Centre for Social Research on 1 December 2021.

Hence, the viral claim video is misleading and fake.
Hence, the viral video is fake and misleading and netizens must be careful while believing in such an edited video.
Conclusion:
In conclusion, the viral video claiming that Pandit Jawaharlal Nehru stated that he was not involved in the Indian independence struggle is found to be falsely edited. The original footage reveals that Pandit Nehru was referring to Muhammad Ali Jinnah's participation in the struggle, not his own. This explanation debunks the false story conveyed by the manipulated video.
- Claim: Pandit Jawaharlal Nehru stated that he was not involved in the struggle for Indian independence and even he opposed it.
- Claimed on: YouTube, LinkedIn, Facebook, X (Formerly known as Twitter)
- Fact Check: Fake & Misleading

Related Blogs
CyberPeace | Automotive Cybersecurity & Digital Forensics
Introduction
After a crash, the story usually comes from the driver, a witness or a police report. But a modern vehicle can leave another version behind - a digital one. An Event Data Recorder (EDR), commonly called a car's black box, can preserve selected information from the seconds around a crash. NHTSA describes EDRs as recording vehicle dynamics, driver inputs, crash characteristics, restraint status and some post-crash information.[1] The exact fields depend on the vehicle. A black box is not a magical device that records everything; it is one evidence source inside a much larger vehicle.
A modern vehicle can also contain safety controllers, diagnostic interfaces, ADAS, telematics and software-update systems. For an investigator, the question is what evidence can be linked to the EDR and what that combined record can actually support.
What Is Actually in the Black Box?
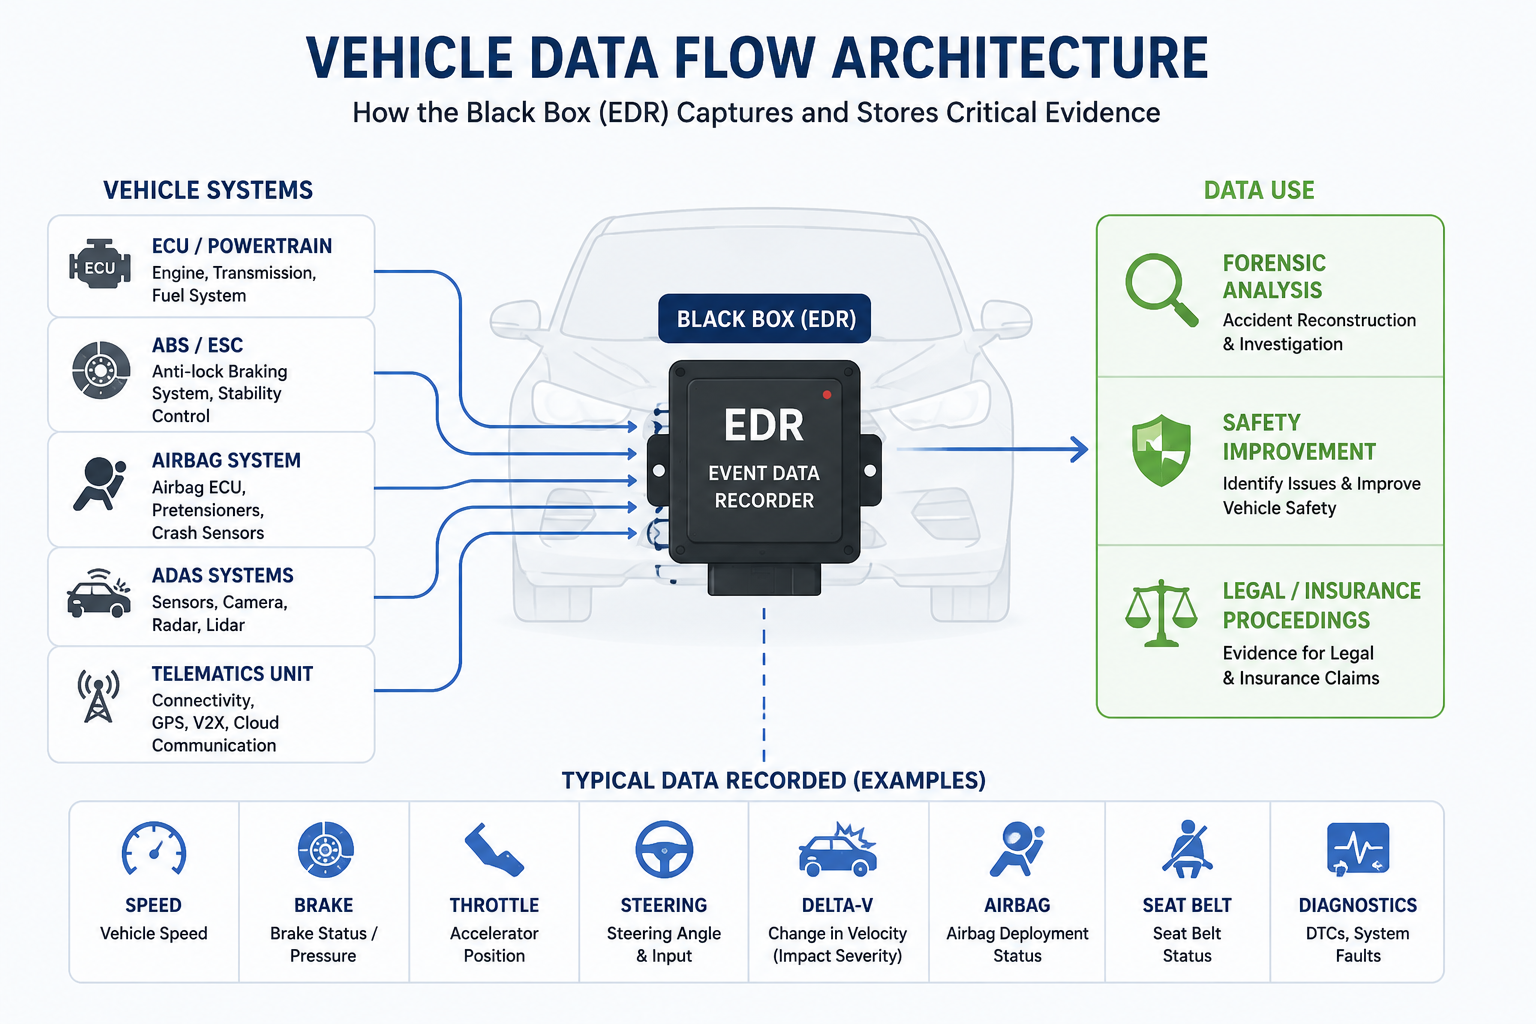
An EDR is best understood as a short event record, not a continuous driving diary. Depending on the vehicle and its configuration, forensic extraction may reveal items such as speed, acceleration, delta-V, engine RPM, throttle position, brake status, steering input, ABS or stability-control activity, seat-belt status and airbag or restraint events. NHTSA's published EDR material shows that data elements can include longitudinal and lateral acceleration, delta-V, vehicle speed, engine speed, throttle, service-brake status, roll/pitch/yaw information and steering input.[2] Do not overread the data: A field that exists in one model should not automatically be assumed to exist in another. A forensic report must identify exactly which module and fields were available and actually recovered.
What Can a Forensic Examination Recover?
A Brake Failure Example
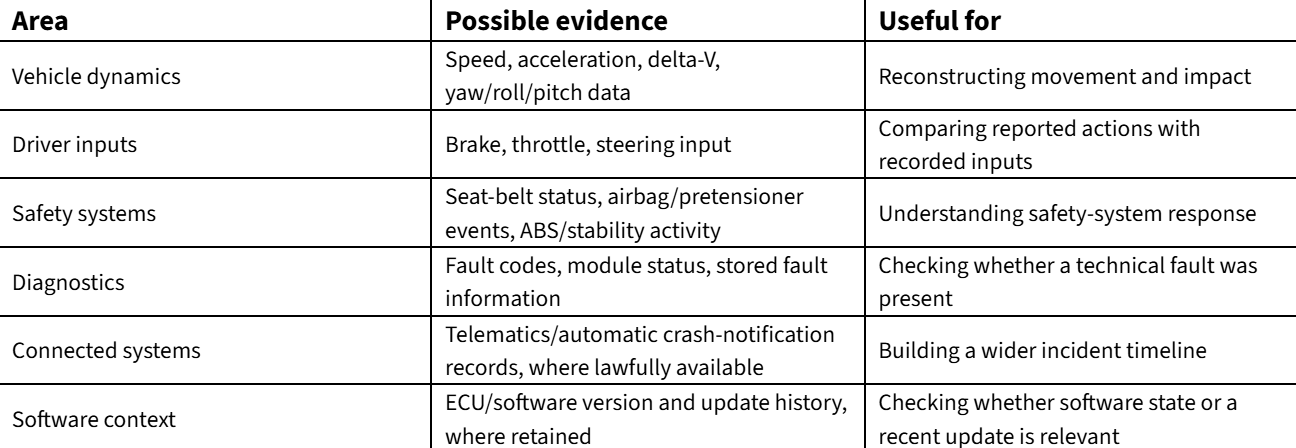
Consider a driver who reports: “I pressed the brake, but nothing happened.” The statement should be preserved, but a forensic investigation should test it. Was brake status captured? What was the speed before the event? Did ABS activate? What were the acceleration and delta-V patterns? Were there relevant fault codes? Was the vehicle recently repaired or updated? Suppose the recovered records show a brake input, ABS activity and a change in vehicle speed before impact. That does not prove the brakes were mechanically perfect. It does, however, make the sentence “nothing happened” too simple. Conversely, a relevant fault appearing just before the event may give investigators a stronger lead. The important part is the comparison: human account, vehicle record, physical evidence and technical history should be examined together.
Smart Vehicles, Digital Evidence and Cybersecurity Investigation
A connected vehicle can communicate through cellular networks, Bluetooth, Wi-Fi, mobile applications, workshop tools and cloud services. If unusual activity appears around a safety-critical incident, investigators may need to look beyond the EDR. Useful questions include:
• Was there unusual diagnostic or service activity before the incident?
• Was a software update or configuration change recently applied?
• Do timestamps from different modules line up, or is there clock drift?
• Can the extracted record be tied back to the original vehicle and module?
• Is there a non-cyber explanation - such as a hardware fault or software defect - that fits the evidence better?
The mindset matters: A cyberattack should be a conclusion supported by evidence, not the default explanation for strange vehicle behaviour.
The Forensic View: From Data to Evidence
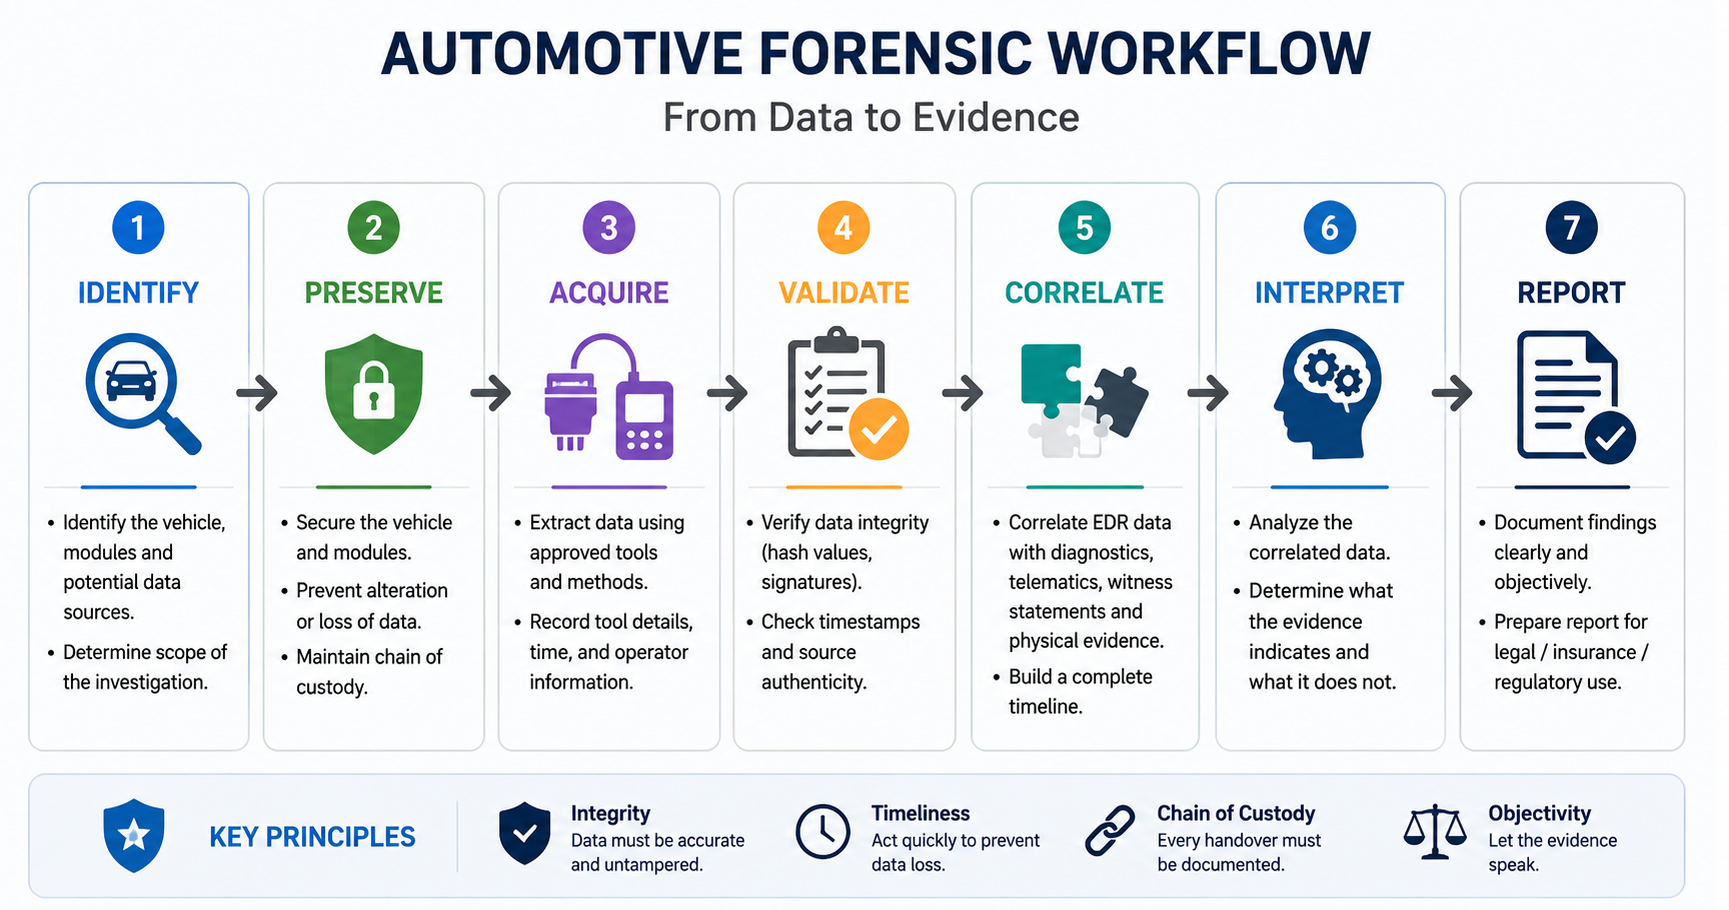
Automotive forensics is not simply plugging in a tool and exporting a report. The investigator should document the vehicle identity, module involved, extraction method, tool version, acquisition time and evidence-preservation steps. The goal is to make the work repeatable and defensible.
• Identify the relevant modules and evidence sources.
• Preserve the vehicle and extracted data against unnecessary alteration.
• Acquire data using a documented and appropriate method.
• Validate provenance, integrity, timestamps and completeness.
• Correlate EDR, diagnostics, software history, connected records and physical evidence.
• Report both findings and uncertainty.
A useful forensic rule: “Recorded” does not mean “proven.” Evidence becomes persuasive when its source, integrity and context are clear.
What the Law and Standards Are Changing
India is moving toward a more formal automotive cybersecurity lifecycle. IS-189 focuses on vehicle cybersecurity and the Cyber Security Management System (CSMS), while AIS-190 deals with software updates and the Software Update Management System (SUMS).[4][5] The wider statutory and type-approval framework is provided by the Motor Vehicles Act, 1988 and the Central Motor Vehicles Rules, 1989. For vehicle prototypes, Rule 126 provides for testing and approval by authorized testing agencies.[6][7]
In June 2026, the Ministry of Road Transport and Highways (MoRTH) came out with draft G.S.R. 503(E). The draft proposes new CMVR Rules 125-T and 125-U covering cybersecurity and software-update requirements. Since G.S.R. 503(E) is still a draft notification, its proposed requirements and the dates from which they may apply should be verified with the latest final notification before treating them as applicable law.[8]
At the international level, UN Regulation No. 155 addresses vehicle cybersecurity, while UN Regulation No. 156 covers software updates and their management.[9][10] This matters to forensics because lifecycle cybersecurity creates an expectation that manufacturers should be able to understand and manage security risks over time. In other words, logs, software-state information, vulnerability records and incident evidence can become part of the security story, not merely post-incident paperwork.
The Real Takeaway
The black box is valuable because it can reduce guesswork. It may tell us how fast the vehicle was moving, whether the driver applied the brake, how the vehicle responded, and what certain safety systems were doing around the event. But it rarely answers the whole case on its own. The strongest investigation is built by joining several pieces: EDR data, diagnostics, software context, connected-system evidence and what was found at the crash scene.
For cybersecurity professionals, the lesson is simple: a secure vehicle should not only resist attacks. It should also leave trustworthy evidence when something goes wrong. Good access controls, reliable timestamps and careful evidence handling help turn “something failed” into a defensible explanation.
Conclusion
The phrase “car black box” sounds simple, but the evidence behind it is not. An EDR can preserve a small but valuable window into a crash. During forensic examination, investigators may also be able to recover diagnostic, safety-system, software and connected-vehicle information, depending on the vehicle and what has been retained. The job is not to collect the largest possible amount of data. It is to collect the right data, preserve it properly and understand what each record can - and cannot - prove.
That is where automotive cybersecurity and digital forensics meet. As vehicles become more connected and software-driven, the ability to reconstruct an incident becomes part of security itself.
References
1. National Highway Traffic Safety Administration (NHTSA), Event Data Recorder (EDR) overview and research resources.
2. NHTSA, Use of Event Data Recorder (EDR) Technology for Highway Crash Data Analysis.
3. NHTSA, Light-Vehicle Event Data Recorder Technologies Update.
4. Automotive Research Association of India (ARAI), AIS-189, Approval of Vehicles with Regards to Cyber Security and Cyber Security Management System, April 2024.
5. Automotive Research Association of India (ARAI), AIS-190, Approval of Vehicles with Regards to Software Update and Software Update Management System, April 2024.
6. Government of India, Motor Vehicles Act, 1988.
7. Government of India, Central Motor Vehicles Rules, 1989, Rule 126.
8. Ministry of Road Transport and Highways, G.S.R. 503(E), 17 June 2026, draft Central Motor Vehicles (Amendment) Rules concerning cybersecurity and software updates.
9. UNECE, UN Regulation No. 155, Cyber Security and Cyber Security Management System.
10. UNECE, UN Regulation No. 156, Software Update and Software Update Management System.
11. NIST, SP 800-86, Guide to Integrating Forensic Techniques into Incident Response.
Executive Summary
A video circulating on social media claims that Iran’s new Supreme Leader Mojtaba Khamenei has passed away, with users attributing the claim to American sources. However, research by the CyberPeace found the claim to be false. Our research confirms that Mojtaba Khamenei is alive and in good health.
Claim
A Facebook user shared the viral video, claiming that Iran’s new Supreme Leader Mojtaba Khamenei had died.
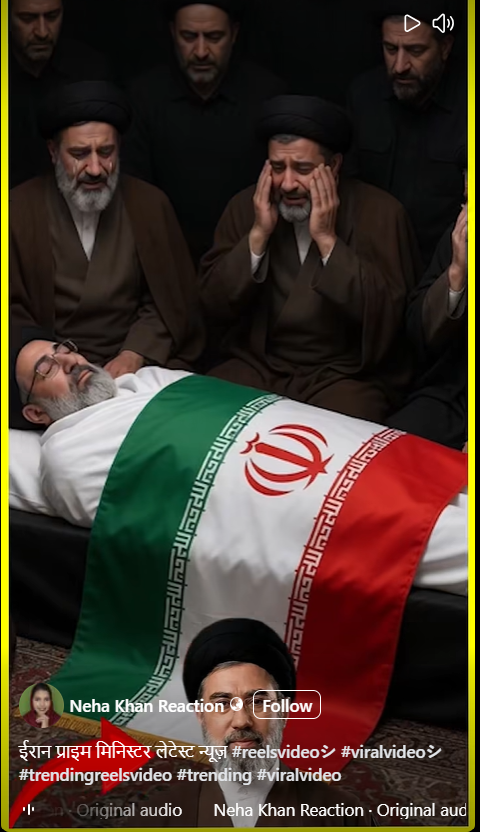
Fact Check
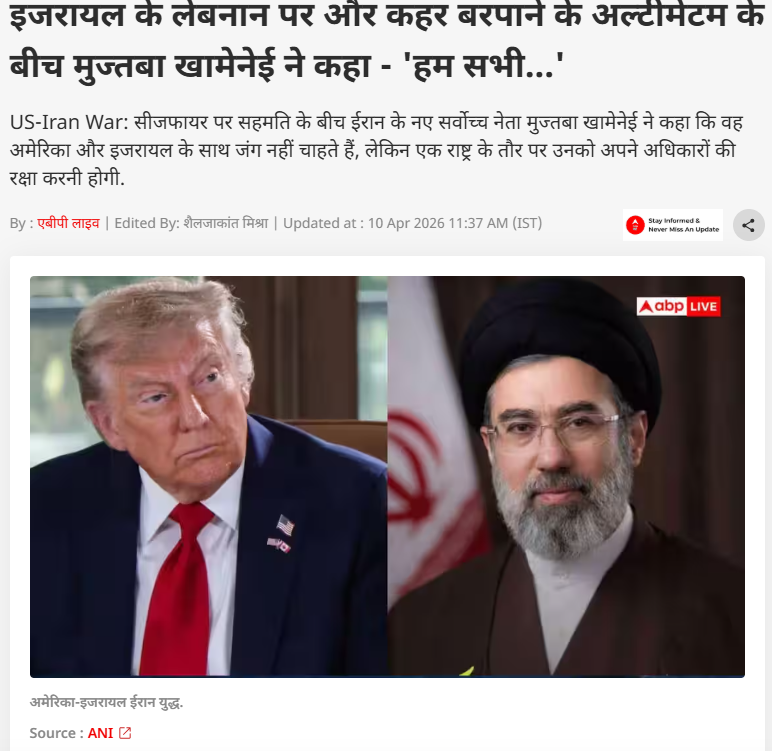
To verify the claim, we conducted keyword searches on Google but found no credible media reports confirming his death. Further research led us to a report published on April 10, 2026, by ABP News. According to the report, amid discussions around a ceasefire, Mojtaba Khamenei issued a statement saying that Iran does not seek war with the United States or Israel, but as a nation, it must defend its rights.
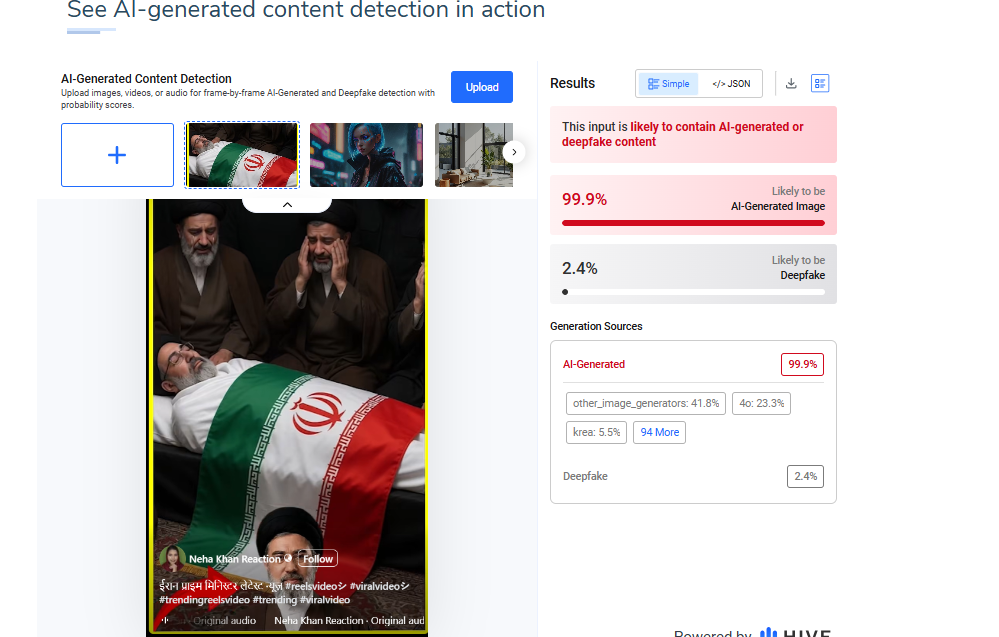
Additionally, the image used in the viral video was analyzed using the AI detection tool HIVE Moderation. The results indicated a 99% probability that the image is AI-generated.
Conclusion
The viral claim is false and misleading. There is no credible evidence to suggest that Mojtaba Khamenei has died. On the contrary, recent verified reports confirm that he is alive and has even issued public statements on ongoing geopolitical developments. The widespread circulation of this claim appears to be driven by misinformation, amplified through social media without verification. The use of AI-generated visuals further adds to the confusion, making the content appear authentic at first glance.

Introduction
Recently, the Delhi Police arrested a licensed telecom PoS agent, who identified himself as “Shivam Telecom," from a roadside kiosk adjacent to Hindu Rao Hospital. On the face of it, the headline may have simply read, “One man, one arrest." However, beneath that arrest is the unsettling story of a fully legitimate retail shop actively forging other people’s identification documents into weapons, one SIM card at a time, for as little as ₹500-600 each. This is not an account of an isolated offender; it is a peek into the vulnerability of SIM card security for typical end-users and the reasons why every mobile phone subscriber must pay attention to the unseen journey of his number.
Why SIM Security Matters Now
Erstwhile, a SIM card was only a simple device for sending text messages and making calls. Today, however, it’s also a direct link to most of our lives online, be it online banking to verify it through one-time passwords (OTP) or Unified Payments Interface (UPI); social media platforms; or email accounts to reset a forgotten password, two-factor authentications (2FA), or even numerous other online services. Therefore, losing a SIM card and getting it fraudulently issued under your name, or criminals accessing your identity to buy a SIM, can be a serious cause of concern, as they can then impersonate you, conduct various frauds, bypass checks, or commit acts that can lead to you being wrongly implicated.
According to the investigation, criminals were procuring SIM cards through the authorized outlets of telecom companies, not unlicensed dealers. This clearly proves a deficiency in the Know Your Customer (KYC) process for the SIM card activation. The situation, however, is worse and is also highlighted by the fact that more than 21 lakh mobile numbers from the more than 114 crore mobile numbers reviewed under the Sanchar Saathi initiative launched by the department of telecommunications (DoT) were associated with fake or invalid identity documents. A state police chief of Tamil Nadu claims that 90% of the cyber fraud cases involved SIM cards obtained through misused identity documents.
How Illegally Activated SIMs Fuel Everyday Scams?
Once a SIM is activated using someone else's identity documents or biometric data, without their knowledge, it becomes a disposable, hard-to-trace tool for criminals. Here's how that plays out in practice:
- Phishing and impersonation calls: Using an honest person’s details for a SIM registration allows the scammer to have a “clean” number that won’t tip off victims about a potential scam immediately when carrying out a fake bank call, fake delivery scam, or fake impersonation of an officer.
- OTP and account-takeover fraud: Since the SIM card is used as the anchor to OTP verification, an unauthorized SIM can be used to capture one-time passwords to activate new digital payments, create a new digital payments account, or use other personal information linked to your phone number to reset your service passwords.
- Financial fraud and money mule networks: According to the investigators, such SIMs were extensively being used to open digital payment accounts as well as to flow money across a number of fraud chains, thus enabling the fraudsters to build a layer of financial infrastructure that is not linked with their actual identities.
- Identity theft with real-world consequences: The identity of the Aadhaar holder (whose document was used to activate the SIM card) might be unaware that a SIM exists under his name until the fraud is uncovered during a loan default or a criminal investigation where he is forced to justify a crime committed using “his” number that he is oblivious to.
That is the anonymity that SIM-card fraud has: the fact that the SIM on the face of it seems genuine, but the one operating it and the registered owner have absolutely no relationship whatsoever.
Red Flags Every Mobile User Should Watch For
Most people won't know their identity has been misused until something goes visibly wrong. A few warning signs are worth taking seriously:
- Your SIM suddenly loses network connectivity or displays "No Service" for an extended period without any known outage, SIM replacement request, or billing issue.
- You stop receiving OTPs or verification messages for banking, UPI, or other online services, particularly if login attempts continue to occur on your accounts.
- You receive unexpected OTPs, verification codes, or account alerts for services you never signed up for, indicating that someone may be attempting to use your mobile number.
- You receive calls or messages intended for someone else or asking you to confirm activities you never performed, which may suggest your number has been misused or duplicated.
- Your bank or telecom provider notifies you of unusual account activity, failed identity verification, or changes that you did not authorize.
- You discover multiple mobile connections registered in your name that you never requested, a risk that often remains unnoticed unless you proactively check through the Department of Telecommunications' Sanchar Saathi portal.
None of these guarantee fraud, but any of them is a reason to check further rather than assume it's a glitch.
Practical Steps to Protect Yourself
The good news is that Indian users now have direct tools to check and control this exposure:
- Identify your SIMs: Via the Department of Telecom’s Sanchar Saathi website, you can access a list of all mobile numbers registered in your name. Report and get any SIMs you do not recognize deactivated promptly.
- Safeguard your identity documents and biometrics: Do not disclose your Aadhaar information, OTPs, or biometrics to unofficial persons or retail agents. Ensure your SIM is activated in your presence by an official dealer of the telecom company.
- Tighten the security of your accounts: Wherever possible, use the most secure multi-factor authentication methods; an authenticator app, rather than just SMS, would be ideal. Consider enabling account change or SIM swap notifications from your telecom provider.
- Stay vigilant about your bank accounts and financial activities. Watch for unusual OTP requests, password change requests, login notifications, and unrecognized devices being logged into your online accounts. Being observant early on helps minimize losses.
- Take swift action if a SIM stops working: Contact your telecom provider and report the misuse to the Sanchar Saathi website as well as your nearest cyber station, or file a complaint through the cybercrime helpline number.
A Shared Responsibility
Consumer vigilance is not enough to save the system. Telecom providers must verify customer authenticity and check their retail points sufficiently so that a roadside vendor of the likes of “Shivam Telecom” cannot have their retail outlet anywhere the retail outlets may not need to be established and can be run even from an abandoned car body on the street for weeks. Authorities are ensuring this by making all franchisees and PoS agents and distributors register, such that the individual activating each SIM is perfectly identifiable. Consumers should take precautions and report suspicious patterns and be vigilant for fraud detection and protect themselves by knowing the system, like the use of the Sanchar Saathi platform.
Conclusion
The Delhi fake SIM case proves that even sophisticated technologies are not enough to protect India’s telecom ecosystem. No amount of biometric validation, AI fraud prevention tools, or rigid KYC compliance can offset a single corrupt agent selling SIM cards over the counter. While law enforcement works to clamp down, the responsibility also falls upon consumers, who need to regularly monitor their SIM registrations, safeguard their identity, and report any suspicious transactions in time to minimize the threat of identity theft and SIM-based cybercrime.
Sources
- https://www.prokerala.com/news/articles/a1784141.html
- https://the420.in/dots-sanchar-saathi-initiative-exposes-21-lakh-sim-cards-activated-illegally
- https://www.sancharsaathi.gov.in/
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2113857
- https://www.business-standard.com/amp/industry/news/nearly-4-million-sims-deactivated-as-govt-cracks-down-on-digital-fraud-125080500300_1.html
- https://www.digit.in/news/telecom/here-are-5-new-sim-card-rules-implemented-by-dot-amid-rising-scams-and-frauds.html
