
#FactCheck – Debunked: Dhoni's Viral Picture Misinterpreted as Political Support
Executive Summary:
The picture that went viral with the false story that Dhoni was supporting the Congress party, actually shows his joy over Chennai Super Kings' victory in the achievement of 6 million followers on X (formerly known as Twitter) in 2020. Dhoni's gesture was misinterpreted by many, which resulted in the spread of false information. The Research team of CyberPeace did an in-depth investigation of the photo's roots and confirmed its authenticity through a reverse image search, highlighting how news outlets and CSK's official social media channels shared it. The case illustrates the value of fact verification and the role of real information in preventing the fake news epidemic.

Claims:
An image of former Indian Cricket captain Mahendra Singh Dhoni, showed him urging people to vote for the Congress party, wearing the Chennai Super Kings (CSK) jersey and showing his right palm visible and gesturing the number 'one' with his left index finger. In reality he is celebrating Chennai Super Kings' milestone achievement on X (formerly Twitter) in 2020. Many people are sharing the misinterpretation knowingly or unknowingly over social media platforms.


Fact Check:
After receiving the post, we ran a reverse image search of the image and found a news article published by NDTV. According to the news outlet, Dhoni and his teammates were celebrating CSK's milestone of reaching six million followers on X (formerly known as Twitter) in the photos.

In the image it is written as a tweet of @chennaiipl, to get an idea we dig into the official account of Chennai Super Kings on X (formerly known as Twitter). And Voila! we found the exact post which surfaced on the X (formerly known as Twitter) on 5th October 2020.

Additionally, we found a video posted on the X (formerly known as Twitter) handle of CSK, featuring other cricketers celebrating the Six Million Followers milestone for which they are thanking the audience for their support. Again, it was posted on Oct 05, 2020. The caption of the video is written as “Chennai Super #SixerOnTwitter! A big thanks to all the super fans for each and every bouquet and brickbat throughout the last decade. All the #yellove to you. #WhistlePodu”

Therefore it is easy to conclude that the viral image of MS Dhoni supporting Congress is wrong and misleading.
Conclusion:
The information that circulated online media regarding a picture of Mahendra Singh Dhoni supporting the Congress Party has been proven to be untrue. The actual photograph was of Dhoni congratulating the Chennai Super Kings for having six million followers on social media in the year 2020. This highlights the need for checking the facts of any news circulating online.
- Claim: A photo allegedly depicting former Indian cricket captain Mahendra Singh Dhoni encouraging people to support the Congress party in elections surfaced online.
- Claimed on: X (Formerly known as Twitter)
- Fact Check: Fake & Misleading

Related Blogs
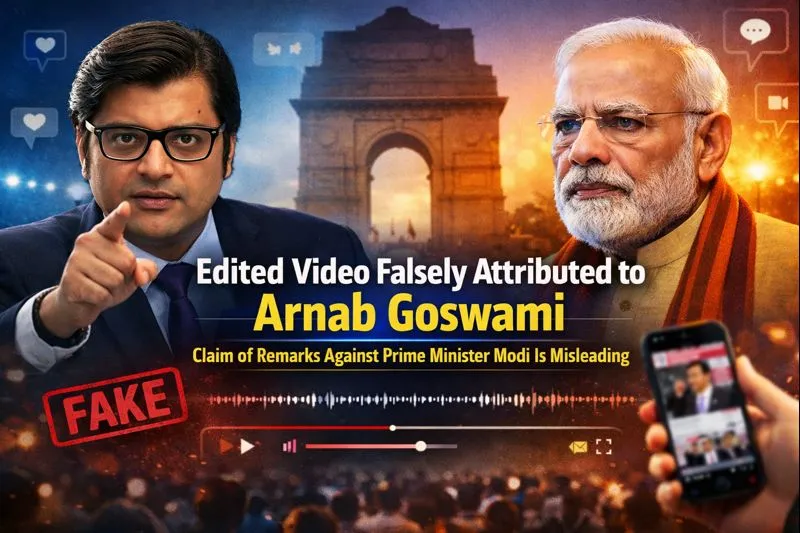
A video has been going viral on social media in recent days in which Republic TV’s Editor-in-Chief and anchor Arnab Goswami can allegedly be heard using objectionable language against Prime Minister Narendra Modi. While sharing the video, users are claiming that Arnab Goswami publicly made controversial remarks about the Prime Minister.
An investigation by CyberPeace Foundation found this claim to be completely false. Our probe revealed that the viral video is edited and is being circulated on social media with a misleading narrative. In the original video, Arnab Goswami was not making any personal statement; rather, he was referring to an old statement made by Congress leader Rahul Gandhi.
Viral Claim
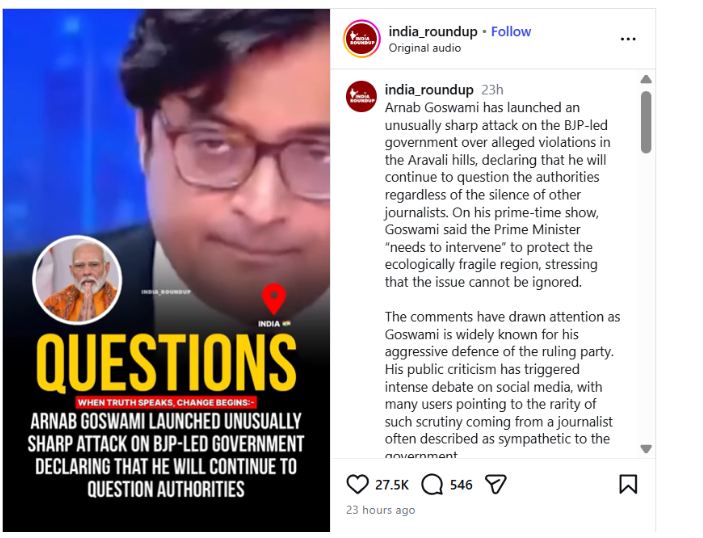
An Instagram user posted this video on 5 January 2026. In the video, a voice resembling Arnab Goswami is heard saying, “Ye jo Narendra Modi hain, ye chhe mahine baad ghar se nahi nikal paayenge aur Hindustan ke log inhein danda maarenge.”
(Translation: “This Narendra Modi will not be able to step out of his house after six months, and the people of India will beat him with sticks.”)
The post link, its archive link, and screenshots can be seen below:
- Instagram link: https://www.instagram.com/reel/DTHrO7bk7Rf/?igsh=MThzbzBlcm82eWN0ZA%3D%3D
- Archive link: https://archive.ph/oaYsf
Fact Check
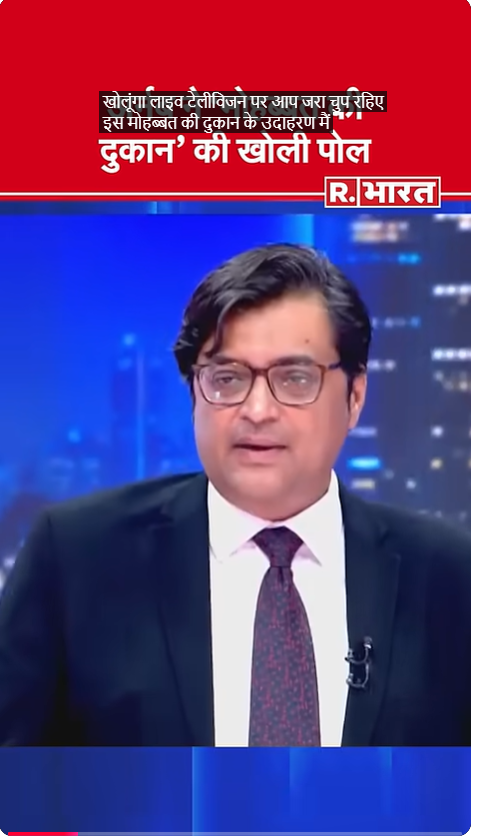
To verify the viral claim, we first examined the video using Google Lens search. During this process, we found a video published on 18 July 2024 on the official YouTube channel of Republic Bharat. The investigation revealed that this video is the longer (extended) version of the viral clip.
After carefully watching the full video, it became clear that Arnab Goswami was not making the statement himself. Instead, he was referring to a remark made by Congress leader Rahul Gandhi during the 2020 Delhi Assembly elections against Prime Minister Narendra Modi. This confirms that the viral video was clipped and presented out of context.
The related video link can be seen below: https://www.youtube.com/shorts/KlQV25-3l8s
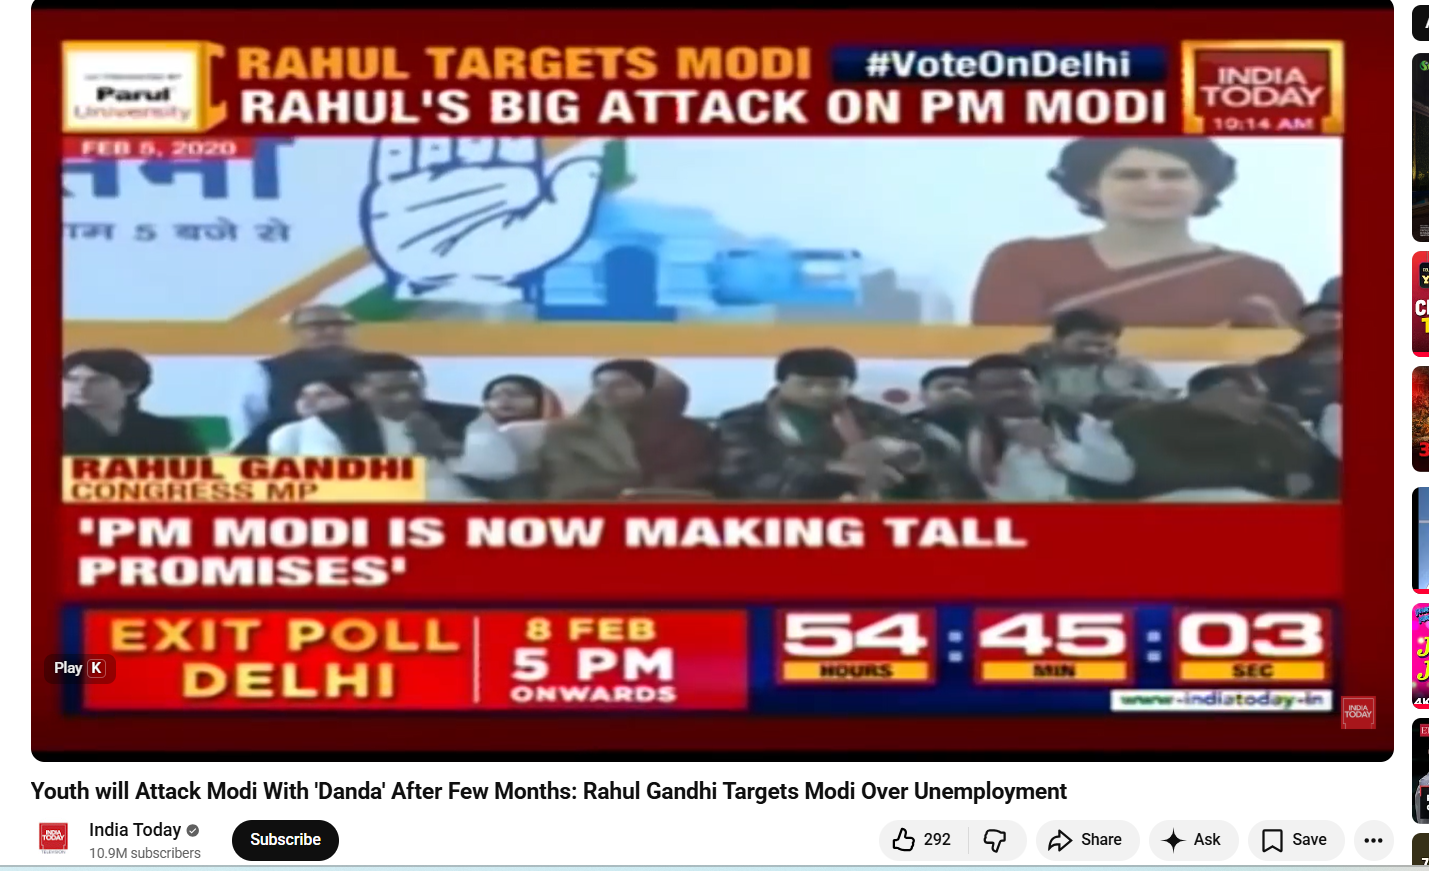
In the next step of the investigation, to verify whether Rahul Gandhi had indeed made such a statement, we conducted a customized keyword search on Google. During this, we found a video published on 6 February 2020 on the official YouTube channel of India Today.
In this video, recorded during a public event ahead of the 2020 Delhi Assembly elections, Rahul Gandhi is seen sharply attacking Prime Minister Narendra Modi, stating that if the Prime Minister fails to resolve the issue of unemployment in the country, the youth would beat him with sticks.
The video link is given below: https://www.youtube.com/watch?v=t5qCSA5nG9Y
Conclusion
The CyberPeace Foundation’s investigation found this claim to be completely fake. The viral video is edited and is being shared in a misleading context. In the original video, Arnab Goswami was referring to an old statement made by Rahul Gandhi, which was selectively clipped and presented in a way that falsely suggests Arnab Goswami himself made objectionable remarks against Prime Minister Narendra Modi.
Introduction
For much of the past two decades, India's contribution to the global technology economy was defined by software services and consumer internet platforms, which is a model that built enormous wealth and made the country the world's third-largest startup ecosystem.
That story is changing. More than ever before, the best received pitches in Bengaluru, Hyderabad, and Chennai are for rocket propulsion, semiconductor design, and autonomous hardware, not apps. And this isn't just a style choice of what gets funded. It's the real concentration of money, people, and political support around "deep tech" ventures based on frontier science and engineering breakthroughs as opposed to incremental software work.
The Data Behind the Narrative
The scale of this shift is now visible in hard numbers. In fact, Indian deeptech companies cumulatively raised $11.4 billion in funding between 2015 and mid-2026, according to the Bharat Deep Tech Report 2026 published by the Indian Venture and Alternate Capital Association (IVCA). 2025 was a record year for Indian deeptech firms, which saw a total raise of $2.96 billion across 189 deals, despite a slowdown in funding in the Indian startup ecosystem overall. Analytically speaking, here is what that reveals: investors haven't just raised the tide with the roadmap; they have explicitly taken a far-flung sector-specific decision to reallocate the capital and instead pursue science-and-engineering-led startups, even when pulling back elsewhere.
That very same report further pointed out that over 85% of all the deeptech funding raised in India since 2015 was obtained in the last six years, suggesting that the sector has only very recently come of age and matured from doing mostly early proof-of-concept experiments to delivering products that have undergone verifiable commercialisation. Of all the capital, funding and deals raised, AI and generative AI, followed by electric vehicles and battery technology, were the highest in terms of both dollars and the number of deals, while semiconductors and space tech were identified as the fastest-growing industrial segments and areas of research, consistent with India's national aspirations around technological self-sufficiency. When it comes to the distribution of deals and funding across India, the report found that Bengaluru on its own accounts for nearly 50%, with the rest of the country grabbing less than half.
Space as the Sector's Proof Point
If any single industry illustrates the credibility of India's hardware pivot, it is private space. Skyroot Aerospace's trajectory offers a useful case study. In May 2026, the Hyderabad-based launch vehicle company raised approximately $60 million in a round co-led by Sherpalo Ventures and GIC, with participation from BlackRock-managed funds, Arkam Ventures, and the Shanghvi Family Office, pushing its valuation to $1.1 billion and making it India's first space-tech unicorn. The round is notable not just for its size but for its composition: sovereign wealth capital (GIC) and global asset managers (BlackRock) backing a hardware company whose Vikram-1 rocket is roughly 95% indigenously built and expected to draw significant demand from the global telecommunications sector, with around 90% of Skyroot's customers based outside India. That the company's valuation nearly doubled in about thirty months also suggests investors are pricing in execution risk more favourably than in earlier cycles, when Indian hardware ventures were often viewed as uninvestable relative to their software counterparts.
This is not the only data point. Alongside Skyroot, companies including Agnikul Cosmos, Dhruva Space, Pixxel and Digantara are working on propulsion, satellite platforms and orbital-debris-tracking technology. Even if all of the Indian space startups do not go on to become businesses on the scale of ISRO, the existence of so many private-sector firms working on these goods and services shows the ecosystem in India is maturing. India's private space startup ecosystem lines up with broader sector reporting that India's private space startup ecosystem is approaching 440 companies as the private-sector push gathers speed through 2026.
Policy Architecture and Patient Capital
A defining characteristic of deeptech like the long R&D cycles, capital-heavy prototyping, and complex regulation makes deeptech firms structurally different from software startups, and Indian policymakers seem to be acknowledging as much. In April 2026, the government announced the Startup India Fund of Funds 2.0, creating a corpus of 10,000 crores to acquire commitments to Alternative Investment Funds, with a focus on deeptech, technology-focused manufacturing and early-growth-stage companies. The intention here, as was articulated, was to increase the supply of institutional capital for companies that diverge from software-investing norms. This complements the operational R & D and Innovation (RDI) Scheme and the India Semiconductor Mission, creating a multilayer public-capital framework for deeptech commercialisation.
Yet the same IVCA survey data complicates any triumphalist reading. Despite these schemes, 40% of surveyed venture funds reported having never engaged with any government capital vehicle, pointing to a persistent gap between policy design and on-the-ground fund utilisation. More critically, the survey identified a structural weak point in the financing pipeline: fund participation drops sharply at the Series B/C stage, with fewer investors able to write larger cheques to growth-stage companies.
Perhaps the single biggest limiting factor for the long term of deeptech in India. Spotting and encouraging deeptech entrepreneurs has definitely begun, but long-term success hinges on an ecosystem that can finance deeptech innovators through the critical scale-up phase – larger-ticket funds that many deeptech firms need to grow from a proof of concept into full-scale commercial products globally. Traditionally, Indian hardware startups have been quickly sold off or listed in foreign markets.
The exit environment reflects this immaturity. IVCA data shows 62% of funds cited exit visibility as their primary challenge, with secondary transactions accounting for 56% of all exits in the period studied, which is a signal that public-market exits (IPOs) remain the exception rather than the rule for deep-tech companies, unlike in India's more established software and fintech sectors.
An Analytical Assessment
Overall, the body of data confirms a measured yet real read on structural change rather than hype about cycles. How funding has focused on AI, semiconductors and spacetech; how some credible unicorns were born using homegrown hardware (like Skyroot); how policy and a fund-of-funds ecosystem were purposefully built – these all led, in Rajat Tandon's words, "from promise to more investible commitments, with an increasingly institutionalised ecosystem play".
However, three analytical caveats temper the enthusiasm. First, India's deep tech capital base, while growing rapidly in percentage terms, remains small in absolute terms relative to the United States and China, and much of it is still concentrated in early rounds rather than growth-stage financing. Second, geographic concentration in Bengaluru risks under-leveraging engineering talent elsewhere in the country. Third, and most consequentially, cross-border regulatory friction, export controls, dual-use technology restrictions, and the need for internationally recognised IP protection remains a binding constraint for hardware ventures seeking to scale beyond the domestic market, a challenge that policy alone cannot resolve.
Conclusion
India's transition from software exporter to deep-tech engineer is therefore real, measurable, and policy-supported, but it is a transition still in its early-to-middle innings, dependent on whether growth-stage capital and international market access can keep pace with early-stage enthusiasm and government intent.
Sources
- YourStory — Indian deeptech investments reach $11.4B: Report
- Outlook Business — India's Deeptech Funding Crosses $11 Bn As Investors Turn To AI, Semiconductors
- Business Standard — Over 85% of India's deeptech funding raised in past six years: IVCA
- The Week — Skyroot Aerospace becomes India's first space tech unicorn
- Outlook Business — Skyroot Aerospace Reaches Unicorn Orbit as Vikram-1 Launch Countdown Begins
- SatelliteToday — Skyroot Secures $60M in Funding, Becoming India's First Space 'Unicorn'
- Convergence Now — India's Startup Funding Map: AI, Sustainability & Deeptech Leading the Next Wave
- Seafund — DeepTech Startups in India: Funding & Innovation 2026
- YourStory (original reference article) — From software to satellites: Why India's next venture opportunity lies in deeptech
Introduction
Imagine an ordinary workday: a finance manager receives a WhatsApp message that appears to come from the company director. A regulatory document must be checked before a payment is released. The file is named “Statement of Account.zip”. The sender is familiar, and the deadline leaves little time to question it. But the archive may contain more than a statement. If a user extracts and runs the malicious Windows file inside, an attacker may compromise the computer and an active WhatsApp Web session. The account can then spread the file or be used for fraudulent payment instructions.
This is an illustrative reconstruction, not the story of one publicly identified victim. It is based on a 7 August 2026 alert from India’s Indian Cyber Crime Coordination Centre (I4C), describing reported WhatsApp takeovers across multiple states. It shows how a visible payment scam may be the final step in a longer technical and social chain. [1]
The real incident: an official warning, not a rumour
On 7 August 2026, I4C, under the Ministry of Home Affairs, warned of a rise in complaints involving professionals and businesses whose WhatsApp accounts were taken over after malicious files were sent as account statements or urgent regulatory notices. Reported filenames included “Statement of Account.zip”, “RBI.zip” and “MCA.zip”, delivered through WhatsApp, SMS or email. I4C said an archive could contain a Windows executable (.exe) and a Dynamic Link Library (.dll); opening the extracted file on a Windows computer could install a Trojan and compromise an active WhatsApp Web session. [1]
The compromised account could then spread the file to contacts and groups. Fraudsters might use an executive’s genuine account - or an attacker-controlled number saved under the executive’s name - to request urgent transfers to mule accounts. I4C identified reports from Delhi, Gujarat, Maharashtra and Rajasthan. It also said over 58,000 potential victims had been alerted by SMS in the preceding 30 days and more than 10,000 people protected through interventions. These are figures reported by I4C at that time, not a count of all victims or losses. [1]
The logical theory: how the attack chain may work
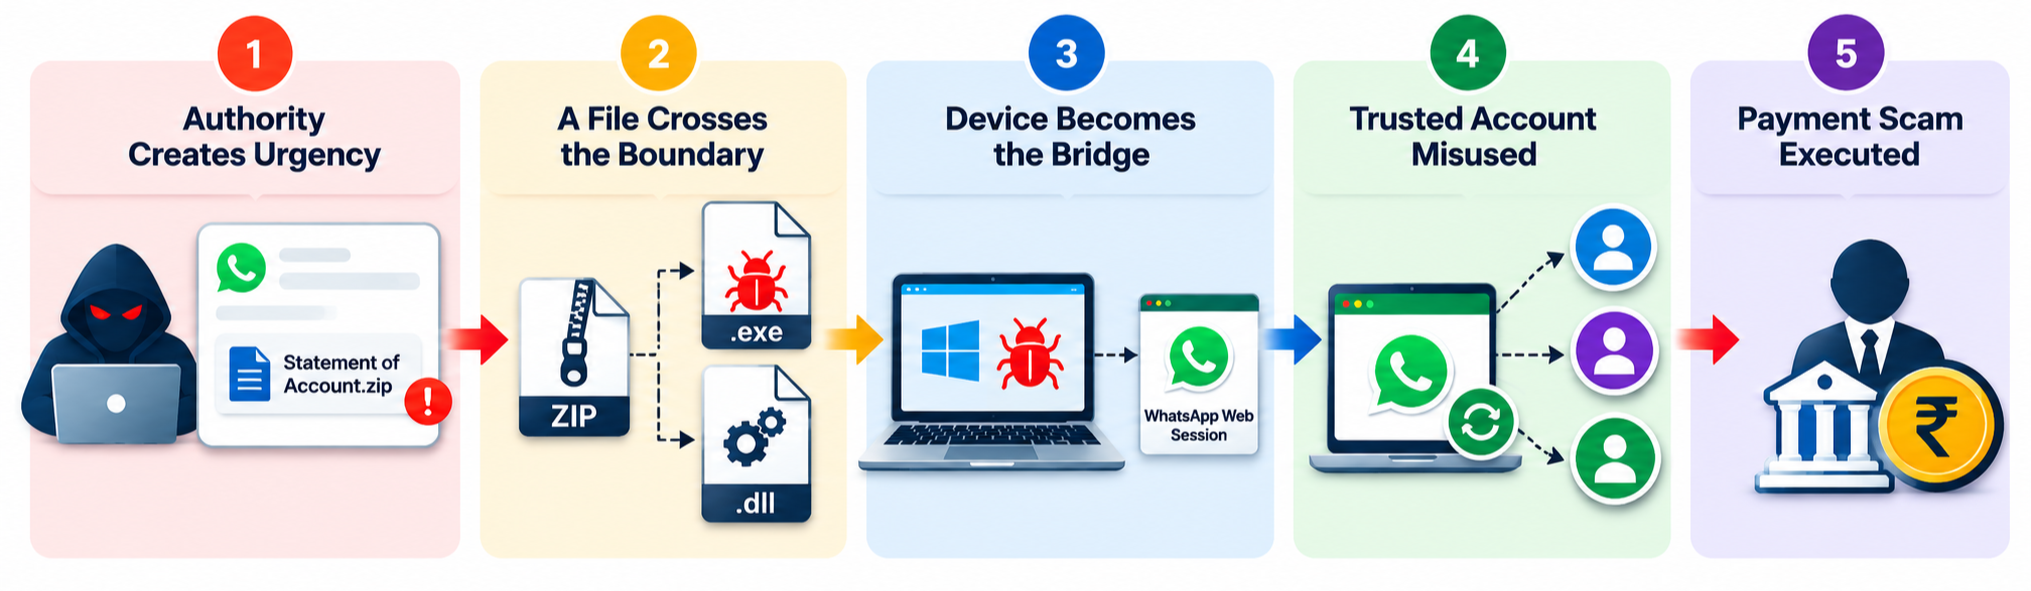
A useful working theory has five stages. It explains the mechanism described by I4C, but it should not be treated as proof that every reported case followed an identical path.
1. Authority creates urgency. I notice that a message borrows the language of compliance, banking or regulation. The aim is to make the recipient act quickly and treat the attachment as business paperwork.
2. A file crosses the boundary. I see that the risky step is not simply receiving a message; the risky step is. Executing the malicious Windows file. The I4C advisory describes an executable paired with a DLL. In DLL sideloading a program loads a library that's malicious or has been placed where it can be loaded unexpectedly. The precise behaviour must be confirmed by examining the sample and system evidence not guessed from a filename. [1][2]
3. The computer becomes the bridge. I read that the public advisory says the malware can compromise the Windows device and hijack a WhatsApp Web session. This means the incident is more than a stolen password: the attacker may be able to act through a session that already appears trusted.
4. Trust helps the file spread. I notice that a file or request arriving from a known colleague is more persuasive than one, from an account. If contacts receive the attachment from a compromised account they may forward it. Open it on a work computer potentially extending the incident.
5. The technical intrusion becomes a payment scam. I see that the attacker uses the authority of the executive’s account to request a transfer. The beneficiary account, transfer timing and messages may become financial evidence alongside the endpoint and messaging records.
How an investigator tests the theory
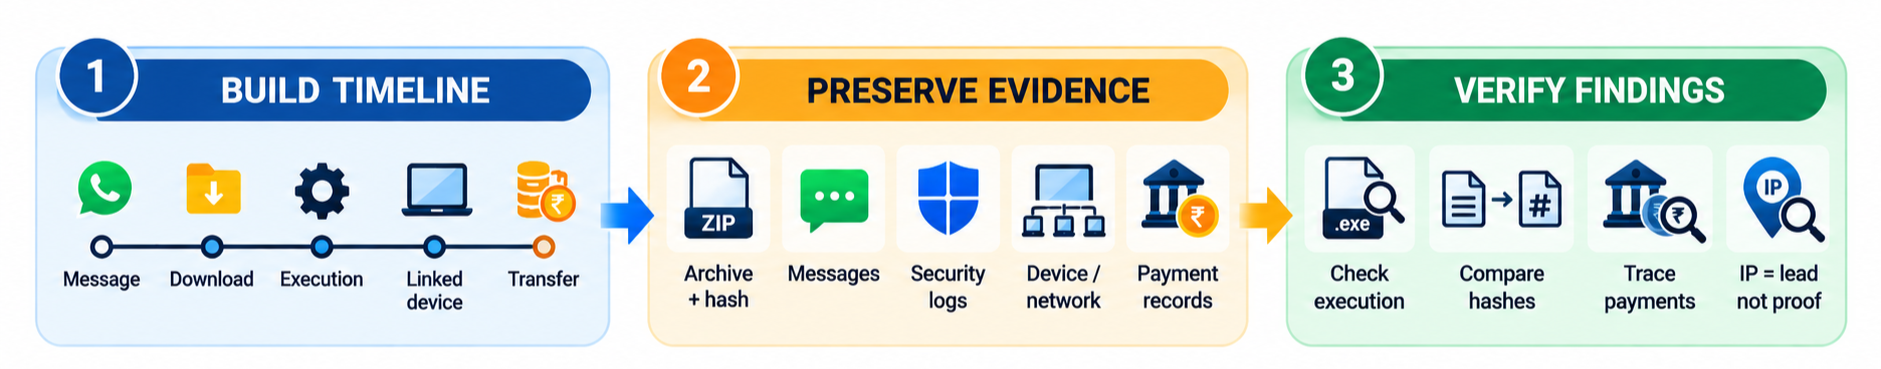
Start with a timeline, not a suspect. Record when the message arrived, when the archive was downloaded and possibly executed, when unusual messages began, which linked devices appeared, and when a transfer was requested. Note each timestamp’s source and time zone. A message in a chat proves it was present there; it does not, by itself, prove who typed it.
Evidence can contain the archive and its hash; message details or email headers; conversation exports and screenshots; Windows security and antivirus logs; available process and network artefacts; linked-device information; and payment instructions, transaction IDs and beneficiary details. Evidence authors should keep originals record each collection and transfer and analyse copies where possible. Evidence responders must not open a file, on a normal work computer to test it. Evidence NIST guidance explains the care needed to preserve evidence. [3]
Test alternatives as well. Proof of file execution before a new session or unusual outgoing messages may support the theory. Matching hashes across affected systems may link samples, and bank records may help trace payments. But a filename does not prove two files are identical, an IP address does not identify a person, and receiving an archive does not prove it ran. If evidence contradicts the theory, revise it.
What organizations should do now
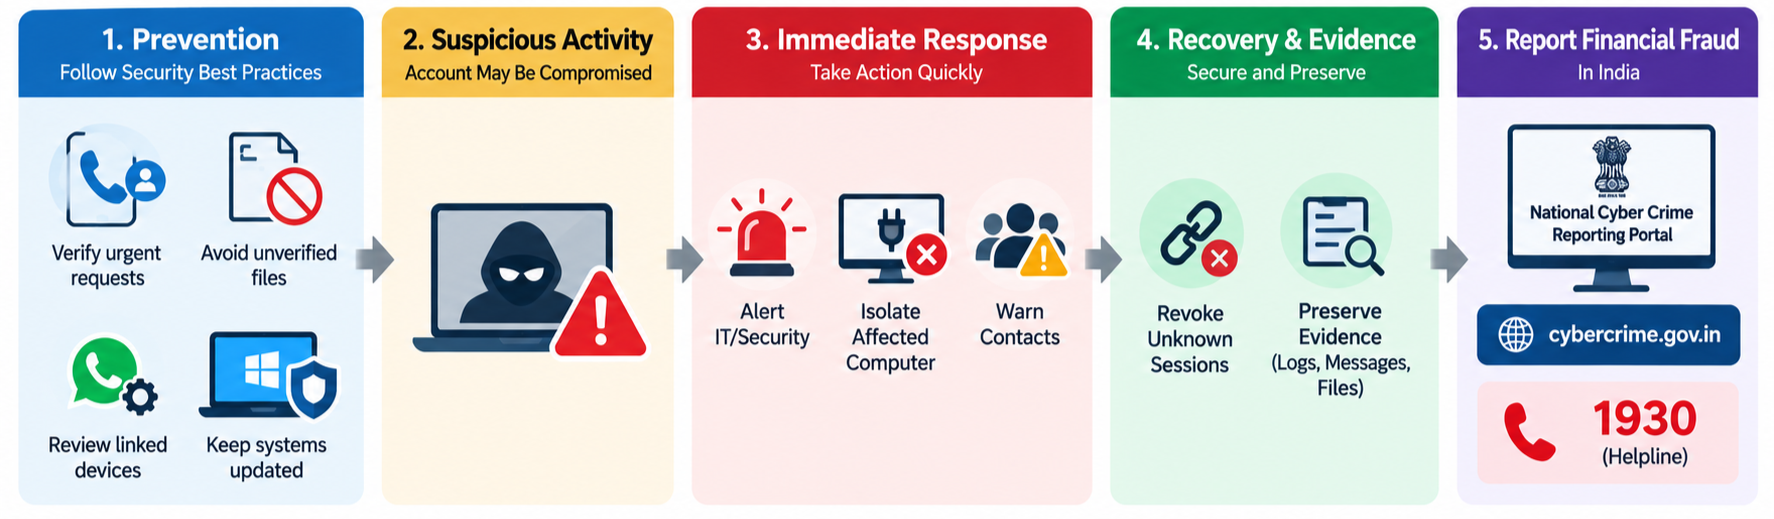
I4C says that any urgent transfers or changes to bank information should be checked using another way like a phone call or meeting in person. They also say to be careful about opening files or programs that are not confirmed check the devices linked to WhatsApp and make sure Windows computers are safe and up to date. [1] Don't approve any payment just because a message seems to be from a up person.
If you think something is wrong, tell the IT or security team stop using the computer that might be affected follow the steps, for an incident tell people who use the account not to open files from it remove any sessions that are not known and keep any proof before cleaning up. In India you can tell about financial cyber-crime by using the National Cyber Crime Reporting Portal or call 1930 right away. [4]
Conclusion
The I4C warning says that a WhatsApp takeover can happen through a series of events not just because someone stole a password. A convincing message that looks like it comes from a regulator can trick a user into opening a file. Once the file runs the computer might reveal a messaging session. Then the trusted account can spread the threat. Make a fake payment request seem real. Every step, in this process can leave clues: file traces, system logs, session data, messages and money trail evidence.
The I4C warning is not proof of what happened on any device. Investigators should use the I4C warning to build a theory test that theory, against saved records think about possibilities and mark what is unknown. For organisations a quick independent check of payment instructions can prevent the final loss. For investigators careful timelines and proper handling of evidence can produce results that can be explained and defended.
References: -
[1] Press Information Bureau, Ministry of Home Affairs / Indian Cyber Crime Coordination Centre (I4C), “I4C cautions corporates and finance professionals against ‘Boss Scam’: WhatsApp account takeover through malicious ‘Statement of Account’, ‘MCA’ and ‘RBI’ files aimed at high-value financial fraud,” 7 August 2026. Source
[2] Press Information Bureau, Ministry of Home Affairs / I4C, “Regulatory and Executive Impersonation for WhatsApp Account Takeover using Malicious Windows Executables and High value financial fraud,” 22 June 2026. Source
[3] Barbara Guttman, Douglas R. White, Shannan Williams and Tracy Walraven, Digital Evidence Preservation: Considerations for Evidence Handlers, NISTIR 8387, National Institute of Standards and Technology, 2022. Source
[4] Government of India, National Cyber Crime Reporting Portal; the portal advises immediate reporting of financial cyber fraud through helpline 1930. Source
