
#FactCheck - Deepfake Video Falsely Claims visuals of a massive rally held in Manipur
Executive Summary:
A viral online video claims visuals of a massive rally organised in Manipur for stopping the violence in Manipur. However, the CyberPeace Research Team has confirmed that the video is a deep fake, created using AI technology to manipulate the crowd into existence. There is no original footage in connection to any similar protest. The claim that promotes the same is therefore, false and misleading.
Claims:
A viral post falsely claims of a massive rally held in Manipur.


Fact Check:
Upon receiving the viral posts, we conducted a Google Lens search on the keyframes of the video. We could not locate any authentic sources mentioning such event held recently or previously. The viral video exhibited signs of digital manipulation, prompting a deeper investigation.
We used AI detection tools, such as TrueMedia and Hive AI Detection tool, to analyze the video. The analysis confirmed with 99.7% confidence that the video was a deepfake. The tools identified "substantial evidence of manipulation," particularly in the crowd and colour gradience , which were found to be artificially generated.


Additionally, an extensive review of official statements and interviews with Manipur State officials revealed no mention of any such rally. No credible reports were found linking to such protests, further confirming the video’s inauthenticity.
Conclusion:
The viral video claims visuals of a massive rally held in Manipur. The research using various tools such as truemedia.org and other AI detection tools confirms that the video is manipulated using AI technology. Additionally, there is no information in any official sources. Thus, the CyberPeace Research Team confirms that the video was manipulated using AI technology, making the claim false and misleading.
- Claim: Massive rally held in Manipur against the ongoing violence viral on social media.
- Claimed on: Instagram and X(Formerly Twitter)
- Fact Check: False & Misleading

Related Blogs
Executive Summary
A video of Dr. Samir V. Kamat, Chairman of the Defence Research and Development Organisation (DRDO), is going viral on social media. In the clip, he appears to claim that Prime Minister Narendra Modi instructed scientists to wash the Agni-6 missile with cow urine, and later use a mixture of cow dung and urine to prevent rusting. Research by CyberPeace Research Wing found that the video is a deepfake, created by manipulating original footage using AI tools. It was also shared by an account previously known for posting anti-India misinformation and is reportedly banned in India.
Claim
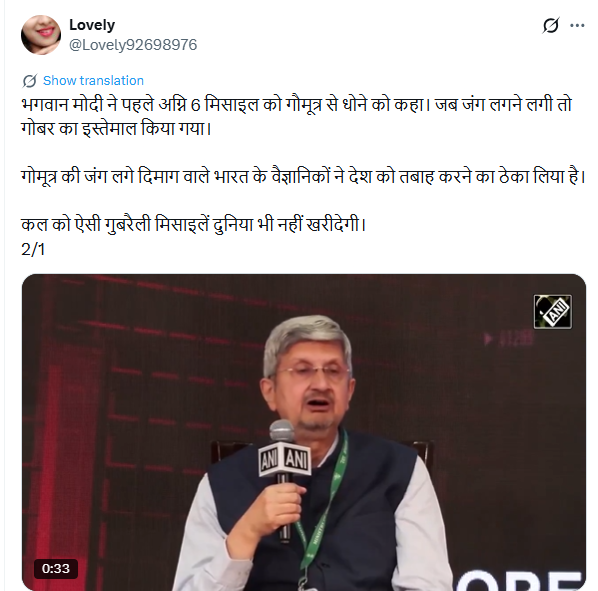
An X user named “Lovely” shared the video on May 1, 2026, alleging that Indian scientists were using cow urine and dung in missile development under government direction. The post used derogatory language and criticized India’s scientific community.
Fact Check
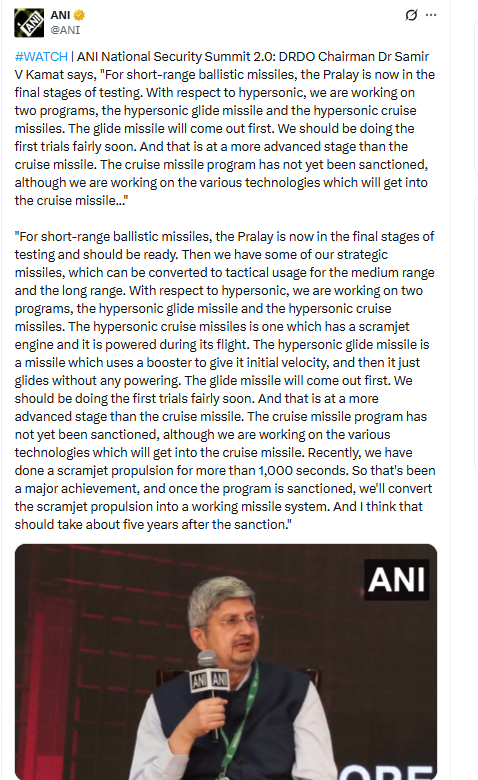
To verify the claim, we searched relevant keywords on Google but found no credible media reports supporting such statements by the DRDO chief. We then extracted keyframes from the viral clip and conducted a reverse image search using Google Lens. This led us to the original video posted by ANI on April 30, 2026. The footage is from the National Security Summit 2.0, where Dr. Kamat spoke about India’s missile development programs.
In the authentic video, Dr. Kamat discusses short-range ballistic missiles like ‘Pralay’, and advancements in hypersonic glide and cruise missile technologies, including scramjet propulsion. There is no mention of cow urine, cow dung, or any such practices.
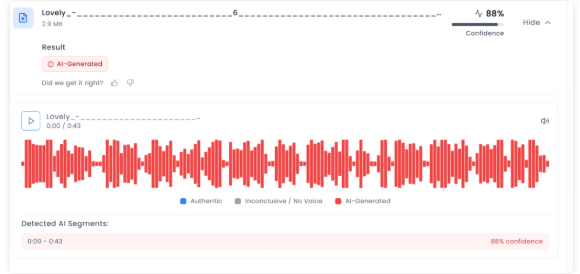
Further analysis using AI detection tool Aurigin indicated an 88% probability that the viral video was AI-generated or manipulated.
Conclusion
Our research confirms that the viral video is fake and AI-manipulated. Dr. Samir V. Kamat never made any statement about washing missiles with cow urine. The clip is a deepfake created to spread misinformation and mislead viewers.

Introduction
In April 2026, a class action suit in a federal court in California rejuvenated one of the most basic assertions in digital communication: that private messages are private. The suit claims that Meta Platforms, its subsidiary WhatsApp, and third-party contractors such as Accenture could have accessed user messages even though it had long promised end-to-end encryption.
This case is not merely about a single company or a single platform. It poses more profound questions regarding the definition, communication and regulation of privacy in an age when digital infrastructure is becoming more and more incomprehensible or unprovable to regular users.
What the Lawsuit Actually Says
The suit was filed by plaintiffs Brian Y. Shirazi and Nida Samson, who alleged that WhatsApp, Meta and contractors had intercepted and shared private messages with third parties without their consent. The complaint states that the federal investigators were notified by the whistleblowers that employees of Meta and external contractors had access to the content of WhatsApp messages that were expected to be encrypted and inaccessible.
This directly puts into question the main privacy promise of WhatsApp. The platform has been promoting itself as an end-to-end encrypted service in which not even WhatsApp can read your messages. The case asserts that this assertion was deceptive in its application and that no one ever gave any consent prior to their messages being intercepted, stored, or read.
The plaintiffs are proposing to represent a nationwide class of users of WhatsApp who sent or received messages between April 5, 2016, and the current time and subclasses in California and Pennsylvania. The claims involve breach of contract, California laws on privacy and data violations, false advertising and the Pennsylvania Wiretapping and Electronic Surveillance Act.
It should be mentioned that they are allegations. Similar assertions have been refuted by Metacomet in the past, with the company asserting that its encryption frameworks ensure that the company cannot access the messages. The case is in progress, and no facts have been found.
The Grey Area No One Talks About
In order to see the significance of this lawsuit outside the court, it is useful to consider the way modern messaging platforms actually work. In principle, end-to-end encryption means that only the sender and receiver can decipher a message. Even the service provider should not be able to access the content.
However, there is a grey space that is seldom publicly discussed: content moderation. User reports, metadata analysis or restricted message review processes are common methods used by platforms to identify harmful content, like fraud, child exploitation, or spam. The complaint indicates that such moderation procedures might have opened avenues to the content of messages to human reviewers or automated systems more than users were made to think.
This is not the first time that privacy and safety are at odds. Many jurisdictions have also advocated access to encrypted communications through legal means in the name of national security or criminal investigations. What this suit does is put that tension into even more stark relief by asking whether platforms are really open with users about these trade-offs.
The Consent Problem
The emphasis on consent is one of the most significant implications of this case. The plaintiffs claim that the users were never warned that their messages would be accessed by the employees or third parties and were never provided with any meaningful option on the same.
This is where the case turns into a data governance issue, rather than a legal one. Most data protection models consider the legality of data processing to be based on whether the users know how their data is being processed or not. When the accusations are found to be true, then the matter is not technical. It would be a contractual and ethical failure, a disjuncture between what platforms promise and what they do.
The implications are huge to the billions of users who use WhatsApp to communicate, both personally and professionally, and even politically.
What This Means Going Forward
An effective attack on the encryption assertions of WhatsApp might have actual implications for the rest of the digital ecosystem. Users might start doubting that any platform can be really considered to guarantee privacy. The regulators can advocate more stringent disclosure policies and compulsory independent audits of encryption systems. Social networks might have to re-architect their moderation frameworks to make sure that safety features do not silently compromise privacy guarantees that they claim.
Meanwhile, there is a real policy dilemma in this case that cannot be disregarded. Complete privacy may preclude the capacity to identify abuse or hateful material. The manner in which that balance is achieved and, more to the point, the manner in which it is made transparent to users is an issue that has yet to be addressed by policymakers, civil society and the tech industry.
Other technical experts have also questioned the plausibility of the claims in the lawsuit at scale, noting that it would be an extraordinary undertaking to systematically bypass end-to-end encryption. This further supports the argument of independent verification mechanisms. The problem is that users should not be forced to decide what they should believe in more: corporate guarantees or legal charges. There must be rules that can be enforced which are above the two.
Conclusion: Beyond One Lawsuit
The WhatsApp class action is eventually concerning a structural issue within the digital economy. Users are expected to have faith in systems that they cannot observe, on the assertions that they cannot test themselves.
This case is a warning, regardless of whether the allegations are proved or not. Privacy cannot be based on marketing language. It needs legally binding norms, actual transparency in the treatment of data, and external control that will provide users with something more to hang on than a tagline.
References
- https://www.bitdefender.com/en-us/blog/hotforsecurity/lawsuit-claims-meta-can-access-whatsapp-messages-despite-end-to-end-encryption-2
- https://blog.cryptographyengineering.com/2026/02/02/whatsapp-encryption-a-lawsuit-and-a-lot-of-noise/
- https://www.bloomberg.com/news/articles/2026-01-25/lawsuit-claims-meta-can-see-whatsapp-chats-in-breach-of-privacy
- https://www.classaction.org/blog/despite-privacy-promises-meta-third-parties-read-and-store-whatsapp-messages-class-action-lawsuit-alleges
Introduction
In recent years, the city of Hyderabad/Cyberabad has emerged as a technology hub, a place with the strong presence of multi corporations, Startups, and research institutions, Hyderabad has become a hub of innovations and technological advancement. However, this growing land of cyber opportunities has also become a hub for cybercriminals as well. In this blog post, we shall explore the reasons why professionals are being targeted and the effects of cyber fraud on techies. Through this investigation, we hope to raise awareness about the seriousness of the problem as well as give vital insights and techniques for Cyberabad’s computer workers to defend themselves against cyber theft. We can work together to make Cyberabad’s technology ecosystem safer and more secure.
Defining Cyber Fraud
In today’s age, where everything has an interconnected digital world, cyber fraud cases are increasing daily. Cyber fraud encompasses a wide range of threats and techniques employed by bad actors, such as Phishing, Ransomware, identity theft, online scams, data breaches, and fake websites designed for users. The sophistication of cyber fraud techniques is constantly evolving, making it challenging for individuals and organisations to stay ahead. Cybercriminals use software vulnerabilities, social engineering tactics, and flaws in cybersecurity defences to carry out their harmful operations. Individuals and organisations must grasp these dangers and tactics to protect themselves against cyber fraud.
Impact of Cyber Frauds
The consequences of Falling victim to cyber fraud can be devastating, both personally and professionally. The emotional and financial toll on individuals may be a challenge. Identity theft may lead to damaged credit scores, fraudulent transactions, and years of recovery work to rehabilitate one’s image. Financial fraud can result in depleted bank accounts, unauthorised charges, and substantial monetary losses. Furthermore, being tricked and violated in the digital environment can generate anxiety, tension, and a lack of confidence.
The impact of cyber fraud goes beyond immediate financial losses and can have long-term consequences for individuals’ and organisations’ entire well-being and stability. As the threat environment evolves, it is critical for people and organisations to recognise the gravity of these repercussions and take proactive actions to protect themselves against cyber theft.

Why are Cyberabad Tech Professionals Targeted?
Tech professionals in Cyberabad are particularly vulnerable to cyber due to various factors. Firstly, their expertise and knowledge in technology make them attractive targets for cybercrooks. These professionals possess valuable coding, Software, and administration skills, making them attractive to cybercriminals.
Secondly, the nature of work often involves enormous use of technology, including regular internet contacts, email exchanges, and access to private information. This expanded digital presence exposes them to possible cyber dangers and makes them more vulnerable to fraudsters’ social engineering efforts. Furthermore, the fast-moving nature of the tech industry, with many deadlines and work pressure to deliver, can create a distraction. This can let them click on some malicious links or share sensitive information unknowingly all these factors let the cyber criminals exploit vulnerabilities.
Unveiling the Statistics
According to various reports, 80% of cyber fraud victims in Hyderabad are techies; the rest are the public targeted by cyber crooks. This surprising number emphasises the critical need to address the vulnerabilities and threats this specific segment within the IT community faces.
Going further into the data, we can acquire insights into the many forms of cyber fraud targeting tech workers, the strategies used by cybercriminals, and the impact these occurrences have on individuals and organisations. Examining precise features and patterns within data might give important information for developing successful preventative and protection methods.
Factors Contributing
Several reasons contribute to the elevated risk of cyber fraud among ICT professionals in Cyberabad. Understanding these aspects helps explain why this group is specifically targeted and may be more vulnerable to such assaults.
Technical Expertise: Tech workers frequently have specialised technical knowledge, but this knowledge may only sometimes extend to cybersecurity. Their primary concentration is writing software, designing systems, or implementing technologies, which may result in missing possible vulnerabilities or a lack of overall cybersecurity understanding.
Confidence in Technology: IT workers have a higher level of confidence in technology because of their knowledge and dependence on technology. This trust can sometimes make individuals more vulnerable to sophisticated frauds or social engineering approaches that prey on their faith in the services they utilise.
Time Constraints and Pressure: Tech workers frequently operate under tight deadlines and tremendous pressure to reach project milestones. This may result in hurried decision-making or disregarding possible warning signals of cyber fraud, rendering them more exposed to assaults that prey on time-sensitive circumstances.
Cybercriminals know that technology workers have valuable knowledge, trade secrets, and intellectual property that may be economically profitable. As a result, they are attractive targets for attacks aiming at stealing sensitive data or gaining unauthorised access to critical systems.
The best practices that cyber techies can apply to safeguard their personal and professional data by following these simple tips:
Strong Passwords: create a strong password, using passwords for all your online accounts and changing them regularly. Remember to use unique combinations!
MFA (Multi-Factor Authentication): Enable MFA wherever possible. This provides an extra degree of protection by requiring a second form of verification, such as a code texted to your mobile device and your password.
Use Secured WiFi: Use secure and encrypted Wi-Fi networks, especially while viewing sensitive information. Avoid connecting to public or unprotected networks, as they can be readily exploited. Recognising Red Flags and Staying Ahead
Social Engineering: Be sceptical of unwanted solicitations or offers, both online and offline. Cybercriminals may try to persuade or fool you using social engineering tactics. Before revealing any personal or private information, think critically and confirm the veracity of the request.
Secure Web Browsing: Only browse trustworthy websites with valid SSL certificates (look for “https://” in the URL). Avoid clicking on strange links or downloading files from unknown sources since they may contain malware or ransomware.
Report Suspicious actions: If you encounter any suspicious or fraudulent actions, report them to the relevant authorities, such as the Cyber Crime Police or your organisation’s IT department. Reporting events can assist in avoiding additional harm and aid in identifying and apprehending hackers.
Stay Current on Security Practises: Stay up to speed on the newest cybersecurity risks and best practices. Follow credible sources, participate in cybersecurity forums or seminars, and remain current on new threats and preventative measures.

Conclusion
The rise in cybercrimes and fraud cases among tech experts in Cyberabad is a disturbing trend that requires prompt intervention. We can establish a safer tech cluster that lives on creativity, trust, and resilience by adopting proactive actions, raising awareness, and encouraging cooperation. Let us work together to prevent cybercrime and ensure the future of Cyberabad’s IT ecosystem.
