
#FactCheck: Video of Bangladesh Restaurant Vandalism Falsely Shared as RSS Volunteers Attacking Restaurant in West Bengal
Executive Summary
A video showing several people vandalising a restaurant is going viral on social media. Some users are sharing it with the claim that Rashtriya Swayamsevak Sangh (RSS) volunteers vandalised a restaurant in West Bengal after being asked to pay the bill. CyberPeace Research found that the video is from Bangladesh. Students had vandalised a restaurant in Dhaka following a minor dispute. The footage of that incident is being falsely shared as showing RSS volunteers vandalising a restaurant in West Bengal.
Claim:
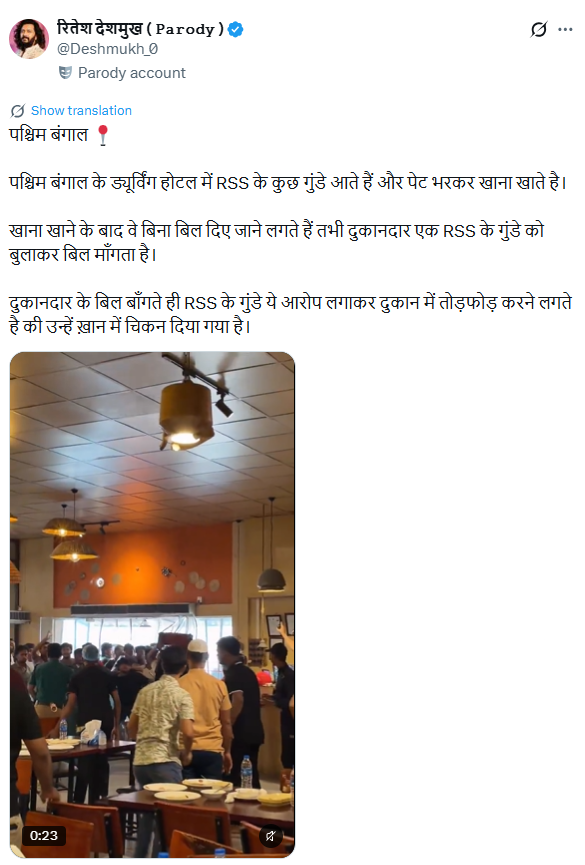
An X user, ‘Deshmukh_0’, posted the video on November 13, 2026 (archive link), with the caption: “Some RSS goons enter the Dewrving Hotel in West Bengal and eat to their heart’s content. After finishing their meal, they try to leave without paying the bill. When the shopkeeper asks one of the RSS goons to pay, they start vandalising the restaurant, alleging that they were served chicken instead of mutton.”
https://x.com/Deshmukh_0/status/2121220869460812137?a=N5xOXlH6zM57KQrKgqY&s=20
Fact Check
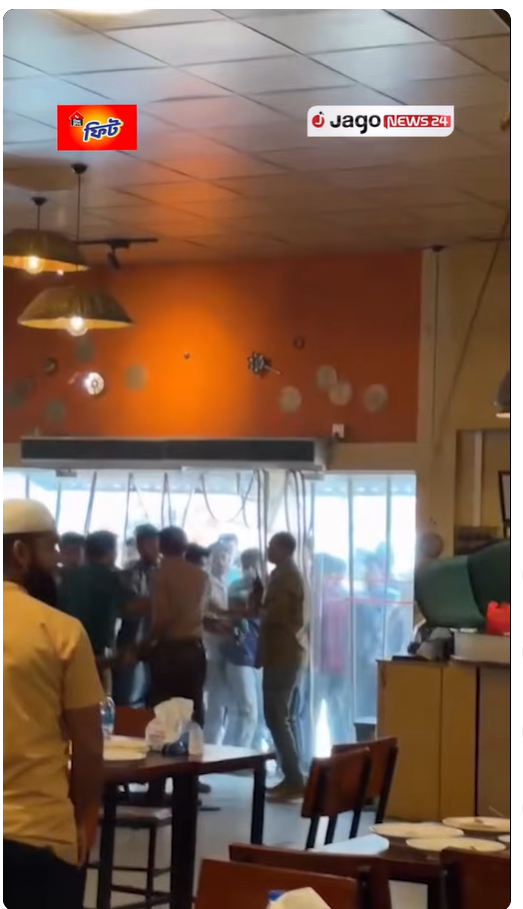
To verify the viral claim, we conducted a Google Lens search using keyframes from the video. We found a news report related to the viral footage, published on November 13, 2026, on the YouTube channel of Bangladeshi news portal ‘Jago News’. The viral clip can also be seen in the report.According to the report, students of Titumir College vandalised a restaurant in Mohakhali following a delay in serving food.
https://www.youtube.com/shorts/hBEyYWDLXzA
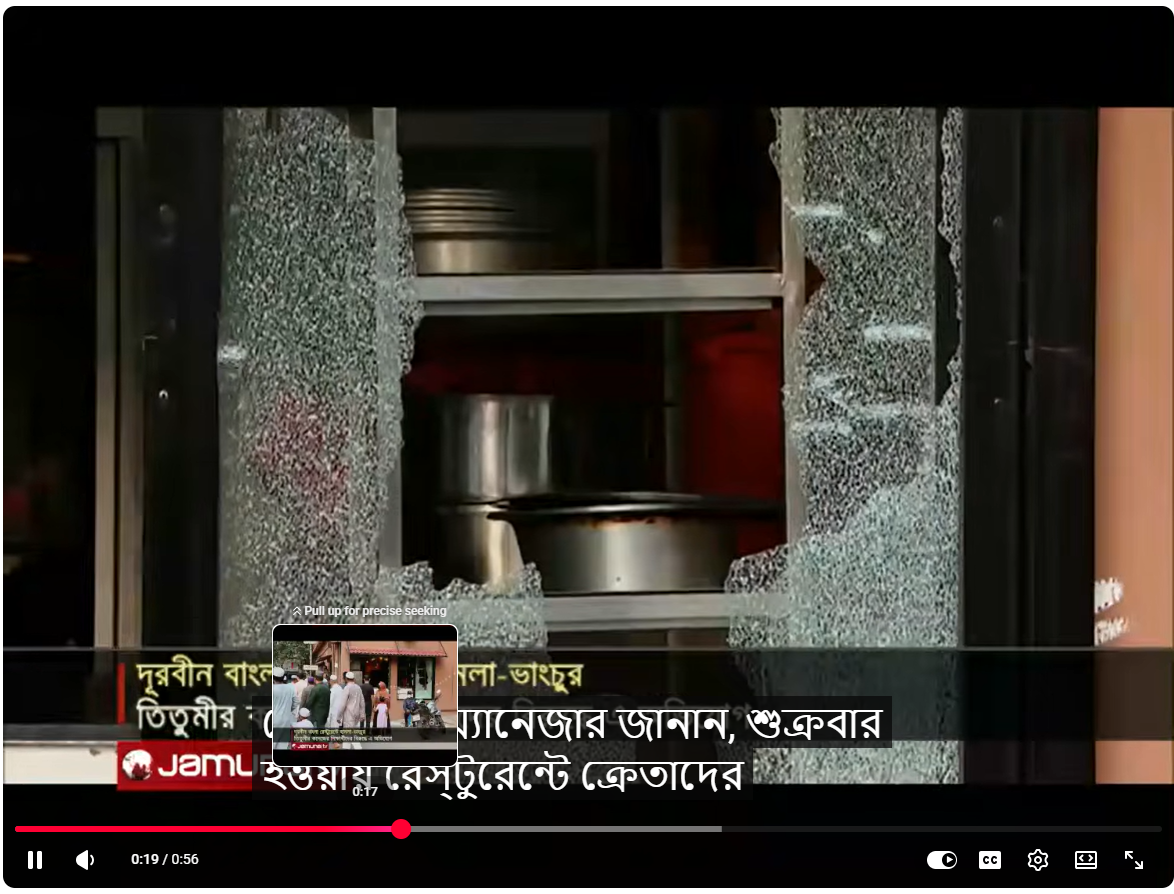
A related video report was also uploaded on November 14, 2026, on the YouTube channel of Bangladeshi news channel ‘Jamuna TV’.According to the report, “Students of Titumir College were accused of attacking restaurant staff and vandalising the ‘Durobin Bangla’ restaurant in Dhaka’s Mohakhali area following a dispute over seating arrangements. A clash subsequently broke out between the students and restaurant staff, leaving several employees and one student injured.”
https://www.youtube.com/watch?v=Qou7dobaISQ
Conclusion:
Students vandalised a restaurant in Dhaka, Bangladesh, following a minor dispute. However, the video of the incident is being falsely shared as showing RSS volunteers vandalising a restaurant in West Bengal.

Related Blogs

In the 21st century, wars are no longer confined to land, sea, and air. Rather, they are increasingly playing out across the digital domain, where effective dominance over networks, data, and communications determines who holds the upper hand. Among these, 5G networks are becoming a defining factor on modern battlefields. The ultra-low latency, massive bandwidth capability, and the ability to connect many devices at a single time are transforming the scale and level of military operations, intelligence, and logistics. This unprecedented connectivity is also met with a host of cybersecurity vulnerabilities that the governments and the militaries have to address.
As India faces a challenging security environment, the emergence of 5G presents both an opportunity and a dilemma. On one hand, it can enhance our command, control, surveillance and battlefield coordination. On the other hand, it also exposes the military and the security establishments to risks of espionage and supply chain vulnerabilities. So in this case, it will be important to strike a balance between innovation and security for turning 5G into a strength rather than a liability.
How can 5G networks be a military asset?
In comparison to its predecessors, 5G is not just about faster downloads. Rather, it is a complete overhaul of network architectures that are designed to support services and technologies according to modern technological requirements. In terms of military application of 5G networks, it can prove a series of game-changing capabilities, such as:-
- Enhanced Command and Control in the form of real-time data sharing between troops, UAVs, Radar systems and the Command Cells to ensure a faster and coordinated decision-making approach.
- Tactical Situational Awareness with the help of 5G-enabled devices can give soldiers instant updates on the terrain, troop movements, or positions and enemy movements.
- Advanced Intelligence, Surveillance and Reconnaissance (ISR) with high-resolution sensors, radars and UAVs that can operate at their full potential by transmitting vast data streams with minimal legacy.
However, 5G networks can also help to become a key component of the communication component of the military command establishments that would allow machines, sensors and human operators to function as a single and integrated force.
Understanding the importance of 5G networks as the Double-Edged Swords of Connectivity-
The potential of 5G is undeniable, but its vulnerabilities cannot be ignored. Because they are software-driven and reliant on dense networks of small cells. For the military, this shows that adversaries could exploit their weaknesses to disrupt the communication, jam signals, and intercept sensitive data, leaving behind some key risks, such as;
- Cybersecurity threats from software-based architectures make 5G networks prone to malware and data breaches.
- Supply chain risks can arise from reliance on foreign hardware and software components with raising fears of embedded backdoors or compromised systems.
- Signal jamming and interface in terms of millimetre-wave spectrum, 5G signals are vulnerable to disruption in contested environments.
- There can also be insider threats and physical sabotage over personnel or unsecured installations that could compromise network integrity.
Securing the Backbone: Cyber Defence Imperatives
To safeguard 5G networks as the backbone for future warfare, the defence establishments need to adopt a layered, proactive cybersecurity strategy. Several measures can be considered, such as;
- Ensuring robust encryption and authentication to protect sensitive data, which requires the installation of advanced protocols like Subscription Concealed Identifiers and zero-trust frameworks to eliminate implicit trust.
- Investing in domestic R&D for 5G components to reduce dependency on foreign suppliers. India’s adoption of the 5Gi standard is a step in this direction, but upgrading it into a military grade remains vital.
- To ensure collaboration across different sectors, the defence forces need to work with civilian agencies and private telecoms support providers to create unified standards and best practices.
Thus, with embedding cybersecurity into every layer of the 5G architecture, India can work in the direction to reduce risks to maintain its operational resilience.
The geopolitical domains of 5G Network as a tool of warfare-
The introduction of 5G networks has definitely come as a tool of technological advancement in the communication sector. But at the same time, it has also posed a geopolitical context as well. The strategic competition between the US and China to dominate the 5G infrastructure has global security implications. For India, aligning closely with either of the blocs will pose a risk to its strategic autonomy, but pursuing non-alignment can give India some leverage to develop its capability on its own.
In this case, partnerships with the QUAD with the US, Japan and Australia can open avenues for cooperating on shared standards, cost sharing, and interoperability in 5G-enabled military systems. Learning from countries like the US and Israel, which are developing their defence communication and network infrastructure to secure 5G networks, or revisiting existing frameworks like COMCASA or BECA with the US can serve as platforms to explore joint protocols for 5G networks.
Conclusion: Opportunities and the way forward-
The 5G network is becoming a part of the central nervous system of the future battlefields. It can offer immense opportunities for India to modernise its defence capabilities and enhance the situational awareness by integrating AI-driven systems. The future lies in adopting a balanced strategy by developing indigenous capabilities, forging trusted partnerships, embedding cybersecurity into every layer of the networking architecture and preparing a skilled workforce to analyse and counter evolving threats. However, by adopting a foresighted preparedness, India can turn the double-edged sword of 5G into a decisive advantage by ensuring that it not only adapts to the digital battlefield, rather India can also lead it.
References
- https://chanakyaforum.com/5g-poised-to-usher-in-a-paradigm-shift-in-military-communications
- https://www.ijert.org/secure-5g-network-architecture-for-armed-forces
- https://www.airforce-technology.com/sponsored/data-is-becoming-more-powerful-than-any-weaponry-on-the-battlefield-and-5g-is-the-backbone/
- https://www.upguard.com/blog/how-5g-technology-affects-cybersecurity
- https://agileblue.com/exploring-the-impact-of-5g-technology-on-cybersecurity-practices/

Introduction
In the hyperconnected world, cyber incidents can no longer be treated as sporadic disruptions; such incidents have become an everyday occurrence. The attack landscape today is very consequential and shows significant multiplication in its frequency, with ransomware attacks incapacitating a health system, phishing attacks hitting a financial institution, or state-sponsored attacks on critical infrastructures. Towards counteracting such threats, traditional ways alone are not enough, they gravely rely on manual research and human intellect. Attackers exercise speed, scale, and stealth, and defenders are always four steps behind. With such a widening gap, it is deemed necessary to facilitate incident response and crisis management with the intervention of automation and artificial intelligence (AI) for faster detection, context-driven decision-making, and collaborative response beyond human capabilities.
Incident Response and Crisis Management
Incident response is the structured way in which organisations deal with responding to detecting, segregating, and recovering from security incidents. Crisis management takes this even further, dealing not only with the technical fallout of a breach but also its business, reputation, and regulatory implications. Echelon used to depend on manual teams of people sorting through logs, cross-correlating alarms, and generating responses, a paradigm effective for small numbers but quickly inadequate in today's threat climate. Today's opponents attack at machine speed, employing automation to launch attacks. Under such circumstances, responding with slow, manual methods means delay and draconian consequences. The AI and automation introduction is a paradigm change that allows organisations to equate the pace and precision with which attackers initiate attacks in responding to incidents.
How Automation Reinvents Response
Cybercrime automation liberates cybercrime analysts from boring and repetitive tasks that consume time. An analyst manually detects potential threats from a list of hundreds each day, while automated systems sift through noise and focus only on genuine threats. Malware can automatically cause infected computers to be disconnected from the network to avoid spreading or may automatically have its suspicious account permissions removed without human intervention. The security orchestration systems move further by introducing playbooks, predefined steps describing how incidents of a certain type (e.g., phishing attempts or malware infections) should be handled. This ensures fast containment while ensuring consistency and minimising human error amid the urgency of dealing with thousands of alerts.
Automation takes care of threat detection, prioritisation, and containment, allowing human analysts to refocus on more complex decision-making. Instead of drowning in the sea of trivial alerts, security teams can now devote their efforts to more strategic areas: threat hunting and longer-term resilience. Automation is a strong tool of defence, cutting response times down from hours to minutes.
The Intelligence Layer: AI in Action
If automation provides speed, then AI is what allows the brain to be intelligent and flexible. Working with old and fixed-rule systems, AI-enabled solutions learn from experiences, adapt to changes in threats, and discover hidden patterns of which human analysts themselves would be unaware. For instance, machine learning algorithms identify normal behaviour on a corporate network and raise alerts on any anomalies that could indicate an insider attack or an advanced persistent threat. Similarly, AI systems sift through global threat intelligence to predict likely attack vectors so organisations can have their vulnerabilities fixed before they are exploited.
AI also boosts forensic analysis. Instead of searching forever for clues, analysts let AI-driven systems trace back to the origin of an event, identify vulnerabilities exploited by attackers, and flag systems that are still under attack. During a crisis, AI is a decision support that predicts outcomes of different scenarios and recommends the best response. In response to a ransomware attack, for example, based on context, AI might advise separating a single network segment or restoring from backup or alerting law enforcement.
Real-World Applications and Case Studies
Already, this mitigation has been provided in the form of real-world applications of automation and AI. Consider, for example, IBM Watson for Cybersecurity, which has been applied in analysing unstructured threat intelligence and providing analysts with actionable results in minutes, rather than days. Like this, systems driven by AI in DARPA's Cyber Grand Challenge demonstrated the ability to automatically identify an instant vulnerability, patch it, and reveal the potential of a self-healing system. AI-powered fraud detection systems stop suspicious transactions in the middle of their execution and work all night to prevent losses. What is common in all these examples is that automation and AI lessen human effort, increase accuracy, and in the event of a cyberattack, buy precious time.
Challenges and Limitations
While promising, the technology is still not fully mature. The quality of an AI system is highly dependent on the training data provided; poor training can generate false positives that drown teams or worse false negatives that allow attackers to proceed unabated. Attackers have also started targeting AI itself by poisoning datasets or designing malware that does not get detected. Aside from risks that are more technical, the operational and financial costs involved in implementing advanced AI-based systems present expensive threats to any company. Organisations will have to make expenditures not only on technology but also for the training of staff to best utilise these tools. There are some ethical and privacy issues to consider as well because systems may be processing sensitive personal data, so global data protection laws such as the GDPR or India's DPDP Act could come into conflict.
Creating a Human-AI Collaboration
The future is not going to be one of substitution by machines but of creating human-AI synergy. Automation can do the drudgery, AI can provide smarts, and human professionals can use judgment, imagination, and ethical decisions. One would want to build AI-fuelled Security Operations Centres where technology and human experts work in tandem. Continuous training must be provided to AI models to reduce false alarms and make them most resistant against adversarial attacks. Regular conduct of crisis drills that combine AI tools and human teams can ensure preparedness for real-time events. Likewise, it is worth integrating ethical AI guidelines into security frameworks to ensure a stronger defence while respecting privacy and regulatory compliance.
Conclusion
Cyber-attacks are an eventuality in this modern time, but the actual impact need not be so harsh. The organisations can maintain the programmatic method of integrating automation and AI into incident response and crisis management so that the response against the very threat can be shifted from reactive firefighting to proactive resilience. Automation gives speed and efficiency while AI gives intelligence and foresight, hence putting the defenders on par and possibly exceeding the speed and sophistication of the attackers. But an utmost system without human inquisitiveness, ethical reasoning, and strategic foresight would remain imperfect. The best defence is in that human-machine relationship symbiotic system wherein automation and AI take care of how fast and how many cyber threats come in, whereas human intellect ensures that every response is aligned with larger organizational goals. This synergy is where cybersecurity resiliency will reside in the future-the defenders won't just be reacting to emergencies but will rather be driving the way.
References
- https://www.sisainfosec.com/blogs/incident-response-automation/
- https://stratpilot.ai/role-of-ai-in-crisis-management-and-its-critical-importance/
- https://www.juvare.com/integrating-artificial-intelligence-into-crisis-management/
- https://www.motadata.com/blog/role-of-automation-in-incident-management/

Introduction
In a major policy shift aimed at synchronizing India's fight against cyber-enabled financial crimes, the government has taken a landmark step by bringing the Indian Cyber Crime Coordination Centre (I4C) under the ambit of the Prevention of Money Laundering Act (PMLA). In the notification released in the official gazette on 25th April, 2025, the Department of Revenue, Ministry of Finance, included the Indian Cyber Crime Coordination Centre (I4C) under Section 66 of the Prevention of Money Laundering Act, 2002 (hereinafter referred to as “PMLA”). The step comes as a significant attempt to resolve the asynchronous approach of different agencies (Enforcement Directorate (ED), State Police, CBI, CERT-In, RBI) set up under the government responsible for preventing and often possessing key information regarding cyber crimes and financial crimes. As it is correctly put, "When criminals sprint and the administration strolls, the finish line is lost.”
The gazetted notification dated 25th April, 2025, read as follows:
“In exercise of the powers conferred by clause (ii) of sub-section (1) of section 66 of the Prevention of Money-laundering Act, 2002 (15 of 2003), the Central Government, on being satisfied that it is necessary in the public interest to do so, hereby makes the following further amendment in the notification of the Government of India, in the Ministry of Finance, Department of Revenue, published in the Gazette of India, Extraordinary, Part II, section 3, sub-section (i) vide number G.S.R. 381(E), dated the 27th June, 2006, namely:- In the said notification, after serial number (26) and the entry relating thereto, the following serial number and entry shall be inserted, namely:— “(27) Indian Cyber Crime Coordination Centre (I4C).”.
Outrunning Crime: Strengthening Enforcement through Rapid Coordination
The usage of cyberspace to commit sophisticated financial crimes and white-collar crimes is a one criminal parallel passover that no one was looking forward to. The disenchanted reality of today’s world is that the internet is used for as much bad as it is for good. The internet has now entered the financial domain, facilitating various financial crimes. Money laundering is a financial crime that includes all processes or activities that are in connection with the concealment, possession, acquisition, or use of proceeds of crime and projecting it as untainted money. In the offence of money laundering, there is an intricate web and trail of financial transactions that are hard to track, as they are, and with the advent of the internet, the transactions are often digital, and the absence of crucial information hampers the evidentiary chain. With this new step, the Enforcement Directorate (ED) will now make headway into the investigation with the information exchange under PMLA from and to I4C, removing the obstacles that existed before this notification.
Impact
The decision of the finance ministry has to be seen in terms of all that is happening around the globe, with the rapid increase in sophisticated financial crimes. By formally empowering the I4C to share and receive information with the Enforcement Directorate under PMLA, the government acknowledges the blurred lines between conventional financial crime and cybercrime. It strengthens India’s financial surveillance, where money laundering and cyber fraud are increasingly two sides of the same coin. The assessment of the impact can be made from the following facilitations enabled by the decision:
- Quicker internet detection of money laundering
- Money trail tracking in real time across online platforms
- Rapid freeze of cryptocurrency wallets or assets obtained fraudulently
Another important aspect of this decision is that it serves as a signal that India is finally equipping itself and treating cyber-enabled financial crimes with the gravitas that is the need of the hour. This decision creates a two-way intelligence flow between cybercrime detection units and financial enforcement agencies.
Conclusion
To counter the fragmented approach in handling cyber-enabled white-collar crimes and money laundering, the Indian government has fortified its legal and enforcement framework by extending PMLA’s reach to the Indian Cyber Crime Coordination Centre (I4C). All the decisions and the brainstorming that led up to this notification are crucial at this point in time for the cybercrime framework that India needs to be on par with other countries. Although India has come a long way in designing a robust cybercrime intelligence structure, as long as it excludes and works in isolation, it will be ineffective. So, the current decision in discussion should only be the beginning of a more comprehensive policy evolution. The government must further integrate and devise a separate mechanism to track “digital footprints” and incorporate a real-time red flag mechanism in digital transactions suspected to be linked to laundering or fraud.
