
#FactCheck: Debunking the Edited Image Claim of PM Modi with Hafiz Saeed
Executive Summary:
A photoshopped image circulating online suggests Prime Minister Narendra Modi met with militant leader Hafiz Saeed. The actual photograph features PM Modi greeting former Pakistani Prime Minister Nawaz Sharif during a surprise diplomatic stopover in Lahore on December 25, 2015.
The Claim:
A widely shared image on social media purportedly shows PM Modi meeting Hafiz Saeed, a declared terrorist. The claim implies Modi is hostile towards India or aligned with terrorists.

Fact Check:
On our research and reverse image search we found that the Press Information Bureau (PIB) had tweeted about the visit on 25 December 2015, noting that PM Narendra Modi was warmly welcomed by then-Pakistani PM Nawaz Sharif in Lahore. The tweet included several images from various angles of the original meeting between Modi and Sharif. On the same day, PM Modi also posted a tweet stating he had spoken with Nawaz Sharif and extended birthday wishes. Additionally, no credible reports of any meeting between Modi and Hafiz Saeed, further validating that the viral image is digitally altered.


In our further research we found an identical photo, with former Pakistan Prime Minister Nawaz Sharif in place of Hafiz Saeed. This post was shared by Hindustan Times on X on 26 December 2015, pointing to the possibility that the viral image has been manipulated.
Conclusion:
The viral image claiming to show PM Modi with Hafiz Saeed is digitally manipulated. A reverse image search and official posts from the PIB and PM Modi confirm the original photo was taken during Modi’s visit to Lahore in December 2015, where he met Nawaz Sharif. No credible source supports any meeting between Modi and Hafiz Saeed, clearly proving the image is fake.
- Claim: Debunking the Edited Image Claim of PM Modi with Hafiz Saeed
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

Disclaimer:
The information is based on claims made by threat actors and does not imply confirmation of the breach, by CyberPeace. CyberPeace includes this detail solely to provide factual transparency and does not condone any unlawful activities. This information is shared only for research purposes and to spread awareness. CyberPeace encourages individuals and organizations to adopt proactive cybersecurity measures to protect against potential threats.
🚨 Data Breach Alert ⚠️:
Recently The Research Wing of CyberPeace and Autobot Infosec have come across a claim on a threat actor’s dark web website alleging a data breach involving 637k+ records from Federal Bank. According to the threat actor’s claim, the data allegedly includes sensitive details such as-
- 🧑Customer Name
- 🆔Customer ID
- 🏠 Customer Address
- 🎂 Date of Birth
- 🔢 Age
- 🚻 Gender
- 📞Mobile Number
- 🪪 PAN Number
- 🚘 Driving License Number
- 🛂 Passport Number
- 🔑 UID Number
- 🗳️ Voter ID Information
The alleged data was initially discovered on a dark web website, where the threat actors allegedly claimed to be offering the breached information for sale. Following their announcement of the breach, a portion of the data was reportedly published on December 27, 2024. A few days later, the full dataset was allegedly released on the same forum.
About the Threat Actor Group:
Bashe, a ransomware group that emerged in 2024, is claimed to have evolved from the LockBit ransomware group, previously operating under the names APT73 and Eraleig. The group employs data encryption combined with extortion tactics, threatening to release sensitive information if ransom demands are unmet. Their operations primarily target critical industries, including technology, healthcare, and finance, demonstrating a strategic focus on high-value sectors.

Breakdown of the Alleged Post by the Threat Actor:
- Target: Allegedly involves Customer’s Data of Federal Bank.
- Data Volume: Claimed breach includes 637,894 records.
- Data Fields: Threat actor claims the data contains sensitive information, including Customer name, Customer ID, Date of Birth, PAN Number, Age, Gender, Father Name, Spouse Name, Driving Licence, Passport Number, UID Number, Voter ID, District, Zip Code, Home Address, Mailing Address, State etc.
Analysis:
The analysis of the alleged data breach highlights the states purportedly most impacted, along with insights into the affected age groups, gender distribution, and other key insights associated with the compromised data. This evaluation aims to provide a clearer understanding of the claimed breach's scope and its potential demographic and geographic impact.
Top States Impacted:
As per the alleged breached data, Tamil Nadu has the highest number of affected customers, accounting for a significant 34.49% of the total breach. Karnataka follows closely with 26.89%, indicating a substantial number of individuals affected in the state. In contrast states such as Uttar Pradesh, Haryana, Delhi, and Rajasthan report minimal impact, with each state having less than 1% of affected customers. Gujarat records 3.70% of the breach, with a sharp drop in affected numbers from other states, highlighting a significant disparity in the extent of the breach across regions.

Impacted Age Range Statistics:
The alleged data breach has predominantly impacted customers in the 31-40 years age group, which constitutes the largest segment at 35.80% of the affected individuals. Following this, the 21-30 years age group also shows significant impact, comprising 27.72% of those affected. The 41-50 years age group accounts for 20.55% of the impacted population, while individuals aged 50 and above represent 12.68%. In contrast, the 0-20 years age group is the least affected, with only 3.24% of customers falling into this category.

Gender Wise Statistics:
The alleged data breach has predominantly impacted male customers, who constitute the majority at 74.05% of the affected individuals. Female customers account for 23.18%, while a smaller segment, categorized as "Others," constitutes 2.77%.

The alleged dataset from the threat actors indicated that a significant portion of customers' personal identification data was compromised. This includes sensitive information such as driving licenses, passport numbers, UID numbers, voter IDs, and PAN numbers.
Significance of the Allegations:
Though the claims have not been independently verified at our end it underscores the rising risks of cyberattacks and data breaches, especially in the financial and banking sectors. If true, the exposure of such sensitive information could lead to financial fraud, identity theft, and severe reputational damage for individuals and organizations alike.
CyberPeace Advisory:
CyberPeace emphasizes the importance of vigilance and proactive measures to address cybersecurity risks:
- Monitor Your Accounts: Keep a close eye on financial and email accounts for any suspicious activity.
- Update Passwords: Change your passwords immediately and enable Multi Factor Authentication(MFA) wherever possible.
- Beware of Phishing Attacks: Threat actors may exploit the leaked data to craft targeted phishing scams. Do not click on unsolicited links or share sensitive details over email or phone.
- For Organizations: Strengthen data protection mechanisms, regularly audit security infrastructure, and respond swiftly to emerging threats.
- Report: For more assistance or to report cyber incidents, visit https://cybercrime.gov.in or contact our helpline team at helpline@cyberpeace.net.
We advise affected parties and the broader public to stay alert and take necessary precautions. CyberPeace remains committed to raising awareness about cybersecurity threats and advocating for better protection mechanisms. We urge all stakeholders to investigate the claims and ensure appropriate steps are taken to protect the impacted data, if the breach is confirmed. Our Research Wing is actively observing the situation and we aim to collaborate with the stakeholders and relevant agencies to mitigate the impact.
Stay Vigilant! Stay CyberPeaceful.
Executive Summary
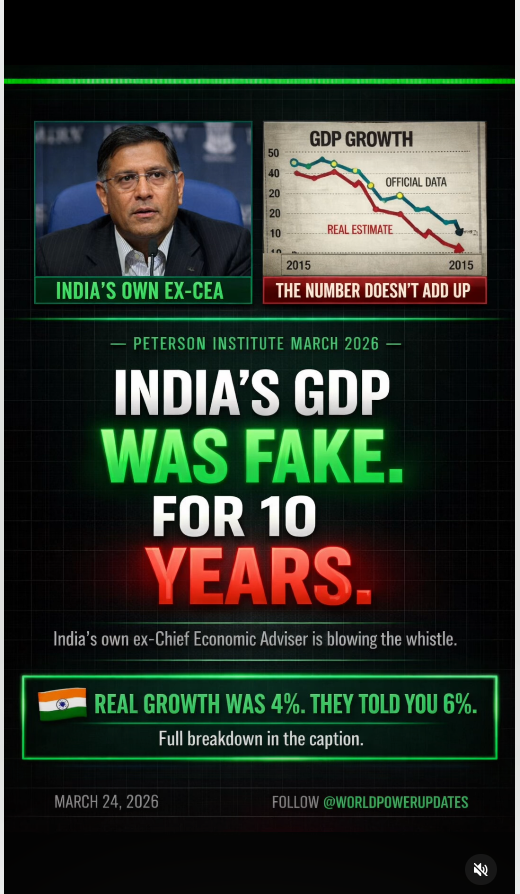
A viral graphic post on social media claims that India’s GDP (Gross Domestic Product) was “fake for 10 years.” The post also states that the real economic growth was around 4%, while official figures reported it at 6%. It further cites a former Chief Economic Adviser (Ex-CEA) and presents the claim as a “revelation.”
Research by CyberPeace Research Wing found this claim to be misleading. No official government document, nor India’s Ministry of Statistics and Programme Implementation (MoSPI), the Reserve Bank of India (RBI), or any recognised international institution has stated that India’s GDP was “fake.”
Claim
On the social media platform Instagram, a user shared a post claiming that the Chief Economic Adviser said India’s GDP (Gross Domestic Product) was “fake for 10 years.” The link to the post and its archive link are given below, along with a screenshot.
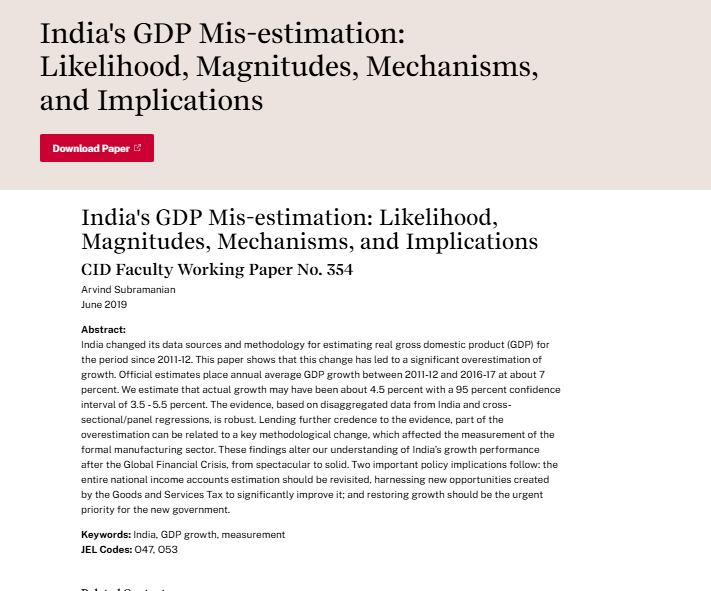
The viral post refers to a 2019 research paper linked to former Chief Economic Adviser (Ex-CEA) Arvind Subramanian. In this study, he raised questions about India’s GDP growth estimation and suggested that during 2011–12 to 2016–17, the actual growth could have been around 4.5%, while the official estimate was close to 7%.
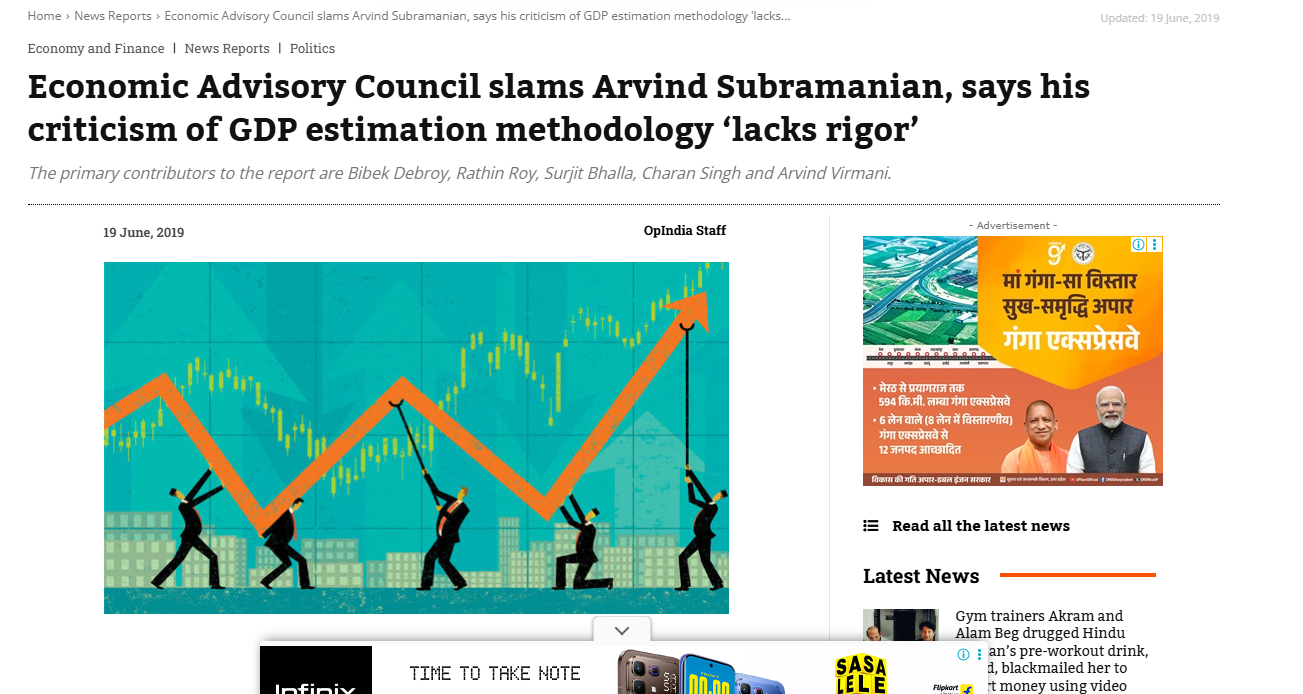
However, the study does not conclude anywhere that India’s GDP was “fake” or entirely incorrect. It only presents an alternative estimation based on different assumptions and methods, which has also been challenged by other economists and government agencies.
- https://www.hks.harvard.edu/centers/cid/publications/faculty-working-papers/india-gdp-overestimate?utm_source
- https://www.hks.harvard.edu/centers/cid/publications/faculty-working-papers/india-gdp-overestimate?utm_source
Conclusion:
The claim circulating on social media is misleading. The former Chief Economic Adviser provided an academic view on GDP estimation, but there is no evidence or official confirmation that India’s GDP was “fake for 10 years.” The data released by the Government of India was not validated by the figures circulated on social media.

Introduction
In the labyrinthine expanse of the digital age, where the ethereal threads of our connections weave a tapestry of virtual existence, there lies a sinister phenomenon that preys upon the vulnerabilities of human emotion and trust. This phenomenon, known as cyber kidnapping, recently ensnared a 17-year-old Chinese exchange student, Kai Zhuang, in its deceptive grip, leading to an $80,000 extortion from his distraught parents. The chilling narrative of Zhuang found cold and scared in a tent in the Utah wilderness, serves as a stark reminder of the pernicious reach of cybercrime.
The Cyber Kidnapping
The term 'cyber kidnapping' typically denotes a form of cybercrime where malefactors gain unauthorised access to computer systems or data, holding it hostage for ransom. Yet, in the context of Zhuang's ordeal, it took on a more harrowing dimension—a psychological manipulation through online communication that convinced his family of his peril, despite his physical safety before the scam.
The Incident
The incident unfolded like a modern-day thriller, with Zhuang's parents in China alerting officials at his host high school in Riverdale, Utah, of his disappearance on 28 December 2023. A meticulous investigation ensued, tracing bank records, purchases, and phone data, leading authorities to Zhuang's isolated encampment, 25 miles north of Brigham City. In the frigid embrace of Utah's winter, Zhuang awaited rescue, armed only with a heat blanket, a sleeping bag, limited provisions, and the very phones used to orchestrate his cyber kidnapping.
Upon his rescue, Zhuang's first requests were poignantly human—a warm cheeseburger and a conversation with his family, who had been manipulated into paying the hefty ransom during the cyber-kidnapping scam. This incident not only highlights the emotional toll of such crimes but also the urgent need for awareness and preventative measures.
The Aftermath
To navigate the treacherous waters of cyber threats, one must adopt the scepticism of a seasoned detective when confronted with unsolicited messages that reek of urgency or threat. The verification of identities becomes a crucial shield, a bulwark against deception. Sharing sensitive information online is akin to casting pearls before swine, where once relinquished, control is lost forever. Privacy settings on social media are the ramparts that must be fortified, and the education of family and friends becomes a communal armour against the onslaught of cyber threats.
The Chinese embassy in Washington has sounded the alarm, warning its citizens in the U.S. about the risks of 'virtual kidnapping' and other online frauds. This scam fragments a larger criminal mosaic that threatens to ensnare parents worldwide.
Kai Zhuang's story, while unique in its details, is not an isolated event. Experts warn that technological advancements have made it easier for criminals to pursue cyber kidnapping schemes. The impersonation of loved ones' voices using artificial intelligence, the mining of social media for personal data, and the spoofing of phone numbers are all tools in the cyber kidnapper's arsenal.
The Way Forward
The crimes have evolved, targeting not just the vulnerable but also those who might seem beyond reach, demanding larger ransoms and leaving a trail of psychological devastation in their wake. Cybercrime, as one expert chillingly notes, may well be the most lucrative of crimes, transcending borders, languages, and identities.
In the face of such threats, awareness is the first line of defense. Reporting suspicious activity to the FBI's Internet Crime Complaint Center, verifying the whereabouts of loved ones, and establishing emergency protocols are all steps that can fortify one's digital fortress. Telecommunications companies and law enforcement agencies also have a role to play in authenticating and tracing the source of calls, adding another layer of protection.
Conclusion
The surreal experience of reading about cyber kidnapping belies the very real danger it poses. It is a crime that thrives in the shadows of our interconnected world, a reminder that our digital lives are as vulnerable as our physical ones. As we navigate this complex web, let us arm ourselves with knowledge, vigilance, and the resolve to protect not just our data, but the very essence of our human connections.
References
- https://www.bbc.com/news/world-us-canada-67869517
- https://www.ndtv.com/feature/what-is-cyber-kidnapping-and-how-it-can-be-avoided-4792135
