
#FactCheck-AI-Generated Video Falsely Shows Samay Raina Making a Joke on Rekha
Executive Summary:
A viral video circulating on social media that appears to be deliberately misleading and manipulative is shown to have been done by comedian Samay Raina casually making a lighthearted joke about actress Rekha in the presence of host Amitabh Bachchan which left him visibly unsettled while shooting for an episode of Kaun Banega Crorepati (KBC) Influencer Special. The joke pointed to the gossip and rumors of unspoken tensions between the two Bollywood Legends. Our research has ruled out that the video is artificially manipulated and reflects a non genuine content. However, the specific joke in the video does not appear in the original KBC episode. This incident highlights the growing misuse of AI technology in creating and spreading misinformation, emphasizing the need for increased public vigilance and awareness in verifying online information.

Claim:
The claim in the video suggests that during a recent "Influencer Special" episode of KBC, Samay Raina humorously asked Amitabh Bachchan, "What do you and a circle have in common?" and then delivered the punchline, "Neither of you and circle have Rekha (line)," playing on the Hindi word "rekha," which means 'line'.ervicing routes between Amritsar, Chandigarh, Delhi, and Jaipur. This assertion is accompanied by images of a futuristic aircraft, implying that such technology is currently being used to transport commercial passengers.

Fact Check:
To check the genuineness of the claim, the whole Influencer Special episode of Kaun Banega Crorepati (KBC) which can also be found on the Sony Set India YouTube channel was carefully reviewed. Our analysis proved that no part of the episode had comedian Samay Raina cracking a joke on actress Rekha. The technical analysis using Hive moderator further found that the viral clip is AI-made.

Conclusion:
A viral video on the Internet that shows Samay Raina making a joke about Rekha during KBC was released and completely AI-generated and false. This poses a serious threat to manipulation online and that makes it all the more important to place a fact-check for any news from credible sources before putting it out. Promoting media literacy is going to be key to combating misinformation at this time, with the danger of misuse of AI-generated content.
- Claim: Fake AI Video: Samay Raina’s Rekha Joke Goes Viral
- Claimed On: X (Formally known as Twitter)
- Fact Check: False and Misleading

Related Blogs
Executive Summary
Following the reported box office success of ‘Dhurandhar 2: The Revenge’, released on March 19, 2026, a video of Ranveer Singh visiting a temple is being widely shared on social media. Users claim that the actor visited the Kashi Vishwanath Temple to offer prayers after the film’s success. Research by CyberPeace found that the viral claim is misleading. The video of Ranveer Singh visiting the Kashi Vishwanath Temple is not recent. It dates back to 2024, when he visited the temple with Kriti Sanon, and is unrelated to the release or success of ‘Dhurandhar 2: The Revenge’.
Claim
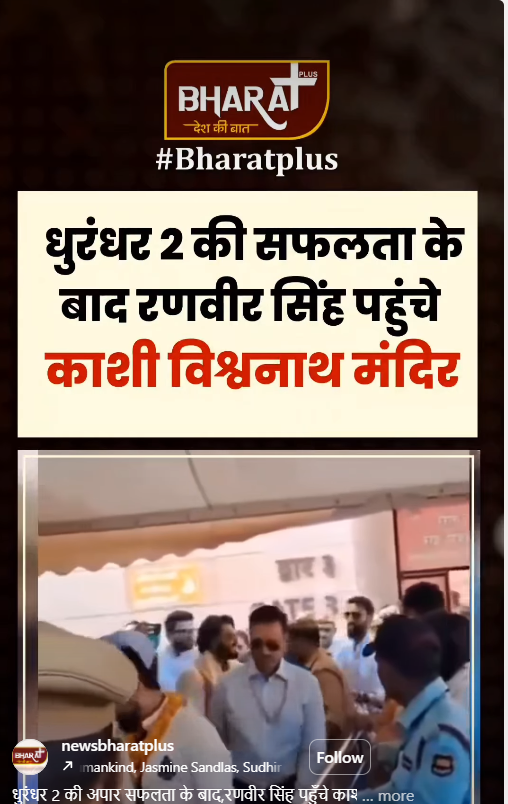
An Instagram user “newsbharatplus” shared the video on March 26, 2026, with a caption stating that after the massive success of Dhurandhar 2, Ranveer Singh visited the temple and performed rituals.
Fact Check
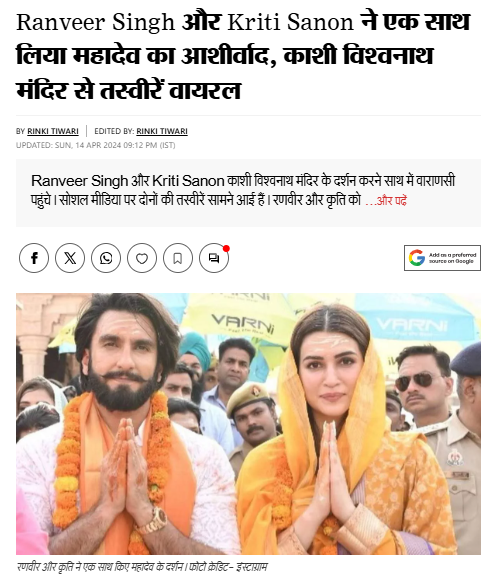
To verify the claim, we extracted keyframes from the viral video and conducted a reverse image search. This led us to a report published by Dainik Jagran on April 14, 2024. According to the report, Ranveer Singh had visited the Kashi Vishwanath Temple along with Kriti Sanon and noted fashion designer Manish Malhotra. During the visit, the trio was seen offering prayers, wearing traditional attire, and applying sandalwood tilak.
https://www.jagran.com/entertainment/bollywood-ranveer-singh-and-kriti-sanon-visits-kashi-vishwanath-temple-with-manish-malhotra-see-photos-here-23696781.html
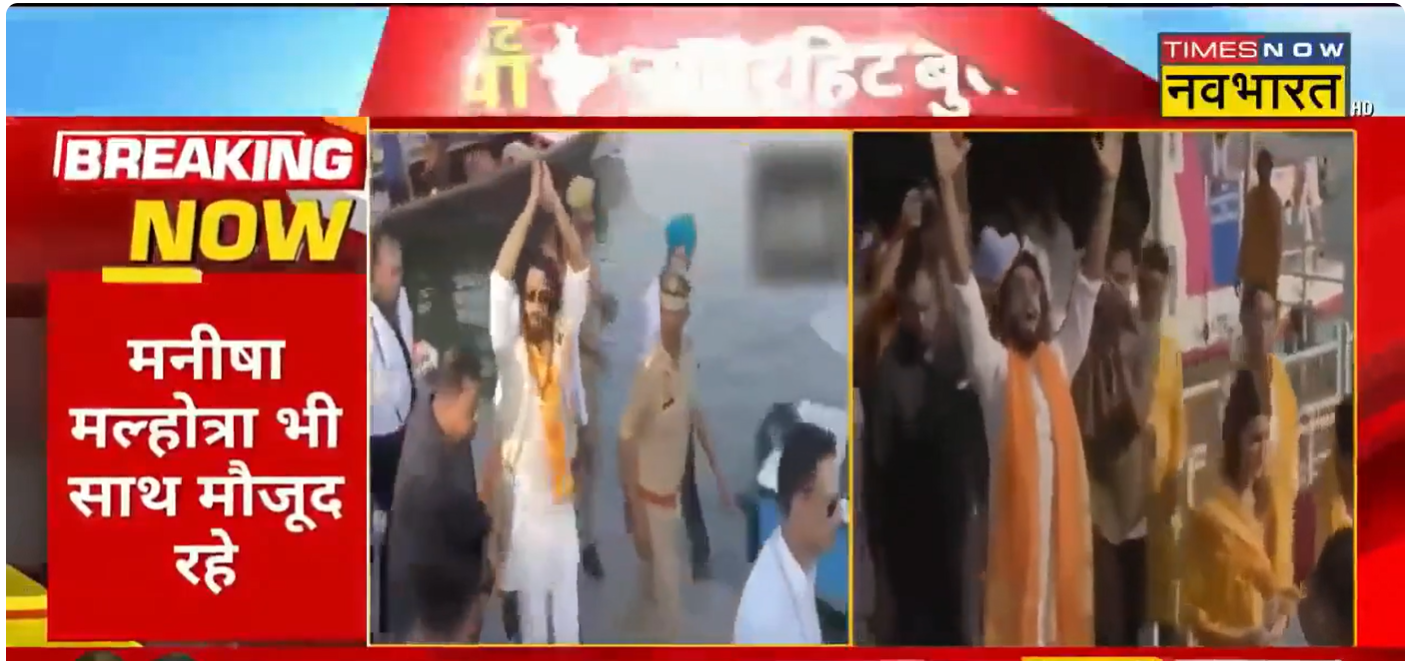
We also found a video report on the official YouTube channel of Times Now Navbharat, uploaded on April 15, 2024, showing Ranveer Singh and Kriti Sanon at the temple. The report also featured visuals from a fashion event held in Varanasi.
- https://www.youtube.com/watch?v=OMuW_SVbfb4
Conclusion
The viral claim is misleading. The video of Ranveer Singh visiting the Kashi Vishwanath Temple is not recent. It dates back to 2024, when he visited the temple with Kriti Sanon, and is unrelated to the release or success of ‘Dhurandhar 2: The Revenge’.

Introduction
The recent advisory issued by CERT, issued on April 26th, 2026, titled “Defending Against Frontier AI-Driven Cyber Risks”, on AI-driven cyber threats does not merely add to the list of routine cybersecurity warnings. Instead, it marks a shift in how cyber risk itself is understood. The concern, here, is not just that attacks are increasing, but also that their nature is changing. Artificial intelligence is no longer assisting cyber operations- whether legitimate or malicious, in fragments; it is beginning to organise and execute them at scale.
What is emerging is a situation where capability is no longer tied to human skill alone. Systems can now identify vulnerabilities, generate exploits, and carry out coordinated attacks with limited intervention. This alters the baseline assumption of cybersecurity, that attacks require effort, time, and expertise.
The Essence: Automation and Capability
At the core of the advisory lies the recognition that AI has introduced speed and autonomy into cyber operations. Tasks such as analysing code, identifying vulnerabilities, or crafting phishing content are no longer sequential processes. They can happen almost simultaneously and at scale.
This is not simply a matter of efficiency. It changes the structure of the threat itself. When attacks can be automated, they become repeatable and less dependent on specialised actors. The advisory also points to the ability of AI systems to conduct multi-stage attacks, moving across networks and adapting strategies in real time.
In a way, the threat is no longer just external. It is embedded within the logics of the technology being used.
Significance: Lower Barriers, Wider Exposure
One of the more important aspects of the advisory is its emphasis on ‘accessibility’. AI lowers the barrier of complexity in the commission of cybercrimes. Activities that once required coordinated teams can now be performed by individuals with access to advanced tools.
This has two consequences. First, the number of potential attackers increases. Second, the scale at which attacks can be carried out expands significantly. Systems that were previously considered low risk may become viable targets simply because automated tools can scan, test, and exploit them rapidly.
There is also a broader anxiety reflected in what is being described as “Mythos concerns”, a shorthand for uncertainty around frontier AI systems and their unpredictable capabilities. This signals that the risk is not fully mapped yet and that regulatory responses are still catching up.
Element of Continuous Risk
The advisory outlines impacts such as unauthorised access, data breaches, identity theft, and financial fraud. These are familiar categories. What is less explicit, but more important, is the shift in how these harms occur.
When AI enables rapid and repeated exploitation, risk becomes continuous. Systems are not attacked once and then secured. They are exposed to ongoing attempts. This creates pressure not only on technical infrastructure but also on legal frameworks that are designed around discrete incidents.
For instance, obligations under the Information Technology Act, 2000 or even emerging data protection frameworks often assume identifiable breaches and reportable events. Continuous probing complicates that model!
Response Framework: From Compliance to Vigilance
CERT-In’s recommendations reflect this change in threat perception. There is a clear emphasis on vigilance rather than mere compliance. Organisations are advised to adopt zero-trust approaches, reduce exposure surfaces, and treat vulnerabilities as immediately exploitable.
The insistence on rapid patching within short timeframes is particularly telling. It acknowledges that the window between vulnerability disclosure and exploitation is shrinking.
There is also a noticeable expansion of responsibility. The advisory does not limit itself to large organisations. It extends guidance to the MSMEs and individuals, recognising that cyber risk is now distributed across the entire digital ecosystem.
A Subtle Legal Shift
Although the advisory itself is not binding in law, it operates within the framework of Section 70B of the Information Technology Act, 2000, which empowers CERT-In to issue directions on cybersecurity best practices and guidelines.
So, while the advisory does not create liability directly, it influences what may later be considered ‘reasonable security practice’. In that sense, it serves as soft law, gradually informing standards of due diligence.
At the same time, there remains a gap. The advisory focuses on defensive measures, but it does not fully address attribution and accountability in AI driven attacks. When actions are automated and anonymised, identifying responsibility and imposing liability becomes more complex.
Conclusion
The CERT In advisory is not just a warning about new threats. It is an acknowledgement of a transition. Cyber risk is moving from being occasional and targeted to being constant and scalable. AI is not simply adding to existing threats; it is restructuring and advancing them.
For cyber vigilance frameworks, this suggests a need to rethink priorities. Static compliance measures are no longer sufficient. It has become necessary to adopt continuous monitoring, adaptive responses, and a clearer understanding of how technology is reshaping risk.
While the advisory does not resolve these questions, it does bring them into focus. And that, in itself, is significant.
References
- CERT-In issues advisory against AI driven cyber attacks for MSMEs, organisations and individuals, Moneycontrol (Apr. 27, 2026), https://www.moneycontrol.com/technology/cert-in-issues-advisory-against-ai-driven-cyber-attacks-for-msmes-organisations-and-individuals-article-13899942.html.
- CERT-In warns of rising AI driven cyber threats amid Mythos concerns, Ommcom News (2026), https://ommcomnews.com/science-tech/cert-in-warns-of-rising-ai-driven-cyber-threats-amid-mythos-concerns/.
- Indian Computer Emergency Response Team (CERT-In), Defending Against Frontier AI Driven Cyber Risks, Advisory No. CIAD-2026-0020 (Apr. 26, 2026)
- Information Technology Act, 2000, § 70B (India).

Introduction
The ramifications of cybercrime can be far-reaching. Depending on the size of the attack, even entire countries can be affected if their critical infrastructure is connected to the internet. The vast majority of security breaches start within the perimeter and most internet attacks are socially engineered. Unwittingly trusting any email or web request from an unknown sender creates a potential danger for those organisations that depend on the Internet for their business functions. In this ever-evolving digital downtown yet another group has emerged from its darkest corners of targeting the UK’s very bastion of British and global heritage; a treasure trove of around 14 million volumes, ancient manuscripts, in the precious British Library. A group self-identified as Rhysida. Their bold maneuver, executed with the stealth of seasoned cyber brigands, has cast a shadow as long and dark as those found in the Gothic novels that rest on the library's shelves. The late October cyber-attack has thrust the British Library into an unnerving state of chaos, a situation more commonly aligned with works of dystopian fiction than the everyday reality of a revered institution.
The Modus Operandi
The gang uses all-new Rhysida ransomware to jeopardize Virtual Private Networks, which is typically used by library staff to gain access to their employee’s systems remotely. The Ransomware presents itself as a regular decoy file in a familiar fashion as regular phishing attacks in an email, tricking its victim and downloading itself into the host system. Once the malware enters the system it stays dormant and lurks around the system for a period of time. The new malware has significantly reduced the dwell time from 4 days to less than 24 hours which enables it to evade periodic system checks to avoid detection.
Implications of Cyber Attack
Implications of the cyber-attack have been sobering and multifaceted. The library's systems, which serve as the lifeline for countless scholars, students, and the reading public, were left in disarray, unsettlingly reminiscent of a grand mansion invaded by incorporeal thieves. The violation has reverberated through the digital corridors of this once-impenetrable fortress, and the virtual aftershocks are ongoing. Patrons, who traverse a diverse spectrum of society, but share a common reverence for knowledge, received unsettling news: the possibility that their private data has been compromised—a sanctity breached, revealing yet again how even the most hallowed of spaces are not impervious to modern threats.
It is with no small sense of irony that we consider the nature of the stolen goods—names, email addresses, and the like. It is not the physical tomes of inestimable value that have been ransacked, but rather the digital footprints of those who sought the wisdom within the library's walls. This virtual Pandora's Box, now unleashed onto the dark web, has been tagged with a monetary value. Rhysida has set the ominous asking price of a staggering $740,000 worth of cryptocurrency for the compromised data, flaunting their theft with a hubris that chills the spine.
Yet, in this convoluted narrative unfolds a subplot that offers some measure of consolation. Payment information purports the library has not been included in this digital heist, offering a glint of reassurance amidst the prevailing uncertainty. This digital storm has had seismic repercussions: the library's website and interconnected systems have been besieged and access to the vast resources significantly hampered. The distressing notice of a 'major technology outage' transformed the digital facade from a portal for endless learning to a bulletin of sorrow, projecting the sombre message across virtual space.
The Impact
The impact of this violation will resonate far beyond the mere disruption of services; it signals the dawn of an era where venerable institutions of culture and learning must navigate the depths of cybersecurity. As the library grapples with the breach, a new front has opened in the age-old battle for the preservation of knowledge. The continuity of such an institution in a digitised world will be tested, and the outcome will define the future of digital heritage management. As the institution rallies, led by Roly Keating, its Chief Executive, one observes not a defeatist retreat, but a stoic, strategic regrouping. Gratitude is extended to patrons and partners whose patience has become as vital a resource as the knowledge the library preserves. The reassurances given, while acknowledging the laborious task ahead, signal not just an intention to repair but to fortify, to adapt, to evolve amidst adversity.
This wretched turn of events serves as a portentous reminder that threats to our most sacred spaces have transformed. The digital revolution has indeed democratised knowledge but has also exposed it to neoteric threats. The British Library, a repository of the past, must now confront a distinctly modern adversary. It requires us to posit whether our contemporary guardians of history are equipped to combat those who wield malicious code as their weapons of choice.
Best Practices for Cyber Resilience
It is crucial to keep abreast with recent developments in cyberspace and emerging trends. Libraries in the digital age must ensure the protection of their patron’s data by applying comprehensive security protocols to safeguard the integrity, availability and confidentiality of sensitive information of their patrons. A few measures that can be applied by libraries include.
- Secured Wi-Fi networks: Libraries offering public Wi-Fi facilities must secure them with strong encryption protocols such as WPA 3. Libraries should establish separate networks for internal operations allowing separation of staff and public networks to protect sensitive information.
- Staff Training Programs: To avoid human error it is imperative that comprehensive training programs are conducted on a regular basis to generate greater awareness of cyber threats among staff and educate them about best practices of cyber hygiene and data security.
- Data Backups and Recovery Protocols: Patrons' sensitive data should be updated and backed up regularly. Proper verification of the user’s data integrity is crucial and should be stored securely in a dedicated repository to ensure full recovery of the user’s data in the event of a breach.
- Strong Authentication: Strong authentication to enhance library defenses is crucial to combat cyber threats. Staff and Patrons should be educated on strong password usage and the implementation of Multi-Factor Authentication to add an extra layer of security.
Conclusion
Finally, whatever the future holds, what remains unassailable is the cultural edifice that is the British Library. Its trials and tribulations, like those of the volumes it safeguards, become a part of a larger narrative of endurance and defiance. In the canon of history—filled with conflicts and resolutions—the library, like the lighter anecdotes and tragic tales it harbours, will decidedly hold its place. And perhaps, with some assurance, we might glean from the sentiment voiced by Milton—an assurance that the path from turmoil to enlightenment, though fraught with strenuous challenges, is paved with lessons learned and resilience rediscovered. Cyberspace is constantly evolving hence it is in our best interest to keep abreast of all developments in this digital sphere. Maximum threats can be avoided if we are vigilant.
References:
