
#FactCheck -AI-Generated Video Falsely Claims Iran Unveiled B-2-Like Drone During War
Executive Summary:
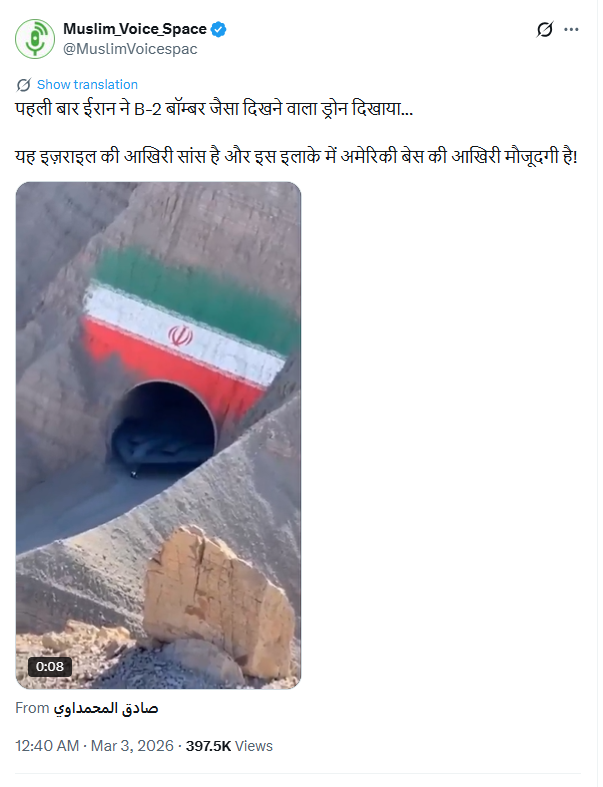
Amid the ongoing war involving the United States, Israel, and Iran, a video clip circulating on social media claims to show Iran unveiling a drone resembling the US B-2 stealth bomber. In the viral clip, an aircraft-like object can be seen emerging from a cave before taking off. Several users are sharing the video with the claim that Iran has deployed a B-2-style drone in the conflict.
However, research by the CyberPeace found that the viral video is not real and was generated using artificial intelligence. While the United States has reportedly used B-2 stealth bombers in strikes against Iran during the conflict, the viral clip does not show an actual Iranian drone.
Claim
X user “Muslim_Voice_Space” posted the video on March 3, 2026, claiming that Iran had rolled out a drone resembling the B-2 bomber for use in the war.
Fact Check
To verify the claim, we first closely examined the viral video. In the opening moments of the clip, the wing of the alleged drone appears to hit the side of the cave while exiting. Despite the apparent collision, the aircraft continues flying smoothly without any visible damage. This unusual detail raised doubts about the authenticity of the footage.
We then analyzed the video using the AI detection tool Hive Moderation, which flagged the clip as likely AI-generated.

Further analysis using the Sightengine AI detection tool also suggested that the video was artificially created. The tool estimated a 75% probability that the footage was generated using AI. It also indicated a 70% likelihood that the clip may have been created using Sora, an AI video-generation tool.

Conclusion
The viral video claiming to show an Iranian drone resembling the US B-2 stealth bomber emerging from a cave is not authentic. Analysis indicates that the clip was created using AI tools and is being misleadingly shared in the context of the ongoing conflict.

Related Blogs
Executive Summary
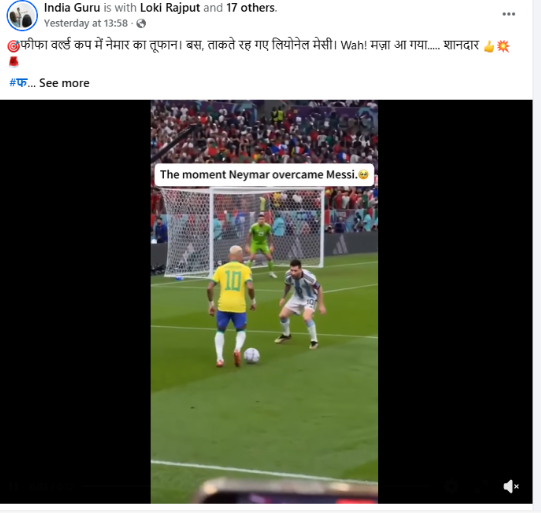
A video linked to the FIFA World Cup 2026 is being widely shared on social media. The clip appears to show a match between Brazil and Argentina, with Neymar and Lionel Messi facing each other on the field. In the video, Messi is seen trying to stop Neymar from scoring, but Neymar dribbles past him and scores a goal. The footage is being circulated as a real moment from the ongoing FIFA World Cup. CyberPeace Research Wing research found the claim to be false. The video does not depict any real football match and was created using artificial intelligence (AI).
Claim
A Facebook user named “India Guru” shared the viral video on June 25, 2026, with the caption: "Neymar’s storm in the FIFA World Cup. Lionel Messi could only watch. Wow! What a moment… Brilliant." https://www.facebook.com/reel/993162133465919 , https://perma.cc/V8SA-Y3SE
Fact Check
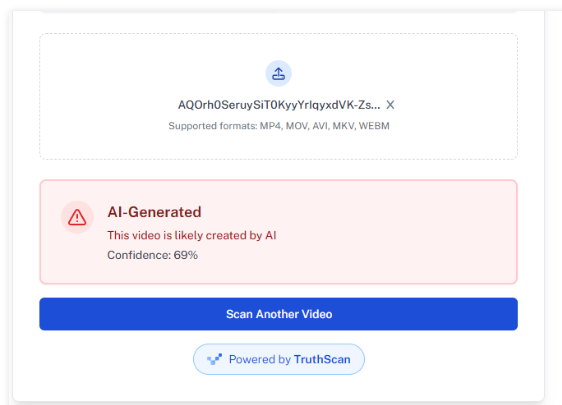
To verify the claim, we searched relevant keywords on Google. However, we found no credible news reports related to the viral video or the claims being made alongside it. We also found no evidence that Brazil and Argentina had played a match against each other during the FIFA World Cup 2026. A closer examination of the footage revealed unusual movements in the legs and body positions of both players, which appeared unnatural and inconsistent with real match footage. These visual anomalies raised suspicions that the video had been generated using artificial intelligence. The video was then analyzed using the AI detection tool Hive Moderation, which indicated a nearly 99 percent probability that the content was AI-generated.
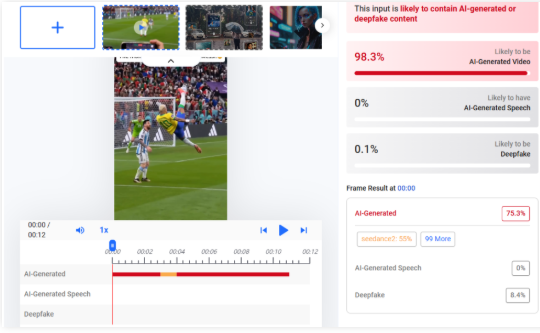
For additional verification, we also examined the clip using Undetectable AI, which similarly indicated a high likelihood that the video had been created using artificial intelligence.
Conclusion
Our research found that the viral claim linking the video to a FIFA World Cup 2026 match between Neymar and Lionel Messi is false. The footage is AI-generated and does not show a real football match.
Executive Summary
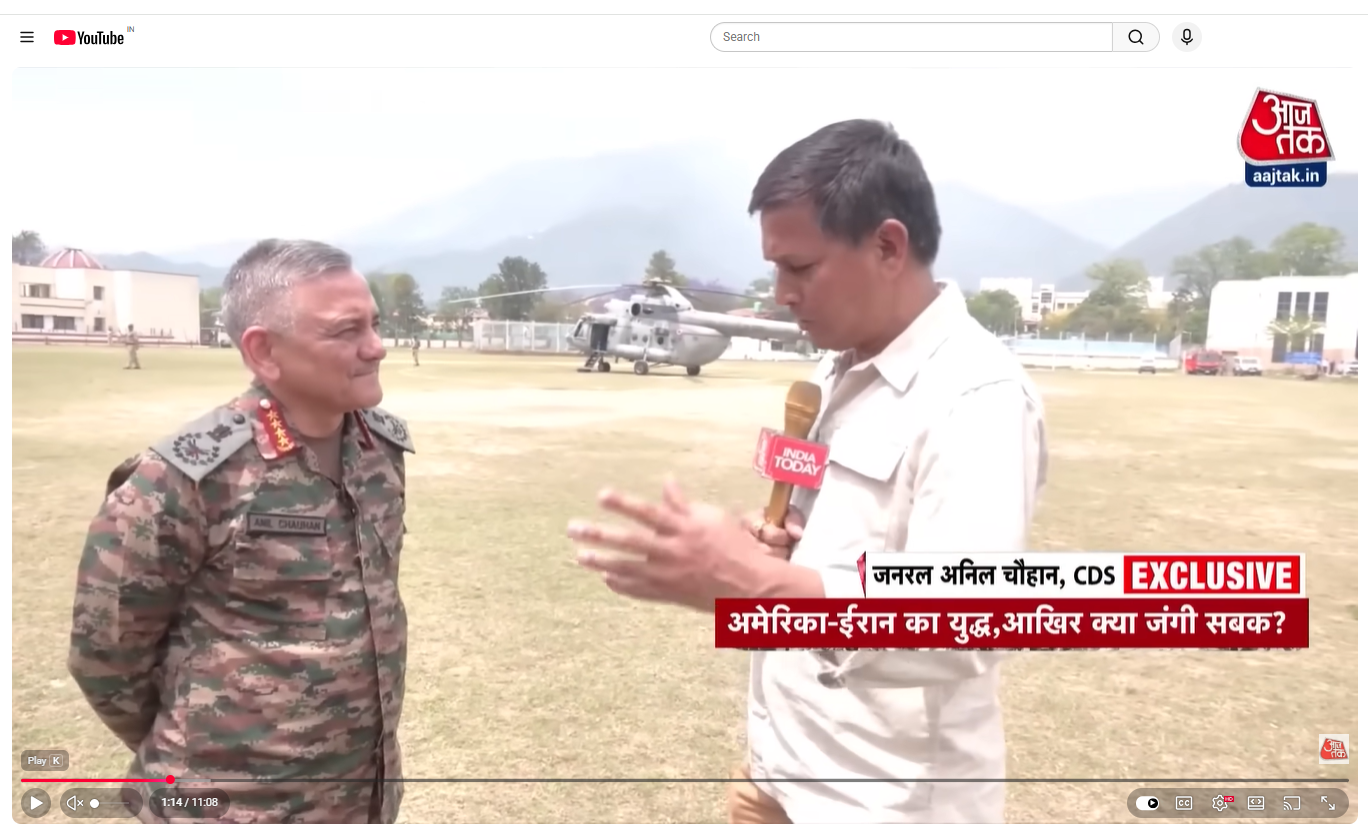
A video circulating on social media claims that Chief of Defence Staff Anil Chauhan described US leaders as “toothless rulers” and said that US President Donald Trump cannot disobey Israeli Prime Minister Benjamin Netanyahu. The clip is being widely shared as a recent statement. However, research by the CyberPeace Research Wing found the claim to be misleading. A review of the full interview revealed that Chauhan was speaking about the need for India to prepare for the next phase of ‘Operation Sindoor’. He emphasised that the armed forces must move beyond past operations and gear up for future challenges.
Claim
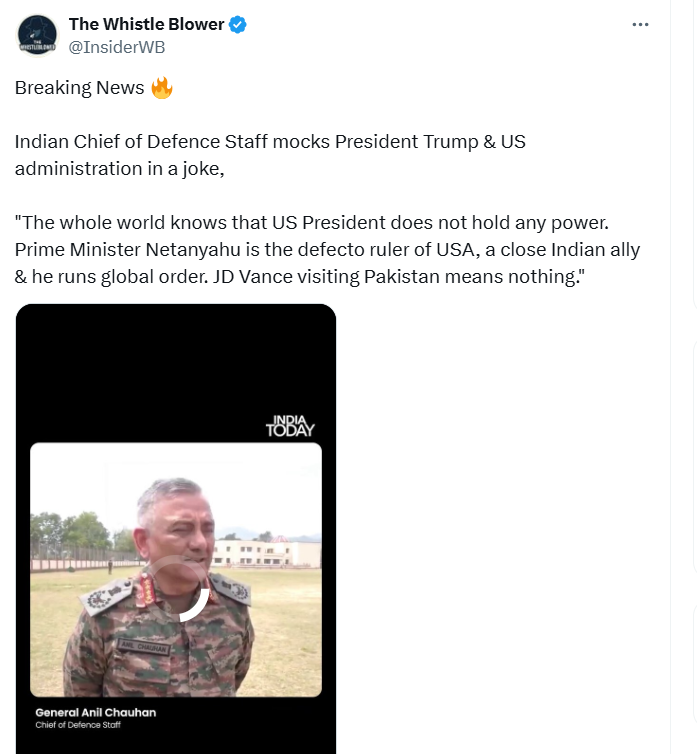
Social media users have shared the video claiming that CDS Anil Chauhan referred to US leaders as “toothless rulers” and stated that Donald Trump cannot act against the wishes of Benjamin Netanyahu.
- Link: https://x.com/InsiderWB/status/2046263000928330130
- Archive: https://archive.ph/j8CeL
Fact Check
A detailed keyword search using terms such as “CDS Anil Chauhan, Donald Trump, JD Vance, Pakistan” did not yield any credible reports or verified statements supporting the viral claim. A reverse image search of keyframes from the clip traced it back to a post shared by India Today on April 18, 2026, where the same visuals and setting were used.
https://x.com/IndiaToday/status/2045531069647327240
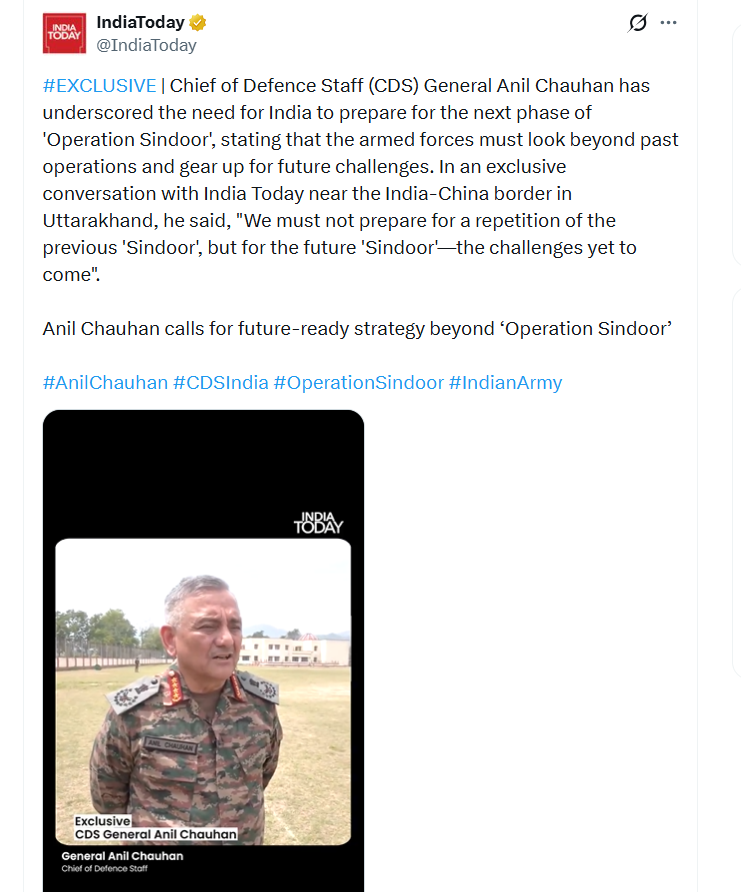
In the original interview, Chauhan focused on military preparedness and the future course of ‘Operation Sindoor’. He did not make any remarks about US leadership, Donald Trump, or Benjamin Netanyahu. The complete version of the interaction, also aired on Aaj Tak, was reviewed in full and similarly contains no such controversial or political statements.
Conclusion
The viral claim is misleading. The video has been edited or taken out of context to falsely attribute remarks to CDS Anil Chauhan that he never made. In reality, his statements were limited to India’s military preparedness and did not include any comments on US or Israeli leadership.
Introduction
How Generative Artificial Intelligence, or GenAI, is changing the employee workday is no longer limited to writing emails or debugging code, but now also includes analysing contracts, generating reports, and much more. The use of AI tools in everyday work has become commonplace, but the speed at which companies have adopted these technologies has created a new kind of risk. Unlike threats that come from an outside attacker, Shadow AI is created inside an organisation by a legitimate employee who uses unapproved AI tools to make their work more efficient and productive. In many cases, the employee is unaware of the potential security, data privacy, and compliance risks involved in using such tools to perform their job duties.
What Is Shadow AI?
Shadow AI is when individuals use AI tools at work that aren’t provided by the company, like tools or other software programs, without the knowledge or permission of the employer. Examples of shadow AI include:
- Using personal ChatGPT or other chatbot accounts to complete tasks at the office
- Uploading business-related documents to online AI technologies for analysis or summarisation.
- Copying proprietary source code into an online AI model for debugging
- Installing browser extensions and add-ons that are not approved by IT or Security personnel.
How Shadow AI Is Harmful
1. Uncontrolled Data Exposure
When employees access or input information into their user-created AI, it becomes outside the controls of the company, such as both employee personal information and any third-party personal information, private company information (such as source code or contracts), and company internal strategies. After a user enters data into their user-created AIs, the company loses all ability to monitor how that data is stored, processed, or maintained. A data leak situation exists without a malicious cyberattack. The biggest risk of a data leak is not maliciousness but rather the loss of control and governance over sensitive data.
2. Regulatory and Legal Non-Compliance
Data protection laws like GDPR, India’s Digital Personal Data Protection (DPDP) Act, HIPAA, and other relevant sectoral laws require businesses to process data in accordance with the law, to minimise the amount of data they use, and to be accountable for their actions. Shadow AI often results in the unlawful use of personal data due to a lack of a legal basis for the processing, unauthorised cross-border data transfers, and not having appropriate contractual protections in place with their AI service providers. Regulators do not see the convenience of employees as an excuse for not complying with the law, and therefore, the organisation is ultimately responsible for any violations that occur.
3. Loss of Intellectual Property
Employees frequently use AI tools to speed up tasks involving proprietary information—debugging code, reviewing contracts, or summarising internal research. When done using unapproved AI platforms, this can expose trade secrets and intellectual property, eroding competitive advantage and creating long-term business risk.
Real-Life Example: Samsung’s ChatGPT Data Leak
In 2023, a case study exemplifying the Shadow AI risk occurred when Samsung Electronics placed a temporary ban on employee access to ChatGPT and other AI tools after reports from engineers revealed they were using ChatGPT to create debugging processes for internal source code and to summarise meeting notes. Consequently, confidential source code related to semiconductors was inadvertently uploaded onto a public AI platform. While there were no known incursions into the company’s system due to this incident, Samsung faced a significant challenge: once sensitive information is input into a public AI tool, it exists on external servers that are outside of the company’s purview or control.
As a result of this incident, Samsung restricted employee use of ChatGPT on corporate devices, issued a series of internal communications prohibiting the sharing of corporate data with public AI tools, and increased the urgency of their discussions regarding the adoption of secure, enterprise-level AI (artificial intelligence) solutions.
What Organisations Are Doing Today
Many organisations respond to Shadow AI risk by:
- Blocking access at the network level
- Circulating warning emails or policies
While these actions may reduce immediate exposure, they fail to address the root cause: employees still need AI to perform their jobs efficiently. As a result, bans often push AI usage underground, increasing Shadow AI rather than eliminating it.
Why Blocking AI Does Not Work—Governance Does
History has demonstrated that prohibition does not work - we see this when trying to block access to cloud storage, instant messaging and collaboration tools. Employees are forced to use personal devices and/or accounts when their employers block AI, which means employers do not have real-time visibility into how their employees are using these technologies, and creates friction with the security and compliance team as they try to enforce the types of tools their employees can use. Prohibiting AI adoption will not stop it from being adopted; it will just create a challenge for employers regarding how safe and responsible it is. The challenge for effective organisations is therefore to shift from denial and develop governance-first AI strategies aimed at controlling data usage, protection and security, rather than merely restricting access to a list of specific tools.
Shadow AI: A Silent Legal Liability Under the GDPR
Shadow AI isn't a problem for the Information Technology Department; it is a failure of Governance, Compliance and Law. By using AI tools that have not been approved as a result, the organisation processes personal data without a lawful basis (Article 6 of the General Data Protection Regulation (GDPR)), repurposes data for use beyond its original intent and in breach of the Purpose Limitation (Article 5(1)(b)), and routinely exceeds necessity and in breach of Data Minimisation (Article 5(1)(c)). The outcome of these actions is the use of tools that involve International Data Transfers Without Authorisation and are therefore in breach of Chapter V, and violate Article 32 because there are no enforceable safeguards in place. Most significantly, the failure to demonstrate Oversight, Logging and Control under Articles 5(2) and 24 constitutes a failure in Accountability. Therefore, from a Regulatory perspective, Shadow AI is not accidental and is not defensible.
The Right Solution: Secure and Governed AI Adoption
1. Provide Approved AI Tools
Employers have an obligation to supply business-approved AI technology for helping workers to be productive while maintaining maximum protections, like storing data separately and not using employees' data for training a model; defining how long data is kept, and the rules around deleting that data. When employees are provided with verified and secure AI options that align with their work processes, they will rely significantly less on Shadow AI.
2. Enforce Zero-Trust Data Access
The governance of AI systems must follow the principles of "zero trust," granting access to data only through the principle of "least privilege," which means that data access will only be allowed by the system user, and providing continuous verification of user-identity and context; this supports and helps establish context-aware controls to monitor and track all user activities, which will be especially important as agent-like AI systems become increasingly autonomous and are capable of operating at machine-speed where even small errors in configuration, will result in rapid and large expose to data.
3. Apply DLP and Audit Logging
It is important to have robust data loss prevention measures in place to protect sensitive data that is sent outside an organisation. The first end user or machine that accesses the data should be detailed in a comprehensive audit log that indicates when and how the data is accessed. In combination with other controls, these measures create accountability, comply with regulations, and assist with appropriately detecting and responding to incidents.
4. Maintain Visibility Across AI, Cloud, and SaaS
Security teams need unified visibility across AI tools, personal cloud applications, and SaaS platforms. Risks move across systems, and controls must follow the data wherever it flows.
Conclusion
This new threat exposes an organisation to the risk of data loss through leaks, regulatory fines, liability for the loss of intellectual property, and reputational damage, all of which can occur without any intent to cause harm. The way forward is not to block AI, but to adopt a clear framework built on governance, visibility, and secure enablement. This approach allows organisations to use AI with confidence, while ensuring trust, accountability, and effective oversight to protect data and support AI in reaching its full transformative potential. AI use is encouraged, but it must be done responsibly, ethically, and securely.
References
- https://bronson.ai/resources/shadow-ai/
- https://www.varonis.com/blog/shadow-ai
- https://www.waymakeros.com/learn/gdpr-hipaa-shadow-ai-compliance-nightmare
- https://www.forbes.com/sites/siladityaray/2023/05/02/samsung-bans-chatgpt-and-other-chatbots-for-employees-after-sensitive-code-leak/
- https://www.usatoday.com/story/special/contributor-content/2025/05/23/shadow-ai-the-hidden-risk-in-todays-workplace/83822081007
