
#FactCheck -AI-Edited Video Falsely Attributes Beauty Parlour Remark to PM Modi in Fuel Conservation Speech
Executive Summary
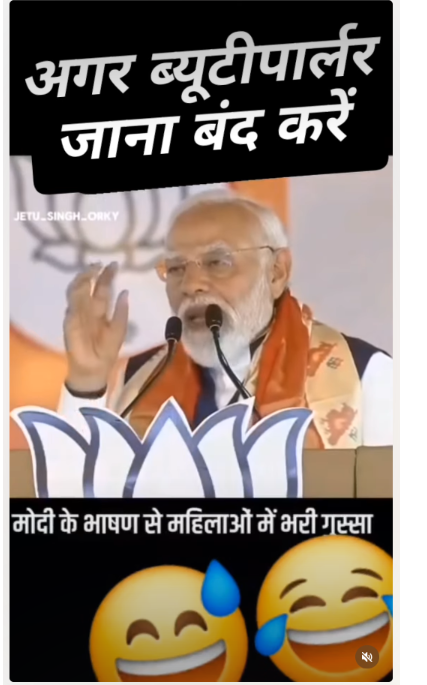
Amid ongoing tensions in West Asia, a video has been circulating on social media claiming that Prime Minister Narendra Modi urged women not to visit beauty parlours as part of an appeal related to fuel conservation. Users are widely sharing the clip as genuine. However, a fact-check by CyberPeace Research Wing has found the claim to be false. The research revealed that the original video, which discussed saving petrol, diesel and cooking gas, has been digitally edited using AI tools and shared with a misleading narrative.
Claim
An Instagram user shared the viral video on May 15, 2026, claiming that the Prime Minister advised women against visiting beauty parlours.
Fact Check
A keyword-based search on Google did not return any credible media reports supporting the viral claim. To verify the video, keyframes were extracted and run through reverse image search. The original footage was traced to the official YouTube channel of Prime Minister Narendra Modi, uploaded on May 10, 2026.
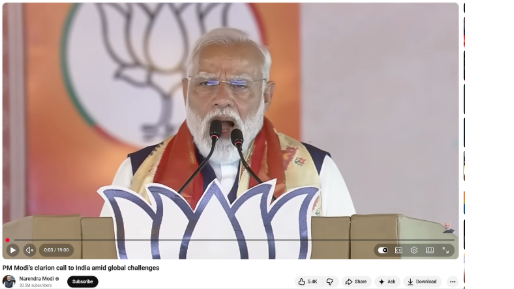
The video shows a rally held in Hyderabad, where the Prime Minister appealed to the public to save fuel by adopting work-from-home practices, promoting swadeshi goods, and refraining from purchasing gold for one year. However, nowhere in the full video is there any mention of advising women not to visit beauty parlours.
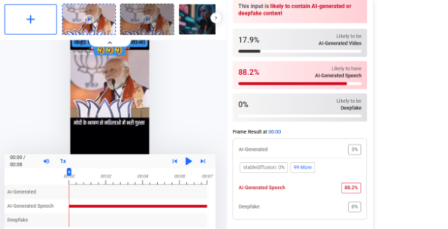
Further analysis also raised suspicion that the viral clip had been digitally altered using AI tools. The video was scanned using the HIVE Moderation AI detection tool, which indicated that it is approximately 88% likely to be AI-generated or manipulated.
Conclusion
The viral video is misleading. The original speech by Prime Minister Narendra Modi about conserving petrol, diesel and cooking gas has been edited using AI tools and circulated with a false claim targeting women visiting beauty parlours.

Related Blogs

Introduction
A famous quote, “Half knowledge is always dangerous”, but “Too much knowledge of anything can lead to destruction”. Recently very infamous spyware and malware named WyrmSpy and Dragon Egg were invented by a Chinese group of hackers APT41. The APT41 is a state-endorsed Clandstein active group based in the People’s Republic of China that has been active since 2012. In contrast to numerous countries-government supported, APT has a footprint record jeopardising both government organisations for clandestine activities as well as different private organisations or enterprises for their financial gain. APT41 group aims at Android devices through spyware wyrmspy and dragon egg, which masquerades as a legitimate application. According to the U.S. jury legal accusation from 2019 to 2020, the group was entangled in threatening over more than 100 public and private individuals and organisations in the United States and around the world.Moreover, a detailed analysis report was shared by the Lookout Threat Researchers, that has been actively monitoring and tracking both spyware and malware.
Briefing about how spyware attacks on Android devices take place
To begin with, this malware imitates a real source Android application to show some sort of notification. Once it is successfully installed on the user’s machine, proclaims multiple device’s permission to enable data filtration.
Wyrmspy complies with log files, photos, device locations, SMS(read and write), and audio recordings. It has also authenticated that there are no detection malware activities found on google play even after running multiple security levels. These malicious things are made with the intent to obtain rooting access privileges to the device and monitor activities to the specified commands received from the C2 servers.
Similarly, Dragon Egg can collect data files, contacts, locations, and audio recordings, and it also accesses camera photos once it successfully trade-off the device. Dragon egg receives a payload that is also known as “smallmload.jar”, which is either from APK(Android Packet Kit).
WyrmSpy initially masquerades as a default operation system application, and Dragon Egg simulates a third-party keyboard/ messaging application.
Overview of APT41 Chinese group background
APT41 is a Chinese-based stealth activity-carrying group that is said to be active since mid-2006. Rumours about APT41 that it was also a part of the 2nd Bureau of the People’s Liberation Army (PLA) General Staff Department’s (GSD) 3rd Department. Owning to that fact, 2006 has seen 140+ organisations’ security getting compromised, ranging from 20 strategically crucial companies.APT is also recognised for rationally plundering hundreds of terabytes of data from at least 141 organisations between 2006 and 2013. It typically begins with spear-phishing emails to the targeted victims. These sent emails contain official templates along with language pretending to be from a legitimate real source, carrying a malicious attachment. As the victim opens the attached file, the backdoor bestows the control of the targeted machine to the APT groups machine. Once there is an unauthorised gain of access, the attacker visits and revisits the victim’s machine. The group remains dormant for lengthy durations, more likely for months or even for years.
Advisory points need to adhere to while using Android devices
- The security patch update is necessary at least once a week
- Clearing up unwanted junk files.
- Cache files of every frequently used application need to clear out.
- Install only required applications from
Google play store. - Download only necessary APK files only it comes from trusted resources.
- Before giving device permission, it is advisable to run your files or URLs on VirusTotal.com this website will give a good closure to the malicious intent.
- Install good antivirus software.
- Individuals need to check the source of the email before opening an attachment to it.
- Never collect or add any randomly found device to your system
- Moreover, the user needs to keep track of their device activity. Rather than using devices just for entertainment purposes, it is more important to look for data protection on that device.
Conclusion
Network Crack Program Hacker Group (NCPH), which grew as an APT41 group with malicious intent, earlier performed the role of grey hat hacker, this group somehow grew up greedy to enhance more money laundering by hacking networks, devices, etc. As this group conducts a supply chain of attacks to gain unauthorised access to the network throughout the world, targeting hundreds of companies, including an extensive selection of industries such as social media, telecommunications, government, defence, education, and manufacturing. Last but not least, many more fraud-making groups with malicious intent will be forming and implementing in the future. It is on individuals and organisations to secure themselves but practise basic security levels to safeguard themselves against such threats and attacks.
Introduction
With the increasing reliance on digital technologies in the banking industry, cyber threats have become a significant concern. Cyberlaw plays a crucial role in safeguarding the banking sector from cybercrimes and ensuring the security and integrity of financial systems.
The banking industry has witnessed a rapid digital transformation, enabling convenient services and greater access to financial resources. However, this digitalisation also exposes the industry to cyber threats, necessitating the formulation and implementation of effective cyber law frameworks.
Recent Trends in the Banking Industry
Digital Transformation: The banking industry has embraced digital technologies, such as mobile banking, internet banking, and financial apps, to enhance customer experience and operational efficiency.
Open Banking: The concept of open banking has gained prominence, enabling data sharing between banks and third-party service providers, which introduces new cyber risks.
How Cyber Law Helps the Banking Sector
The banking sector and cyber crime share an unspoken synergy due to the mass digitisation of banking services. Thanks to QR codes, UPI and online banking payments, India is now home to 40% of global online banking transactions. Some critical aspects of the cyber law and banking sector are as follows:
Data Protection: Cyberlaw mandates banks to implement robust data protection measures, including encryption, access controls, and regular security audits, to safeguard customer data.
Incident Response and Reporting: Cyberlaw requires banks to establish incident response plans, promptly report cyber incidents to regulatory authorities, and cooperate in investigations.
Customer Protection: Cyberlaw enforces regulations related to online banking fraud, identity theft, and unauthorised transactions, ensuring that customers are protected from cybercrimes.
Legal Framework: Cyberlaw provides a legal foundation for digitalisation in the banking sector, assuring customers that regulations protect their digital transactions and data.
Cybersecurity Training and Awareness: Cyberlaw encourages banks to conduct regular training programs and create awareness among employees and customers about cyber threats, safe digital practices, and reporting procedures.

RBI Guidelines
The RBI, as India’s central banking institution, has issued comprehensive guidelines to enhance cyber resilience in the banking industry. These guidelines address various aspects, including:
Technology Risk Management
Cyber Security Framework
IT Governance
Cyber Crisis Management Plan
Incident Reporting and Response
Recent Trends in Banking Sector Frauds and the Role of Cyber Law
Phishing Attacks: Cyberlaw helps banks combat phishing attacks by imposing penalties on perpetrators and mandating preventive measures like two-factor authentication.
Insider Threats: Cyberlaw regulations emphasise the need for stringent access controls, employee background checks, and legal consequences for insiders involved in fraudulent activities.
Ransomware Attacks: Cyberlaw frameworks assist banks in dealing with ransomware attacks by enabling legal actions against hackers and promoting preventive measures, such as regular software updates and data backups.
Master Directions on Cyber Resilience and Digital Payment Security Controls for Payment System Operators (PSOs)
Draft of Master Directions on Cyber Resilience and Digital Payment Security Controls for Payment System Operators (PSOs) issued by the Reserve Bank of India (RBI). The directions provide guidelines and requirements for PSOs to improve the safety and security of their payment systems, with a focus on cyber resilience. These guidelines for PSOs include mobile payment service providers like Paytm or digital wallet payment platforms.
Here are the highlights-
The Directions aim to improve the safety and security of payment systems operated by PSOs by providing a framework for overall information security preparedness, with an emphasis on cyber resilience.
The Directions apply to all authorised non-bank PSOs.
PSOs must ensure adherence to these Directions by unregulated entities in their digital payments ecosystem, such as payment gateways, third-party service providers, vendors, and merchants.
The PSO’s Board of Directors is responsible for ensuring adequate oversight over information security risks, including cyber risk and cyber resilience. A sub-committee of the Board may be delegated with primary oversight responsibilities.
PSOs must formulate a Board-approved Information Security (IS) policy that covers roles and responsibilities, measures to identify and manage cyber security risks, training and awareness programs, and more.
PSOs should have a distinct Board-approved Cyber Crisis Management Plan (CCMP) to detect, contain, respond, and recover from cyber threats and attacks.
A senior-level executive, such as a Chief Information Security Officer (CISO), should be responsible for implementing the IS policy and the cyber resilience framework and assessing the overall information security posture of the PSO.
PSOs need to define Key Risk Indicators (KRIs) and Key Performance Indicators (KPIs) to identify potential risk events and assess the effectiveness of security controls. The sub-committee of the Board is responsible for monitoring these indicators.
PSOs should conduct a cyber risk assessment when launching new products, services, technologies, or significant changes to existing infrastructure or processes.
PSOs, including inventory management, identity and access management, network security, application security life cycle, security testing, vendor risk management, data security, patch and change management life cycle, incident response, business continuity planning, API security, employee awareness and training, and other security measures should implement various baseline information security measures and controls.
PSOs should ensure that payment transactions involving debit to accounts conducted electronically are permitted only through multi-factor authentication, except where explicitly permitted/relaxed.

Conclusion
The relationship between cyber law and the banking industry is crucial in ensuring a secure and trusted digital environment. Recent trends indicate that cyber threats are evolving and becoming more sophisticated. Compliance with cyber law provisions and adherence to guidelines such as those provided by the RBI is essential for banks to protect themselves and their customers from cybercrimes. By embracing robust cyber law frameworks, the banking industry can foster a resilient ecosystem that enables innovation while safeguarding the interests of all stakeholders or users.

Along with the loss of important files and information, data loss can result in downtime and lost revenue. Unexpected occurrences, including natural catastrophes, cyber-attacks, hardware malfunctions, and human mistakes, can result in the loss of crucial data. Recovery from these without a backup plan may be difficult, if not impossible.
The fact is that the largest threat to the continuation of your organization today is cyberattacks. Because of this, disaster recovery planning should be approached from a data security standpoint. If not, you run the risk of leaving your vital systems exposed to a cyberattack. Cybercrime has been more frequent and violent over the past few years. In the past, major organizations and global businesses were the main targets of these attacks by criminals. But nowadays, businesses of all sizes need to be cautious of digital risks.
Many firms might suffer a financial hit even from a brief interruption to regular business operations. But imagine if a situation forced a company to close for a few days or perhaps weeks! The consequences would be disastrous.
One must have a comprehensive disaster recovery plan in place that is connected with the cybersecurity strategy, given the growing danger of cybercrime.
Let’s look at why having a solid data security plan and a dependable backup solution are essential for safeguarding a company from external digital threats.
1. Apply layered approaches
One must specifically use precautionary measures like antivirus software and firewalls. One must also implement strict access control procedures to restrict who may access the network.
One must also implement strict access control procedures to restrict who may access the network.
2. Understand the threat situation
If someone is unaware of the difficulties one should be prepared for, how can they possibly expect to develop a successful cybersecurity strategy? They can’t, is the simple response.
Without a solid understanding of the threat landscape, developing the plan will require a lot too much speculation. With this strategy, one can allocate resources poorly or perhaps completely miss a threat.
Because of this, one should educate themselves on the many cyber risks that businesses now must contend with.
3. Adopt a proactive security stance
Every effective cybersecurity plan includes a number of reactive processes that aren’t activated until an attack occurs. Although these reactive strategies will always be useful in cybersecurity, the main focus of your plan should be proactiveness.
There are several methods to be proactive, but the most crucial one is to analyze your network for possible threats regularly. your network securely. Having a SaaS Security Posture Management (SSPM) solution in place is beneficial for SaaS applications, in particular.
A preventive approach can lessen the effects of a data breach and aid in keeping data away from attackers.
4. Evaluate your ability to respond to incidents
Test your cybersecurity disaster recovery plan’s effectiveness by conducting exercises and evaluating the outcomes. Track pertinent data during the exercise to see if your plan is working as expected.
Meet with your team after each drill to evaluate what went well and what didn’t. This strategy enables you to continuously strengthen your plan and solve weaknesses. This procedure may be repeated endlessly and should be.
You must include cybersecurity protections in your entire disaster recovery plan if you want to make sure that your business is resilient in the face of cyber threats. You may strengthen data security and recover from data loss and corruption by putting in place a plan that focuses on both the essential components of proactive data protection and automated data backup and recovery.
For instance, Google distributes all data among several computers in various places while storing each user’s data on a single machine or collection of machines. To prevent a single point of failure, chunk the data and duplicate it across several platforms. As an additional security safeguard, they give these data chunks random names that are unreadable to the human eye.[1]
The process of creating and storing copies of data that may be used to safeguard organizations against data loss is referred to as backup and recovery. In the case of a main data failure, the backup’s goal is to make a duplicate of the data that can be restored.
5. Take zero-trust principles
Don’t presume that anything or anybody can be trusted; zero trust is a new label for an old idea. Check each device, user, service, or other entity’s trustworthiness before providing it access, then periodically recheck trustworthiness while access is allowed to make sure the entity hasn’t been hacked. Reduce the consequences of any breach of confidence by granting each entity access to only the resources it requires. The number of events and the severity of those that do happen can both be decreased by using zero-trust principles.
6. Understand the dangers posed by supply networks
A nation-state can effectively penetrate a single business, and that business may provide thousands of other businesses with tainted technological goods or services. These businesses will then become compromised, which might disclose their own customers’ data to the original attackers or result in compromised services being offered to customers. Millions of businesses and people might be harmed as a result of what began with one infiltrating corporation.
In conclusion, a defense-in-depth approach to cybersecurity won’t vanish. Organizations may never be able to totally eliminate the danger of a cyberattack, but having a variety of technologies and procedures in place can assist in guaranteeing that the risks are kept to a minimum.
