
#FactCheck - Viral Video Misrepresented as Reaction to Pakistan’s Defeat in T20 World Cup
Executive Summary
A video is being widely shared on social media with the claim that Baloch people celebrated by dancing after Pakistan’s crushing defeat to India in the T20 World Cup. However, research by the CyberPeace found the claim to be misleading. The video is actually from a Lohri celebration held on January 23 at Government College University in Lahore, and is unrelated to any cricket match. India defeated Pakistan by 61 runs in the T20 World Cup 2026 match held in Colombo last Sunday. India scored 175 runs for the loss of seven wickets in 20 overs, while Pakistan were bowled out for 114 runs in 18 overs.
Claim
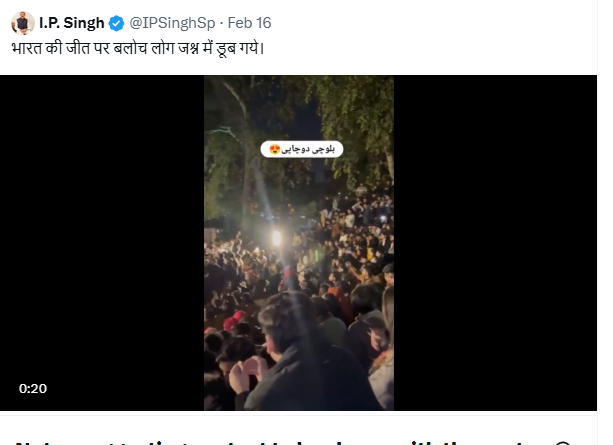
The 30-second video was shared on X with the caption, “Baloch people celebrate India’s victory.” The footage shows a group of men dressed in traditional attire dancing around a fire, while a large crowd gathers around and applauds.
Fact Check
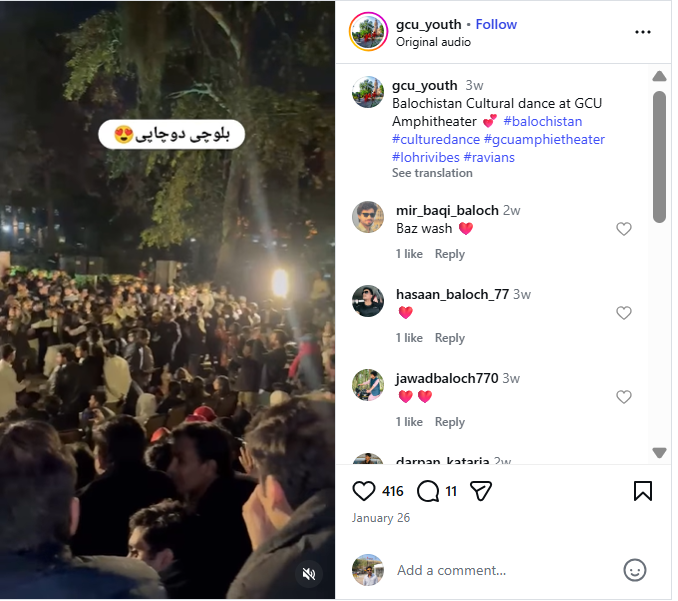
To verify the authenticity of the viral claim, key frames from the video were extracted and subjected to reverse image search. The search led to an Instagram post uploaded on January 26, 2026, by an account associated with Government College University Lahore. The caption described the performance as a Balochistan cultural dance held at the university’s amphitheatre.
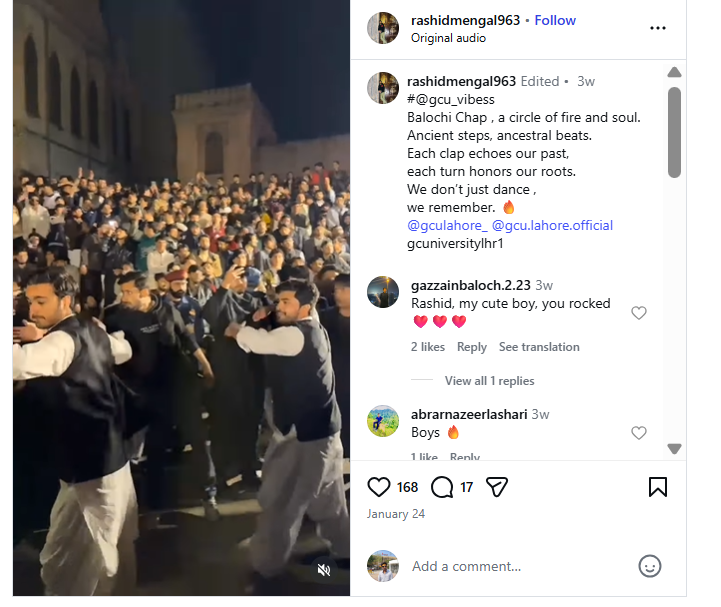
Further research also uncovered another video of the same event, recorded from a different angle and uploaded on January 24, 2026, on Instagram. The caption again confirmed that the event took place at Government College University Lahore.
Conclusion
The evidence confirms that the viral video does not show Baloch people celebrating Pakistan’s defeat in the T20 World Cup. Instead, it depicts a cultural dance performance during a Lohri celebration at Government College University Lahore, and has been shared with a misleading claim.

Related Blogs
Introduction
The advancement of technology has brought about remarkable changes in the aviation industry, including the introduction of inflight internet access systems. While these systems provide passengers with connectivity during their flights, they also introduce potential vulnerabilities that can compromise the security of aircraft systems.
Inflight Internet Access Systems
Inflight internet access systems have become integral to the modern air travel experience, allowing passengers to stay connected even at 30,000 feet. However, these systems can also be attractive targets for hackers, raising concerns about the safety and security of aircraft operations.
The Vulnerabilities of Inflight Internet Access Systems:
Securing Networked Avionics
Avionics, the electronic systems that support aircraft operation, play a crucial role in flight safety and navigation. While networked avionics are designed with robust security measures, they are not invulnerable to cyber threats. Therefore, it is essential to implement comprehensive security measures to protect these critical systems.
- Ensuring Robust Architecture: Networked avionics should be designed with a strong focus on security. Implementing secure network architectures, such as segmentation and isolation, can minimise the risk of unauthorised access and limit the potential impact of a breach.
- Rigorous Security Testing: Avionics systems should undergo rigorous security testing to identify vulnerabilities and weaknesses. Regular assessments, penetration testing, and vulnerability scanning are essential to proactively address any security flaws.
- Collaborative Industry Efforts: Collaboration between manufacturers, airlines, regulatory bodies, and security researchers is crucial in strengthening the security of networked avionics. Sharing information, best practices, and lessons learned can help identify and address emerging threats effectively.
- Continuous Monitoring and Updtes: Networked avionics should be continuously monitored for any potential security breaches. Prompt updates and patches should be applied to address newly discovered vulnerabilities and protect against known attack vectors.
Best practices to be adopted for the security of Aircraft Systems
- Holistic Security Approach: Recognizing the interconnectedness of inflight internet access systems and networked avionics is essential. A holistic security approach should be adopted to address vulnerabilities in both systems and protect the overall aircraft infrastructure.
- Comprehensive Security Measures: The security of inflight internet access systems should be on par with any other internet-connected device. Strong authentication, encryption, intrusion detection, and prevention systems should be implemented to mitigate risks and ensure the integrity of data transmissions.
- Responsible Practices and Industry Collaboration: Encouraging responsible practices and fostering collaboration between security researchers and industry stakeholders can accelerate the identification and remediation of vulnerabilities. Open communication channels and a cooperative mindset are vital in addressing emerging threats effectively.
- Robust Access Controls: Strong access controls, such as multi-factor authentication and role-based access, should be implemented to limit unauthorised access to avionics systems. Only authorised personnel should have the necessary privileges to interact with these critical systems.
Conclusion
Inflight internet access systems bring convenience and connectivity to air travel but also introduce potential risks to the security of aircraft systems. It is crucial to understand and address the vulnerabilities associated with these systems to protect networked avionics and ensure passenger safety. By implementing robust security measures, conducting regular assessments, fostering collaboration, and adopting a comprehensive approach to aircraft cybersecurity, the aviation industry can mitigate the risks and navigate the sky with enhanced safety and confidence. Inflight internet access systems and networked avionics are vital components of modern aircraft, providing connectivity and supporting critical flight operations. Balancing connectivity and cybersecurity is crucial to ensure the safety and integrity of aircraft systems.
Introduction
Recently, a Consultation Paper on Regulatory Mechanisms for Over-The-Top (OTT) Communication Services was published by the Telecom Regulatory Authority of India (TRAI). The paper explores several OTT regulation-related challenges and solicits input from stakeholders on a suggested regulatory framework. We’ll summarise the paper’s main conclusions in this blog.
Structure of the Paper
The Telecom Regulatory Authority of India’s Consultation Paper on Regulatory Mechanism for Over-The-Top (OTT) Communication Services and Selective Banning of OTT Services intends to solicit comments and recommendations from stakeholders about the regulation of OTT services in India. The paper is broken up into five chapters that cover the introduction and background, issues with regulatory mechanisms for OTT communication services, issues with the selective banning of OTT services, a summary of the issues for consultation, and an overview of international practices on the topic. Written comments from interested parties are requested and may be sent electronically to the Advisor (Networks, Spectrum and Licencing) at TRAI. These comments will also be posted on the TRAI website.
Overview of the Paper
- Chapter 1: Introduction and Background
- The first chapter of the essay introduces the subject of OTT communication services and argues why regulatory frameworks are necessary. The chapter also gives a general outline of the topics and the paper’s organisation that will be covered in the following chapters.
- Chapter 2: Examination of the Issues Related to Regulatory Mechanism for Over-The-Top Communication Services
- The second chapter of the essay looks at the problems with OTT communication service regulation. It talks about the many kinds of OTT services and how they affect the conventional telecom sector. The chapter also looks at the regulatory issues raised by OTT services and the various strategies used by various nations to address them.
- Chapter 3: Examination of the Issues Related to Selective Banning of OTT Services
- The final chapter of the essay looks at the problems of selectively outlawing OTT services. It analyses the justifications for government restrictions on OTT services as well as the possible effects of such restrictions on consumers and the telecom sector. The chapter also looks at the legal and regulatory structures that determine how OTT services are prohibited in various nations.
- Chapter 4: International Practices
- An overview of global OTT communication service best practices is given in the paper’s fourth chapter. It talks about the various regulatory strategies used by nations throughout the world and how they affect consumers and the telecom sector. The chapter also looks at the difficulties regulators encounter when trying to create efficient regulatory frameworks for OTT services.
- Chapter 5: Issues for Consultation
- This chapter is the spirit of the consultation paper as it covers the points and questions for consultation. This chapter has been classified into two sub-sections – Issues Related to Regulatory Mechanisms for OTT Communication Services and Issues Related to the Selective Banning of OTT Services. The inputs will be entirely focused on these sub headers, and the scope, extent, and ambit of the consultation paper rests on these questions and necessary inputs.
Conclusion
An important publication that aims to address the regulatory issues raised by OTT services is the Consultation Paper on Regulatory Mechanisms for Over-The-Top Communication Services. The paper offers a thorough analysis of the problems with OTT service regulation and requests input from stakeholders on the suggested regulatory structure. In order to make sure that the regulatory framework is efficient and advantageous for everyone, it is crucial for all stakeholders to offer their opinion on the document.

Introduction
The whole world is shifting towards a cashless economy, with innovative payment transaction systems such as UPI payments, card payments, etc. These payment systems require processing, storage, and movement of millions of cardholders data which is crucial for any successful transaction.
And therefore to maintain the credibility of this payment ecosystem, security or secure movement and processing of cardholders data becomes paramount. Entities involved in a payment ecosystem are responsible for the security of cardholders data. Security is also important because if breaches happen in cardholders data it would amount to financial loss. Fraudsters are attempting smart ways to leverage any kind of security loopholes in the payment system.
So these entities which are involved in the payment ecosystem need to maintain some security standards set by one council of network providers in the payment industry popularly known as the Payment Card Industry Security Standard Council.
Overview of what is PCI and PCI DSS Compliance
Earlier every network providers in the payment industry have their own set of security standards but later they all together i.e., Visa, Mastercard, American Express, Discover, and JCB constituted an independent body to come up with comprehensive security standards like PCI DSS, PA DSS, PCI-PTS, etc. And these network providers ensure the enforcement of the security standards by putting conditions on services being provided to the merchant or acquirer bank.
In other words, PCI DSS particularly is the global standard that provides a baseline of technical and operational requirements designed to protect account data. PCI DSS is a security standard specially designed for merchants and service providers in the payment ecosystem to protect the cardholders data against any fraud or theft.
It applies to all the entities including third-party vendors which are involved in processing storing and transmitting cardholders data. In organization, even all CDE (Card Holder Data Environment) including system components or network component that stores and process cardholders data, has to comply with all the requirements of PCI compliance. Recently PCI has released a new version of PCI DSS v4.0 a few months ago with certain changes from the previous version after three years of the review cycle.
12 Requirements of PCI DSS
This is the most important part of PCI DSS as following these requirements can make any organization to some extent PCI compliant. So what are these requirements:
- Installing firewalls or maintaining security controls in the networks
- Use strong password in order to secure the CDE( Card holders data environment)
- Protection of cardholder data
- Encrypting the cardholder data during transmission over an open and public network.
- Timely detection and protection of the cardholders data environment from any malicious activity or software.
- Regular updating the software thereby maintaining a secure system.
- Rule of business need to know should apply to access the cardholders data
- Identification and authentication of the user are important to access the system components.
- Physical access to cardholders data should be restricted.
- Monitoring or screening of system components to know the malicious activity internally in real-time.
- Regular auditing of security control and finding any vulnerabilities available in the systems.
- Make policies and programs accordingly in order to support information security.
How organization can become PCI compliant
- Scope: First step is to determine all the system components or networks storing and processing cardholders data i.e., Cardholders Data Environment.
- Assess: Then test whether these systems or networks are complying with all the requirements of PCI DSS COMPLIANCE.
- Report: Documenting all the assessment through self assessment questionnaire by answering following questions like whether the requirements are met or not? Whether the requirements are met with customized approach.
- Attest: Then the next step is to complete the attestation process available on the website of PCI SSC.
- Submit: Then organization can submit all the documents including reports and other supporting documents if it is requested by other entities such as payment brands, merchant or acquirer.
- Remediate: Then the organisation should take remedial action for the requirements which are not in place on the system components or networks.
Conclusion
One of the most important issues facing those involved in the digital payment ecosystem is cybersecurity. The likelihood of being exposed to cybersecurity hazards including online fraud, information theft, and virus assaults is rising as more and more users prefer using digital payments.
And thus complying and adopting with these security standards is the need of the hour. And moreover RBI has also mandated all the regulated entities ( NBFCs Banks etc) under one recent notification to comply with these standards.
