
#FactCheck - Viral Clip and Newspaper Article Claiming 18% GST on 'Good Morning' Messages Debunked
Executive Summary
A recent viral message on social media such as X and Facebook, claims that the Indian Government will start charging an 18% GST on "good morning" texts from April 1, 2024. This news is misinformation. The message includes a newspaper clipping and a video that was actually part of a fake news report from 2018. The newspaper article from Navbharat Times, published on March 2, 2018, was clearly intended as a joke. In addition to this, we also found a video of ABP News, originally aired on March 20, 2018, was part of a fact-checking segment that debunked the rumor of a GST on greetings.

Claims:
The claim circulating online suggests that the Government will start applying a 18% of GST on all "Good Morning" texts sent through mobile phones from 1st of April, this year. This tax would be added to the monthly mobile bills.


Fact Check:
When we received the news, we first did some relevant keyword searches regarding the news. We found a Facebook Video by ABP News titled Viral Sach: ‘Govt to impose 18% GST on sending good morning messages on WhatsApp?’

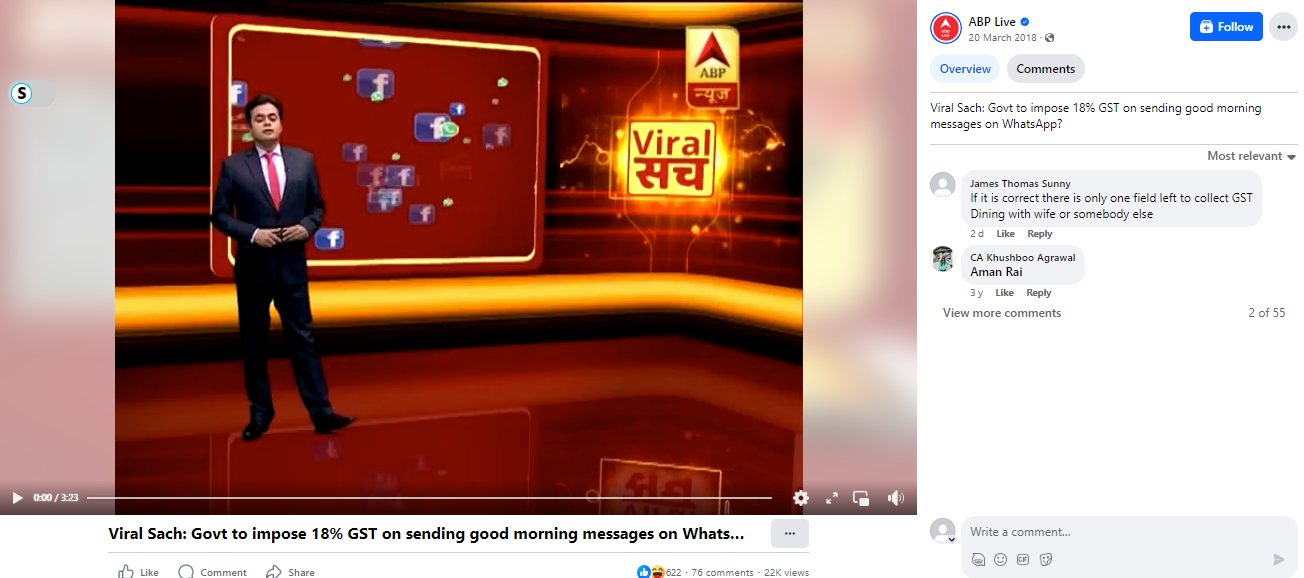
We have watched the full video and found out that the News is 6 years old. The Research Wing of CyberPeace Foundation also found the full version of the widely shared ABP News clip on its website, dated March 20, 2018. The video showed a newspaper clipping from Navbharat Times, published on March 2, 2018, which had a humorous article with the saying "Bura na mano, Holi hain." The recent viral image is a cutout image from ABP News that dates back to the year 2018.
Hence, the recent image that is spreading widely is Fake and Misleading.
Conclusion:
The viral message claiming that the government will impose GST (Goods and Services Tax) on "Good morning" messages is completely fake. The newspaper clipping used in the message is from an old comic article published by Navbharat Times, while the clip and image from ABP News have been taken out of context to spread false information.
Claim: India will introduce a Goods and Services Tax (GST) of 18% on all "good morning" messages sent through mobile phones from April 1, 2024.
Claimed on: Facebook, X
Fact Check: Fake, made as Comic article by Navbharat Times on 2 March 2018

Related Blogs
Executive Summary
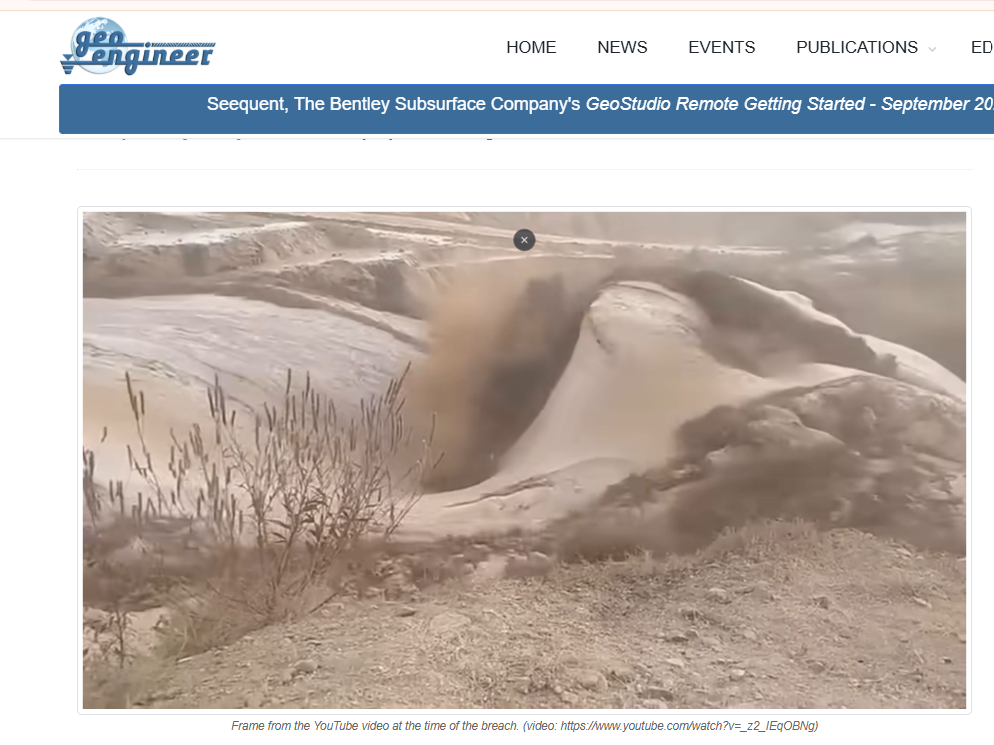
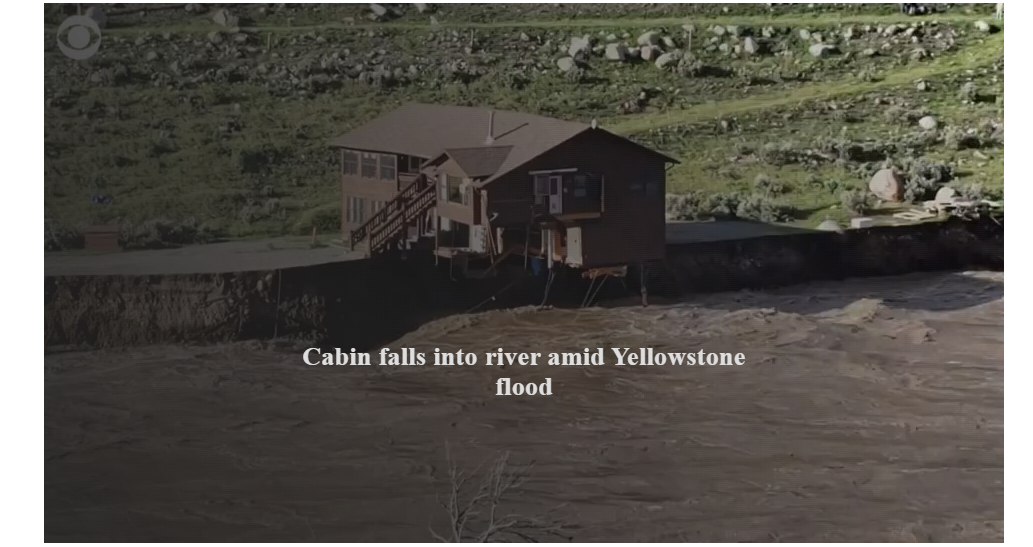
Following the flash floods that struck the Nepal-Tibet border on Wednesday morning, 289 bodies have so far been recovered, while around 1,500 people remain missing. A large number of foreign nationals, along with Nepali citizens, are also among those reported missing. Meanwhile, a video showing a massive landslide is being widely circulated on social media. The viral clip is actually a compilation of two separate videos. The first shows a landslide rapidly turning into a torrent of muddy floodwater, while the second shows a two-storey house on a riverbank being swept away by rising floodwaters. A research done by the Research Wing of the CyberPeace found that both videos are old and unrelated to Nepal. The first video is from Myanmar, while the second was recorded in the United States.
Claim:
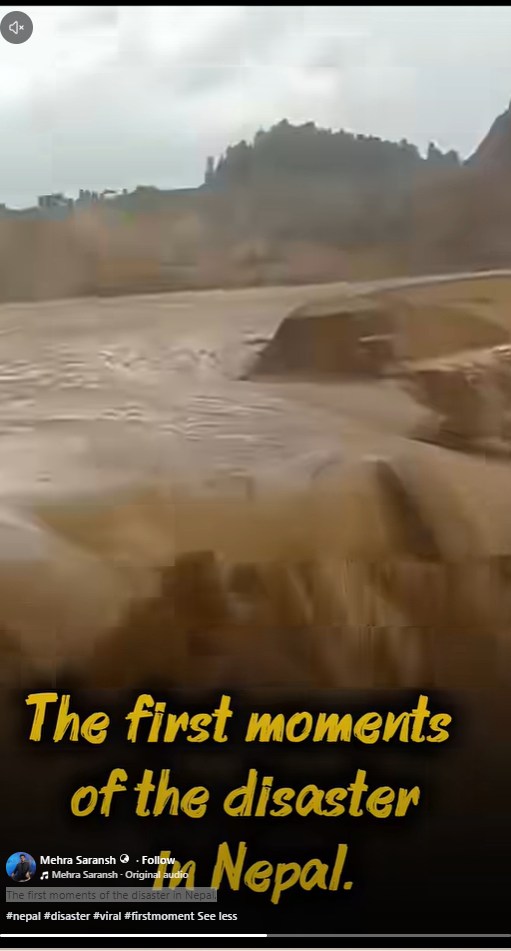
A user on social media platform Facebook shared the video, claiming that it shows the initial scenes of the devastating floods and landslides that struck Nepal.
https://www.facebook.com/reel/1572666177989617
Fact Check:
To verify the first video, we conducted a reverse image search of its keyframes. During the search, we found a longer version of the same footage, which was shared on an Instagram account on June 30. This confirmed that the viral clip is unrelated to the recent floods in Nepal.
https://www.instagram.com/reels/DaLtKtjzTtq/
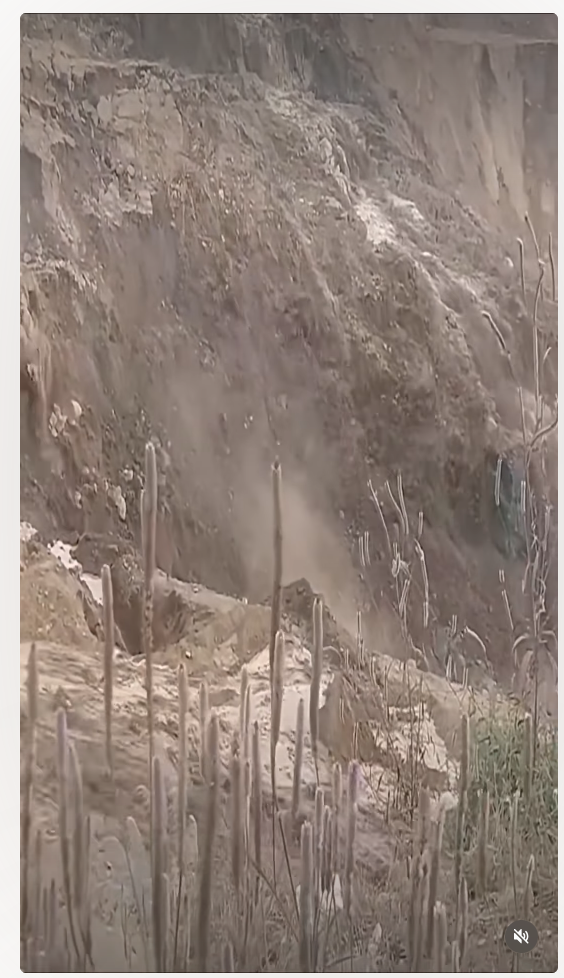
During the research, we also found the full version of the video on a YouTube channel, where it was uploaded on January 28, 2024. Although the video caption did not clearly specify the location of the incident, it mentioned Myanmar several times. This confirms that the viral video is old footage from Myanmar and not related to the recent disaster in Nepal.
https://www.youtube.com/watch?v=_z2_IEqOBNg&t=3s
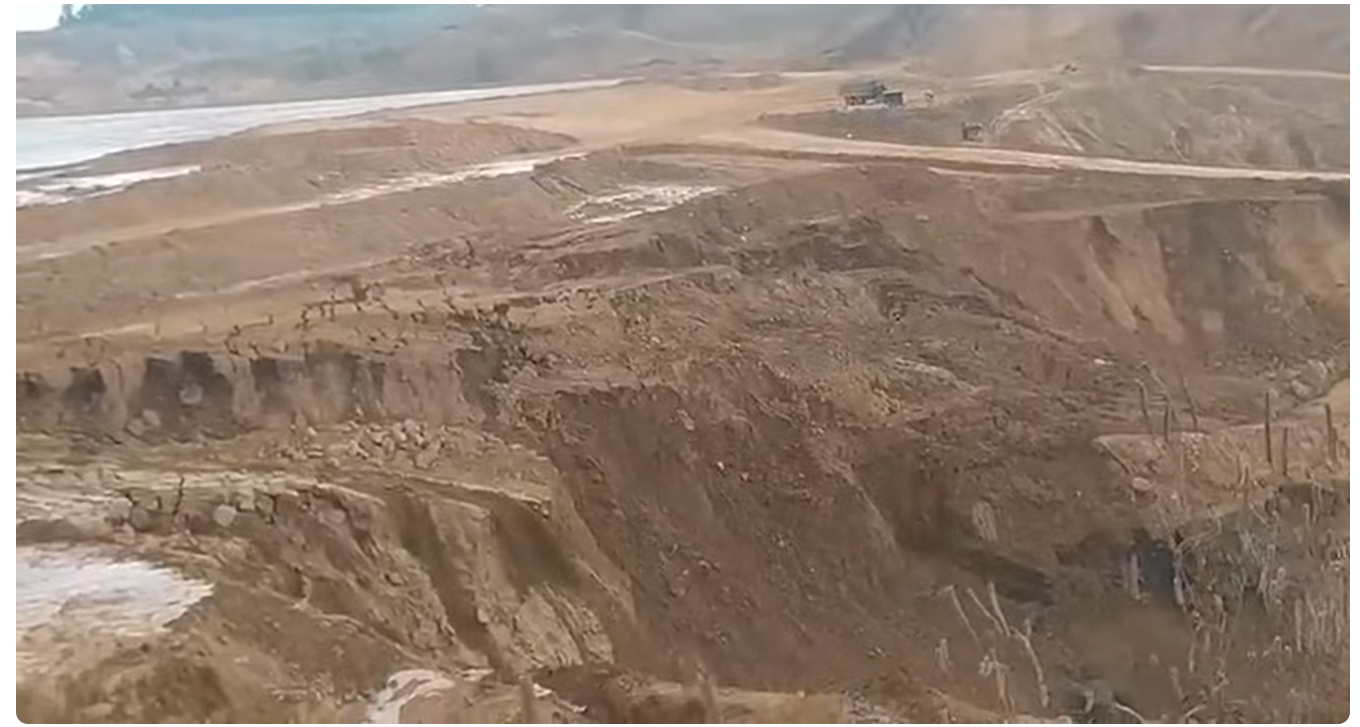
We found another report, published on January 25, 2024, that carried screenshots from the viral footage. It stated that the incident took place between January 24 and 25, 2024, in Myanmar’s Hpakant mining area. Further verification led us to a report published by EOS.org, the digital science news outlet of the American Geophysical Union. The report examined the incident by comparing Planet Labs satellite imagery captured before and after the event, providing further evidence about the location of the incident.
https://www.geoengineer.org/news/mine-waste-dam-failure-in-myanmar-caught-on-video
https://eos.org/thelandslideblog/myanmar-1
Second Clip
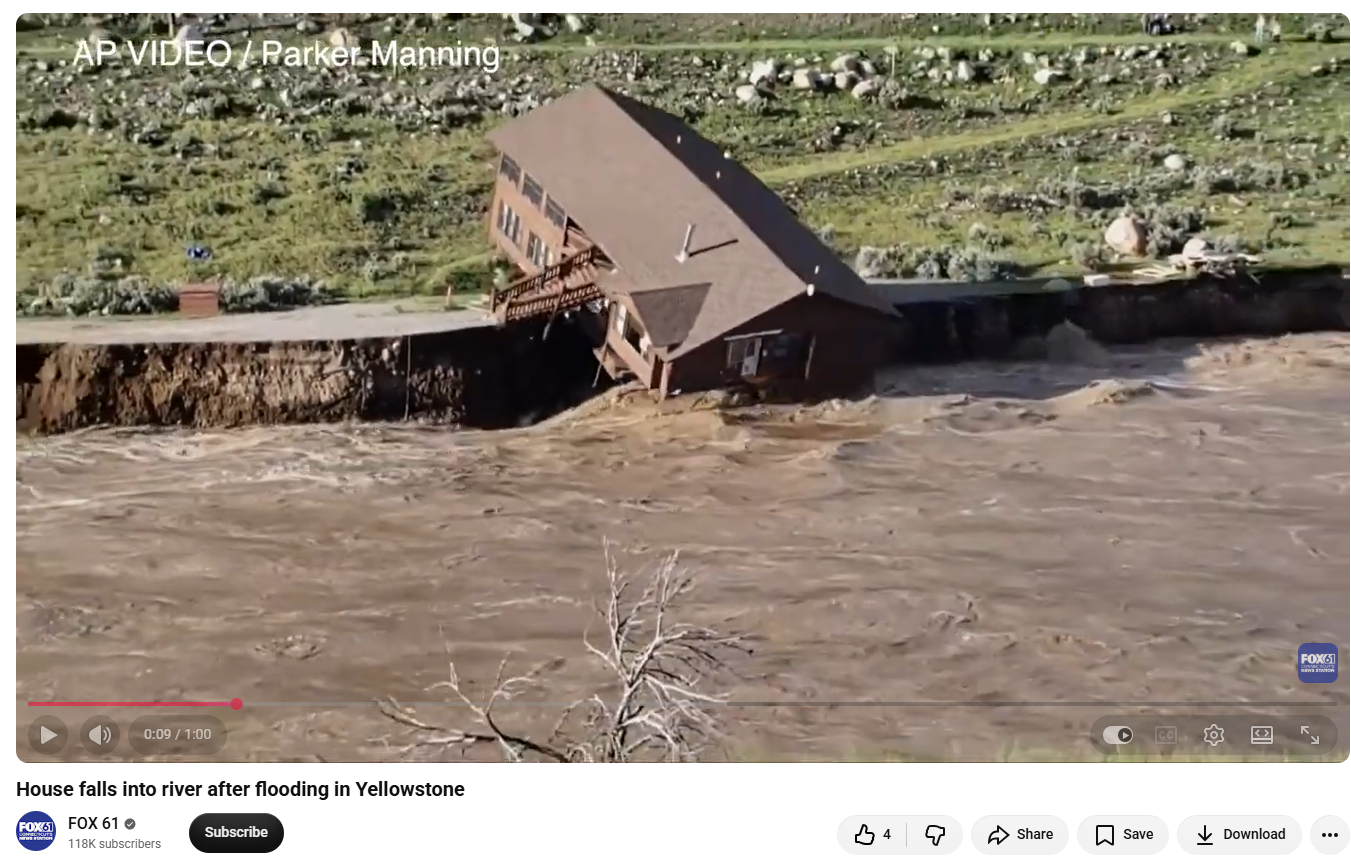
For the second clip, a reverse image search of its keyframes led us to a CBC report dated June 14, 2022, which carried a photograph of the same two-storey house seen in the viral footage. The report identified the location as Gardiner, Montana, USA, where the Yellowstone River experienced severe flooding and a rapid rise in water levels. It also stated that the house belonged to Parker Manning, who recorded the footage himself while vacationing with his family at a spot roughly half a mile upstream from the house.
https://www.cbsnews.com/news/yellowstone-flooding-video-house-collapses-river/
We also found a post related to the viral video on FOX 61, where the footage was shared with a generic caption. The link to the post and a screenshot are provided below.
Conclusion
Our research found that both videos are old and unrelated to Nepal. The first video is from Myanmar, while the second is from the United States.

Introduction
Quantum mechanics is not a new field. It finds its roots in the works of physicists such as Niels Bohr in the 1920s, and has informed the development of technologies like nuclear power in the past. But with developments in science and engineering, we are at the cusp of harnessing quantum mechanics for a new wave of real-world uses in sensing and metrology, computing, networking, security, and more. While at different stages of development, quantum technologies have the potential to revolutionise global security, economic systems, and digital infrastructure. The science is dazzling, but it is equally urgent to start preparing for its broader impact on society, especially regarding privacy and digital security. This article explores quantum computing, its threat to information integrity, and global interdependencies as they exist today, and discusses policy areas that should be addressed.
What Is Quantum Computing?
Classical computers use binary bits (0 or 1) to represent and process information. This binary system forms the base of modern computing. But quantum computers use qubits (quantum bits) as a basic unit, which can exist in multiple states ( 0, 1, both, or with other qubits) simultaneously due to quantum principles like superposition and entanglement. This creates an infinite range of possibilities in information processing and allows quantum machines to perform complex computations at speeds impossible for traditional computers. While still in their early stages, large-scale quantum computers could eventually:
- Break modern encryption systems
- Model complex molecules for drug discovery
- Optimise global logistics and financial systems
- Accelerate AI and machine learning
While this could eventually present significant opportunities in fields such as health innovation, material sciences, climate modelling, and cybersecurity, challenges will continue to arise even before the technology is ready for commercial application. Policymakers must start anticipating their impact.
Threats
Policy solutions surrounding quantum technologies will depend on the pace of development of the elements of the quantum ecosystem. However, the most urgent concerns regarding quantum computing applications are the risk to encryption and the impact on market competition.
1. Cybersecurity Threat: Digital infrastructure today (e.g., cloud services, networks, servers, etc.) across sectors such as government, banking and finance, healthcare, energy, etc., depends on encryption for secure data handling and communications. Threat actors can utilise quantum computers to break this encryption. Widely used asymmetric encryption keys, such as RSA or ECC, are particularly susceptible to being broken. Threat actors could "harvest now, decrypt later”- steal encrypted data now and decrypt it later when quantum capabilities mature. Although AES-256, a symmetric encryption standard, is currently considered resistant to quantum decryption, it only protects data after a secure connection is established through a process that today relies on RSA or ECC. This is why governments and companies are racing to adopt Post- Quantum Cryptography (PQC) and quantum key distribution (QKD) to protect security and privacy in digital infrastructure.
2. Market Monopoly: Quantum computing demands significant investments in infrastructure, talent, and research, which only a handful of countries and companies currently possess. As a result, firms that develop early quantum advantage may gain unprecedented competitive leverage through offerings such as quantum-as-a-service, disrupting encryption-dependent industries, or accelerating innovation in pharmaceuticals, finance, and logistics. This could reinforce the existing power asymmetries in the global digital economy. Given these challenges, proactive and forward-looking policy frameworks are critical.
What Should Quantum Computing Policy Cover?
Commercial quantum computing will transform many industries. Policy will have to be flexible and be developed in iterations to account for fast-paced developments in the field. It will also require enduring international collaboration to effectively address a broad range of concerns, including ethics, security, privacy, competition, and workforce implications.
1. Cybersecurity and Encryption: Quantum policy should prioritise the development and standardisation of quantum-resistant encryption methods. This includes ongoing research into Post-Quantum Cryptography (PQC) algorithms and their integration into digital infrastructure. Global policy will need to align national efforts with international standards to create unified quantum-safe encryption protocols.
2. Market Competition and Access: Given the high barriers to entry, regulatory frameworks should promote fair competition, enabling smaller players like startups and developing economies to participate meaningfully in the quantum economy. Frameworks to ensure equitable access, interoperability, and fair competition will become imperative as the quantum ecosystem matures so that society can reap its benefits as a whole.
4. Ethical Considerations: Policymakers will have to consider the impact on privacy and security, and push for the responsible use of quantum capabilities. This includes ensuring that quantum advances do not contribute to cybercrime, disproportionate surveillance, or human rights violations.
5. International Standard-Setting: Setting benchmarks, shared terminologies, and measurement standards will ensure interoperability and security across diverse stakeholders and facilitate global collaboration in quantum research and infrastructure.
6. Military and Defence Implications: Militarisation of quantum technologies is a growing concern, and national security affairs related to quantum espionage are being urgently explored. Nations will have to develop regulations to protect sensitive data and intellectual property from quantum-enabled attacks.
7. Workforce Development and Education: Policies should encourage quantum computing education at various levels to ensure a steady pipeline of talent and foster cross-disciplinary programs that blend quantum computing with fields like machine learning, AI, and engineering.
8. Environmental and Societal Impact: Quantum computing hardware requires specialised conditions such as extreme cooling. Policy will have to address the environmental footprint of the infrastructure and energy consumption of large-scale quantum systems. Broader societal impacts of quantum computing, including potential job displacement, accessibility issues, and the equitable distribution of quantum computing benefits, will have to be explored.
Conclusion
Like nuclear power and AI, the new wave of quantum technologies is expected to be an exciting paradigm shift for society. While they can bring numerous benefits to commercial operations and address societal challenges, they also pose significant risks to global information security. Quantum policy will require regulatory, strategic, and ethical frameworks to govern the rise of these technologies, especially as they intersect with national security, global competition, and privacy. Policymakers must act in collaboration to mitigate unethical use of these technologies and the entrenchment of digital divides across countries. The OECD’s Anticipatory Governance of Emerging Technologies provides a framework of essential values like respect for human rights, privacy, and sustainable development, which can be used to set a baseline, so that quantum computing and related technologies benefit society as a whole.
References
- https://www.weforum.org/stories/2024/07/explainer-what-is-quantum-technology/
- https://www.paconsulting.com/insights/what-is-quantum-technology
- https://delinea.com/blog/quantum-safe-encryption#:~:text=This%20can%20result%20in%20AES,%2D128%20to%20AES%2D256.
- https://www.oecd.org/en/publications/a-quantum-technologies-policy-primer_fd1153c3-en.html
Introduction
Web applications are essential in various sectors, including online shopping, social networks, banking, and healthcare systems. However, they also pose numerous security threats, including Cross-Site Scripting (XSS), a client-side code injection vulnerability. XSS attacks exploit the trust relationship between users and websites, allowing them to change web content, steal private information, hijack sessions, and gain full control of user accounts without breaking into the core server. This vulnerability is part of the OWASP Top 10 Web Application Security Risks.
What is Cross-Site Scripting (XSS)?
An XSS attack occurs when an attacker injects client-side scripts into web pages viewed by other users. When users visit the affected pages, their browsers naively execute the inserted scripts. The exploit takes advantage of web applications that allow users to submit content without properly sanitising inputs or encoding outputs. These scripts can cause a wide range of damage, including but not limited to stealing session cookies for session hijacking, redirecting users to malicious sites, logging keystrokes to capture credentials, and altering the DOM to display fake or phishing content.
How Does XSS Work?
- Injection: A malicious user submits code through a website input, like a comment or form.
- Execution: The submitted code runs automatically in the browsers of other users who view the page.
- Exploitation:The attacker can steal session information, capture credentials, redirect users, or modify the page content.
The fundamental cause behind the XSS vulnerabilities is the application of:
- Accepting trusted input from the users.
- After users' input, web pages have the strings embedded without any sanitisation.
- Not abiding by security policies like Content Security Policy (CSP).
With such vulnerabilities, attackers can generate malicious payloads like: <script>alert('XSS');</script>
This code might seem simple, but its execution provides the attacker with the possibility to do the following:
- Copy session tokens through hidden HTTP requests.
- From attacker-controlled domains, load attacker scripts.
- Change the DOM structure to show fake login forms for phishing.
Types of XSS Attacks: XSS (Cross-Site Scripting) attacks can occur in three main variations:
- Stored XSS: This type of attack occurs when an attacker injects an administered payload into the database or a message board. The script then runs whenever a user visits the affected board.
- Reflected XSS: In this attack, the danger lies in a parameter of the URL. Its social engineering techniques are attacks, in which it requires tricking people to click on a specially designed link. For example:
- DOM-Based XSS: This technique injects anything harmful without the need for server-side scripts, in contrast to other approaches. It targets JavaScript client-side scripts such as `document.write` and `innerHTML`. Without carrying out any safety checks, these scripts will alter the page's look (DOM stands for Document Object Model). If the hash is given a malicious string, it is run directly within the browser.
What Makes XSS a Threat?
A Cross-Site Scripting attack is only a primary attack vector, and can lead to significant damage that includes the following:
- Statement Hijacking. This uses scripts to steal cookies, which are then used to pose as authorized users.
- Theft of Credentials. Users’ passwords and usernames are wrenched from keystroke trackers.
- Phishing. Users are prompted with deceitful login forms that are used to capture sensitive details.
- Website Vandalism. Modified website material lowers the esteem of the brand.
- Monetary and Legal Consequences. There are compounding effects to GDPR and DPDP Act compliance in case of Data breaches, which incur penalties and fines.
Incidents in the Real World
In 2021, an XSS Stored attack occurred on a famous e-commerce platform eBay, through their product review system. The malicious JavaScript code was set to trigger every time an infected product page was accessed by customers. This caused a lot of problems, including account takeovers, unauthorised purchases, and damage to the company’s reputation. This example further worsens the fact that even reputed platforms can be targeted by XSS attacks.
How to Prevent XSS?
Addressing XSS vulnerabilities demands attention to detail and coordinated efforts across functions, as illustrated in the steps below:
Input Validation and Output Encoding:
- Ensure input validation is in place on the client and server.
- Perform output encoding relative to context: HTML: <, >, &.
- JavaScript: Escape quotes and slashes
Content Security Policy (CSP): CSP allows scripts to be executed only from the verified sources, which helps diminish the odds of harmful scripts running on your website. For example, the Header in the code could look to some degree like this: Content-Security-Policy: script-src 'self';
Unsafe APIs should be dodged: Avoid the use of document.write(), innerHTML, and eval(), and make sure to use:
- TextContent for inserting text.
- CreateElement() and other DOM creation methods for structured content.
Secure Cookies: Apply the HttpOnly and Secure cookie flags to block JavaScript access.
Framework Protections: Use the protective features in frameworks such as:
- React, which escapes data embedded in JSX automatically.
- Angular, which uses context-aware sanitisation.
Periodic Security Assessment:
- Use DAST tools to test the security posture of an application.
- Perform thorough penetration testing and security-oriented code reviews.
Best Practices for Developers: Assume a Secure Development Lifecycle (SDLC) integrating XSS stoppage at each point.
- Educate developers on OWASP secure coding guidelines.
- Automate scanning for vulnerabilities in CI/CD pipelines.
Conclusion:
To reduce the potential danger of XSS, both developers and companies must be diligent in their safety initiatives, ranging from using Content Security Policies (CSP) to verifying user input. Web applications can shield consumers and the company from the subtle but long-lasting threat of Cross-Site Scripting if security controls are implemented during the web application development stage and regular vulnerability scans are conducted.
References
- https://owasp.org/www-community/attacks/xss/
- https://www.paloaltonetworks.com/cyberpedia/xss-cross-site-scripting
- https://developer.mozilla.org/en-US/docs/Glossary/Cross-site_scripting
- https://www.cloudflare.com/learning/security/threats/cross-site-scripting/
