
#FactCheck - MS Dhoni Sculpture Falsely Portrayed as Chanakya 3D Recreation
Executive Summary:
A widely used news on social media is that a 3D model of Chanakya, supposedly made by Magadha DS University matches with MS Dhoni. However, fact-checking reveals that it is a 3D model of MS Dhoni not Chanakya. This MS Dhoni-3D model was created by artist Ankur Khatri and Magadha DS University does not appear to exist in the World. Khatri uploaded the model on ArtStation, calling it an MS Dhoni similarity study.

Claims:
The image being shared is claimed to be a 3D rendering of the ancient philosopher Chanakya created by Magadha DS University. However, people are noticing a striking similarity to the Indian cricketer MS Dhoni in the image.


Fact Check:
After receiving the post, we ran a reverse image search on the image. We landed on a Portfolio of a freelance character model named Ankur Khatri. We found the viral image over there and he gave a headline to the work as “MS Dhoni likeness study”. We also found some other character models in his portfolio.


Subsequently, we searched for the mentioned University which was named as Magadha DS University. But found no University with the same name, instead the name is Magadh University and it is located in Bodhgaya, Bihar. We searched the internet for any model, made by Magadh University but found nothing. The next step was to conduct an analysis on the Freelance Character artist profile, where we found that he has a dedicated Instagram channel where he posted a detailed video of his creative process that resulted in the MS Dhoni character model.

We concluded that the viral image is not a reconstruction of Indian philosopher Chanakya but a reconstruction of Cricketer MS Dhoni created by an artist named Ankur Khatri, not any University named Magadha DS.
Conclusion:
The viral claim that the 3D model is a recreation of the ancient philosopher Chanakya by a university called Magadha DS University is False and Misleading. In reality, the model is a digital artwork of former Indian cricket captain MS Dhoni, created by artist Ankur Khatri. There is no evidence of a Magadha DS University existence. There is a university named Magadh University in Bodh Gaya, Bihar despite its similar name, we found no evidence in the model's creation. Therefore, the claim is debunked, and the image is confirmed to be a depiction of MS Dhoni, not Chanakya.

Related Blogs
Executive Summary:
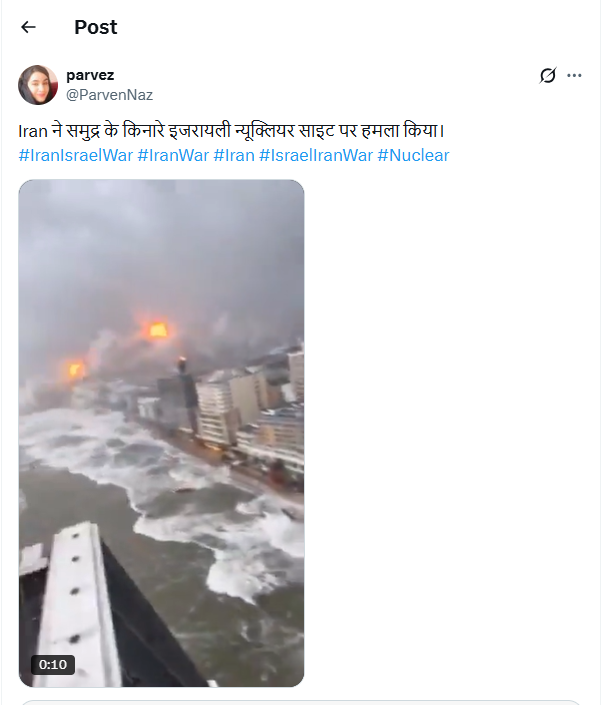
A video is going viral on social media linking it to the ongoing conflict between the US-Israel and Iran. The clip shows explosions on buildings and is being shared with the claim that it depicts an attack on Israel. It is further claimed that Iran targeted a nuclear site located near the sea in Israel, and this video shows that attack. However, an research by the CyberPeace found the claim to be false. The video is not from a real incident but has been created using AI.
Claim:
On social media platform X, a user shared the viral video on March 8, 2026, with the caption: “Iran attacked an Israeli nuclear site located near the sea.”
Fact Check:
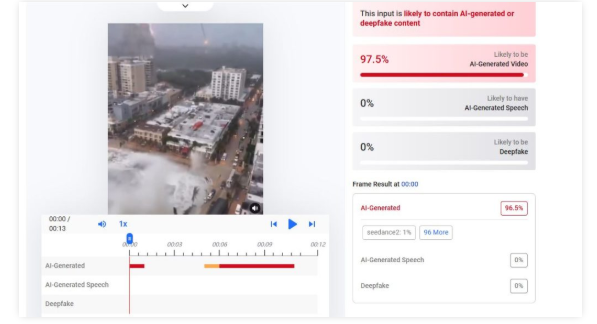
To verify the viral claim, we searched relevant keywords on Google but found no credible news reports supporting it.On closely examining the video, we observed several technical inconsistencies. The person seen in the video appears robotic, raising suspicion that the content may be AI-generated. To confirm this, we analyzed the video using AI detection tools. The tool Hive Moderation indicated that the video is approximately 97.5 percent likely to be generated using artificial intelligence.
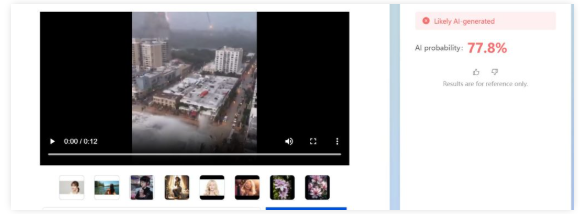
We also used the AI detection tool Matrix.Tencent. The results suggested that the video is likely AI-generated, with around a 77 percent probability.
Conclusion:
Our research found that the viral video claiming to show an Iranian attack on Israel is AI-generated and not related to any real incident.

Introduction:
With improved capabilities and evasion strategies, the Vultur banking Trojan has reappeared and is a serious danger to Android users. The virus now employs numerous encrypted payloads, encrypted communication, and poses as legitimate apps. It is transmitted by trojanized dropper programs on the Google Play Store. Vultur targets victims via phone calls and SMS messages. With the help of this updated version of Vultur, attackers may take total control of compromised devices. They can perform a variety of remote control operations like install, remove, upload, and download files, halt the execution of programs, and circumvent the lock screen. The virus is now far more hazardous than it was previously because of its improved capacity to remotely access and manipulate machines.
Overview:
The Android banking malware Vultur is well-known for its ability to record screens. It was first identified by ThreatFabric in March 2021 and targets banking apps for remote control and keylogging.
The malicious apps were hosted on the Google Play Store by the Brunhilda dropper-framework, which was used for its distribution. Initial versions of the program used reputable remote access tools such as ngrok and AlphaVNC.
Hybrid attacks have been used in recent operations to disseminate the Brunhilda dropper via phone calls and SMS. The dropper uses a number of payloads to distribute an upgraded version of Vultur.
41 new Firebase Cloud Messaging (FCM) commands and seven new Command-and-Control (C2) methods are included in the most recent version of Vultur.
With the help of Android's Accessibility Services, these enhancements concentrate on remote access functionality that improves the malware's capacity to communicate with the victim's screen.
Modus operandi of Attack:
Hybrid Attack Method:
- Utilizes a phone call, two SMS messages, and trick users into installing malware.
- First SMS tricks victims into calling a certain number by claiming to have made significant, unlawful transactions, which gives the impression of urgency.
- Although there was no transaction in reality, the urgency motivates victims to act quickly.
Trozonized MacAfee App:
- The victims are told to install a trojanized version of the McAfee Security program from a given link during the phone call.
- This app looks harmless and has features similar to the original McAfee Security app, but it's actually the Brunhilda dropper.
- The victims are misled into assuming that the security software they are installing is authentic.
Execution of Vultur Payloads:
- Three payloads connected to Vultur are decrypted and executed via the Brunhilda dropper.
- Threat actors can carry out a variety of malicious operations, including keylogging and screen recording, on the victim's mobile device thanks to these payloads, which grant them total access over it.
- The infected device of the victim allows the threat actors to launch additional assaults or obtain private data.
Indication of the attack:
The symptoms of a Vultur banking Trojan infection include:
- Remote Access: This malware gives the hacker the ability to remotely use the infected device via clicking, scrolling, and swiping through Android's accessibility services.
- File Management: Through this, the malware is able to copy, share, remove, create, and locate files from devices it has infected.
- App Blocking: For instance; the malicious software can be programmed to stop the victims from opening a certain bunch of apps.
- Custom Notifications: Attackers can embed the malware with the functionality of displaying the customized notifications in the taskbar.
- Keyguard Disabling: The malware may be designed to turn off Screen Lock Guard feature so the lock screen security measure can be easily bypassed.
- Encrypted C2 Communication: The malware chooses AES data encryption, with Base64 text encoding to provide hidden traces for C2 communication.
- Payload Decryption: The malware uses native code, mostly written in C as well as C++, to decode the goods, thus, making a process of reversing more complicated.
- Spying on Financial Apps: The malware uses screen-streaming and keylogging as ways of acquiring facts about the victim’s mobile banking applications.
Indicator of Compromise:
File hash (SHA-256)
- edef007f1ca60fdf75a7d5c5ffe09f1fc3fb560153633ec18c5ddb46cc75ea21
- 89625cf2caed9028b41121c4589d9e35fa7981a2381aa293d4979b36cf5c8ff2
- 1fc81b03703d64339d1417a079720bf0480fece3d017c303d88d18c70c7aabc3
- 4fed4a42aadea8b3e937856318f9fbd056e2f46c19a6316df0660921dd5ba6c5
- 001fd4af41df8883957c515703e9b6b08e36fde3fd1d127b283ee75a32d575fc
- fc8c69bddd40a24d6d28fbf0c0d43a1a57067b19e6c3cc07e2664ef4879c221b
- 7337a79d832a57531b20b09c2fc17b4257a6d4e93fcaeb961eb7c6a95b071a06
- 7f1a344d8141e75c69a3c5cf61197f1d4b5038053fd777a68589ecdb29168e0c
- 26f9e19c2a82d2ed4d940c2ec535ff2aba8583ae3867502899a7790fe3628400
- 2a97ed20f1ae2ea5ef2b162d61279b2f9b68eba7cf27920e2a82a115fd68e31f
- c0f3cb3d837d39aa3abccada0b4ecdb840621a8539519c104b27e2a646d7d50d
- 92af567452ecd02e48a2ebc762a318ce526ab28e192e89407cac9df3c317e78d
- fa6111216966a98561a2af9e4ac97db036bcd551635be5b230995faad40b7607
- dc4f24f07d99e4e34d1f50de0535f88ea52cc62bfb520452bdd730b94d6d8c0e
- 627529bb010b98511cfa1ad1aaa08760b158f4733e2bbccfd54050838c7b7fa3
- f5ce27a49eaf59292f11af07851383e7d721a4d60019f3aceb8ca914259056af
- 5d86c9afd1d33e4affa9ba61225aded26ecaeb01755eeb861bb4db9bbb39191c
- 5724589c46f3e469dc9f048e1e2601b8d7d1bafcc54e3d9460bc0adeeada022d
- 7f1a344d8141e75c69a3c5cf61197f1d4b5038053fd777a68589ecdb29168e0c
- fd3b36455e58ba3531e8cce0326cce782723cc5d1cc0998b775e07e6c2622160
- 819044d01e8726a47fc5970efc80ceddea0ac9bf7c1c5d08b293f0ae571369a9
- 0f2f8adce0f1e1971cba5851e383846b68e5504679d916d7dad10133cc965851
- fb1e68ee3509993d0fe767b0372752d2fec8f5b0bf03d5c10a30b042a830ae1a
- d3dc4e22611ed20d700b6dd292ffddbc595c42453f18879f2ae4693a4d4d925a
- f4d7e9ec4eda034c29b8d73d479084658858f56e67909c2ffedf9223d7ca9bd2
- 7ca6989ccfb0ad0571aef7b263125410a5037976f41e17ee7c022097f827bd74
- c646c8e6a632e23a9c2e60590f012c7b5cb40340194cb0a597161676961b4de0
Command and Control Servers
- safetyfactor[.]online
- cloudmiracle[.]store
- flandria171[.]appspot[.]com (FCM)
- newyan-1e09d[.]appspot[.]com (FCM)
Droppers distribution URL’s
- mcafee[.]960232[.]com
- mcafee[.]353934[.]com
- mcafee[.]908713[.]com
- mcafee[.]784503[.]com
- mcafee[.]053105[.]com
- mcafee[.]092877[.]com
- mcafee[.]582630[.]com
- mcafee[.]581574[.]com
- mcafee[.]582342[.]com
- mcafee[.]593942[.]com
- mcafee[.]930204[.]com
Steps to be taken when your device is compromised?.
- Change the password: Vultur revealed multiple cases where threat actors can gain access to your financial and private information. To safeguard your account, reset passwords on other devices and create secure, unique passwords during the time. Instead of simply storing your password, a reputed password manager is the most secure way of storing information.
- Keep an eye on your transactions and accounts: It is advised that you regularly monitor your online accounts for any unusual or illegal activity. Keep a watch out for any irregularities, and report anything suspicious to the provider or authorities straight immediately.. Also check your credit reports and scores attentively to make sure that your identity or cards are not compromised.
- Make sure you are using identity theft protection: Many pieces of information about your identity are stored in an Android device. Cyber criminals can easily get hold of this data and make major damage to you, including stealing your money and identity. For your own protection, some of the identity theft protection services that monitor all your personal information and notify you on any unusual activity and, as well, helps you to freeze your accounts would be beneficial.
- Immediately get in touch with your banks and credit card companies: Your personal information such as credit card or bank details is of high risk to be exposed to hackers who could use them to make transactions without you knowing. You should inform your credit card and the lending bank about the situation as soon as possible. They would help you if your cards were used for fraudulent charges and your card be either frozen or canceled. Besides, they can get new cards issued.
- Make your contacts alert regarding the fraud you faced: Threat actors may access your social media or email accounts to send phishing messages or spam to people in your contact list, if they gain access to them. Moreover, they may masquerade as you and try to extort cash from you or disclose your personal information. Distributing a message to your contacts stating that they shouldn’t open or reply to any messages that look like they are not from you and look very strange or suspicious, will be a great idea.
- Make a backup and wipe all your device content in factory settings: You can always factory reset your device to ensure it is free of viruses and spyware. In other words, it will refresh Android and leave behind all your data and settings. Back up all the critical data prior to processing it and assure that everything is restored from a trustworthy source only.
Preventive measures to be taken:
- Avoid calling back to the hacker: If a hacker texts you claiming to have approved a sizable bank transaction, refrain from picking up the phone. You can always check by making a call to your own financial intuition. However, never pick up on an unknown number that someone else sends you.
- Avoid sideloading apps and shortened URLs: Try to avoid sideloading apps. That's the moment when you install apps from unofficial sources. Users may be tricked into downloading malware using short URLs.
- Be careful granting permissions: Be cautious when allowing permissions for apps. Think about whether an app really needs access to specific data or device functions.
- Limit the apps you have on your phone: On your phone, having plenty of apps might sometimes make it easier to become infected with malware. Over time, these apps may allow harmful code to enter your system, and the more programs you have to update and monitor, the greater the risk to your Android device. This is how to remove pointless apps from your Android device.
- Download apps from reputable sources: Additionally, make sure the programs you download are from reputable and authorized developers. Do your homework and read reviews before you install.
- Keep your Android device updated: With the help of software and security upgrades, your phone can automatically maintain security. Remember to install them.
- Have good antivirus software on all your devices: The best defense against malware on all of your devices is to install antivirus software. By blocking you from clicking on potentially dangerous links, antivirus software can keep malware off your devices and keep hackers from accessing your personal data.
Conclusion:
Vultur is a terrifying banking Trojan with a great deal of sophistication. It's unsettling that hackers can take complete control of your Android device, which emphasizes how crucial it is that you take precautions. It all starts with a text message in these attacks. You must take the time to independently contact your banking institution to check whether there are any issues. You may prevent having your entire device compromised and your personal information exposed by simply investing an additional few minutes.
Reference:
- https://research.nccgroup.com/2024/03/28/android-malware-vultur-expands-its-wingspan/
- https://www.threatfabric.com/blogs/vultur-v-for-vnc\
- https://www.tomsguide.com/computing/malware-adware/this-nasty-android-banking-trojan-lets-hackers-completely-hijack-your-phone-how-to-stay-safe
- https://thehackernews.com/2024/04/vultur-android-banking-trojan-returns.html?m=1
- https://www.smallbiztechnology.com/archive/2024/04/vultur-trojan-heightens-android-app-security-risks.html/
- https://securityaffairs.com/161320/malware/vultur-banking-trojan-android.html
- https://www.malwarebytes.com/blog/detections/android-trojan-spy-vultur
- https://www.scmagazine.com/brief/updated-vultur-android-banking-trojan-emerges
- https://innovatecybersecurity.com/security-threat-advisory/windows-server-updates-blamed-for-domain-controller-crashes-kb5035855-and-kb5035857/
Introduction
In today's digital economy, data is not only a business asset but also the fuel for innovation, decision-making, and consumer trust. However, the digitisation of services has made personal or sensitive data a top target for cybercriminals. The stakes are high: a data breach can cost millions of fines, cause damage to reputation and devastate the confidence of consumers. Therefore, regulatory compliance and data protection have become a strategic imperative.
From the General Data Protection Regulation (GDPR) in the EU to the Digital Personal Data Protection (DPDP) Act of India, various sector-specific regulations like HIPAA for healthcare in the US, companies are now subject to a web of data protection and compliance laws. The challenge is to balance compliance efforts with strong security, a balance that demands both policy restraint and technical resilience. This blog examines pivotal pillars, shifting trends and actionable best practices for dominating data protection and compliance in 2025 and beyond.
Why Data Protection and Compliance Matter More Than Ever
Data protection isn't just about keeping fines at bay, it's about preserving the relationship with customers, partners and regulators. A 2024 IBM report says the average data-breach cost has now exceeded USD 4.5 million, with regulatory fines constituting a large portion of the cost. In addition to economics, breaches tend to result in intellectual property loss, customer loss and long-term brand attenuation. Compliance ensures organisations remain within certain legislative necessities for collecting, holding, transferring and setting of personal and sensitive information. Failure to conformity can lead to serious penalties: under GDPR, fines could be up to 4% of the company's annual turnover or €20 million, whichever is higher. In regulated sectors like banking and healthcare, compliance breaches can also lead to the suspension of licenses.
Important Regulatory Frameworks Informing 2025
- GDPR and Its Global Ripple Effect
GDPR was enacted in 2018 and continues to have a ripple effect on privacy legislation worldwide. Its tenets of lawfulness, transparency, data minimisation and purpose limitation have been replicated in many jurisdictions such as Brazil's LGPD and South Korea's PIPA.
- India's DPDP Act
The DPDP Act, 2023, gives high importance to consent-based processing of data, transparent notice rules and fiduciary responsibilities for data. With a penalty for default of up to INR 250 crore, it's amongst the most impactful laws for digital personal data protection.
- Sectoral Regulations
- HIPAA for healthcare information in the US.
- PCI DSS for payment card security.
- DORA (Digital Operational Resilience Act) in the EU for financial organisations.
- These industry-specific models generate overlapping compliance responsibilities, making cross-enterprise compliance programs vital.
Key Pillars of a Sound Data Protection & Compliance Program
- Data Governance and Classification
Having insight into what data you have to store, where it is stored and who can have access to it is the keystone of compliance. Organisations need to have data classification policies in place to group information based on sensitivity and impose more rigorous controls on sensitive data.
- Security Controls and Privacy by Design
Strong technical defences, encryption, multi-factor authentication, and intrusion detection are the initial defences. Privacy by design integrated in product development guarantees compliance is thought through from the initial stage, not added on afterwards.
- Consent and Transparency
Contemporary data legislation highlights informed consent. This entails simple, non-technical privacy notices, detailed opt-in choices, and straightforward withdrawal options. Transparency produces trust and lessens legal danger.
- Incident Response and Breach Notification
Most laws demand timely breach notifications, and GDPR insists on reporting within 72 hours. Having a documented incident response plan maintains legal deadlines and reduces harm.
- Employee Training and Awareness
Human mistake is the top source of data breaches. Ongoing training in prevention of phishing, password management, basic cyber hygiene and compliance requirements is crucial.
Upcoming Trends in 2025
- AI-Powered Compliance Monitoring
Organisations are embracing AI-powered solutions to systematically monitor data flows, identify policy breaches and auto-create compliance reports. The solutions assist in closing the loop between IT security teams and compliance officers.
- Cross-Border Data Transfer Mechanisms
With increasingly severe regulations, companies are spending more on secure cross-border data transfer frameworks like Standard Contractual Clauses (SCCs) and Binding Corporate Rules (BCRs).
- Privacy-Enhancing Technologies (PETs)
Methods such as homomorphic encryption and differential privacy are picking up steam, enabling organisations to sift through datasets without revealing sensitive personal data.
- ESG and Data Ethics
Data handling is increasingly becoming a part of Environmental, Social and Governance (ESG) reporting. Ethical utilisation of customer data, not just compliance, has become a reputational differentiator.
Challenges in Implementation
Despite having transparent frameworks, data protection plans encounter challenges like jurisdictions having competing needs, and global compliance is becoming expensive. The emerging technologies, such as generative AI, often bring privacy threats that haven’t been fully covered by legislation. Small and micro enterprises have neither the budget nor the skills to implement enterprise-level compliance programs. Qualifying these challenges often needs a risk-based strategy, allocations of resources to top areas of impact and automating the compliance chores wherever possible.
Best Practices for 2025 and Beyond
In 2025, regulatory compliance and data protection are no longer a precaution or a response to a breach but are strategic drivers of resilience and trust. As regulatory analysis rises, cyber threats evolve, and consumer expectations grow, administrations need to integrate compliance into the very fabric of their actions. By bringing governance and technology together, organisations can break free from a "checklist" mentality and instead adopt a proactive and risk-sensitive approach. Eventually, data protection is not just about not getting in trouble; it's about developing a kind that succeeds in the digital era.
References
- GDPR – Official EU Regulation Page: https://gdpr.eu
- India’s DPDP Act Overview – MeitY: https://www.meity.gov.in/data-protection-framework
- HIPAA – US Department of Health & Human Services: https://www.hhs.gov/hipaa
- PCI DSS Standards: https://www.pcisecuritystandards.org
- IBM Cost of a Data Breach Report 2024: https://www.ibm.com/reports/data-breach
- OECD – Privacy Guidelines: https://www.oecd.org/sti/privacy-guidelines
