
#FactCheck - Debunking the AI-Generated Image of an Alleged Israeli Army Dog Attack
Executive Summary:
A photo allegedly shows an Israeli Army dog attacking an elderly Palestinian woman has been circulating online on social media. However, the image is misleading as it was created using Artificial Intelligence (AI), as indicated by its graphical elements, watermark ("IN.VISUALART"), and basic anomalies. Although there are certain reports regarding the real incident in several news channels, the viral image was not taken during the actual event. This emphasizes the need to verify photos and information shared on social media carefully.

Claims:
A photo circulating in the media depicts an Israeli Army dog attacking an elderly Palestinian woman.


Fact Check:
Upon receiving the posts, we closely analyzed the image and found certain discrepancies that are commonly seen in AI-generated images. We can clearly see the watermark “IN.VISUALART” and also the hand of the old lady looks odd.

We then checked in AI-Image detection tools named, True Media and contentatscale AI detector. Both found potential AI Manipulation in the image.


Both tools found it to be AI Manipulated. We then keyword searched for relevant news regarding the viral photo. Though we found relevant news, we didn’t get any credible source for the image.

The photograph that was shared around the internet has no credible source. Hence the viral image is AI-generated and fake.
Conclusion:
The circulating photo of an Israeli Army dog attacking an elderly Palestinian woman is misleading. The incident did occur as per the several news channels, but the photo depicting the incident is AI-generated and not real.
- Claim: A photo being shared online shows an elderly Palestinian woman being attacked by an Israeli Army dog.
- Claimed on: X, Facebook, LinkedIn
- Fact Check: Fake & Misleading

Related Blogs

Executive Summary
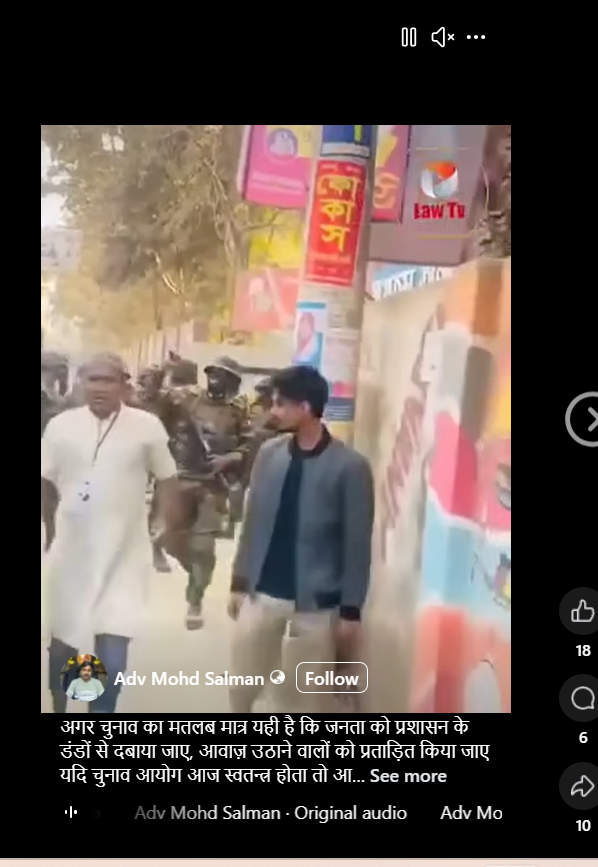
As West Bengal heads for vote counting on May 4, 2026, following the second phase of Assembly polling held on April 29, a video is being widely shared on social media. The clip shows security personnel baton-charging civilians, with users claiming it depicts force being used during the West Bengal Assembly Elections 2026. Research by CyberPeace Research Wing found that the viral claim is misleading. The video is actually from Bangladesh and is being falsely linked to the West Bengal elections to spread confusion.
Claim
A Facebook user named “Adv Mohd Salman” shared the clip on April 29, 2026, using Bengal-related hashtags and claiming that voters standing in line were beaten to influence the election outcome. The post alleged that free and fair voting rights were being suppressed.
Fact Check
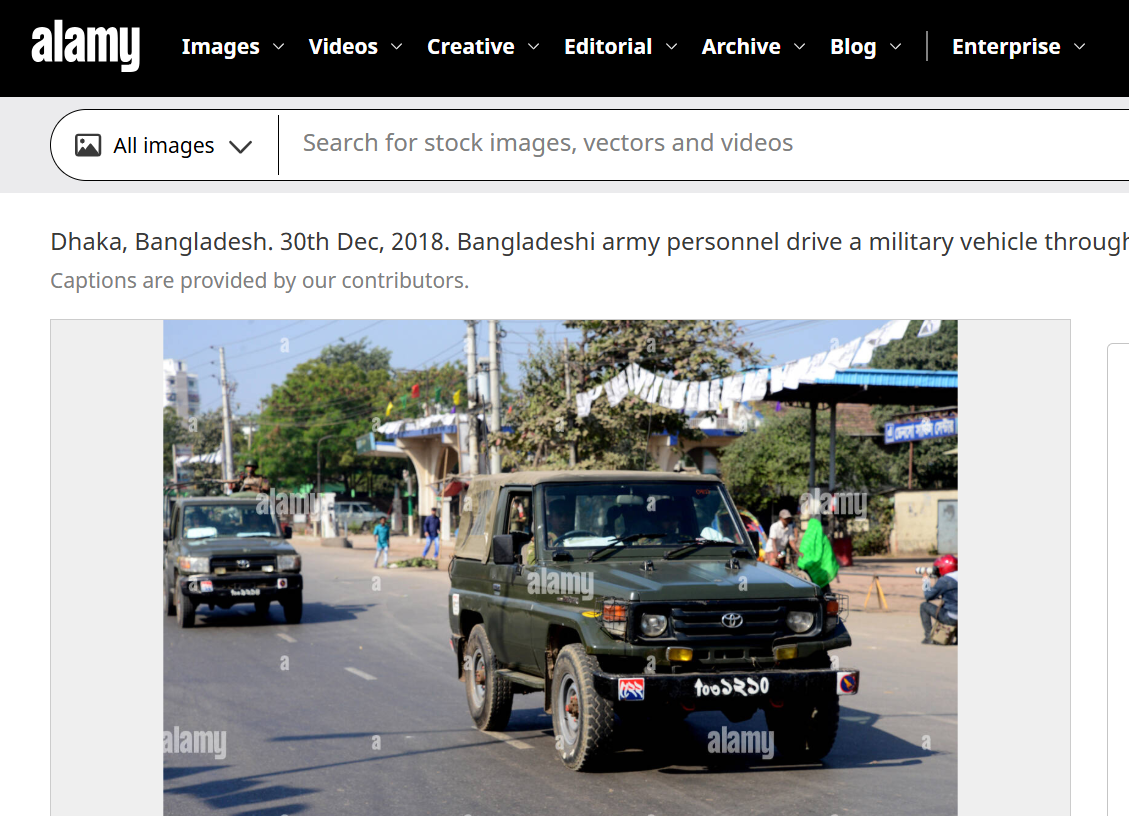
To verify the claim, we closely examined the viral video. A vehicle visible in the footage had a registration number written in a non-Hindi script. Using Google Lens reverse image search, we found a matching image uploaded on Alamy on December 30, 2018. The image showed a military vehicle with the same script and registration style seen in the viral clip.
According to the description on the platform, the image was taken in Dhaka during Bangladesh’s national elections and showed Bangladeshi army personnel moving through a street near a polling station. This confirms that the viral footage is not related to the 2026 West Bengal Assembly elections.
Conclusion
Our research confirms that the video showing security personnel baton-charging civilians is from Bangladesh, not West Bengal. It is being falsely shared as footage from the 2026 West Bengal Assembly elections to mislead users.
Executive Summary
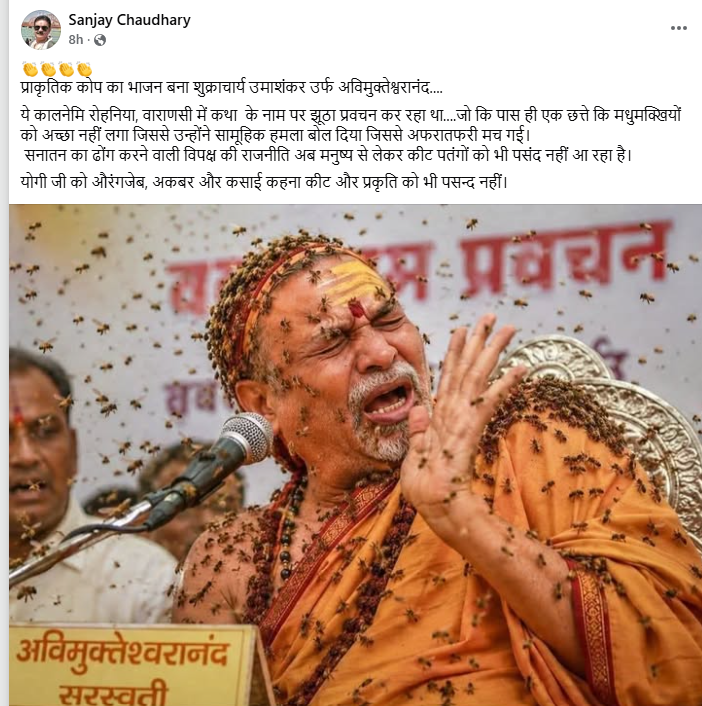
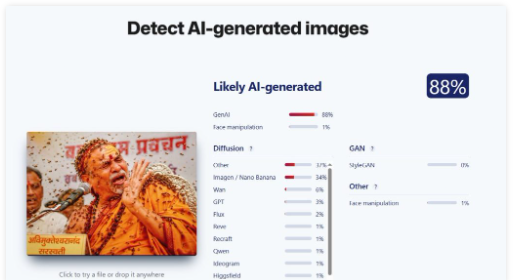
During the Gau Raksha Yatra of Shankaracharya Swami Avimukteshwaranand Saraswati, bees reportedly attacked a discourse event in Rohania area of Varanasi, Uttar Pradesh. Following the incident, a picture has gone viral on social media showing bees attacking Swami Avimukteshwaranand Saraswati. Several users are sharing the image as genuine while targeting the Shankaracharya online. CyberPeace Research Wing investigated the viral image and found it to be fake. Our research revealed that the picture was created using Artificial Intelligence (AI). While it is true that a bee attack occurred during Swami Avimukteshwaranand Saraswati’s discourse program, the viral image itself is fabricated.
Claim
A Facebook user named “Sanjay Chaudhary” shared the viral image on May 15, 2026, with the caption: “Prakritik kop ka bhajan bana Shukracharya Umashankar alias Avimukteshwaranand… This Kaalnemi was delivering false sermons in Rohania, Varanasi in the name of religion… The bees from a nearby hive did not like it and collectively attacked, creating chaos. Even insects and nature no longer like the opposition’s politics disguised as Sanatan Dharma. Calling Yogi Ji Aurangzeb, Akbar and butcher is not acceptable even to nature and insects.”
Post link and archive link are given below:
- https://www.facebook.com/sanjaychaudhary073/posts/pfbid02kgts8igKDwgctz3MamECMGoGfQR5aWPTdsDgLeux3pD9jwP7ADfgNpoPfHvMb9Zul
- https://perma.cc/E6SE-BAXZ
Fact-Check
To verify the viral claim, we used Google Open Search tools and found reports related to the incident on the YouTube channel of News18 UP Uttarakhand. A report published on May 13, 2026 stated that bees attacked the discourse event during Swami Avimukteshwaranand’s Gau Raksha Yatra in Rohania, Varanasi. The incident created panic at the venue, forcing the Swami to end his discourse midway. The channel also uploaded a YouTube Shorts video related to the incident.

As part of the research, we further analyzed the viral image using AI detection tools. First, we used the tool “Sight Engine,” which indicated an 88 percent probability that the image was AI-generated.
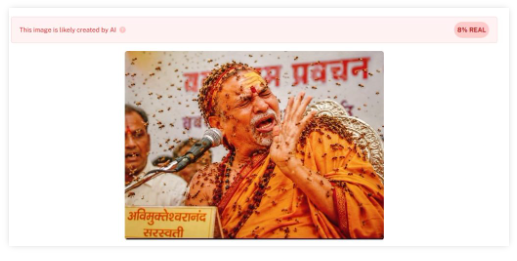
We then examined the image using another AI detection tool called “Undetectable,” which also suggested that the photo was likely created using AI.
Conclusion
Our research found that the viral image is AI-generated. The picture was created using artificial intelligence tools. While bees did attack during Swami Avimukteshwaranand Saraswati’s Gau Raksha Yatra on May 13, 2026, the viral image circulating on social media is fictional and not real.

Introduction
Since users are now constantly retrieving critical data on their mobile devices, fraudsters are now focusing on these devices. App-based, network-based, and device-based vulnerabilities are the three main ways of attacking that Mobile Endpoint Security names as mobile threats. Composed of the following features: program monitoring and risk, connection privacy and safety, psychological anomaly and reconfiguration recognition, and evaluation of vulnerabilities and management, this is how Gartner describes Mobile Threat Defense (MTD).
The widespread adoption and prevalence of cell phones among consumers worldwide have significantly increased in recent years. Users of these operating system-specific devices can install a wide range of software, or "apps," from online marketplaces like Google Play and the Apple App Store. The applications described above are the lifeblood of cell phones; they improve users' daily lives and augment the devices' performance. The app marketplaces let users quickly search for and install new programs, but certain malicious apps/links/websites can also be the origin of malware hidden among legitimate apps. These days, there are many different security issues and malevolent attacks that might affect mobile devices.
Unveiling Malware Landscape
The word "malware" refers to a comprehensive category of spyware intended to infiltrate networks, steal confidential data, cause disruptions, or grant illegal access. Malware can take many forms, such as Trojan horses, worms, ransomware, infections, spyware, and adware. Because each type has distinct goals and features, security specialists face a complex problem. Malware is a serious risk to both people and businesses. Security incidents, monetary losses, harm to one's credibility, and legal repercussions are possible outcomes. Understanding malware's inner workings is essential to defend against it effectively. Malware analysis is helpful in this situation. The practice of deconstructing and analysing dangerous software to comprehend its behaviour, operation, and consequences is known as malware analysis.Major threats targeting mobile phones
Viruses: Viruses are self-renewing programs that can steal data, launch denial of service assaults, or enact ransomware strikes. They spread by altering other software applications, adding malicious code, and running it on the target's device. Computer systems all over the world are still infected with viruses, which attack different operating systems like Mac and Microsoft Windows, even though there is a wealth of antiviral programs obtainable to mitigate their impacts.
Worms: Infections are independent apps that propagate quickly and carry out payloads—such as file deletion or the creation of botnets—to harm computers. Worms, in contrast to viruses, usually harm a computer system, even if it's just through bandwidth use. By taking advantage of holes in security or other vulnerabilities on the target computer, they spread throughout computer networks.
Ransomware: It causes serious commercial and organisational harm to people and businesses by encrypting data and demanding payment to unlock it. The daily operations of the victim organisation are somewhat disrupted, and they need to pay a ransom to get them back. It is not certain, though, that the financial transaction will be successful or that they will receive a working translation key.
Adware: It can be controlled via notification restrictions or ad-blockers, tracks user activities and delivers unsolicited advertisements. Adware poses concerns to users' privacy even though it's not always malevolent since the information it collects is frequently combined with information gathered from other places and used to build user profiles without their permission or knowledge.
Spyware: It can proliferate via malicious software or authentic software downloads, taking advantage of confidential data. This kind of spyware gathers data on users' actions without their authorisation or agreement, including:Internet activityBanking login credentialsPasswordsPersonally Identifiable Information (PII)
Navigating the Mobile Security Landscape
App-Centric Development: Regarding mobile security, app-centric protections are a crucial area of focus. Application authorisations should be regularly reviewed and adjusted to guarantee that applications only access the knowledge that is essential and to lower the probability of data misuse. Users can limit hazards and have greater oversight over their confidentiality by closely monitoring these settings. Installing trustworthy mobile security apps also adds another line of protection. With capabilities like app analysis, real-time protection, and antivirus scanning, these speciality apps strengthen your gadget's protection against malware and other harmful activity.
Network Security: Setting priorities for secure communication procedures is crucial for safeguarding confidential data and thwarting conceivable dangers in mobile security. Avoiding unprotected public Wi-Fi networks is essential since they may be vulnerable to cyberattacks. To lessen the chance of unwelcome entry and data surveillance, promote the usage of reliable, password-protected networks instead. Furthermore, by encrypting data transfer, Virtual Private Networks (VPNs) provide additional protection and make it more difficult for malevolent actors to corrupt information. To further improve security, avoid using public Wi-Fi for essential transactions and hold off until a secure network is available. Users can strengthen their handheld gadgets against possible privacy breaches by implementing these practices, which can dramatically lower the risk of data eavesdropping and illegal access.
Constant development: Maintaining a robust mobile security approach requires a dedication to constant development. Adopt a proactive stance by continuously improving and modifying your security protocols. By following up on recurring outreach and awareness campaigns, you can stay updated about new hazards. Because cybersecurity is a dynamic field, maintaining one step ahead and utilising emerging technologies is essential. Stay updated with security changes, implement the newest safeguards, and incorporate new industry standard procedures into your plan. This dedication to ongoing development creates a flexible barrier, strengthening your resistance to constantly evolving mobile security threats.
Threat emergency preparedness: To start, familiarise yourself with the ever-changing terrain associated with mobile dangers to security. Keep updated on new threats including malware, phishing, and illegal access.
Sturdy Device Management: Put in place a thorough approach to device management. This includes frequent upgrades, safe locking systems, and additional safeguarding capabilities like remote surveillance and erasing.
Customer Alertness: Emphasise proper online conduct and acquaint yourself and your team with potential hazards, such as phishing efforts.
Dynamic Measures for a Robust Wireless Safety Plan
In the dynamic field of mobile assurances, taking a proactive strategy is critical. To strengthen safeguards, thoroughly research common risks like malware, phishing, and illegal access. Establish a strong device management strategy that includes frequent upgrades, safe locking mechanisms, and remote monitoring and deletion capabilities for added security.
Promoting user awareness by educating people so they can identify and block any hazards, especially regarding phishing attempts. Reduce the dangers of data eavesdropping and illegal access by emphasising safe communication practices, using Virtual Private Networks (VPNs), and avoiding public Wi-Fi for essential transactions.
Pay close attention to app-centric integrity by periodically checking and modifying entitlements. Downloading trustworthy mobile security apps skilled at thwarting malware and other unwanted activity will enhance your smartphone's defenses. Lastly, create an atmosphere of continuous development by keeping up with new threats and utilising developing technology to make your handheld security plan more resilient overall.
Conclusion
Mobile privacy threats grow as portable electronics become increasingly integrated into daily activities. Effective defense requires knowledge of the various types of malware, such as worms, ransomware, adware, and spyware. Tools for Mobile Threat Defense, which prioritise vulnerability assessment, management, anomaly detection, connection privacy, and program monitoring, are essential. App-centric development, secure networking procedures, ongoing enhancement, threat readiness, strong device control, and user comprehension are all components of a complete mobile security strategy. People, as well as organisations, can strengthen their defenses against changing mobile security threats by implementing dynamic measures and maintaining vigilance, thereby guaranteeing safe and resilient mobile surrounding.
References
https://www.titanfile.com/blog/types-of-computer-malware/
https://www.simplilearn.com/what-is-a-trojan-malware-article
https://www.linkedin.com/pulse/latest-anti-analysis-tactics-guloader-malware-revealed-ukhxc/?trk=article-ssr-frontend-pulse_more-articles_related-content-card

