
#Factcheck-Viral Image of Men Riding an Elephant Next to a Tiger in Bihar is Misleading
Executive Summary:
A post on X (formerly Twitter) featuring an image that has been widely shared with misleading captions, claiming to show men riding an elephant next to a tiger in Bihar, India. This post has sparked both fascination and skepticism on social media. However, our investigation has revealed that the image is misleading. It is not a recent photograph; rather, it is a photo of an incident from 2011. Always verify claims before sharing.

Claims:
An image purporting to depict men riding an elephant next to a tiger in Bihar has gone viral, implying that this astonishing event truly took place.

Fact Check:
After investigation of the viral image using Reverse Image Search shows that it comes from an older video. The footage shows a tiger that was shot after it became a man-eater by forest guard. The tiger killed six people and caused panic in local villages in the Ramnagar division of Uttarakhand in January, 2011.

Before sharing viral posts, take a brief moment to verify the facts. Misinformation spreads quickly and it’s far better to rely on trusted fact-checking sources.
Conclusion:
The claim that men rode an elephant alongside a tiger in Bihar is false. The photo presented as recent actually originates from the past and does not depict a current event. Social media users should exercise caution and verify sensational claims before sharing them.
- Claim: The video shows people casually interacting with a tiger in Bihar
- Claimed On:Instagram and X (Formerly Known As Twitter)
- Fact Check: False and Misleading

Related Blogs
Executive Summary
A video is being widely shared on social media, purportedly showing a person drawing water from a drain and using it to cook biryani. The video is being shared as being from India. Some users sharing the video are also advising people to take care of their stomach and intestinal health while eating and drinking outside. A research done by the Research Wing of the CyberPeace found that the viral video is not authentic but AI-generated and is being shared with a misleading claim.
Claim:
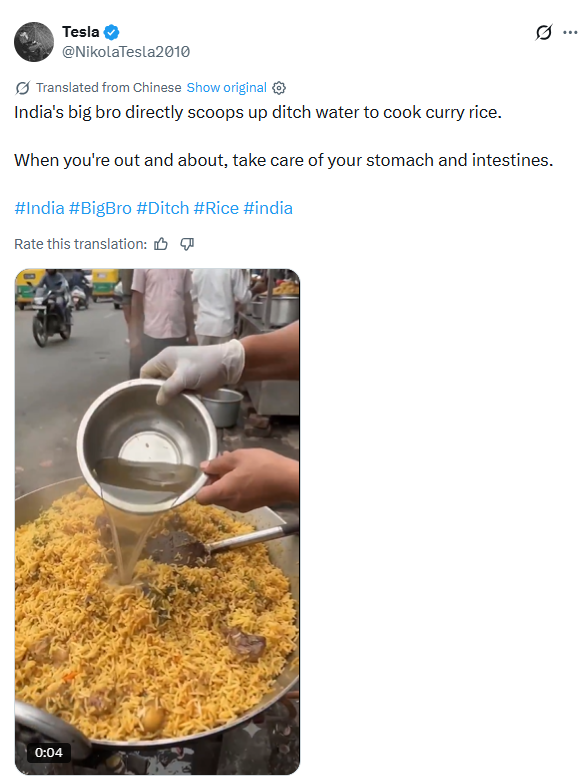
A user on the social media platform Facebook shared the viral video with the caption: “A person in India is cooking biryani using water from a drain.” The post link, archive link and screenshot are provided below.
https://x.com/NikolaTesla2010/status/2094021398113226802?s=20
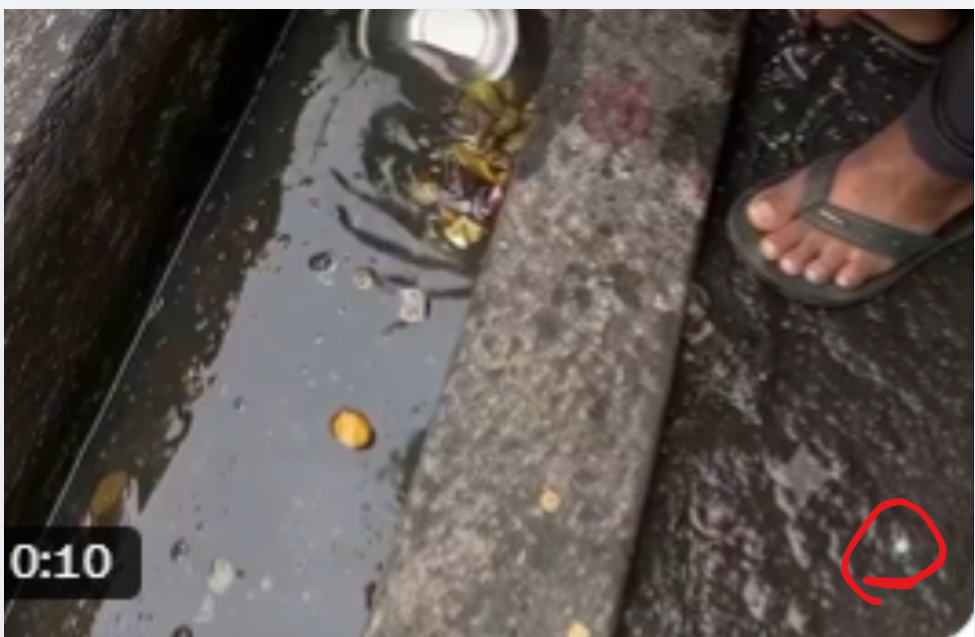
Fact Check:
Upon closely examining the viral video, we noticed the Google Gemini logo clearly visible in the bottom-right corner. This raised suspicions that the video could be AI-generated.
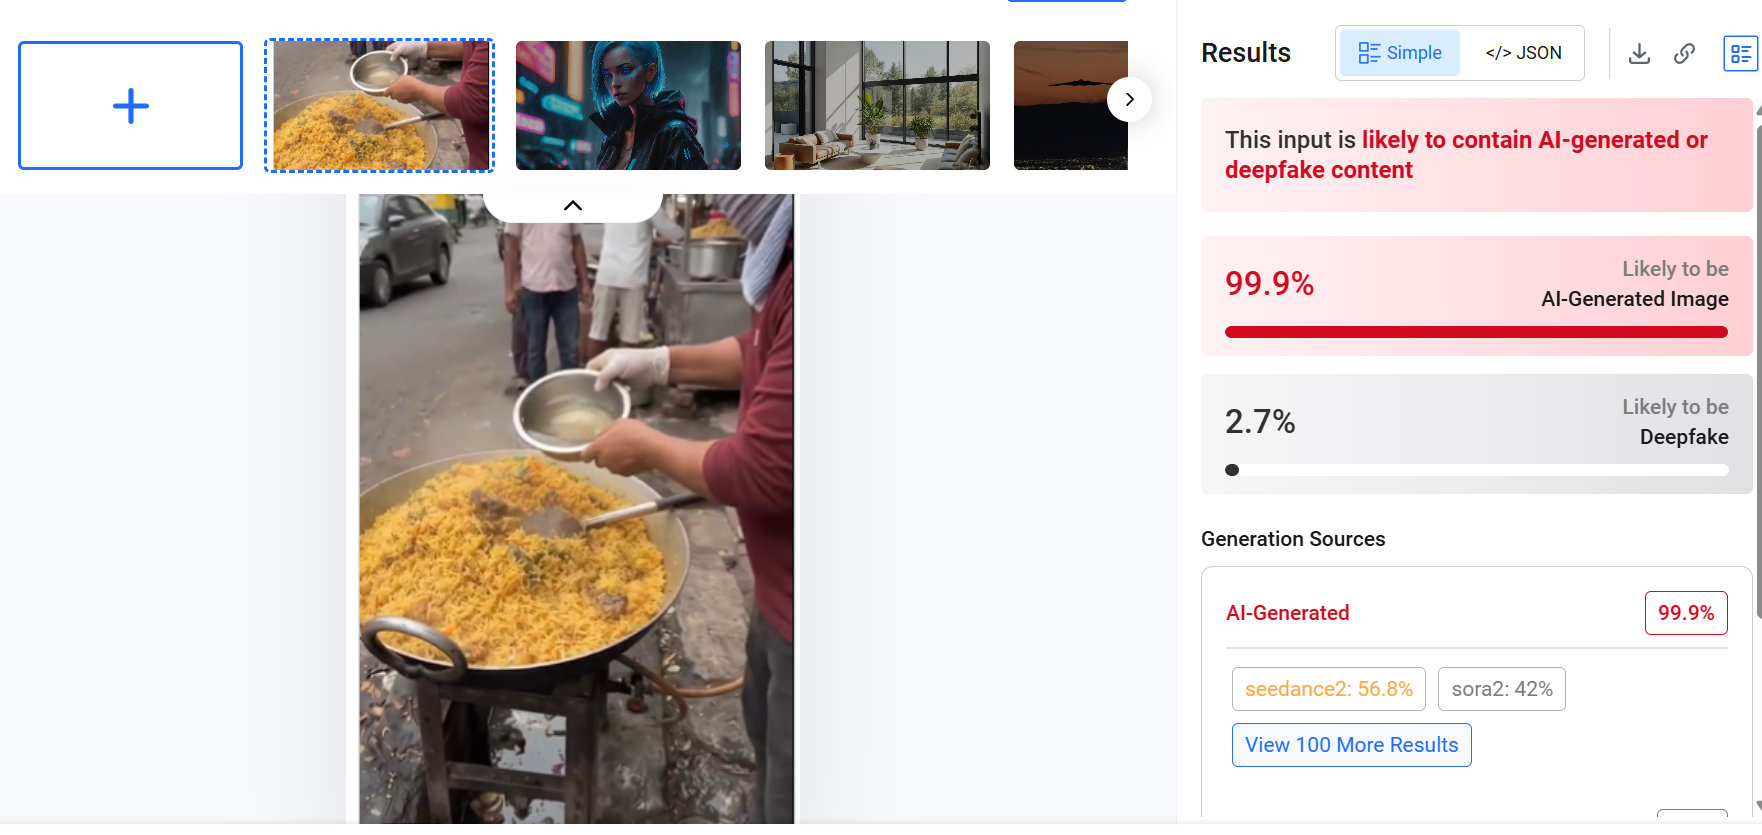
As part of our research, we ran the video through the AI detection tool Hive Moderation. According to the results, the viral video is 99 percent likely to be AI-generated.
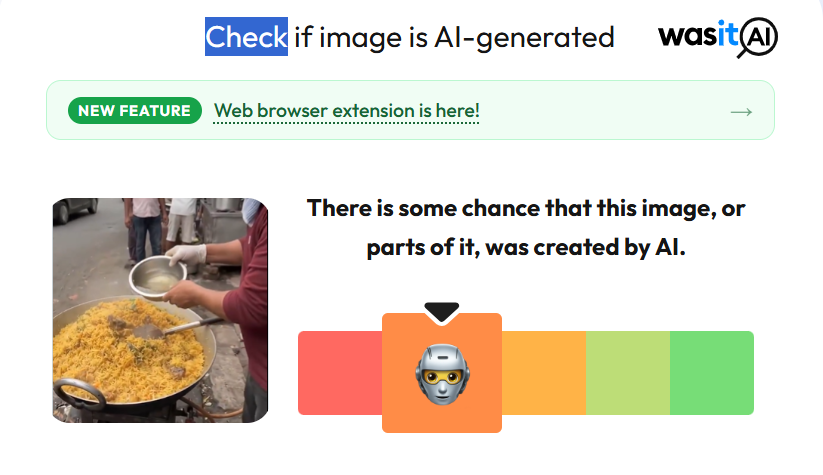
As part of our research, we scanned the video using WasIt AI. According to the results, the viral video is AI-generated.
Conclusion
The evidence gathered during our research establishes that the viral video claiming to show a person cooking biryani using water from a drain in India is misleading. The Google Gemini logo is clearly visible in the video, while AI detection tools Hive Moderation and WasIt AI also identified the footage as AI-generated. Therefore, the video does not depict a genuine incident.
Introduction
Over the last few years, several public data breaches in Venezuela have revealed a lack of cohesion and progress in its data privacy system and left many people susceptible to fraud, identity theft and long-term harm via the internet. It is clear from these data breaches that when organizations fail to adequately protect their data, both through cybersecurity failures and weak legal protections, they can lead to problems throughout an entire system through which all individuals in the system could potentially suffer.
Among the more notable breaches are the Movistar Venezuela data breach from 2025 and the Cashea App data leak from earlier this year. Each of these examples demonstrates to some extent how the absence of an adequate privacy regulatory scheme can worsen the results of a data breach.
The Movistar Breach: A Regulatory Warning (2025)
Venezuelan digital rights group VE Sin Filtro published a report late in April 2025, which found a database revealed to have been opened onto the internet containing personal information belonging to over 3.2 million Movistar customers. The initial breach contained personal, and confidential, data of Venezuelan citizens such as national identification numbers, full names, city of residence, and phone numbers which could have been exploited to commit identity theft, SIM-swap fraud, and targeted scams.
One significant issue with this situation was that Movistar failed to disclose the breach publicly or contact impacted customers at the time of the disclosure. As a result, there appears to be a significant gap in Sanctions / Other Means of Enforcing Security Countermeasures Laws. Since there are numerous countries that enforce GDPR-style regulations and as such, this matter should lead to a complete investigation and possible fines against those responsible but in Venezuela there is still a lack of accountability.
Cashea App Leak: A 2026 Data Shock
A second alleged data breach came to light in February of 2026. It involved a Venezuelan buy-now-pay-later (BNPL) fintech called Cashea App, which is typically heavily utilized domestically. Reports have circulated that threat actors have been offering a database, believed to hold more than 79 million transaction records. This is more than double the size and sensitivity of the data involved in the Movistar Breach.
According to reports, the leaked data included:
- Bank account details and payment methods
- Merchant profiles and internal business identifiers
- Detailed transaction histories with names, national ID numbers, timestamps, and installment data
This level of exposure goes far beyond basic identifiers. Financial transaction histories combined with personal identifiers enable sophisticated fraud, targeted social engineering, and long-term misuse of financial identities. As with the Movistar breach, no official acknowledgment or notification was issued by Cashea at the time of reporting, again underscoring Venezuela’s weak enforcement environment.
Why These Breaches Matter: The Legal Dimension
The incidents show us that there is a bigger problem with the way Venezuela has set up its framework for protecting data. For instance, the Venezuelan Constitution recognises the principles of data protection and privacy; however, these rights only exist in a theoretical manner; they lack implementing legislation, procedural clarity, and institutional enforcement.
Constitutional Basis of Data Protection
The Supreme Tribunal of Justice (TSJ) stated the core principles for protecting data are found in the Venezuelan Constitution. After the TSJ issued its 2011 ruling, Article 28 of the Venezuelan Constitution gives individuals the right to know what data the state has about them, how the state uses that data, and to correct or delete any harmful data. Article 60 of the Venezuelan Constitution protects individuals' privacy and restricts excessive data collection by the state.
The Constitutional Chamber also put into place additional guiding principles for how to protect personal data, including:
- The data subject must give prior informed and revocable consent.
- The purpose for which the data is collected must be specified and only the minimum amount of information necessary can be collected.
- The data collected must be accurate and of good quality.
- There are confidentiality obligations for third parties regarding the use of the data.
- It is the government's responsibility to put into place procedures and mechanisms to monitor compliance with the data protection laws.
- There are civil, criminal and administrative liabilities for individuals and legal entities that violate the data protection laws.
But, in a civil law country, when courts make rulings, they usually are persuasive only as opposed to being legally binding, and even constitutional rulings cannot be implemented until enabling legislation is passed.
Absence of a Comprehensive Data Protection Law
In contrast to the European Union's GDPR (General Data Protection Regulation), the United States' sectoral approach, and emerging Latin American data protection systems such as the ones in Brazil, Chile and Colombia, Venezuela has no independent data protection law. This lack of law leads to numerous types of uncertainty in the realm of data protection laws:
- No defined data controller or processor obligations
- No standardized lawful bases for processing
- No clear breach notification timelines
- No independent data protection authority
- No procedural pathway for individuals to seek redress
As a result, data protection in Venezuela is not treated as an independent legal discipline but instead becomes derivative, arising incidentally within constitutional litigation or sector-specific disputes.
Regulatory Fragmentation and Institutional Weakness
Due to the TSJ decisions made in 2011, there has been a lack of regulatory action taken in a systematic fashion and instead most actions have been done on a case by case basis as valid incidents arise. The National Cybersecurity Council was established in 2024; however, its function is to support the establishment of cybersecurity infrastructure and has no defined powers regarding the enforcement of privacy.
This creates a fragmented institutional landscape where:
- Authorities lack clear jurisdiction over privacy violations
- Companies face minimal compliance guidance
- Individuals struggle to understand or enforce their rights
The Movistar and Cashea incidents highlight how this fragmentation translates into practical impunity following major data exposures.
What’s Next? A Legal Opportunity for Reform
The repercussions of insufficient safeguards for data protection extend past the damage incurred to a person's privacy:
- Loss of trust in both financial and digital services
- Heightened likelihood of financial fraud and crime
- Lack of willingness from foreign companies to conduct business with Venezuela’s platforms.
- Long-term negative impact on the reputation of domestic companies.
- Possible inability to access cross-border transfer of data due to other jurisdictions’ decisions to restrict transfers into jurisdictions without cutting-edge enforcement of protections for privacy.
In a digital economy that increasingly requires robust data protection to function successfully, a lack of action to create strong protections will cause a significant economic impact.
Conclusion
Major data breaches such as the ones at Movistar in 2025 and Cashea App in 2026 show that constitutional privacy rights alone are insufficient without enforceable legal framework. Privacy laws must move from being just a principle to being a law that has institutions, procedures, and accountability to make sure the privacy of the users is protected.
Now with the global digital economy being so interconnected, not having regulations creates openings for vulnerabilities for people. If Venezuela hopes to protect their citizens, create an innovation-friendly environment, and compete in the global market, they must implement comprehensive data privacy reforms as soon as possible.
REFERENCES
- https://iapp.org/news/a/venezuela-data-breach-highlights-scattered-privacy-regulation
- https://www.apolocybersecurity.com/en/blog-posts/ciberataque-a-movistar-que-ha-pasado-a-quien-afecta-y-como-proteger-tus-datos
- https://darknetsearch.com/knowledge/news/en/cashea-app-data-leak-79m-records-exposed-in-venezuela/
- https://www.binance.com/en-IN/square/post/294369884695410
Introduction
Not every major breach begins with a sophisticated new exploit. Sometimes it begins with a device nobody remembered to update, and this one began exactly that way, at scale. Security researchers have disclosed a campaign that compromised more than 14,530 internet connected cameras made by Dahua Technology, (one of the world's largest surveillance equipment manufacturers), using a mix of stolen credentials, two long known authentication flaws, and a peer to peer relay technique that let attackers reach devices tucked behind home and office routers. The operation, tracked by researchers at Hunt.io, has been named Operation CameraSwarm. It ran between June 17 and July 22, 2026, and was reconstructed almost entirely from an exposed 407 megabyte working directory the attackers themselves left accessible, containing over 2,600 files, campaign logs, shell history, and tooling. Confirmed compromises were concentrated in Ukraine and Russia, and researchers described the operators/attackers as Russian speaking based on language artifacts found in the recovered material, suggesting the campaign was most plausibly built around surveillance or access relevant to the ongoing conflict between the two countries, though no formal attribution to a named threat actor or state entity has been established or claimed. What makes this worth understanding in detail is not just the scale, though 14,500 compromised cameras is a serious number, but how mundane the actual break in methods were. None of this depended on the attackers discovering some brand new, unknown flaw, the kind of vulnerability security researchers call a ‘zero day’. It depended on something far more ordinary: thousands of devices running years-old software that had never been patched, combined with cheap automated tools that could try weak passwords and known exploits at scale.
What is Dahua, and why does this matter
Dahua Technology, founded in Hangzhou in 2001, is a publicly traded, partially state owned Chinese company and the world's second largest video surveillance manufacturer by revenue, trailing only fellow Chinese firm Hikvision. Its cameras, digital video recorders, and network video recorders are sold in roughly 180 countries through more than 2,100 partners, and the company has shipped tens of millions of devices into homes, retail stores, offices, and public infrastructure worldwide. That scale is precisely what makes any systemic vulnerability in Dahua's product line consequential well beyond a single country or sector.
How the attackers actually got in
Hunt.io attributed the compromises to three distinct attack paths. The largest, by far, was straightforward credential attacks, essentially automated login guessing using weak, default, or previously leaked passwords, which researchers traced to 12,324 unique IP addresses across more than 13,000 recorded campaign attempts. The second path exploited two authentication bypass flaws, catalogued as CVE-2021-33044 and CVE-2021-33045, both rated a severe 9.8 out of 10 on the current CVSS severity scale used by the US National Vulnerability Database. These are not new vulnerabilities. They were publicly disclosed back in 2021, and Dahua issued fixed firmware for them years ago, yet both remain listed today on the US Cybersecurity and Infrastructure Security Agency's Known Exploited Vulnerabilities catalog, a designation reserved specifically for flaws still being actively exploited in the wild despite available patches. The third and most technically interesting path involved a peer to peer, or P2P, relay mechanism built into Dahua's own Easy4IP cloud infrastructure, a system designed to let users remotely access their camera without manually configuring network settings. Security firm ITRES Labs, which documented this exposure separately in 2025, found that on firmware released before mid-2024, simply knowing a device's serial number was enough to establish a connection route through Dahua's relay servers before the camera's own login check ever kicked in, a design gap that let attackers reach devices even when they sat behind network address translation, the technical barrier that normally shields home devices from direct internet exposure. Hunt.io's recovered operator logs claimed an extraordinary 89.4 percent of live serial numbers tested returned an open channel without any authentication at all, though it is worth noting that figure comes solely from the attackers' own recovered data and has not been independently verified by Dahua, ITRES Labs, or any public incident response body as of this writing. Beyond the initial break in, the campaign also planted 1,923 cameras with a persistent account, essentially a backdoor login the operators could return to later, and researchers found evidence suggesting parts of the toolkit may have been built specifically to hand off access to a third party, though no confirmed link to a named threat actor or state sponsor has been established.
Why cameras remain such a persistent target
Internet connected cameras occupy an unusual position in the broader device ecosystem. Unlike a laptop or phone, they are rarely patched by an end user paying regular attention, they are often installed once and forgotten, and many owners never change the default credentials shipped from the factory. A compromised camera also offers an attacker something more than a foothold, live or recorded video feeds of homes, businesses, and sometimes sensitive facilities, which carries value well beyond the kind of access a compromised laptop typically provides.
CyberPeace Advisory | What device owners should do now
For anyone running Dahua surveillance equipment, or any internet connected camera system, several concrete steps meaningfully reduce exposure.
For Dahua device owners specifically:
Two steps address the exact mechanisms this campaign exploited.
- First, check the device's firmware version against Dahua's official download portal and apply the latest available update immediately, since the fixes for both 2021 authentication bypass vulnerabilities have existed for years and simply have not been applied on thousands of devices.
- Second, disable the P2P or Easy4IP remote access feature entirely unless it is actively required, since this is the exact mechanism the third attack path, the serial number based relay, relied on to reach cameras without any login check at all.
For any internet connected camera system, including in India:
The remaining precautions apply regardless of manufacturer, and are worth following on any brand of camera, DVR, or NVR connected to the internet.
- Replace default or weak passwords with strong, unique credentials on every camera and recorder, and remove any unused or unrecognised accounts, since the persistent account technique this campaign used depends entirely on unnoticed access surviving unchecked.
- Place surveillance devices on a segmented network separate from computers and phones, so that a compromised camera cannot become a stepping stone into more sensitive systems.
- Periodically audit which devices on a home or office network are internet facing at all, since many cameras end up exposed simply because remote access was left switched on by default and nobody thought to check.
- And where a device offers the option, disable any built in peer to peer or cloud relay convenience feature unless genuinely needed, since the underlying design pattern this campaign exploited, a remote access shortcut that runs before proper authentication.Is not unique to Dahua and has shown up across other camera brands in the past.
The view from India
This disclosure lands at a particularly relevant moment for India, which enforced sweeping new restrictions on Chinese origin CCTV equipment earlier this year. Since April 1, 2026, internet connected surveillance cameras sold in India have been required to carry Standardisation Testing and Quality Certification under Essential Requirements norms first introduced by the Ministry of Electronics and Information Technology in April 2024, It's a country-of-origin requirement under the Essential Requirements norms (introduced by India's Ministry of Electronics and Information Technology in April 2024), manufacturers must disclose the origin of key components like the System-on-Chip (SoC), and devices using Chinese-origin chipsets are reportedly not being granted approval by certifying authorities. Since Dahua's cameras, like Hikvision's and TP-Link's, generally rely on Chinese-made chipsets, the practical effect is that their products haven't received STQC certification, which functions as a blanket exclusion without the government needing to name any single company in the rule text itself. The stated rationale for that policy, concerns over hidden backdoor access, transmission of data to foreign servers, and deployment near sensitive locations, reads almost like a preview of exactly the kind of exposure Operation CameraSwarm has now documented in the wild. It is worth being precise here: the restriction applies to new sales, not existing installations, and CameraSwarm's confirmed victims were concentrated in Ukraine and Russia rather than India. But the underlying lesson travels well beyond any one country's borders. A camera manufactured with a convenience feature that bypasses its own login check, sitting unpatched for years despite a fix being publicly available, is a vulnerability that does not respect national boundaries, and India's decision to tighten certification requirements before an incident of this scale surfaced looks, in hindsight, considerably more prudent than reactive.
References
- The Hacker News, "Hackers Compromised 14,500+ Dahua Devices Using Credential Attacks, Auth Bypasses, and P2P." August 19, 2026. https://thehackernews.com/2026/08/hackers-compromised-14500-dahua-devices.html
- Hunt.io, "Operation CameraSwarm: Dahua Cameras Compromised." https://hunt.io/blog/operation-cameraswarm-dahua-cameras-compromised
- ITRES Labs, "Dahua Beyond CVE-2025-31702: P2P Relay Exposure." October 29, 2025. https://labs.itresit.es/2025/10/29/dahua-beyond-cve-2025-31702-p2p-relay-exposure?
- Dahua Security, "DHCC-SA-202106-001: Security Advisory - Identity Authentication Bypass Vulnerability Found in Some Dahua Products." https://www.dahuasecurity.com/about-dahua/trust-center/dahua-psirt/dhcc-sa-202106-001%3Asecurity-advisory---identity-authentication-bypass-vulnerability-found-in-some-dahua-products
- National Vulnerability Database, "CVE-2021-33044 Detail." https://nvd.nist.gov/vuln/detail/CVE-2021-33044
- CISA, "Known Exploited Vulnerabilities Catalog." https://www.cisa.gov/known-exploited-vulnerabilities-catalog
- Business Standard, "India to ban Chinese CCTV from Apr 1 as security concerns reshape market." https://www.business-standard.com/industry/news/india-ban-chinese-cctv-government-security-concerns-hikvision-dahua-market-126033000316_1.html
- PTC News, "India CCTV ban 2026: Hikvision, Dahua face STQC block as new security rules begin." https://www.ptcnews.tv/amp/nation/india-cctv-ban-hikvision-dahua-stqc-rules-2026-4422961
- Uyghur Human Rights Project, "Surveillance Tech Series: Dahua's Links to Human Rights Abuses in East Turkistan." https://uhrp.org/report/dahuas-links-to-human-rights-abuses-in-east-turkistan/
