
#FactCheck-Viral Fire Video Falsely Linked to Hezbollah Strike on Israeli Military HQ
Executive Summary
Despite a truce announced in mid-April, sporadic violence has continued between Israel and the Iran-backed Hezbollah in Lebanon. Meanwhile, a video circulating widely on social media shows a multi-storey building engulfed in flames, with users falsely linking it to the ongoing conflict. Posts sharing the clip claim it depicts a Hezbollah strike on an Israeli military headquarters, alleging that several soldiers were killed and that Israel is censoring visuals from the incident. However, research by the CyberPeace Research Wing found the claim to be misleading. The video is unrelated to the Israel-Hezbollah conflict. Verification shows that the footage actually captures a fire at an apartment building in New York City. Firefighters can be seen at the scene attempting to control the blaze.
Claim
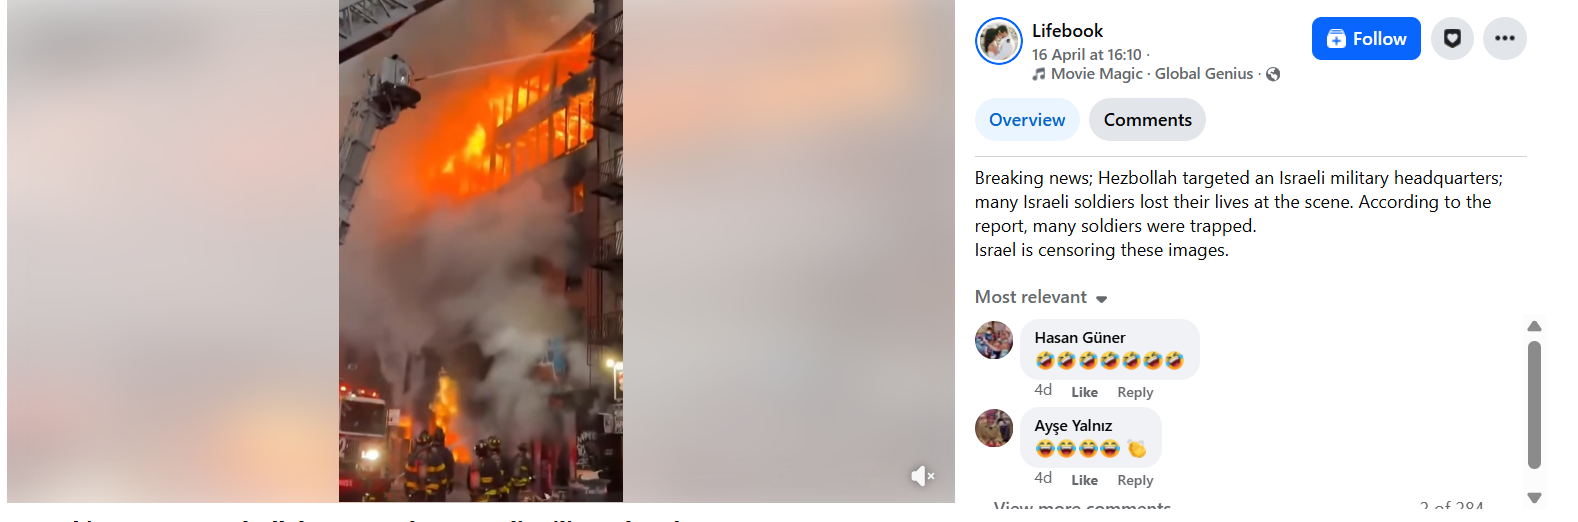
A Facebook post shared on April 16, 2026, read: “Breaking news; Hezbollah targeted an Israeli military headquarters; many Israeli soldiers lost their lives at the scene… Israel is censoring these images.” The video has garnered more than 240,000 views.
- https://perma.cc/BQ6X-4LAT
- https://www.facebook.com/watch/?v=1283830349750737
Fact Check
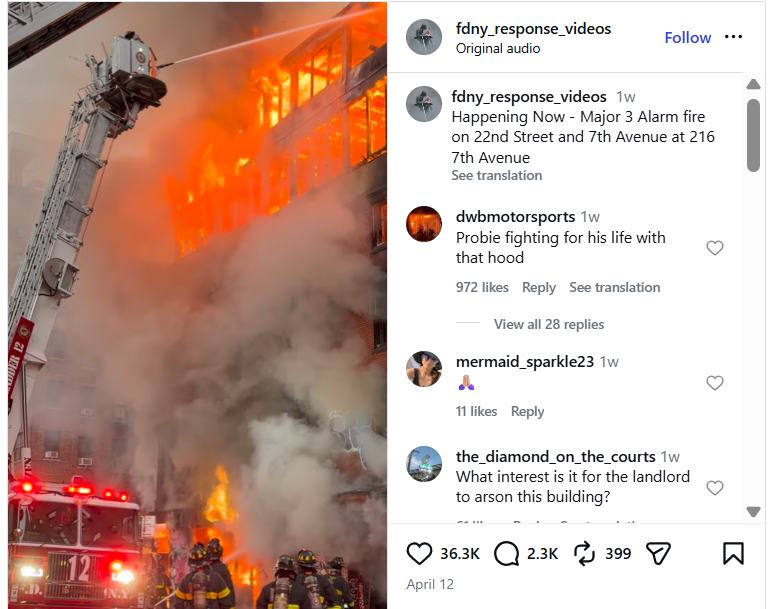
A reverse image search using keyframes from the viral clip led to a higher-quality version posted on April 12, 2026, by an Instagram account titled “FDNY response video.” The caption stated: “Happening now — Major 3 alarm fire on 22nd Street and 7th Avenue at 216 7th Avenue.”
- https://www.instagram.com/p/DXB0ePqjgGD/
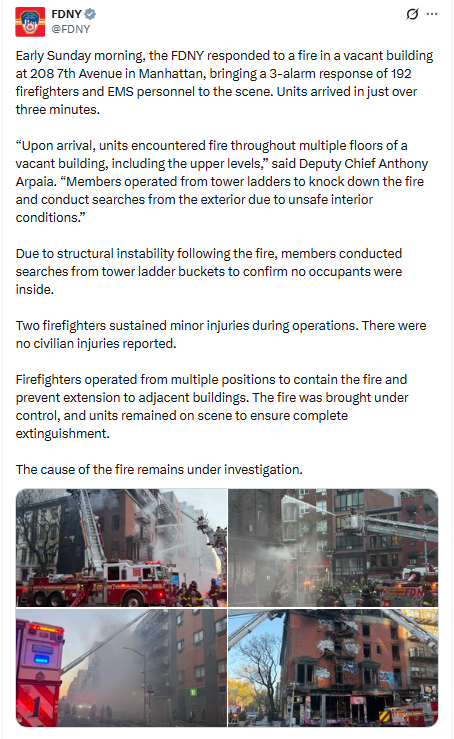
Further verification found that images of the same incident were shared on April 13, 2026, by the official X account of the New York City Fire Department. According to the post, no civilians were injured in the fire, although two firefighters sustained minor injuries while battling the blaze.
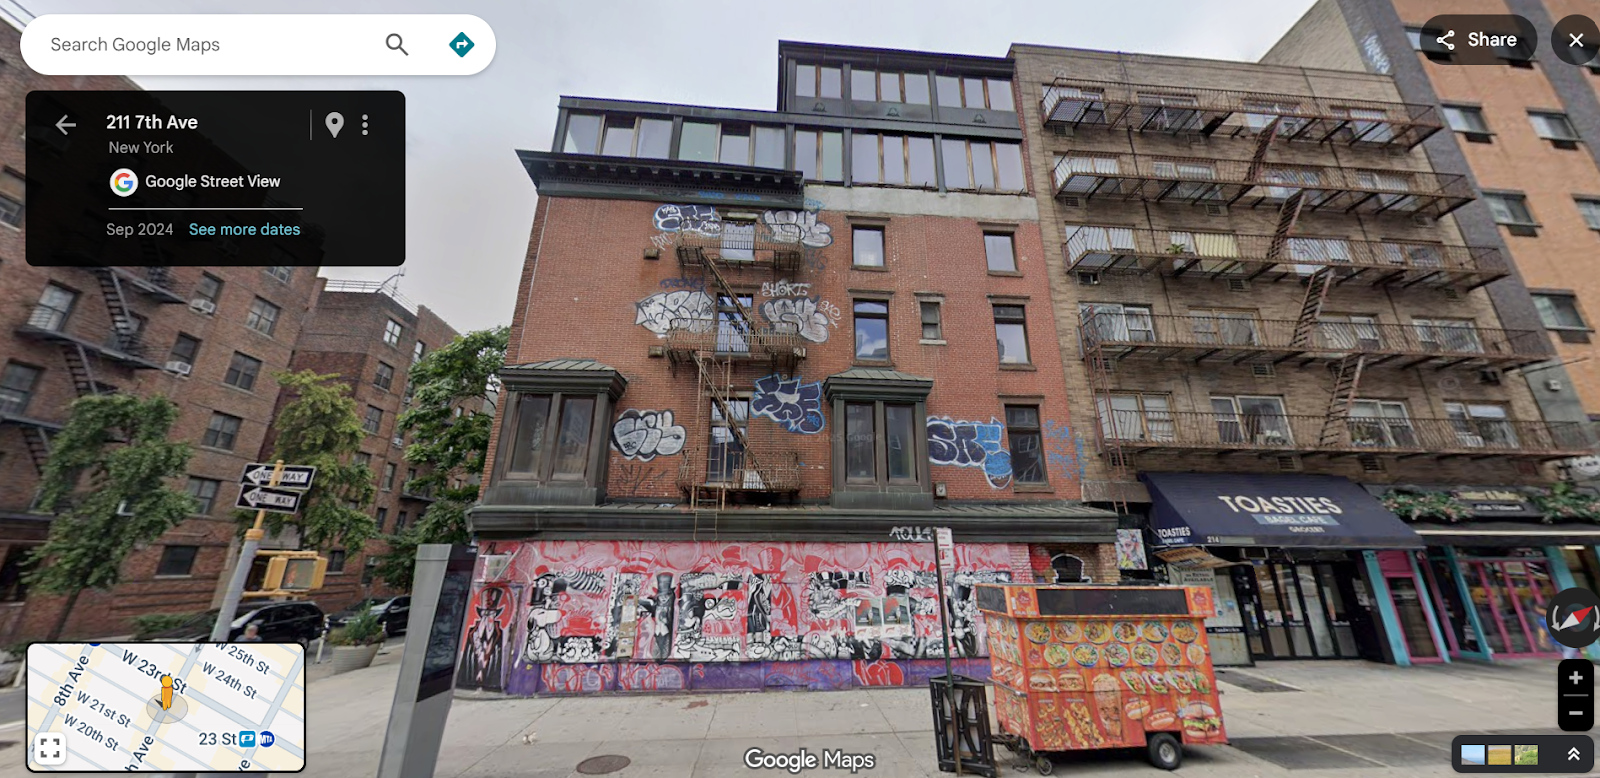
Using the location details mentioned in the posts, visible structures in the video were matched with Google Maps street imagery, confirming that the footage was indeed filmed in New York City.
Conclusion
The research establishes that the viral video is being shared with a false claim. It does not show any attack on an Israeli military facility but rather a residential building fire in New York City.

Related Blogs
Executive Summary
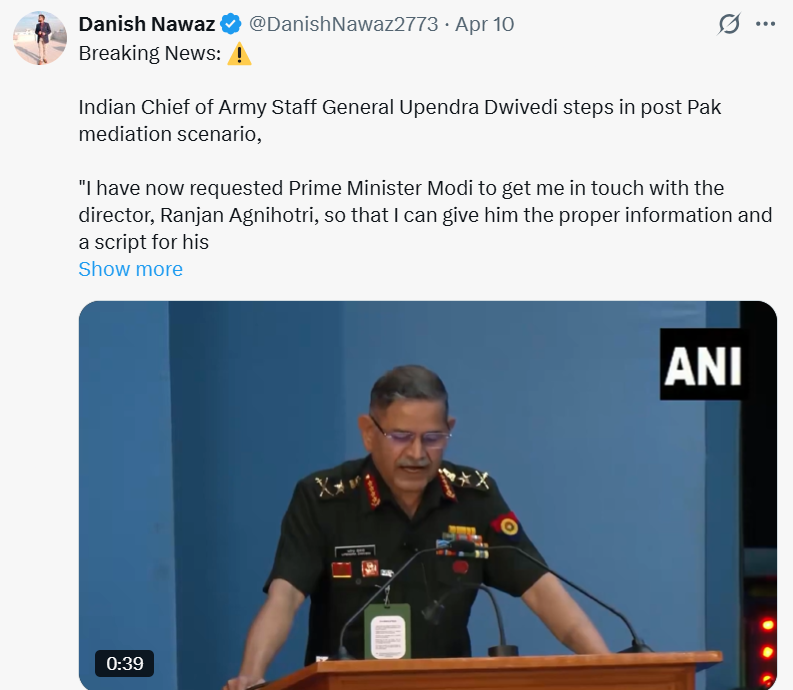
A video circulating on social media, shared by a Pakistani account, claims to show Indian Army Chief General Upendra Dwivedi making a controversial statement. In the clip, he is allegedly heard saying that he requested Prime Minister Narendra Modi to connect him with film director Ranjan Agnihotri so he could provide inputs and a script for a movie on “Operation Sindoor.”
However, research by CyberPeace has found that the viral video is an AI-generated deepfake. General Upendra Dwivedi has made no such statement.
Claim
A Pakistani user shared the viral video on X (formerly Twitter) on April 10, 2026, making the above claim.
Post links:
- https://x.com/DanishNawaz2773/status/2042312967811973225?s=20
- https://archive.ph/kAwoR
Fact Check
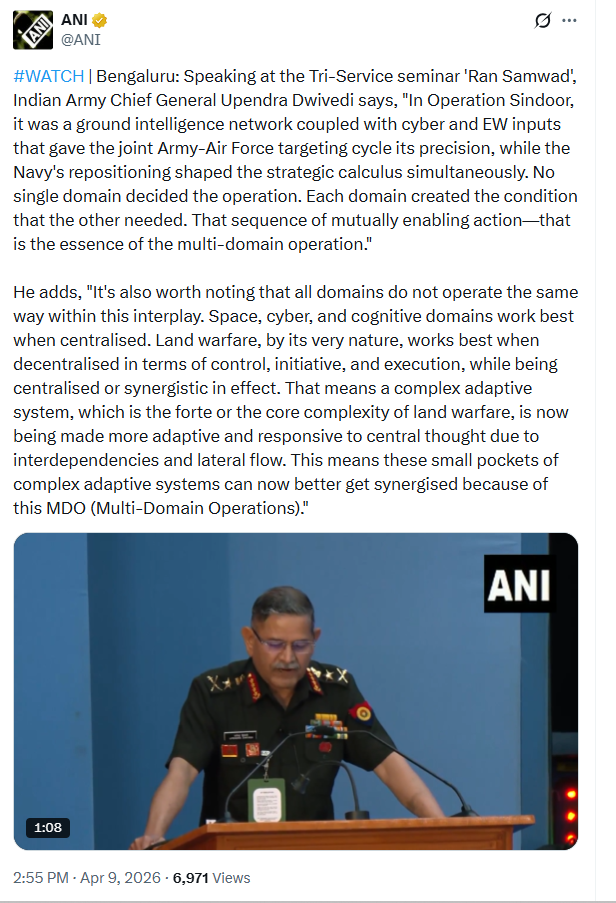
To verify the claim, we conducted keyword searches on Google but found no credible media reports supporting it. Further research led us to the original video posted on the X account of ANI. In this authentic clip, General Upendra Dwivedi is seen speaking at the ‘Ran Samwad’ seminar held in Bengaluru.
In the original video, he discusses the operational aspects of “Operation Sindoor,” including ground intelligence, cyber and electronic warfare inputs, Pakistan’s behaviour, and the challenges of a two-front scenario. There is no mention whatsoever of Pakistan mediation, Prime Minister Modi, Ranjan Agnihotri, any movie script, or a film based on Operation Sindoor.
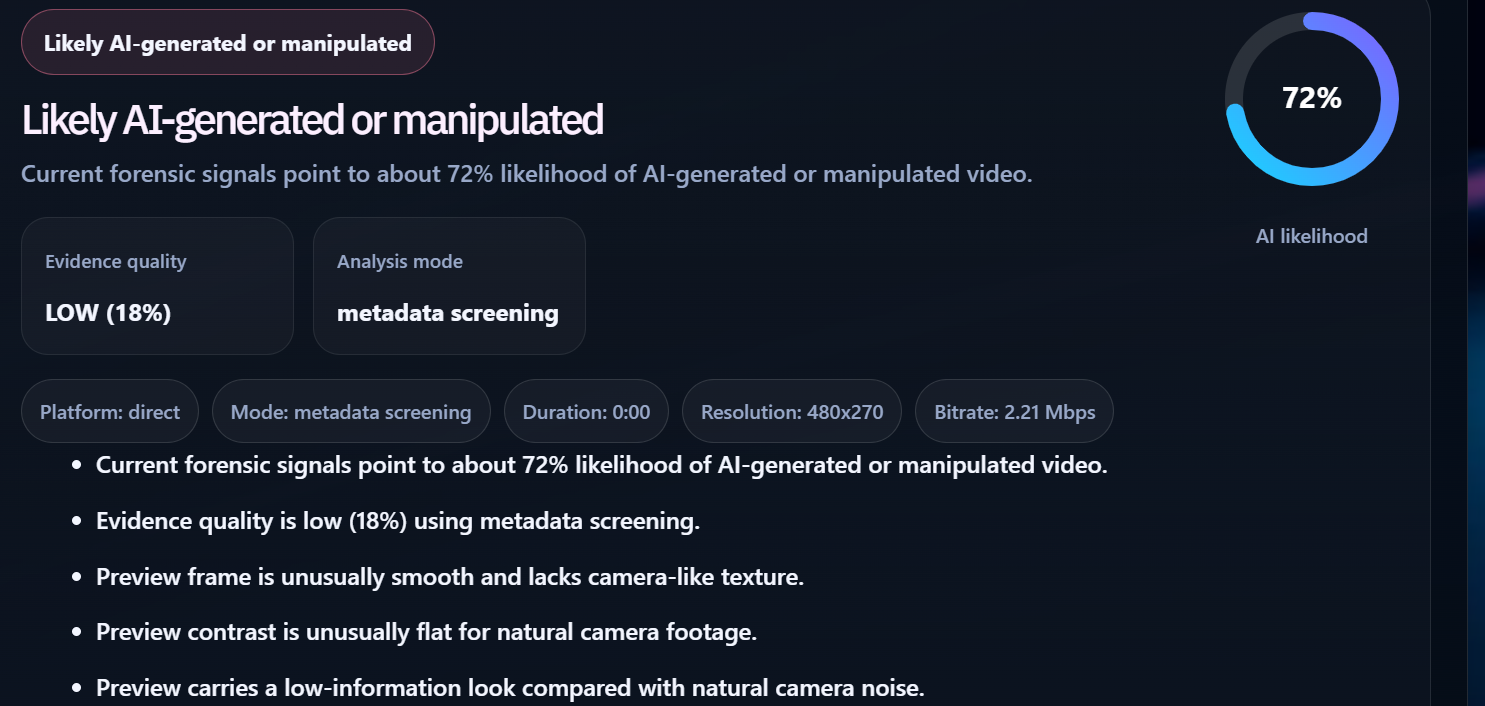
This clearly indicates that the viral clip has been manipulated and taken out of context. The video was further analyzed using the AI detection tool DetectVideo AI, which indicated a 72% probability that the content is AI-generated. This strongly supports the conclusion that the video is a deepfake.
Conclusion
The viral claim is false. The video featuring General Upendra Dwivedi has been digitally altered using AI techniques to insert fabricated statements. The original footage is from the ‘Ran Samwad’ seminar in Bengaluru, where he spoke about military strategy and multi-domain operations, not about any film or director. There is no evidence to suggest that he made any statement regarding contacting a filmmaker or contributing to a movie script. The inclusion of such references in the viral clip is entirely fabricated. This case highlights how AI-generated deepfakes are increasingly being used to spread misinformation, especially in sensitive contexts involving the military and international relations. Viewers are advised to rely on verified sources and exercise caution before sharing such content.

Introduction
A photo circulating on social media depicting modified tractors is being misrepresented as part of the 'Delhi Chalo' farmers' protest narrative. In the recent swirl of misinformation surrounding the 'Delhi Chalo' farmers' protest. A photo, ostensibly showing a phalanx of modified tractors, has been making the rounds on social media platforms, falsely tethered to the ongoing protests. This image, accompanied by a headline suggesting a mechanical metamorphosis to resist police barricades, was allegedly published by a news agency. However, beneath the surface of this viral phenomenon lies a more complex and fabricated reality.
The Movement
The 'Delhi Chalo' movement, a clarion call that resonated with thousands of farmers from the fertile plains of Punjab, the verdant fields of Haryana, and the sprawling expanses of Uttar Pradesh, has been a testament to the agrarian community's demand for assured crop prices and legal guarantees for the Minimum Support Price (MSP). The protest, which has seen the fortification of borders and the chaos at the Punjab-Haryana border on February 13, 2024, has become a crucible for the farmers' unyielding spirit.
Yet, amidst this backdrop of civil demonstration and discourse, a nefarious narrative of misinformation has taken root. The viral image, which has been shared with the fervour of wildfire, was accompanied by a screenshot of an article allegedly published by the news agency. This article, dated February 11, 2024, quoted an anonymous official who claimed that intelligence agencies had alerted the police to the protesters' plans to outfit tractors with hydraulic tools. The implication was clear: these machines had been transformed into battering rams against the bulwark of law enforcement.
The Pursuit of Truth
However, the India TV Fact Check team, in their relentless pursuit of truth, unearthed that the viral photo of these so-called modified tractors is nothing but a chimerical creation, a figment of artificial intelligence. Visual discrepancies betrayed its AI-generated nature.
This is not the first time that the misinformation has loomed over the farmers' protest. Previous instances, including a viral video of a modified tractor, have been debunked by the same fact-checking team. These efforts are a bulwark against the tide of false narratives that seek to muddy the waters of public understanding.
The claim that the photo depicted modified tractors intended for use in the ‘Delhi Chalo’ farmers' protest rally in Delhi on February 13, 2024, was a mirage.
The Fact Check
OpIndia, in their article, clarified that the photo used was a representative image created by AI and not a real photograph. To further scrutinize this viral photo, the HIVE AI detector tool was employed, indicating a 99.4% likelihood of the image being AI-generated. Thus, the claim made in the post was misleading.
The viral photo claiming that farmers had modified their tractors to avoid tear gas shells and remove barricades put up by the police during the rally was a digital illusion. The internet has become a fertile ground for the rapid spread of misinformation, reaching millions in an instant. Social media, with its complex algorithms, amplifies this spread, as any interaction, even those intended to debunk false information, inadvertently increases its reach. This phenomenon is exacerbated by 'echo chambers,' where users are exposed to a homogenous stream of content that reinforces their pre-existing beliefs, making it difficult to encounter and consider alternative perspectives.
Conclusion
The viral image depicting modified tractors for the ‘Delhi Chalo’ farmers' protest rally was a digital fabrication, a testament to the power of AI in creating convincing yet false narratives. As we navigate the labyrinth of information in the digital era, it is imperative to remain vigilant, to question the veracity of what we see and hear, and to rely on the diligent work of fact-checkers in discerning the truth. The mirage of modified machines serves as a stark reminder of the potency of misinformation and the importance of critical thinking in the age of artificial intelligence.
References
- https://www.indiatvnews.com/fact-check/fact-check-ai-generated-tractor-photo-misrepresented-delhi-chalo-farmers-protest-narrative-msp-police-barricades-punjab-haryana-uttar-pradesh-2024-02-15-917010
- https://factly.in/this-viral-image-depicting-modified-tractors-for-the-delhi-chalo-farmers-protest-rally-is-created-using-ai/

Disclaimer:
This report is based on extensive research conducted by CyberPeace Research using publicly available information, and advanced analytical techniques. The findings, interpretations, and conclusions presented are based on the data available at the time of study and aim to provide insights into global ransomware trends.
The statistics mentioned in this report are specific to the scope of this research and may vary based on the scope and resources of other third-party studies. Additionally, all data referenced is based on claims made by threat actors and does not imply confirmation of the breach by CyberPeace. CyberPeace includes this detail solely to provide factual transparency and does not condone any unlawful activities. This information is shared only for research purposes and to spread awareness. CyberPeace encourages individuals and organizations to adopt proactive cybersecurity measures to protect against potential threats.
CyberPeace Research does not claim to have identified or attributed specific cyber incidents to any individual, organization, or nation-state beyond the scope of publicly observable activities and available information. All analyses and references are intended for informational and awareness purposes only, without any intention to defame, accuse, or harm any entity.
While every effort has been made to ensure accuracy, CyberPeace Research is not liable for any errors, omissions, subsequent interpretations and any unlawful activities of the findings by third parties. The report is intended to inform and support cybersecurity efforts globally and should be used as a guide to foster proactive measures against cyber threats.
Executive Summary:
The 2024 ransomware landscape reveals alarming global trends, with 166 Threat Actor Groups leveraging 658 servers/underground resources and mirrors to execute 5,233 claims across 153 countries. Monthly fluctuations in activity indicate strategic, cyclical targeting, with peak periods aligned with vulnerabilities in specific sectors and regions. The United States was the most targeted nation, followed by Canada, the UK, Germany, and other developed countries, with the northwestern hemisphere experiencing the highest concentration of attacks. Business Services and Healthcare bore the brunt of these operations due to their high-value data, alongside targeted industries such as Pharmaceuticals, Mechanical, Metal, Electronics, and Government-related professional firms. Retail, Financial, Technology, and Energy sectors were also significantly impacted.
This research was conducted by CyberPeace Research using a systematic modus operandi, which included advanced OSINT (Open-Source Intelligence) techniques, continuous monitoring of Ransomware Group activities, and data collection from 658 servers and mirrors globally. The team utilized data scraping, pattern analysis, and incident mapping to track trends and identify hotspots of ransomware activity. By integrating real-time data and geographic claims, the research provided a comprehensive view of sectoral and regional impacts, forming the basis for actionable insights.
The findings emphasize the urgent need for proactive Cybersecurity strategies, robust defenses, and global collaboration to counteract the evolving and persistent threats posed by ransomware.
Overview:
This report provides insights into ransomware activities monitored throughout 2024. Data was collected by observing 166 Threat Actor Groups using ransomware technologies across 658 servers/underground resources and mirrors, resulting in 5,233 claims worldwide. The analysis offers a detailed examination of global trends, targeted sectors, and geographical impact.
Top 10 Threat Actor Groups:
The ransomware group ‘ransomhub’ has emerged as the leading threat actor, responsible for 527 incidents worldwide. Following closely are ‘lockbit3’ with 522 incidents and ‘play’ with 351. Other Groups are ‘akira’, ‘hunters’, ‘medusa’, ‘blackbasta’, ‘qilin’, ‘bianlian’, ‘incransom’. These groups usually employ advanced tactics to target critical sectors, highlighting the urgent need for robust cybersecurity measures to mitigate their impact and protect organizations from such threats.

Monthly Ransomware Incidents:
In January 2024, the value began at 284, marking the lowest point on the chart. The trend rose steadily in the subsequent months, reaching its first peak at 557 in May 2024. However, after this peak, the value dropped sharply to 339 in June. A gradual recovery follows, with the value increasing to 446 by August. September sees another decline to 389, but a sharp rise occurs afterward, culminating in the year’s highest point of 645 in November. The year concludes with a slight decline, ending at 498 in December 2024 (till 28th of December).

Top 10 Targeted Countries:
- The United States consistently topped the list as the primary target probably due to its advanced economic and technological infrastructure.
- Other heavily targeted nations include Canada, UK, Germany, Italy, France, Brazil, Spain, and India.
- A total of 153 countries reported ransomware attacks, reflecting the global scale of these cyber threats

Top Affected Sectors:
- Business Services and Healthcare faced the brunt of ransomware threat due to the sensitive nature of their operations.
- Specific industries under threats:
- Pharmaceutical, Mechanical, Metal, and Electronics industries.
- Professional firms within the Government sector.
- Other sectors:
- Retail, Financial, Technology, and Energy sectors were also significant targets.

Geographical Impact:
The continuous and precise OSINT(Open Source Intelligence) work on the platform, performed as a follow-up action to data scraping, allows a complete view of the geography of cyber attacks based on their claims. The northwestern region of the world appears to be the most severely affected by Threat Actor groups. The figure below clearly illustrates the effects of this geographic representation on the map.

Ransomware Threat Trends in India:
In 2024, the research identified 98 ransomware incidents impacting various sectors in India, marking a 55% increase compared to the 63 incidents reported in 2023. This surge highlights a concerning trend, as ransomware groups continue to target India's critical sectors due to its growing digital infrastructure and economic prominence.

Top Threat Actors Group Targeted India:
Among the following threat actors ‘killsec’ is the most frequent threat. ‘lockbit3’ follows as the second most prominent threat, with significant but lower activity than killsec. Other groups, such as ‘ransomhub’, ‘darkvault’, and ‘clop’, show moderate activity levels. Entities like ‘bianlian’, ‘apt73/bashe’, and ‘raworld’ have low frequencies, indicating limited activity. Groups such as ‘aps’ and ‘akira’ have the lowest representation, indicating minimal activity. The chart highlights a clear disparity in activity levels among these threats, emphasizing the need for targeted cybersecurity strategies.

Top Impacted Sectors in India:
The pie chart illustrates the distribution of incidents across various sectors, highlighting that the industrial sector is the most frequently targeted, accounting for 75% of the total incidents. This is followed by the healthcare sector, which represents 12% of the incidents, making it the second most affected. The finance sector accounts for 10% of the incidents, reflecting a moderate level of targeting. In contrast, the government sector experiences the least impact, with only 3% of the incidents, indicating minimal targeting compared to the other sectors. This distribution underscores the critical need for enhanced cybersecurity measures, particularly in the industrial sector, while also addressing vulnerabilities in healthcare, finance, and government domains.

Month Wise Incident Trends in India:
The chart indicates a fluctuating trend with notable peaks in May and October, suggesting potential periods of heightened activity or incidents during these months. The data starts at 5 in January and drops to its lowest point, 2, in February. It then gradually increases to 6 in March and April, followed by a sharp rise to 14 in May. After peaking in May, the metric significantly declines to 4 in June but starts to rise again, reaching 7 in July and 8 in August. September sees a slight dip to 5 before the metric spikes dramatically to its highest value, 24, in October. Following this peak, the count decreases to 10 in November and then drops further to 7 in December.

CyberPeace Advisory:
- Implement Data Backup and Recovery Plans: Backups are your safety net. Regularly saving copies of your important data ensures you can bounce back quickly if ransomware strikes. Make sure these backups are stored securely—either offline or in a trusted cloud service—to avoid losing valuable information or facing extended downtime.
- Enhance Employee Awareness and Training: People often unintentionally open the door to ransomware. By training your team to spot phishing emails, social engineering tricks, and other scams, you empower them to be your first line of defense against attacks.
- Adopt Multi-Factor Authentication (MFA): Think of MFA as locking your door and adding a deadbolt. Even if attackers get hold of your password, they’ll still need that second layer of verification to break in. It’s an easy and powerful way to block unauthorized access.
- Utilize Advanced Threat Detection Tools: Smart tools can make a world of difference. AI-powered systems and behavior-based monitoring can catch ransomware activity early, giving you a chance to stop it in its tracks before it causes real damage.
- Conduct Regular Vulnerability Assessments: You can’t fix what you don’t know is broken. Regularly checking for vulnerabilities in your systems helps you identify weak spots. By addressing these issues proactively, you can stay one step ahead of attackers.
Conclusion:
The 2024 ransomware landscape reveals the critical need for proactive cybersecurity strategies. High-value sectors and technologically advanced regions remain the primary targets, emphasizing the importance of robust defenses. As we move into 2025, it is crucial to anticipate the evolution of ransomware tactics and adopt forward-looking measures to address emerging threats.
Global collaboration, continuous innovation in cybersecurity technologies, and adaptive strategies will be imperative to counteract the persistent and evolving threats posed by ransomware activities. Organizations and governments must prioritize preparedness and resilience, ensuring that lessons learned in 2024 are applied to strengthen defenses and minimize vulnerabilities in the year ahead.
