
#FactCheck: India-Bangladesh Border Video Falsely Shared as Chinese Army Occupying Arunachal Pradesh
Executive Summary
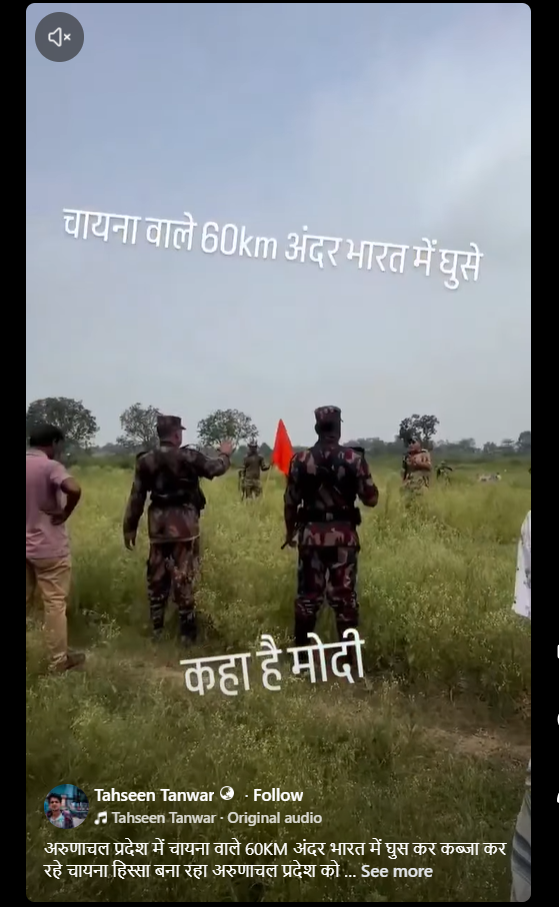
A video is being widely shared on social media with the claim that the Chinese Army has entered 60 kilometres inside Arunachal Pradesh and occupied Indian territory. In the video, a man appears to be recording the situation using his selfie camera, while soldiers can be seen standing face-to-face and arguing with each other in the background. The CyberPeace Research Wing found that the claim is false. The viral video is not from Arunachal Pradesh. It shows a confrontation between India’s Border Security Force (BSF) and Bangladesh’s Border Guard Bangladesh (BGB) along the India-Bangladesh border.
Claim
A Facebook user shared the video with the caption:
"China is entering 60 km inside India and occupying Arunachal Pradesh. China is turning Arunachal Pradesh into its territory. Where are Prime Minister Modi, Defence Minister Rajnath Singh and Home Minister Amit Shah?"
Post link:
https://www.facebook.com/reel/1736825064305394
https://www.facebook.com/reel/1736825064305394
FactCheck
Our research found no credible news report confirming that Chinese troops had entered 60 kilometres inside Arunachal Pradesh or occupied Indian territory.
The people in the viral video can be heard speaking in Bengali, suggesting that the footage could be from the India-Bangladesh border rather than Arunachal Pradesh.
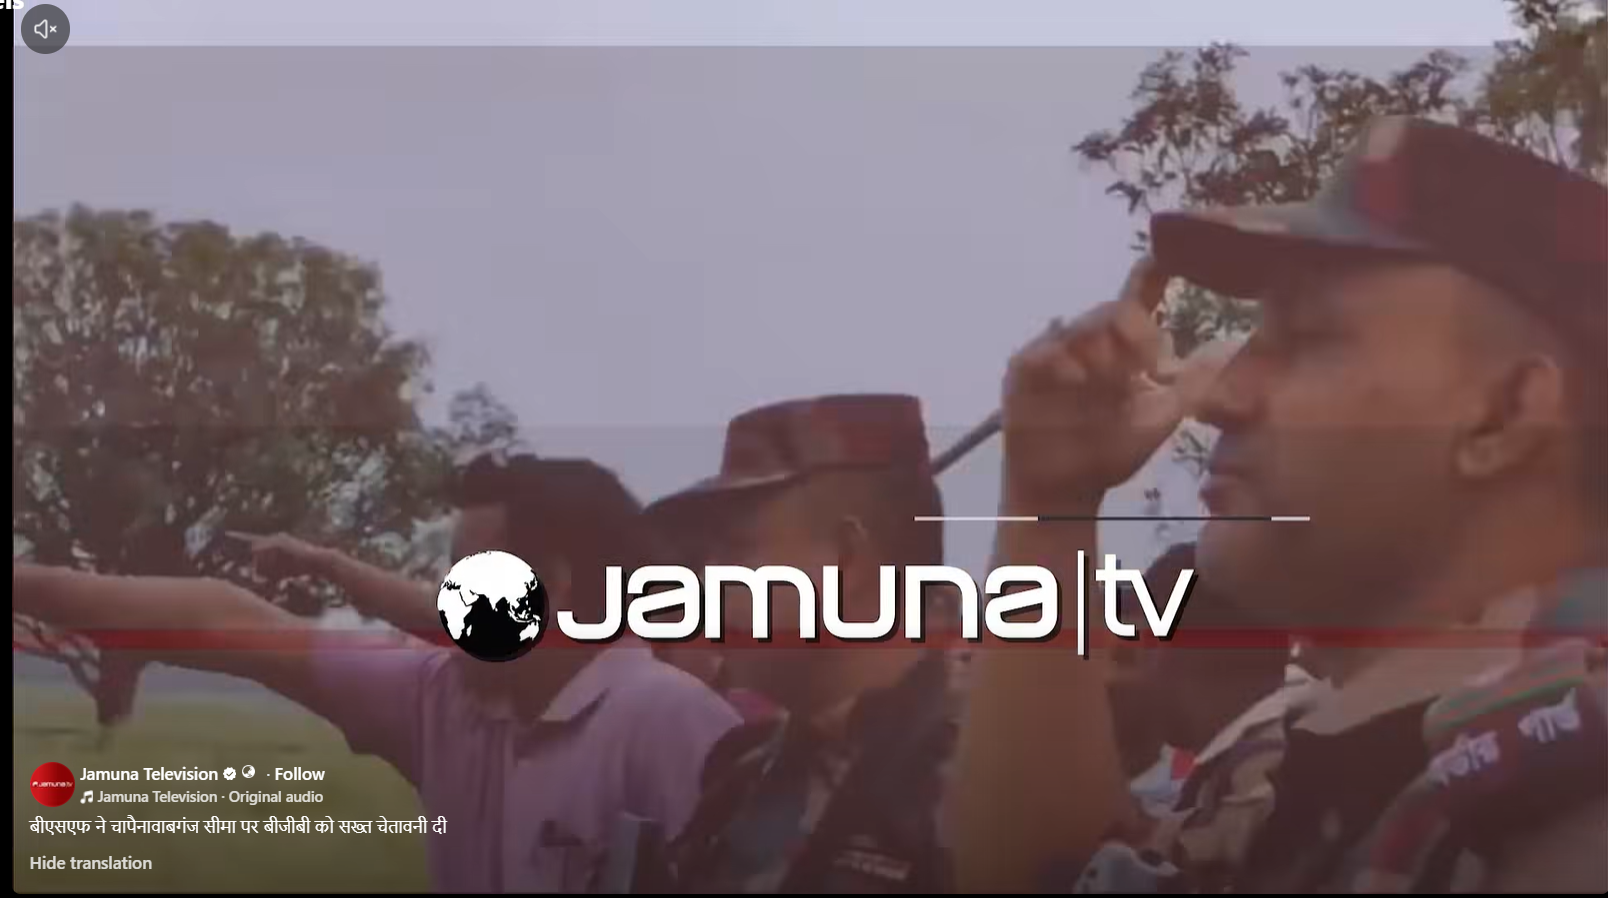
A reverse image search of keyframes from the viral video led us to an identical video posted on the Facebook page of Bangladeshi news channel Jamuna TV on June 20. According to the caption, the incident took place along the Chapainawabganj border in Bangladesh, where personnel of India’s BSF and Bangladesh’s BGB had confronted each other.
https://www.facebook.com/reel/1049262804595610
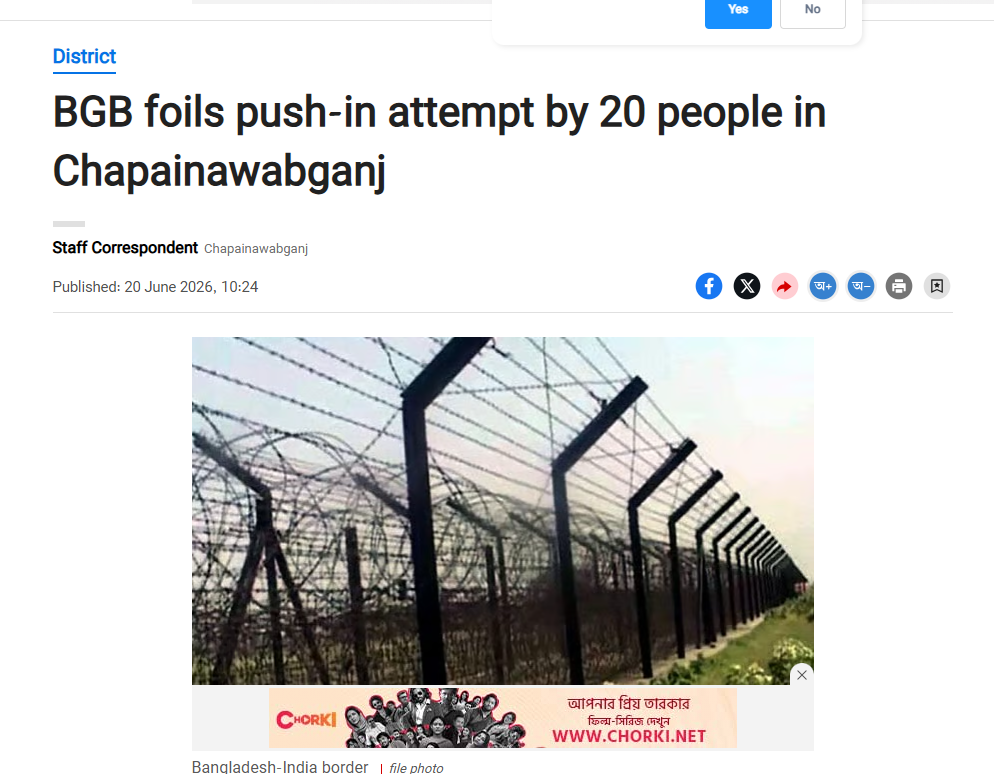
We also found reports from Bangladeshi media outlet Prothom Alo about the incident. According to the reports, Bangladeshi security personnel had stopped around 20 people who were attempting to return to Bangladesh from India, following which a verbal altercation took place between BSF and BGB personnel.
https://www.prothomalo.com/bangladesh/district/syzkfootaq
Conclusion
The viral claim is false. The video does not show Chinese troops entering or occupying 60 kilometres of territory inside Arunachal Pradesh. It actually shows a confrontation between BSF and BGB personnel along the India-Bangladesh border in the Chapainawabganj area of Bangladesh. The footage is being circulated with a false Arunachal Pradesh-related narrative.

Related Blogs

Executive Summary
A video is being shared on social media with the claim that it shows Iran’s attack on a US military base located in Kuwait. It is being claimed that the video is from a recent attack carried out by Iran. CyberPeace Research Wing ’s research found the claim to be false. The research revealed that the video is actually from Panwan, a coastal town in southern Pakistan. The footage was published in connection with reports of a suicide attack carried out by a prominent militant organisation. The video has no connection with the alleged Iranian attack on a US military base in Kuwait.
Claim:
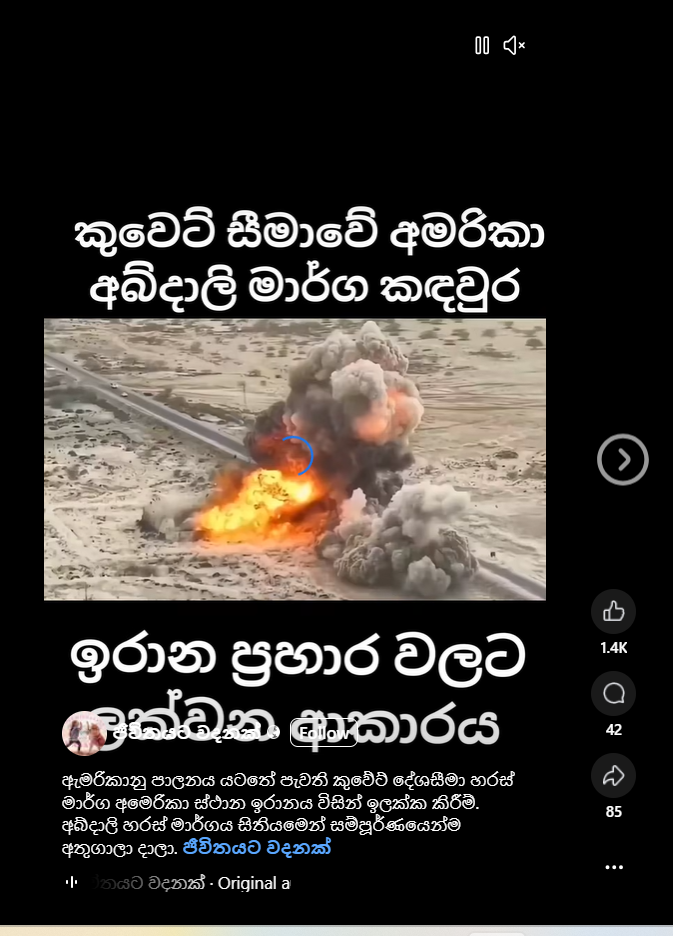
A Facebook post shared in the Sinhala language on July 25, 2026, claimed: “Iran targeted US-controlled Kuwaiti border checkpoints. The Abdali border checkpoint has been completely destroyed.” The post was shared along with a video of around one minute. In the video, a blue truck can be seen entering a secured compound. Within seconds, a massive explosion takes place, followed by a thick cloud of smoke rising into the sky. Text written in Sinhala on the video claimed: “Watch how Iran is attacking the US Abdali border crossing base located on the Kuwait border.”
https://www.facebook.com/reel/979364938493872
https://web.archive.org/web/20260730055635/https://www.facebook.com/reel/979364938493872
Factcheck
As part of the research, keyframes from the viral video were extracted and a reverse image search was conducted. During the search, we found a report published by India Today on July 4, 2026. According to the report, the footage actually shows a suicide attack carried out by the Pakistan-based Baloch Liberation Army (BLA) militant group.
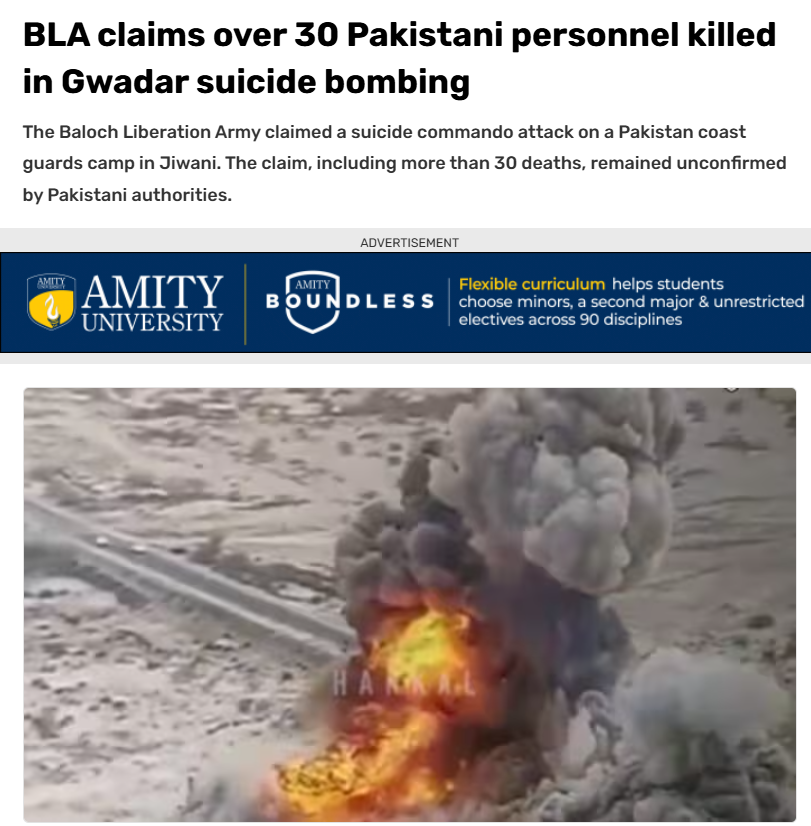
Further research led us to a report about a suicide bombing in Gwadar, Pakistan. According to the report, the BLA claimed responsibility for the attack and claimed that more than 30 security personnel were killed. Journalist Diksha Bisla also shared details about the incident.
https://www.facebook.com/watch/?v=1233630812123459

A search on Google Maps showed the Panwan area and a structure along Gwadar Road that resembles the location visible in the viral video.

Conclusion:
CyberPeace Research Wing ’s research found that the claim is false. The viral video is not related to any alleged Iranian attack on a US military base in Kuwait. The footage is from Panwan, a coastal town in southern Pakistan, and was circulated during reports of a suicide attack claimed by the Baloch Liberation Army (BLA).
Introduction
The appeal is to be heard by the TDSAT (telecommunication dispute settlement & appellate tribunal) regarding several changes under Digital personal data protection. The Changes should be a removal of the deemed consent, a change in appellate mechanism, No change in delegation legislation, and under data breach. And there are some following other changes in the bill, and the digital personal data protection bill 2023 will now provide a negative list of countries that cannot transfer the data.
New Version of the DPDP Bill
The Digital Personal Data Protection Bill has a new version. There are three major changes in the 2022 draft of the digital personal data protection bill. The changes are as follows: The new version proposes changes that there shall be no deemed consent under the bill and that the personal data processing should be for limited uses only. By giving the deemed consent, there shall be consent for the processing of data for any purposes. That is why there shall be no deemed consent.
- In the interest of the sovereignty
- The integrity of India and the National Security
- For the issue of subsidies, benefits, services, certificates, licenses, permits, etc
- To comply with any judgment or order under the law
- To protect, assist, or provide service in a medical or health emergency, a disaster situation, or to maintain public order
- In relation to an employee and his/her rights
The 2023 version now includes an appeals mechanism
It states that the Board will have the authority to issue directives for data breach remediation or mitigation, investigate data breaches and complaints, and levy financial penalties. It would be authorised to submit complaints to alternative dispute resolution, accept voluntary undertakings from data fiduciaries, and advise the government to prohibit a data fiduciary’s website, app, or other online presence if the terms of the law were regularly violated. The Telecom Disputes Settlement and Appellate Tribunal will hear any appeals.
The other change is in delegated legislation, as one of the criticisms of the 2022 version bill was that it gave the government extensive rule-making powers. The committee also raised the same concern with the ministry. The committed wants that the provisions that cannot be fully defined within the scope of the bill can be addressed.
The other major change raised in the new version bill is regarding the data breach; there will be no compensation for the data breach. This raises a significant concern for the victims, If the victims suffer a data breach and he approaches the relevant court or authority, he will not be awarded compensation for the loss he has suffered due to the data breach.
Need of changes under DPDP
There is a need for changes in digital personal data protection as we talk about the deemed consent so simply speaking, by ‘deeming’ consent for subsequent uses, your data may be used for purposes other than what it has been provided for and, as there is no provision for to be informed of this through mandatory notice, there may never even come to know about it.
Conclusion
The bill requires changes to meet the need of evolving digital landscape in the digital personal data protection 2022 draft. The removal of deemed consent will ultimately protect the data of the data principal. And the data of the data principal will be used or processed only for the purpose for which the consent is given. The change in the appellate mechanism is also crucial as it meets the requirements of addressing appeals. However, the no compensation for a data breach is derogatory to the interest of the victim who has suffered a data breach.

Disclaimer:
This report is the collaborative outcome of insights derived from the CyberPeace Helpline’s operational statistics and the CyberPeace Research Team, covering the monthly helpline case trends of May 2025, the report identifies recurring trends, operational challenges, and strategic opportunities. The objective is to foster research-driven solutions that enhance the overall efficacy of the helpline.
Executive Summary:
This report summarizes the cybercrime cases reported in May, offering insights into case types, gender distribution, resolution status, and geographic trends.
As per our analysis, out of various Cyber Frauds Financial Fraud was the most reported issue, making up 43% of cases, followed by Cyberbullying (26%) and Impersonation (14%). Less frequent but serious issues included Sexual Harassment, Sextortion, Hacking, Data Tampering, and Cyber Defamation, each accounting for 3–6%, highlighting a mix of financial and behavioral threats.The gender distribution was fairly balanced, with 51% male and 49% female respondents. While both genders were affected by major crimes like financial fraud and cyber bullying, some categories—such as sexual harassment—reflected more gender-specific risks, indicating the need for gender-responsive policies and support.
Regarding case status, 60% remain under follow-up while 40% have been resolved, reflecting strong case-handling efforts by the team.
The location-wise data shows higher case concentrations in Uttar Pradesh, Andhra Pradesh, Karnataka, and West Bengal, with significant reports also from Delhi, Telangana, Maharashtra, and Odisha. Reports from the northeastern and eastern states confirm the nationwide spread of cyber incidents.In conclusion, the findings point to a growing need for enhanced cybersecurity awareness, preventive strategies, and robust digital safeguards to address the evolving cyber threat landscape across India.
Cases Received in May:
As per the given dataset, the following types of cases were reported to our team during the month of May:
- 💰 Financial Fraud – 43%
- 💬 Cyber Bullying – 26%
- 🕵️♂️ Impersonation – 14%
- 🚫 Sexual Harassment – 6%
- 📸 Sextortion – 3%
- 💻 Hacking – 3%
- 📝 Data Tampering – 3%
- 🗣️ Cyber Defamation – 3%

The chart illustrates various cybercrime categories and their occurrence rates. Financial Fraud emerges as the most common, accounting for 43% of cases, highlighting the critical need for stronger digital financial security. This is followed by Cyber Bullying at 26%, reflecting growing concerns around online harassment, especially among youth. Impersonation ranks third with 14%, involving identity misuse for deceitful purposes. Less frequent but still serious crimes such as Sexual Harassment (6%), Sextortion, Hacking, Data Tampering, and Cyber Defamation (each 3%) also pose significant risks to users’ privacy and safety. Overall, the data underscores the need for improved cybersecurity awareness, legal safeguards, and preventive measures to address both financial and behavioral threats in the digital space.
Gender-Wise Distribution:
- 👨 Male – 51%
- 👩 Female – 49%

The chart illustrates the distribution of respondents by gender. The data shows that Male participants make up 51% of the total, while Female participants account for 49%. This indicates a fairly balanced representation of both genders, with a slight majority of male respondents.
Gender-Wise Case Distribution:

- The chart presents a gender-wise distribution of various cybercrime cases, offering a comparative view of how different types of cyber incidents affect males and females.
- It highlights that both genders are significantly impacted by cybercrimes such as financial fraud and cyber bullying, indicating a widespread risk across the board.
- Certain categories, including sexual harassment, cyber defamation, and hacking, show more gender-specific patterns of victimization, pointing to differing vulnerabilities.
- The data suggests the need for gender-sensitive policies and preventive measures to effectively address the unique risks faced by males and females in the digital space.
- These insights can inform the design of tailored awareness programs, support services, and intervention strategies aimed at improving cybersecurity for all individuals.
Major Location Wise Distribution:
The map visualization displays location-wise distribution of reported cases across India. The cases reflect the cyber-related incidents or cases mapped geographically.

The map highlights the regional distribution of cybercrime cases across Indian states, with a higher concentration in Uttar Pradesh, Andhra Pradesh, Karnataka, and West Bengal. States like Delhi, Telangana, Maharashtra, and Odisha also show notable activity, indicating widespread cyber threats. Regions including Assam, Tripura, Bihar, Jharkhand, and Jammu & Kashmir further reflect the pan-India spread of such incidents. This distribution stresses the need for targeted cybersecurity awareness and stronger digital safeguards nationwide
CyberPeace Advisory:
- Use Strong and Unique Passwords: Create complex passwords using a mix of letters, numbers, and symbols. Avoid reusing the same password across multiple platforms.
- Enable Multi-Factor Authentication (MFA): Add an extra layer of security by using a second verification step like an OTP or authentication app.
- Keep Software Updated: Regularly update your operating system, apps, and security tools to protect against known vulnerabilities.
- Install Trusted Security Software: Use reliable antivirus and anti-malware programs to detect and block threats.
- Limit Information Sharing: Be cautious about sharing personal or sensitive details, especially on social media or public platforms.
- Secure Your Network: Protect your Wi-Fi with a strong password and encryption. Avoid accessing confidential information on public networks.
- Back Up Important Data: Regularly save copies of important files in secure storage to prevent data loss in case of an attack.
- Stay Informed with Cybersecurity Training: Learn how to identify scams, phishing attempts, and other online threats through regular awareness sessions.
- Control Access to Data: Give access to sensitive information only to those who need it, based on their job roles.
- Monitor and Respond to Threats: Continuously monitor systems for unusual activity and have a clear response plan for handling security incidents.
- CyberPeace Helpline mail ID: helpline@cyberpeace.net
- CyberPeace Helpline Number: 9570000066
- Central Government Helpline: https://cybercrime.gov.in/
- Central Government Helpline Number: 1930
Conclusion
The cybercrime cases reported in May highlight a diverse and evolving threat landscape across India. Financial fraud, cyber bullying, and impersonation are the most prevalent, affecting both genders almost equally, though some crimes like sexual harassment call for targeted gender-sensitive measures. With 60% of cases still under follow-up, the team’s efforts in investigation and resolution remain strong. Geographically, cyber incidents are widespread, with higher concentrations in several key states, demonstrating that no region is immune. These findings underscore the urgent need to enhance cybersecurity awareness, strengthen preventive strategies, and build robust digital safeguards. Proactive and inclusive approaches are essential to protect individuals and communities and to address the growing challenges posed by cybercrime nationwide.
