
#FactCheck: A digitally altered video of actor Sebastian Stan shows him changing a ‘Tell Modi’ poster to one that reads ‘I Told Modi’ on a display panel.
Executive Summary:
A widely circulated video claiming to feature a poster with the words "I Told Modi" has gone viral, improperly connecting it to the April 2025 Pahalgam attack, in which terrorists killed 26 civilians. The altered Marvel Studios clip is allegedly a mockery of Operation Sindoor, the counterterrorism operation India initiated in response to the attack. This misinformation emphasizes how crucial it is to confirm information before sharing it online by disseminating misleading propaganda and drawing attention away from real events.
Claim:
A man can be seen changing a poster that says "Tell Modi" to one that says "I Told Modi" in a widely shared viral video. This video allegedly makes reference to Operation Sindoor in India, which was started in reaction to the Pahalgam terrorist attack on April 22, 2025, in which militants connected to The Resistance Front (TRF) killed 26 civilians.


Fact check:
Further research, we found the original post from Marvel Studios' official X handle, confirming that the circulating video has been altered using AI and does not reflect the authentic content.

By using Hive Moderation to detect AI manipulation in the video, we have determined that this video has been modified with AI-generated content, presenting false or misleading information that does not reflect real events.

Furthermore, we found a Hindustan Times article discussing the mysterious reveal involving Hollywood actor Sebastian Stan.

Conclusion:
It is untrue to say that the "I Told Modi" poster is a component of a public demonstration. The text has been digitally changed to deceive viewers, and the video is manipulated footage from a Marvel film. The content should be ignored as it has been identified as false information.
- Claim: Viral social media posts confirm a Pakistani military attack on India.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

The European Union (EU) has made trailblazing efforts regarding protection and privacy, coming up with the most comprehensive and detailed regulation called the GDPR (General Data Protection Regulation). As countries worldwide continue to grapple with setting their laws, the EU is already taking on issues with tech giants and focusing on the road ahead. Its contentious issues with Meta and the launch of Meta’s AI assistant in the EU are thus seen as a complex process, shaped by stringent data privacy regulations, ongoing debates over copyright, and ethical AI practices. This development is considered important as previously, the EU and Meta have had issues (including fines and and also received a pushback concerning its services), which broadly include data privacy regarding compliance with GDPR, antitrust law concerns- targeting ads, facebook marketplace activities and content moderation with respect to the spread of misinformation.
Privacy and Data Protection Concerns
A significant part of operating Large Language Models (LLMs) is the need to train them with a repository of data/ plausible answers from which they can source. If it doesn’t find relevant information or the request is out of its scope, programmed to answer, it shall continue to follow orders, but with a reduction in the accuracy of its response. Meta's initial plans to train its AI models using publicly available content from adult users in the EU received a setback from privacy regulators. The Irish Data Protection Commission (DPC), acting as Meta's lead privacy regulator in Europe, raised the issue and requested a delay in the rollout to assess its compliance with GDPR. It has also raised similar concerns with Grok, the AI tool of X, to assess whether the EU users’ data was lawfully processed for training it.
In response, Meta stalled the release of this feature for around a year and agreed to exclude private messages and data from users under the age of 18 and implemented an opt-out mechanism for users who do not wish their public data to be used for AI training. This approach aligns with GDPR requirements, which mandate a clear legal basis for processing personal data, such as obtaining explicit consent or demonstrating legitimate interest, along with the option of removal of consent at a later stage, as the user wishes. The version/service available at the moment is a text-based assistant which is not capable of things like image generation, but can provide services and assistance which include brainstorming, planning, and answering queries from web-based information. However, Meta has assured its users of expansion and exploration regarding the AI features in the near future as it continues to cooperate with the regulators.
Regulatory Environment and Strategic Decisions
The EU's regulatory landscape, characterised by the GDPR and the forthcoming AI Act, presents challenges for tech companies like Meta. Citing the "unpredictable nature" of EU regulations, Meta has decided not to release its multimodal Llama AI model—capable of processing text, images, audio, and video—in the EU. This decision underscores the tension between innovation and regulatory compliance, as companies navigate the complexities of deploying advanced AI technologies within strict legal frameworks.
Implications and Future Outlook
Meta's experience highlights the broader challenges faced by AI developers operating in jurisdictions with robust data protection laws. The most critical issue that remains for now is to strike a balance between leveraging user data for AI advancement while respecting individual privacy rights.. As the EU continues to refine its regulatory approach to AI, companies need to adapt their strategies to ensure compliance while fostering innovation. Stringent measures and regular assessment also keep in check the accountability of big tech companies as they make for profit as well as for the public.
Reference:
- https://thehackernews.com/2025/04/meta-resumes-eu-ai-training-using.html
- https://www.thehindu.com/sci-tech/technology/meta-to-train-ai-models-on-european-users-public-data/article69451271.ece
- https://about.fb.com/news/2025/04/making-ai-work-harder-for-europeans/
- https://www.theregister.com/2025/04/15/meta_resume_ai_training_eu_user_posts/
- https://noyb.eu/en/twitters-ai-plans-hit-9-more-gdpr-complaints
- https://www.businesstoday.in/technology/news/story/meta-ai-finally-comes-to-europe-after-a-year-long-delay-but-with-some-limitations-468809-2025-03-21
- https://www.bloomberg.com/news/articles/2025-02-13/meta-opens-facebook-marketplace-to-rivals-in-eu-antitrust-clash
- https://www.nytimes.com/2023/05/22/business/meta-facebook-eu-privacy-fine.html#:~:text=Many%20civil%20society%20groups%20and,million%20for%20a%20data%20leak.
- https://ec.europa.eu/commission/presscorner/detail/en/ip_24_5801
- https://www.thehindu.com/sci-tech/technology/european-union-accuses-facebook-owner-meta-of-breaking-digital-rules-with-paid-ad-free-option/article68358039.ece
- https://www.theregister.com/2025/04/14/ireland_investigation_into_x/
- https://www.theverge.com/2024/7/18/24201041/meta-multimodal-llama-ai-model-launch-eu-regulations?utm_source=chatgpt.com
- https://www.axios.com/2024/07/17/meta-future-multimodal-ai-models-eu?utm_source=chatgpt.com
Executive Summary
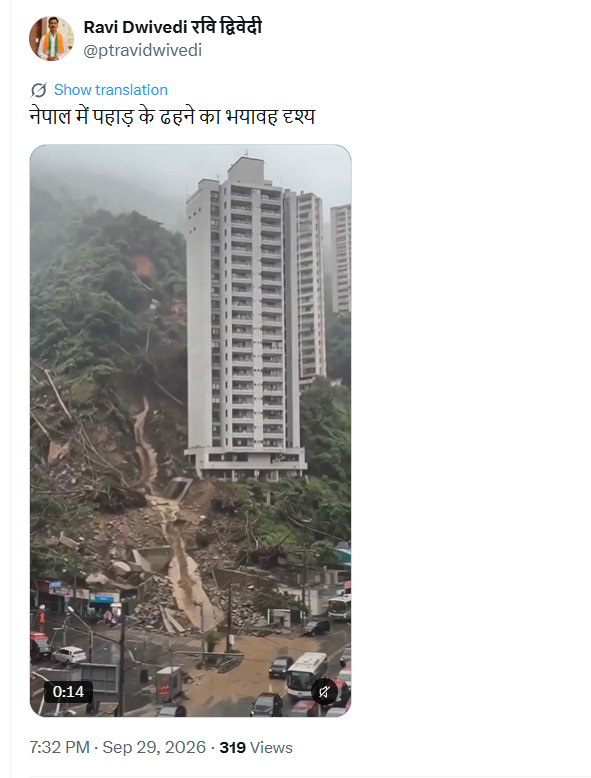
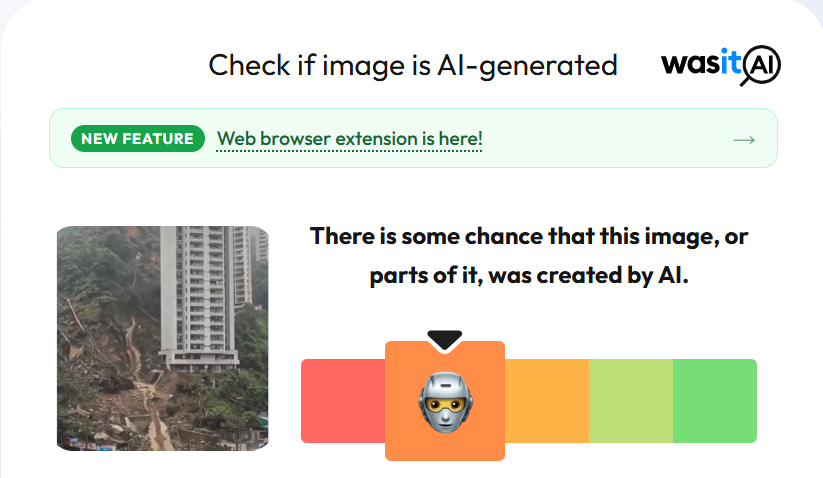
A video is being shared on social media showing a large amount of debris cascading down a mountain amid multi-storey buildings. The video is being shared with the claim that it shows a landslide incident in Nepal. CyberPeace Research found the viral claim to be false. Our research found that the viral video is AI-generated and is being shared with a misleading claim.
Claim:
A Facebook user shared the viral video on September 29, 2026, with the caption, “A horrifying scene of a mountain collapsing in Nepal.” The post link, archive link and screenshot are provided below.
https://x.com/ptravidwivedi/status/2104934750595219494
Fact Check
To verify the authenticity of the viral claim, we conducted a reverse image search using keyframes from the video. However, we did not find any credible media reports or other reliable sources related to the video during the search. Upon closely examining the viral video, we noticed several inconsistencies that raised suspicions that the video may be AI-generated.
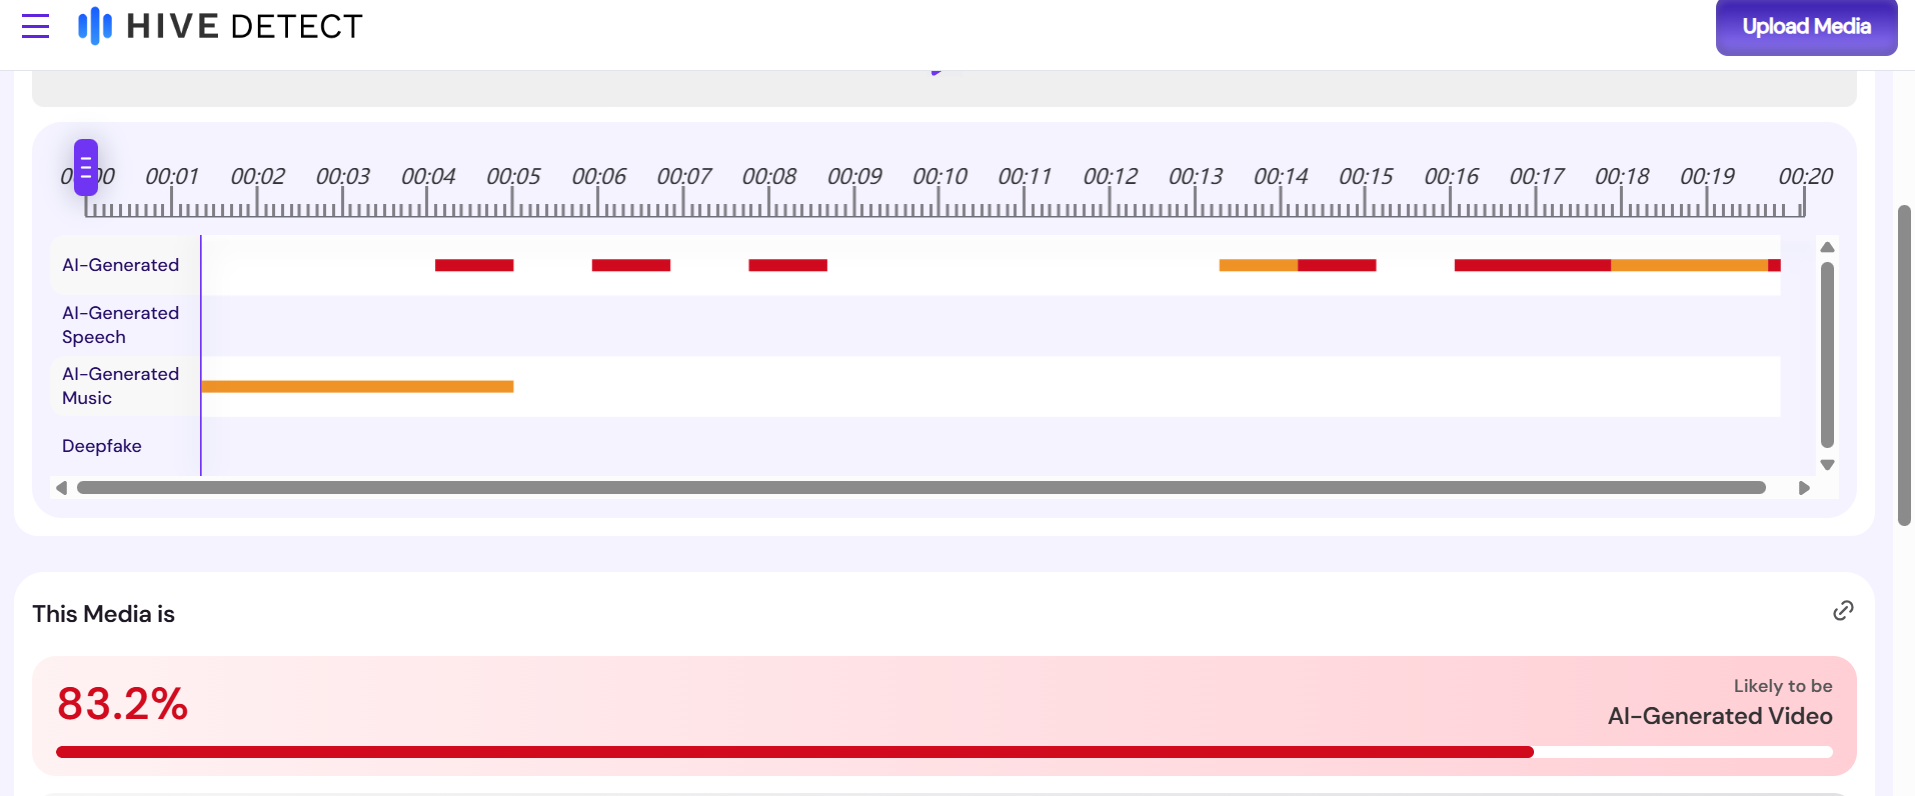
As part of the next step in our research, we scanned the video using the AI detection tool Hive Detect. According to the results, the viral video has an 83 per cent likelihood of being AI-generated.
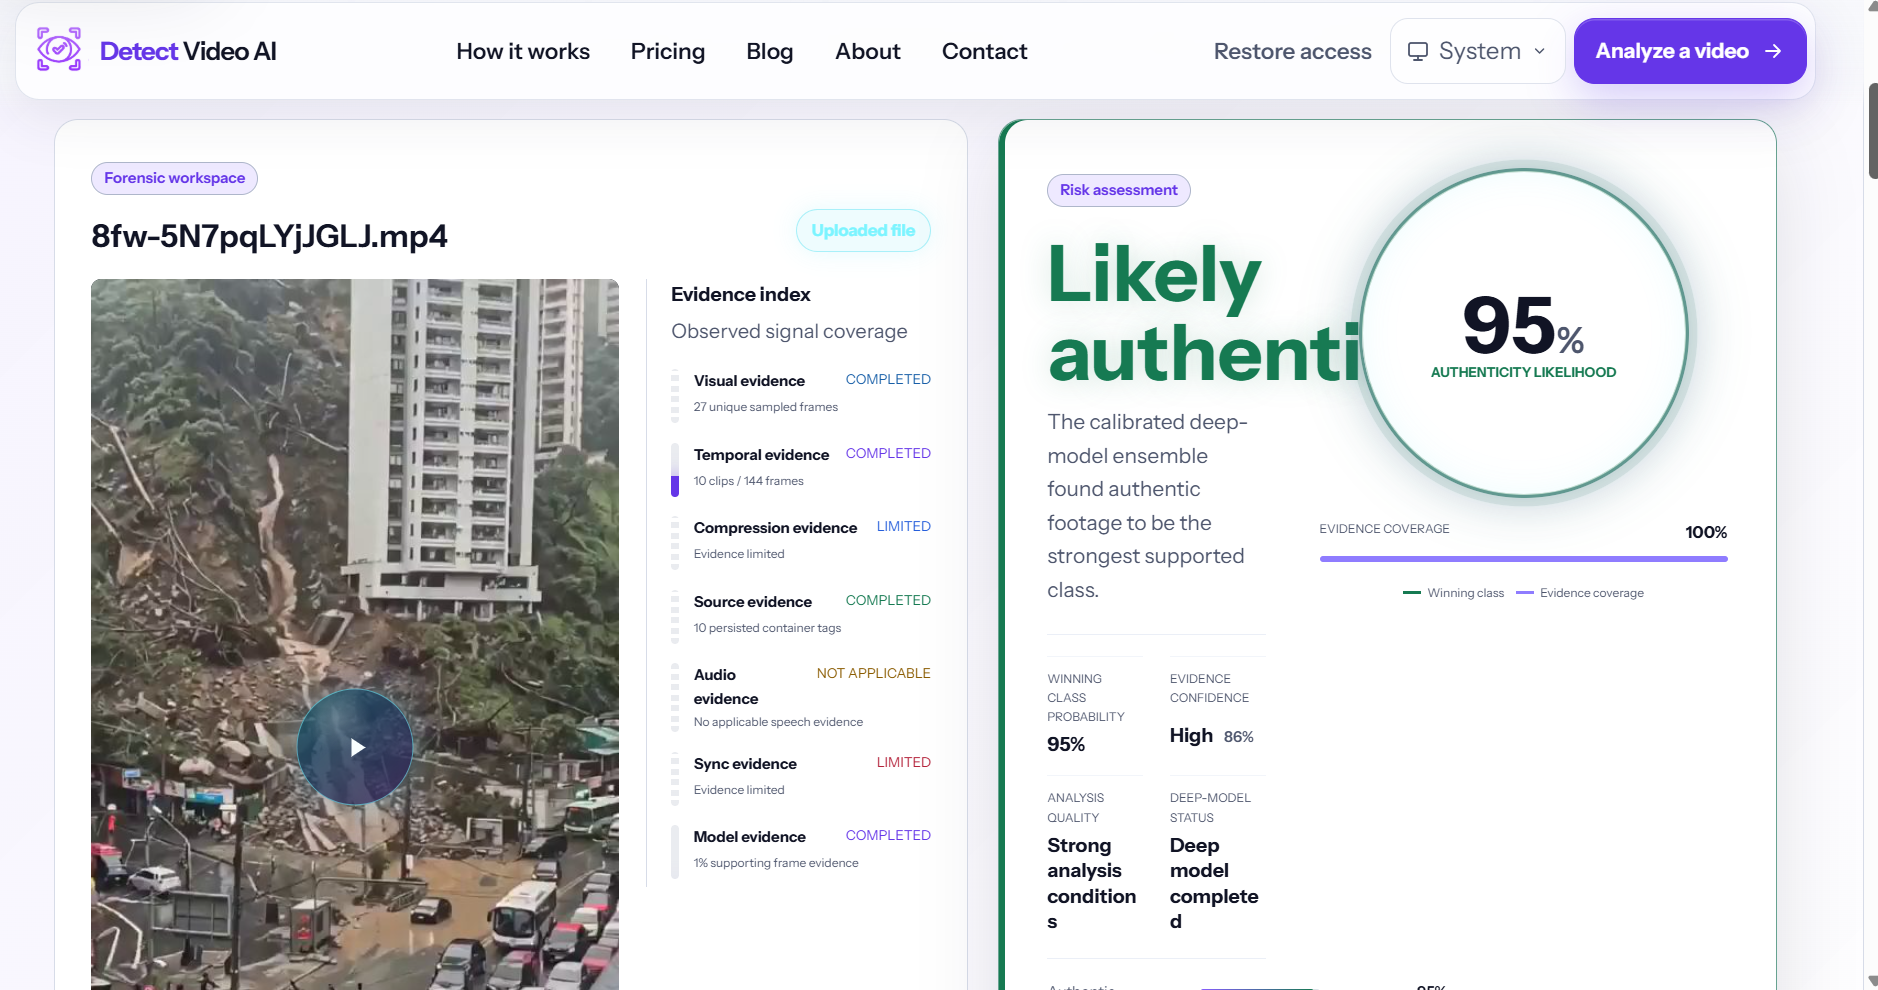
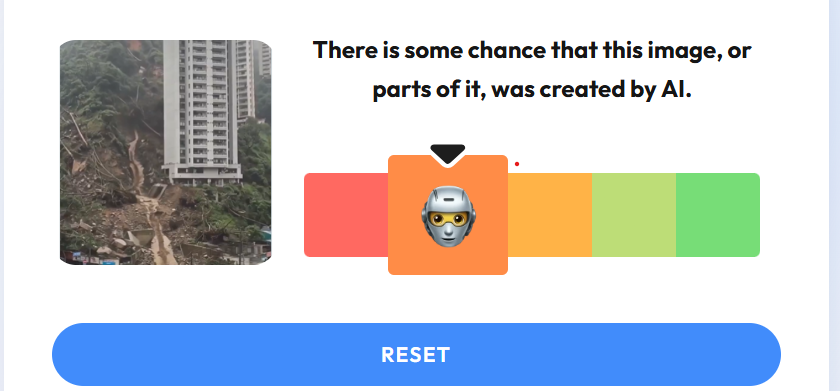
At the end of our research, we scanned the viral video using the AI detection tool WasIt AI. According to the results, the viral video was found to be AI-generated.
Conclusion
Our research found that the viral video is AI-generated and is being shared with a misleading claim.
Introduction
In the sprawling online world, trusted relationships are frequently taken advantage of by cybercriminals seeking to penetrate guarded systems. The Watering Hole Attack is one advanced method, which focuses on a user’s ecosystem by compromising the genuine sites they often use. This attack method is different from phishing or direct attacks as it quietly exploits the everyday browsing of the target to serve malicious content. The quiet and exact nature of watering hole attacks makes them prevalent amongst Advanced Persistent Threat (APT) groups, especially in conjunction with state-sponsored cyber-espionage operations.
What Qualifies as a Watering Hole Attack?
A Watering Hole Attack targets and infects a trusted website. The targeted website is one that is used by a particular organization or community, such as a specific industry sector. This type of cyberattack is analogous to the method of attack used by animals and predators waiting by the water’s edge for prey to drink. Attackers prey on their targets by injecting malicious code, such as an exploit kit or malware loader, into websites that are popular with their victims. These victims are then infected when they visit said websites unknowingly. This opens as a gateway for attackers to infiltrate corporate systems, harvest credentials, and pivot across internal networks.
How Watering Hole Attacks Unfold
The attack lifecycle usually progresses as follows:
- Reconnaissance - Attackers gather intelligence on the websites frequented by the target audience, including specialized communities, partner websites, or local news sites.
- Website Exploitation - Through the use of outdated CMS software and insecure plugins, attackers gain access to the target website and insert malicious code such as JS or iframe redirections.
- Delivery and Exploitation - The visitor’s browser executes the malicious code injected into the page. The code might include a redirection payload which sends the user to an exploit kit that checks the user’s browser, plugins, operating system, and other components for vulnerabilities.
- Infection and Persistence - The infected system malware such as RATs, keyloggers, or backdoors. These enable lateral and long-term movements within the organisation for espionage.
- Command and Control (C2) - For further instructions, additional payload delivery, and stolen data retrieval, infected devices connect to servers managed by the attackers.
Key Features of Watering Hole Attacks
- Indirect Approach: Instead of going after the main target, attackers focus on sites that the main target trusts.
- Supply-Chain-Like Impact: An infected industry portal can affect many companies at the same time.
- Low Profile: It is difficult to identify since the traffic comes from real websites.
- Advanced Customization: Exploit kits are known to specialize in making custom payloads for specific browsers or OS versions to increase the chance of success.
Why Are These Attacks Dangerous?
Worming hole attacks shift the battlefield to new grounds in cyber warfare on the web. They eliminate the need for firewalls, email shields, and other security measures because they operate on the traffic to and from real, trusted websites. When the attacks work as intended, the following consequences can be expected:
- Stealing Credentials: Including privileged accounts and VPN credentials.
- Espionage: Theft of intellectual property, defense blueprints, or government confidential information.
- Supply Chain Attacks: Resulting in a series of infections among related companies.
- Zero-Day Exploits: Including automated attacks using zero-day exploits for full damage.
Incidents of Primary Concern
The implications of watering hole attacks have been felt in the real world for quite some time. An example from 2019 reveals this, where a known VoIP firm’s site was compromised and used to spread data-stealing malware to its users. Likewise, in 2014, the Operation Snowman campaign—which seems to have a state-backed origin—attempted to infect users of a U.S. veterans’ portal in order to gain access to visitors from government, defense, and related fields. Rounding up the list, in 2021, cybercriminals attacked regional publications focusing on energy, using the publications to spread malware to company officials and engineers working on critical infrastructure, as well as to steal data from their systems. These attacks show the widespread and dangerous impact of watering hole attacks in the world of cybersecurity.
Detection Issues
Due to the following reasons, traditional approaches to security fail to detect watering hole attacks:
- Use of Authentic Websites: Attacks involving trusted and popular domains evade detection via blacklisting.
- Encrypted Traffic: Delivering payloads over HTTPS conceals malicious scripts from being inspected at the network level.
- Fileless Methods: Using in-memory execution is a modern campaign technique, and detection based on signatures is futile.
Mitigation Strategies
To effectively neutralize the threat of watering hole attacks, an organization should implement a defense-in-depth strategy that incorporates the following elements:
- Patch Management and Hardening -
- Conduct routine updates on operating systems, web browsers, and extensions to eliminate exploit opportunities.
- Either remove or reduce the use of high-risk elements such as Flash and Java, if feasible.
- Network Segmentation - Minimize lateral movement by isolating critical systems from the general user network.
- Behavioral Analytics - Implement Endpoint Detection and Response (EDR) tools to oversee unusual behaviors on processes—for example, script execution or dubious outgoing connections.
- DNS Filtering and Web Isolation - Implement DNS-layer security to deny access to known malicious domains and use browser isolation for dangerous sites.
- Threat Intelligence Integration - Track watering hole threats and campaigns for indicators of compromise (IoCs) on advisories and threat feeds.
- Multi-Layer Email and Web Security - Use web gateways integrated with dynamic content scanning, heuristic analysis, and sandboxing.
- Zero Trust Architecture - Apply least privilege access, require device attestation, and continuous authentication for accessing sensitive resources.
Incident Response Best Practices
- Forensic Analysis: Check affected endpoints for any mechanisms set up for persistence and communication with C2 servers.
- Log Review: Look through proxy, DNS, and firewall logs to detect suspicious traffic.
- Threat Hunting: Search your environment for known Indicators of Compromise (IoCs) related to recent watering hole attacks.
- User Awareness Training: Help employees understand the dangers related to visiting external industry websites and promote safe browsing practices.
The Immediate Need for Action
The adoption of cloud computing and remote working models has significantly increased the attack surface for watering hole attacks. Trust and healthcare sectors are increasingly targeted by nation-state groups and cybercrime gangs using this technique. Not taking action may lead to data leaks, legal fines, and break-ins through the supply chain, which damage the trustworthiness and operational capacity of the enterprise.
Conclusion
Watering hole attacks demonstrate how phishing attacks evolve from a broad attack to a very specific, trust-based attack. Protecting against these advanced attacks requires the zero-trust mindset, adaptive defenses, and continuous monitoring, which is multicentral security. Advanced response measures, proactive threat intelligence, and detection technologies integration enable organizations to turn this silent threat from a lurking predator to a manageable risk.
References
- https://www.fortinet.com/resources/cyberglossary/watering-hole-attack
- https://en.wikipedia.org/wiki/Watering_hole_attack
- https://www.proofpoint.com/us/threat-reference/watering-hole
- https://www.techtarget.com/searchsecurity/definition/watering-hole-attack
