
#FactCheck- Viral video of massive fire falsely linked to Israel-Iran conflict; actually from Dagestan gas pipeline blast
Executive Summary
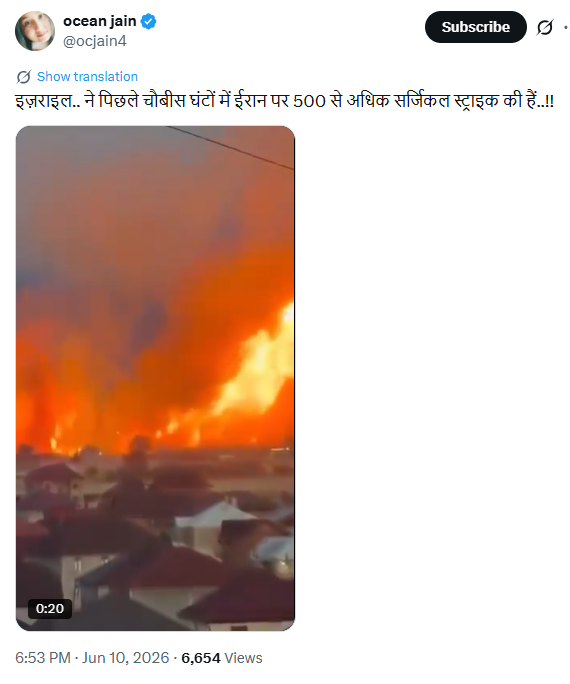
A video showing a massive fire with thick black smoke is being widely shared on social media with the claim that it depicts a recent Israeli attack on Iran. CyberPeace Research Wing research found that the claim is false. The viral video is not related to Iran or any Israel-Iran conflict. It actually shows a gas pipeline fire in Kizilyurt city of Russia’s Dagestan region.
Claim:
A video circulating on X shows a large fire breaking out at a location with thick black smoke rising. The clip is being shared with a caption claiming, “Israel has carried out more than 500 surgical strikes on Iran in the last 24 hours.” Post link: https://x.com/ocjain4/status/2064700017361985702, https://x.com/ocjain4/status/2064700017361985702
Fact Check:
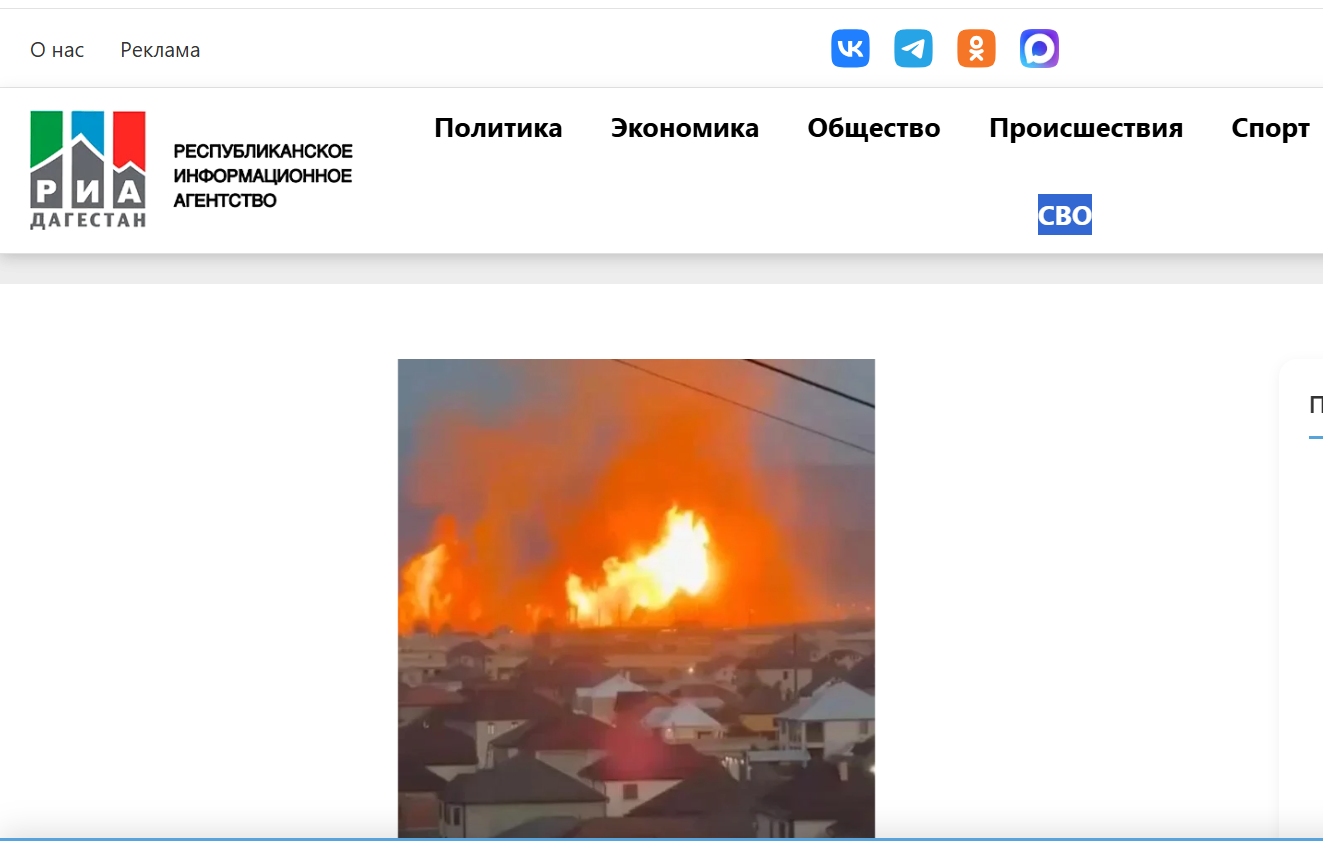
A reverse image search using keyframes from the viral video led to visuals published in a report on a Dagestan-based media outlet dated June 9. The report stated that the Russian Emergency Situations Ministry’s Dagestan department received reports of three explosions at a methane gas station.
https://riadagestan.ru/news/incidents/v_dagestane_vzorvalas_azs
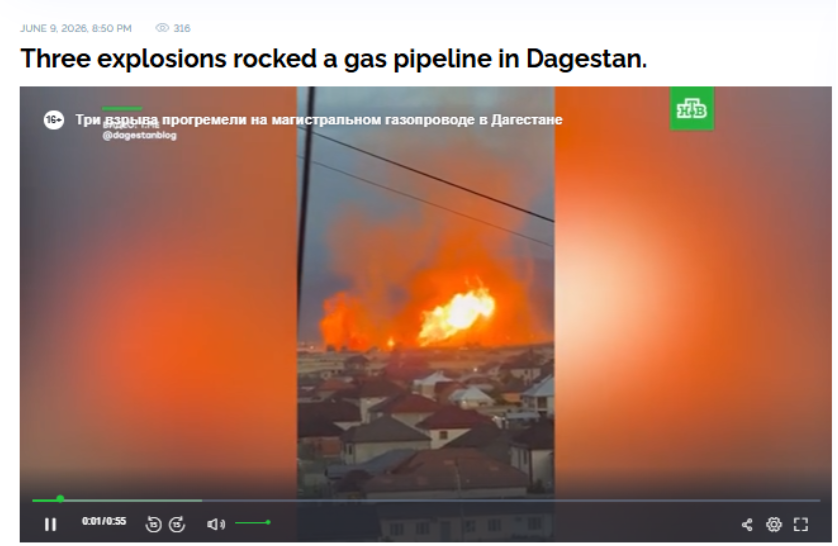
Further research found that several Russian media outlets also published the same visuals on June 9, describing them as a pipeline explosion and fire in Kizilyurt, Dagestan
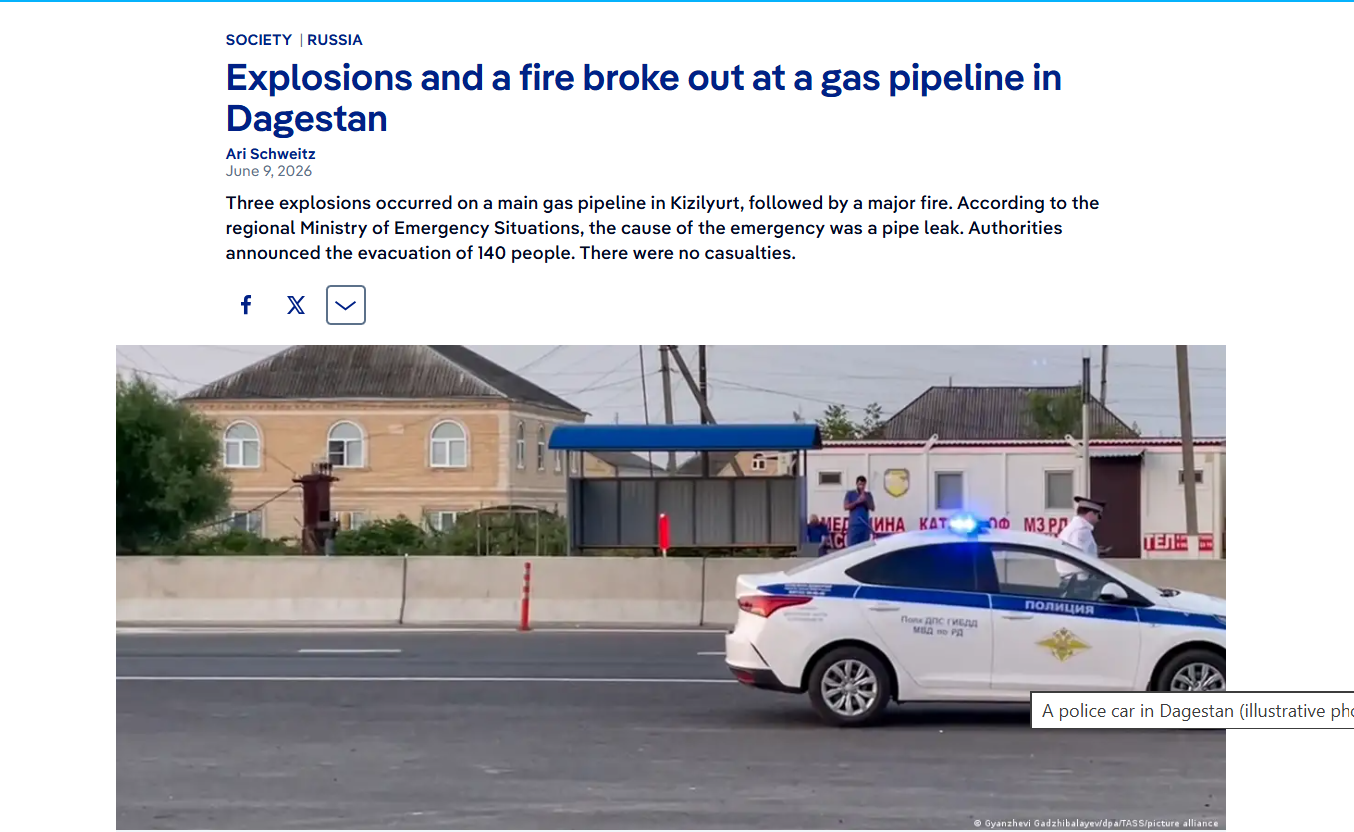
We also found a report published by DW on June 9, 2026, which stated that three explosions occurred on the Mozdok–Kazimagomed gas pipeline in Kizilyurt, Dagestan, resulting in a massive fire with flames rising up to 15 meters. According to local authorities, no casualties or injuries were reported..
https://www.dw.com/ru/na-gazoprovode-v-dagestane-progremeli-tri-vzryva-voznik-pozar/a-77481599
Conclusion:
The research clearly shows that the viral video is unrelated to the Israel-Iran conflict. It actually depicts a gas pipeline fire in Russia’s Dagestan region, which has been falsely shared as a recent Israeli strike on Iran.

Related Blogs
Introduction
Military equipment used by elite special forces is supposed to be the most tightly secured hardware a country owns, the last place anyone would expect a hidden flaw in its parts supply chain to slip through undetected. Yet that is precisely where one surfaced this August, when The Telegraph, revealed that cameras fitted to the Royal Navy's K3 Scout surveillance drones, equipment used by Britain's Royal Marines and closely associated with the Special Boat Service, the United Kingdom's elite maritime special forces unit, had been secretly transmitting signals to an internet address inside China. The United Kingdom's Ministry of Defence stripped the affected cameras of all internet connectivity the moment the transmissions were discovered, and has spent the days since insisting no sensitive data actually left the country. That distinction, between what was taken and what was exposed, is where this incident becomes genuinely worth examining.
What was actually found, and what was not
The K3 Scout is an 8.4 metre uncrewed surface vessel built by Kraken Technology Group, a British defence manufacturer based in Fareham, Hampshire, capable of reaching 55 knots and remaining at sea for up to 30 days. The Royal Navy purchased roughly 20 of these vessels under Project Beehive, a £12 million programme designed to fold autonomous systems into frontline maritime operations quickly, and the Royal Marines' Coastal Forces Squadron and 47 Commando have operated the fleet since March 2026.
A routine cyber vulnerability assessment, not an external tip off or an adversarial intrusion, is what caught the problem. Investigators found the electro-optical and infrared cameras mounted on the vessels sending what the industry calls heartbeat communications, routine signals a connected device sends simply to confirm it is powered on and functioning, to an IP address located in China. Kraken did not manufacture the cameras in house; the company sourced them from a third party supplier that had reportedly given assurances about their security, assurances the heartbeat traffic now calls directly into question.
Every source, including the UK Ministry of Defence itself, confirms the cameras were sending signals to an IP address in China. What remains unconfirmed is which company actually manufactured the compromised camera components. Neither The Telegraph nor the Ministry of Defence has publicly named the specific camera manufacturer, and an unverified social media claim allegedly identifying a Canadian supplier has since been disputed by that company, with no confirmation from official sources tying it to the incident as of now.
Crucially, the UK Ministry of Defence has been consistent on one point across every statement it has issued: its investigation found no evidence that classified information, government systems, or mission critical data were accessed, compromised, or transmitted outside the country. That is a meaningful distinction, and one worth taking at face value rather than dismissing as reflexive reassurance, since heartbeat signals by design carry connectivity status rather than payload content. But security researchers who reviewed the case have been equally consistent in noting that even metadata this thin has value to a watching adversary. Knowing when and where a piece of specialised military hardware is powered on and actively connected can itself function as a targeting signal, revealing patterns of deployment, operational tempo, and geographic presence without a single classified file ever leaving the device.
Why this particular fleet matters
The timing sharpens the concern considerably. A defence source cited in reporting on the story indicated the K3 Scout fleet was being considered as part of a future British contribution to securing freedom of navigation in the Strait of Hormuz, where the United Kingdom has already deployed a warship amid discussions of a multinational security mission. Equipment destined for a contested, strategically sensitive waterway having any unexplained data path back to a systemic rival's territory is not a detail that stays confined to a procurement footnote. The vessels were also tested during a NATO exercise in the Baltic Sea in 2025, meaning any compromised telemetry pattern could theoretically have been observed by the very alliance partners Britain was demonstrating the technology to.
The deeper issue is structural rather than incidental. Modern military hardware, however elite the unit operating it, is rarely built end to end by a single trusted manufacturer. Cameras, sensors, chipsets, and firmware routinely pass through several tiers of suppliers before reaching a finished platform, and each tier is a potential point where the chain of custody and verification can quietly break down. Kraken's own assurances about its camera supplier illustrate exactly how that failure propagates: a manufacturer can act in good faith, rely on a vendor's word, and still end up fielding compromised hardware, because the vulnerability was never introduced at the assembly stage but several layers upstream, in components whose ultimate origin was never fully audited.
CyberPeace View | A wider principle worth naming
There is a broader ethical and legal frame worth applying here, one that extends beyond ordinary cybersecurity practice into the territory international humanitarian law occupies. The core distinction that law draws, between combatants and protected persons, between military objectives and civilian life, depends fundamentally on operators having accurate, uncompromised situational awareness. A surveillance platform is not merely a piece of hardware; it is the sensory apparatus through which decisions with real consequences for human life get made in contested environments. If the integrity of that apparatus cannot be guaranteed, the reliability of everything built on top of it, target verification, proportionality assessments, distinction between combatant and civilian, is quietly weakened at its foundation. This is not a claim that the K3 Scout breach itself caused harm; the Ministry of Defence's own findings suggest it did not. It is a reminder that supply chain integrity in military sensing equipment is not simply a procurement or cybersecurity concern sitting apart from the laws of armed conflict. It sits underneath them, because a compromised sensor is, in a very real sense, a compromised judgment further down the chain.
Where India fits into this story
India has been grappling with functionally the same problem for years, and its response offers a useful point of comparison. Reporting dating back to 2023 revealed that Indian defence officials had quietly barred domestic drone manufacturers from using components sourced from countries sharing a land border with India, an unmistakable, if unstated, reference to China, citing exactly the kind of vulnerability now playing out in Britain's fleet, compromised communication functions, cameras, and operating software capable of leaking intelligence. That policy has hardened considerably since. Earlier this year, the Ministry of Defence in New Delhi finalised a stringent framework requiring that drones procured from domestic manufacturers contain no Chinese origin components or electronics at all, and at least one major drone order was placed on hold after allegations surfaced that the supplier had used Chinese parts despite those restrictions.
The commercial consequence of that caution has been real and acknowledged openly by industry figures; sourcing components outside China raises costs, given that up to 70 percent of the global drone supply chain has historically run through Chinese manufacturing. But India appears to have concluded, well ahead of this particular British incident becoming public, that the cost of auditing and diversifying a supply chain is lower than the cost of fielding compromised sensing equipment inside sensitive military operations. Indian firms have responded by building propulsion, avionics, and camera systems in house specifically to close this gap, treating component provenance as a first order design question rather than an afterthought bolted on after a breach forces the issue. Seen from that vantage point, the K3 Scout episode reads less like a uniquely British failure and more like a case study in a risk India's own defence establishment had already priced in.
Lessons from the breach
A few conclusions follow fairly directly from how this incident unfolded. First, routine cyber vulnerability assessments work, and this case is arguably an argument for doing more of them, more often, rather than a sign that current practice failed; the breach was caught internally, before any confirmed operational harm occurred. Second, a manufacturer's own assurances about a component supplier are not a substitute for independent verification, since Kraken's good faith reliance on its camera vendor's word is precisely where this vulnerability slipped through. Third, and most durably, defence procurement increasingly needs to treat component provenance as inseparable from operational security, not as a compliance checkbox to be satisfied once at contract signing. India's multi-year pivot toward auditing and localising sensitive component supply chains, imperfect and costly as it has been, points toward the direction other defence establishments will likely be pushed in as more incidents like this one surface. The K3 Scout breach did not, on the evidence available, compromise a single mission. What it compromised was the assumption that hardware assurances alone are sufficient, and that assumption was never going to survive close scrutiny forever.
References
- LBC, "Spy cameras on Navy drones used by UK's elite special forces sending signals to China as security fears grow." https://www.lbc.co.uk/article/royal-navy-spy-drones-sending-signals-to-china-5Hjdfpm_2/
- Defence Blog, "Royal Navy naval drone cameras secretly sent data to China." https://defence-blog.com/royal-navy-naval-drone-cameras-secretly-sent-data-to-china/
- The National Interest, "The Royal Navy's Spy Drones May Have Been Spying for China, Too." https://nationalinterest.org/blog/buzz/royal-navys-spy-drones-may-have-been-spying-for-china-too-sa-081026
- Kyiv Post, "UK Navy Drone Camera Components Were Secretly Communicating With China." https://www.kyivpost.com/post/82061
- The Defense News, "UK's Royal Navy K3 Scout Drone Cameras Found Sending Data to an IP Address in China." https://www.thedefensenews.com/UKs-Royal-Navy-K3-Scout-Drone-Cameras-Found-Sending-Data-to-an-IP-Address-in-China/
- The Jerusalem Post, "UK drones sent data to China, raising US, European fears on Chinese components." https://www.jpost.com/international/article-905191
- Firstpost, "UK military drones fitted with Chinese cameras found sending data to Beijing: Report." https://www.firstpost.com/world/uk-military-drones-fitted-with-chinese-cameras-found-sending-data-to-beijing-report-14037075.html
- Firstpost, "UK deploys warship to West Asia amid plans for multinational Hormuz security mission." https://www.firstpost.com/world/uk-deploys-warship-to-west-asia-amid-plans-for-multinational-hormuz-security-mission-ws-e-14009471.html
- Reuters via Inquirer.net, "India bars makers of military drones from using Chinese parts." https://newsinfo.inquirer.net/1813810/india-bars-makers-of-military-drones-from-using-chinese-parts
- The Print, "Amid concerns about use of Chinese parts in drones, Army general urges industry to be transparent." https://theprint.in/defence/amid-concerns-about-use-of-chinese-parts-in-drones-army-general-urges-industry-to-be-transparent/2305866/
- idrw.org, "India Unveils Drone Security Framework to Eliminate Chinese Components and Strengthen UAV Cyber Defences." https://idrw.org/india-unveils-drone-security-framework-to-eliminate-chinese-components-and-strengthen-uav-cyber-defences/
- The Week, "The hidden weakness in India's military drones: Zen Technologies says it has fixed the Chinese problem." https://www.theweek.in/news/defence/2026/07/09/the-hidden-weakness-in-indias-military-drones-zen-technologies-says-it-has-fixed-the-chinese-problem.html

Introduction
The United Nations (UN) has unveiled a set of principles, known as the 'Global Principles for Information Integrity', to combat the spread of online misinformation, disinformation, and hate speech. These guidelines aim to address the widespread harm caused by false information on digital platforms. The UN's Global Principles are based on five core principles: social trust and resilience, independent, free, and pluralistic media, healthy incentives, transparency and research, and public empowerment. The UN chief emphasized that the threats to information integrity are not new but are now spreading at unprecedented speeds due to digital platforms and artificial intelligence technologies.
These principles aim to enhance global cooperation in order to create a safer online environment. It was further highlighted that the spread of misinformation, disinformation, hate speech, and other risks in the information environment poses threats to democracy, human rights, climate action, and public health. This impact is intensified by the emergence of rapidly advancing Artificial Intelligence Technology (AI tech) that poses a growing threat to vulnerable groups in information environments.
The Highlights of Key Principles
- Societal Trust and Resilience: Trust in information sources and the ability and resilience to handle disruptions are critical for maintaining information integrity. Both are at risk from state and non-state actors exploiting the information ecosystem.
- Healthy Incentives: Current business models reliant on targeted advertising threaten information integrity. The complex, opaque nature of digital advertising benefits large tech companies and it requires reforms to ensure transparency and accountability.
- Public Empowerment: People require the capability to manage their online interactions, the availability of varied and trustworthy information, and the capacity to make informed decisions. Media and digital literacy are crucial, particularly for marginalized populations.
- Independent, Free, and Pluralistic Media: A free press supports democracy by fostering informed discourse, holding power accountable, and safeguarding human rights. Journalists must operate safely and freely, with access to diverse news sources.
- Transparency and research: Technology companies must be transparent about how information is propagated and how personal data is used. Research and privacy-preserving data access should be encouraged to address information integrity gaps while protecting those investigating and reporting on these issues.
Stakeholders Called for Action
Stakeholders, including technology companies, AI actors, advertisers, media, researchers, civil society organizations, state and political actors, and the UN, have been called to take action under the UN Global Principles for Information Integrity. These principles should be used to build and participate in broad cross-sector coalitions that bring together diverse expertise from civil society, academia, media, government, and the international private sector, focussing on capacity-building and meaningful youth engagement through dedicated advisory groups. Additionally, collaboration is required to develop multi-stakeholder action plans at regional, national, and local levels, engaging communities in grassroots initiatives and ensuring that youth are fully and meaningfully involved in the process.
Implementation and Monitoring
To effectively implement the UN Global Principles at large requires developing a multi-stakeholder action plan at various levels such as at the regional, national, and local levels. These plans should be informed and created by advice and counsel from an extensive range of communities including any of the grassroots initiatives having a deep understanding of regional challenges and their specific needs. Monitoring and evaluation are also regarded as essential components of the implementation process. Regular assessments of the progress, combined with the flexibility to adapt strategies as needed, will help ensure that the principles are effectively translated into practice.
Challenges and Considerations
Implementing these Global Principles of the UN will have certain challenges. The complexities that the digital landscape faces with the rapid pace of technological revamp, and alterations in the diversity of cultural and political contexts all present significant hurdles. Furthermore, the efforts to combat misinformation must be balanced with protecting fundamental rights, including the right to freedom of expression and privacy. Addressing these challenges to counter informational integrity will require continuous and ongoing collaboration with constant dialogue among stakeholders towards a commitment to innovation and continuous learning. It is also important to recognise and address the power imbalance within the information ecosystem, ensuring that all voices are heard and that any person, specifically, the marginalised communities is not cast aside.
Conclusion
The UN Global Principles for Online Misinformation and Information Integrity provide a comprehensive framework for addressing the critical challenges that are present while facing information integrity today. Advocating and promoting societal trust, healthy incentives, public empowerment, independent media, and transparency, these principles offer a passage towards a more resilient and trustworthy digital environment. The future success of these principles depends upon the collaborative efforts of all stakeholders, working together to safeguard the integrity of information for everyone.
References
- https://www.business-standard.com/world-news/un-unveils-global-principles-to-combat-online-misinformation-hate-speech-124062500317_1.html
- https://www.un.org/sustainabledevelopment/blog/2024/06/global-principles-information-integrity-launch/
- https://www.un.org/sites/un2.un.org/files/un-global-principles-for-information-integrity-en.pdf
- https://www.un.org/en/content/common-agenda-report/assets/pdf/Common_Agenda_Report_English.pdf
Introduction
How Generative Artificial Intelligence, or GenAI, is changing the employee workday is no longer limited to writing emails or debugging code, but now also includes analysing contracts, generating reports, and much more. The use of AI tools in everyday work has become commonplace, but the speed at which companies have adopted these technologies has created a new kind of risk. Unlike threats that come from an outside attacker, Shadow AI is created inside an organisation by a legitimate employee who uses unapproved AI tools to make their work more efficient and productive. In many cases, the employee is unaware of the potential security, data privacy, and compliance risks involved in using such tools to perform their job duties.
What Is Shadow AI?
Shadow AI is when individuals use AI tools at work that aren’t provided by the company, like tools or other software programs, without the knowledge or permission of the employer. Examples of shadow AI include:
- Using personal ChatGPT or other chatbot accounts to complete tasks at the office
- Uploading business-related documents to online AI technologies for analysis or summarisation.
- Copying proprietary source code into an online AI model for debugging
- Installing browser extensions and add-ons that are not approved by IT or Security personnel.
How Shadow AI Is Harmful
1. Uncontrolled Data Exposure
When employees access or input information into their user-created AI, it becomes outside the controls of the company, such as both employee personal information and any third-party personal information, private company information (such as source code or contracts), and company internal strategies. After a user enters data into their user-created AIs, the company loses all ability to monitor how that data is stored, processed, or maintained. A data leak situation exists without a malicious cyberattack. The biggest risk of a data leak is not maliciousness but rather the loss of control and governance over sensitive data.
2. Regulatory and Legal Non-Compliance
Data protection laws like GDPR, India’s Digital Personal Data Protection (DPDP) Act, HIPAA, and other relevant sectoral laws require businesses to process data in accordance with the law, to minimise the amount of data they use, and to be accountable for their actions. Shadow AI often results in the unlawful use of personal data due to a lack of a legal basis for the processing, unauthorised cross-border data transfers, and not having appropriate contractual protections in place with their AI service providers. Regulators do not see the convenience of employees as an excuse for not complying with the law, and therefore, the organisation is ultimately responsible for any violations that occur.
3. Loss of Intellectual Property
Employees frequently use AI tools to speed up tasks involving proprietary information—debugging code, reviewing contracts, or summarising internal research. When done using unapproved AI platforms, this can expose trade secrets and intellectual property, eroding competitive advantage and creating long-term business risk.
Real-Life Example: Samsung’s ChatGPT Data Leak
In 2023, a case study exemplifying the Shadow AI risk occurred when Samsung Electronics placed a temporary ban on employee access to ChatGPT and other AI tools after reports from engineers revealed they were using ChatGPT to create debugging processes for internal source code and to summarise meeting notes. Consequently, confidential source code related to semiconductors was inadvertently uploaded onto a public AI platform. While there were no known incursions into the company’s system due to this incident, Samsung faced a significant challenge: once sensitive information is input into a public AI tool, it exists on external servers that are outside of the company’s purview or control.
As a result of this incident, Samsung restricted employee use of ChatGPT on corporate devices, issued a series of internal communications prohibiting the sharing of corporate data with public AI tools, and increased the urgency of their discussions regarding the adoption of secure, enterprise-level AI (artificial intelligence) solutions.
What Organisations Are Doing Today
Many organisations respond to Shadow AI risk by:
- Blocking access at the network level
- Circulating warning emails or policies
While these actions may reduce immediate exposure, they fail to address the root cause: employees still need AI to perform their jobs efficiently. As a result, bans often push AI usage underground, increasing Shadow AI rather than eliminating it.
Why Blocking AI Does Not Work—Governance Does
History has demonstrated that prohibition does not work - we see this when trying to block access to cloud storage, instant messaging and collaboration tools. Employees are forced to use personal devices and/or accounts when their employers block AI, which means employers do not have real-time visibility into how their employees are using these technologies, and creates friction with the security and compliance team as they try to enforce the types of tools their employees can use. Prohibiting AI adoption will not stop it from being adopted; it will just create a challenge for employers regarding how safe and responsible it is. The challenge for effective organisations is therefore to shift from denial and develop governance-first AI strategies aimed at controlling data usage, protection and security, rather than merely restricting access to a list of specific tools.
Shadow AI: A Silent Legal Liability Under the GDPR
Shadow AI isn't a problem for the Information Technology Department; it is a failure of Governance, Compliance and Law. By using AI tools that have not been approved as a result, the organisation processes personal data without a lawful basis (Article 6 of the General Data Protection Regulation (GDPR)), repurposes data for use beyond its original intent and in breach of the Purpose Limitation (Article 5(1)(b)), and routinely exceeds necessity and in breach of Data Minimisation (Article 5(1)(c)). The outcome of these actions is the use of tools that involve International Data Transfers Without Authorisation and are therefore in breach of Chapter V, and violate Article 32 because there are no enforceable safeguards in place. Most significantly, the failure to demonstrate Oversight, Logging and Control under Articles 5(2) and 24 constitutes a failure in Accountability. Therefore, from a Regulatory perspective, Shadow AI is not accidental and is not defensible.
The Right Solution: Secure and Governed AI Adoption
1. Provide Approved AI Tools
Employers have an obligation to supply business-approved AI technology for helping workers to be productive while maintaining maximum protections, like storing data separately and not using employees' data for training a model; defining how long data is kept, and the rules around deleting that data. When employees are provided with verified and secure AI options that align with their work processes, they will rely significantly less on Shadow AI.
2. Enforce Zero-Trust Data Access
The governance of AI systems must follow the principles of "zero trust," granting access to data only through the principle of "least privilege," which means that data access will only be allowed by the system user, and providing continuous verification of user-identity and context; this supports and helps establish context-aware controls to monitor and track all user activities, which will be especially important as agent-like AI systems become increasingly autonomous and are capable of operating at machine-speed where even small errors in configuration, will result in rapid and large expose to data.
3. Apply DLP and Audit Logging
It is important to have robust data loss prevention measures in place to protect sensitive data that is sent outside an organisation. The first end user or machine that accesses the data should be detailed in a comprehensive audit log that indicates when and how the data is accessed. In combination with other controls, these measures create accountability, comply with regulations, and assist with appropriately detecting and responding to incidents.
4. Maintain Visibility Across AI, Cloud, and SaaS
Security teams need unified visibility across AI tools, personal cloud applications, and SaaS platforms. Risks move across systems, and controls must follow the data wherever it flows.
Conclusion
This new threat exposes an organisation to the risk of data loss through leaks, regulatory fines, liability for the loss of intellectual property, and reputational damage, all of which can occur without any intent to cause harm. The way forward is not to block AI, but to adopt a clear framework built on governance, visibility, and secure enablement. This approach allows organisations to use AI with confidence, while ensuring trust, accountability, and effective oversight to protect data and support AI in reaching its full transformative potential. AI use is encouraged, but it must be done responsibly, ethically, and securely.
References
- https://bronson.ai/resources/shadow-ai/
- https://www.varonis.com/blog/shadow-ai
- https://www.waymakeros.com/learn/gdpr-hipaa-shadow-ai-compliance-nightmare
- https://www.forbes.com/sites/siladityaray/2023/05/02/samsung-bans-chatgpt-and-other-chatbots-for-employees-after-sensitive-code-leak/
- https://www.usatoday.com/story/special/contributor-content/2025/05/23/shadow-ai-the-hidden-risk-in-todays-workplace/83822081007
