
#FactCheck -AI-Generated Video Falsely Shared as Leopard Dragging Passenger From Moving Train
Executive Summary
A video is being widely shared on social media claiming that a leopard dragged away a passenger from a moving train. Several users are circulating the clip as a real incident. However, CyberPeace Research Wing research found the claim to be false. Our research revealed that the viral video is not real and was generated using Artificial Intelligence (AI).
Claim
An X user (formerly Twitter) shared the viral clip with the caption:“A leopard snatched a man from a moving train.”The link, archived version, and screenshot of the post are provided below.

Fact Check
On closely examining the video, several visual inconsistencies were noticed. The leopard’s body appears distorted at multiple points in the clip. In some frames, parts of the animal’s body seem to merge into the background, while in others, sections appear incomplete or disappear entirely — something not typically seen in authentic footage. In the final part of the video, where the leopard is allegedly shown attacking a passenger, the person’s hands, limbs, and body also appear blurred and distorted. Additionally, unusual and selective blurring can be observed throughout the video, indicating possible editing or AI manipulation.
To further verify the clip, we scanned the viral video using the AI detection tool Sightengine. According to the results, the video showed an 86 percent probability of being AI-generated.

As part of the research , we also analysed the clip using another AI detection platform, UndetectableTM AI, which likewise indicated that the viral video was AI-generated.

Conclusion
Our research found that the viral video claiming to show a leopard dragging away a passenger from a moving train is fake. The clip is AI-generated and does not depict a real incident.

Related Blogs
Executive Summary
A video showing protesters and smoke rising from an area is being widely shared on social media with the claim that it depicts violent protests in Nepal over demands to declare the country a Hindu nation. The CyberPeace Research Wing found that the claim is false. The viral video is actually from the Gen-Z protests in Nepal in September 2025 and is unrelated to the recent demands for a Hindu state.
Claim
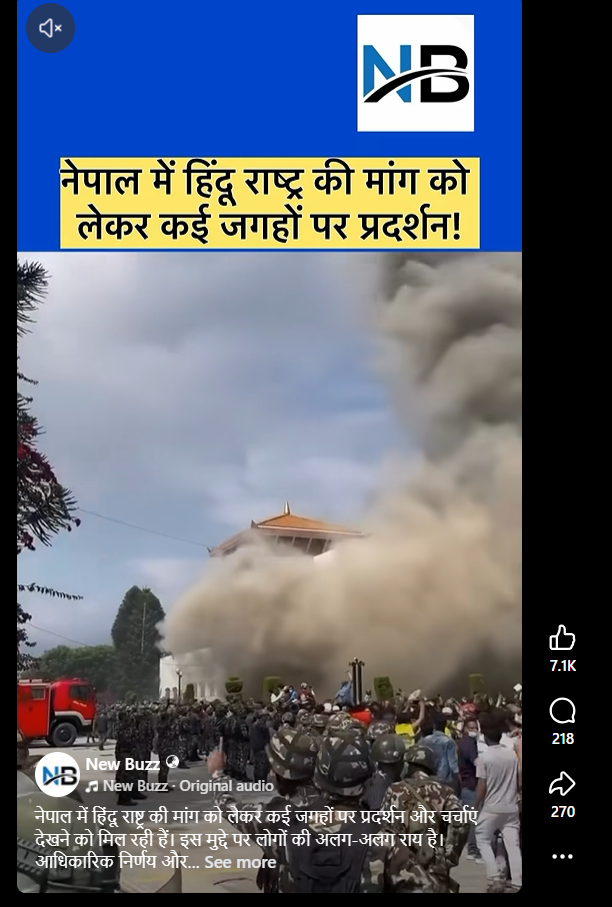
Following reports of communal violence in Nepal in July 2026, an organisation submitted a memorandum to Home Minister Soodan Gurung, calling for discussions on declaring Nepal a Hindu nation. Against this backdrop, a video showing protesters and smoke has gone viral on social media. A Facebook user, ‘New Buzz’, shared the video on August 5, 2026, with the caption:
"Protests and discussions are being seen in several places in Nepal over the demand for a Hindu nation. People have different views on this issue. One should reach a conclusion only on the basis of official decisions and credible information."
https://www.facebook.com/reel/27872198842449234
https://ghostarchive.org/archive/P89Qo
FactCheck:
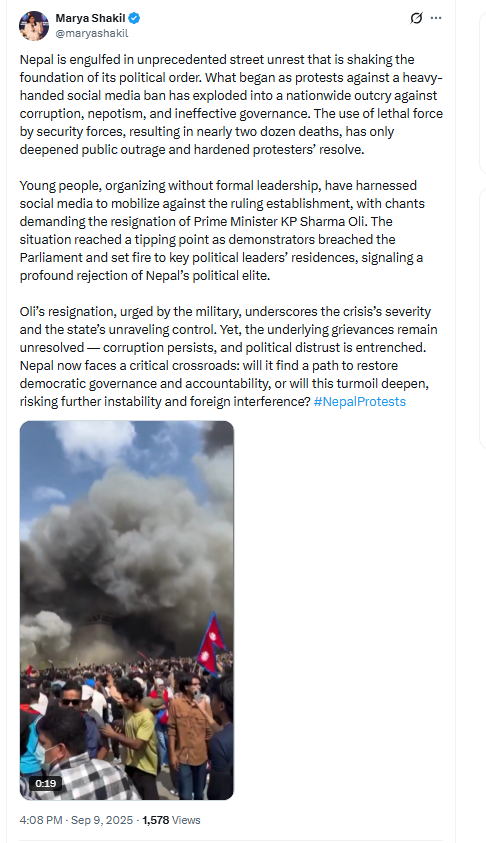
To verify the claim, we extracted keyframes from the viral video and conducted a reverse image search using Google Lens. The search led us to a post by India Today journalist Marya Shakil on X, dated September 9, 2025. She had shared the same video and identified it as footage from the Gen-Z protests in Nepal against corruption
https://x.com/maryashakil/status/1965364156992782723?s=20
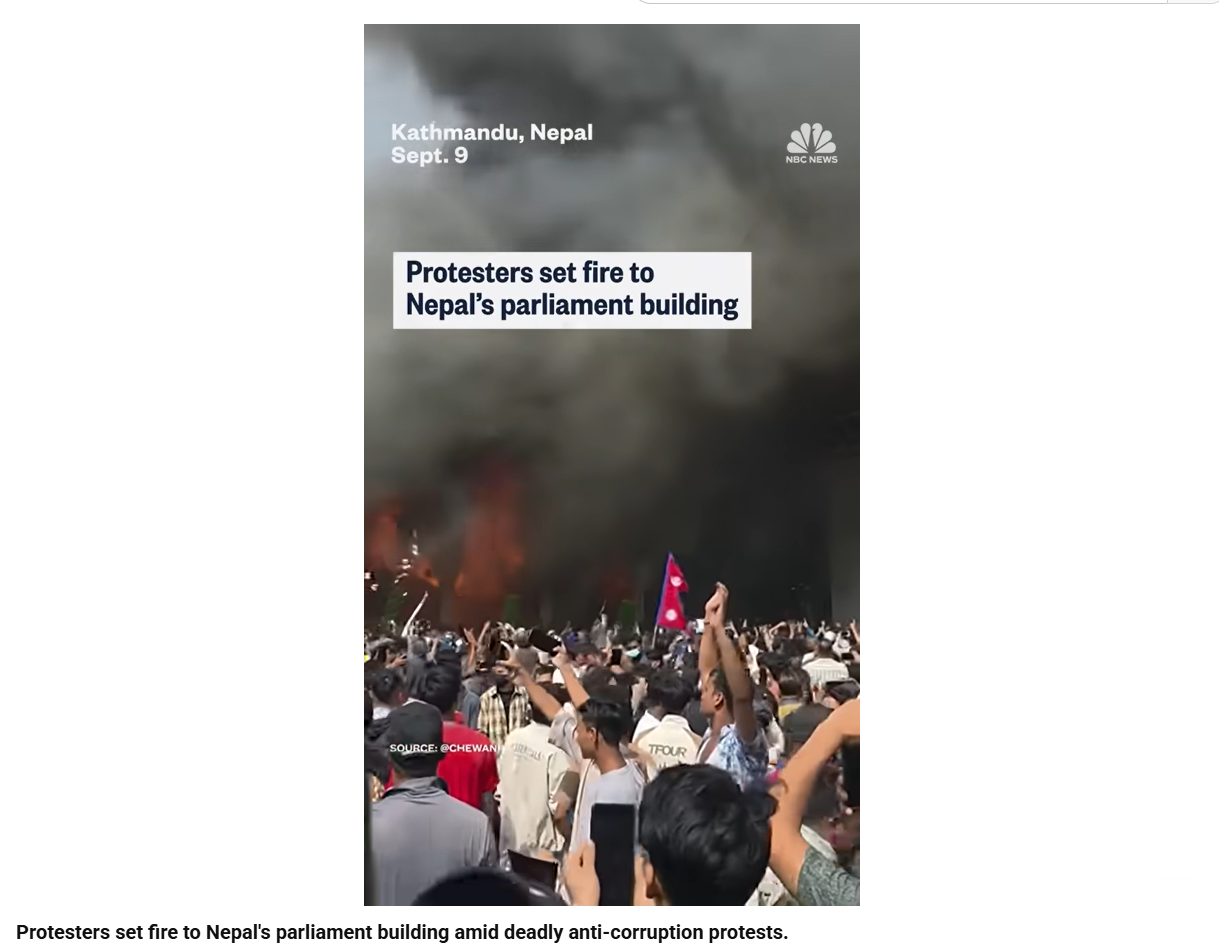
We also found a related news report on the NBC News YouTube channel, published on September 9, 2025. The video report also identified the footage as being from the protests in Nepal..
https://www.youtube.com/watch?v=PXnhHoH0XKE
Conclusion
The viral claim is false. The video being shared as footage of violent protests in Nepal over the demand for a Hindu nation actually dates back to the September 2025 Gen-Z protests against corruption. Although an organisation submitted a 13-point memorandum to Nepal's Home Minister following the July 2026 communal violence, including a demand for discussions on declaring Nepal a Hindu nation, the viral video is unrelated to that development.
Introduction
Picture this - you wake up one morning, check your phone, and discover that a fraudster has emptied your bank account overnight. Your first instinct is to call someone, anyone, who can stop the money from vanishing for good. For millions of Indians today, that number is 1930, the national cybercrime helpline. At a high-level review meeting in June 2026, Union Home Minister Amit Shah directed that the helpline undergo a comprehensive revamp, one that brings in artificial intelligence, multilingual support, and a stronger framework for resolving victim grievances. This is not a minor patch. It is a signal that India wants to treat cybercrime response as a serious governance priority rather than an administrative checkbox.
The Evolution of 1930: From a Pilot Number to National Infrastructure
The helpline’s origin lies in 155260 (Old helpline no.), launched in 2020 by the Indian Cyber Crime Coordination Centre (I4C) with the Reserve Bank of India and the banking sector, built specifically to intercept financial fraud before funds could be laundered across accounts. In 2021, it was renamed 1930 to make the number easier for citizens to recall under stress, a small but telling decision: a security architecture only works if people can remember it during a crisis. It was paired with the National Cybercrime Reporting Portal, launched in August 2019 to strengthen reporting and response mechanisms nationwide, which was later expanded to cover all categories of cybercrime after starting out limited to content-related offences. Over five years, state police forces extended 1930 into round-the-clock, multi-line operations and linked it to local cyber cells, turning a central scheme into genuinely federated infrastructure. The numbers now justify that investment: more than ₹7,000 crore has been saved nationally through the Citizen Financial Cyber Fraud Reporting and Management System, while Mumbai alone blocked or recovered nearly ₹202 crore for victims in 2025 through the helpline. What began as a pilot number has become a core node in India’s financial security architecture.
AI and Multilingual Support as a Citizen-Centric Governance Shift
What makes Shah’s directive significant is not the technology itself but the design philosophy it embeds. The instruction to integrate AI and multilingual support is explicitly aimed at removing language barriers and enabling faster, more efficient complaint registration across the country. For a country with no single dominant spoken language, this is not a feature addition; it is a recognition that uniform, English-or-Hindi-first service design has been quietly excluding the citizens most vulnerable to fraud. Multilingual access addresses a long-standing gap by allowing citizens from non-Hindi-speaking states to report cybercrime in their own languages, significantly broadening reach. This marks a shift away from treating digital governance as a one-size-fits-all portal and toward treating it as a service obligation that adapts to the citizen rather than the reverse, a principle with implications well beyond cybercrime reporting.
Routing, Tracking and Escalation: Engineering Accountability into Redressal
The proposed reforms move beyond the front-end call experience into the architecture of follow-through. AI integration is expected to improve call routing, enable faster identification of fraud patterns, and assist real-time coordination between central and state law enforcement agencies. This matters because cyber fraud is intrinsically cross-jurisdictional: a victim in one state is often defrauded through an account opened in another. Shah directed central agencies to work closely with state governments to ensure that every call received on the helpline is followed through to its logical conclusion — language that, in policy terms, is an attempt to convert a complaint-registration system into a complaint-resolution system. Intelligent routing and case tracking, if implemented well, replace ad hoc coordination between states with a traceable escalation mechanism, the missing link that has historically allowed cases to stall after the first call was logged.
Frozen Accounts and the Procedural Burden on Victims
No part of the revamp is more consequential for ordinary victims than the directive on bank account freezes. The problem is compounded when a cybercrime complaint is registered in one state while the frozen account sits in another, leaving legitimate account holders, sometimes innocent third parties, locked out of their own funds for weeks. Shah directed that grievances arising from the freezing of bank accounts linked to financial frauds be addressed promptly, an instruction that responds directly to a problem now before the courts Judicial scrutiny on this exact question is intensifying: the Karnataka High Court recently held that banks cannot freeze an account completely when investigating agencies have directed only a partial freeze limited to a specified amount. A national, technology-backed mechanism for resolving such freezes would convert a recurring source of citizen grievance into a procedural safeguard, addressing one of the most cited failures of the existing system.
Reading the Reforms Within India’s Broader Cyber Resilience Strategy
Positioned within India’s wider digital governance trajectory, the 1930 revamp fits a recognisable pattern: build foundational infrastructure first, then layer intelligence and personalisation onto it once adoption is proven. The same logic shaped Aadhaar, UPI and the Digital India programme more broadly. India has seen a sharp rise in digital financial fraud, investment scams, sextortion and phishing attacks in recent years, and the Ministry of Home Affairs’ response, expanding I4C, building specialised cybercrime units, and now investing in AI-led citizen interfaces, signals that cyber resilience is being treated less as a law-enforcement afterthought and more as a core pillar of financial-system integrity, alongside RBI and NPCI-led safeguards.
Will These Reforms Strengthen Trust?
The credibility of any reform lies in implementation, not announcement. Public commentary on the revamp captures this tension well: citizens have welcomed the intent while noting that earlier promises of coordination did not always translate into resolved cases, and that awareness gaps in rural India persist regardless of how sophisticated the backend becomes The 1930 revamp will be judged not by how quickly complaints are registered, an area where India already performs reasonably, but by how reliably they are closed. If AI-driven routing and a genuine national escalation mechanism reduce the gap between complaint and resolution, particularly on account freezes, the reform will have done more for citizen trust than any awareness campaign could. If implementation falters at the state-bank coordination layer, the technology will simply make an old problem move faster without making it smaller.
Conclusion
The story of 1930 is the story of Indian digital governance maturing in real time: from a hastily assembled fraud helpline to a piece of national financial security infrastructure now being re-engineered for scale, language diversity and accountability. Amit Shah’s directive should be read not as a single announcement but as an acknowledgment that citizen-facing systems must keep pace with the sophistication of the threats they are built to counter. Whether this becomes a genuine trust-building reform or another well-intentioned upgrade depends entirely on what happens after the press statement — in LEA’s call centres, bank back-offices and state coordination desks across the country.
References
- https://www.republicworld.com/india/amit-shah-orders-major-overhaul-of-national-cybercrime-helpline-1930-calls-for-ai-upgrade-2026-06-17-128739
- https://the420.in/amit-shah-national-cybercrime-helpline-revamp/
- https://inc42.com/buzz/home-minister-amit-shah-calls-for-ai-led-revamp-of-national-cybercrime-helpline/
- https://thenewsmill.com/2026/06/amit-shah-directs-ai-upgrade-for-national-cybercrime-helpline-1930/
- https://risingkashmir.com/national/amit-shah-reviews-national-cybercrime-helpline-1930-calls-for-ai-upgrade-12048424
- https://www.newkerala.com/news/a/amit-shah-reviews-national-cybercrime-helpline-1930-calls-929.htm
- https://simple.wikipedia.org/wiki/1930_(Indian_Cybercrime_Helpline)
- https://www.newsonair.gov.in/over-rs-7000-crore-saved-through-citizen-financial-cyber-fraud-reporting-and-management-system
- https://the420.in/mumbai-1930-cyber-helpline-saves-202-crore-2025

Introduction
The Government of India has initiated a cybercrime crackdown that has resulted in the blocking of 781,000 SIM cards and 208,469 IMEI (International Mobile Equipment Identity) numbers that are associated with digital fraud as of February 2025. This data was released as a written response by the Union Minister of State for Home Affairs, Bandi Sanjay Kumar, with respect to a query presented in the Lok Sabha. A significant jump from the 669,000 SIM cards blocked in the past year, efforts aimed at combating digital fraud are in full swing, considering the increasing cases. The Indian Cyber Crime Coordination Centre (I4C) is proactively blocking other platform accounts found suspicious, such as WhatsApp Accounts (83,668) and Skype IDs (3,962) on its part, aiding in eliminating identified threat actors.
Increasing Digital Fraud And The Current Combative Measures
According to the data tabled by the Ministry of Finance in the Rajya Sabha, the first 10 months of the Financial year 2024-2025 have recorded around 2.4 million incidents covering an amount of Rs. 4,245 crore involving cases of digital Financial Fraud cases. Apart from the evident financial loss, such incidents also take an emotional toll as people are targeted regardless of their background and age, leaving everyone equally vulnerable. To address this growing problem, various government departments have dedicated measures to combat and reduce such incidents. Some of the notable initiatives/steps are as follows:
- The Citizen Financial Cyber Fraud Reporting and Management System- This includes reporting Cybercrimes through the nationwide toll-free (1930) number and registration on the National Cyber Crime Reporting Portal. On being a victim of digital fraud, one can call the toll-free number, describing details of the incident, which would further help in the investigation. After reporting the incident, the complainant receives a generated login ID/acknowledgement number that they can use for further reference.
- International Incoming Spoofed Calls Prevention System- This is a mechanism developed to counter fraudulent calls that appear to originate from within India but are actually made from international locations. This system prevents the misuse of the Calling Line Identity (CLI), which is manipulated to deceive recipients in order to carry out financial crimes like digital arrests, among other things. Coordinating with the Department of Telecommunication (DoT), private telecommunication service providers (TSPs) are being encouraged to check with their ILD (International Long-Distance) network as a measure. Airtel has recently started categorising such numbers as International numbers on their part.
- Chakshu Facility at Sanchar Saathi platform- A citizen-centric initiative, created by the Department of Telecommunications, to empower mobile subscribers. It focuses on reporting unsolicited commercial communication (spam messages) and reporting suspected fraudulent communication. (https://sancharsaathi.gov.in/).
- Aadhaar-based verification of SIM cards- A directive issued by the Prime Minister's Office to the Department of Telecommunications mandates an Aadhaar-based biometric verification for the issuance of new SIM cards. This has been done so in an effort to prevent fraud and cybercrime through mobile connections obtained using fake documents. Legal action against non-compliant retailers in the form of FIRs is also being taken.
On the part of the public, awareness of the following steps could encourage them on how to deal with such situations:
- Awareness regarding types of crimes and the tell-tale signs of the modus operandi of a criminal: A general awareness and a cautionary approach to how such crimes take place could help better prepare and respond to such malicious scams. Some important signs on the part of the offender include pressuring the victim into immediate action, insistence on video calls, and the threat of arrest in case of non-compliance. It is also important to note that no official authority, in any legal capacity, allows for enabling a digital/online arrest.
- Knowing the support channels: Awareness regarding reporting mechanisms and cyber safety hygiene tips can help in building cyber resilience amongst netizens.
Conclusion
As cybercrooks continue to find new ways of duping people of their hard-earned money, both government and netizens must make efforts to combat such crimes and increase awareness on both ends (systematic and public). Increasing developments in AI, deepfakes, and other technology often render the public inept at assessing the veracity of the source, making them susceptible to such crime. A cautionary yet proactive approach is need of the hour.
References
- https://mobileidworld.com/india-blocks-781000-sim-cards-in-major-cybercrime-crackdown/
- https://www.storyboard18.com/how-it-works/over-83k-whatsapp-accounts-used-for-digital-arrest-blocked-home-ministry-60292.htm
- https://www.business-standard.com/finance/news/digital-financial-frauds-touch-rs-4-245-crore-in-the-apr-jan-period-of-fy25-125032001214_1.html
- https://www.business-standard.com/india-news/govt-blocked-781k-sims-3k-skype-ids-83k-whatsapp-accounts-till-feb-125032500965_1.html
- https://pib.gov.in/PressReleasePage.aspx?PRID=2042130
- https://mobileidworld.com/india-mandates-aadhaar-biometric-verification-for-new-sim-cards-to-combat-fraud/
- https://pib.gov.in/PressReleaseIframePage.aspx?PRID=2067113
