
#FactCheck - Fake Image Claiming Patanjali selling Beef Biryani Recipe mix is Misleading
Executive Summary:
A photo that has gone viral on social media alleges that the Indian company Patanjali founded by Yoga Guru Baba Ramdev is selling a product called “Recipe Mix for Beef Biryani”. The image incorporates Ramdev’s name in its promotional package. However, upon looking into the matter, CyberPeace Research Team revealed that the viral image is not genuine. The original image was altered and it has been wrongly claimed which does not even exist. Patanjali is an Indian brand designed for vegetarians and an intervention of Ayurveda. For that reason, the image in context is fake and misleading.

Claims:
An image circulating on social media shows Patanjali selling "Recipe Mix for Beef Biryani”.

Fact Check:
Upon receiving the viral image, the CyberPeace Research Team immediately conducted an in-depth investigation. A reverse image search revealed that the viral image was taken from an unrelated context and digitally altered to be associated with the fabricated packaging of "National Recipe Mix for Biryani".

The analysis of the image confirmed signs of manipulation. Patanjali, a well-established Indian brand known for its vegetarian products, has no record of producing or promoting a product called “Recipe mix for Beef Biryani”. We also found a similar image with the product specified as “National Biryani” in another online store.

Comparing both photos, we found that there are several differences.
Further examination of Patanjali's product catalog and public information verified that this viral image is part of a deliberate attempt to spread misinformation, likely to damage the reputation of the brand and its founder. The entire claim is based on a falsified image aimed at provoking controversy, and therefore, is categorically false.
Conclusions:
The viral image associating Patanjali and Baba Ramdev with "Recipe mix for Beef Biryani" is entirely fake. This image was deliberately manipulated to spread false information and damage the brand’s reputation. Social media users are encouraged to fact-check before sharing any such claims, as the spread of misinformation can have significant consequences. The CyberPeace Research Team emphasizes the importance of verifying information before circulating it to avoid spreading false narratives.
- Claim: Patanjali and Baba Ramdev endorse "Recipe mix for Beef Biryani"
- Claimed on: X
- Fact Check: Fake & Misleading

Related Blogs
Executive Summary
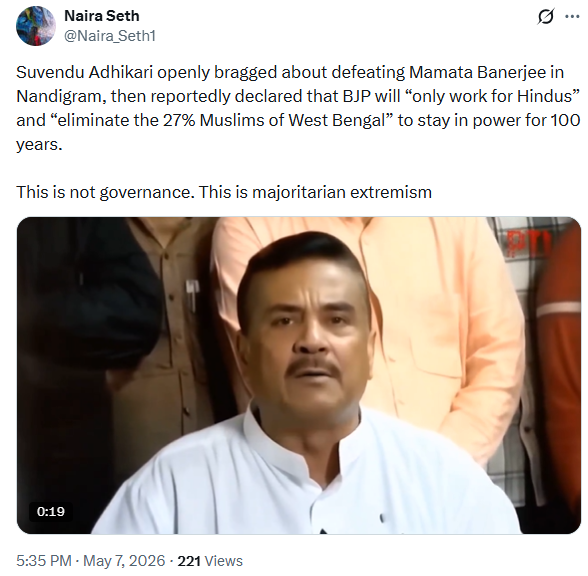
A video circulating on social media falsely claims to show West Bengal leader Suvendu Adhikari making inflammatory and communal remarks. In the viral clip, he is allegedly heard saying that if elected, his party would “work only for Hindus” and “eliminate the 27% Muslim population in West Bengal,” while also claiming that the BJP would remain in power for over 100 years. CyberPeace Research Wing research found that the viral video, which allegedly shows West Bengal leader Suvendu Adhikari making a statement about eliminating the Muslim population in West Bengal to ensure long-term BJP rule, is AI-generated and not real.
Claim
An X user (@Naira_Seth1) shared the clip alleging it reflects “majoritarian extremism disguised as politics,” suggesting that Suvendu Adhikari made communally charged and unconstitutional statements.
Fact Check
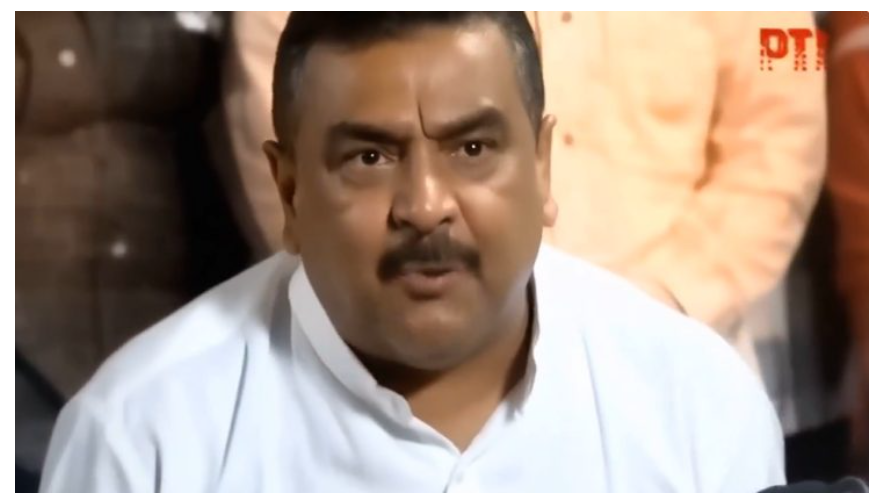
A detailed analysis of the video shows clear signs of manipulation. The person appearing in the latter part of the clip does not match Suvendu Adhikari.
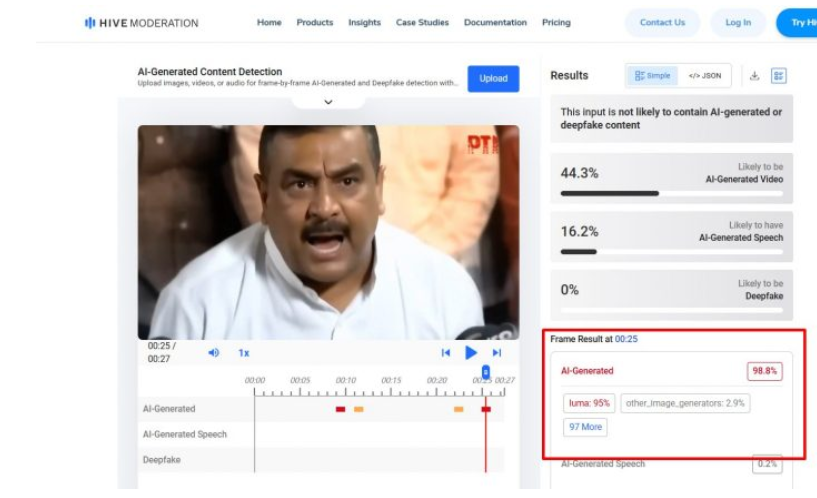
Additionally, the video was tested using an AI detection tool (Hive Moderation), which indicated a 98.8% probability of AI-generated content, particularly around the 0:25 timestamp.
Further verification through reverse image search of key frames led to an original press byte of Suvendu Adhikari posted by PTI News on May 6. In that authentic video, he is seen speaking about taking strict legal action against criminals, with no mention of any religious community or communal statements.
https://x.com/PTI_News/status/2052020784152068114?s=20

Conclusion
The viral video allegedly showing Suvendu Adhikari making communal remarks is AI-generated and misleading. The original footage confirms that no such statements were made, and the clip has been digitally manipulated to spread misinformation.
On 25 September 2026, at UN Headquarters in New York, External Affairs Minister S. Jaishankar signed the United Nations Convention against Cybercrime on the sidelines of the 81st session of the UN General Assembly, calling it a step that "strengthens international cooperation for a safer digital future."
The signature places India among the growing list of nations joining what is officially the first comprehensive global treaty dedicated to cybercrime. What Jaishankar's brief statement did not mention is that this same treaty has spent the better part of three years drawing sustained, detailed criticism from human rights organisations, technology companies, and digital rights groups, who argue it risks becoming a tool for surveillance rather than a tool against crime.
A Conversation CyberPeace Has Been Having for Years
For CyberPeace, India’s signature is not an isolated development but the latest chapter in a conversation the organisation has been following since the Convention was still being negotiated.
In December 2024, CyberPeace published its analysis of the emerging UN Convention against Cybercrime, examining its objectives, proposed offences, mechanisms for international cooperation, electronic evidence and its relationship with the Budapest Convention. The analysis also highlighted an important principle embedded in the emerging framework: that stronger cybercrime enforcement must operate alongside due process, privacy and human-rights safeguards.
That conversation continued in October 2025, when CyberPeace published The Digital Leviathan: The UN Cybercrime Treaty and the Future of Global Governance. The piece examined the Convention not merely as a cybercrime instrument, but as part of a larger evolution in global digital governance, particularly around cross-border evidence, international cooperation and the changing architecture of cyber sovereignty.
And in August 2026, CyberPeace returned to the question from the operational side in The World Is Rewriting the Rules Against Cyber-Enabled Transnational Crime. The analysis placed the Convention alongside the wider international response to transnational cyber-enabled crime, including scam networks, financial fraud and increasingly sophisticated criminal ecosystems that operate across multiple jurisdictions.
What the Convention actually is
The treaty's full, formal title is unusually descriptive for a UN instrument: the United Nations Convention against Cybercrime, Strengthening International Cooperation for Combating Certain Crimes Committed by Means of Information and Communications Technology Systems and for the Sharing of Evidence in Electronic Form of Serious Crimes. The UN General Assembly adopted it unanimously on 24 December 2024, following three years of negotiation, and it opened for signature at a ceremony in Hanoi, Vietnam, in October 2025. It will remain open for signature at UN Headquarters through 31 December 2026, and comes into force ninety days after the fortieth country ratifies it.
At its core, the Convention gives signatory states a shared legal framework for two things: preventing and prosecuting offences committed through digital systems, and cooperating across borders when evidence, offenders, or victims of a crime are scattered across multiple jurisdictions, a structural problem that has long frustrated cybercrime investigations. It also includes provisions specifically addressing the recovery of criminal proceeds, adding a financial dimension that lets states cooperate not just on prosecuting offenders but on tracing and reclaiming stolen money that has moved across borders, often through mule accounts and shell transactions designed to outrun any single country's jurisdiction.
Why India signed, in its own words
Jaishankar's public reasoning was concise. Cybercrime, in the government's framing, does not respect national boundaries, and India's own cybercrime caseload, spanning cross-border financial fraud, romance scams, and organised online extortion networks often operating from outside India's borders, has repeatedly run into exactly the jurisdictional walls this Convention is designed to lower. Prof. Triveni Singh, a well known cybercrime expert and former IPS officer, put the practical case plainly: "Cybercrime does not stop at national borders. Criminals can operate from one country and target victims in another. This convention can help countries share evidence and work together faster. For India, stronger international cooperation can make it easier to investigate cross-border cyber fraud and trace stolen money."
The part the announcement leaves out
Here is where the story gets considerably more complicated than a signing ceremony photo suggests. Since before the Convention's text was even finalised, a wide coalition of digital rights organisations, including the Electronic Frontier Foundation, Human Rights Watch, the Global Network Initiative, and Privacy International, has warned that the treaty's language is dangerously broad, and that its safeguards against misuse are considerably weaker than they need to be.
Cisco, one of the few major technology companies to comment publicly, stated the Convention does not do enough to "sufficiently protect basic human rights." UN Secretary-General António Guterres, notably, has himself urged countries to sign and ratify the Convention while simultaneously calling for its implementation to be "rooted in human rights," a somewhat unusual dual message from the very institution that produced the text, and one that implicitly acknowledges the concerns raised against it.
Where this leaves India
None of this means India's signature was unwarranted. The jurisdictional friction Prof. Triveni Singh described is real and well documented, and a shared international framework for evidence sharing genuinely could accelerate investigations that currently stall for months while agencies wait on slow, bilateral mutual legal assistance requests. India's existing domestic cybercrime coordination architecture is already substantial, spanning I4C, the National Cybercrime Reporting Portal, and newer mechanisms like the Citizen Financial Cyber Fraud Reporting and Management System and the Sahyog platform, and a global treaty that maps onto this existing infrastructure could genuinely close gaps that purely domestic tools cannot reach, particularly in cases where the perpetrator, the server, and the victim all sit in different countries, a pattern that has become close to the default in organised online financial fraud rather than the exception.
But the criticisms levelled at the Convention are not fringe objections; they come from some of the most established digital rights organisations in the world, and they focus specifically on the treaty's most powerful surveillance and cross-border cooperation provisions, the very mechanisms India will now need to operationalise domestically. Signing the Convention is also only the first procedural step; India's obligations under it will not take practical effect until the instrument is ratified domestically, a process that typically allows room for a signatory state to clarify how broadly or narrowly it intends to apply the treaty's more expansive provisions. How India chooses to implement those provisions, whether through the kind of judicial oversight and narrow, offence-specific application human rights groups have called for, or through the broader interpretation the treaty's text technically permits, will likely determine whether this Convention becomes a genuine tool against fraud and organised cybercrime, or a broader instrument whose reach eventually extends well past the digital offences it was signed to address.
References
- The420.in, "India Signs UN Cybercrime Convention to Strengthen Global Fight Against Digital Crime." ANI, "EAM Jaishankar signs UN Convention against Cybercrime on UNGA sidelines." https://aninews.in/news/world/us/eam-jaishankar-signs-un-convention-against-cybercrime-on-unga-sidelines20260926063207/
- Ministry of Cyber Affairs, "India signs UN Convention against Cybercrime at UNGA 81." https://ministryofcyberaffairs.com/news/india-signs-un-convention-against-cybercrime-at-unga-81-95b7e43b-7e29-4722-a4a7-304bca55b71c
- Electronic Frontier Foundation, "UN Cybercrime Convention Negotiations Enter Final Phase With Troubling Surveillance Powers Still on the Table." https://www.eff.org/deeplinks/2023/08/un-cybercrime-convention-negotiations-enter-final-phase-troubling-surveillance
- Electronic Frontier Foundation, "First Draft of UN Cybercrime Convention Drops Troubling Provisions, But Dangerous And Open-Ended Cross Border Surveillance Powers Are Still on the Table."
- https://www.eff.org/deeplinks/2023/07/first-draft-un-cybercrime-treaty-drops-troubling-provisions-dangerous-and-open
- Global Network Initiative, "GNI Calls on Member States Not to Support the UN Cybercrime Convention." https://globalnetworkinitiative.org/gni-statement-on-uncc/
- Just Security, "The UN Cybercrime Convention: Analyzing the Risks to Human Rights and Global Privacy." https://www.justsecurity.org/98738/cybercrime-convention-human-rights/
- TechRadar Pro, "UN cybercrime convention inadequate, says Human Rights Watch." https://techradar.com/pro/un-cybercrime-convention-inadequate-says-human-rights-watch
- Digital Watch Observatory, "Comparative analysis: the Budapest Convention vs the UN Convention Against Cybercrime." https://dig.watch/updates/comparative-analysis-the-budapest-convention-vs-the-un-convention-against-cybercrime
- epicenter.works, "Cybercrime Convention: Cross-Border Human Rights Violations." https://epicenter.works/en/content/cybercrime-convention-cross-border-human-rights-violations
- UN Press, "Secretary-General Urges All Countries to Sign, Ratify New UN Convention against Cybercrime, Calls for Solutions Rooted in Human Rights." https://press.un.org/en/2025/sgsm22961.doc.htm
- https://cyberpeace.org/resources/blogs/the-digital-leviathan-the-un-cybercrime-treaty-and-the-future-of-global-governance
- https://cyberpeace.org/resources/blogs/the-world-is-rewriting-the-rules-against-cyber-enabled-transnational-crime
Introduction
Public infrastructure has traditionally served as the framework for civilisation, transporting people, money, and ideas across time and space, from the iron veins of transcontinental railroads to the unseen arteries of the internet. In democracies where free markets and public infrastructure co-exist, this framework has not only facilitated but also accelerated progress. Digital Public Infrastructure (DPI), which powers inclusiveness, fosters innovation, and changes citizens from passive recipients to active participants in the digital age, is emerging as the new civic backbone as we move away from highways and towards high-speed data.
DPI makes it possible for innovation at the margins and for inclusion at scale by providing open-source, interoperable platforms for identities, payments, and data exchange. Examples of how the Global South is evolving from a passive consumer of technology to a creator of globally replicable governance models are India’s Aadhaar (digital identification), UPI (real-time payments), and DigiLocker (data empowerment). As the ‘digital commons’ emerges, DPI does more than simply link users; it also empowers citizens, eliminates inefficiencies from the past, and reimagines the creation and distribution of public value in the digital era.
Securing the Digital Infrastructure: A Contemporary Imperative
As humans, we are already the inhabitants of the future, we stand at the temporal threshold for reform. Digital Infrastructure is no longer just a public good. It’s now a strategic asset, akin to oil pipelines in the 20th century. India is recognised globally for the introduction of “India Stack”, through which the face of digital payments has also been changed. The economic value contributed by DPIs to India’s GDP is predicted to reach 2.9-4.2 percent by 2030, having already reached 0.9% in 2022. Its role in India’s economic development is partly responsible for its success; among emerging market economies, it helped propel India to the top of the revenue administrations’ digitalisation index. The other portion has to do with how India’s social service delivery has changed across the board. By enabling digital and financial inclusion, it has increased access to education (DIKSHA) and is presently being developed to offer agricultural (VISTAAR) and digital health (ABDM) services.
Securing the Foundations: Emerging Threats to Digital Public Infrastructure
The rising prominence of DPI is not without its risks, as adversarial forces are developing with comparable sophistication. The core underpinnings of public digital systems are the target of a new generation of cyber threats, ranging from hostile state actors to cybercriminal syndicates. The threats pose a great risk to the consistent development endeavours of the government. To elucidate, targeted attacks on Biometric databases, AI-based Misinformation and Psychological Warfare, Payment System Hacks, State-sponsored malware, cross-border phishing campaigns, surveillance spyware and Sovereign Malware are modern-day examples of cyber threats.
To secure DPI, a radical rethink beyond encryption methods and perimeter firewalls is needed. It requires an understanding of cybersecurity that is systemic, ethical, and geopolitical. Democracy, inclusivity, and national integrity are all at risk from DPI. To preserve the confidence and promise of digital public infrastructure, policy frameworks must change from fragmented responses to coordinated, proactive and people-centred cyber defence policies.
CyberPeace Recommendations
Powering Progress, Ignoring Protection: A Precarious Path
The Indian government is aware that cyberattacks are becoming more frequent and sophisticated in the nation. To address the nation’s cybersecurity issues, the government has implemented a number of legislative, technical, and administrative policy initiatives. While the initiatives are commendable, there are a few Non-Negotiables that need to be in place for effective protection:
- DPIs must be declared Critical Information Infrastructure. In accordance with the IT Act, 2000, the DPI (Aadhaar, UPI, DigiLocker, Account Aggregator, CoWIN, and ONDC) must be designated as Critical Information Infrastructure (CII) and be supervised by the NCIIPC, just like the banking, energy, and telecom industries. Give NCIIPC the authority to publish required security guidelines, carry out audits, and enforce adherence to the DPI stack, including incident response protocols tailored to each DPI.
- To solidify security, data sovereignty, and cyber responsibility, India should spearhead global efforts to create a Global DPI Cyber Compact through the “One Future Alliance” and the G20. To ensure interoperable cybersecurity frameworks for international DPI projects, promote open standards, cross-border collaboration on threat intelligence, and uniform incident reporting guidelines.
- Establish a DPI Threat Index to monitor vulnerabilities, including phishing attacks, efforts at biometric breaches, sovereign malware footprints, spikes in AI misinformation, and patterns in payment fraud. Create daily or weekly risk dashboards by integrating data from state CERTs, RBI, UIDAI, CERT-In, and NPCI. Use machine learning (ML) driven detection systems.
- Make explainability audits necessary for AI/ML systems used throughout DPI to make sure that the decision-making process is open, impartial, and subject to scrutiny (e.g., welfare algorithms, credit scoring). Use the recently established IndiaAI Safety Institute in line with India’s AI mission to conduct AI audits, establish explanatory standards, and create sector-specific compliance guidelines.
References
- https://orfamerica.org/newresearch/dpi-catalyst-private-sector-innovation?utm_source=chatgpt.com
- https://www.institutmontaigne.org/en/expressions/indias-digital-public-infrastructure-success-story-world
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2116341
- https://www.pib.gov.in/PressReleaseIframePage.aspx?PRID=2033389
- https://www.governancenow.com/news/regular-story/dpi-must-ensure-data-privacy-cyber-security-citizenfirst-approach
