
World Environment Day 2025: The Hidden Cost of Our Digital Lives
On June 5th, the world comes together to reflect on how the way we live impacts the environment. We discuss conserving water, cutting back on plastic, and planting trees, but how often do we think about the environmental impact of our digital lives?
The internet is ubiquitous but invisible in a world that is becoming more interconnected by the day. It drives our communications, meetings, and recollections. However, there is a price for this digital convenience: carbon emissions.
A Digital Carbon Footprint: What Is It?
Electricity is necessary for every video we stream, email we send, and file we store on the cloud. But almost 60% of the electricity produced today is generated from burning fossil fuels. The digital world uses an incredible amount of energy, from the energy-hungry data centres that house our information to the networks that send it. Thus, the greenhouse gas emissions produced by our use of digital tools and services are referred to as our "digital carbon footprint."
To put it in perspective:
- Up to 150–200 grams of CO₂ can be produced by streaming an hour-long HD video on your phone.
- A typical email sent can release about 4 grams of CO₂, and more if it contains attachments.
- Comparable to the airline industry, the internet as a whole accounts for 1.5% to 4% of global greenhouse gas emissions.
Why It Matters
Ironically, despite the fact that digital life frequently feels "clean" and weightless, it is backed by enormous, power-hungry infrastructures. Additionally, our online activity is growing at a rapid pace as digital penetration increases. Plus, with the advent of AI and big data, the demand for energy is only going to rise. The harms of air, water, and soil degradation, and biodiversity loss are already upon us. It's high time we reconsider how we use technology on World Environment Day.
What Can You Do?
The good news is that even minor adjustments to our online conduct can have an impact.
🗑️ Clear out your digital clutter by getting rid of unnecessary emails, apps, and files.
📥 Unsubscribe from mailing lists that you no longer use.
📉 When HD is not required, stream videos with lower quality.
⚡ Make use of energy-saving gadgets and disconnect them when not in use.
🌐 Make the move to renewable energy-powered, environmentally friendly cloud providers.
🗳️ Support informed policy by engaging with your elected representatives and advocating for greener tech policies. Knowing your digital rights and responsibilities can help shape smarter policies and a healthier planet.
We at the CyberPeace Foundation think that cyberspace needs to be sustainable. An eco-friendly digital world is also a safer one, where all communities can thrive in harmony. We must promote digital responsibility, including its environmental component, as we work towards digital equity and resilience.
On this World Environment Day, let's go one step further and work towards a greener internet as well as a greener planet.

Related Blogs

A Foray into the Digital Labyrinth
In our digital age, the silhouette of truth is often obfuscated by a fog of technological prowess and cunning deception. With each passing moment, the digital expanse sprawls wider, and within it, synthetic media, known most infamously as 'deepfakes', emerge like phantoms from the machine. These adept forgeries, melding authenticity with fabrication, represent a new frontier in the malleable narrative of understood reality. Grappling with the specter of such virtual deceit, social media behemoths Facebook and YouTube have embarked on a prodigious quest. Their mission? To formulate robust bulwarks around the sanctity of fact and fiction, all the while fostering seamless communication across channels that billions consider an inextricable part of their daily lives.
In an exploration of this digital fortress besieged by illusion, we unpeel the layers of strategy that Facebook and YouTube have unfurled in their bid to stymie the proliferation of these insidious technical marvels. Though each platform approaches the issue through markedly different prisms, a shared undercurrent of necessity and urgency harmonizes their efforts.
The Detailing of Facebook's Strategic
Facebook's encampment against these modern-day chimaeras teems with algorithmic sentinels and human overseers alike—a union of steel and soul. The company’s layer upon layer of sophisticated artificial intelligence is designed to scrupulously survey, identify, and flag potential deepfake content with a precision that borders on the prophetic. Employing advanced AI systems, Facebook endeavours to preempt the chaos sown by manipulated media by detecting even the slightest signs of digital tampering.
However, in an expression of profound acumen, Facebook also serves reminder of AI's fallibility by entwining human discernment into its fabric. Each flagged video wages its battle for existence within the realm of these custodians of reality—individuals entrusted with the hefty responsibility of parsing truth from technologically enabled fiction.
Facebook does not rest on the laurels of established defense mechanisms. The platform is in a perpetual state of flux, with policies and AI models adapting to the serpentine nature of the digital threat landscape. By fostering its cyclical metamorphosis, Facebook not only sharpens its detection tools but also weaves a more resilient protective web, one capable of absorbing the shockwaves of an evolving battlefield.
YouTube’s Overture of Transparency and the Exposition of AI
Turning to the amphitheatre of YouTube, the stage is set for an overt commitment to candour. Against the stark backdrop of deepfake dilemmas, YouTube demands the unveiling of the strings that guide the puppets, insisting on full disclosure whenever AI's invisible hands sculpt the content that engages its diverse viewership.
YouTube's doctrine is straightforward: creators must lift the curtains and reveal any artificial manipulation's role behind the scenes. With clarity as its vanguard, this requirement is not just procedural but an ethical invocation to showcase veracity—a beacon to guide viewers through the murky waters of potential deceit.
The iron fist within the velvet glove of YouTube's policy manifests through a graded punitive protocol. Should a creator falter in disclosing the machine's influence, repercussions follow, ensuring that the ecosystem remains vigilant against hidden manipulation.
But YouTube's policy is one that distinguishes between malevolence and benign use. Artistic endeavours, satirical commentary, and other legitimate expositions are spared the policy's wrath, provided they adhere to the overarching principle of transparency.
The Symbiosis of Technology and Policy in a Morphing Domain
YouTube's commitment to refining its coordination between human insight and computerized examination is unwavering. As AI's role in both the generation and moderation of content deepens, YouTube—which, like a skilled cartographer, must redraw its policies increasingly—traverses this ever-mutating landscape with a proactive stance.
In a Comparative Light: Tracing the Convergence of Giants
Although Facebook and YouTube choreograph their steps to different rhythms, together they compose an intricate dance aimed at nurturing trust and authenticity. Facebook leans into the proactive might of their AI algorithms, reinforced by updates and human interjection, while YouTube wields the virtue of transparency as its sword, cutting through masquerades and empowering its users to partake in storylines that are continually rewritten.
Together on the Stage of Our Digital Epoch
The sum of Facebook and YouTube's policies is integral to the pastiche of our digital experience, a multifarious quilt shielding the sanctum of factuality from the interloping specters of deception. As humanity treads the line between the veracious and the fantastic, these platforms stand as vigilant sentinels, guiding us in our pursuit of an old-age treasure within our novel digital bazaar—the treasure of truth. In this labyrinthine quest, it is not merely about unmasking deceivers but nurturing a wisdom that appreciates the shimmering possibilities—and inherent risks—of our evolving connection with the machine.
Conclusion
The struggle against deepfakes is a complex, many-headed challenge that will necessitate a united front spanning technologists, lawmakers, and the public. In this digital epoch, where the veneer of authenticity is perilously thin, the valiant endeavours of these tech goliaths serve as a lighthouse in a storm-tossed sea. These efforts echo the importance of evergreen vigilance in discerning truth from artfully crafted deception.
References
- https://about.fb.com/news/2020/01/enforcing-against-manipulated-media/
- https://indianexpress.com/article/technology/artificial-intelligence/google-sheds-light-on-how-its-fighting-deep-fakes-and-ai-generated-misinformation-in-india-9047211/
- https://techcrunch.com/2023/11/14/youtube-adapts-its-policies-for-the-coming-surge-of-ai-videos/
- https://www.trendmicro.com/vinfo/us/security/news/cybercrime-and-digital-threats/youtube-twitter-hunt-down-deepfakes
Executive Summary:
New Linux malware has been discovered by a cybersecurity firm Volexity, and this new strain of malware is being referred to as DISGOMOJI. A Pakistan-based threat actor alias ‘UTA0137’ has been identified as having espionage aims, with its primary focus on Indian government entities. Like other common forms of backdoors and botnets involved in different types of cyberattacks, DISGOMOJI, the malware allows the use of commands to capture screenshots, search for files to steal, spread additional payloads, and transfer files. DISGOMOJI uses Discord (messaging service) for Command & Control (C2) and uses emojis for C2 communication. This malware targets Linux operating systems.
The DISCOMOJI Malware:
- The DISGOMOJI malware opens a specific channel in a Discord server and every new channel corresponds to a new victim. This means that the attacker can communicate with the victim one at a time.
- This particular malware connects with the attacker-controlled Discord server using Emoji, a form of relay protocol. The attacker provides unique emojis as instructions, and the malware uses emojis as a feedback to the subsequent command status.
- For instance, the ‘camera with flash’ emoji is used to screenshots the device of the victim or to steal, the ‘fox’ emoji cracks all Firefox profiles, and the ‘skull’ emoji kills the malware process.
- This C2 communication is done using emojis to ensure messaging between infected contacts, and it is almost impossible for Discord to shut down the malware as it can always change the account details of Discord it is using once the maliciou server is blocked.
- The malware also has capabilities aside from the emoji-based C2 such as network probing, tunneling, and data theft that are needed to help the UTA0137 threat actor in achieving its espionage goals.
Specific emojis used for different commands by UTA0137:
- Camera with Flash (📸): Captures a picture of the target device’s screen as per the victim’s directions.
- Backhand Index Pointing Down (👇): Extracts files from the targeted device and sends them to the command channel in the form of attachments.
- Backhand Index Pointing Right (👉): This process involves sending a file found on the victim’s device to another web-hosted file storage service known as Oshi or oshi[. ]at.
- Backhand Index Pointing Left (👈): Sends a file from the victim’s device to transfer[. ]sh, which is an online service for sharing files on the Internet.
- Fire (🔥): Finds and transmits all files with certain extensions that exist on the victim’s device, such as *. txt, *. doc, *. xls, *. pdf, *. ppt, *. rtf, *. log, *. cfg, *. dat, *. db, *. mdb, *. odb, *. sql, *. json, *. xml, *. php, *. asp, *. pl, *. sh, *. py, *. ino, *. cpp, *. java,
- Fox (🦊): This works by compressing all Firefox related profiles in the affected device.
- Skull (💀): Kills the malware process in windows using ‘os. Exit()’
- Man Running (🏃♂️): Execute a command on a victim’s device. This command receives an argument, which is the command to execute.
- Index Pointing up (👆) : Upload a file to the victim's device. The file to upload is attached along with this emoji
Analysis:
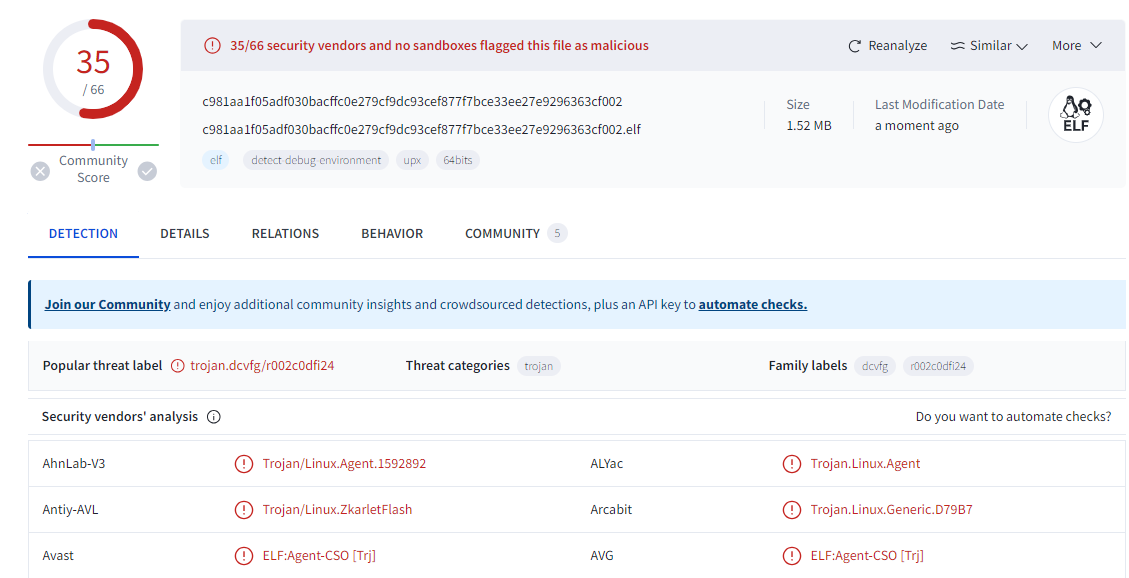
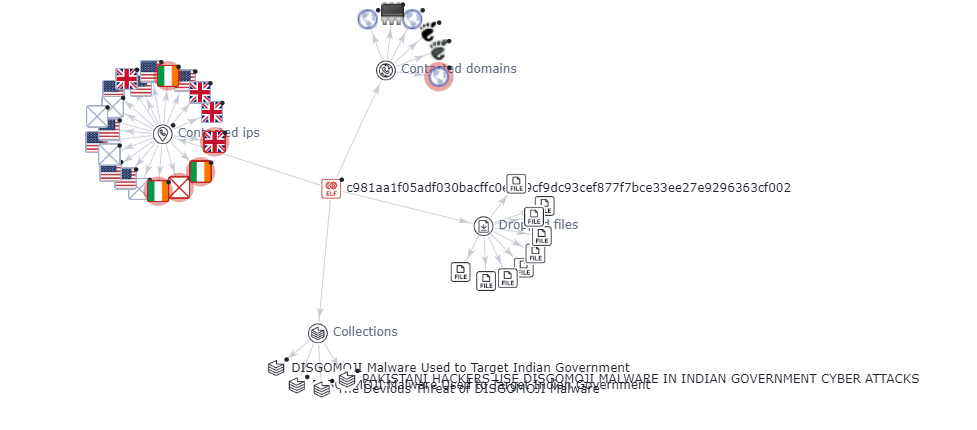
The analysis was carried out for one of the indicator of compromised SHA-256 hash file- C981aa1f05adf030bacffc0e279cf9dc93cef877f7bce33ee27e9296363cf002.
It is found that most of the vendors have marked the file as trojan in virustotal and the graph explains the malicious nature of the contacted domains and IPs.
Discord & C2 Communication for UTA0137:
- Stealthiness: Discord is a well-known messaging platform used for different purposes, which means that sending any messages or files on the server should not attract suspicion. Such stealthiness makes it possible for UTA0137 to remain dormant for greater periods before launching an attack.
- Customization: UTA0137 connected to Discord is able to create specific channels for distinct victims on the server. Such a framework allows the attackers to communicate with each of the victims individually to make a process more accurate and efficient.
- Emoji-based protocol: For C2 communication, emojis really complicates the attempt that Discord might make to interfere with the operations of the malware. In case the malicious server gets banned, malware could easily be recovered, especially by using the Discord credentials from the C2 server.
- Persistence: The malware, as stated above, has the ability to perpetually exist to hack the system and withstand rebooting of systems so that the virus can continue to operate without being detected by the owner of the hacked system.
- Advanced capabilities: Other features of DISGOMOJI are the Network Map using Nmap scanner, network tunneling through Chisel and Ligolo and Data Exfiltration by File Sharing services. These capabilities thus help in aiding the espionage goals of UTA0137.
- Social engineering: The virus and the trojan can show the pop-up windows and prompt messages, for example the fake update for firefox and similar applications, where the user can be tricked into inputting the password.
- Dynamic credential fetching: The malware does not write the hardcoded values of the credentials in order to connect it to the discord server. This also inconveniences analysts as they are unable to easily locate the position of the C2 server.
- Bogus informational and error messages: They never show any real information or errors because they do not want one to decipher the malicious behavior easily.
Recommendations to mitigate the risk of UTA0137:
- Regularly Update Software and Firmware: It is essential to regularly update all the application software and firmware of different devices, particularly, routers, to prevent hackers from exploiting the discovered and disclosed flaws. This includes fixing bugs such as CVE-2024-3080 and CVE-2024-3912 on ASUS routers, which basically entails solving a set of problems.
- Implement Multi-Factor Authentication: There are statistics that show how often user accounts are attacked, it is important to incorporate multi-factor authentication to further secure the accounts.
- Deploy Advanced Malware Protection: Provide robust guard that will help the user recognize and prevent the execution of the DISGOMOJI malware and similar threats.
- Enhance Network Segmentation: Utilize stringent network isolation mechanisms that seek to compartmentalize the key systems and data from the rest of the network in order to minimize the attack exposure.
- Monitor Network Activity: Scanning Network hour to hour for identifying and handling the security breach and the tools such as Nmap, Chisel, Ligolo etc can be used.
- Utilize Threat Intelligence: To leverage advanced threats intelligence which will help you acquire knowledge on previous threats and vulnerabilities and take informed actions.
- Secure Communication Channels: Mitigate the problem of the leakage of developers’ credentials and ways of engaging with the discord through loss of contact to prevent abusing attacks or gaining control over Discord as an attack vector.
- Enforce Access Control: Regularly review and update the user authentication processes by adopting stricter access control measures that will allow only the right personnel to access the right systems and information.
- Conduct Regular Security Audits: It is important to engage in security audits periodically in an effort to check some of the weaknesses present within the network or systems.
- Implement Incident Response Plan: Conduct a risk assessment, based on that design and establish an efficient incident response kit that helps in the early identification, isolation, and management of security breaches.
- Educate Users: Educate users on cybersecurity hygiene, opportunities to strengthen affinity with the University, and conduct retraining on threats like phishing and social engineering.
Conclusion:
The new threat actor named UTA0137 from Pakistan who was utilizing DISGOMOJI malware to attack Indian government institutions using embedded emojis with a command line through the Discord app was discovered by Volexity. It has the capability to exfiltrate and aims to steal the data of government entities. The UTA0137 was continuously improved over time to permanently communicate with victims. It underlines the necessity of having strong protection from viruses and hacker attacks, using secure passwords and unique codes every time, updating the software more often and having high-level anti-malware tools. Organizations can minimize advanced threats, the likes of DISGOMOJI and protect sensitive data by improving network segmentation, continuous monitoring of activities, and users’ awareness.
References:
https://otx.alienvault.com/pulse/66712446e23b1d14e4f293eb
https://thehackernews.com/2024/06/pakistani-hackers-use-disgomoji-malware.html?m=1
https://cybernews.com/news/hackers-using-emojis-to-command-malware/
https://www.volexity.com/blog/2024/06/13/disgomoji-malware-used-to-target-indian-government/

Introduction
India has always been celebrated as the land of abundance, once known as the ‘golden bird’ that attracted the world with its prosperity and wisdom. In the current century, as the world moves deeper into the age where every nation is redefining its strength through advancements in every sector, including technology, India is preparing for a powerful transformation. “Viksit Bharat 2047” is an initiative aimed at achieving India's aspiration of becoming a developed nation by its centennial year of independence. India’s growth story is shifting as it takes a step towards development in every field and advances progress both in terms of generating economic growth and breakthroughs in technologies across industries.
Today, when technology touches every aspect of our lives, ‘Cyber Security’ becomes a key area that will significantly drive progress and hold strong importance under the Viksit Bharat vision, especially with the rise of emerging technologies such as AI, quantum computing, cryptography, 5G & 6G, robotics and automation, Internet of Things (IoT), augmented reality (AR) & virtual reality (VR) etc.
Key Initiatives Taken by the Centre
Indian Cyber Crime Coordination Centre:
The Indian Cybercrime Coordination Centre (I4C) was established by the Ministry of Home Affairs (MHA) to provide a framework for law enforcement agencies (LEAs) to deal with cybercrime in a coordinated and comprehensive manner. I4C is actively working on initiatives to combat emerging threats in cyberspace, and it has become a strong pillar of India’s cybersecurity and cybercrime prevention. The ‘National Cyber Crime Reporting Portal’, equipped with a 24x7 cybercrime helpline number 1930, is one of the key components of the I4C.
Recently under I4C, key initiatives were launched to strengthen cybersecurity. The Cyber Fraud Mitigation Centre (CFMC) has been incorporated to bring together banks, financial institutions, telecom companies, Internet Service Providers, and law enforcement agencies on a single platform to tackle online financial crimes efficiently. The Cyber Commandos Program will establish a specialised wing of trained Cyber Commandos in states, Union Territories, and Central Police Organisations to counter rising cyber threats. The Samanvay platform, a web-based Joint Cybercrime Investigation Facility System, has been introduced as a one-stop data repository for cybercrime to foster data sharing and collaboration. The Suspect Registry Portal, connected to the National Cybercrime Reporting Portal (NCRP), has been designed to track cybercriminals and strengthen fraud risk management.
India’s AI Mission:-
The Indian Cabinet has approved a comprehensive national-level IndiaAI Mission. The mission aims to strengthen the Indian AI innovation ecosystem by democratizing computing access, improving data quality, developing indigenous AI capabilities, attracting top AI talent, enabling industry collaboration, providing startup risk capital, ensuring socially impactful AI projects, and bolstering ethical AI. Through India AI Mission, the government is facilitating the development of India’s own foundational models, including Large Language Models (LLMs) and problem-specific AI solutions tailored to Indian needs.
The mission is implemented by the 'IndiaAI' Independent Business Division (IBD) under the Digital India Corporation (DIC) and consists of several components, such as IndiaAI Compute Capacity, IndiaAI Innovation Centre (IAIC), IndiaAI Datasets Platform, IndiaAI Application Development Initiative, IndiaAI Future Skills, IndiaAI Startup Financing, and Safe & Trusted AI. The main objective is to create and nurture an ecosystem for India’s AI innovation.
Startup India:-
With more than 1.59 lakh startups recognised by the Department for Promotion of Industry and Internal Trade (DPIIT) as of January 15, 2025, India has firmly established itself as the third-largest startup ecosystem in the world. Startup India is a flagship initiative launched by the Government of India on 16th January 2016 to build a strong ecosystem for nurturing innovation and startups in the country, which will drive economic growth and generate large-scale employment opportunities.
Key Regulations:-
The Centre, in order to better regulate the cyber domain, has come up with significant regulations. To protect the personal data of citizens, the Digital Personal Data Protection Act, 2023 has been enacted. The Intermediary Guidelines 2021 lay down obligations on social media platforms and intermediaries to ensure accountability and user safety. The Telecommunications Act 2023 has also been enacted. Further, the Promotion and Regulation of Online Gaming Bill 2025, passed by Parliament on 21st August 2025, aims to address related concerns. In addition, Cert-In issues guidelines & advisories from time to time, in order to strengthen cybersecurity.
CyberPeace Outlook
CyberPeace has been at the forefront in transforming policy, technology, and ethical growth in the cyber landscape through its key initiatives. In 2023, CyberPeace hosted the Global CyberPeace Summit in collaboration with Civil 20 and G20 India, with knowledge support from the United Service Institution of India and participation from MeitY, NCIIPC, CERT-In, Zoom, Meta, InMobi, ICANN, Internet Society, MANRS, APNIC, and leading universities, which helped shape critical global conversations on trust, safety, and collaboration in cyberspace.
Viksit Bharat 2047 is more than just a vision for economic success; it is a pledge to create a nation that is technologically secure, resilient, and globally competitive. In this journey, cybersecurity will be at the heart of India's digital reboot, securing its innovation, empowering its citizens, and ensuring its future.
References
- https://www.cyberpeace.org/resources/blogs/i4c-foundation-day-celebration-shri-amit-shah-launches-key-initiatives-to-tackle-cybercrime
- https://www.cyberpeace.org/resources/blogs/indiaai-mission
- https://bharatarticles.com/viksit-bharat-2047-vision-challenges-and-roadmap-to-a-developed-india/
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2012355
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2093125
