
Securing Digital Banking: RBI Mandates Migration to [.]bank[.]in Domains
Introduction
The Reserve Bank of India (RBI) has mandated banks to switch their digital banking domains to 'Bank.in' by October 31, 2025, as part of a strategy to modernise the sector and maintain consumer confidence. The move is expected to provide a consistent and secure interface for online banking, as a response to the increasing threats posed by cybercriminals who exploit vulnerabilities in online platforms. The RBI's directive is seen as a proactive measure to address the growing concerns over cybersecurity in the banking sector.
RBI Circular - Migration to '.bank.in' domain
The official circular released by the RBI dated April 22, 2025, read as follows:
“It has now been decided to operationalise the ‘. bank.in’ domain for banks through the Institute for Development and Research in Banking Technology (IDRBT), which has been authorised by National Internet Exchange of India (NIXI), under the aegis of the Ministry of Electronics and Information Technology (MeitY), to serve as the exclusive registrar for this domain. Banks may contact IDRBT at sahyog@idrbt.ac.in to initiate the registration process. IDRBT shall guide the banks on various aspects related to application process and migration to new domain.”
“All banks are advised to commence the migration of their existing domains to the ‘.bank.in’ domain and complete the process at the earliest and in any case, not later than October 31, 2025.”
CyberPeace Outlook
The Reserve Bank of India's directive mandating banks to shift to the 'Bank.in' domain by October 31, 2025, represents a strategic and forward-looking measure to modernise the nation’s digital banking infrastructure. With this initiative, the RBI is setting a new benchmark in cybersecurity by creating a trusted, exclusive domain that banks must adopt. This move will drastically reduce cyber threats, phishing attacks, and fake banking websites, which have been major sources of financial fraud. This fixed domain will simplify verification for consumers and tech platforms to more easily identify legitimate banking websites and apps. Furthermore, a strong drop in online financial fraud will have a long-term effect by this order. Since phishing and domain spoofing are two of the most prevalent forms of cybercrime, a shift to a strictly regulated domain name system will remove the potential for lookalike URLs and fraudulent websites that mimic banks. As India’s digital economy grows, RBI’s move is timely, essential, and future-ready.
References

Related Blogs

Introduction
MSMEs, being the cornerstone of the Indian economy, are one of the most vulnerable targets in cyberspace and no enterprise is too small to be a target for malicious actors. MSMEs hardly ever perform a cyber-risk assessment, but when they do, they may run into a number of internal problems, such as cyberattacks brought on by inadequate networking security, online fraud, ransomware assaults, etc. Tackling cyber threats in MSMEs is critical mainly because of their high level of dependance on digital technologies and the growing sophistication of cyber attacks. Protecting them from cyber threats is essential, as a security breach can have devastating consequences, including financial loss, reputational damage, and operational disruptions.
Key Cyber Threats that MSMEs are facing
MSMEs are most vulnerable to are phishing attacks, ransomware, malware and viruses, insider threats, social engineering attacks, supply chain attacks, credential stuffing and brute force attacks and Distributed Denial of Service (DDoS) Attacks. Some of these attacks are described as under-
- Insider threats arise from employees or contractors who intentionally or unintentionally compromise security. It involves data theft, misuse of access privileges, or accidental data exposure.
- Social engineering attacks involve manipulating individuals into divulging confidential information or performing actions that compromise security by pretexting, baiting, and impersonation.
- Supply chain attacks exploit the trust in relationships between businesses and their suppliers and introduce malware, compromise data integrity, and disrupt operations.
- Credential stuffing and brute force attacks give unauthorized access to accounts and systems, leading to data breaches and financial losses.
Challenges Faced by MSMEs in Cybersecurity
The challenges faced by MSMEs in cyber security are mainly due to limited resources and budget constraints which leads to other issues such as a lack of specialized expertise as MSMEs often lack the IT support of cyber security experts. Awareness and training are needed to mitigate poor understanding of cyber threats and their complexity in nature. Vulnerabilities in the supply chain are present as they rely on third-party vendors and partners often, introducing potential supply chain vulnerabilities. Regulatory compliance is often complex and is taken seriously only when an issue crops up but it needs special attention especially with the DPDP Act coming in. The lack of an incident response plan leads to delayed and inadequate responses to cyber incidents, increasing the impact of breaches.
Best Practices for Tackling Cyber Threats for MSMEs
To effectively tackle cyber threats, MSMEs should adopt a comprehensive approach such as:
- Implementing and enforcing strong access controls by using MFA or 2FA and password policies. Limiting employee access as role based and updating the same as and when needed.
- Regularly apply security patches and use automated patch management solutions to prevent exploitation of known vulnerabilities.
- Conduct employee training and awareness programs and promote a security-first approach for the employees and assessing employee readiness to identify improvement areas.
- Implement network security measures by using firewalls and intrusion detection systems. Using secure Wi-Fi networks via strong encryptions and changing default credentials for the router are recommended, as is segmenting networks to limit lateral movement within the network in case of a breach.
- Regular data backup ensures that in case of an attack, data loss can be recovered and made available in secure offsite locations to protect it from unauthorized access.
- Developing an incident response plan that outlines the roles, responsibilities and procedure for responding to cyber incidents with regular drills to ensure readiness and clear communication protocols for incident reporting to regulators, stakeholders and customers.
- Implement endpoint security solutions using antivirus and anti-malware softwares. Devices should be against unauthorized access and implement mobile device management solutions enforcing security policies on employee-owned devices used for work purposes.
- Cyber insurance coverage will help in transferring financial risks in case of cyber incidents. It should have comprehensive coverage including business interruptions, data restoration, legal liabilities and incident response costs.
Recommended Cybersecurity Solutions Tailored for MSMEs
- A Managed Security Service Provider offers outsourced cybersecurity services, including threat monitoring, incident response, and vulnerability management that may be lacking in-house.
- Cloud-Based Security Solutions such as firewall as a service and Security Information and Event Management , provide scalable and cost-effective protection for MSMEs.
- Endpoint Detection and Response (EDR) Tools detect and respond to threats on endpoints, providing real-time visibility into potential threats and automating incident response actions.
- Security Awareness Training Platforms deliver interactive training sessions and simulations to educate employees about cybersecurity threats and best practices.
Conclusion
Addressing cyber threats in MSMEs requires a proactive and multi-layered approach that encompasses technical solutions, employee training, and strategic planning. By implementing best practices and leveraging cybersecurity solutions tailored to their specific needs, MSMEs can significantly enhance their resilience against cyber threats. As cyber threats continue to evolve, staying informed about the latest trends and adopting a culture of security awareness will be essential for MSMEs to protect their assets, reputation, and bottom line.
References:
- https://economictimes.indiatimes.com/small-biz/security-tech/security/cyber-security-pitfalls-and-how-negligence-can-be-expensive-for-msmes/articleshow/99508822.cms?from=mdr
- https://www.investopedia.com/financial-edge/0112/3-ways-cyber-crime-impacts-business.aspx
- https://www.financialexpress.com/business/sme-msme-tech-cisco-launches-new-tool-for-smbs-to-assess-their-cybersecurity-readiness-2538348/
- https://www.cloverinfotech.com/blog/small-businesses-big-problems-are-cyber-attacks-crushing-indias-msmes/
Executive Summary:
A video is being shared on social media showing two women wearing burqas arguing with a man riding a motorcycle on a road and later slapping him. Social media users are sharing the video as being from India, claiming that Muslim women are being targeted in public places. The video is being widely circulated across various social media platforms with this claim. However, research by the CyberPeace Research Wing found that the viral video does not show an incident of Muslim women being targeted in India. The video is actually from the shooting of a short film in Pakistan.
Claim:
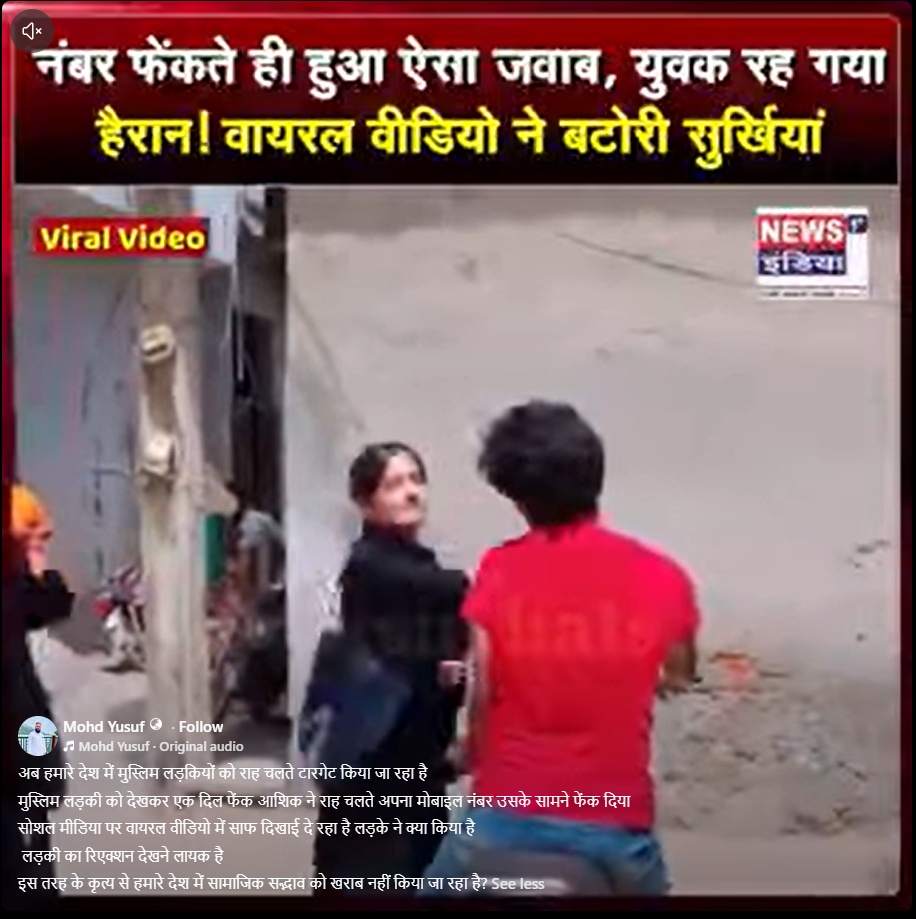
A Facebook user shared the viral video claiming, “Muslim girls are now being targeted while walking on the streets in our country. Seeing a Muslim girl, a love-struck man threw his mobile number in front of her while walking past. The viral video clearly shows what the boy did, and the girl's reaction is worth watching. Such acts are harming social harmony in our country.”
The archived link and screenshot of the post are provided below.
https://www.facebook.com/reel/1087774553785531
FactCheck
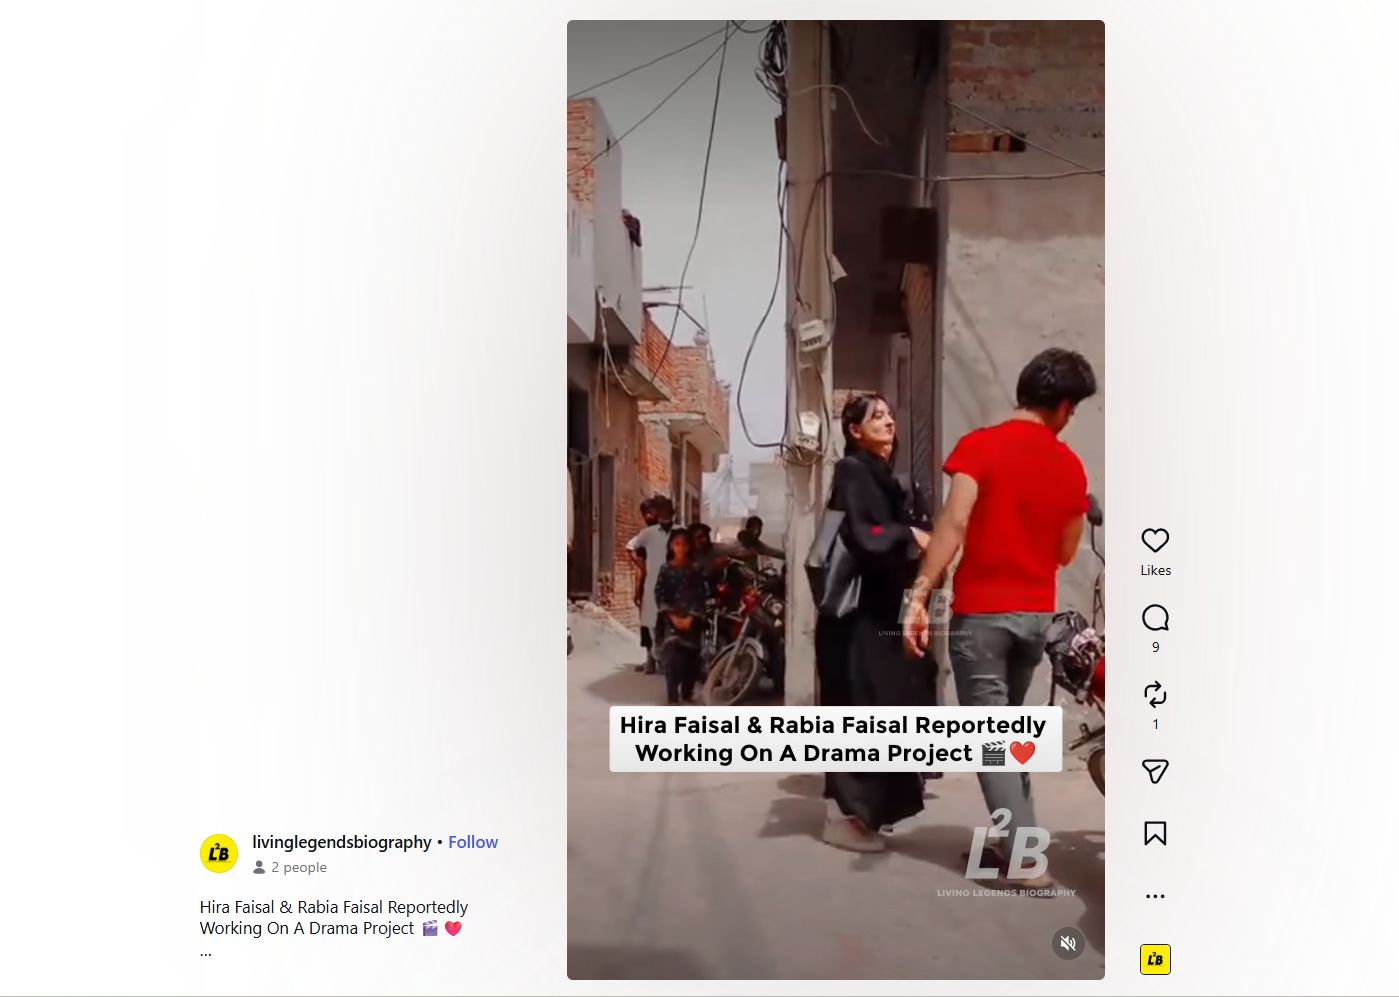
To verify the authenticity of the viral claim, we conducted a reverse image search of the keyframes from the video. During the search, we found the same video on a Pakistani Instagram account, @livinglegendsbiography, where it was posted on May 25, 2026. The caption of the post clearly stated that the video was part of a drama shoot featuring Heera Faisal and Rabia Faisal. The video itself also contains indications that it was staged. After the man is slapped, both women wearing burqas and the motorcycle rider can be seen laughing. This further confirms that the video is not from a real incident but was part of a scripted drama shoot. The link to the post and a screenshot are provided below.
https://www.instagram.com/reels/DYwXNp4I-eE/
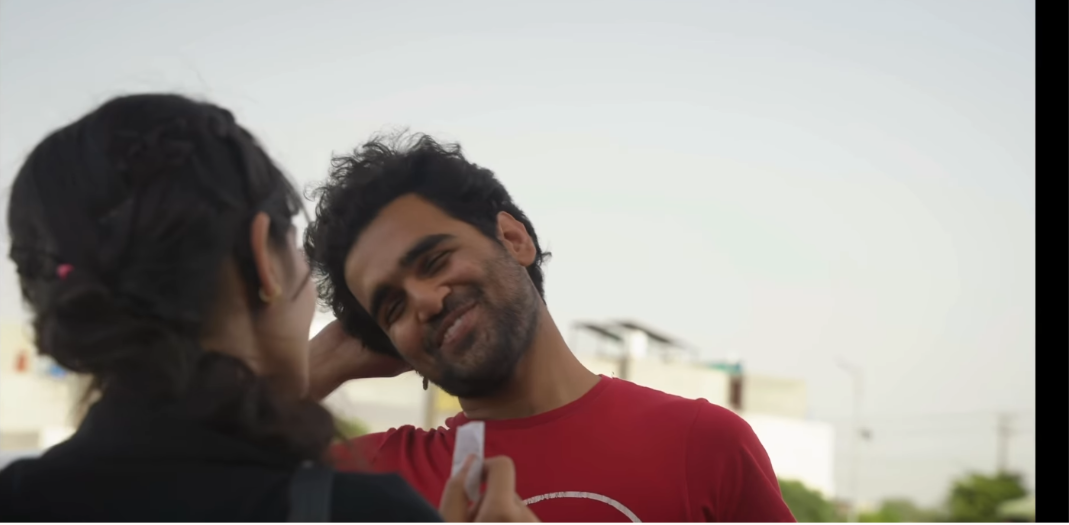
Continuing our research, we also found the trailer of the short film ‘Ghairat’ posted on Rabia Faisal’s Instagram account on July 5, 2026. The trailer features several scenes that closely resemble those seen in the viral video. According to the information provided in the post, the short film was released on July 20, 2026. This further confirms that the viral video is not from a real incident, but was part of the shooting of the short film. The link to the post and a screenshot are provided below.
Conclusion:
The evidence gathered during our research makes it clear that the video circulating on social media does not show a real incident of Muslim women being targeted in public places in India. During the research, we found the same video on a Pakistani Instagram account, where it was identified as part of a drama shoot featuring Heera Faisal and Rabia Faisal. We also found the trailer of the short film ‘Ghairat’ on Rabia Faisal’s account, which contains scenes resembling those seen in the viral video. Based on the available evidence, it is clear that the viral video was recorded during the shooting of a short film in Pakistan. Therefore, the claim that the video shows an incident of Muslim women being targeted in India is false.

Introduction
India's broadcasting sector has undergone significant changes in recent years with technological advancements such as the introduction of new platforms like Direct-to-Home (DTH), Internet Protocol television (IPTV), Over-The-Top (OTT), and integrated models. Platform changes, emerging technologies and advancements in the advertising space have all necessitated the need for new governing laws that take these developments into account.
The Union Government and concerned ministry have realised there is a pressing need to develop a robust regulatory framework for the Indian broadcasting sector in the country and consequently, a draft Broadcasting Services (Regulation) Bill, 2023, was released in November 2023 and the Union Ministry of Information and Broadcasting (MIB) had invited feedback and comments from different stakeholders. The draft Bill aims to establish a unified framework for regulating broadcasting services in the country, replacing the current Cable Television Networks (Regulation) Act, 1995 and other policy guidelines governing broadcasting.
Recently a new draft of an updated ‘Broadcasting Services (Regulation) Bill, 2024,’ was shared with selected broadcasters, associations, streaming services, and tech firms, each marked with their identifier to prevent leaks.
Key Highlights of the Updated Broadcasting Bill
As per the recent draft of the Broadcasting Services (Regulation) Bill, 2024, social media accounts could be identified as ‘Digital News Broadcasters’ and can be classified within the ambit of the regulation. Some of the major aspects of the new bill were first reported by Hindustan Times.
The new draft of the Broadcasting Services (Regulation) Bill, 2024, proposes that individuals who regularly upload videos to social media, make podcasts, or write about current affairs online could be classified as Digital News Broadcasters. This entails that YouTubers and Instagrammers who receive a share of advertising revenue or monetize their social media presence through affiliate activities will be regulated as Digital News Broadcasters. This includes channels, podcasts, and blogs that cover news and utilise Google AdSense. They must comply with a Programme Code and Advertising Code.
Online content creators who do not provide news or current affairs but provide programming and curated programs beyond a certain threshold will be treated as OTT broadcasters in case they provide content licensed or live through a website or social media platform.
The new version also introduces new obligations for intermediaries and social media intermediaries related to streaming services and digital news broadcasters, and, in contrast to the last version circulated in 2023, the latest also carries provisions targeting online advertising. In the context of streaming services, OTT broadcasting services are no longer a part of the definition of "internet broadcasting services." The definition of OTT broadcasting service has also been revised, allowing content creators who regularly upload their content to social media to be considered as OTT broadcasting services.
The new definition of an 'intermediary' includes social media intermediaries, advertisement intermediaries, internet service providers, online search engines, and online marketplaces.
The new Bill allows the government to prescribe different due diligence guidelines for social media platforms and online advertisement intermediaries and requires all intermediaries to provide appropriate information, including information pertaining to the OTT broadcasters and Digital News Broadcasters on their platform, to the central government to ensure compliance with the act. This entails the liability provisions for social media intermediaries which do not provide information “pertaining to OTT Broadcasters and Digital News Broadcasters” on its platforms for compliance. This suggests that when information is sought about a YouTube, Instagram or X/Twitter user, the platform will need to provide this information to the Indian government.
A new draft bill contains specific provisions governing ‘Online Advertising’ and to do so it creates the category of 'advertising intermediaries'. These intermediaries enable the buying or selling of advertisement space on the internet or placing advertisements on online platforms without endorsing the advertisement.
Final Words
The Indian Ministry of Information and Broadcasting (MIB) is making efforts to propose robust regulatory changes to the country's new-age broadcast sector, which would cover the specific provisions for Digital News Broadcasters, OTT Broadcasters and Intermediaries. The proposed bill defining the scope and obligation of each.
However, these changes will have significant implications for press and creative freedom. The changes in the new version of the updated bill from its previous draft expanded the applicability of the bill to a larger number of key actors, this move brought ‘content creators’ under the definition of OTT or digital news broadcasters, which raises concerns about overly rigid provisions and might face criticism from media representative perspectives.
According to recent media reports, the Broadcasting Services (Regulation) Bill, 2024 version has been withdrawn by the I&B ministry facing criticism from relevant stakeholders.
The ministry must take due consideration and feedback from concerned stakeholders and place reliance on balancing individual rights while promoting a healthy regulated landscape considering the needs of the new-age broadcasting sector.
References:
- https://www.medianama.com/2024/07/223-india-broadcast-bill-online-creators/#:~:text=Online%20content%20creators%20that%20do,or%20a%20social%20media%20platform.
- https://www.hindustantimes.com/india-news/new-draft-of-broadcasting-bill-news-influencers-may-be-classified-as-broadcasters-101721961764666.html
- https://www.hindustantimes.com/india-news/broadcasting-bill-still-in-drafting-stage-mib-tells-rs-101722058753083.html
- https://www.newslaundry.com/2024/07/29/indias-new-broadcast-bill-now-has-compliance-requirements-for-youtubers-and-instagrammers
- https://m.thewire.in/article/media/social-media-videos-text-digital-news-broadcasting-bill
- https://mib.gov.in/sites/default/files/Public%20Notice_07.12.2023.pdf
- https://news.abplive.com/news/india/centre-withdraws-draft-of-broadcasting-services-regulation-bill-1709770
