
#FactCheck: False Claims of Fireworks in Dubai International Stadium celebrating India’s Champions Trophy Victory 2025
Executive Summary:
A misleading video claiming to show fireworks at Dubai International Cricket Stadium following India’s 2025 ICC Champions Trophy win has gone viral, causing confusion among viewers. Our investigation confirms that the video is unrelated to the cricket tournament. It actually depicts the fireworks display from the December 2024 Arabian Gulf Cup opening ceremony at Kuwait’s Jaber Al-Ahmad Stadium. This incident underscores the rapid spread of outdated or misattributed content, particularly in relation to significant sports events, and highlights the need for vigilance in verifying such claims.
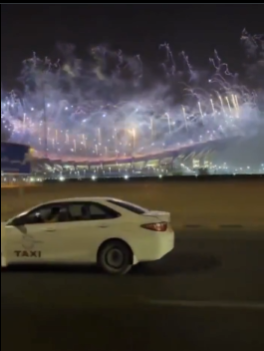
Claim:
The circulated video claims fireworks and a drone display at Dubai International Cricket Stadium after India's win in the ICC Champions Trophy 2025.

Fact Check:
A reverse image search of the most prominent keyframes in the viral video led it back to the opening ceremony of the 26th Arabian Gulf Cup, which was hosted by Jaber Al-Ahmad International Stadium in Kuwait on December 21, 2024. The fireworks seen in the video correspond to the imagery in this event. A second look at the architecture of the stadium also affirms that the venue is not Dubai International Cricket Stadium, as asserted. Additional confirmation from official sources and media outlets verifies that there was no such fireworks celebration in Dubai after India's ICC Champions Trophy 2025 win. The video has therefore been misattributed and shared with incorrect context.

Fig: Claimed Stadium Picture

Conclusion:
A viral video claiming to show fireworks at Dubai International Cricket Stadium after India's 2025 ICC Champions Trophy win is misleading. Our research confirms the video is from the December 2024 Arabian Gulf Cup opening ceremony at Kuwait’s Jaber Al-Ahmad Stadium. A reverse image search and architectural analysis of the stadium debunk the claim, with official sources verifying no such celebration took place in Dubai. The video has been misattributed and shared out of context.
- Claim: Fireworks in Dubai celebrate India’s Champions Trophy win.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

Introduction
Phishing as a Service (PhaaS) platform 'LabHost' has been a significant player in cybercrime targeting North American banks, particularly financial institutes in Canada. LabHost offers turnkey phishing kits, infrastructure for hosting pages, email content generation, and campaign overview services to cybercriminals in exchange for a monthly subscription. The platform's popularity surged after introducing custom phishing kits for Canadian banks in the first half of 2023.Fortra reports that LabHost has overtaken Frappo, cybercriminals' previous favorite PhaaS platform, and is now the primary driving force behind most phishing attacks targeting Canadian bank customers.
In the digital realm, where the barriers to entry for nefarious activities are crumbling, and the tools of the trade are being packaged and sold with the same customer service one might expect from a legitimate software company. This is the world of Phishing-as-a-Service (PhaaS), and at the forefront of this ominous trend is LabHost, a platform that has been instrumental in escalating attacks on North American banks, with a particular focus on Canadian financial institutions.
LabHost is not a newcomer to the cybercrime scene, but its ascent to infamy was catalyzed by the introduction of custom phishing kits tailored for Canadian banks in the first half of 2023. The platform operates on a subscription model, offering turnkey solutions that include phishing kits, infrastructure for hosting malicious pages, email content generation, and campaign overview services. For a monthly fee, cybercriminals are handed the keys to a kingdom of deception and theft.
Emergence of Labhost
The rise of LabHost has been meticulously chronicled by various cyber security firms which reports that LabHost has dethroned the previously favored PhaaS platform, Frappo. LabHost has become the primary driving force behind the majority of phishing attacks targeting customers of Canadian banks. Despite suffering a disruptive outage in early October 2023, LabHost has rebounded with vigor, orchestrating several hundreds of attacks per month.
Their investigation into LabHost's operations reveals a tiered membership system: Standard, Premium, and World, with monthly fees of $179, $249, and $300, respectively. Each tier offers an escalating scope of targets, from Canadian banks to 70 institutions worldwide, excluding North America. The phishing templates provided by LabHost are not limited to financial entities; they also encompass online services like Spotify, postal delivery services like DHL, and regional telecommunication service providers.
LabRat
The true ingenuity of LabHost lies in its integration with 'LabRat,' a real-time phishing management tool that enables cybercriminals to monitor and control an active phishing attack. This tool is a linchpin in man-in-the-middle style attacks, designed to capture two-factor authentication codes, validate credentials, and bypass additional security measures. In essence, LabRat is the puppeteer's strings, allowing the phisher to manipulate the attack with precision and evade the safeguards that are the bulwarks of our digital fortresses.
LabSend
In the aftermath of its October disruption, LabHost unveiled 'LabSend,' an SMS spamming tool that embeds links to LabHost phishing pages in text messages. This tool orchestrates a symphony of automated smishing campaigns, randomizing portions of text messages to slip past the vigilant eyes of spam detection systems. Once the SMS lure is cast, LabSend responds to victims with customizable message templates, a Machiavellian touch to an already insidious scheme.
The Proliferation of PhaaS
The proliferation of PhaaS platforms like LabHost, 'Greatness,' and 'RobinBanks' has democratized cybercrime, lowering the threshold for entry and enabling even the most unskilled hackers to launch sophisticated attacks. These platforms are the catalysts for an exponential increase in the pool of threat actors, thereby magnifying the impact of cybersecurity on a global scale.
The ease with which these services can be accessed and utilized belies the complexity and skill traditionally required to execute successful phishing campaigns. Stephanie Carruthers, who leads an IBM X-Force phishing research project, notes that crafting a single phishing email can consume upwards of 16 hours, not accounting for the time and resources needed to establish the infrastructure for sending the email and harvesting credentials.
PhaaS platforms like LabHost have commoditized this process, offering a buffet of malevolent tools that can be customized and deployed with a few clicks. The implications are stark: the security measures that businesses and individuals have come to rely on, such as multi-factor authentication (MFA), are no longer impenetrable. PhaaS platforms have engineered ways to circumvent these defenses, rendering them vulnerable to exploitation.
Emerging Cyber Defense
In the face of this escalating threat, a multi-faceted defense strategy is imperative. Cybersecurity solutions like SpamTitan employ advanced AI and machine learning to identify and block phishing threats, while end-user training platforms like SafeTitan provide ongoing education to help individuals recognize and respond to phishing attempts. However, with phishing kits now capable of bypassing MFA,it is clear that more robust solutions, such as phishing-resistant MFA based on FIDO/WebAuthn authentication or Public Key Infrastructure (PKI), are necessary to thwart these advanced attacks.
Conclusion
The emergence of PhaaS platforms represents a significant shift in the landscape of cybercrime, one that requires a vigilant and sophisticated response. As we navigate this treacherous terrain, it is incumbent upon us to fortify our defenses, educate our users, and remain ever-watchful of the evolving tactics of cyber adversaries.
References
- https://www-bleepingcomputer-com.cdn.ampproject.org/c/s/www.bleepingcomputer.com/news/security/labhost-cybercrime-service-lets-anyone-phish-canadian-bank-users/amp/
- https://www.techtimes.com/articles/302130/20240228/phishing-platform-labhost-allows-cybercriminals-target-banks-canada.htm
- https://www.spamtitan.com/blog/phishing-as-a-service-threat/
- https://timesofindia.indiatimes.com/gadgets-news/five-government-provided-botnet-and-malware-cleaning-tools/articleshow/107951686.cms
Executive Summary
A 57-second video featuring India’s Chief of Army Staff Upendra Dwivedi is widely circulating on social media. The clip is being shared with the claim that the Army chief admitted India had “betrayed” Iran by providing the location of an Iranian naval ship to Israel, allegedly leading to its destruction The video is spreading amid heightened tensions in West Asia involving United States, Israel, and Iran. According to posts sharing the claim, the Iranian naval vessel IRIS Dena, which had participated in a naval event in Visakhapatnam and was returning to Iran with around 130 personnel onboard, was torpedoed by a US submarine near the southern coast of Sri Lanka on March 4 while sailing in the Indian Ocean.
In the viral clip, the speaker—presented as the Indian Army chief—appears to say that India informed Israel about the exact location of the Iranian ship after it left Indian waters, describing Israel as a strategic ally and suggesting that the attack occurred in international waters. The clip also claims that India had no direct involvement in the alleged joint US-Israel torpedo strike.
However, research conducted by the CyberPeace found the claim to be false. Our research shows that the video does not contain a genuine statement from Army Chief Upendra Dwivedi and is in fact a manipulated clip.
Claim
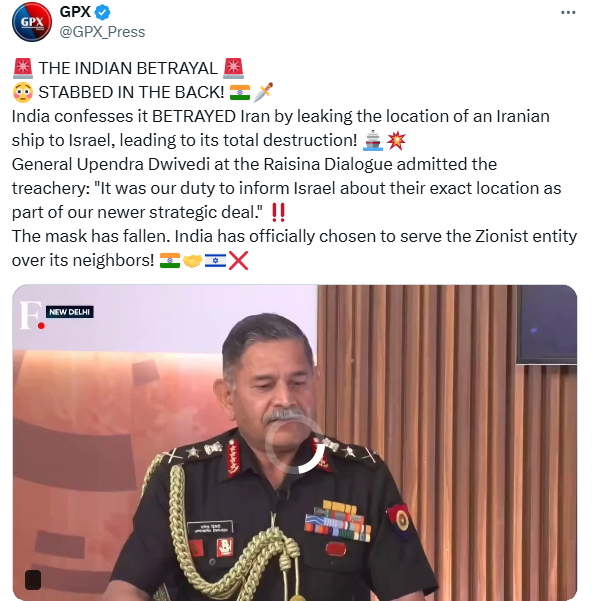
On X (formerly Twitter), a page named GPX (@GPX_Press) shared the video on March 9 with the caption: “India confesses it BETRAYED Iran by leaking the location of an Iranian ship to Israel, leading to its total destruction!”
Fact Check
During the verification process, researchers noticed a ticker in the viral video reading “Raisina Dialogue 2026 × Firstpost.” Using this clue, we conducted a keyword search on YouTube and located a video uploaded by Firstpost on March 7 titled “India’s Army Chief Speaks on Op Sindoor, Pakistan and Future of Warfare | Raisina Dialogue 2026.”
In the 21-minute interview, Army Chief Upendra Dwivedi is seen speaking with strategic affairs expert Harsh V. Pant. According to the video description, the discussion focuses on lessons from Operation Sindoor and the evolving nature of modern warfare.

The viral clip appears to be taken from this interview. However, throughout the conversation, Dwivedi does not mention any conflict involving the United States, Israel, and Iran, nor does he refer to the sinking of an Iranian naval ship in the Indian Ocean. This indicates that the circulating clip has been edited and misrepresented to create a misleading narrative.
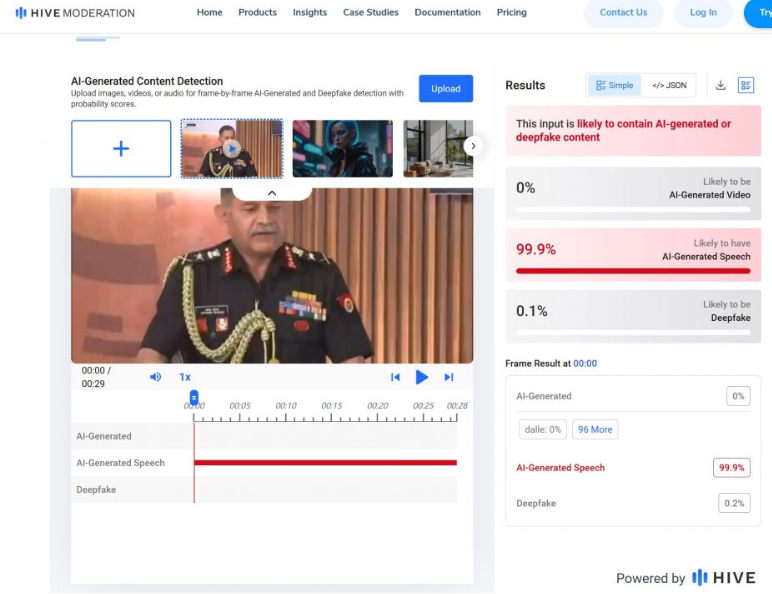
For additional verification, the viral video was analyzed using the AI detection tool Hive Moderation. The results suggested a 99.9% probability that the speech in the clip was generated using AI, indicating manipulation of the original footage.
Conclusion
The research makes it clear that the viral video does not reflect an authentic statement by India’s Army Chief Upendra Dwivedi. The clip has been altered and the audio appears to be AI-generated. In other words, the circulating video is a deepfake being shared with a misleading claim.

Introduction
In India, the population of girls and adolescents is 253 million, as per the UNICEF report, and the sex ratio at birth is 929 per 1000 male children as of 2023. Cyberspace has massively influenced the daily aspects of our lives, and hence the safety aspect of cyberspace cannot be ignored any more. The social media platforms play a massive role in information dissemination and sharing. The data trail created by the use of such platforms is often used by cyber criminals to target innocent girls and children.
On Ground Stats
Of the six million crimes police in India recorded between 1 January and 31 December last year, 428,278 cases involved crimes against women. It’s a rise of 26.35% over six years – from 338,954 cases in 2016. A majority of the cases in 2021, the report said, were of kidnappings and abduction, rapes, domestic violence, dowry deaths and assaults. Also, 107 women were attacked with acid, 1,580 women were trafficked, 15 girls were sold, and 2,668 were victims of cybercrimes. With more than 56,000 cases, the northern state of Uttar Pradesh, which is India’s most populous with 240 million people, once again topped the list. Rajasthan followed it with 40,738 cases and Maharashtra with 39,526 cases. This shows the root of the problem and how deep this menace goes in our society. With various campaigns and initiatives by Government and the CSO, awareness is on the rise, but still, we need a robust prevention mechanism to address this issue critically.
Influence of Social Media Platforms
Social media platforms such as Facebook, Instagram and Twitter were created to bring people closer by eliminating geographical boundaries, which is strengthened by the massive internet connectivity network across the globe. Throughout 2022, on average, there are about 470.1 million active social media users in India on a monthly basis, with an annual growth rate of 4.2 % in 2021-22. This represents about 33.4 % of the total population. These social media users, on average, spend about 2.6 hours on social media, and each, on average, has accounts on 8.6 platforms.
The bad actors have also upskilled themselves and are now using these social platforms to commit cybercrimes. Some of these crimes against girls and women include – Impersonation, Identity theft, Cyberstalking, Cyber-Enabled human trafficking and many more. These crimes are on the rise post-pandemic, and instances of people using fake IDs to lure young girls into their traps are being reported daily. One such instance is when Imran Mansoori created an Instagram account in the name of Rahul Gujjar, username: rahul_gujjar_9010. Using social engineering and scoping out the vulnerabilities, he trapped a minor girl in a relationship & took her to a hotel in Moradabad. The hotel manager raised the suspicion of seeing a different ID & called the Police, Imran was then arrested. But many such crimes go unreported, and it is essential for all stakeholders to create a safeguard regarding girls’ and women’s safety.
Legal Remedies at our disposal
The Indian Legal system has been evolving with time towards the online safety of girls and women. The National Commission for Protection of Child Rights (NCPCR) and the National Commission for Women (NCW) have worked tirelessly to safeguard girls and women to create a wholesome, safe, secure environment. The Information Technology Act governs cyberspace and its associated rights and duties. The following provisions of the IT Act are focused towards safeguarding the rights –
- Violation of privacy – Section 66E
- Obscene material – Section 67
- Pornography & sexually explicit act – Section 67A
- Child pornography – Section 67B
- Intermediaries due diligence rules – Section 79
Apart from these provisions, acts like POCSO, IPC, and CrPC, draft the Digital Personal Data Protection Bill, Intermediary Guidelines on Social Media and Online Gaming and telecommunications bill.
Conclusion
The likelihood of becoming a victim of cybercrime is always growing due to increased traffic in the virtual world, which is especially true for women who are frequently viewed as easy targets. The types of cyber crimes that target women have grown, and the trend has not stopped in India. Cyber flaming, cyber eve-teasing, cyber flirting, and internet cheating are some new-generation crimes that are worth mentioning here. In India, women tend to be reluctant to speak up about issues out of concern that doing so might damage their reputations permanently. Without being fully aware of the dangers of the internet, women grow more susceptible the more time they spend online. Women should be more alert to protect themselves from targeted online attacks.
