
#FactCheck- Claim of Paper Currency Being Discontinued from June 30 Along with AI-Generated Audio of PM Modi Goes Viral
Executive Summary
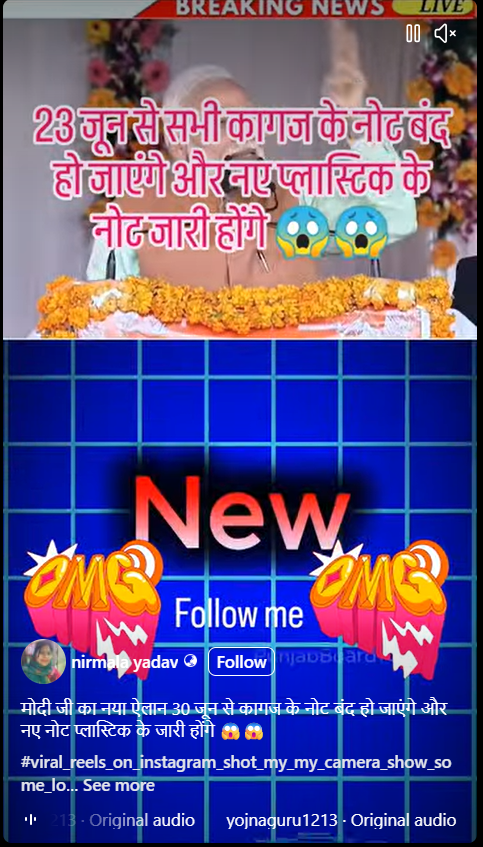
A post is being widely circulated on social media claiming that paper currency will be discontinued in the country from June 30 and replaced with new plastic notes. The claim is being shared along with an audio clip purportedly featuring Prime Minister Narendra Modi, warning people that paper notes will no longer be valid after June 30 and that new plastic currency will be introduced in the market.CyberPeace Research Wing research found the claim to be false. The viral post about discontinuation of paper currency from June 30 is baseless, and the audio attributed to the Prime Minister has been generated using artificial intelligence.
Claim:
An X (formerly Twitter) user shared the viral post claiming that paper currency will be completely withdrawn from circulation in India from June 30 and replaced with plastic notes. The post includes an audio clip allegedly featuring PM Modi.
Post link and archive link can be seen below:
https://www.facebook.com/reel/2172216560209848
Factcheck
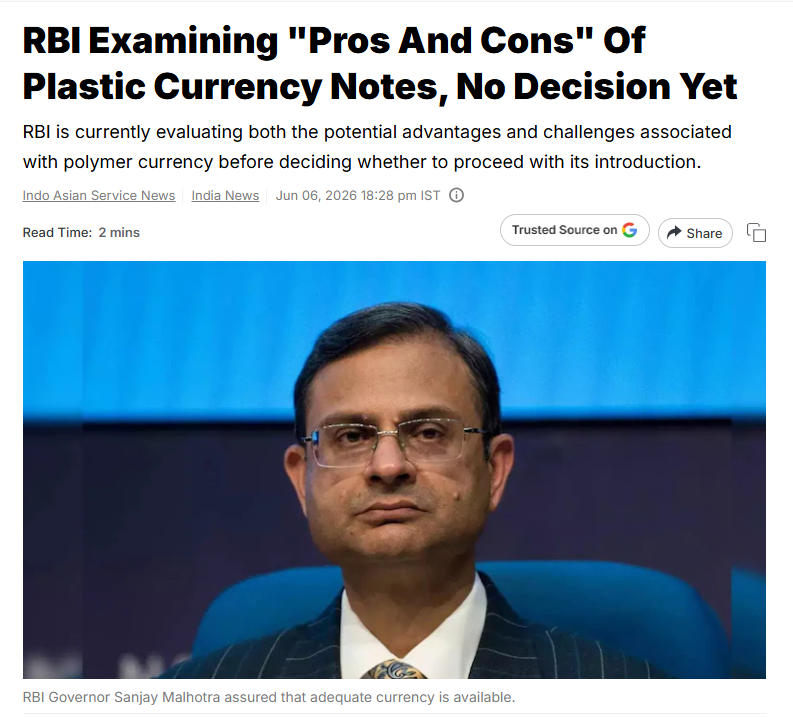
To verify the claim, we conducted a keyword search online. During the research, we found a report published by NDTV on June 6, which stated that the Reserve Bank of India (RBI) is currently examining a proposal related to polymer-based (plastic) currency notes. The report clarified that the proposal is at a very preliminary stage and no final decision has been made. RBI Governor Sanjay Malhotra stated that the central bank is evaluating the pros and cons of polymer notes and will inform the public once any decision is taken. The report does not mention any discontinuation of existing paper currency.
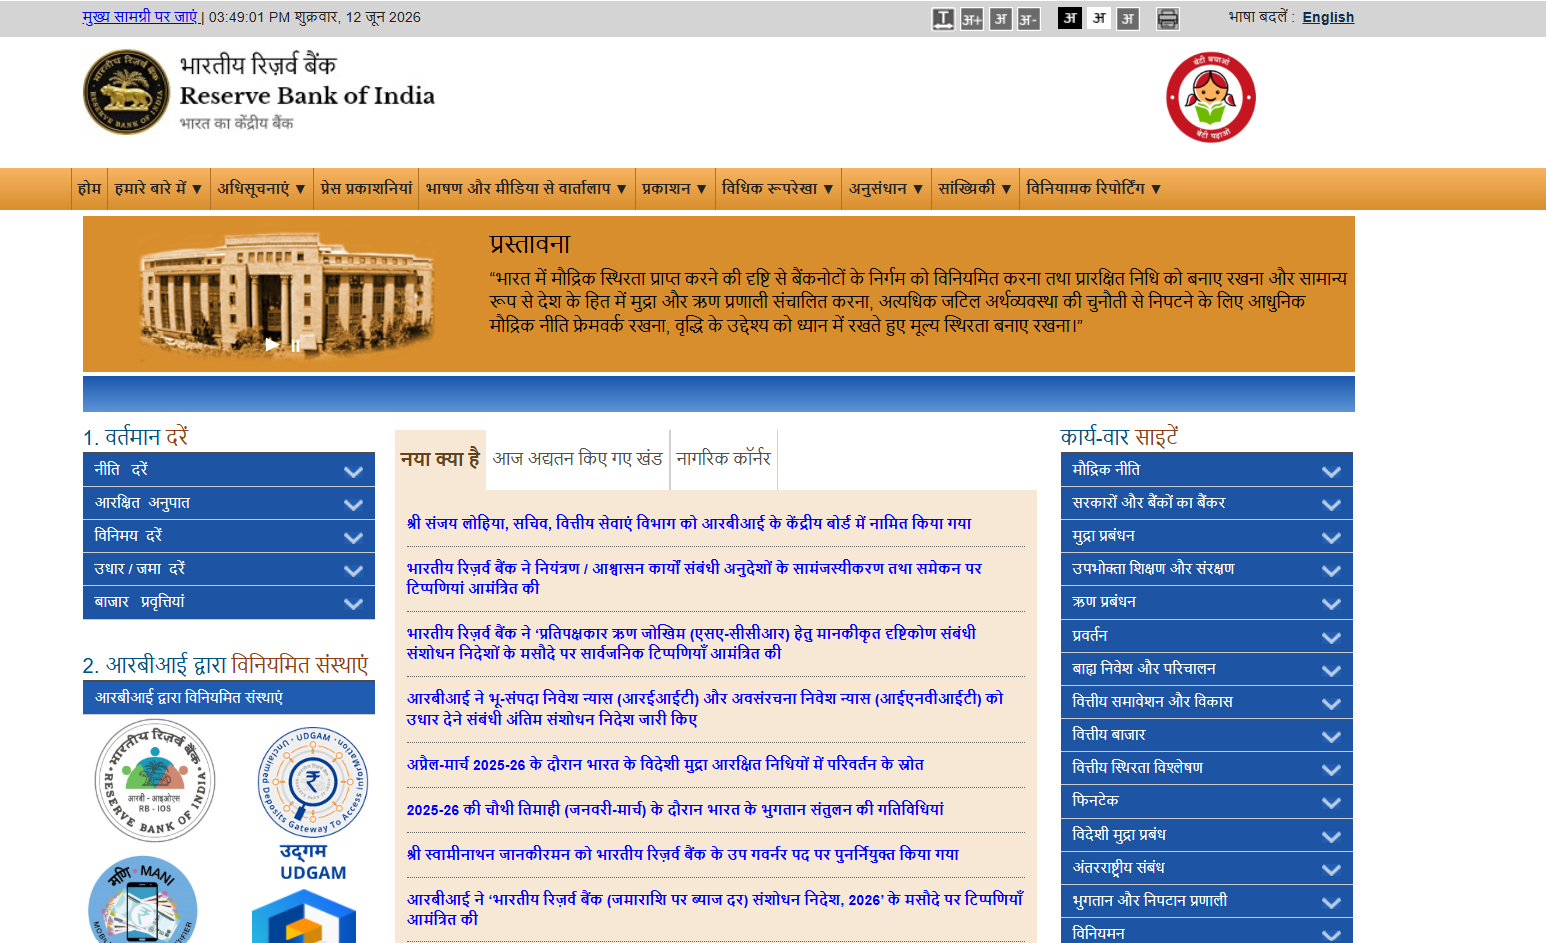
We also checked official sources, including the Prime Minister’s social media handles and the Reserve Bank of India website, but found no announcement or notification regarding the discontinuation of paper currency from June 30.
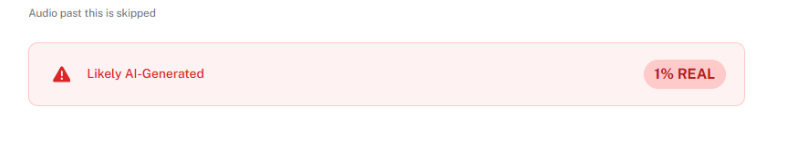
Since the claim included an audio clip attributed to PM Modi, we analyzed it using AI voice detection tools. The Undetectable AI tool identified the voice with 99% probability as AI-generated.
Conclusion:
The research clearly shows that the claim about discontinuation of paper currency from June 30 is baseless. The audio attributed to Prime Minister Narendra Modi is also AI-generated and does not represent any official statement.

Related Blogs

What is Juice Jacking?
We all use different devices during the day, but they converge to a common point when the battery runs out, the cables and adaptors we use to charge the devices are daily necessities for everyone. These cables and adaptors have access to the only port in the phones and hence are used for juice-jacking attacks. Juice jacking is when someone installs malware or spyware software in your device using an unknown charging port or cable.
How does juice jacking work?
We all use phones and gadgets, like I-phones, smartphones, Android devices: and smartwatches, to simplify our lives. But one thing common in it is the charging cables or USB ports, as the data and power supply pass through the same port/cable.
This is potentially a problem with devastating consequences. When your phone connects to another device, it pairs with it (ports/cables) and establishes a trusted relationship. That means the devices can exchange data. During the charging process, the USB cord opens a path into your device that a cybercriminal can exploit.
There is a default setting in the phones where data transfer is disabled, and the connections which provide the power are visible at the end. For example, in the latest models, when you plug your device into a new port or a computer, a question is pooped asking whether the device is trusted. The device owner cannot see what the USB port connects to in case of juice jacking. So, if you plug in your phone and someone checks on the other end, they may be able to transfer data between your device and theirs, thus leading to a data breach.
A leading airline was recently hacked into, which caused delayed flights across the country. When investigated, it was found that malware was planted in the system by using a USB port, which allowed the hackers access to critical data to launch their malware attack.
FBI’s Advisory
Federal Bureau of Investigation and other Interpol agencies have been very critical of cybercriminals. Inter-agency cooperation has improved the pace of investigation and chances of apprehending criminals. In a tweet by the FBI, the issue of Juice Jakcking was addressed, and public places like airports, railways stations, shopping malls etc., are pinpointed places where such attacks have been seen and reported. These places offer easy access to charging points for various devices, which are the main targets for bad actors. The FBI advises people not to use the charging points and cables at airports, railways stations and hotels and also lays emphasis upon the importance of carrying your own cable and charger.
Tips to protect yourself from juice jacking
There are a few simple and effective tips to keep your smart devices smart, such as –
- Avoid using public charging stations: The best way to protect yourself and your devices is to avoid public charging stations it’s always a good habit to charge your phones in your car, at home, and in offices when not in use.
- Using a wall outlet is a safer option: If it’s too urgent for you to use a public station, try to use wall outlets rather than poles because data can’t get easily transferred.
- Use other methods/modes of charging: If you are travelling, carrying a power bank is always safe, as it is easy to carry.
- Software security: – It’s always advised to update your phone’s software regularly. Once connected to the charging station, lock your device. This will prevent it from syncing or transferring data.
- Enable Airplane mode while charging: If you need to charge your phone from an unknown source in a public area, it is advisable to put the phone on airplane mode or switch it off to prevent anyone from gaining access to your device through any open network.
However, many mobile phones (including iPhones) turn on automatically when connected to power. As a result, your mileage may vary. This is an effective safeguard if your phone does not turn on automatically when connected to power.
Conclusion
As of present, juice-jacking attacks are less frequent. While not the most common type of attack today, the number of occurrences is expected to rise as smartphone gadget usage and penetration are rising across the globe. Our cyber safety and security are in our hands, and hence protecting them is our paramount digital duty. Always remember we see no harm in charging ports, but that doesn’t mean that the possibility of a threat can be ruled out completely. With the increased use of ports for charging, earphones, and data transfer, such crimes will continue and evolve with time. Thus, it is essential to counter these attacks by sharing knowledge and awareness of such crimes and reporting them to competent authorities to eradicate the menace of cybercriminals from our digital ecosystem.

Introduction
Recently the attackers employed the CVE-2017-0199 vulnerability in Microsoft Office to deliver a fileless form of the Remcos RAT. The Remcos RAT makes the attacker have full control of the systems that have been infected by this malware. This research will give a detailed technical description of the identified vulnerability, attack vector, and tactics together with the practical steps to counter the identified risks.
The Targeted Malware: Remcos RAT
Remcos RAT (Remote Control & Surveillance) is a commercially available remote access tool designed for legitimate administrative use. However, it has been widely adopted by cybercriminals for its stealth and extensive control capabilities, enabling:
- System control and monitoring
- Keylogging
- Data exfiltration
- Execution of arbitrary commands
The fileless variant utilised in this campaign makes detection even more challenging by running entirely in system memory, leaving minimal forensic traces.
Attack Vector: Phishing with Malicious Excel Attachments
The phishing email will be sent which appears as legitimate business communication, such as a purchase order or invoice. This email contains an Excel attachment that is weaponized to exploit the CVE-2017-0199 vulnerability.
Technical Analysis: CVE-2017-0199 Exploitation
Vulnerability Assessment
- CVE-2017-0199 is a Remote Code Execution (RCE) vulnerability in Microsoft Office which uses Object Linking and Embedding (OLE) objects.
- Affected Components:some text
- Microsoft Word
- Microsoft Excel
- WordPad
- CVSS Score: 7.8 (High Severity)
Mechanism of Exploitation
The vulnerability enables attackers to craft a malicious document when opened, it fetches and executes an external payload via an HTML Application (HTA) file. The execution process occurs without requiring user interaction beyond opening the document.
Detailed Exploitation Steps
- Phishing Email and Malicious Document some text
- The email contains an Excel file designed to make use of CVE-2017-0199.
- When the email gets opened, the document automatically connects to a remote server (e.g., 192.3.220[.]22) to download an HTA file (cookienetbookinetcache.hta).
- Execution via mshta.exe some text
- The downloaded HTA file is executed using mshta.exe, a legitimate Windows process for running HTML Applications.
- This execution is seamless and does not prompt the user, making the attack stealthy.
- Multi-Layer Obfuscation some text
- The HTA file is wrapped in several layers of scripting, including: some text
- JavaScript
- VBScript
- PowerShell
- This obfuscation helps evade static analysis by traditional antivirus solutions.
- The HTA file is wrapped in several layers of scripting, including: some text
- Fileless Payload Deployment some text
- The downloaded executable leverages process hollowing to inject malicious code into legitimate system processes.
- The Remcos RAT payload is loaded directly into memory, avoiding the creation of files on disk.
Fileless Malware Techniques
1. Process Hollowing
The attack replaces the memory of a legitimate process (e.g., explorer.exe) with the malicious Remcos RAT payload. This allows the malware to:
- Evade detection by blending into normal system activity.
- Run with the privileges of the hijacked process.
2. Anti-Analysis Techniques
- Anti-Debugging: Detects the presence of debugging tools and terminates malicious processes if found.
- Anti-VM and Sandbox Evasion: Ensures execution only on real systems to avoid detection during security analysis.
3. In-Memory Execution
- By running entirely in system memory, the malware avoids leaving artifacts on the disk, making forensic analysis and detection more challenging.
Capabilities of Remcos RAT
Once deployed, Remcos RAT provides attackers with a comprehensive suite of functionalities, including:
- Data Exfiltration: some text
- Stealing system information, files, and credentials.
- Remote Execution: some text
- Running arbitrary commands, scripts, and additional payloads.
- Surveillance: some text
- Enabling the camera and microphone.
- Capturing screen activity and clipboard contents.
- System Manipulation: some text
- Modifying Windows Registry entries.
- Controlling system services and processes.
- Disabling user input devices (keyboard and mouse).
Advanced Phishing Techniques in Parallel Campaigns
1. DocuSign Abuse
Attackers exploit legitimate DocuSign APIs to create authentic-looking phishing invoices. These invoices can trick users into authorising payments or signing malicious documents, bypassing traditional email security systems.
2. ZIP File Concatenation
By appending multiple ZIP archives into a single file, attackers exploit inconsistencies in how different tools handle these files. This allows them to embed malware that evades detection by certain archive managers.
Broader Implications of Fileless Malware
Fileless malware like Remcos RAT poses significant challenges:
- Detection Difficulties: Traditional signature-based antivirus systems struggle to detect fileless malware, as there are no static files to scan.
- Forensic Limitations: The lack of disk artifacts complicates post-incident analysis, making it harder to trace the attack's origin and scope.
- Increased Sophistication: These campaigns demonstrate the growing technical prowess of cybercriminals, leveraging legitimate tools and services for malicious purposes.
Mitigation Strategies
- Patch Management some text
- It is important to regularly update software to address known vulnerabilities like CVE-2017-0199. Microsoft released a patch for this vulnerability in April 2017.
- Advanced Email Security some text
- It is important to implement email filtering solutions that can detect phishing attempts, even those using legitimate services like DocuSign.
- Endpoint Detection and Response (EDR)some text
- Always use EDR solutions to monitor for suspicious behavior, such as unauthorized use of mshta.exe or process hollowing.
- User Awareness and Training some text
- Educate users about phishing techniques and the risks of opening unexpected attachments.
- Behavioral Analysis some text
- Deploy security solutions capable of detecting anomalous activity, even if no malicious files are present.
Conclusion
The attack via CVE-2017-0199 further led to the injection of a new fileless variant of Remcos RAT, proving how threats are getting more and more sophisticated. Thanks to the improved obfuscation and the lack of files, the attackers eliminate all traditional antiviral protection and gain full control over the infected computers. It is real and organisations have to make sure that they apply patches on time, that they build better technologies for detection and that the users themselves are more wary of the threats.
References
- Fortinet FortiGuard Labs: Analysis by Xiaopeng Zhang
- Perception Point: Research on ZIP File Concatenation
- Wallarm: DocuSign Phishing Analysis
- Microsoft Security Advisory: CVE-2017-0199

Introduction
Meta Platforms is experiencing a long-term surge of lawsuits that not only question particular practices, but also the very design and governance of its platforms, across the United States and beyond. This range of privacy breaches to youth mental health damages and antitrust issues are all indicative of a new era of judicial, regulatory, and civil society scrutiny of the duties of big tech firms. The main question is no longer whether harmful content is placed on platforms, but to what extent they are actively creating harm-producing environments.
From Content to Conduct: A Turning Point in Legal Strategy
Over the years, Meta and other sites have depended on legal safeguards like the US Communications Decency Act, Section 230, which protects companies against liability due to user-created content. New ways of testing that protection are now being tried.
Recent incidents have shifted off the blame of particular content and has placed the emphasis on the design of the platform. Courts are becoming more receptive to consider whether the characteristics of infinite scroll, algorithmic amplification, and engagement-based ranking systems are contributing to quantifiable harm.
In March 2026, a California jury declared that Meta and Google were negligent in creating platforms that led to youth addiction and mental health problems. The jury decided that Meta and Google were to pay off a joint sum of 6 million dollars in damages, with 70 percent of the sum being charged on Meta. It is a bellwether case, which means that it is related to about 2,000 other pending cases by parents and school districts. This change is important as it avoids legal barriers. When the liability is linked to the design decisions instead of user-created content, accountability begins to shift.
The Youth Harm Cases: A Big Tobacco Moment
Social media are becoming the subject of increased scrutiny by courts and regulators as products that have quantifiable psychological impacts. The most impactful group of lawsuits against Meta is, perhaps, the one concerning youth mental health.
A day prior to the California verdict, a New Mexico jury ordered Meta to pay $375 million in damages due to failure to safeguard young users against child predators on Instagram and Facebook, and found that the company had lied to consumers about the safety of its products and violated state consumer protection laws.
Similar arguments have been presented in other lawsuits filed by attorneys general in over 30 states, and the cases reflect previous regulatory turning points in other industries such as tobacco. The question that courts are not merely asking is whether there is harm or not. They are questioning whether businesses were aware of creating systems that capitalize on behavioral weaknesses. It has been reported in internal documents and accounts of former employees that Meta made a profit by intentionally turning its platforms into addictions to children, with algorithmic functions tailored to drive users into engagement loops, maximising time on platform to the detriment of wellbeing.
Meta has refuted these characterisations, claiming that teen mental health is multifaceted and cannot be blamed on an individual app. The companies have indicated that they will appeal the verdicts.
Privacy and Data Misuse: An Ongoing Fault Line
Platform design is not the only issue that Meta faces in legal matters. Cases centered on privacy have been a recurrent problem in the last ten years, and previous cases have claimed that Facebook monitored users even after they have logged out, scanned personal messages, and utilized personal data in a manner that was beyond user expectations. In more recent times, in April 2026, a class action suit was filed claiming that WhatsApp messages were accessed by Meta employees and third-party contractors, despite the long-standing end-to-end encryption guarantees of the platform.
These instances indicate a structural problem that is consistent. Consent mechanisms and privacy policies tend to be out of date with the reality of data use, and the gap between legal compliance and what users actually know or expect.
Antitrust: A Win, But Not a Clean One
One of the legal fronts was Meta all the way. In November 2025, a judge in the US District Court, James Boasberg, declared that Meta was not a social networking monopoly, finding that the FTC did not demonstrate that the acquisitions of Instagram and WhatsApp by the company were against the antitrust law. The decision has since been appealed by the FTC, which continues to argue that "Meta broke our antitrust laws by acquiring Instagram and WhatsApp, and that American consumers have been harmed by it.
The case also demonstrates a significant drawback of the antitrust law as a form of regulation of tech companies. By the time the trial occurred five years after the lawsuit was initiated, the social media market had evolved such that Tik Tok was a major competitor, undermining the market definition claims of the FTC. The structural issue of whether a few platforms are too powerful in the communication of the masses is not answered, although the legal claim in this instance might have been unsuccessful.
Policy Takeaways: What This Means Going Forward
The accumulating number of lawsuits against Meta provides a number of valuable lessons to policymakers.
- Platform design has become a regulatory topic. Laws should go beyond content regulation and deal with the construction of systems. Engagement maximising features can also increase harm, and this trade-off must be governed explicitly.
- Transparency should be mandatory and not discretionary. Privacy policies and disclosures on platforms are usually too complicated or ambiguous. Regulators might be required to make more transparent and standardised disclosures regarding the use of data and the operation of recommendation systems.
- Section 230 safeguards are under reinterpretation. Courts are becoming open to restrict immunity in cases where the harm is associated with the conduct of the platform and not the content of the user. This would redefine the law of all digital platforms, and not only Meta.
- Cross-border coordination is needed. Meta is an international company, yet the regulatory reaction is still divided. This will require more coordination among jurisdictions to guarantee uniform enforcement and to eliminate regulatory arbitrage.
Conclusion
The lawsuits of Meta are not single cases. They are a more general reconsideration of the regulation of digital platforms and the accountability of those responsible when design decisions have harm at scale. In the wider context of the technology ecosystem, the implications are structural. Courts are starting to question not only what is hosted on them, but how they work and why they are constructed in the manner they are.
The age of minimal responsibility is being supplanted by a more challenging requirement: that platforms should foresee, quantify, and alleviate the harms they produce. The result of these cases will not only decide the future of Meta in terms of legal matters. They will influence the regulations of the digital economy in the years to come.
References
- https://www.npr.org/2026/03/25/nx-s1-5746125/meta-youtube-social-media-trial-verdict
- https://www.pbs.org/newshour/show/jury-finds-meta-and-youtube-liable-in-landmark-youth-addiction-case
- https://www.cbsnews.com/news/meta-ftc-whatsapp-instagram/
- https://www.cnbc.com/2026/01/20/ftc-appeals-metaruling-antitrust-instagram-whatsapp.html
- https://www.bbc.com/news/articles/czjw0zgz9zyo
