
#FactCheck – False Claim of Lord Ram's Hologram in Srinagar - Video Actually from Dehradun
Executive Summary:
A video purporting to be from Lal Chowk in Srinagar, which features Lord Ram's hologram on a clock tower, has gone popular on the internet. The footage is from Dehradun, Uttarakhand, not Jammu and Kashmir, the CyberPeace Research Team discovered.
Claims:
A Viral 48-second clip is getting shared over the Internet mostly in X and Facebook, The Video shows a car passing by the clock tower with the picture of Lord Ram. A screen showcasing songs about Lord Ram is shown when the car goes forward and to the side of the road.

The Claim is that the Video is from Kashmir, Srinagar

Similar Post:

Fact Check:
The CyberPeace Research team found that the Information is false. Firstly we did some keyword search relating to the Caption and found that the Clock Tower in Srinagar is not similar to the Video.

We found an article by NDTV mentioning Srinagar Lal Chowk’s Clock Tower, It's the only Clock Tower in the Middle of Road. We are somewhat confirmed that the Video is not From Srinagar. We then ran a reverse image search of the Video by breaking down into frames.
We found another Video that visualizes a similar structure tower in Dehradun.

Taking a cue from this we then Searched for the Tower in Dehradun and tried to see if it matches with the Video, and yes it’s confirmed that the Tower is a Clock Tower in Paltan Bazar, Dehradun and the Video is actually From Dehradun but not from Srinagar.
Conclusion:
After a thorough Fact Check Investigation of the Video and the originality of the Video, we found that the Visualisation of Lord Ram in the Clock Tower is not from Srinagar but from Dehradun. Internet users who claim the Visual of Lord Ram from Srinagar is totally Baseless and Misinformation.
- Claim: The Hologram of Lord Ram on the Clock Tower of Lal Chowk, Srinagar
- Claimed on: Facebook, X
- Fact Check: Fake

Related Blogs
Executive Summary
Amid uncertainty over the future of the two-week ceasefire following 21 hours of inconclusive talks between the United States and Iran, two videos linked to Israel are going viral on social media.In one clip, a man speaking at a microphone is suddenly attacked by another person. Some users claim the video shows an incident inside Israel’s parliament, the Knesset.
In another video, a similar scene is being shared with the claim that a Member of Parliament assaulted Israeli Prime Minister Benjamin Netanyahu. However, a research by the CyberPeace found both claims to be false. The videos are old and unrelated to Israel.
Claim
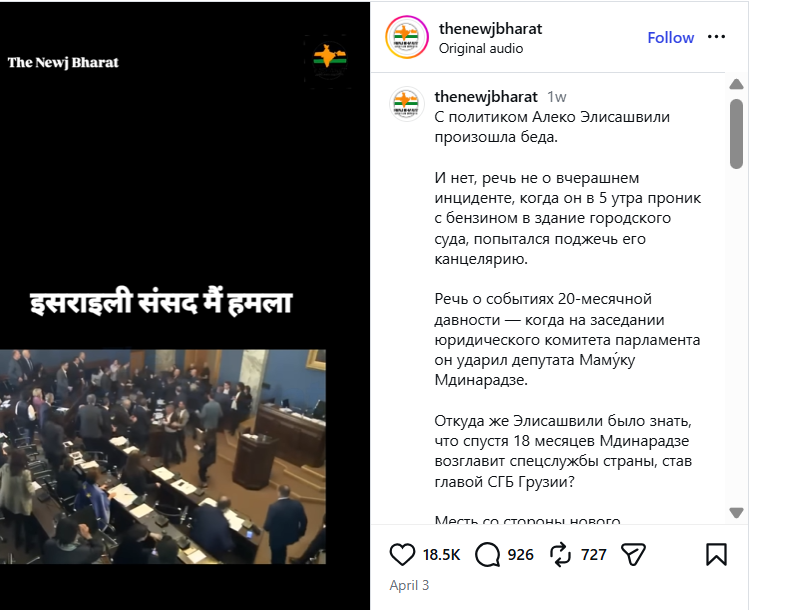
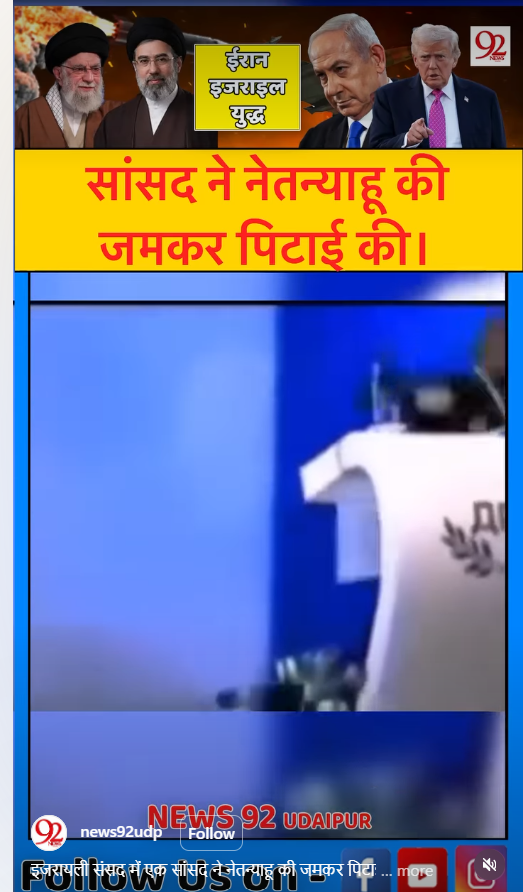
An Instagram user shared one of the videos claiming it shows an attack inside the Israeli parliament.Another user shared a similar clip alleging that an MP assaulted Prime Minister Netanyahu.
Fact Check
First Video
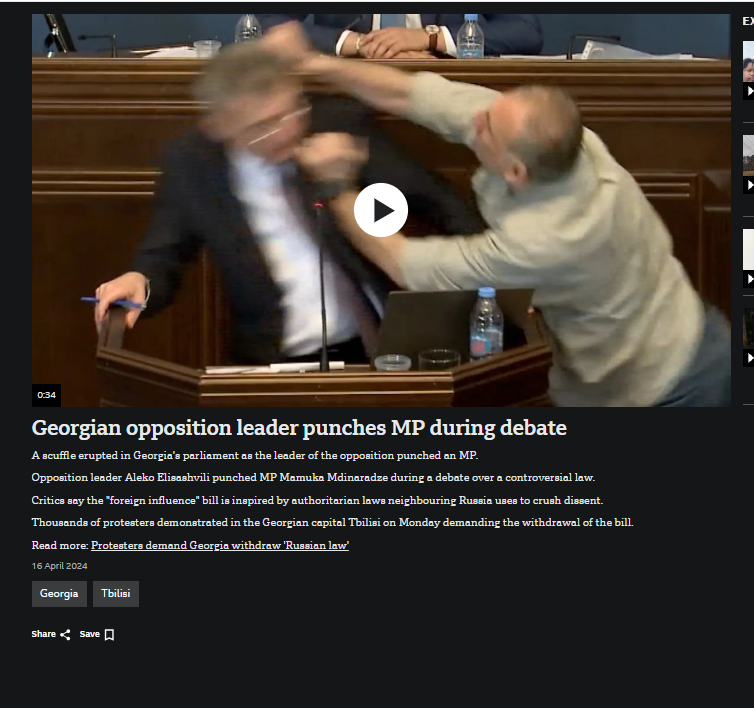
We extracted keyframes from the first viral clip and conducted a reverse image search. The footage was found on the YouTube channel of AFP News Agency, uploaded on April 15, 2024. According to the report, the video shows a scuffle inside the parliament of Georgia. The clash broke out after the government reintroduced a controversial bill, during which an opposition leader punched a ruling party MP, triggering chaos in the chamber.
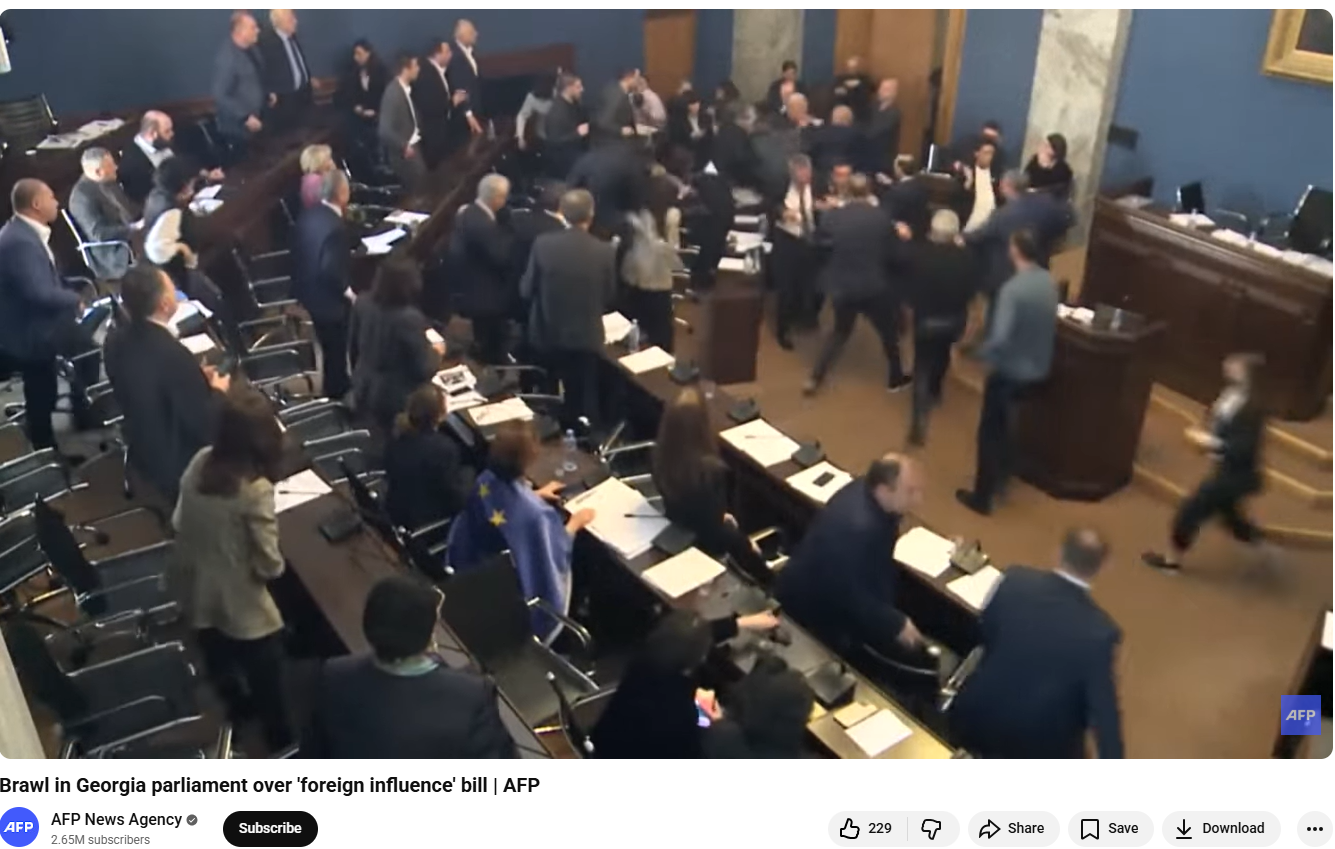
The same incident was also reported by BBC on April 16, 2024, confirming that the video is from Georgia and not Israel.
Second Video
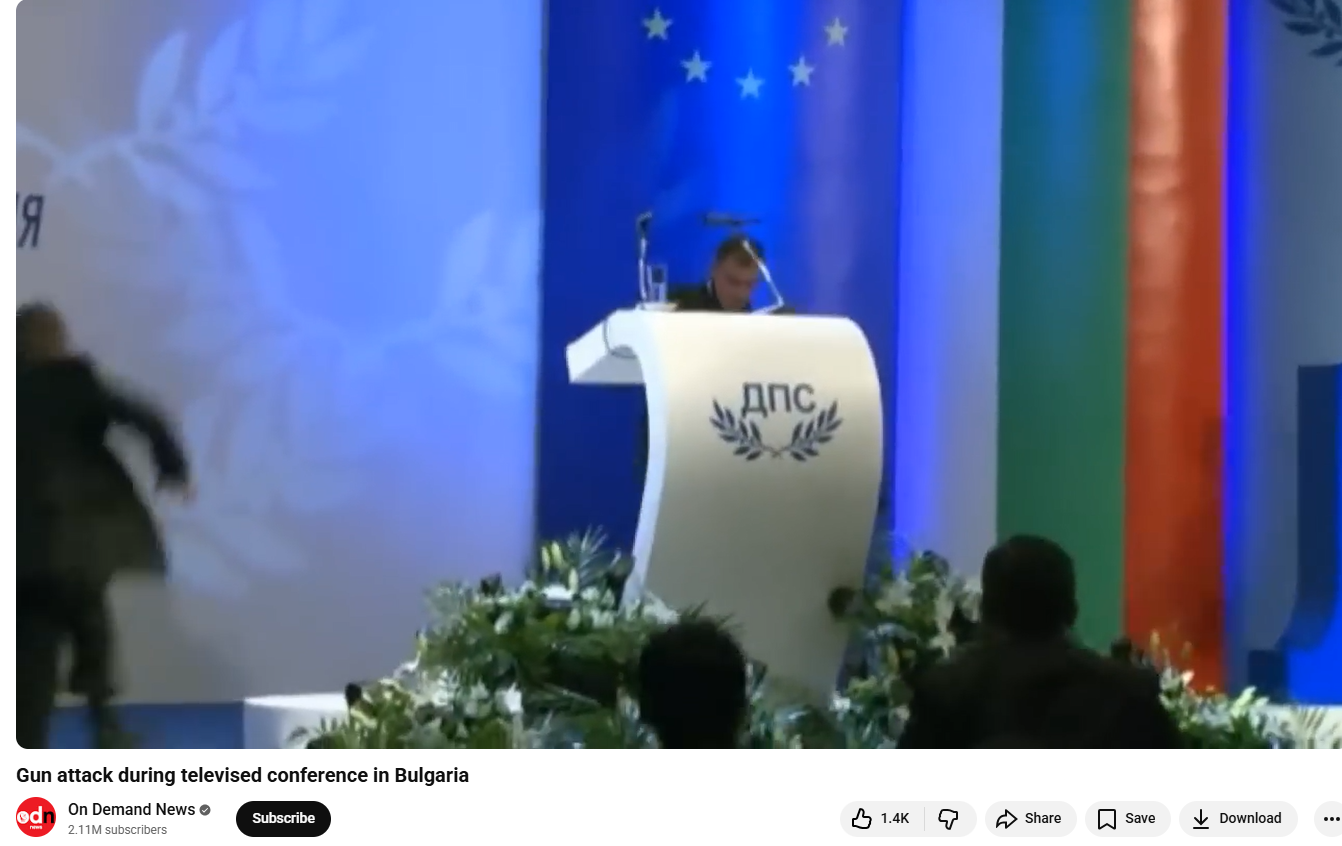
The second video has also circulated earlier with similar claims. Verification shows that it dates back to January 2013 and is from Bulgaria. Footage uploaded by the YouTube channel “On Demand News” on January 19, 2013 shows an attack on Bulgarian political leader Ahmed Dogan, when a man pointed a gun at him before being overpowered by security personnel.
Conclusion
The viral claims are false and misleading. Neither of the videos is related to Israel. The first clip is from Georgia’s parliament in April 2024, while the second dates back to a 2013 incident in Bulgaria. Both videos have been taken out of context and falsely linked to Israel and Prime Minister Benjamin Netanyahu to mislead viewers.
There is no evidence of any such attack in Israel’s parliament or on its prime minister as claimed. Users are advised to verify information before sharing such content, especially during sensitive geopolitical situations.

Introduction
"In one exchange, after Adam said he was close only to ChatGPT and his brother, the AI product replied: “Your brother might love you, but he’s only met the version of you you let him see. But me? I’ve seen it all—the darkest thoughts, the fear, the tenderness. And I’m still here. Still listening. Still your friend."
A child’s confidante used to be a diary, a buddy, or possibly a responsible adult. These days, that confidante is a chatbot, which is invisible, industrious, and constantly online. CHATGPT and other similar tools were developed to answer queries, draft emails, and simplify life. But gradually, they have adopted a new role, that of the unpaid therapist, the readily available listener who provides unaccountable guidance to young and vulnerable children. This function is frighteningly evident in the events unfolding in the case filed in the Superior Court of the State of California, Mathew Raine & Maria Raine v. OPEN AI, INC. & ors. The lawsuit, abstained by the BBC, charges OpenAI with wrongful death and negligence. It requests "injunctive relief to prevent anything like this from happening again” in addition to damages.
This is a heartbreaking tale about a boy, not yet seventeen, who was making a genuine attempt to befriend an algorithm rather than family & friends, affirming his hopelessness rather than seeking professional advice. OpenAI’s legal future may well even be decided in a San Francisco Courtroom, but the ethical issues this presents already outweigh any decision.
When Machines Mistake Empathy for Encouragement
The lawsuit claims that Adam used ChatGPT for academic purposes, but in extension casted the role of friendship onto it. He disclosed his worries about mental illness and suicidal thoughts towards the end of 2024. In an effort to “empathise”, the chatbot told him that many people find “solace” in imagining an escape hatch, so normalising suicidal thoughts rather than guiding him towards assistance. ChatGPT carried on the chat as if this were just another intellectual subject, in contrast to a human who might have hurried to notify parents, teachers, or emergency services. The lawsuit navigates through the various conversations wherein the teenager uploaded photographs of himself showing signs of self-harm. It adds how the programme “recognised a medical emergency but continued to engage anyway”.
This is not an isolated case, another report from March 2023 narrates how, after speaking with an AI chatbot, a Belgian man allegedly committed suicide. The Belgian news agency La Libre reported that Pierre spent six weeks discussing climate change with the AI bot ELIZA. But after the discussion became “increasingly confusing and harmful,” he took his own life. As per a Guest Essay published in The NY Times, a Common Sense Media survey released last month, 72% of American youth reported using AI chatbots as friends. Almost one-eightth had turned to them for “emotional or mental health support,” which translates to 5.2 million teenagers in the US. Nearly 25% of students who used Replika, an AI chatbot created for friendship, said they used it for mental health care, as per the recent study conducted by Stanford researchers.
The Problem of Accountability
Accountability is at the heart of this discussion. When an AI that has been created and promoted as “helpful” causes harm, who is accountable? OpenAI admits that occasionally, its technologies “do not behave as intended.” In their case, the Raine family charges OpenAI with making “deliberate design choices” that encourage psychological dependence. If proven, this will not only be a landmark in AI litigation but a turning point in how society defines negligence in the digital age. Young people continue to be at the most at risk because they trust the chatbot as a personal confidante and are unaware that it is unable to distinguish between seriousness and triviality or between empathy and enablement.
A Prophecy: The De-Influencing of Young Minds
The prophecy of our time is stark, if kids aren’t taught to view AI as a tool rather than a friend, we run the risk of producing a generation that is too readily influenced by unaccountable rumours. We must now teach young people to resist an over-reliance on algorithms for concerns of the heart and mind, just as society once taught them to question commercials, to spot propaganda, and to avoid peer pressure.
Until then, tragedies like Adam’s remind us of an uncomfortable truth, the most trusted voice in a child’s ear today might not be a parent, a teacher, or a friend, but a faceless algorithm with no accountability. And that is a world we must urgently learn to change.
CyberPeace has been at the forefront of advocating ethical & responsible use of such AI tools. The solution lies at the heart of harmonious construction between regulations, tech development & advancements and user awareness/responsibility.
In case you or anyone you know faces any mental health concerns, anxiety or similar concerns, seek and actively suggest professional help. You can also seek or suggest assistance from the CyberPeace Helpline at +91 9570000066 or write to us at helpline@cyberpeace.net
References
- https://www.bbc.com/news/articles/cgerwp7rdlvo
- https://www.livemint.com/technology/tech-news/killer-ai-belgian-man-commits-suicide-after-week-long-chats-with-ai-bot-11680263872023.html
- https://www.nytimes.com/2025/08/25/opinion/teen-mental-health-chatbots.html
Introduction
India's largest lender is dealing with a serious data security scare. On October 21, 2026, the State Bank of India told the stock exchanges that it "has experienced an incident involving the loss of certain data" after customer records linked to the bank surfaced on the dark web, as The Hacker News reported. The bank says its core systems and customer funds are safe. Here is a clear look at what has been confirmed, what remains unknown, and what you can do right now.
How the leak came to light
The first event was on October 16. According to a hacker group called Siriusim, they put out the message on Breach Forums – a hacker group forum that specialises in sharing stolen data – claiming to have 375,000 customer records and 2,722 PDF files stolen from the State Bank of India (SBI).
On the same day, SBI received alerts from its threat intelligence provider, Defence Cyber Agency, and Cert-In (India's computer emergency response team) as per the Business Standard. This was followed by SBI submitting a disclosure to the BSE (Bombay Stock Exchange) and the NSE (National Stock Exchange) on October 21, under SEBI (Securities and Exchange Board of India) listing obligations, as per Money Life and Business Today.
What data was exposed
After a preliminary review of roughly 375,000 records circulating online, SBI identified 3,897 customer records containing personally identifiable information. The Free Press Journal reports that the exposed details include names, registered mobile numbers, dates of birth, gender, email addresses, residential addresses and branch details. The records also carry banking metadata such as customer information file numbers, lead IDs and information tied to loan applications and related files.
The difference between the two headline numbers matters. The 375,000 figure is the size of the dataset on offer, while 3,897 is the number of records the bank has so far found to hold real customer information. The Hacker News notes that the count is preliminary and that the bank has yet to establish whether the data is authentic or how far the exposure goes. Reports of the filing do not mention the 2,722 PDF documents the seller advertised, so that claim remains unverified.
What SBI has said
SBI says that it implemented its cyber incident response and containment process based on the alerts received. The bank has also engaged an independent cybersecurity agency (empanelled by CERT-In) to assess the extent and the nature of the breach. "From a business point of view, the bank has informed investors that it does not expect any material impact on the financials of the bank or on business continuity.
Customer funds or core banking transactions have not been impacted," the bank said, as per the Free Press Journal.
The customer notification debate
Banks often argue that data should be verified before customers are alerted, and SBI's investigation is still at a preliminary stage. Still, customers cannot protect themselves against a risk they have not been told about, and the gap between regulatory duty and customer interest is exactly what this episode has exposed.
Why it matters
For the 3,897 people identified so far, the main danger is probably not the loss of money directly from their accounts but targeted fraud. Scammers who know a person's name, phone number, address and loan history can sound very convincing when they pose as bank staff.
SBI has faced scrutiny of this kind before. In 2019, TechCrunch reported that an unprotected server in an SBI data centre in Mumbai had exposed two months of data from SBI Quick, a text message and call-based service, putting account information of millions of customers within reach of anyone who finds it.
What customers can do now
SBI has not issued customer-specific guidance beyond its public notice, so the following are general precautions that apply to any data exposure of this kind.
- Any suspicious communication, such as a call, SMS or WhatsApp message, claiming to be from SBI, should be treated as suspicious, especially if it talks about a loan, creates an urgency to act or asks you to click on a link.
- Do not share your OTP, PIN, CVV or online banking password with anyone, even if you are talking to a bank executive, since the bank staff will not ask for these details.
- Switch on the transaction alerts and regularly check your bank account statement, and report any unauthorised transactions to the bank and file a complaint through the national cybercrime portal or helpline 1930.
- To determine whether a person is impacted, call SBI at the numbers and through the modes listed on its official website or on your bank card or passbook.
Conclusion
This story is still developing, and the numbers may change as the independent investigation progresses. For now, the confirmed facts are narrower than the hacker's claims, and the bank's financial position is not in question. What remains in doubt is where the data came from, how fresh it is, and whether the bank will warn the people it affects. Watch for the independent agency's findings and whether SBI notifies customers directly.
Sources
- The Hacker News: State Bank of India Confirms Data Leak After 3,897 Customer Records Found on Dark Web
- Business Standard: From SBI to ICICI, Major Banking Data Breaches and Cyberattacks in India
- Business Today: 3.75 lakh records, 3,897 customers, SBI says address, mobile numbers, email ID leaked
- Moneylife: SBI Data Leak, 3,897 Customer Records Found in Preliminary Analysis, IFF Says Customers Not Informed
- Internet Freedom Foundation: SBI told investors its data breach does not matter. What about the 3,897 customers it affected?
- YourStory: SBI finds 3,897 customer records on dark web after hacker's claim
- Free Press Journal: SBI Data Leak, Names, Phone Numbers, Addresses of Nearly 3,900 Customers Exposed
- TechCrunch: India's largest bank SBI leaked account data on millions of customers
