
#Fact Check: Pakistan’s Airstrike Claim Uses Video Game Footage
Executive Summary:
A widely circulated claim on social media, including a post from the official X account of Pakistan, alleges that the Pakistan Air Force (PAF) carried out an airstrike on India, supported by a viral video. However, according to our research, the video used in these posts is actually footage from the video game Arma-3 and has no connection to any real-world military operation. The use of such misleading content contributes to the spread of false narratives about a conflict between India and Pakistan and has the potential to create unnecessary fear and confusion among the public.

Claim:
Viral social media posts, including the official Government of Pakistan X handle, claims that the PAF launched a successful airstrike against Indian military targets. The footage accompanying the claim shows jets firing missiles and explosions on the ground. The video is presented as recent and factual evidence of heightened military tensions.


Fact Check:
As per our research using reverse image search, the videos circulating online that claim to show Pakistan launching an attack on India under the name 'Operation Sindoor' are misleading. There is no credible evidence or reliable reporting to support the existence of any such operation. The Press Information Bureau (PIB) has also verified that the video being shared is false and misleading. During our research, we also came across footage from the video game Arma-3 on YouTube, which appears to have been repurposed to create the illusion of a real military conflict. This strongly indicates that fictional content is being used to propagate a false narrative. The likely intention behind this misinformation is to spread fear and confusion by portraying a conflict that never actually took place.


Conclusion:
It is true to say that Pakistan is using the widely shared misinformation videos to attack India with false information. There is no reliable evidence to support the claim, and the videos are misleading and irrelevant. Such false information must be stopped right away because it has the potential to cause needless panic. No such operation is occurring, according to authorities and fact-checking groups.
- Claim: Viral social media posts claim PAF attack on India
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

Introduction
As various technological developments enable our phones to take on a greater role, these devices, along with the applications they host, also become susceptible to greater risks. Recently, Zimperium, a tech company that provides security services for mobiles and applications from threats like malware, phishing, etc., has announced its identification of a malware that is targeted toward stealing information from Indian Banks. The Indian Express reports that data from over 25 million devices has been exfiltrated, making it increasingly dangerous, just going by the it has affected so far.
Understanding the Threat: The Case of FatBoyPanel
A malware is a malicious software that is a file or a program, intentionally harmful to a network, server, computer, and other devices. It is also of various types; however, in the context of the aforementioned case, it is a Trojan horse i.e., a file/program designed to trick the victim into assuming it to be a legitimate software program that is trying to gain access. They are able to execute malicious functions on a device as soon as they are activated post-installation.
The FatBoyPanel, as it is called, is a malware management system that carried out a massive cyberattack, targeting Indian mobile users and their bank details. Their modus operandi included the process of social engineering, wherein attackers posed as bank officials who called their target and warned them that if no immediate action was taken to update their bank details, their account would be suspended immediately. On panicking and asking for instructions, they were told to download a banking application from the link sent in the form of an Android Package Kit (APK) file (that requires one to enable “Install from Unknown Sources” ) and install it. Various versions of similar incidents were acted on by other attackers, all to trick the target into downloading the file sent. The apps sent through the links are fake, and once installed, they immediately ask for critical permissions such as access to contacts, device storage, overlay permissions (to show fake login pages over real apps), and access to SMS messages (to steal OTPs and banking alerts). This aids in capturing text messages (especially OTPs related to banks), read stored files, monitor app usage, etc. This data is stolen and then sent to the FatBoyPanel backend, where hackers are able to see real-time data on their dashboard, which they can further download and sell. FatBoyPanel is a C&C (command and control) server that acts as a centralised control room.
Protecting Yourself: Essential Precautions in the Digital Realm
Although there are various other types of malware, how one must deal with them remains the same. Following are a few instructions that one can practice in order to stay safe:
- Be cautious with app downloads: Only download apps from official app stores (Google Play Store, Apple App Store). Even then, check the developer's reputation, app permissions, and user reviews before installing.
- Keep your operating system and apps updated: Updates often include security patches that protect against known vulnerabilities.
- Be wary of suspicious links and attachments: Avoid clicking on links or opening attachments in unsolicited emails, SMS messages, or social media posts. Verify the sender's authenticity before interacting.
- Enable multi-factor authentication (MFA) wherever possible: While malware like FatBoyPanel can sometimes bypass OTP-based MFA, it still adds an extra layer of security against many other threats.
- Use strong and unique passwords: Employ a combination of uppercase and lowercase letters, numbers, and symbols for all your online accounts. Avoid reusing passwords across different platforms.
- Install and maintain a reputable mobile security app: These apps can help detect and remove malware, as well as warn you about malicious websites and links (Bitdefender, etc.)
- Regularly review app permissions and give access judiciously: Check what permissions your installed apps have and revoke any that seem unnecessary or excessive.
- Educate yourself and stay informed: Keep up-to-date with the latest cybersecurity threats and best practices.
Conclusion
The emergence of malware management systems indicates just how sophisticated the attackers have become over the years. Vigilance at the level of the general public is recommended, but so are increasing efforts in awareness regarding such methods of crime, as people continue to remain vulnerable in aspects related to cybersecurity. Sensitive information at stake, we must take steps to sensitise and better prepare the public to deal with the growing landscape of the digital world.
References
- https://zimperium.com/blog/mobile-indian-cyber-heist-fatboypanel-and-his-massive-data-breach
- https://indianexpress.com/article/technology/tech-news-technology/fatboypanel-new-malware-targeting-indian-users-what-is-it-9965305/
- https://www.techtarget.com/searchsecurity/definition/malware
Introduction
Parliament is about to begin its Monsoon Session from July 20, 2026 to August 13, 2026, and the mood in Delhi already feels charged. Ahead of the opening bell, the government has flagged five new bills for introduction, alongside a couple of pending pieces of legislation it may take up for passage. Predictably, the political oxygen in the run-up has gone almost entirely to what isn't on that list — reports this week noted the conspicuous absence of the long-anticipated Delimitation Bill and a Constitutional amendment for women's reservation in the Lok Sabha, a gap that has already drawn sharp reactions from Congress leaders. What is on the list has generated its own share of noise: a Foreign Contribution (Regulation) Amendment Bill that NGOs are watching warily, a Prevention of Insults to National Honour (Amendment) Bill tied to safeguards for the National Flag and Anthem, and a Supreme Court (Number of Judges) Amendment Bill proposing to raise the Court's sanctioned strength from 33 to 37. Every one of these will command its share of prime-time debate. But tucked quietly among the five is a bill that, headline for headline, may end up mattering more to the everyday Indian economy than all the others combined: the Micro, Small and Medium Enterprises Development (Amendment) Bill, 2026.
MSMEs play a foundational role in India’s economic engine, powering employment, entrepreneurship and growth across the country. That makes this Bill one worth watching closely, because even seemingly technical changes to the MSME framework could have very real consequences for millions of businesses and the people whose livelihoods depend on them.
What the Bill Actually Does
The MSME sector hasn't seen a structural legal update since the original MSMED Act of 2006 nearly two decades in an economy that looks nothing like it did back then. The new amendment is designed to close that gap. According to the government's own description of the bill, it aims to align the 2006 law with the sector's changed realities, improve ease of doing business, and shift toward what officials are calling "trust-based" regulation rather than a purely compliance-driven approach.
Three provisions stand out.
- First, it strengthens the mechanism for resolving delayed payments to micro and small enterprises, arguably the single biggest complaint MSME owners have voiced for years.
- Second, it creates a pathway to enforce arbitral awards specifically for micro and small units, giving smaller suppliers real teeth when a dispute is decided in their favor.
- Third, it gives states more flexibility in deciding the composition of Micro and Small Enterprises Facilitation Councils (MSEFCs) , the bodies that adjudicate payment disputes which should allow more councils to be formed and cut down on case backlogs.
The Delayed Payment Crisis, in Numbers
To understand why this matters, look at the scale of the problem the bill is trying to fix. The MSME Ministry's Samadhaan portal, which lets small enterprises file delayed-payment complaints online, had received close to 2.57 lakh applications as of June 2026, involving claimed dues of roughly ₹55,244 crore. Of these, only about 58,000 cases had actually been resolved by facilitation councils. That's a resolution rate that leaves the vast majority of small businesses waiting often for money already owed to them for goods or services delivered.
The government did tighten the screws somewhat in 2024 through Section 43B(h) of the Income Tax Act, which denies large buyers a tax deduction if they don't pay MSME suppliers within the 15-to-45-day window mandated by law. Enforcement, however, has remained patchy, and industry bodies like Assocham have continued to flag delayed payments including from PSUs and government departments as a core source of financial stress for small firms, with high interest charges on overdue statutory dues compounding the problem.
Why This Is Bigger Than One Bill
A regulation targeting the payments practices of India's micro, small, and medium-sized enterprises is more than just paperwork and procedural wrangling; the stakes for the Indian economy and society are enormous. According to the 2025-26 Economic Survey, MSMEs now contribute about 31.1% of India’s GDP, 35.4% of its manufacturing output, and 48.58% of its exports, while employing 33 to 39 crore people and providing India’s second largest source of employment after agriculture. The official Udyam database of MSMEs crossed the 8.7 crore mark by June 2026, underscoring a clear trend towards the sector’s formalisation in the last few years. Access to finance is the second pillar of MSME empowerment. The Credit Guarantee Fund Trust for Micro and Small Enterprises has authorised several lakh crores in guarantees, and most recently, the government increased its loan guarantee cover ceiling from Rs 5 crore to Rs 10 crore to facilitate more collateral-free loans to businesses. However, the actual credit gap remains estimated in the tens of lakh crores, with the biggest gaps faced by women-led and medium enterprises. While the MSME Bill doesn’t directly address access to finance, improved and quicker payment settlement mechanisms are expected to relieve some working-capital stress and dissuade small firms from falling into expensive informal credit markets. The MSME Bill also adds to a wave of recent measures to de-regulate smaller enterprises, such as the Jan Vishwas (Amendment of Provisions) Bill that was passed earlier in 2026. That Bill modified or deleted criminal offences with a more lenient civil equivalent across numerous central acts, a change industry lobby FISME called a significant move towards ease of doing business.
The Data Protection Clock Is Already Ticking - The Gap Payment Reform Won't Close
It's also worth noting that India's Digital Personal Data Protection (DPDP) Act, 2023 is now in force, with rules notified in November 2025 and full compliance — including breach notification, security safeguards. With nearly half of Indian small businesses already reporting cyber incidents each year, MSMEs have a narrowing runway to build the security practices this regime will expect of them. Given that scale of exposure, there's a real case for the MSME Amendment Bill, or a companion policy, to go further — mandating baseline cyber-hygiene standards for Udyam-registered firms or tying credit-guarantee schemes to demonstrated security practices. Payment reform alone protects an MSME's right to be paid; it does little to protect what happens to that money, or that data, once it arrives.Payment reform alone protects an MSME's right to be paid; it does little to protect what happens to that money, or that data, once it arrives. CyberPeace calls on relevant agencies to issue clearer advisories and introduce additional, cost-friendly cybersecurity safeguards tailored to MSMEs' limited budgets and IT capacity.
What to Watch For
Whether the MSME Bill gets the attention it deserves during this session is an open question. With the Opposition expected to spend political capital on delimitation, the Vande Mataram bill, unemployment, inflation, and the NEET paper-leak controversy, a technical amendment to an enterprise development law is unlikely to dominate floor debate even though it may end up affecting more households than any single headline bill this session.
Conclusion
For India's roughly 7-8 crore MSMEs, most of them family-run and thinly capitalised, the details that get finalised in the coming weeks how MSEFCs are reconstituted, how arbitral awards get enforced, how "trust-based" regulation is actually defined will matter far more than who wins the argument over delimitation. It's worth watching this one closely, even if the cameras are pointed elsewhere.
Sources
- https://www.business-standard.com/india-news/vande-mataram-bill-among-five-new-legislations-listed-for-monsoon-session-126071601319_1.html
- https://www.prokerala.com/news/articles/a1780267.html

Executive Summary:
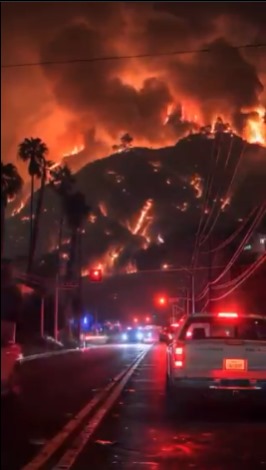
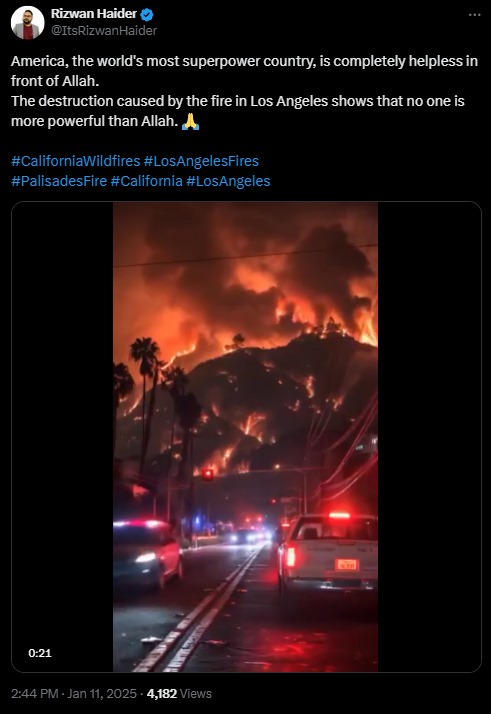
A viral post on X (formerly Twitter) has been spreading misleading captions about a video that falsely claims to depict severe wildfires in Los Angeles similar to the real wildfire happening in Los Angeles. Using AI Content Detection tools we confirmed that the footage shown is entirely AI-generated and not authentic. In this report, we’ll break down the claims, fact-check the information, and provide a clear summary of the misinformation that has emerged with this viral clip.
Claim:
A video shared across social media platforms and messaging apps alleges to show wildfires ravaging Los Angeles, suggesting an ongoing natural disaster.
Fact Check:
After taking a close look at the video, we noticed some discrepancy such as the flames seem unnatural, the lighting is off, some glitches etc. which are usually seen in any AI generated video. Further we checked the video with an online AI content detection tool hive moderation, which says the video is AI generated, meaning that the video was deliberately created to mislead viewers. It’s crucial to stay alert to such deceptions, especially concerning serious topics like wildfires. Being well-informed allows us to navigate the complex information landscape and distinguish between real events and falsehoods.

Conclusion:
This video claiming to display wildfires in Los Angeles is AI generated, the case again reflects the importance of taking a minute to check if the information given is correct or not, especially when the matter is of severe importance, for example, a natural disaster. By being careful and cross-checking of the sources, we are able to minimize the spreading of misinformation and ensure that proper information reaches those who need it most.
- Claim: The video shows real footage of the ongoing wildfires in Los Angeles, California
- Claimed On: X (Formerly Known As Twitter)
- Fact Check: Fake Video
