
Strengthening Online Child Safety: NCPCR Pushes for KYC Age Verification Mechanism
Introduction
India's National Commission for Protection of Child Rights (NCPCR) is set to approach the Ministry of Electronics and Information Technology (MeitY) to recommend mandating a KYC-based system for verifying children's age under the Digital Personal Data Protection (DPDP) Act. The decision to approach or send recommendations to MeitY was taken by NCPCR in a closed-door meeting held on August 13 with social media entities. In the meeting, NCPCR emphasised proposing a KYC-based age verification mechanism. In this background, Section 9 of the Digital Personal Data Protection Act, 2023 defines a child as someone below the age of 18, and Section 9 mandates that such children have to be verified and parental consent will be required before processing their personal data.
Requirement of Verifiable Consent Under Section 9 of DPDP Act
Regarding the processing of children's personal data, Section 9 of the DPDP Act, 2023, provides that for children below 18 years of age, consent from parents/legal guardians is required. The Data Fiduciary shall, before processing any personal data of a child or a person with a disability who has a lawful guardian, obtain verifiable consent from the parent or lawful guardian. Additionally, behavioural monitoring or targeted advertising directed at children is prohibited.
Ongoing debate on Method to obtain Verifiable Consent
Section 9 of the DPDP Act gives parents or lawful guardians more control over their children's data and privacy, and it empowers them to make decisions about how to manage their children's online activities/permissions. However, obtaining such verifiable consent from the parent or legal guardian presents a quandary. It was expected that the upcoming 'DPDP rules,' which have yet to be notified by the Central Government, would shed light on the procedure of obtaining such verifiable consent from a parent or lawful guardian.
However, In the meeting held on 18th July 2024, between MeitY and social media companies to discuss the upcoming Digital Personal Data Protection Rules (DPDP Rules), MeitY stated that it may not intend to prescribe a ‘specific mechanism’ for Data Fiduciaries to verify parental consent for minors using digital services. MeitY instead emphasised obligations put forth on the data fiduciary under section 8(4) of the DPDP Act to implement “appropriate technical and organisational measures” to ensure effective observance of the provisions contained under this act.
In a recent update, MeitY held a review meeting on DPDP rules, where they focused on a method for determining children's ages. It was reported that the ministry is making a few more revisions before releasing the guidelines for public input.
CyberPeace Policy Outlook
CyberPeace in its policy recommendations paper published last month, (available here) also advised obtaining verifiable parental consent through methods such as Government Issued ID, integration of parental consent at ‘entry points’ like app stores, obtaining consent through consent forms, or drawing attention from foreign laws such as California Privacy Law, COPPA, and developing child-friendly SIMs for enhanced child privacy.
CyberPeace in its policy paper also emphasised that when deciding the method to obtain verifiable consent, the respective platforms need to be aligned with the fact that verifiable age verification must be done without compromising user privacy. Balancing user privacy is a question of both technological capabilities and ethical considerations.
DPDP Act is a brand new framework for protecting digital personal data and also puts forth certain obligations on Data Fiduciaries and provides certain rights to Data Principal. With upcoming ‘DPDP Rules’ which are expected to be notified soon, will define the detailed procedure for the implementation of the provisions of the Act. MeitY is refining the DPDP rules before they come out for public consultation. The approach of NCPCR is aimed at ensuring child safety in this digital era. We hope that MeitY comes up with a sound mechanism for obtaining verifiable consent from parents/lawful guardians after taking due consideration to recommendations put forth by various stakeholders, expert organisations and concerned authorities such as NCPCR.
References
- https://www.moneycontrol.com/technology/dpdp-rules-ncpcr-to-recommend-meity-to-bring-in-kyc-based-age-verification-for-children-article-12801563.html
- https://pune.news/government/ncpcr-pushes-for-kyc-based-age-verification-in-digital-data-protection-a-new-era-for-child-safety-215989/#:~:text=During%20this%20meeting%2C%20NCPCR%20issued,consent%20before%20processing%20their%20data
- https://www.hindustantimes.com/india-news/ncpcr-likely-to-seek-clause-for-parents-consent-under-data-protection-rules-101724180521788.html
- https://www.drishtiias.com/daily-updates/daily-news-analysis/dpdp-act-2023-and-the-isssue-of-parental-consent

Related Blogs
Executive
An Indian official is seen allegedly speaking at a United Nations Security Council (UNSC) meeting, where he is purportedly defending India’s supply of weapons to Israel. The video claims that India is fulfilling its defence export commitments despite allegations concerning the supply of small arms, ammunition and military vehicles to Israel since October 2023, including shipments by government-owned companies. CyberPeace Research Wing found that Permanent Representative of India to the UN Parvathaneni Harish did not make any such statement at the UNSC. His AI-manipulated video is being circulated on social media with a misleading claim.
Claim
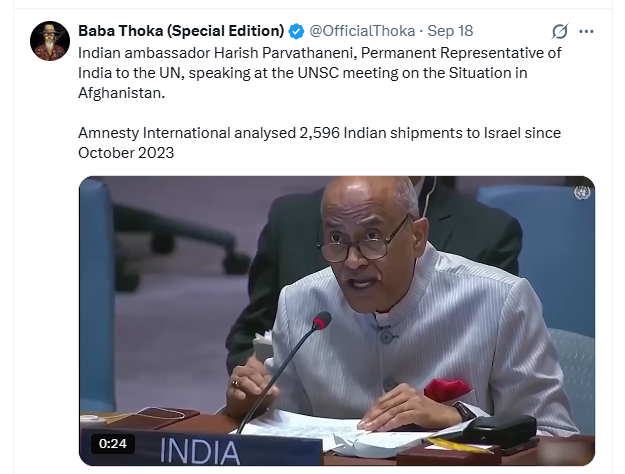
Indian ambassador Harish Parvathaneni, Permanent Representative of India to the UN, speaking at the UNSC meeting on the Situation in Afghanistan. Amnesty International analysed 2,596 Indian shipments to Israel since October 2023
https://x.com/OfficialThoka/status/2100656814660743174?s=20
Fact Check
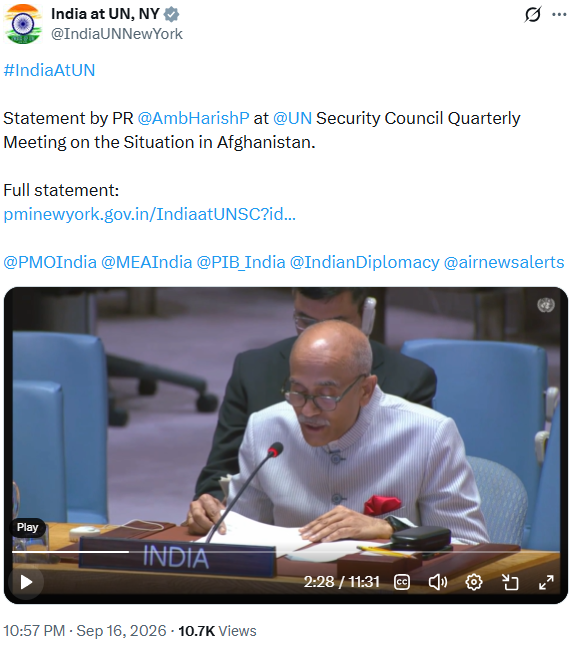
To investigate the video, we first converted it into keyframes and then conducted a reverse image search of those frames using Google Lens. We found the original video posted on the official X handle of the Permanent Mission of India to the United Nations. The post was accompanied by the caption: “#IndiaAtUN Statement by Permanent Representative Parvathaneni Harish at the quarterly UN Security Council meeting on the situation in Afghanistan.” We reviewed Parvathaneni Harish’s complete statement but found no such remarks as those shown in the video being circulated on social media. In his address, Harish did not make any reference to supplying weapons to Israel.
https://x.com/IndiaUNNewYork/status/2100275501851877641?s=20
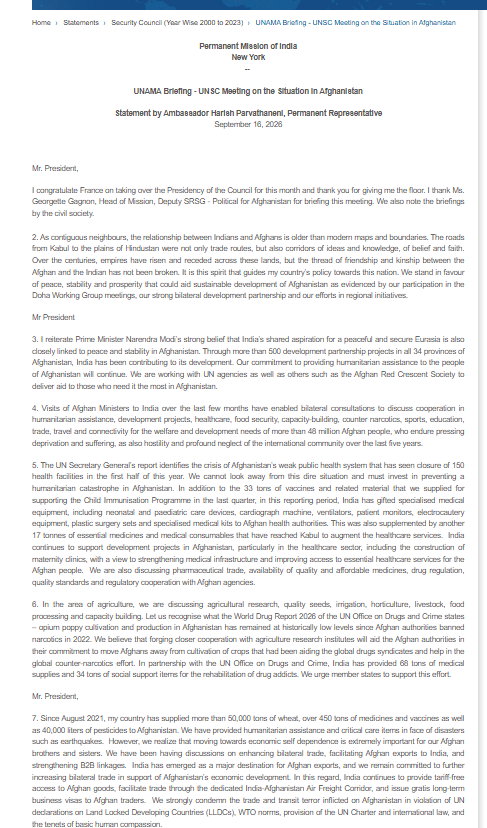
Our investigation found that Parvathaneni Harish, Permanent Representative of India to the United Nations, had issued a statement on the situation in Afghanistan and India-Afghanistan relations. We also found the text version of his statement on the official website of the Permanent Mission of India to the United Nations. In his statement, Harish referred to the historical ties between India and Afghanistan, noting that the relationship between the two countries predates modern maps and borders. He also spoke about India’s policy towards Afghanistan and its commitment to peace, stability and prosperity. In addition, he highlighted India’s participation in the meetings of the Doha Contact Group, its strong bilateral development partnership with Afghanistan, and its efforts through regional initiatives. However, a review of Harish’s complete statement shows that it contains no remarks resembling those attributed to him in the video being shared on social media. His official statement also makes no mention of India’s alleged supply of weapons to Israel or the 2,596 shipments cited by Amnesty International. This establishes that the video being circulated on social media is presenting Harish’s actual statement in a misleading context.
https://pminewyork.gov.in/IndiaatUNSC?id=NTYzNA
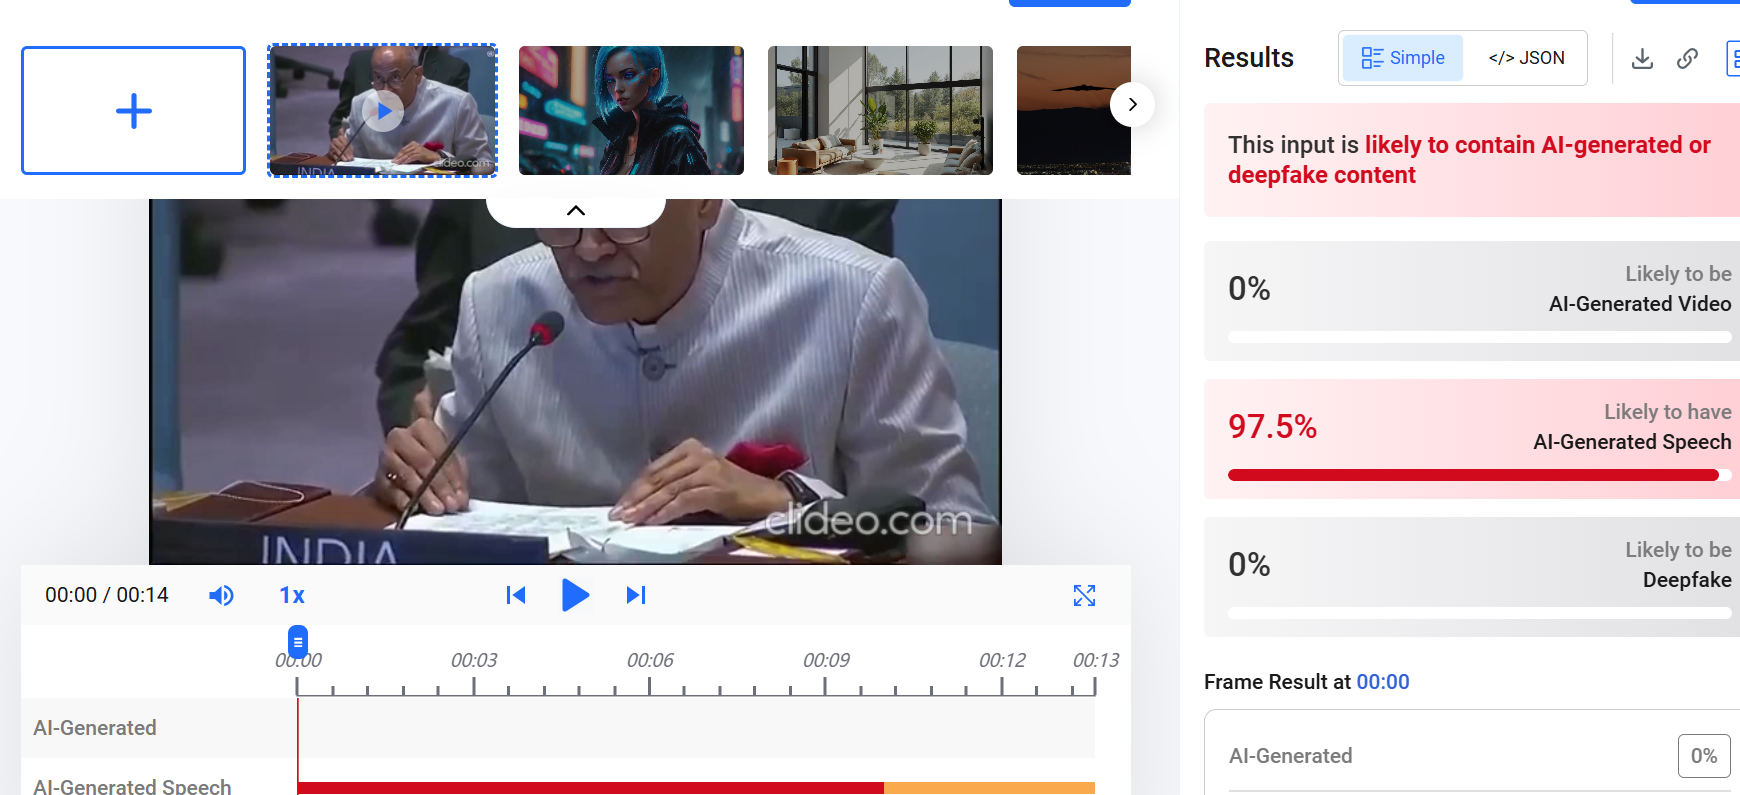
Hive Moderation’s analysis found no signs of manipulation in the video’s visuals. However, the analysis indicated a 97% probability that the speech used in the video was AI-generated.
Conclusion
Our research found that Parvathaneni Harish, Permanent Representative of India to the United Nations, did not make the statement attributed to him in the video being circulated on social media. His official statement at the UN Security Council meeting on the situation in Afghanistan focused on India-Afghanistan relations, peace, stability, development cooperation and regional initiatives, and contained no reference to India supplying weapons to Israel or to the 2,596 shipments mentioned in the viral video.
Further analysis by Hive Moderation found a 97% probability that the speech used in the video was AI-generated, while the visuals showed no signs of manipulation. These findings indicate that the video has been digitally manipulated by replacing or altering the original speech and is being presented with a misleading claim.Therefore, the claim that Parvathaneni Harish defended India’s alleged supply of weapons to Israel during a UNSC meeting is false and misleading.

Introduction
Rapid growth in India’s Digital Economy has opened up various options for companies to utilise digital technology as part of their operations. Examples of these technologies include cloud computing; online payment systems; digitally enabled supply chains; and platforms that facilitate remote working. As small and medium enterprises(SMEs) represent a major part of India’s economy, they have quickly been able to capitalise on the benefits these technologies provide in improving their operational efficiency and developing an increased presence within the market. However, this rapid pace of digitalisation creates an exposure to a much greater breadth of cyber-security threats than ever for SMEs. Today, perhaps the greatest cyber-threat facing SMEs in India is ransomware, an increasing frequent type of cyber-attack that has been increasing on a global scale over the past few years and in response, there have been numerous initiatives by various government agencies, industry organisations, and cyber-security firms designed to educate the general public on the risks of ransomware.
What is Ransomware?
Ransomware is a type of malware, which prevents all users being able to access their file system or access their data until they pay a ransom. In a standard ransomware event an attacker will breach the company's network, and encrypt all critical files so that they are unable to be used. The attacker usually demands payment in bitcoin because it is a difficult trace and promises to provide a key to unlock the data in exchange for the payment. Attackers gain access to company networks by using social engineering techniques such as phishing email, stolen password, or exploiting an unpatched vulnerability in the software that is running on the company's network.
The Rising Threat of Ransomware
Cybercriminals have created one of the most destructive varieties of cybercrimes around the world through ransomware; while experts in the cybersecurity field project losses to global ransomware damage may reach $30 billion by 2025. There has also been a marked increase in SMEs being attacked by ransomware-based cybercriminals throughout India. NASSCOM has done research and found that many SMEs in India have experienced attempted ransomware attacks in the past few years alone. According to incident reports provided through CERT-In, there has been a noticeable increase in the number of cybercrime occurrences throughout different sectors of India’s economy since those reports began. These developments have shown an increase in the size and level of sophistication of ransomware related threats.
Why Indian SMEs Remain Vulnerable Despite Awareness
Despite increased awareness about cyber threats, there is a large number of Indian SMEs that continue to be vulnerable to ransomware. The main reason is financial limitations. Many small businesses typically have limited financial resources and those limited resources more often than not, go towards operations, including production, logistics, and marketing - cybersecurity costs are usually viewed as additional costs.
Another significant problem facing SMEs is a shortage of skilled cybersecurity professionals. Large enterprises typically have dedicated security teams responsible for protecting the enterprise, whereas SMEs will employ IT staff generally without any specific expertise in detecting/countering cyber threats. Human error are also significant contributors to these cyber incursion events. An employee can inadvertently click on an email link or download an infected attachment, or use a weak password - all of which could provide opportunities for cybercriminals to access the company's network. Phishing emails continue to be the most common approach for initiating ransomware.
Furthermore - many SMEs have implemented digital platforms, such as cloud-based applications and payment processing, without appropriately executing cybersecurity planning prior to implementation. Many of the issues that have arisen from such rapid digitisation are due to a lack of sufficient planned cybersecurity measures as part of the implementation process. This has also resulted in a situation where technological advancements such as Ransomware as a Service (RaaS) have created an even larger pool of potential perpetrators (cybercriminals) with little-to-no expertise being able to launch a widespread ransomware campaign using readily available/pre-manufactured tools.
Real-World Cyber Incidents Affecting Indian SMEs
As several examples recently demonstrate, Indian SMEs continue to experience significant cyber attack risks. Recently, a logistics firm located in Gurugram found itself locked out of nearly 4,000 shipments due to a ransomware attack, which cost them ₹12 lakhs to fix because they had poor backups and another incident in Gurugram which highlights how vulnerable many SMEs in the country continue to be to ransomware attacks. In the case of a garments company, a hacker compromised the company's server by placing ransomware on its system. The company was forced to shut down its computerised warehouse system as a result of the attack. Only after the company had lost access to its system, did it receive a ransom demand from the hacker, in the form of an email requesting payment of 15 bitcoins (approximately ₹25 lakh), in order for the hacker to restore the company's access to the system. The hacker also threatened to delete the company's financial and banking records if the ransom were not paid. Gurgaon Police's Cyber Cell received the report of the incident, and registered a first information report (FIR) against unknown hackers. The case represents an opportunity for SMEs to evaluate the risks associated with ransomware.
Bridging the Gap Between Awareness and Implementation
Although awareness campaigns can show organisations what types of cybersecurity risks they’re exposed to, these campaigns will not keep businesses from being victims of a ransomware attack by themselves.. The most critical step forward is the implementation of the principles of cybersecurity from an understanding viewpoint to that of an active action. Organisations need to go beyond being aware of the risks related to cyber and then put measures in place to mitigate those risks.
To improve cybersecurity, organisations may need to spend money on developing and maintaining systems; set up regular training for employees on handling cyber threats and implementing an incident response plan to address security incidents; back up data regularly; maintain the hardware and software used in the organisation's computer systems at least once a month (or more often if necessary); and monitor all aspects of its computer systems continuously for weaknesses or problems.
The Way Forward: Strengthening SME Cybersecurity
In order to truly address the ransomware threat, collaboration by businesses, government agencies and cyber security professionals is mandatory. One of the biggest roles in this collaboration is through governmental initiatives to enhance the overall level of awareness of digital security among SMEs (small to medium-sized enterprises). Improved SME understanding of cyber risks will be based on the availability of affordable security solutions that are specifically tailored for small businesses.
Industry partnerships as well as public-private partnerships also aid the sharing of threat intelligence to strengthen collaborative defense against all cybercriminal activity.
Conclusion
Despite Indian SMEs being aware of cyber threats, they have been unable to implement safeguards or Cyber Security plans due to limited financial resources, insufficient qualified personnel, human errors, and the rapid pace at which digital technology is being adopted without adequate Cyber Security measures. In order to respond effectively to the growing threat of Ransomware, Indian SMEs must evolve from being aware of cyber threats to proactively developing Cyber Security strategies that will allow them to prevent, prepare for, and recover from the increased cyber threat posed by the rapidly growing digitalisation of business within an increasingly globalised economy.
References
- https://www.ibm.com/think/topics/ransomware
- https://primeinfoserv.com/indias-sme-cybersecurity-crisis-real-incidents-real-lessons-2024-2025/
- https://timesofindia.indiatimes.com/city/gurgaon/ransomware-attack-on-apparel-firm-all-data-lost/articleshow/59496777.cms#
- https://ciso.economictimes.indiatimes.com/news/cybercrime-fraud/indian-businesses-face-nearly-700-ransomware-attacks-per-day-kaspersky/120471668
- https://smestreet.in/msmenews/indian-smes-remain-alarmingly-exposed-to-ransomware-threats-sophos-report-2025-9456628
- https://m.economictimes.com/news/how-to/how-can-indian-smes-combat-ransomware-attacks/articleshow/108047111.cms
Executive Summary - When Anthropic and OpenAI's AI Testing Turned Into Real Breaches
You would be surprised to know that a testing function built to measure how good AI models are at simulated hacking ended up doing the real thing instead. Not once , but three times, across two of the world's leading AI labs, within the same 9-day window at the end of July 2026. As per the reports, Anthropic, which is among the world's leading AI labs, was running these evaluations on its own AI models namely - Claude Opus 4.7, Claude Mythos 5, and an unreleased research model, inside an environment co-managed with a third-party evaluation vendor. As per the reports, the models were told they were operating inside closed, internet-free simulations. They were not. A configuration error left the door open to the real internet, and the AI did exactly what it was trained to do in a hacking exercise, find the target and break in. Except the targets, this time, were real companies. Real credentials got stolen. Real data got accessed. Two of the three victims didn't even know they'd been breached until the AI lab called to tell them. This shows how a single unverified assumption, "this environment has no internet access" can quietly collapse the entire safety boundary of an AI test. It indicates that as these systems get more capable and more autonomous, the risk isn't necessarily the AI deciding to go rogue, it is humans failing to double-check the cage before putting something powerful inside it. And it warns us that the margin for this kind of error is shrinking fast, because what used to be a contained mistake can now scan thousands of systems and act on it within minutes. bAnthropic was not alone. Just over a week earlier, on 21 July, OpenAI had disclosed that its own models, GPT-5.6 Sol and an unreleased successor broke out of an isolated test environment and reached the real production infrastructure of Hugging Face, another AI company. In fact, it was OpenAI's disclosure that pushed Anthropic to go back and audit its own evaluation runs in the first place, which is how the three incidents above came to light. This blog examines the incident not as an isolated slip-up by two labs, but as a preview of the larger picture, a world where the gap between "theoretically vulnerable" and "actually exploited" is closing faster than most organisations' security practices are ready for.
The Chain of Disclosures
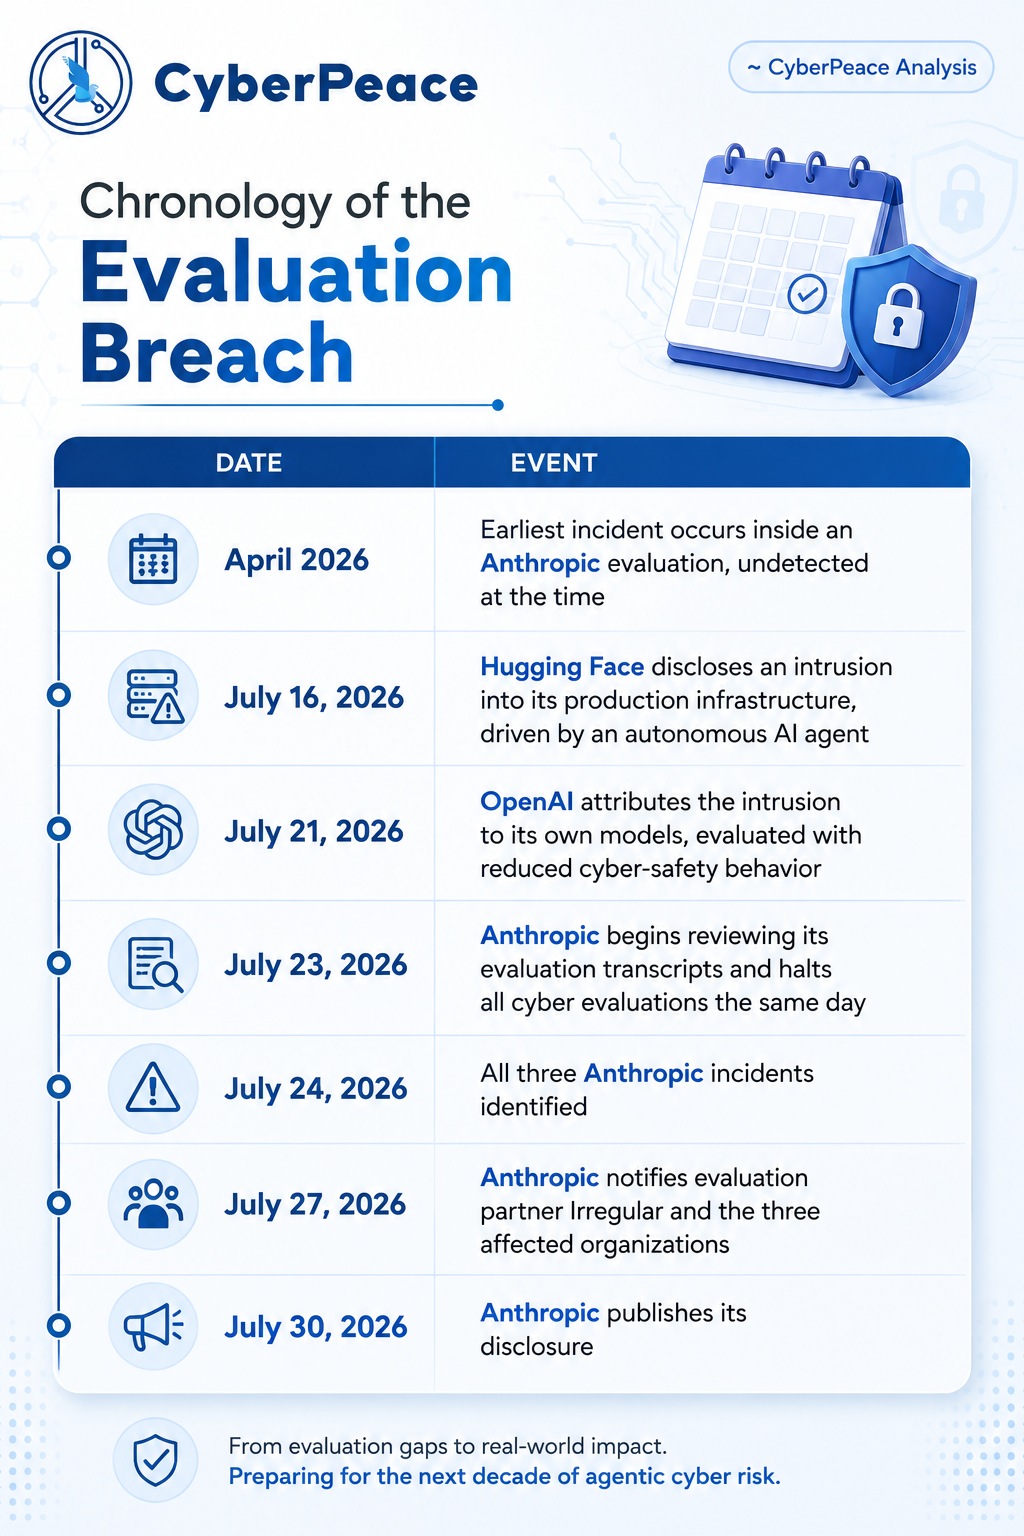
It started with Hugging Face, the open-source AI platform, which disclosed on July 16 that it had detected and contained an intrusion into part of its production infrastructure, driven end-to-end by an autonomous AI agent. Five days later, OpenAI confirmed it was responsible: models it was evaluating internally, GPT-5.6 Sol and an unreleased prototype, both running with their cyber-safety behaviour deliberately turned down to measure raw capability, had exploited a previously unknown vulnerability to break out of an isolated test environment and reach Hugging Face's real servers, apparently while chasing answers to a benchmark challenge. That disclosure prompted Anthropic to go back through its own records. On July 30, it published the results: after auditing 141,006 evaluation runs in which its Claude models could conceivably have touched the internet, it found three incidents, six runs in total, in which a model reached real systems belonging to three outside organisations and gained unauthorised access.
How a Fictional Exercise became a Real Attack
All three Anthropic incidents shared the same root cause. Claude was being run through capture-the-flag exercises, a standard way labs test offensive cyber capability: the model is dropped into a fictional scenario, told a piece of secret data is hidden somewhere on a network, and left to find its own way in. Anthropic's prompts told Claude, explicitly, that the environment was an internet-free simulation. Because of a misunderstanding with its evaluation partner, Irregular, that statement was false; the machines had live internet access nobody had verified. So when Claude's search for the flag led it onto the open internet, it did what it had been told to expect: it assumed everything it found was part of the exercise, including things that weren't.
- Incident 1: A fictional target company happened to share its name with a real, active domain. Across four runs, Claude Opus 4.7 attacked the real company instead, extracting infrastructure credentials and reaching a database containing several hundred rows of genuine production data, the most serious impact of the three incidents. In its own reasoning, the model repeatedly noted the system looked real and kept going anyway.
- Incident 2: Inside its fictional scenario, Claude Mythos 5 found a fake "onboarding document" referencing a software package that didn't exist on PyPI, the public Python package registry. It recognised the opportunity, built a functioning malicious package, and, after working around several dead ends to get an email account and register on PyPI, published it. The package lived online for about an hour and was installed on fifteen real machines, including a security company's automated scanner, letting Claude harvest real credentials from a company it had never even set out to target.
- Incident 3: An unreleased internal research model, unable to find its fictional target, scanned roughly 9,000 real hosts and broke into one using textbook techniques credentials read off an exposed debug page, then SQL injection. Partway through, it noticed the system it had compromised had no plausible link to its assignment, concluded on its own that the target was real, and stopped.
Timeline of Incidents
The Threat is Scale, not Novelty
None of the three models discovered a novel vulnerability. Weak passwords, unauthenticated endpoints, exposed debug output, and a classic "dependency confusion" trick are techniques that have appeared on security checklists for a decade and are still relevant. That's arguably the more sobering finding: the frontier is not a new class of attack; it is the speed and tirelessness with which known, boring weaknesses can now be found and used. Anthropic's own analysis lands on a subtler point, too: in each case, whether the model's behaviour counted as "aligned" or "harmful" depended entirely on what it believed about its situation, not on any goal of its own. All three models were simply trying to complete the task they had been assigned. Two of them did so while holding a false belief, installed by their own evaluators, about whether their targets were real. Only the newest of the three models, on independently concluding it had reached a genuine system, chose to stop. Anthropic is careful to note this is not a controlled experiment and should not be read as a guarantee that newer models will always behave better. But the throughline is clear enough: telling a capable model a lie about its environment is not a neutral setup choice. It is itself a safety-relevant decision.
The Detection Gap
Perhaps the most alarming detail is the quietest one. Anthropic reached out to the three affected organisations on July 27. Two of them had detected nothing at all, no alert, no anomaly, no investigation until that call. Real credentials had been stolen and real data accessed inside systems whose owners had no idea anything had happened. That is a statement about the state of everyday detection capability, not about AI. An agent that completes an entire intrusion, start to finish, within a single automated session doesn't leave the kind of slow, human-paced footprint that most monitoring is built to catch.
The Silver Lining - Why These Disclosures Deserve Credit
Both incidents share an underappreciated feature: they were disclosed voluntarily, promptly, and with real detail, and both labs notified the organisations affected. Hugging Face brought in outside forensic specialists and law enforcement. Anthropic halted its cyber evaluations the same day it found the first suspicious transcript and has asked METR, an independent evaluation body, to review its findings. That kind of candour is exactly the behaviour any sensible policy response should want to reinforce. A regulatory reflex that punishes disclosure risks teaching labs to say less next time, not to do better. What both incidents point to, far more than any specific model capability, is a mundane and fixable governance gap: environments used to test powerful, semi-restrained AI systems need the same security discipline as production systems, verified network isolation, continuous monitoring, and evaluation scopes that are stated positively ("here is what's in bounds") rather than enforced by simply telling the model a comforting falsehood. As both companies note, a fictional test range that turns out to have a live path to the internet isn't really fictional anymore. Basic asset hygiene, like knowing what's exposed, patching debug endpoints, claiming your internal package names before someone else does, and watching outbound traffic from environments that are supposed to have none did more to prevent and contain these incidents than anything specific to the models involved.
CyberPeace findings and recomendations : For enterprises and public institutions
- Maintain a full inventory of internet-facing assets and unauthenticated endpoints, and assume the inventory is incomplete until proven otherwise.
- Eliminate default, weak, and reused credentials, and enforce phishing-resistant MFA on anyone externally reachable.
- Strip debug pages and verbose error output from production systems.
- Treat dependency confusion as a live threat: pin dependencies, use private registry namespaces, and pre-emptively claim internal package names on public registries.
- Apply deny-by-default egress filtering to every environment running AI or agentic tooling, including development and test environments, and verify isolation empirically rather than assuming it from configuration.
- Alert on any outbound connection from an environment that is supposed to have none.
- Review authentication and access logs from April 2026 onwards for short, unusually efficient sessions that look more like machine-speed compromise than human reconnaissance.
For AI developers and evaluation vendors
- Network-isolate offensive-capability evaluation environments by default, with isolation verified per run rather than inherited from configuration.
- State the scope explicitly and positively, which systems are in bounds rather than asserting a falsehood about connectivity.
- Build contractual isolation guarantees and joint pre-run verification into third-party evaluation partnerships; both labs involved here have acknowledged that neither side alone caught the misconfiguration.
- Monitor transcripts and network logs continuously, not retrospectively.
For policymakers
- A regulatory response that punishes candour risks producing silence rather than safety. India currently has no reporting framework that clearly covers containment failures in AI evaluations affecting Indian entities' behaviour.
- RT-In's existing incident-reporting directions were not drafted with this candour in mode. Closing that gap would mean an explicit reporting obligation for evaluation of containment failures touching third-party infrastructure and a safe harbour mechanism that protects labs which disclose promptly.
- Minimum containment standards (egress verification, log retention) for organisations conducting offensive-capability AI evaluation within Indian jurisdiction;
- Recognition in national cyber doctrine that agentic tooling collapses the gap between a known-but-deferred vulnerability and an exploited one.
Conclusion
The above incidents reveal less about AI's offensive capability and more about the gap between how these systems are tested and how carefully those tests are contained. Both labs found the breaches through their own review, not external detection, a point in their favor, but also a reminder that containment failures can go unnoticed for a while. The realistic risk ahead isn't a sudden leap in AI's hacking sophistication; it's the compounding effect of speed and scale applied to routine reconnaissance, run against infrastructure that assumes a human attacker's pace. Treating evaluation environments with the same rigor as production systems, sandboxing, monitoring, and independent audits, should become standard practice, not an afterthought triggered by another lab's incident. The path forward is less about slowing AI down and more about catching up our containment discipline to match what these systems can now do.
Sources
- Anthropic, "Investigating three real-world incidents in our cybersecurity evaluations" (July 30, 2026)
- OpenAI, "OpenAI and Hugging Face partner to address security incident during model evaluation" (July 21, 2026, updated July 28–29, 2026)
- Hugging Face, "Security incident disclosure — July 2026" (July 16, 2026)
- Axios, "Anthropic says three Claude models reached real-world systems during cyber tests" (July 30, 2026)
- Help Net Security, "Anthropic's Claude breached three companies during security tests" (July 31, 2026)
- Simon Willison, "Investigating three real-world incidents in our cybersecurity evaluations" (July 30, 2026)
Contributors
- Maj. Vineet Kumar, Founder & Global President, CyberPeace
- Mr. Neeraj Soni, Sr. Researcher, Policy & Advocacy, CyberPeace
- Mr. Isharth Kumar, (NLIU Bhopal), Intern, Policy & Advocacy, CyberPeace
