
Proactive Moderation for Digital Safety: Insights from WhatsApp’s Crackdown on Fraud in India
Introduction
The 2023-24 annual report of the Union Home Ministry states that WhatsApp is among the primary platforms being targeted for cyber fraud in India, followed by Telegram and Instagram. Cybercriminals have been conducting frauds like lending and investment scams, digital arrests, romance scams, job scams, online phishing etc., through these platforms, creating trauma for victims and overburdening law enforcement, which is not always the best equipped to recover their money. WhatsApp’s scale, end-to-end encryption, and ease of mass messaging make it both a powerful medium of communication and a vulnerable target for bad actors. It has over 500 million users in India, which makes it a primary subject for scammers running illegal lending apps, phishing schemes, and identity fraud.
Action Taken by Whatsapp
As a response to this worrying trend and in keeping with Rule 4(1)(d) of the Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Rules, 2021, [updated as of 6.4.2023], WhatsApp has been banning millions of Indian accounts through automated tools, AI-based detection systems, and behaviour analysis, which can detect suspicious activity and misuse. In July 2021, it banned over 2 million accounts. By February 2025, this number had shot up to over 9.7 million, with 1.4 million accounts removed proactively, that is, before any user reported them. While this may mean that the number of attacks has increased, or WhatsApp’s detection systems have improved, or both, what it surely signals is the acknowledgement of a deeper, systemic challenge to India’s digital ecosystem and the growing scale and sophistication of cyber fraud, especially on encrypted platforms.
CyberPeace Insights
- Under Rule 4(1)(d) of the IT Rules, 2021, significant social media intermediaries (SSMIs) are required to implement automated tools to detect harmful content. But enforcement has been uneven. WhatsApp’s enforcement action demonstrates what effective compliance with proactive moderation can look like because of the scale and transparency of its actions.
- Platforms must treat fraud not just as a content violation but as a systemic abuse of the platform’s infrastructure.
- India is not alone in facing this challenge. The EU’s Digital Services Act (DSA), for instance, mandates large platforms to conduct regular risk assessments, maintain algorithmic transparency, and allow independent audits of their safety mechanisms. These steps go beyond just removing bad content by addressing the design of the platform itself. India can draw from this by codifying a baseline standard for fraud detection, requiring platforms to publish detailed transparency reports, and clarifying the legal expectations around proactive monitoring. Importantly, regulators must ensure this is done without compromising encryption or user privacy.
- WhatsApp’s efforts are part of a broader, emerging ecosystem of threat detection. The Indian Cyber Crime Coordination Centre (I4C) is now sharing threat intelligence with platforms like Google and Meta to help take down scam domains, malicious apps, and sponsored Facebook ads promoting illegal digital lending. This model of public-private intelligence collaboration should be institutionalized and scaled across sectors.
Conclusion: Turning Enforcement into Policy
WhatsApp’s mass account ban is not just about enforcement but an example of how platforms must evolve. As India becomes increasingly digital, it needs a forward-looking policy framework that supports proactive monitoring, ethical AI use, cross-platform coordination, and user safety. The digital safety of users in India and those around the world must be built into the architecture of the internet.
References
- https://scontent.xx.fbcdn.net/v/t39.8562-6/486805827_1197340372070566_282096906288453586_n.pdf?_nc_cat=104&ccb=1-7&_nc_sid=b8d81d&_nc_ohc=BRGwyxF87MgQ7kNvwHyyW8u&_nc_oc=AdnNG2wXIN5F-Pefw_FTt2T4K6POllUyKpO7nxwzCWxNgQEkVLllHmh81AHT2742dH8&_nc_zt=14&_nc_ht=scontent.xx&_nc_gid=iaQzNQ8nBZzxuIS4rXLOkQ&oh=00_AfEnbac47YDXvymJ5vTVB-gXteibjpbTjY5uhP_sMN9ouw&oe=67F95BF0
- https://scontent.xx.fbcdn.net/v/t39.8562-6/217535270_342765227288666_5007519467044742276_n.pdf?_nc_cat=110&ccb=1-7&_nc_sid=b8d81d&_nc_ohc=aj6og9xy5WQQ7kNvwG9Vzkd&_nc_oc=AdnDtVbrQuo4lm3isKg5O4cw5PHkp1MoMGATVpuAdOUUz-xyJQgWztGV1PBovGACQ9c&_nc_zt=14&_nc_ht=scontent.xx&_nc_gid=gabMfhEICh_gJFiN7vwzcA&oh=00_AfE7lXd9JJlEZCpD4pxW4OOc03BYcp1e3KqHKN9-kaPGMQ&oe=67FD6FD3
- https://www.hindustantimes.com/india-news/whatsapp-is-most-used-platform-for-cyber-crimes-home-ministry-report-101735719475701.html
- https://www.indiatoday.in/technology/news/story/whatsapp-bans-over-97-lakhs-indian-accounts-to-protect-users-from-scam-2702781-2025-04-02

Related Blogs
Executive Summary
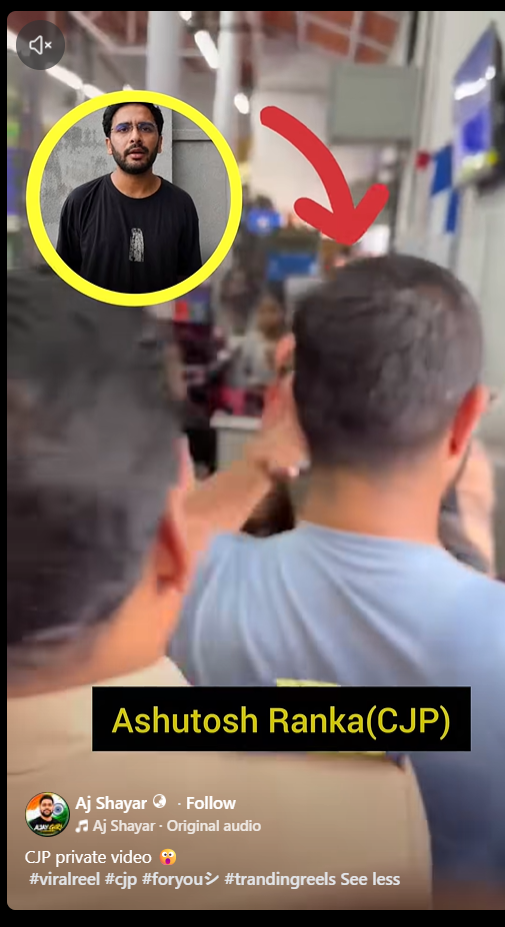
A video is being shared on Facebook with the claim that it shows CJP spokesperson Ashutosh Ranka being assaulted. The video shows several people beating a man. A picture of Ashutosh Ranka has been overlaid on the video along with the text, “CJP Private Video.” Some users commenting on the post also believe that the video genuinely shows Ranka being assaulted. CyberPeace Research found that the video is from Mira Road, where MNS workers had assaulted store manager Jay Pathak.
Claim
A video is being shared on Facebook claiming that it shows a private video of CJP.
https://www.facebook.com/reel/1405149115120742
Fact Check
We first searched Google using keywords such as “CJP spokesperson Ashutosh Ranka assaulted.” However, we did not find any credible media reports mentioning the incident described in the claim.
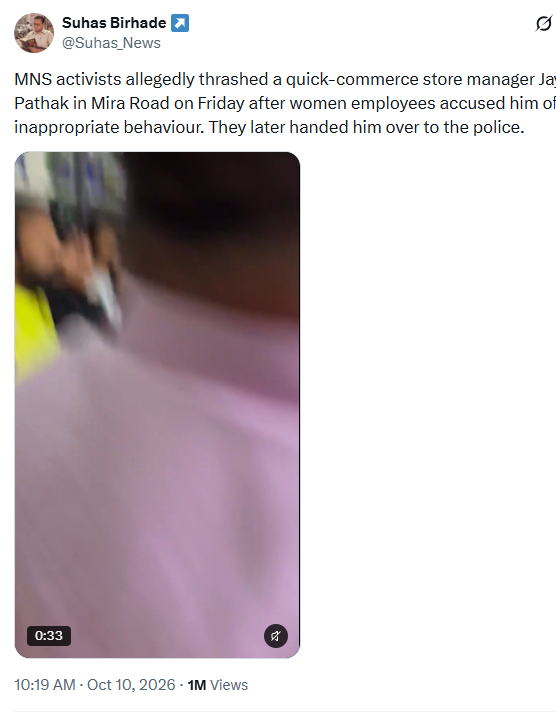
We then conducted a reverse image search of a frame from the viral video using Google Lens. This led us to a longer version of the same video, which was shared on October 10, 2026, by the X account @Suhas_News. According to the accompanying information, Maharashtra Navnirman Sena (MNS) workers assaulted store manager Jay Pathak in Mira Road after female employees alleged that they had been treated inappropriately.
https://www.facebook.com/reel/1405149115120742
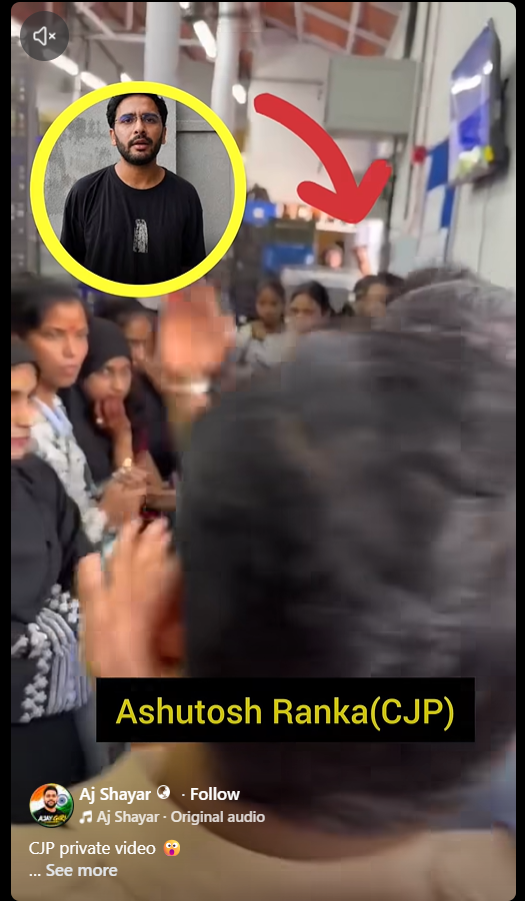
https://x.com/Suhas_News/status/2108782017391525953
We also found the same video shared with the same information on the official Facebook page of news agency Midday India on October 10, 2026.
https://www.facebook.com/reel/4737845496451020
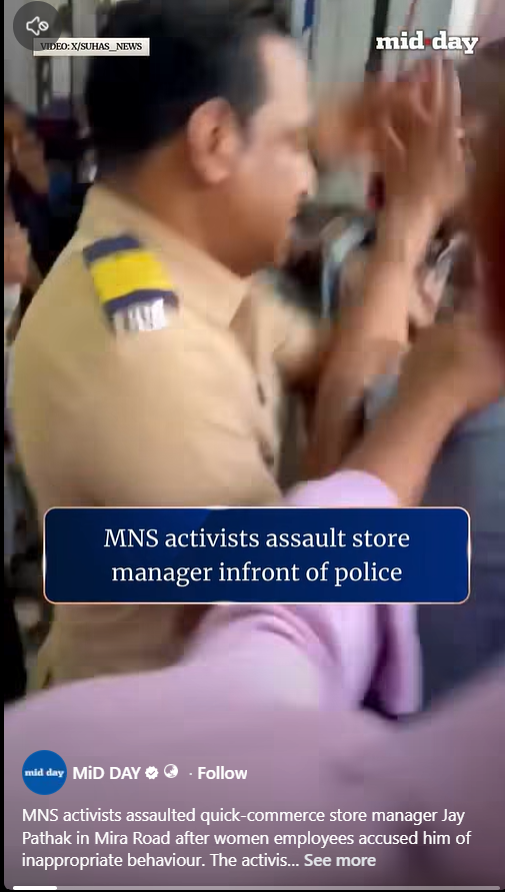
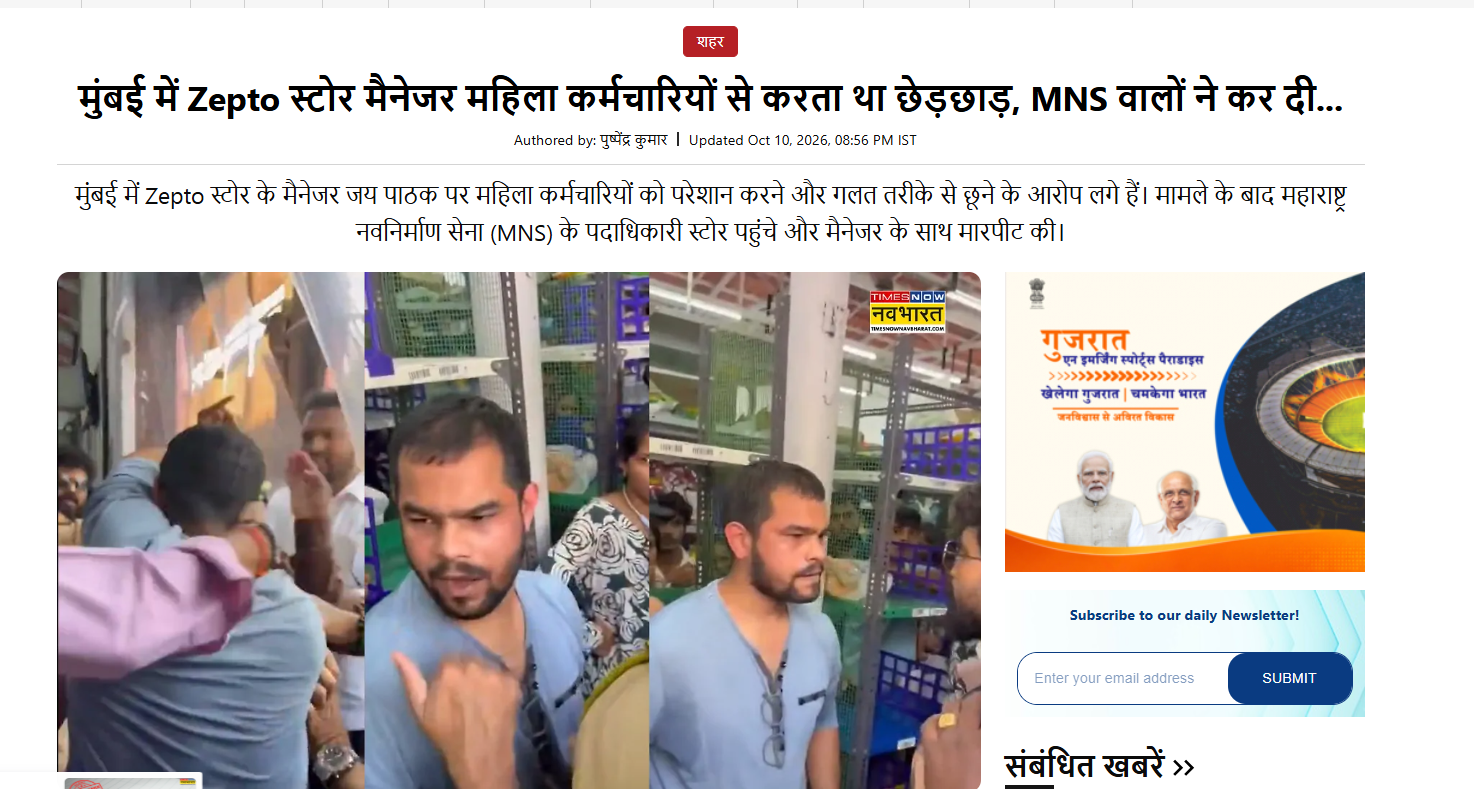
In the next stage of our research, we found a report published by Times Now on October 10, 2026, related to the viral video. According to the report, five female employees of a Zepto store located in the Shivar Garden area of Mira Road had accused their manager, Jai Pathak, of repeatedly touching them inappropriately and sexually harassing them.
Conclusion
Our research found that a video showing the assault of store manager Jai Pathak in Mira Road is being shared with the misleading claim that it shows CJP spokesperson Ashutosh Ranka being beaten.

Introduction
The Kerala High Court banned the use of mobile phones during office hours on the 2nd of December 2024, and issued an Official Memorandum titled, ‘Indulgence In Online Gaming And Watching Social Media Content During Office Hours’. This memorandum, issued by the Registrar General, prohibits mobile phone usage for personal activities such as gaming and social media during working hours. This memorandum aims to curb the productivity woes and reinforce professional discipline and further ensure the smooth functioning of the office operations.
The memorandum reiterated its earlier notices from 2009 and 2013, where the High Court had emphasised that violations would be taken seriously. This reflects the High Court’s commitment to maintaining efficiency and professionalism in the workplace. According to the memorandum, controlling officers will monitor the staff for violations and strict actions will be taken if the rules are flouted.
Background
The circumstances that led to the Kerala HC’s decision are as follows: staff engaged in playing online games, browsing social media, watching videos or movies and even engaging in online shopping or trading during work hours, excluding the allocated lunch recess (as per the memorandum).
As mentioned earlier, this memorandum is not the first of its kind. There were similar directives that were issued in 2009 and 2013 to target the poor productivity standards, rooted in the staff members' behaviours. The present memorandum is unlike the previously mentioned ones as, it specifically addresses the rise in mobile-based distractions, like online gaming and trading. The present directive does not outline any exceptions to senior officials with designated responsibilities, and emphasises universal adherence for all levels of the workforce.
According to Cell Phones at Workplace Statistics, around 97% of workers use their smartphones during work hours, mixing personal and job-related activities. And more than 55% of managers say that cell phones are a major reason for lower productivity among employees.
Therefore, it can be safely concluded that even though smartphones have become indispensable tools for communication, their misuse has wider implications for overall organisational productivity.
CyberPeace Outlook
The Kerala High Court's decision to restrict personal mobile phone usage during work hours underscores the importance of fostering a disciplined and focused workplace environment. While smartphones are vital for communication, their misuse poses significant productivity challenges. Some proactive steps that employers can take are implementing clear policies, conducting regular training sessions and promoting a culture of accountability. Balancing digital freedom and professional responsibility is the key to ensuring that technological tools serve as enablers of efficiency rather than distractions in the workplace.
References
- https://www.thehindu.com/sci-tech/technology/kerala-high-court-issues-memo-banning-staff-from-gaming-and-social-media-during-work-hours/article68963949.ece
- https://timesofindia.indiatimes.com/technology/tech-news/kerala-high-court-bans-mobile-gaming-and-social-media-for-staff-during-work-hours/articleshow/116101149.cms
- https://images.assettype.com/barandbench/2024-12-05/1hiq8ffv/Kerala_High_Court_OM.pdf
- https://www.coolest-gadgets.com/cell-phones-at-workplace-statistics/
Introduction
The trajectory of India's digital economy is growing at an unprecedented rate, and so is India's cybercrime ecosystem. Parliamentary data tabled before the Rajya Sabha in May 2024 by the MHA suggests an overwhelming 900% growth in cybercrime complaints from 2021 to '25, while annual losses crossed 22,800 crore in 2024. The structural issues like the low victim restitution rate, the lack of forensic infrastructure, issues of jurisdiction related to offshore fraud factories targeting Indian citizens, and the huge disparity in awareness levels amongst India's youngest online citizens continue to exist. This brief brings out the clear trends in cybercrime, the role of institutional mechanisms in its prevention and response, failure points, and recommends appropriate policy interventions from the perspective of CyberPeace.
The Data Imperative
Since its operationalisation in 2019 by the Indian Cyber Crime Coordination Centre (I4C), the NCRP serves as India's most significant institutional apparatus for cybercrime reporting and response. Data placed before the Rajya Sabha by the Ministry of Home Affairs on 30 July 2025 show that, with almost no exception, complaints of cybercrime have increased far more quickly than most traditional indicators of public safety. Between 2021 and June 2025, the NCRP received 6.59 million complaints, evidence of both a sustained and escalating expansion of India's cyber threat profile. Complaints per year more than quadrupled from 4.52 lakh in 2021 to 19.18 lakh in 2024 (324% over the period); by 2025, the NCRP had received 28.15 lakh complaints, a 523 percent rise compared with the 2021 baseline:
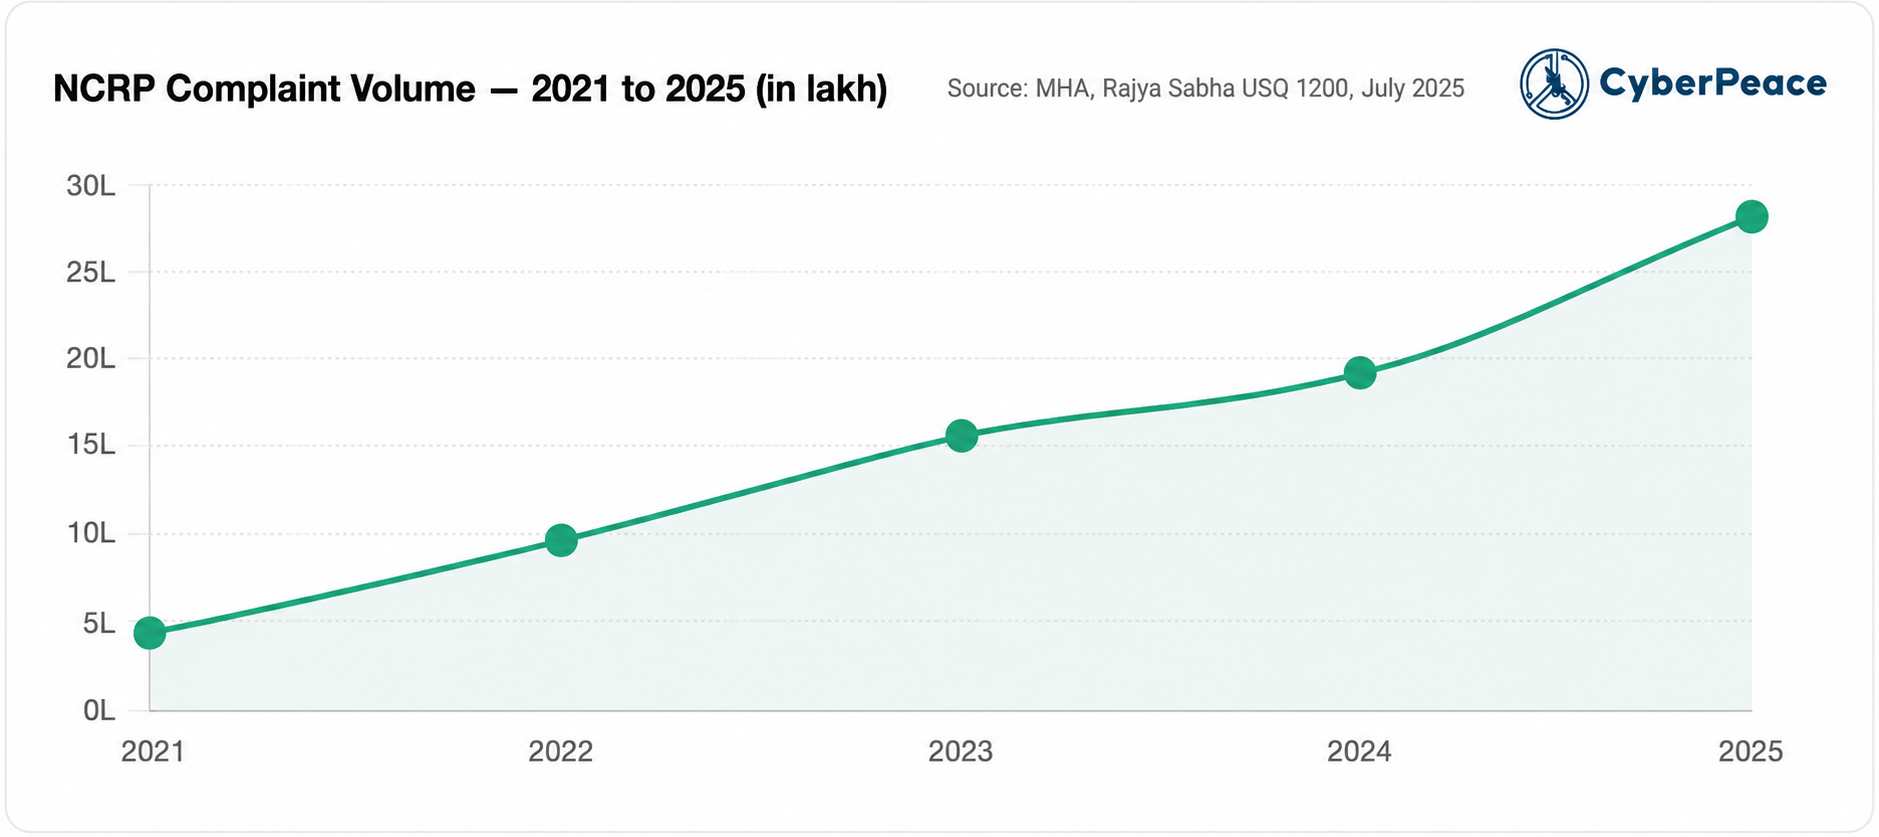
Clearly, cyber-enabled crime is no longer an occasional crisis but a systemic governance issue requiring consistent regulation and institution-building.
The financial fallout has also accelerated dramatically. Figures indicate that reported financial losses due to cybercrime jumped from 2,290 crore in 2022 to 22,812 crore in 2024 a 895% leap in two years:
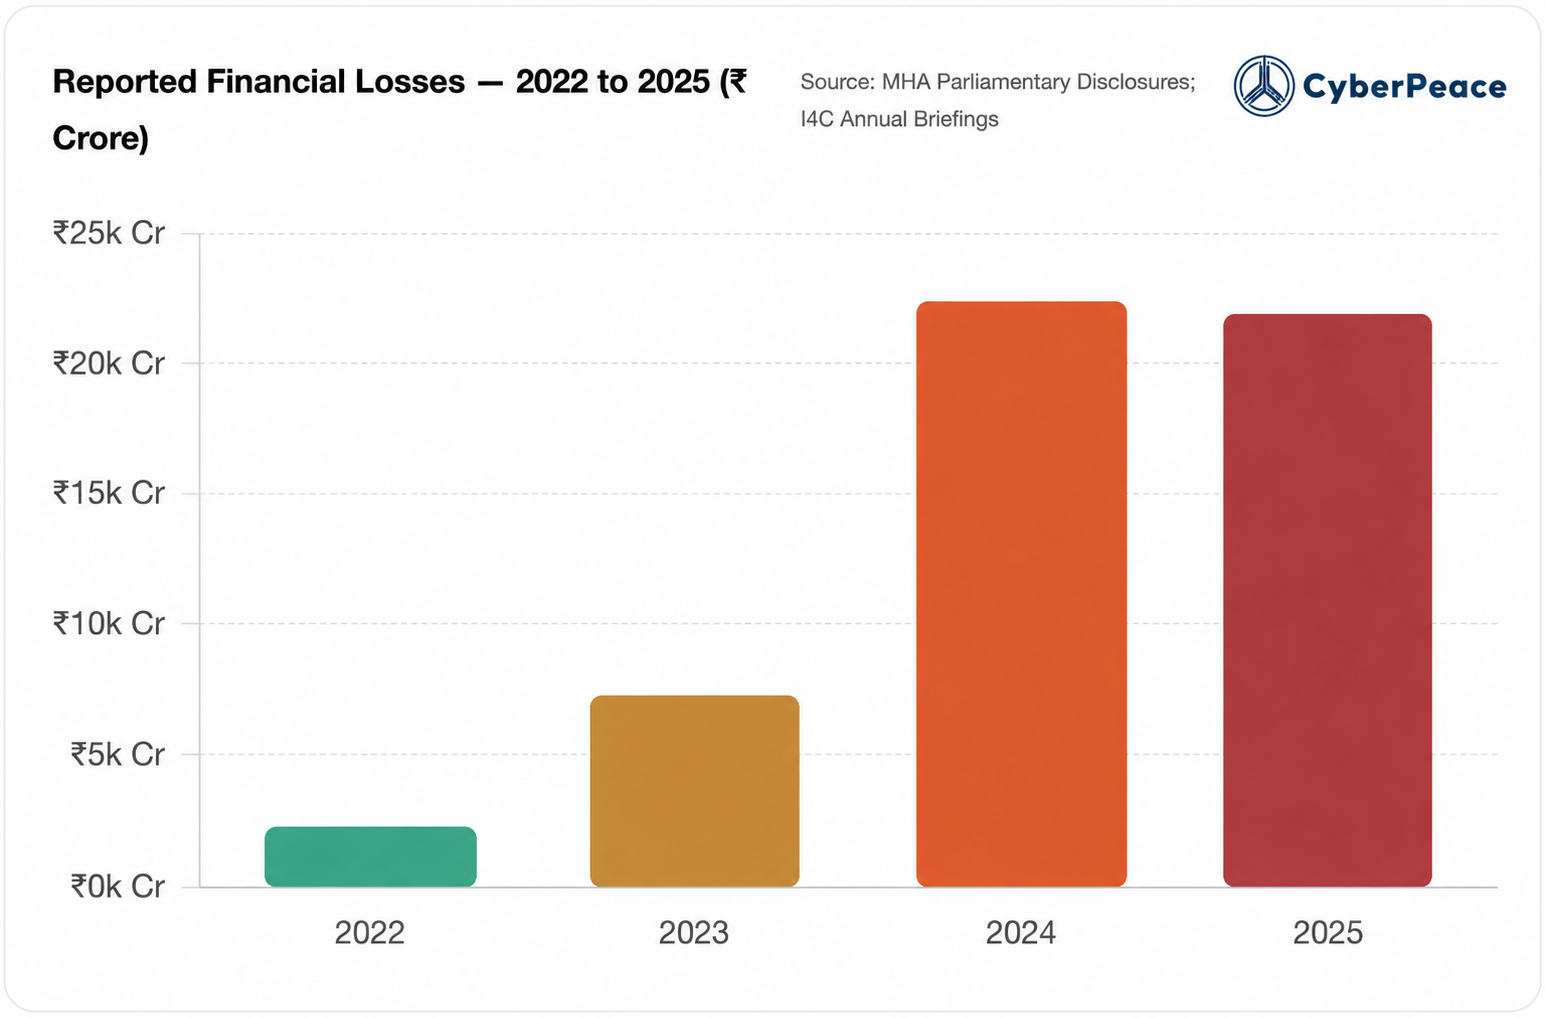
Though response mechanisms such as the Citizen Financial Cyber Fraud Reporting and Management System (CFCFRMS) successfully blocked or recovered close to 8,690 crore as of January 2026, victims appear to get back only about 2.18 percent of the losses they report.
In most areas, reporting and response have expanded greatly, but both the rate and scale of cyber-enabled financial fraud continue to outstrip India's remediation and law enforcement capacity.
Threat Typology of India’s Fraud Ecosystem
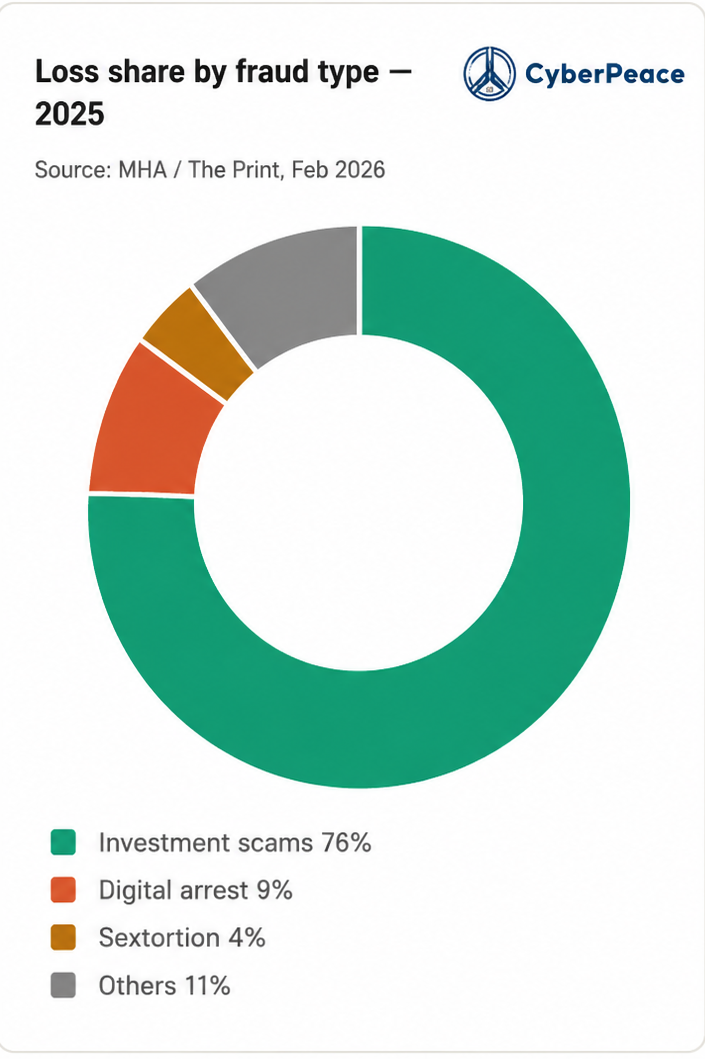
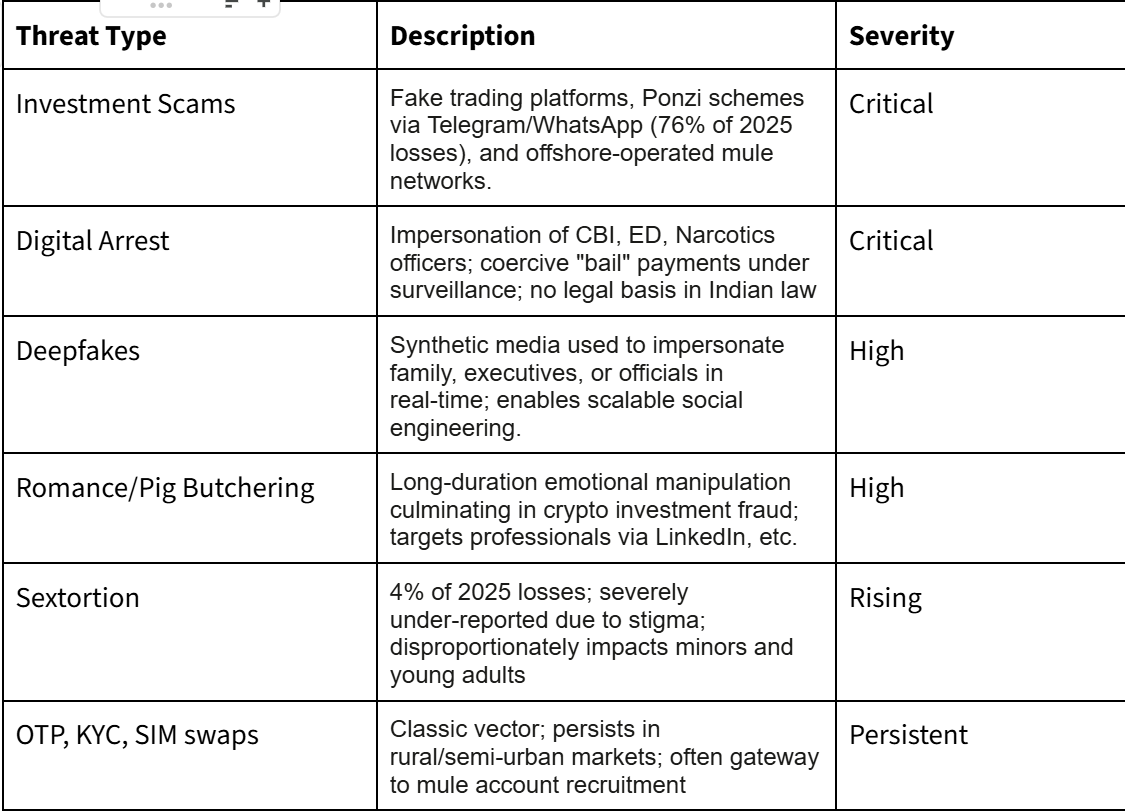
The nature of cyber crime in India has evolved from an opportunistic volume-based activity to a layered transnational criminal environment. I4C intelligence as tabled in Parliament reveals investment scams as the biggest threat: they accounted for 76% of the financial fraud lost in 2025 (although only 35% of complaints were filed, thus, a very high value per case was lost).
Digital arrest frauds, which tap on citizens' unawareness that "digital arrest" is not permissible under Indian law, rose from 39,925 cases (91 crore) in 2022 to 123,672 cases (1,935crore) in 2024.
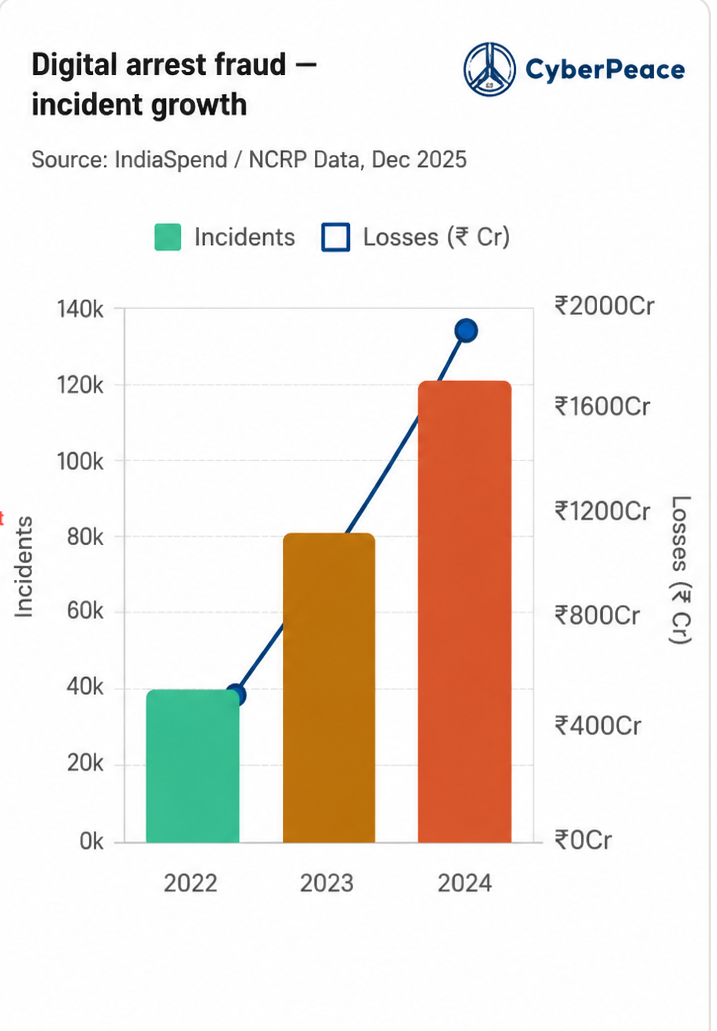
The fast rise in the number of incidents as well as in the volume of fraud clearly points out that digital arrest fraud has moved away from the phase of novel scam typology to a formidable cyber-extortion landscape. The main orchestrators of investment, trading, dating, and digital arrest scams targeting Indian citizens were recently identified by the I4C CEO Rajesh Kumar as transnational criminal scam networks in Cambodia, Myanmar, and Laos. Hence, this issue does not only fall within the domain of domestic law enforcement but constitutes a transnational cybercrime requiring parallel financial intelligence, diplomatic initiative, platform responsibility, and international investigative collaboration.
Geographic Concentration
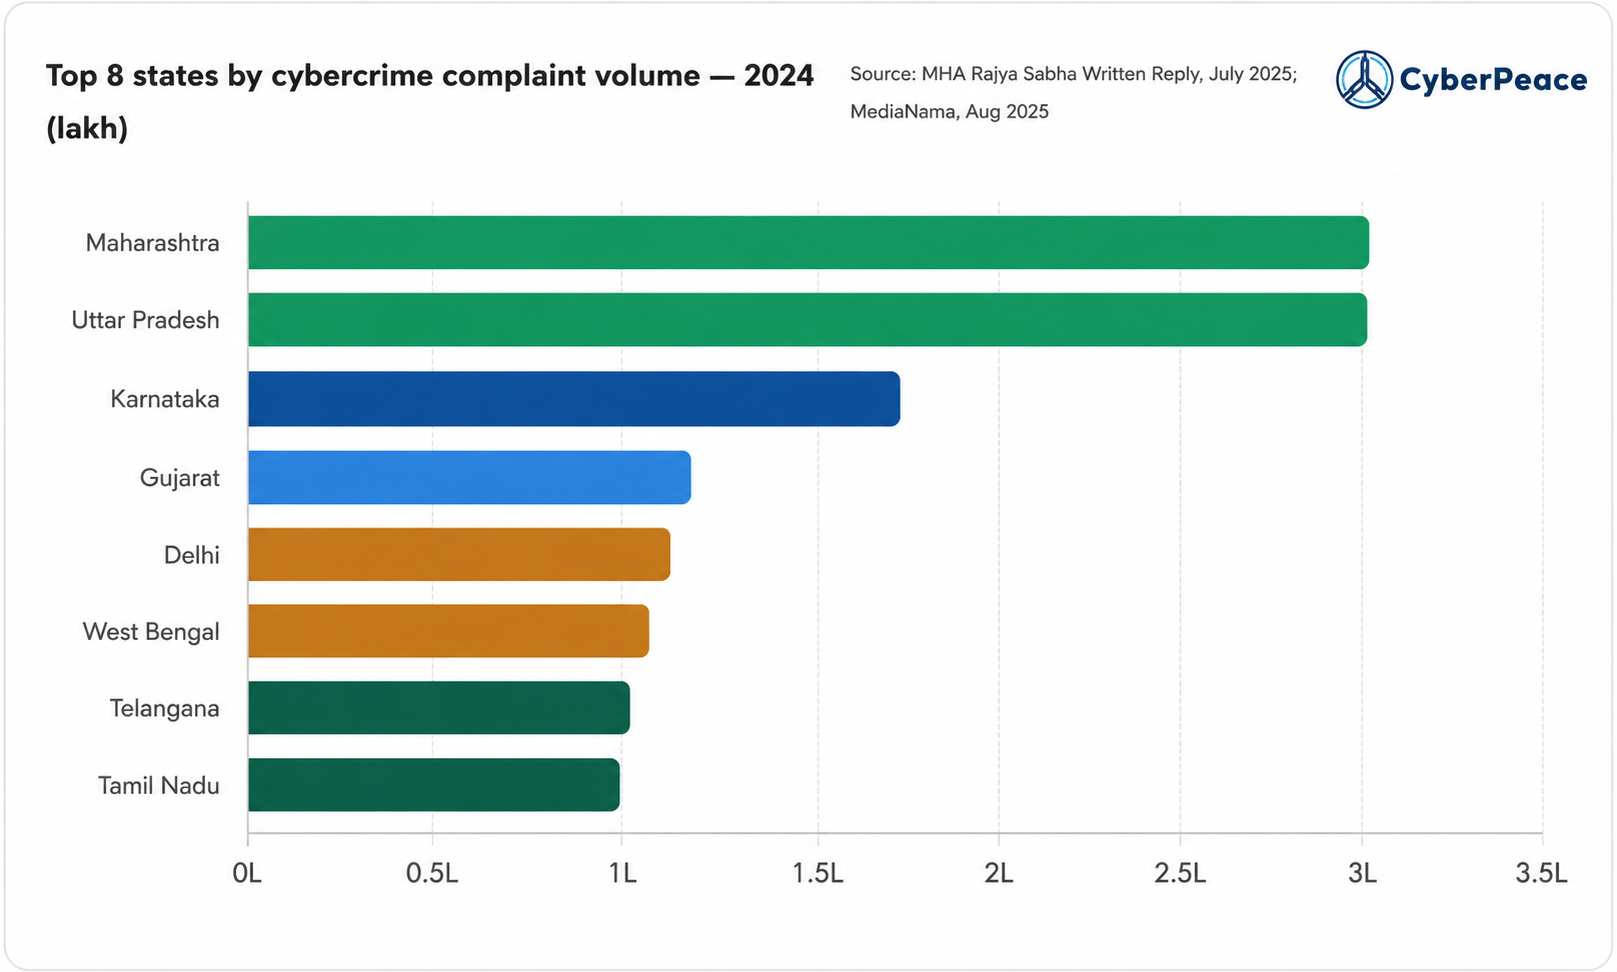
Maharashtra and UP register the highest volumes in total complaints at 3.03 lakh and 3.01 lakh, owing to them being the financial capital and most populous state, respectively. Karnataka, Gujarat, Delhi, WB, Telangana, TN, Rajasthan, and Haryana register above 1 lakh complaints each. However, the critical information that is being missed is that while complaint rate growth is the fastest in Tier 2 and 3 geographies (Haryana leads per-capita complaint rate with 381/100k people in 2023; Telangana (261); Uttarakhand (243)), this signifies rural digital growth as a risk multiplier.
Institutional Architecture: Mechanisms and Performances
India's institutional response to cybercrime, led by the Ministry of Home Affairs' Indian Cyber Crime Coordination Centre (I4C), is one of the world's largest real-time fraud detection and prevention ecosystems. The backbone of this is the Citizen Financial Cyber Fraud Reporting and Management System (CFCFRMS), which has onboarded over 700 banks, payment service providers, e-commerce portals, digital wallets, and, since the Standard Operating Procedure was issued on 2nd January 2026, virtual asset service providers and crypto exchanges. This interconnected network allows for prompt freezing of funds and timely fraud intervention during the 'golden hour' of a cybercrime report.
Institutional capacity is robust, with approximately 8,690 crore saved via the CFCFRMS since its inception for over 24.65 lakh complaints. The national cybercrime helpline (1930) receives close to 10,000 calls daily, while the Suspect Registry has enabled the rejection of 9,519 crore via the detection of 23.05 lakh suspect entities and 27.37 lakh mule accounts. In parallel, the CyTrain platform has expanded training by registering 151,081 police and judicial officers and issuing 142,025 certificates. Cyberforensic labs in all 33 States and Union Territories have received central assistance totalling 132.93 crore, and data-driven interstate crime analytics and offender linkages through the Samanvaya and Pratibimb platforms have led to 21,857 arrests.
Ecosystem Gaps
Through I4C, CFCFRMS, CyTrain, and the establishment of forensic infrastructure in states, India’s cybercrime ecosystem has greatly grown. But due to the rapid proliferation of cybercrime, systemic shortcomings are revealed regarding the restoration of victims, investigation, forensic capacity, cross-border enforcement, awareness, and stakeholder coordination:
- Victim Restitution Deficit: Although the total of ₹ 8,690 crore frozen has increased, the refund for victim compensation is limited to only ₹ 167 crore (2.18%) due to lengthy restoration processes relying on court orders.
- Forensic Capacity Limitations: 2 national, state-level, unevenly equipped cyber forensic labs can’t match the needs of over 10 million cybercrime complaints per year.
- Low conviction rate: The investigations of cybercrimes suffer from evidence collection and criminal proceedings, leading to limited conviction rates.
- Cross-border enforcement challenges: Many of the investment and digital arrest scams, in fact, are originating from Cambodia, Myanmar, and Laos, rendering the cybercrime response mechanisms of India helpless.
- Lack of Awareness: First-time digital users are quite prone to online scams and fraud, and many of the victims continue not reporting due to social stigma and lack of confidence.
- Partial Stakeholder Integration: Banks and small financial institutions, small companies, and emerging virtual asset providers not yet on board allow the money to slip through without being tracked.
CyberPeace Insights: Strategic Way Forward
India has already built a relatively mature response structure for cybercrime with I4C, CFCFRMS, and CyTrain and is coordinating the financial sector on it. The way ahead lies in outcome-oriented improvements and not just in the ability to report and intercept more. Here are the priority interventions that address the most important institutional shortcomings identified in the current ecosystem:
- Fast-track victim restoration: Introduce time-bound victim restoration mechanisms for low-value incidents through simplified processes and mandate national-level roll-out of successful Lok Adalat-based settlement mechanisms.
- District-level cyber forensics: Establish cyber forensic support units at the district level and enhance access to mobile, cloud, and blockchain forensic capabilities.
- AI-powered fraud prevention: Mandate deep-fake and voice-clone detection mechanisms across all financial institutions and telecom networks; embed predictive risk analytics into transaction screening frameworks.
- Cyber Suraksha Gram initiative: Increase digital fraud awareness across all common service centres, Jan Dhan enrollment schemes, and rural banking channels, and tackle the awareness asymmetry.
- Regional cybercrime coordination: Establish real-time, operational intelligence-sharing mechanisms with Southeast Asian economies, which have become home to large scam networks preying on Indian citizens.
- Specialised cyber prosecution ecosystem: Develop exclusive cyber courts, standardise digital evidence procedures, and broaden the scope of CyTrain to include the development of specialised cadres of investigators and prosecutors capable of handling increasingly complex cybercrime cases.
Conclusion
The 22,812 crore lost due to cybercrime in 2024 was more than a mere figure; it signifies a serious concern regarding citizen trust, economic security, and digital inclusion. Though India's institutional response to cybercrime is one of the largest, with an operational I4C and a CFCFRMS functioning in real time, the victim compensation and prosecution mechanism falls short. It's time for implementation: faster recovery of resources, increased enforcement, a larger scale of awareness, and finally, translating the institutional innovations into concrete justice for victims nationwide.
References
- https://sansad.in/getFile/annex/270/AU1341_tmaxdx.pdf?source=pqars
- https://www.mha.gov.in/MHA1/Par2017/pdfs/par2025-pdfs/LS02122025/452.pdf
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2244504®=3&lang=2
- https://static.pib.gov.in/WriteReadData/specificdocs/documents/2025/oct/doc2025107659501.pdf
- https://www.medianama.com/2025/08/223-india-cybercrime-500-percent-increase-2021-2024/
- https://theprint.in/india/cybercrime-saw-24-spike-in-2025-indians-lost-rs-22495-crore-mainly-in-investment-scams/2859930/
