
#FactCheck-Mosque fire in India? False, it's from Indonesia
Executive Summary:
A social media viral post claims to show a mosque being set on fire in India, contributing to growing communal tensions and misinformation. However, a detailed fact-check has revealed that the footage actually comes from Indonesia. The spread of such misleading content can dangerously escalate social unrest, making it crucial to rely on verified facts to prevent further division and harm.

Claim:
The viral video claims to show a mosque being set on fire in India, suggesting it is linked to communal violence.

Fact Check
The investigation revealed that the video was originally posted on 8th December 2024. A reverse image search allowed us to trace the source and confirm that the footage is not linked to any recent incidents. The original post, written in Indonesian, explained that the fire took place at the Central Market in Luwuk, Banggai, Indonesia, not in India.

Conclusion: The viral claim that a mosque was set on fire in India isn’t True. The video is actually from Indonesia and has been intentionally misrepresented to circulate false information. This event underscores the need to verify information before spreading it. Misinformation can spread quickly and cause harm. By taking the time to check facts and rely on credible sources, we can prevent false information from escalating and protect harmony in our communities.
- Claim: The video shows a mosque set on fire in India
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs

Overview:
‘Kia Connect’ is the application that is used to connect ‘Kia’ cars which allows the user control various parameters of the vehicle through the application on his/her smartphone. The vulnerabilities found in most Kias built after 2013 with but little exception. Most of the risks are derived from a flawed API that deals with dealer relations and vehicle coordination.
Technical Breakdown of Exploitation:
- API Exploitation: The attack uses the vulnerabilities in Kia’s dealership network. The researchers also noticed that, for example, the logs generated while impersonating a dealer and registering on the Kia dealer portal would be sufficient for deriving access tokens needed for next steps.
- Accessing Vehicle Information: The license plate number allowed the attackers to get the Vehicle Identification Number (VIN) number of their preferred car. This VIN can then be used to look up more information about the car and is an essential number to determine for the shared car.
- Information Retrieval: Having the VIN number in hand, attackers can launch a number of requests to backends to pull more sensitive information about the car owner, including:
- Name
- Email address
- Phone number
- Geographical address
- Modifying Account Access: With this information, attackers could change the accounts settings to make them a second user on the car, thus being hidden from the actual owner of the account.
- Executing Remote Commands: Once again, it was discovered that attackers could remotely execute different commands on the vehicle, which includes:some text
- Unlocking doors
- Starting the engine
- Monitoring the location of the vehicle in terms of position.
- Honking the horn
Technical Execution:
The researchers demonstrated that an attacker could execute a series of four requests to gain control over a Kia vehicle:
- Generate Dealer Token: The attacker sends an HTTP request in order to create a dealer token.
- Retrieve Owner Information: As indicated using the generated token, they make another request to another endpoint that returns the owner’s email address and phone number.
- Modify Access Permissions: The attacker takes advantage of the leaked information (email address and VIN) of the owner to change between users accounts and make himself the second user.
- Execute Commands: As the last one, they can send commands to perform actions on the operated vehicle.
Security Response and Precautionary Measures for Vehicle Owners
- Regular Software Updates: Car owners must make sure their cars receive updates on the recent software updates provided by auto producers.
- Use Strong Passwords: The owners of Kia Connect accounts should develop specific and complex passwords for their accounts and then update them periodically. They should avoid using numbers like the birth dates, vehicle numbers and simple passwords.
- Enable Multi-Factor Authentication: For security, vehicle owners should turn on the use of the secondary authentication when it is available to protect against unauthorized access to an account.
- Limit Personal Information Sharing: Owners of vehicles should be careful with the details that are connected with the account on their car, like the e-mail or telephone number, sharing them on social networks, for example.
- Monitor Account Activity: It is also important to monitor the account activity because of change or access attempts that are unauthorized. In case of any abnormality or anything suspicious felt while using the car, report it to Kia customer support.
- Educate Yourself on Vehicle Security: Being aware of cyber threats that are connected to vehicles and learning about how to safeguard a vehicle from such threats.
- Consider Disabling Remote Features When Not Needed: If remote features are not needed, then it is better to turn them off, and then turn them on again when needed. This can prove to help diminish the attack vector for would-be hackers.
Industry Implications:
The findings from this research underscore broader issues within automotive cybersecurity:
- Web Security Gaps: Most car manufacturers pay more attention to equipment running in automobiles instead of the safety of the websites that the car uses to operate thereby exposing automobiles that are connected very much to risks.
- Continued Risks: Vehicles become increasingly connected to internet technologies. Auto makers will have to carry cyber security measures in their cars in the future.
Conclusion:
The weaknesses found in Kia’s connected car system are a key concern for Automotive security. Since cars need web connections for core services, suppliers also face the problem of risks and need to create effective safeguards. Kia took immediate actions to tighten the safety after disclosure; however, new threats will emerge as this is a dynamic domain involving connected technology. With growing awareness of these risks, it is now important for car makers not only to put in proper security measures but also to maintain customer communication on how it safeguards their information and cars against cyber dangers. That being an incredibly rapid approach to advancements in automotive technology, the key to its safety is in our capacity to shield it from ever-present cyber threats.
Reference:
- https://timesofindia.indiatimes.com/auto/cars/hackers-could-unlock-your-kia-car-with-just-a-license-plate-is-yours-safe/articleshow/113837543.cms
- https://www.thedrive.com/news/hackers-found-millions-of-kias-could-be-tracked-controlled-with-just-a-plate-number
- https://www.securityweek.com/millions-of-kia-cars-were-vulnerable-to-remote-hacking-researchers/
- https://news24online.com/auto/kia-vehicles-hack-connected-car-cybersecurity-threat/346248/
- https://www.malwarebytes.com/blog/news/2024/09/millions-of-kia-vehicles-were-vulnerable-to-remote-attacks-with-just-a-license-plate-number
- https://informationsecuritybuzz.com/kia-vulnerability-enables-remote-acces/
- https://samcurry.net/hacking-kia
Executive Summary
A video showing a man being beaten with a cricket bat is being widely shared on social media. It is being claimed that a priest had allegedly misbehaved with a girl at the same house where he had gone to perform a puja, following which the girl’s brother beat him up. However, our Research found the claim to be misleading. CyberPeace Research found that the video is around four years old. According to reports, the man was beaten after he allegedly objected to a cricket bat being kept inside a temple. Four youths were arrested by the police in connection with the incident.
Claim:
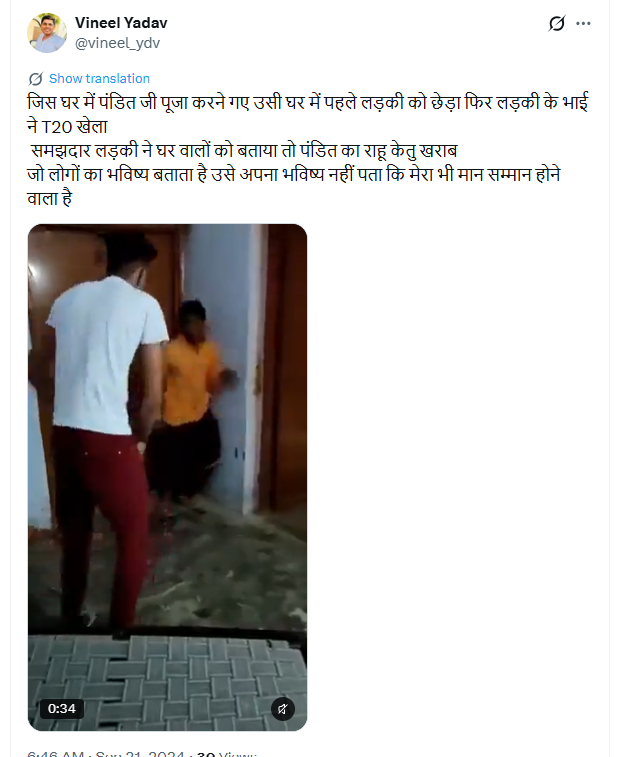
An X user shared the viral video with the caption: “The priest went to a house to perform a puja, where he first harassed a girl, and then the girl’s brother played T20. The sensible girl informed her family. The priest who predicts other people’s future could not predict his own—that his honour was also going to be at stake.”
https://x.com/vineel_ydv/status/1837299886921753054?s=20
https://ghostarchive.org/archive/b91vB
Fact Check
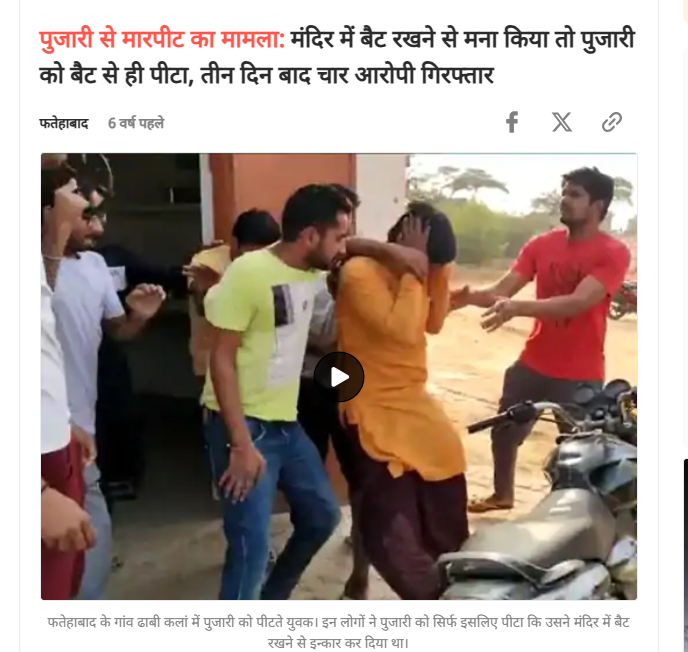
To verify the viral claim, we searched Google using relevant keywords. During the search, we did not find any credible media reports supporting the claim. To further verify the claim, we conducted a reverse image search of keyframes from the video. During the search, we found a report published by Dainik Bhaskar on November 5, 2020. According to the report, police arrested four youths in connection with the assault of a priest in Fatehabad, Haryana. The report stated that three days earlier, the youths had beaten the priest with a cricket bat after he objected to them keeping the bat inside the temple.
https://www.bhaskar.com/local/haryana/news/fatehabad-haryana-priest-beaten-with-cricket-bat-very-hardly-in-fatehabad-police-arrested-four-accused-127888122.html
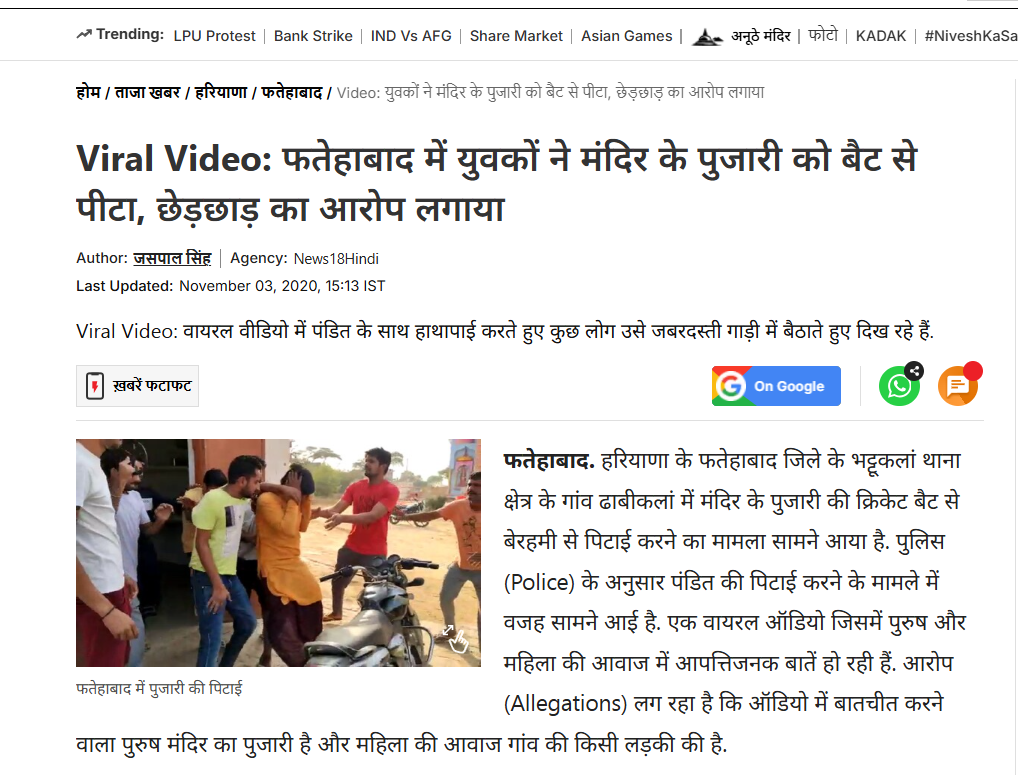
As part of the next step in our Research, we found a report published on the News18 website with a generic caption. The viral image was also included in the report.
Conclusion
Our Research found that the video is around four years old and is unrelated to the claim being circulated on social media. The incident took place after the priest objected to the youths keeping a cricket bat inside the temple, following which he was assaulted with the bat. Police subsequently arrested four youths in connection with the incident. Therefore, the claim that the priest was beaten after allegedly harassing a girl at the house where he had gone to perform a puja is misleading.
Introduction
It might seem too good to be true: free movies, live TV and sports without any subscription plan are deals that no one in India could actually refuse, and that’s precisely the explanation as to why applications such as Pikashow have gained tremendous traction in India and all over the world as well. However, cybersecurity authorities have a strong cause of concern: the threat that this type of application poses towards lakhs of Indians with malicious software, stealing information and even money. Pikashow may be a perfect case study to establish this problem, but in fact, it all ties down to how downloading anything without the recognised applications has certain risks attached to it.
The Pikashow Warning
With no monthly subscription fees, Pikashow is a popular free app for streaming movies, web series, live TV channels and sports programmes. Since its development, Pikashow has had a reputation for never being found on the Google Play Store or Apple’s App Store, which necessitates a process of side-loading. A side load, in this case, entails downloading the Pikashow APK file from an unofficial third-party source and manually installing the app, circumventing the security measures of official download channels.
The latter is significant because security experts who have analysed Pikashow argue that it acts as an informal content aggregator; movies and TV series are illegally scooped up from online streaming services, then shared via various third-party links and streamed without a content licence or any agreement with legitimate providers.
Without going through the rigorous checks conducted by Google or Apple, security researchers discovered that even while the app appeared to be working fine with its promised streams, hidden malware within the installer can run silently, leading to potentially significant security risks such as data theft of user logins, one-time passwords, and private files, including banking credentials. This has been cited to be so problematic for India that law enforcement agencies like the Indian Cyber Crime Coordination Centre under the Ministry of Home Affairs and the Cyber Dost platform are expected to have issued public advisories linking Pikashow to a proliferation of cases of cybercrime. Users should take into account the legal implications alongside security concerns, as using piracy apps may not only lead to device-compromising issues but can also be against the Copyright Act of India as well, thus increasing the risk of legal prosecution.
Why This Isn't Just a "Pikashow Problem"
This should not be viewed as a single warning concerning one app. Pikashow is merely an illustration of one app from millions that exists outside official app stores and is built with the same mechanics that make Pikashow dangerous and applicable to virtually any app, game, or "modded" file which is downloaded from a random website, third-party app store, or Telegram channel.
Some issues that persist are-
- Official app stores are like a filter that is not perfect, but it is still critical to the security on a user's device. Both Google and Apple's App stores run automatic and manual malware scanners, screen permissions for legitimate use, and have the ability to remove malicious developers as necessary. Empirical research has estimated just how important this is: more than fifty-times more malware exists on sideloaded, "unofficial" apps versus official. Mobile security firm Zimperium claims nearly 40% of all devices tested with malware were infected due to downloading an app from outside the official app stores; furthermore, nearly 80% of malicious, sideloaded apps contained riskware or trojans.
- Informational channels can also be used to gain the trust of users by mimicking familiar brands One frequently mentioned scheme is one where malicious actors repackage popular apps with a malignant intent to syphon the app, disguised as a free, trustworthy app. Often when these apps are available, they work exactly the same as the legitimate app, as a matter of fact, but quietly in the background steal passwords or log keystrokes; this was discovered to be occurring with a financial trojan called TeaBot, where bank details and login info were intercepted through the device's Accessibility Service.
- There is generally no recourse or legal liability that applies once something has gone wrong. While official app stores are official developers that can be identified to submit complaints against them, if a third-party download leads to damages, that developer generally cannot be located to establish liability or legal standing.
- Excessive app permissions will often go undetected This occurs for the similar reasons that a malicious actor can include such a clause as explained above. There's really nothing to stop the developer from asking to utilise one's SMS, call log, camera, microphone, storage or location when there's not one reason for one application to need access to everything on the device.
- Expired software has the same or more risk It's actually very common to see apps that receive security updates out in the wild that either don't have the appropriate update sent over to third-party app stores or third-party stores don't have the capacity to update the affected applications. That's why most official third-party app downloads should be of fairly new versions; for example, outdated versions of a banking app, which is being patched as well as receiving other updates from Google or Apple still, will continue to persist on third-party download sites for some time after patching, which could then be malicious.
- Even legitimate, globally recognised apps can and have been compromised The same vulnerability was noted for TikTok in 2023, which, when found on unofficial APK download sites, contained hidden data-tracking malware yet looked identical to the official app version.
How to Protect Yourself
The reassuring thing is that the vast majority of this risk can be eliminated through simple, repeatable habits. Use trusted sources like Google Play and Apple's App Store, which are not faultless, of course, but they remove many infected apps from circulation following review.
- Be sceptical of "free" premium-paid apps.
- If something in a file from a site you don't recognise offers content or features that are normally behind a paywall and they want nothing to do with it, that is a bad sign, not a good deal. Review app permissions when you go to install anything. A flashlight doesn't need access to your SMS messages or contacts, as one recently downloaded on a colleague's Android allegedly attempted to acquire them from the Google Play store. After sideloading any app that you do not fully trust, it's always a wise idea to uninstall it and scan the handset to ensure malicious files aren't still lingering around.
- Choose legitimate services to avoid malware.
- In entertainment terms this will apply most clearly to piracy but applies similarly elsewhere in many senses. Trusted sources that are licensed include YouTube, JioCinema, Hotstar, Netflix, Amazon Prime Video, and MX Player, among others, which will offer content similar to illegally acquired or pirated versions without the security, as well as the legal risks. If you have recently used the file installation route to any degree of caution on a sensitive device, then also monitor banking and payment apps.
- That is not least because the most reported consequence of infection from an illicit or unknown source is the theft of financial account login details.
Conclusion
Free entertainment can look tempting, but as cybersecurity experts keep pointing out, "free" often just means the cost has been shifted from your wallet to your data, your device, and potentially your bank account. The safest rule of thumb remains simple: if an app isn't on an official store, ask why and think twice before installing it.
Sources
- Pikashow app risky, may expose users to malware and data theft: Experts — Times of India
- Free OTT Hack or Cyber Trap? Pikashow Flagged for Serious Security Risks — The420.in
- Pikashow Warning: Free Movies Could Empty Your Bank Account, Government Issues Strong Alert — The420.in
- Is Pikashow Safe or Risky to Use in 2025? Expert's Advice — AiPlex AntiPiracy
- Why Pikashow May Not Be Safe for Your Device — AiPlex AntiPiracy
- Concerns Rise Over the Safety of Popular Streaming App Pikashow — openPR
- Beyond the App Store: The Hidden Risks of Sideloading Apps — Zimperium
- App Sideloading: Risks, Rules, and How IT Admins Respond — Trio
- What Are the Risks of Sideloading Apps on Your Smartphone? — Bitdefender
- Sideloading Risk: Alternative App Stores and Brand Protection — Allure Security
- Building a Trusted Ecosystem for Millions of Apps: A Threat Analysis of Sideloading — Apple
